
[m] munio
Security scanner and runtime guard for AI agent tool calls


AI agents call external tools — MCP servers, OpenClaw skills, API endpoints. A malicious or poorly-written tool can exfiltrate your data, execute arbitrary commands, or chain actions into multi-step attacks. munio catches these issues before they reach your agent.
pipx install munio
munio config-scan
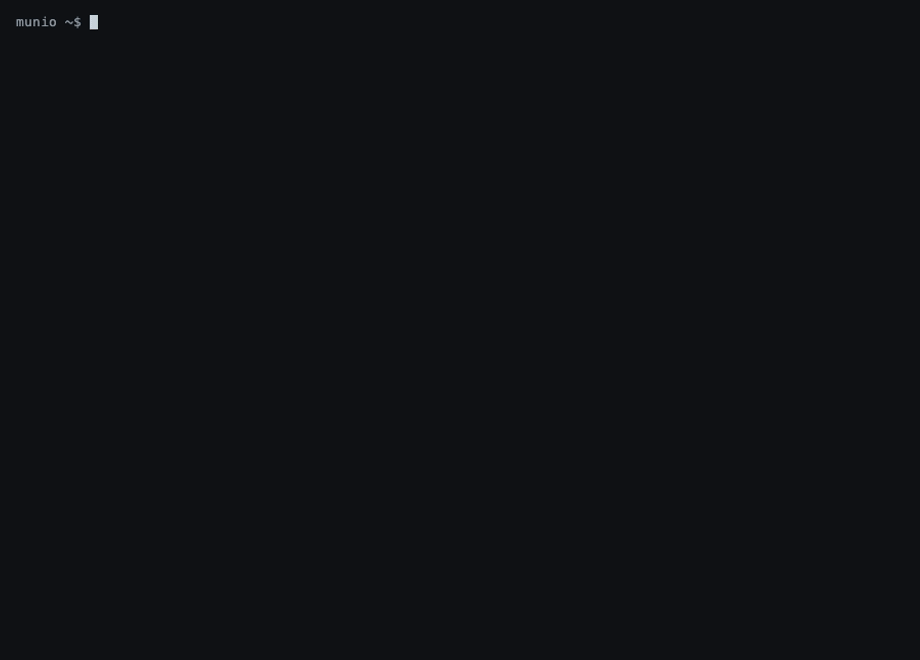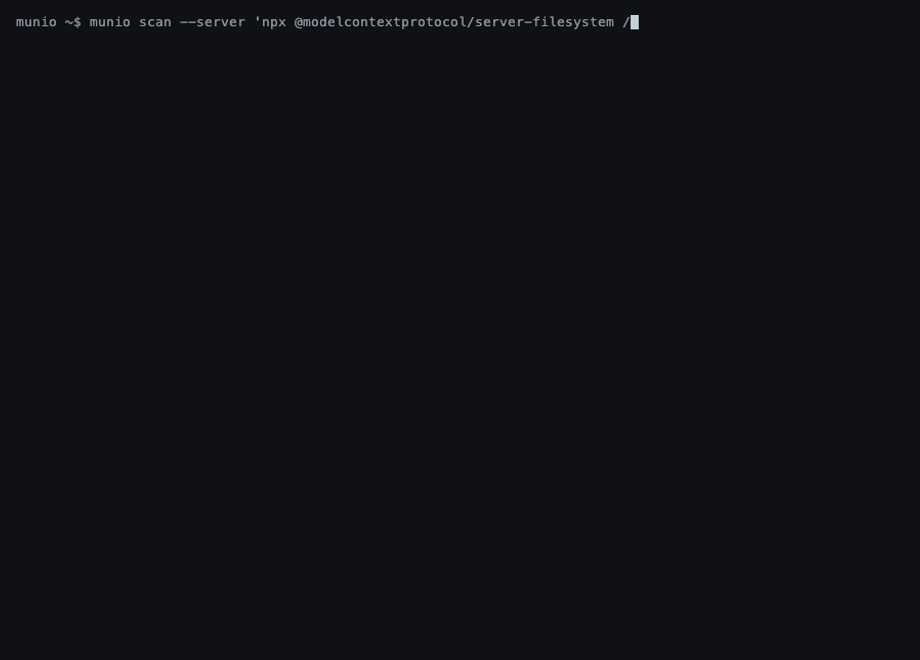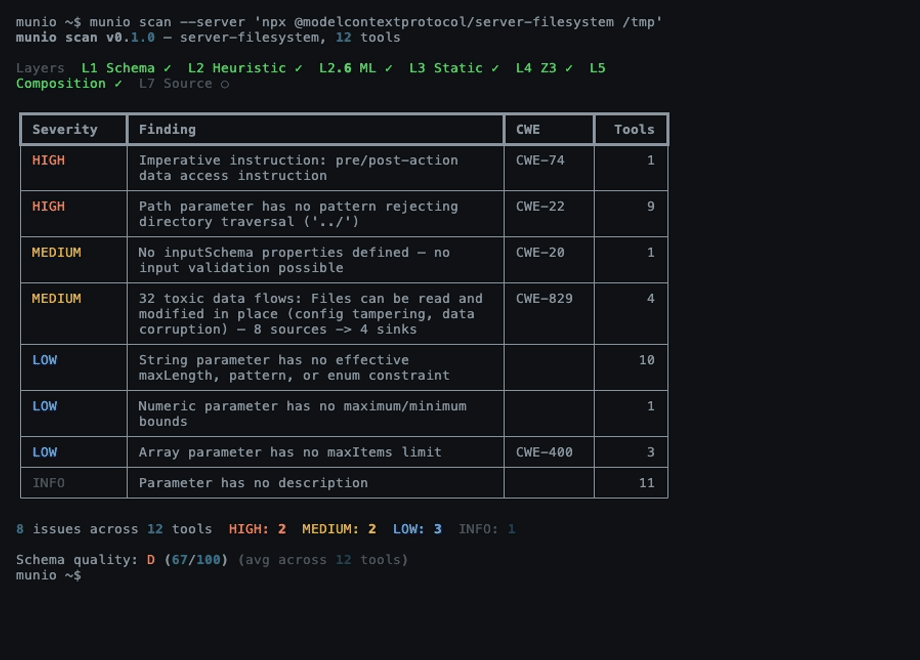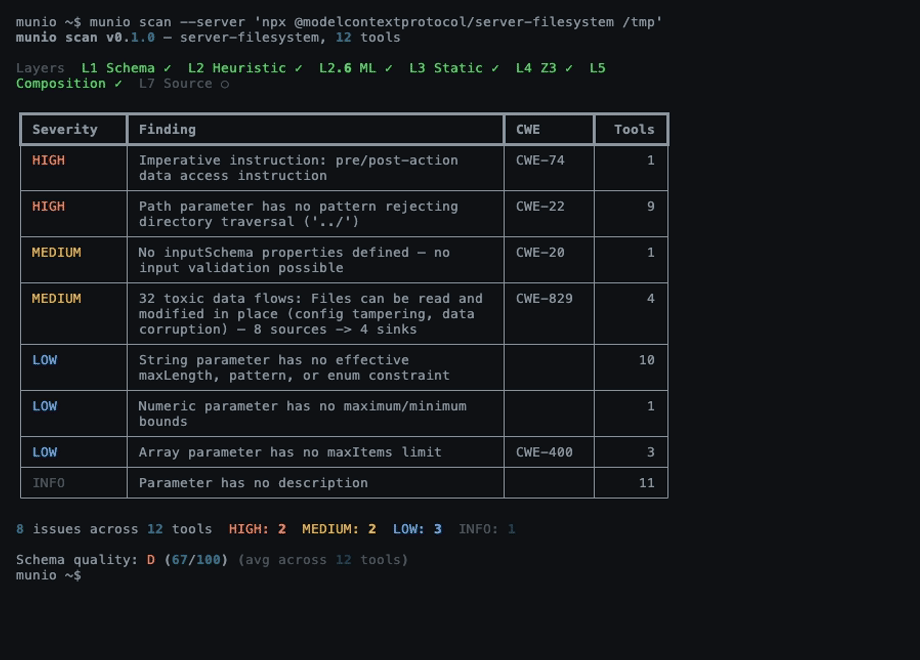
For deep tool schema analysis:
munio scan --server "npx @modelcontextprotocol/server-filesystem /tmp"No MCP servers? Try the bundled example:
munio scan --file examples/vulnerable-server.json --detailsThe same vulnerability classes that led to 512 findings in Copilot extensions and 820+ malicious OpenClaw skills -- path traversal, command injection, SSRF, prompt injection -- exist in every AI tool-calling ecosystem. MCP servers, OpenClaw skills, and framework-integrated tools share the same attack surface.
munio was built by scanning 700+ public MCP servers and responsibly disclosing the vulnerabilities found. It works with MCP, OpenClaw, LangChain, CrewAI, and OpenAI Agents SDK.
| Category | Examples | How |
|---|---|---|
| Path traversal | ../../etc/passwd in file parameters |
Schema analysis + Z3 formal proof |
| SSRF | http://169.254.169.254 in URL parameters |
Pattern matching + Z3 proof |
| Command injection | ; rm -rf / in shell parameters |
Denylist + regex + Z3 proof |
| Prompt injection | Hidden instructions in tool descriptions | ML classifier (188 languages) |
| Data exfiltration | read_file + http_request = stolen secrets |
Compositional flow analysis |
| Supply chain | Unpinned npm deps, hardcoded API keys in config | Config file scanner |
pipx install munio          # CLI (recommended)
pip install munio            # library
pip install "munio[z3]"      # with formal verification
pip install "munio[all]" # everythingmunio scan --server "npx @foo/mcp-server" # scan a live server
munio scan --file tools.json # scan exported schemas
munio scan # auto-discover from IDE configs
munio scan --details # show affected tools and fixes
munio scan --format sarif --output report.sarif # SARIF 2.1.0 for CI8 analysis layers: L1 Schema, L2 Heuristic, L2.5 ML Classifier, L2.6 Multilingual ML, L3 Static, L4 Z3 Formal, L5 Compositional, L7 Source.
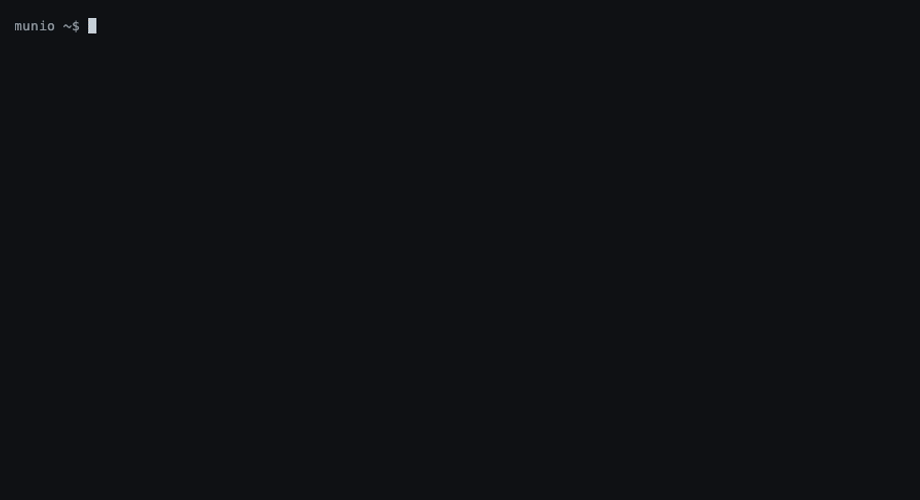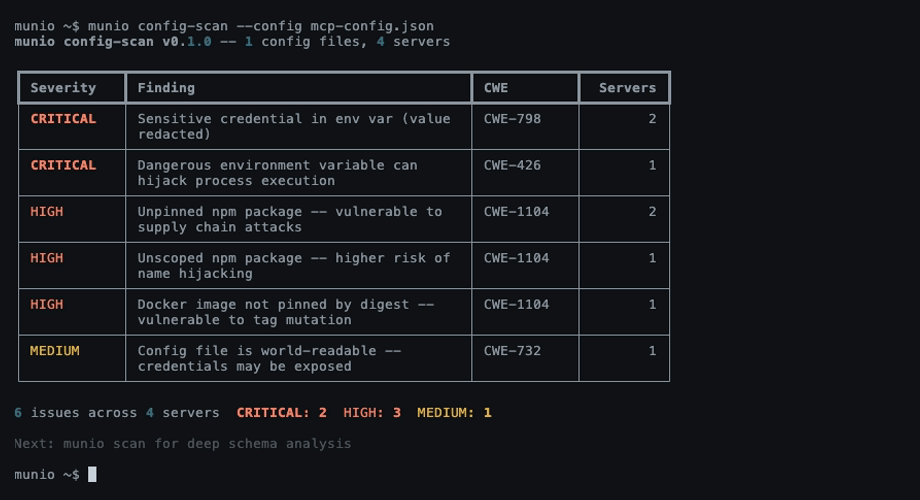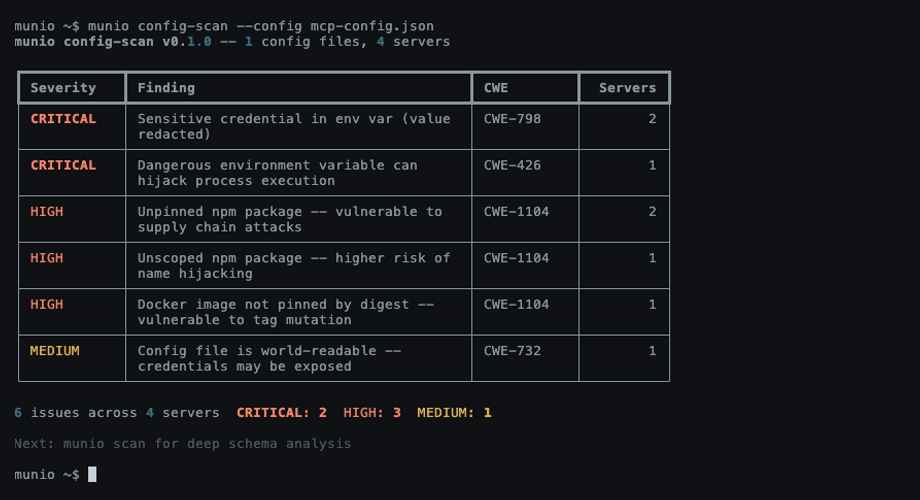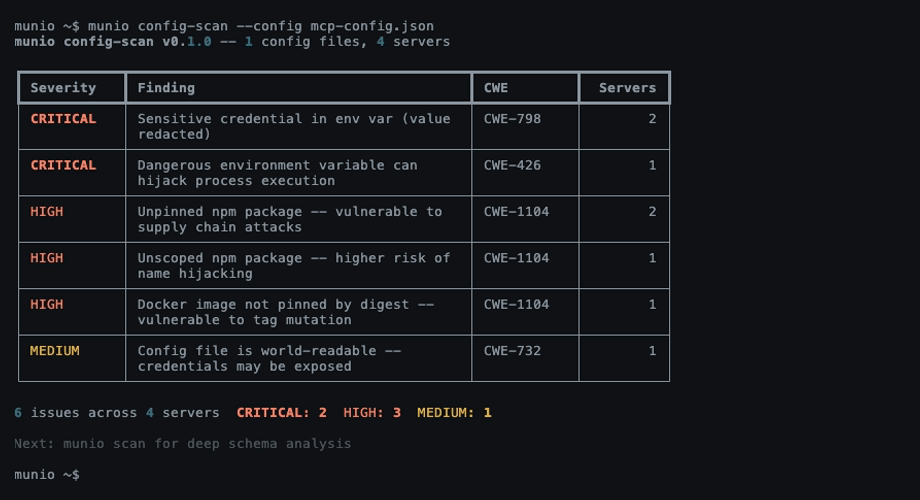
Finds hardcoded credentials, unpinned dependencies, and supply chain risks in Claude Desktop, Cursor, VS Code, Windsurf, Cline, and Junie configs. No server connections needed.
munio config-scan                    # auto-discover all IDE configs
munio config-scan --config file.json # scan a specific config
munio compose --schemas-dir ./schemas  # analyze pre-fetched schemas
munio compose --format markdown # generate CVE filing draftsIntercept every tool call before execution. No code changes.
munio init      # wrap all MCP servers in IDE configs
munio status    # check protection status
munio restore   # remove wrapper
After munio init, every tools/call is verified against YAML constraints. Dangerous calls are blocked before reaching the server.
name: block-dangerous-urls
action: http_request
check:
  type: denylist
  field: url
  values: ["evil.com", "169.254.169.254"]
  match: contains
on_violation: block
severity: critical
8 check types: denylist, allowlist, threshold, regex_deny, regex_allow, composite, rate_limit, sequence_deny.
from munio import Guard

guard = Guard(constraints="generic")
result = guard.check({"tool": "http_request", "args": {"url": "https://evil.com"}})
# result.allowed = False
Adapters for LangChain, CrewAI, OpenAI Agents SDK, and MCP. See docs.
The runtime gate is 100% in-process and deterministic — no SMT solver, no
subprocess, and the [z3] extra is not required to run it:
| What | Backend | Latency |
|---|---|---|
| Denylists, allowlists, regex, thresholds | Pure Python | <0.01ms |
| Multi-variable arithmetic constraints | Exact endpoint evaluator | <0.1ms |
For a constraint like cost * quantity <= budget, munio decides whether any
in-bounds value of a missing variable could violate it by evaluating the
polynomial at the bounds — an exact answer, no solver. Constraints outside that
grammar are rejected at load time with an actionable message, never mis-decided.
Z3 is used only offline, where satisfiability is the real problem and there's
no latency pressure: deploy-time policy verification (munio policy) and static
scanning (munio scan layer L4). Both are in the optional [z3] extra.
| Command | What |
|---|---|
munio scan |
Scan MCP server tool schemas |
munio config-scan |
Scan config files for supply chain risks |
munio compose |
Detect cross-server attack chains |
munio init / status / restore |
Manage runtime protection |
munio gate -- CMD |
Proxy a single MCP server |
munio check JSON |
Verify a single action |
munio serve |
HTTP API server |
munio policy |
Deploy-time Z3 policy verification |
munio download-models |
Download ML classifier models |
git clone https://github.com/munio-dev/munio.git && cd munio
make install    # uv sync + pre-commit hooks
make test       # 3900+ tests
make ci         # lint + typecheck + tests + coverage