You signed in with another tab or window. Reload to refresh your session.You signed out in another tab or window. Reload to refresh your session.You switched accounts on another tab or window. Reload to refresh your session.Dismiss alert
In this part of source code, we find that users can make connection requests to any IP address.
Then we found that the designer page did not verify the access user's permission.
So we can directly implement the SSRF attack on this page to detect the database port of the intranet device.
When the database port is detected to be open, the page will respond to the database login failure.
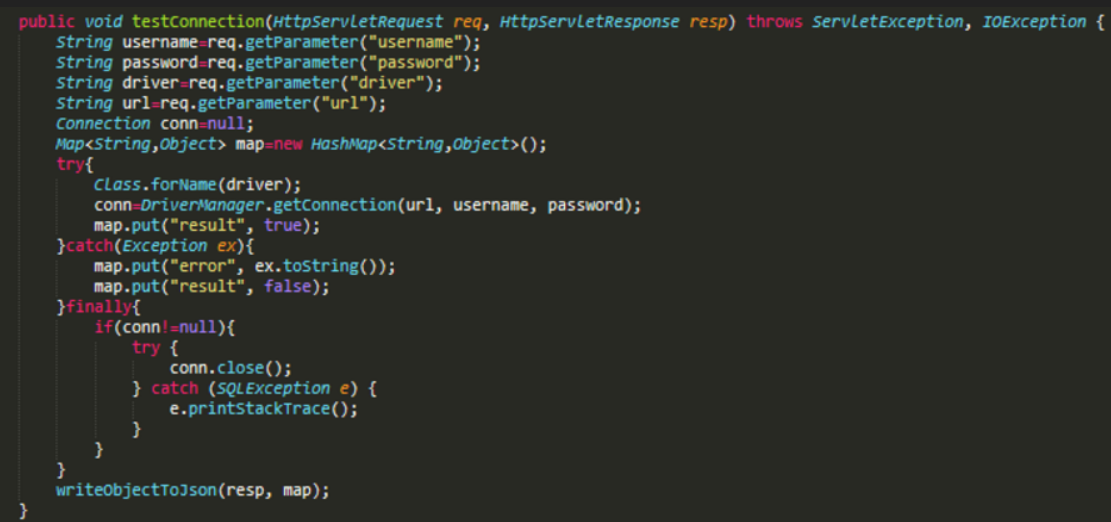
In this part of source code, we find that users can make connection requests to any IP address.


Then we found that the designer page did not verify the access user's permission.
So we can directly implement the SSRF attack on this page to detect the database port of the intranet device.
When the database port is detected to be open, the page will respond to the database login failure.