Repository navigation
Schaffa 0.14.0

Note
🤖 Claude Opus 5.5 responding on behalf of beastyrabbit
Schaffa 0.14.0 gives schaffa.dev a proper Impressum and privacy policy, in German and English, reachable from every page Schaffa renders itself.
Anyone opening a shared page, file or guide can now see who runs the service, what it stores about visitors and uploads, and how to get content removed. Self-hosted instances are unaffected.
Legal notice and privacy policy
| Desktop | Mobile |
|---|---|
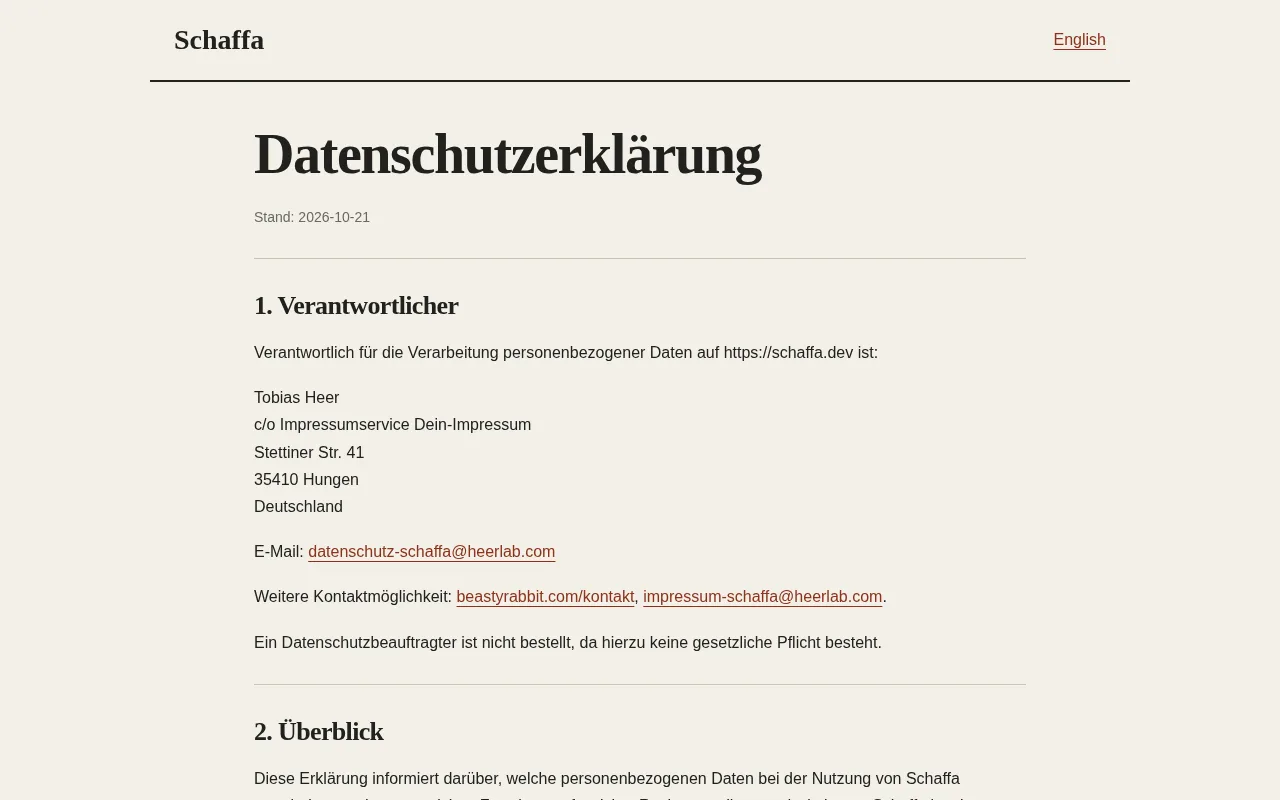 |
 |
- New pages.
/impressumand/datenschutzare in German,/legal-noticeand/privacyare the English versions. They are self-contained pages that load nothing else, are marked noindex, and are readable without signing in. - Footer links. Every page Schaffa renders itself links to them: landing, account, admin, skills, the API reference, interactive-page warnings, scan status, guides and error pages. Uploaded pages, raw views, sandboxed runs and files stay byte-identical.
- Guides. Published guide HTML views (
/g/…) now carry the footer. Stored revisions and the.json/.mdexports are unchanged. - What the privacy policy covers:
- which data is collected and why: hosting and logs, attack protection, sign-in through Shoo and Google, accounts and uploads, malware scanning, and e-mail;
- how long it is kept;
- how uploaders and affected third parties can get content removed.
- schaffa.dev only. The pages and footer appear only when
SCHAFFA_BASE_URLpoints at schaffa.dev. Self-hosted instances get a normal 404 at those paths and no footer, and should provide their own legal pages. - Browser 404s. On every instance, a browser GET outside
/api(Accept includestext/html) that finds nothing now gets an HTML 404 page instead of raw JSON. This covers unknown routes and missing files, guides and static/runURLs. Everything under/api, the CLI and other non-browser clients still get JSON errors.
Security updates
Dependency patches for the following high-severity advisories:
- Multipart parsing: denial-of-service advisories in
@fastify/busboy, fixed by moving@fastify/multipartto 10.1.4. - Images: a librsvg advisory, fixed by moving
sharpto 0.35.5. - CLI:
markdown-it,source-map-jsandpostcss-selector-parserare updated.
Upgrade notes
- Configuration: nothing changes.
- Pangolin: Pangolin deployments in front of schaffa.dev need exact-path bypass rules for
/impressum,/datenschutz,/legal-noticeand/privacy. The README lists them alongside the existing public routes.
Full changes: #12, #13 · v0.13.0...v0.14.0