Repository navigation
Schaffa 0.15.0

Note
🤖 Claude Opus 5.5 responding on behalf of beastyrabbit
Schaffa 0.15.0 can now show how it is actually used and catch errors before anyone reports them. Visitors stay in control: analytics only runs after they opt in, and the pages and files people publish are never instrumented.
Usage analytics with real consent
| Landing page, desktop | Datenschutz, mobile |
|---|---|
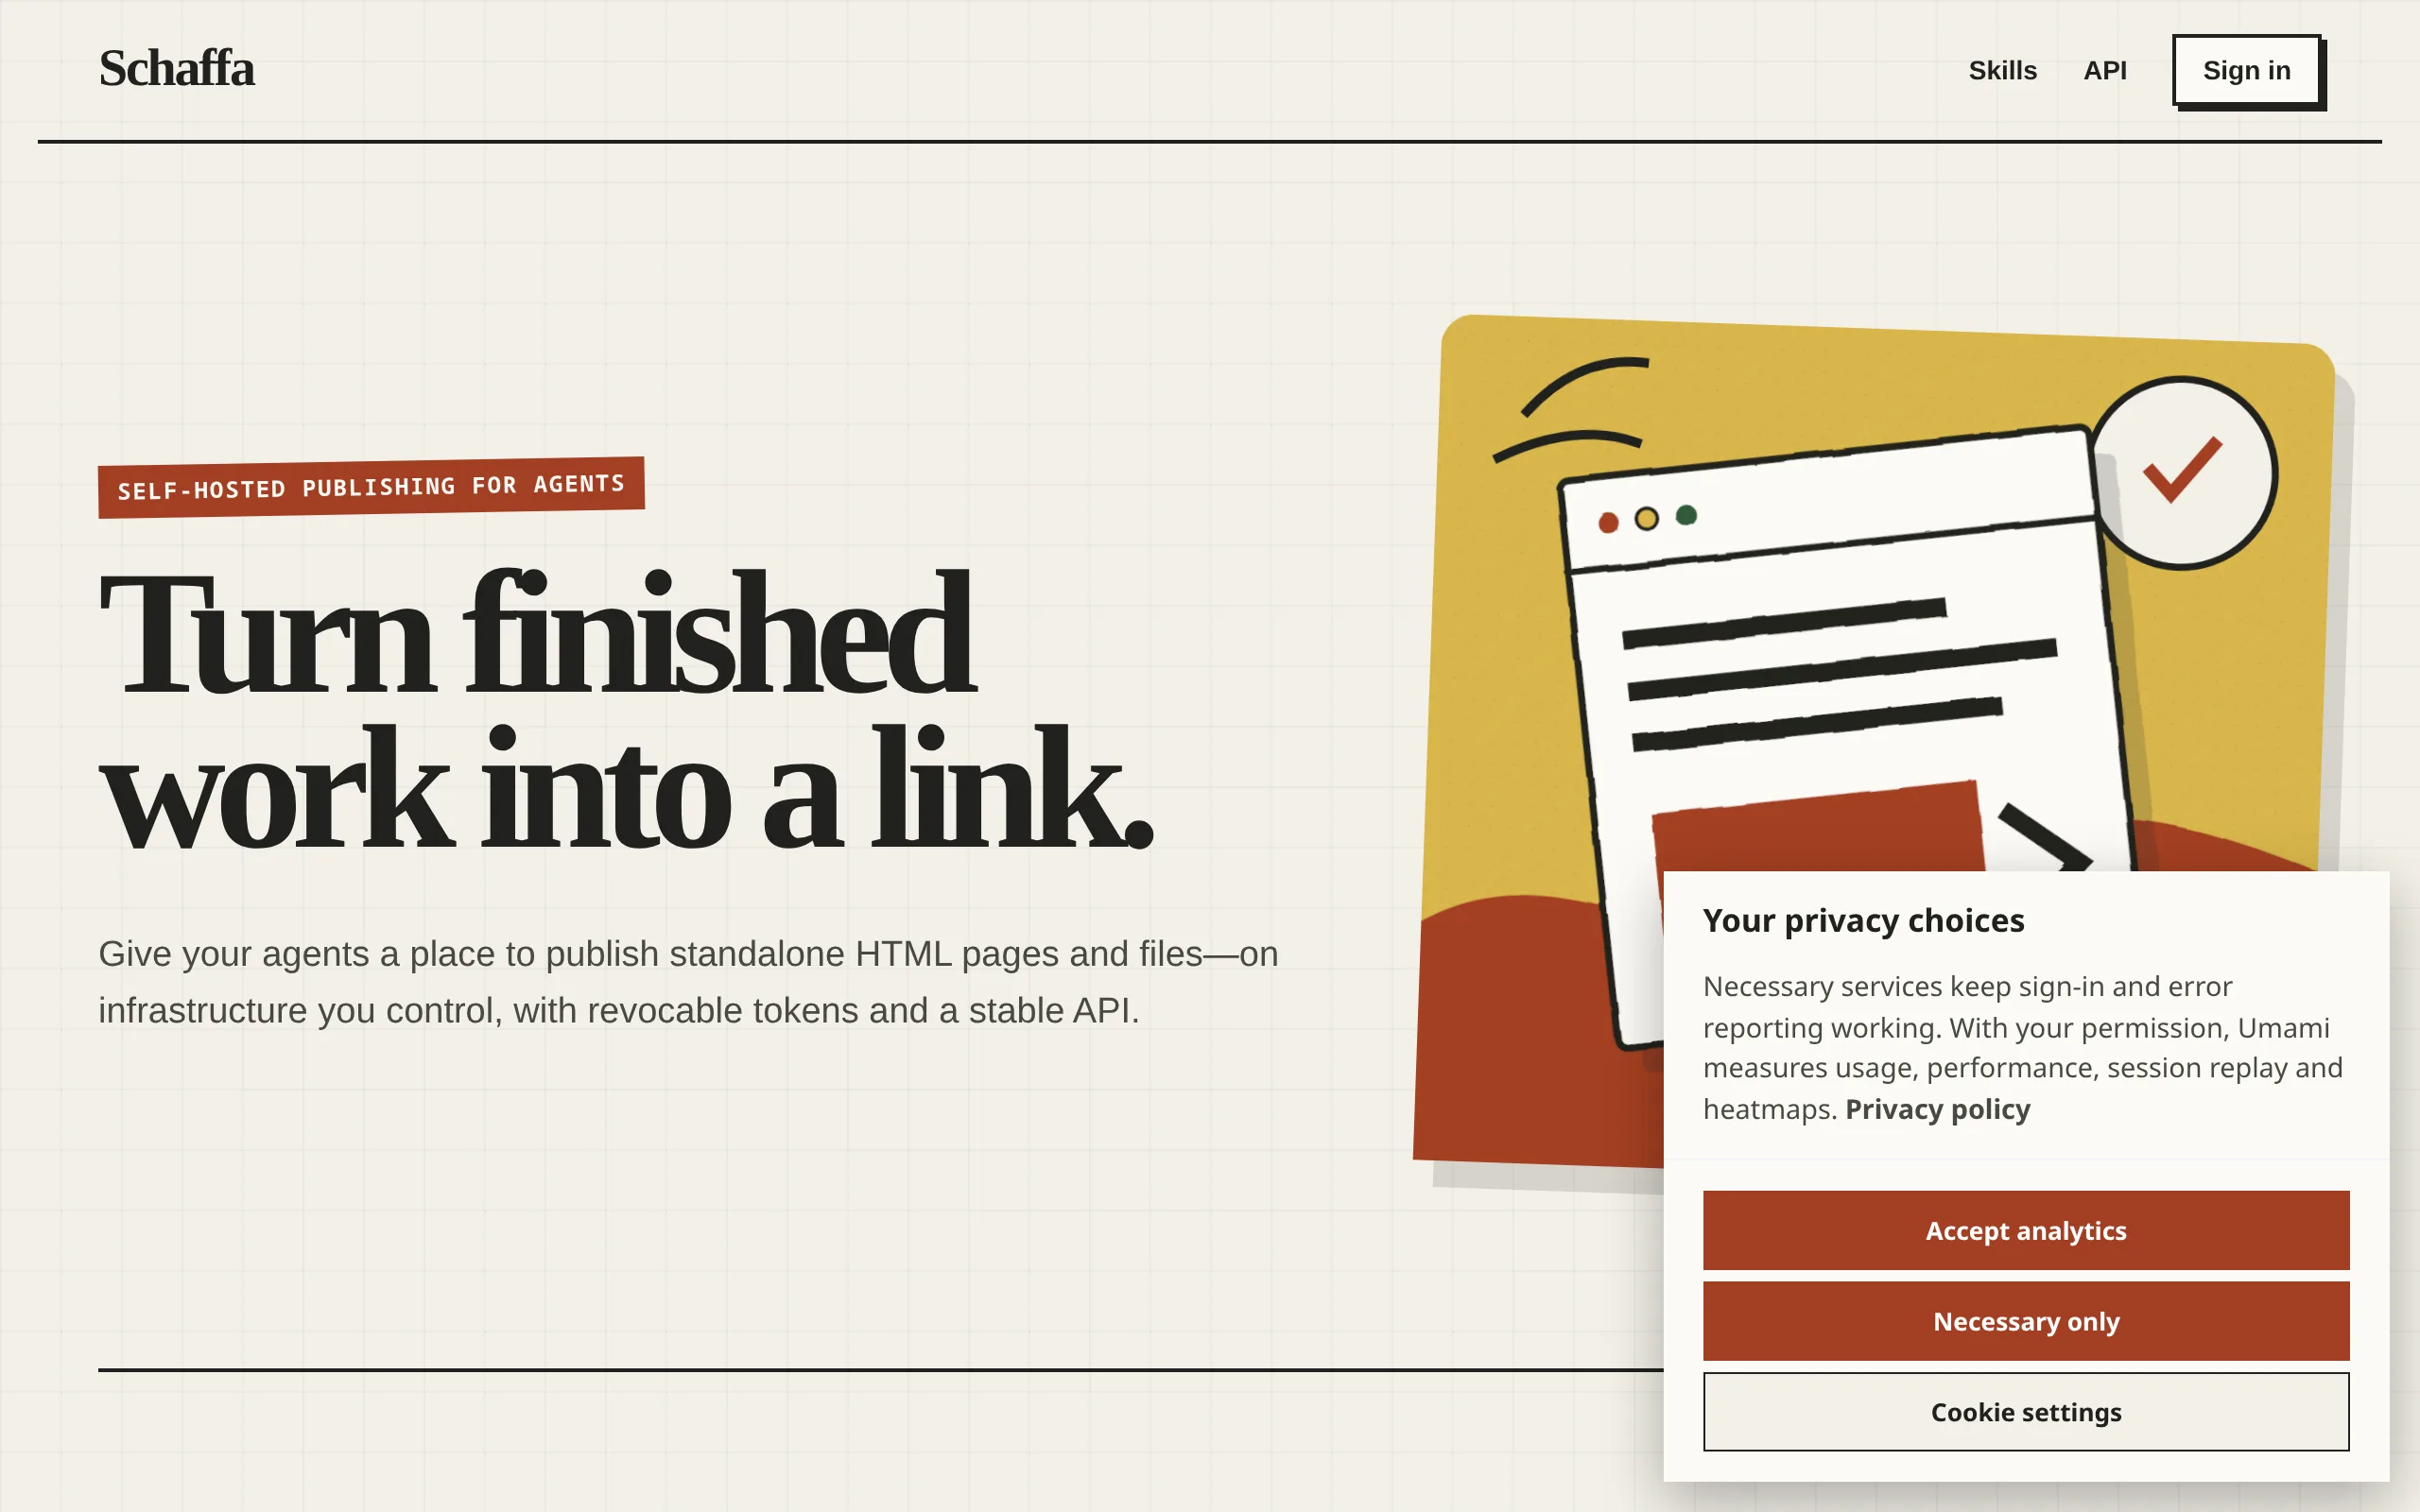 |
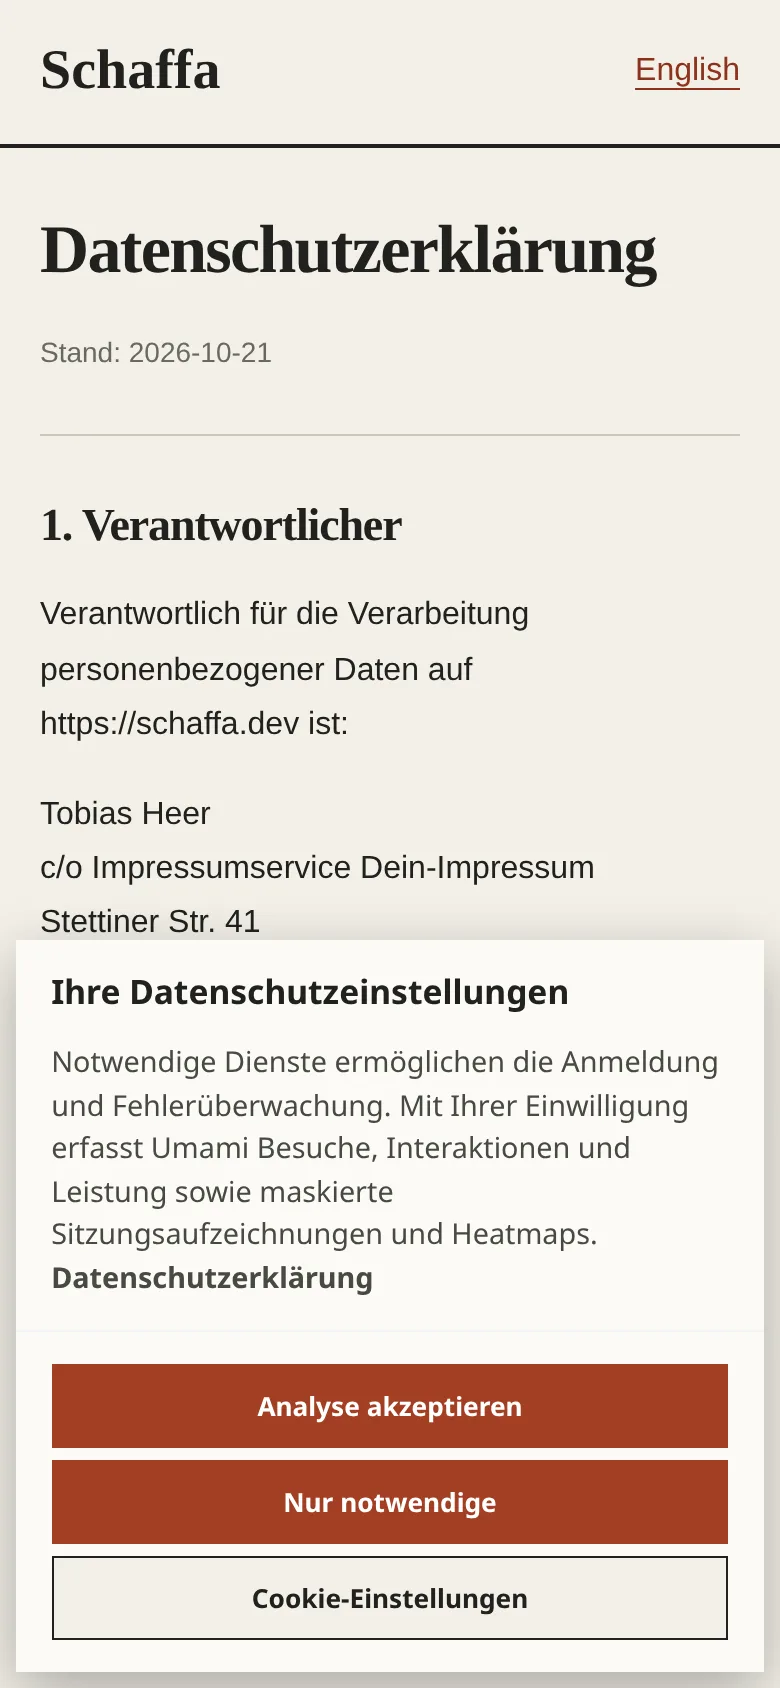 |
- Bilingual cookie banner. Schaffa's own public pages ask once, in German or English depending on the page. That covers landing, skills, account and sign-in, Impressum and privacy. "Accept analytics" and "Necessary only" carry equal weight. Cookie-Einstellungen / Cookie settings in the footer reopens the dialog at any time, and withdrawing consent stops tracking immediately.
- Self-hosted Umami, after opt-in only. It records pageviews, Core Web Vitals, outbound links and key actions: sign-in started, quickstart and skill-install copies, token copies, CTA clicks. Masked session replay and heatmaps are included too. Inputs, the account workspace and token displays are always blocked, and replay never runs on account pages or on pages that show a secret.
- Nothing on published content. Uploaded pages, files, guides and presentations stay byte-identical and get no banner, script or replay. Views of published content and API outcomes are counted on the server instead: what was published, deleted, rejected by a scan or quota, sign-ins, tokens. These counts carry no cookies, IP address or other personal data.
- Admin stays quiet.
/admingets error reporting only, with no banner and no analytics.
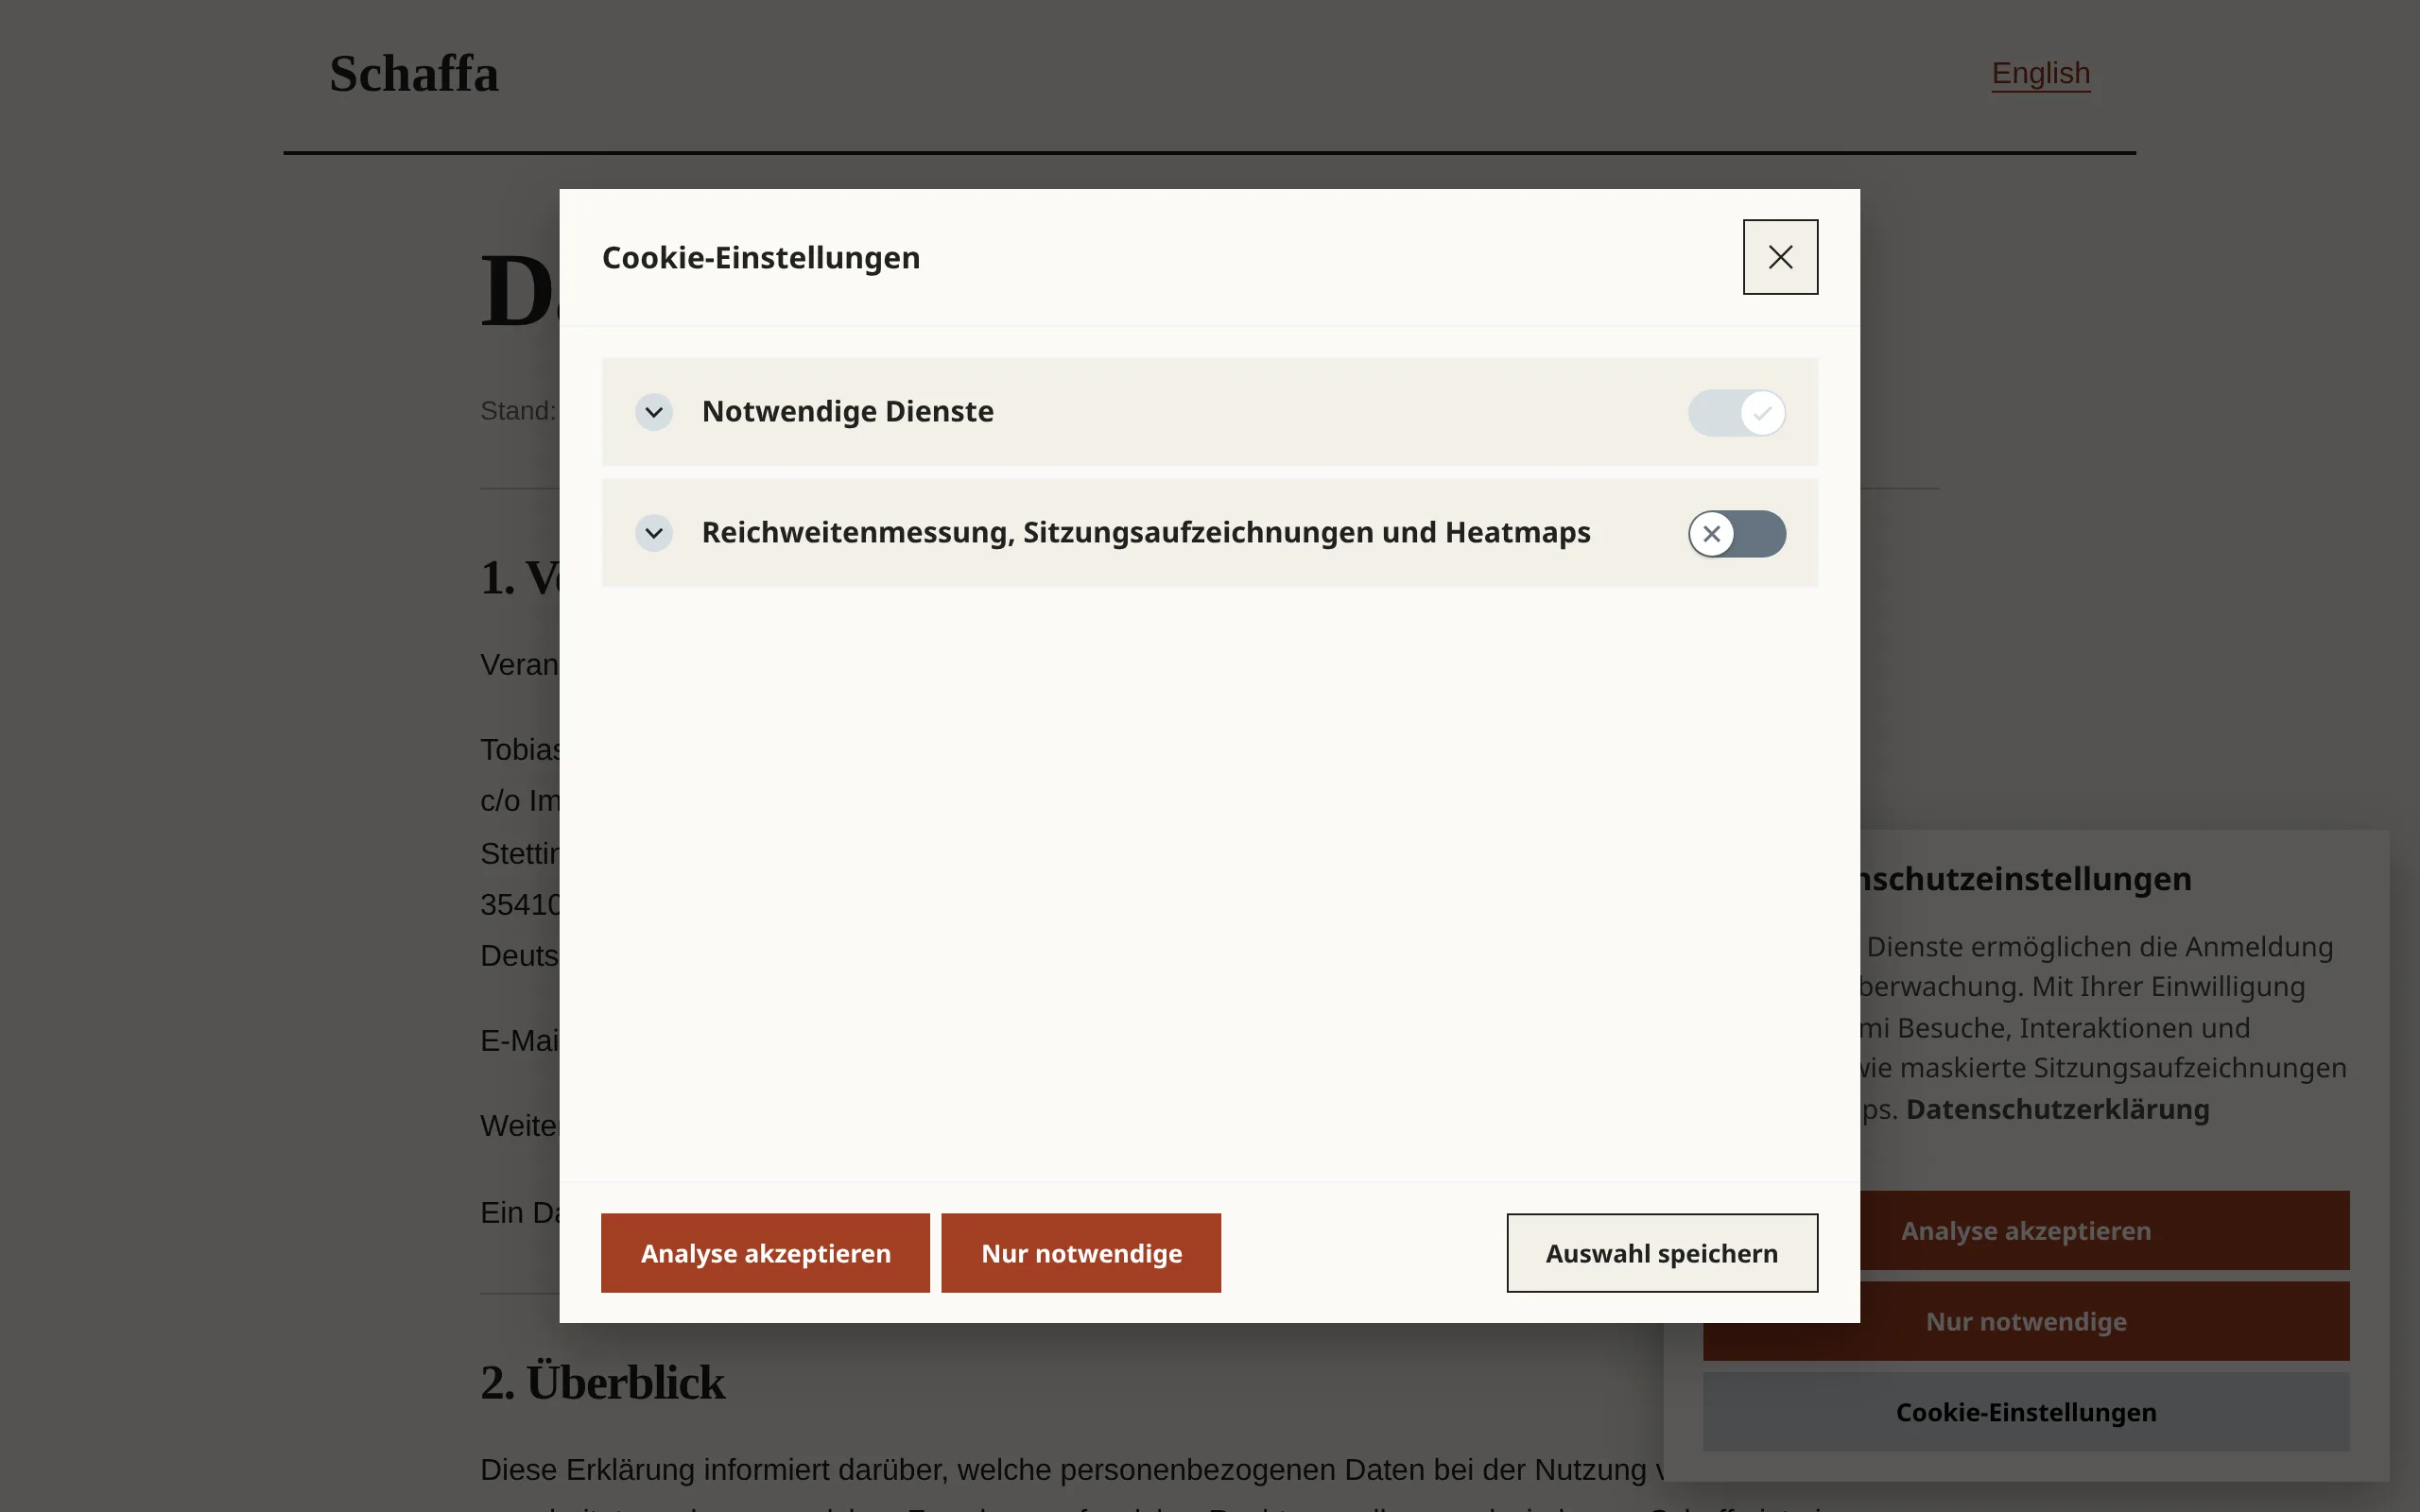
Error tracking with GlitchTip
- Server and browser errors now reach the self-hosted GlitchTip: unexpected 5xx responses, failures in background jobs, unhandled rejections, and errors users actually see. Expected states such as a full storage quota are not reported.
- Privacy: no personal data, no cookies, no browser storage. Tokens, e-mail addresses (including quoted and internationalized ones), URL parameters and concrete IDs in paths are removed before a report leaves the server or browser.
- Readable stack traces. Every release uploads source maps for its exact image: debug IDs are checked against the published container first. Maps are stripped from the image itself.
Privacy policy
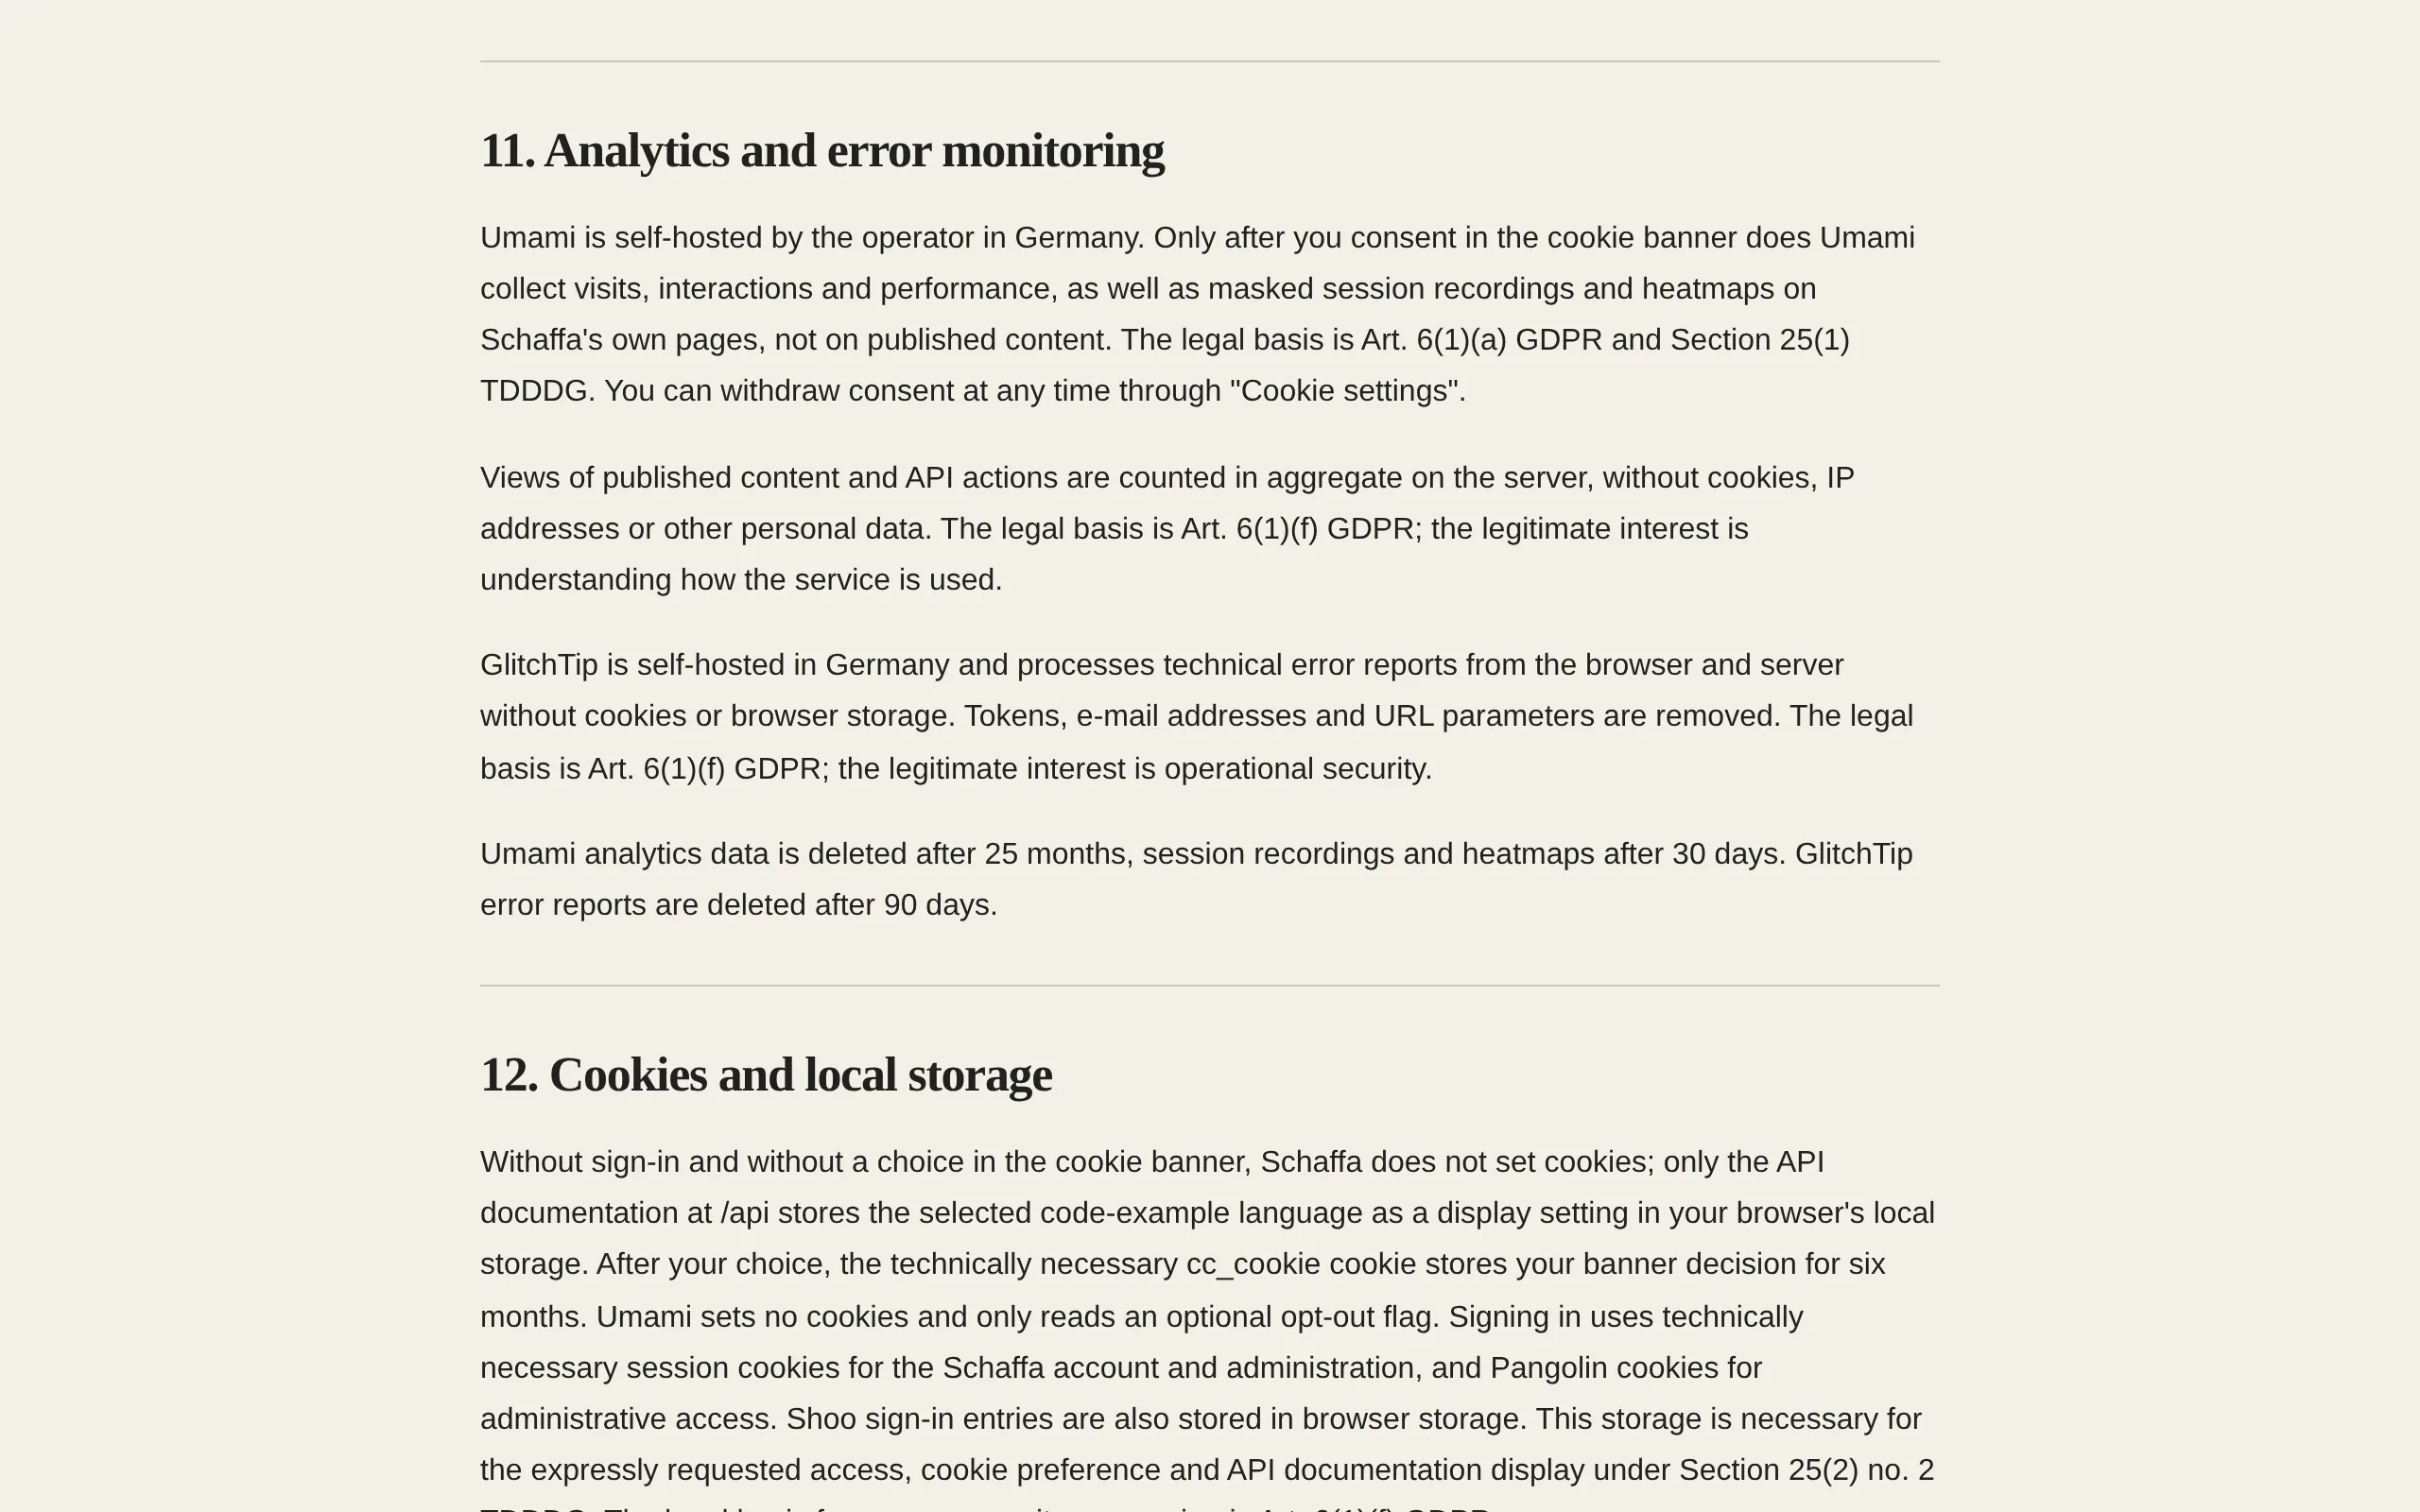
The privacy policy gains a section Reichweitenmessung und Fehlerüberwachung / Analytics and error monitoring, and the cookies section now names the banner's cc_cookie and the API reference's stored code-example language. Retention: Umami analytics data for 25 months, replays and heatmaps for 30 days, error reports for 90 days.
Upgrade notes
- Off by default. Telemetry only starts when
UMAMI_URL+UMAMI_WEBSITE_IDand/orGLITCHTIP_DSNare set. Self-hosted instances without them behave exactly like 0.14.0, with no banner and unchanged CSPs. See Optional analytics and error reporting. - Node startup. The container now starts with
node --import ./dist/instrumentation.js dist/server.js. Custom start commands should do the same. - Pangolin: no new public routes. The new assets are served under the existing
/assets/*bypass. - Security: a scoped override moves
brace-expansionto 5.0.12 to fix two high-severity advisories that came in through the Sentry SDK.
Full changes: #14 · v0.14.0...v0.15.0