Repository navigation
Prowler 5.7.0

New features to highlight in this version
🚀 Performance Improvements
- Optimized
/findings/metadataand resource-related filters for significantly faster querying and filtering of findings - Enhanced
/overviewsendpoints for better response times and scalability in large environments - Added new high-performance endpoints to fetch the latest findings and metadata quickly
Important
The performance optimization included in /findings and /findings/metadata applies for scans from this release on. This also applies to the service, region and resource_type filters for these views.
These updates collectively reduce latency, improve data freshness, and scale better across high-volume environments.
👨💻 GitHub Provider (CLI Only)
We’ve added GitHub as a new cloud provider in the Prowler CLI. Including:
- 11 security checks tailored for GitHub, see all with
prowler github --list-checksor in Prowler Hub at https://hub.prowler.com/ - Based on CIS GitHub Benchmark v1.0.0
Warning
Currently available in the CLI only — support for the App is coming in an upcoming release!
Tip
Try it out now with prowler github
📘 Prowler ThreatScore for Microsoft 365
We’ve extended Prowler ThreatScore to support Microsoft 365 environments:
- Assigns a contextual risk score to your M365 tenant based on detected misconfigurations and best practices
- Helps prioritize remediation efforts with actionable insights
- Enhances visibility into your Microsoft 365 security posture
Tip
Try it out now with prowler m365 --compliance prowler_threatscore_m365
📘 CIS M365 Benchmark v4.0.0
You can now assess your M365 environment against the CIS v4.0 framework. This brings M365 in line with our existing CIS support for AWS, GCP, Kubernetes and Azure, expanding your ability to meet compliance requirements across cloud platforms.
Tip
Try it out now with prowler m365 --compliance cis_4.0_m365
📘 CIS AWS Foundations Benchmark v5.0.0
Prowler now includes full coverage for the CIS AWS Foundations Benchmark version 5.0.0, aligning with the latest security best practices from the Center for Internet Security.
Tip
Try it out now with prowler aws --compliance cis_5.0_aws
Provider UID Filter Enhanced
We’ve significantly enhanced the Provider UID filter in the App to make multi-cloud analysis faster and more intuitive:
- 🌐 Provider icons (AWS, GCP) for instant visual identification
- 🏷️ Including the Cloud Provider alias
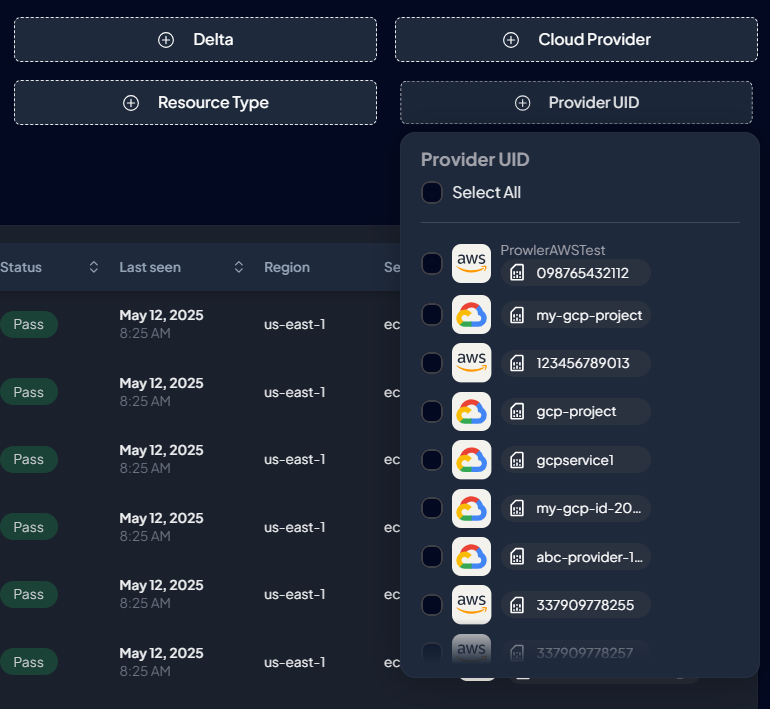
☁️ AWS CloudFormation Quick Link for IAM Role Setup
We’ve streamlined the setup process for AWS IAM Role credentials with a new CloudFormation Quick Link:
- Launch the required IAM Role stack in one click
- Pre-filled with the necessary permissions and trust policies
- Available directly in the IAM Role credentials step for faster onboarding

This update helps you get started with Prowler in AWS faster and with fewer manual steps.
🎨 UI
🚀 Added
- Add a new chart to show the split between passed and failed findings. (#7680)
- Added
Accordioncomponent. (#7700) - Improve
Provider UIDfilter by adding more context and enhancing the UI/UX. (#7741) - Added an AWS CloudFormation Quick Link to the IAM Role credentials step (#7735)
- Use
getLatestFindingson findings page when no scan or date filters are applied. (#7756)
🐞 Fixed
- Fix form validation in launch scan workflow. (#7693)
- Moved ProviderType to a shared types file and replaced all occurrences across the codebase. (#7710)
- Added filter to retrieve only connected providers on the scan page. (#7723)
- Removed the alias if not added from findings detail page. (#7751)
💻 API
🚀 Added
- Added huge improvements to
/findings/metadataand resource related filters for findings (#7690). - Added improvements to
/overviewsendpoints (#7690). - Added new queue to perform backfill background tasks (#7690).
- Added new endpoints to retrieve latest findings and metadata (#7743).
🔧 SDK
🚀 Added
- Update the compliance list supported for each provider from docs. (#7694)
- Allow setting cluster name in in-cluster mode in Kubernetes. (#7695)
- Add Prowler ThreatScore for M365 provider. (#7692)
- Add GitHub provider. (#5787)
- Add
repository_default_branch_requires_multiple_approvalscheck for GitHub provider. (#6160) - Add
repository_default_branch_protection_enabledcheck for GitHub provider. (#6161) - Add
repository_default_branch_requires_linear_historycheck for GitHub provider. (#6162) - Add
repository_default_branch_disallows_force_pushcheck for GitHub provider. (#6197) - Add
repository_default_branch_deletion_disabledcheck for GitHub provider. (#6200) - Add
repository_default_branch_status_checks_requiredcheck for GitHub provider. (#6204) - Add
repository_default_branch_protection_applies_to_adminscheck for GitHub provider. (#6205) - Add
repository_branch_delete_on_merge_enabledcheck for GitHub provider. (#6209) - Add
repository_default_branch_requires_conversation_resolutioncheck for GitHub provider. (#6208) - Add
organization_members_mfa_requiredcheck for GitHub provider. (#6304) - Add GitHub provider documentation and CIS v1.0.0 compliance. (#6116)
- Add CIS 5.0 compliance framework for AWS. (7766)
- Add CIS 4.0 for M365 provider. (#7699)
🐞 Fixed
- Update and upgrade CIS for all the providers (#7738)
- Cover policies with conditions with SNS endpoint in
sns_topics_not_publicly_accessible. (#7750) - Change severity logic for
ec2_securitygroup_allow_ingress_from_internet_to_all_portscheck. (#7764)
Full Changelog: 5.6.0...5.7.0