Repository navigation
Bootloaders trusted firmware m
Trusted Firmware-M, the Armv8-M secure runtime.
| Type | Monolithic bootloader (type3) |
| Upstream | https://github.com/TrustedFirmware-M/trusted-firmware-m |
| CVEs attributed | 2 |
| Vulnerability-fixing commits | 4 naming a CVE, 58 keyword-matched |
| CVEs with a linked fix | 0 |
Secure boot (often MCUboot-based BL2) plus the secure processing environment the non-secure application calls into.
Type 3: reset to application on a microcontroller.
See Boot-Stages for the eight-stage model these phases map onto.
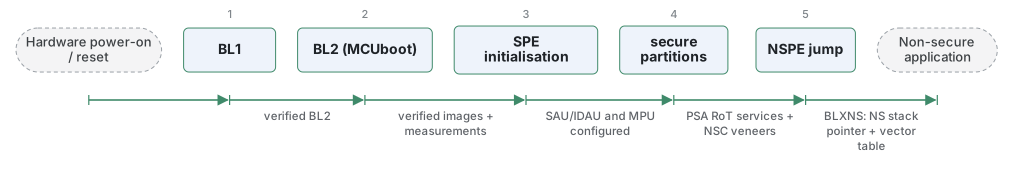
- BL1 -- Optional immutable ROM stage on platforms that need one; verifies and loads BL2.
- BL2 (MCUboot) -- TF-M uses MCUboot as its second-stage loader to verify and, if needed, swap the secure and non-secure images.
- SPE initialisation -- The Secure Processing Environment sets up the SAU/IDAU and MPU so secure memory and peripherals are unreachable from the non-secure side.
- secure partitions -- The partition manager starts the PSA RoT services -- Crypto, Internal Trusted Storage, Protected Storage, Initial Attestation.
- NSPE jump -- Control is transferred to the non-secure application through a non-secure function call.
The boundary here is spatial rather than temporal: after the jump, both sides are running, and the interface between them is the Armv8-M security extension. The non-secure application calls secure services through veneer functions in the Non-Secure Callable region, which the PSA Firmware Framework routes to the right partition. Measurements taken by BL2 are passed up in a shared data region so the attestation service can report what was actually loaded.
The transfer to the non-secure world sets the non-secure stack pointer and vector table from the NSPE image header and branches with BLXNS. Secure state is not torn down -- it stays resident for the life of the device, which is the whole point of the design.
| CWE | CVEs |
|---|---|
| CWE-787 | 1 |
| CWE-121 | 1 |
Detected in its build configuration and source:
- cfi
- encryption
- measured boot
- rollback protection
- secure boot
- signature verification
See Security-Mechanisms for how these are detected and what a detection does and does not prove.
git -C oss-bootloaders submodule update --init type3/trusted-firmware-m
./scripts/analysis/run-tool.sh codeql trusted-firmware-m
See Tools for what each tool applies to.