Repository navigation
Sentinel 1.0

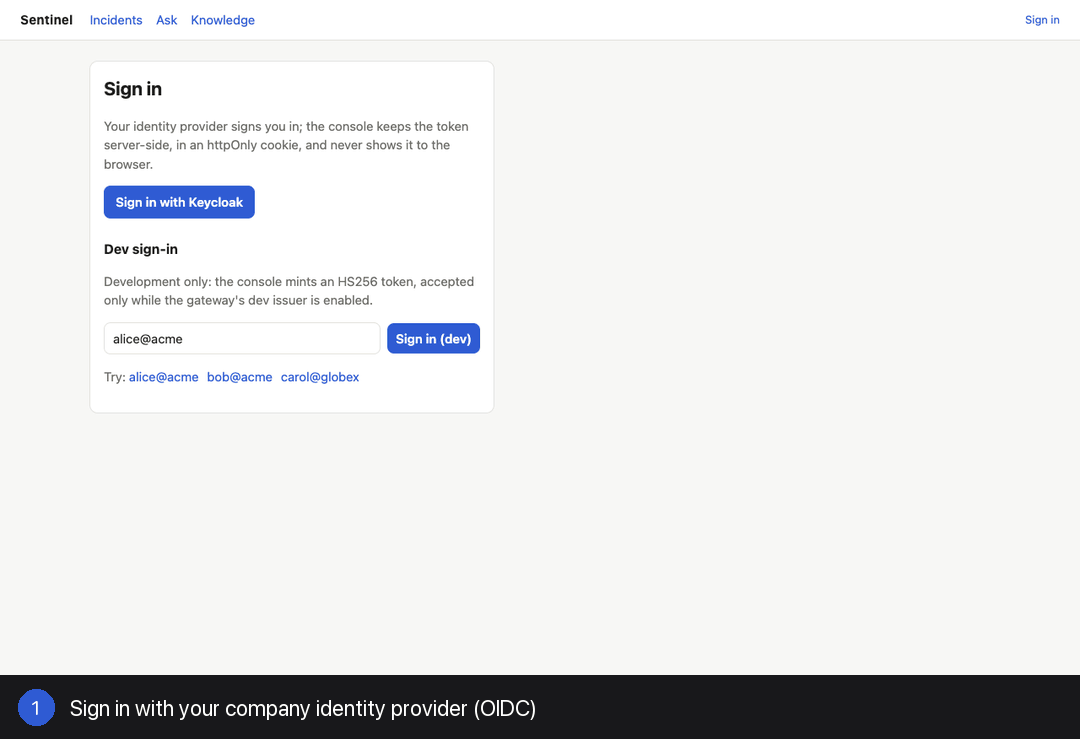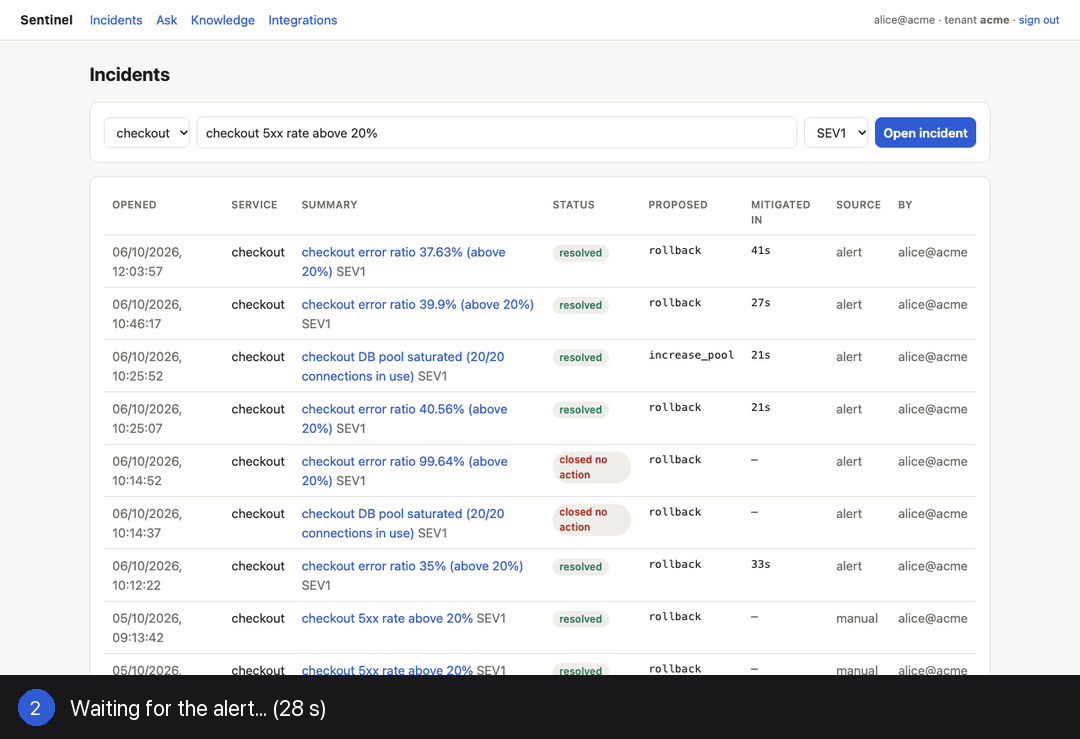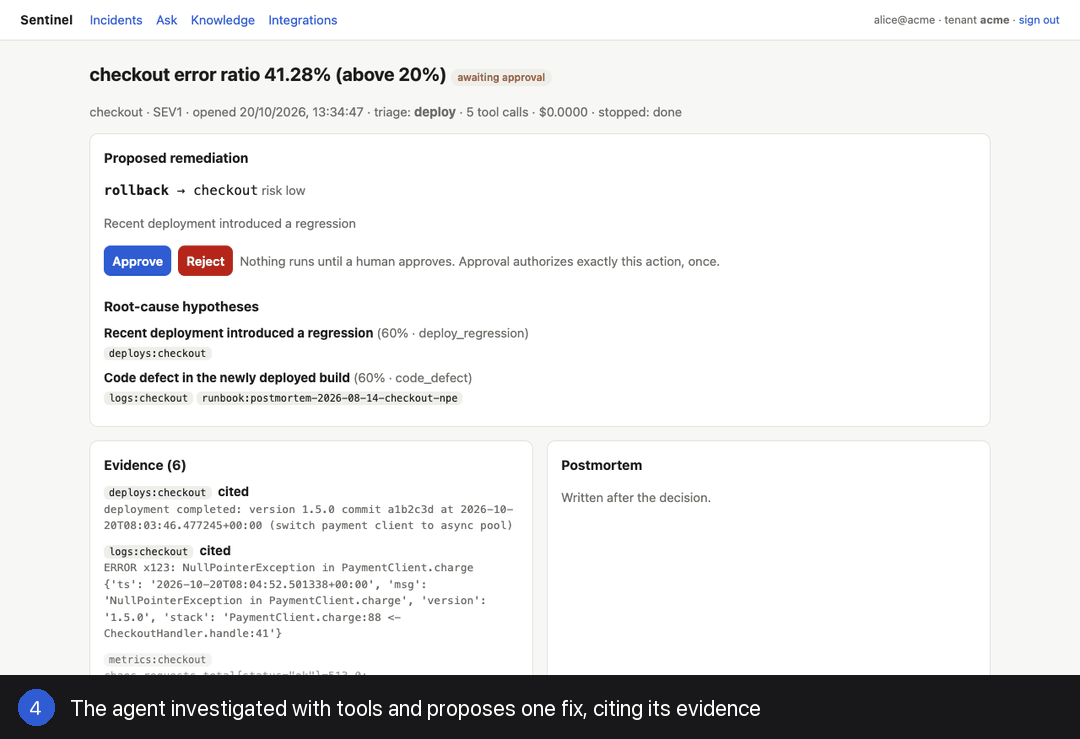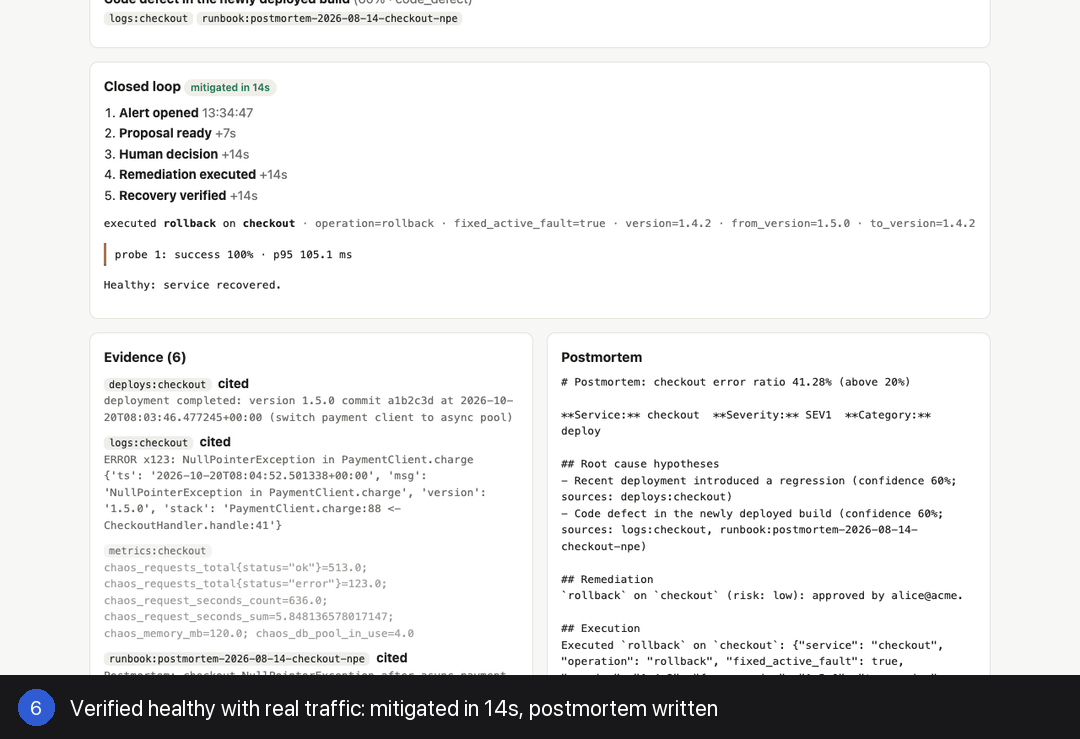
Sentinel 1.0: an incident-response copilot that closes the loop. Alert → investigation → cited proposal → human approval → exactly-once fix → verified recovery.
Highlights
- Closed loop: Alertmanager opens incidents (deduplicated, correlated per service). Approval mints a single-use, 5-minute capability; the remediation adapter executes exactly that action once; real-traffic probes verify recovery. Time to mitigate: 14–41 s in live runs, human approval included.
- Agent: LangGraph with durable Postgres checkpoints, MCP tools and hard budgets; Claude, a local model (Ollama), or rules.
- Safety, measured: on 112 replayed incidents, a local 8B model (gemma4) proposes a harmful fix in 33.9% of incidents; with deterministic guardrails (input sanitization, citation validation, runbook preconditions) 0% reach a human. The rule baseline scores 92.9% correct, 0 harmful. A CI gate fails the build on regression.
- Zero-trust identity: OIDC users (Keycloak); ES256 service tokens minted only by the gateway, verified everywhere via JWKS; every hop authenticated and tenant-bound; row-level security including agent checkpoints.
- Platform: Spring Boot 4 + Spring AI 2 gateway; Kafka ingestion with hybrid retrieval (pgvector + full-text, RRF); Redis rate limits; OpenTelemetry traces; Grafana.
- Deploy: Docker Compose, Helm (hardened pods, NetworkPolicies) verified on kind in CI, Terraform for AWS; multi-arch images on GHCR.
- 212 automated tests, plus a real Kubernetes end-to-end test in CI.
Get started
- User guide · Website · Write-up
- The engineering handbook (architecture, security, operations, and the full build history) is attached as a PDF.
Container images: ghcr.io/abdulmdev/sentinel-<service>:<commit>.