Repository navigation
Releases
1.7.249.dev0 — verified web tabs on stable OpenCode 2.x

Highlights
- Mirror TUI tabs in
oc-box webon OpenCode 2.3.2 and other stable 2.x releases. Previously only three native versions could attempt verification. - Verify the native contracts rather than trusting a version number. The index uses a verified live TUI report or checked saved membership from the same private workspace. Saved membership never supplies current focus.
- Keep browsing available if native contracts change. Use Open native OpenCode Home or
oc-box web --session IDwhen the mirrored list cannot be verified.
Open another host terminal while the TUI is running and select the same workspace:
oc-box web --project ~/devel/demoAn already running owner does not acquire the reporting helper on attach.
Compatible saved membership can work immediately with the updated web launcher;
live selection reports require the helper from a normal owning startup. No
reset, reimport or downgrade is needed. Prerelease and modified native identities
remain ineligible for mirroring. Automatic resume, manual history sync, recovery,
browser attachments, sharing, and authentication retain their existing rules.
Validation and scope
The clean release commit passed source and package CI on Python 3.10 and 3.13,
native V1/V2 coverage, and the current stable native 2.x web-tab integration
job,
all seven distro dependency checks,
and the build-only publication gate
with Twine, isolated vault and tui checks, and exact artifact identity
verification. Local native 2.3.2 checks verified authenticated tab listing,
fresh TUI selection, and unchanged session transcripts.
The exact release source is
74b69e0183140e44a15eb43eb5c9ab091a9075de,
absolute commit count 278, public version 1.7.249.dev0, full identity
1.7.249.dev0+g74b69e0.
This is an experimental development prerelease. Native synthetic checks do not
establish interactive browser/desktop or rootless-Podman acceptance for this
source, or guarantee every future OpenCode 2.x version implements the same API
and saved-state layout. No prior host report was relabeled: the interrupted-history
host reports remain scoped to 5135664, as documented in the
previous release.
The manager and combined browser
validation limitations remain. UI full restore returned zero but its later
verifier refused manifest; intentional root-mode tightening is not proof of
all-entry equality or the sole cause. Portable UI was unarmed, and remaining
three-scope Storage, reviewed ciphertext deletion, source-removal preservation,
final journal/attestation and manager Quit checks remain unaccepted/unperformed.
Human observations remain NOT_AUTOMATICALLY_PASSED.
Only the development channel is updated. LinkedIn automation is skipped.
1.7.248.dev0 — persistent clipboard settings and interrupted-history archival
Highlights
- Remember Ctrl+Y clipboard importing per workspace. Enable once with
--host-clipboard; later native TUI clients inherit the choice. - Keep opt-outs explicit and durable.
--no-host-clipboardsaves disabled, and strict clipboard symlink settings survive disable/re-enable. Useoc-box preferences --host-clipboard on|offto change policy without launching or unlocking. - Archive interrupted history after verified shutdown. On eligible native OpenCode 2.3.x failures, oc-box can make one guarded post-stop archival attempt. Work is not resumed, and an interrupted turn still reports a nonzero result even when archival succeeds.
Usage
# Enable once for this workspace:
oc-box --project ~/devel/demo --host-clipboard

# Later clients inherit it:
oc-box --project ~/devel/demo

# Save disabled without opening a client:
oc-box preferences --project ~/devel/demo --host-clipboard off
Clipboard importing remains off when no choice is saved. Only the dedicated
host Ctrl+Y shortcut reads the clipboard; startup and preference changes never
read it. Saved policy contains booleans, not clipboard contents or helper paths.
Ordinary Ctrl+V/text paste and the independent host-drop preference are unchanged.
--no-host-clipboard-symlinks now saves strict capture for future clients;
--host-clipboard-symlinks explicitly restores ordinary symlink following.
Either startup option requires effective clipboard enable. The independent
preferences --host-clipboard-symlinks on|off setter can prepare that choice even
while importing is disabled. Normal file drops and live sharing remain strict.
Saved enable gracefully skips unavailable terminals/native V1/missing desktop
helpers without clearing the choice. Explicit enable still requires supported
native V2, a direct supported Konsole/Kitty terminal and its desktop helper.
An additional native TUI client can save/use the preference without restarting,
unlocking or refreshing the existing owner. Existing clients never live-toggle.
Fresh restores do not reactivate archived host clipboard policy.
Automatic history archival still requires verified whole-container shutdown,
the same workspace resources, and checked exports and imports. Explicit stop
can cancel recovery. A saved archive is not proof the interrupted work finished;
oc-box does not consume queued input or retry the work.
Validation and scope
The exact clean combined commit passed source and package CI on Python 3.10
and 3.13, native V1/V2 integration and native 2.3.x recovery fixtures,
all seven distro dependency checks,
and the build-only publication gate
with Twine, isolated vault and tui checks, and exact artifact identity validation.
Source: 69a9ab2493754527cead47dcf192795d606d79ef,
absolute commit count 277, public version 1.7.248.dev0, full identity
1.7.248.dev0+g69a9ab2. The original full-history baseline remains 29.
The owner reviewed focused host results for history-fix commit
5135664,
including source, native binary and approved runner hashes:
- Graceful: 31/31 checks passed; all 13 archives verified.
- Stop-cancel: 29/29 checks passed; explicit stop prevented a restart or Reader launch.
- Live transport: 31/31 checks passed; all 13 archives verified without consuming queued work or changing execution markers.
This is an experimental development prerelease, not stable promotion or
security certification. Those host results apply only to 5135664, not the
combined source. No new live desktop/native-composer or rootless-Podman
acceptance is claimed for persistent clipboard policy.
The existing manager limitations remain: UI full restore returned zero but the
later verifier refused manifest; intentional root-mode tightening is not proof
of all-entry equality or the sole cause. Portable UI was unarmed, and remaining
three-scope Storage, reviewed ciphertext deletion, source-removal preservation,
final journal/attestation and manager Quit checks remain unaccepted/unperformed.
Human observations remain NOT_AUTOMATICALLY_PASSED. Combined-browser validation
limitations documented in the 1.7 notes
also remain unchanged.
Stable master, its releases and PyPI files are unchanged. GitHub and PyPI are
the only publication targets for this release; LinkedIn automation is skipped.
1.7.243.dev0 — faster checked sync, clipboard imports and easier optional tooling
1.7.243.dev0 — faster checked sync, clipboard imports and easier optional tooling
Experimental development prerelease from devel, source
a52eadc21c1ba42a97a654adab2cd30738f460ba. This includes the merged performance
and CI corrections, host clipboard work, reorganized documentation and additive
vault/TUI upgrade support. The final tooling-only successor lets the approved
announcement reuse the committed README TUI screenshot; it changes no application
runtime behavior.
Highlights
- Faster guarded history synchronization: one private, pass-local Python
helper replaces repeated source container/Python startup while retaining full
checked exports, per-request stop admission and independent host verification. - Opt-in host clipboard imports: a dedicated Ctrl-Y action imports PNG
clipboard data or supported copied local image/PDF files into the native TUI,
without background polling, model/output triggers or automatic Send. - Add optional tooling independently: new
upgrade --vaultand--tui
options can add verified optional dependencies, together or separately, with
manager ownership, target support and check-only protections. - Clearer OpenCode 2.x documentation: task-oriented guides, legacy separation
and real Textual TUI previews make setup and workspace management easier to find.
Important behavior and upgrade notes
The performance change applies only to the existing guarded post-stop Reader
path. It still inventories and checks every session, including unchanged history;
archive bytes, checkpoints, serial destination changes and fresh native readback
remain authoritative. Transport failure is not automatically restarted/replayed.
Private frames are bounded, one response at a time, and helper reaping/strict EOF
precedes final success. Ordinary live/manual sync and V1 retain prior transports.
The 30-second activity grace and 180-second snapshot budget remain. Client
detachment is not foreground quiescence: a web client can close while its turn
continues. Foreground-active recovery refusals remain intentional; jobs are not
deleted, acknowledged or declared complete. Actual client failures, partial sync
and uncertain cleanup remain nonzero with retry guidance.
Clipboard imports copy rather than move or cut sources. Clipboard-only ordinary
symlink following is the default, with --no-host-clipboard-symlinks for strict
capture; normal drops and live sharing do not inherit that exception. Protected
selected/canonical paths and pinned-descriptor checks remain. Retargeting between
copy and shortcut is a disclosed tradeoff; MIME discovery is not proof of
file-manager provenance. Native 2.x eligibility does not prove future composer
behavior, and unsupported transfer/terminal contracts still refuse.
Existing launchers must first perform their normal owning-manager update before
using newly introduced extra flags. For a compatible GitHub-managed host install:
oc-box upgrade --devel
oc-box upgrade --devel --vault --tui
Python-package installations continue through their verified owning manager.
No root/container refusal or workspace/state downgrade boundary is waived.
Validation and experimental limits
The source includes the fixed-error CI audit correction without weakening its
whitelist and an HTTP deadline test double that models normal response closure.
Required final-source source/package/native/distro and build-only checks are
reviewed before publication; build artifacts alone are not host acceptance.
The operator reported a native 2.3.2 candidate run with 138 unchanged checked
exports, zero pending, 15.2-second copy and successful cleanup/stop messages.
An earlier 136-unchanged-session Reader run took 74.1 seconds. These are separate,
uncontrolled observations with different workloads and unmeasured cache/system
conditions; they are not an overall-shutdown or universal speed claim. The later
report did not supply the final CLI exit status. No changed-import verification
is established by an all-unchanged host run.
Focused source and local synthetic/native tests retain their original source
identities. Clipboard PNG/copied-file/linked-folder reports are scoped operator
observations, not broad desktop/platform acceptance. Existing native 2.3.0 host
recovery failure remains failed/incomplete at 20/29; later informational audits
do not relabel it passed.
Stable 2.3.x history support selects guarded candidate column/metadata contracts,
not proof that unknown future startup is non-executing. These are not complete
SQLite-schema fingerprints. Unknown minor/major identities and unsupported job
or recovery forms retain their documented refusals.
Previously disclosed UI limits remain: full UI restore returned 0 but its later
verifier refused manifest; extraction-root mode tightening from 0755 to 0700
establishes neither all-entry equality nor the sole cause. Portable UI was unarmed;
remaining Storage, reviewed ciphertext deletion, source-removal preservation,
final journal/attestation and manager Quit checks are unaccepted/unperformed.
Human observations retain NOT_AUTOMATICALLY_PASSED. Combined rendered-browser,
real-provider, network-containment and broad host acceptance are not implied.
This is not stable promotion or security certification.
TUI preview
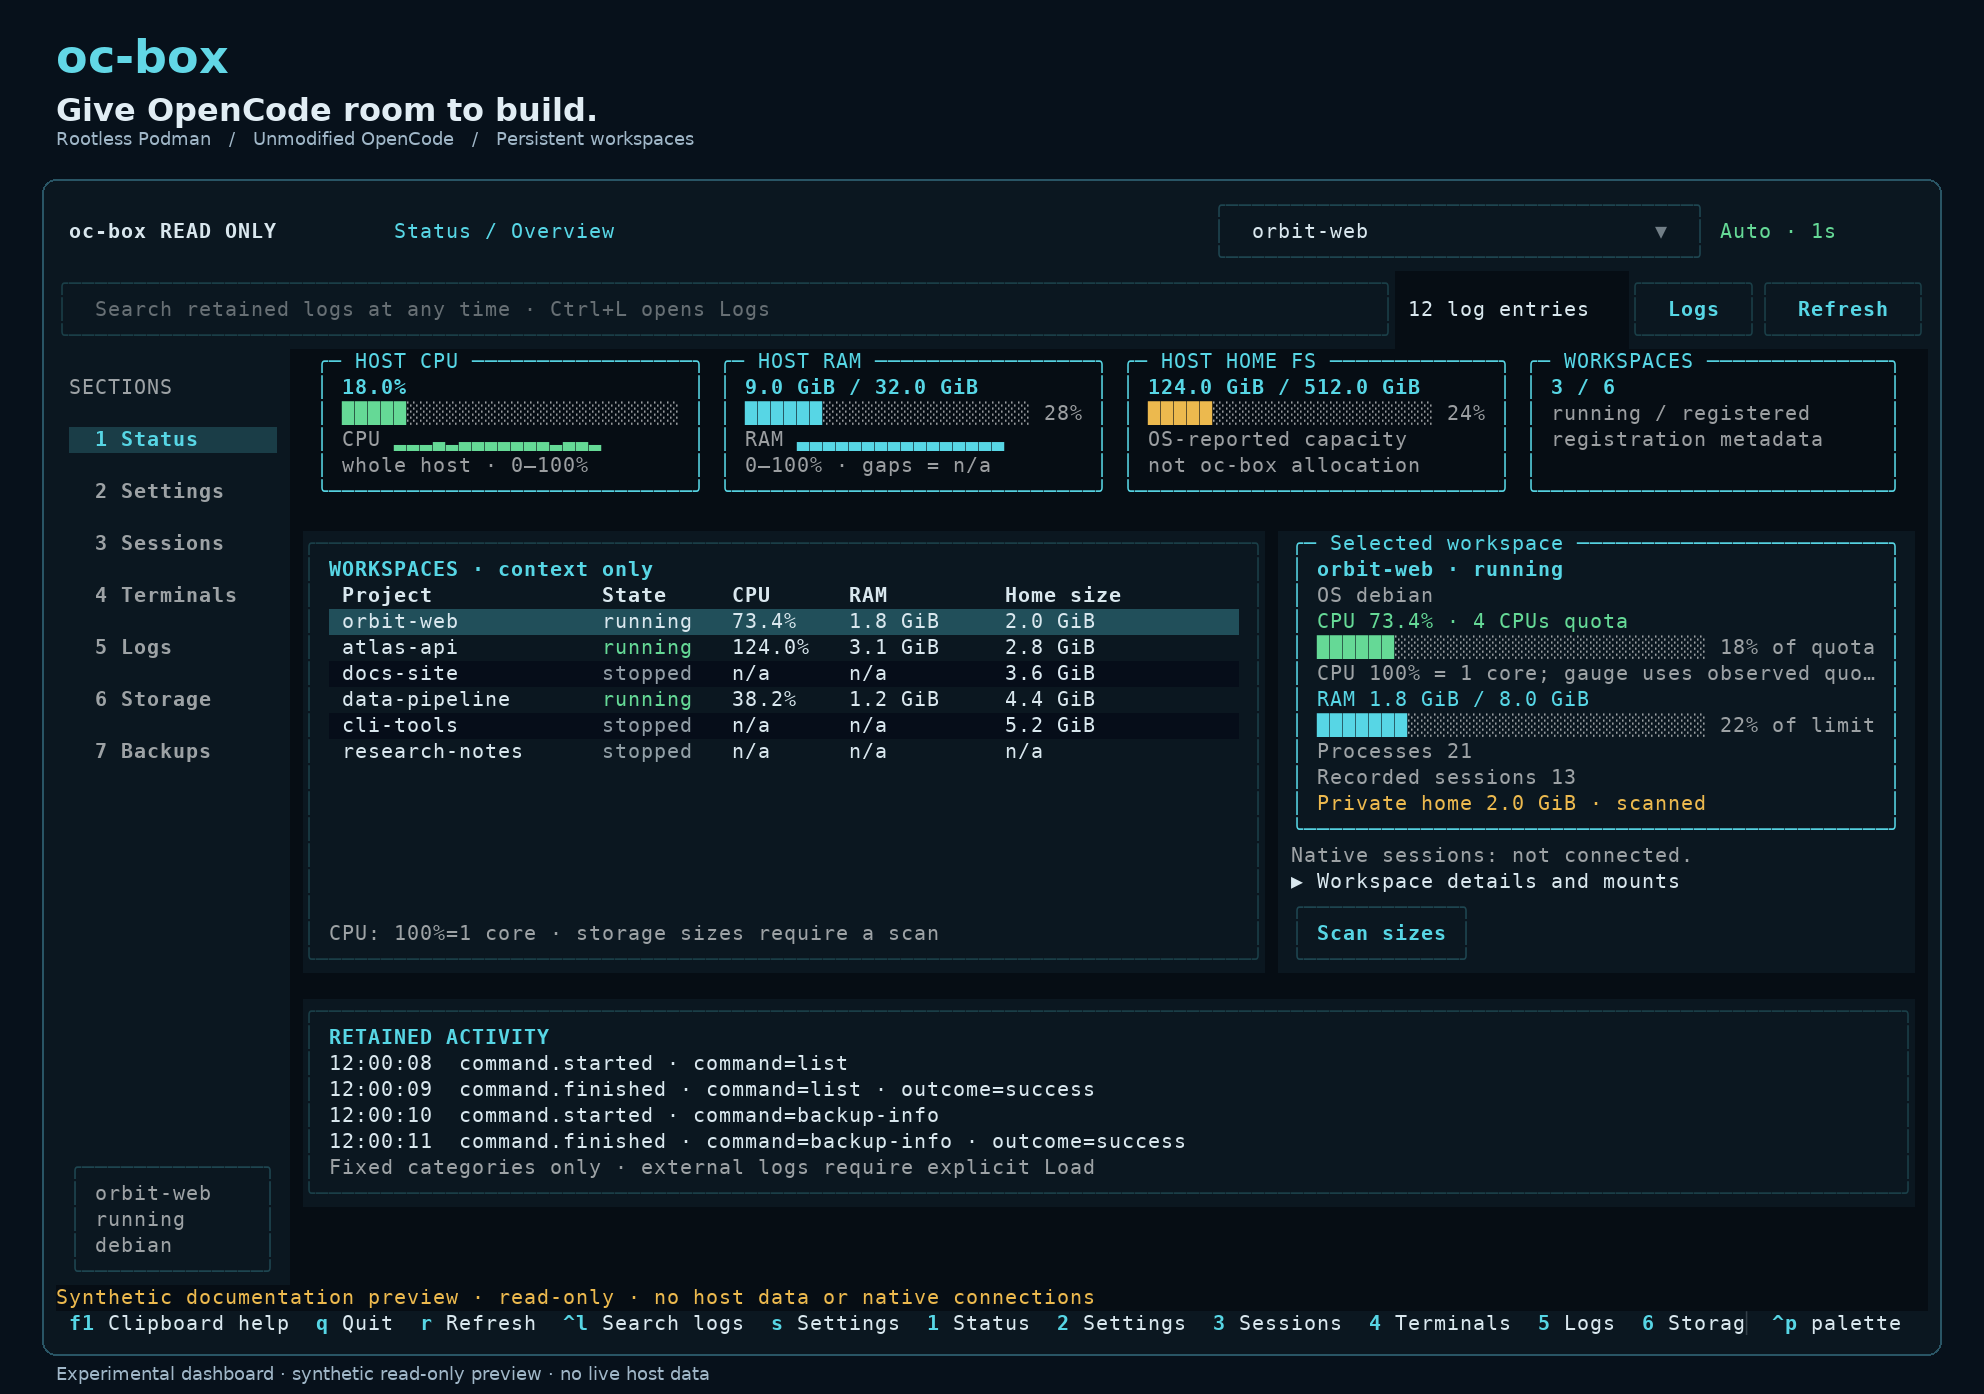
Actual Textual compositor; synthetic read-only preview, no live host data.
LinkedIn highlights
- Faster checked history sync with a private export helper.
- Opt-in clipboard imports for native OpenCode TUI clients.
- Add vault and TUI support independently during upgrades.
LinkedIn post
oc-box 1.7.243.dev0 · development preview — experimental
Give OpenCode room to build.
oc-box runs unmodified OpenCode in persistent rootless-Podman workspaces on Linux, with an optional Textual dashboard for workspace status, sessions, terminals, logs, storage and backup controls.
New in this devel update:
• Faster guarded history sync: one private export helper per snapshot pass, keeping full source checks and independent destination verification.
• Opt-in clipboard imports: bring PNG clipboard data or supported copied image/PDF files into the native TUI with a dedicated host shortcut—no background clipboard polling or automatic Send.
• Easier optional tooling: add vault and TUI dependencies independently during upgrades.
• Reorganized OpenCode 2.x guides and genuine TUI previews.
One operator-reported run copied 138 unchanged sessions in 15.2 seconds; an earlier 136-session run took 74.1 seconds. Different runs, not a controlled benchmark; the 30-second activity grace is unchanged.
Screenshot: actual Textual UI with synthetic read-only data.
Try devel, share feedback, and help shape the next release.
This is a development prerelease, not a stable recommendation.
Release notes: https://github.com/groopcd/oc-box/releases/tag/v1.7.243.dev0
#OpenSource #Linux #OpenCode #Podman #DeveloperTools
1.7.225.dev0 — guarded OpenCode 2.3.x history recovery
1.7.225.dev0 — guarded history recovery across stable OpenCode 2.3 patches
Experimental development prerelease from devel, source
44b1c1442411732c012689202bcb6cd8f9c8befb. Not a stable release or security
certification. Stable master and v1.6.94 remain unchanged.
Highlights
- Recognize stable OpenCode 2.3.x: one shared storage-profile selector handles
canonical stable2.3.Nreleases instead of requiring a new allowlist entry
for every patch. Legacy 2.2.6/2.2.7 remain shell-only. - Handle the real 2.3.1/2.3.2 scheduler change: recognize known
schedule
and newerautomationcolumn layouts, require exactly one, and refuse every
scheduler row before native startup, including terminal/unknown and WAL rows. - Validate newer retained-subagent metadata: optional
outstandinglists
receive bounded, explicit shell/subagent validation. Image, Code Mode, nested,
unknown and malformed forms remain refused rather than silently discarded. - Explain compatibility refusals: unsupported versions warn before the owning
client opens; recognized metadata/API incompatibilities advise checking for an
oc-box update first and updating an older OpenCode when appropriate. Keep data;
never reset or downgrade workspace state to bypass a refusal.
Shutdown behavior
The existing verified whole-container stop, same-resource restart, isolated
unregistered Reader, checked exports/imports, host verification and final cleanup
remain authoritative. Native executable probes must match the captured exact
patch on both sides; a common series does not waive a patch mismatch. Native
2.3.0 cannot consume an automation-layout store through this path.
A raw clean client may return 0 after a live timeout only when the guarded copy
and cleanup succeed. Actual client failures, cancellation, unknown status,
partial/failing sync and uncertain cleanup remain nonzero, with manual-sync
guidance. Interruption and unconfirmed-background-completion warnings remain.
No job is declared complete, deleted, acknowledged or resumed.
The 30-second activity grace is unchanged. This release does not speed up large
history exports, expand unrelated native UI/attachment support, or enable ordinary
manual-sync preparation as an automatic-recovery shortcut.
Validation and limits
- Focused source checks and independent runtime review covered the shared
profile, strict scheduler/job metadata, exact binary matching, failure/cleanup
outcomes and fixed compatibility guidance. - A fresh synthetic native 2.3.2 regression passed: 12 sessions verified, one
Reader, eight source and eight destination automation refusals, preserved
source/destination jobs, claims, queued input and original history, and no
extra provider/shell/plugin execution. Initial fixture failures remain failed
evidence; corrected runs are recorded separately. - The operator subsequently reported a real-workspace pass with this exact
candidate and native 2.3.2: all 136 sessions exported unchanged, zero pending,
successful automatic post-stop fallback and final cleanup, exit 0 without
manual sync. This is user-supplied output, not an independently inspected full
host-fixture gate. It establishes no new changed-archive import verification,
job completion, general lifecycle or performance claim. - CI retains native 2.3.0 and follows the latest stable 2.3 patch, recording its
actual version and binary hash.
Future-patch behavior is not proven solely by matching layouts. Guards check
columns, not all defaults, triggers, indexes or foreign keys; native startup can
change without changing them. Unknown minor/major series, prereleases and
modified identities remain refused. Nonempty outstanding forms have synthetic
metadata coverage, not a separately observed native reproduction.
Historical acceptance and failure evidence retain their exact source/native
identities. The earlier 631d317 host runner remains failed/incomplete at 20/29;
its twelve verified archives and later informational retained-state audit do not
reclassify that run or accept every subsequent source.
Previously disclosed dashboard limits remain: full UI restore returned 0 but the
later verifier refused manifest. The observed extraction-root mode tightening
from 0755 to 0700 does not establish all-entry equality or the sole cause of that
refusal. Portable UI was unarmed; remaining three-scope
Storage, reviewed ciphertext deletion, source-removal preservation, final
journal/attestation and manager Quit checks are unaccepted/unperformed. Human
observations retain NOT_AUTOMATICALLY_PASSED. Offline/native results do not imply
rendered-browser/host-gesture, real-provider, network-containment or comprehensive
host acceptance. This prerelease does not promote stable or waive those gates.
Distribution
GitHub development prerelease and matching oc-box==1.7.225.dev0 package. Exact
publishing-workflow wheel, sdist, validated identity and checksums are attached
after successful publication. No LinkedIn announcement is approved.
1.7.224.dev0 — verified shutdown history-sync outcomes
1.7.224.dev0 — verified shutdown history-sync outcomes
Experimental development prerelease from devel; not a stable release or a
security certification. Source: cb1e299b34835fcc2468913967af1bcb8aa0423a.
Highlights
- Use the final synchronization result: a clean native client may now exit
successfully after a live-readiness timeout only when the existing guarded
post-stop archive copy, native verification, recovery cleanup and final
container stop all succeed. - Keep real failures actionable: original client errors and cancellation,
unknown client status, partial or failed synchronization and uncertain cleanup
remain nonzero. The guidance to retryoc-box syncremains on synchronization
or cleanup failure. - Separate waiting from copying: progress labels distinguish the live
activity wait from archive synchronization. Aggregate-only feedback reports
source mode and exported/unchanged/updated/pending counts without identifiers,
transcript text, commands or credential values.
Behavior and safety
The initial 30-second live-work grace is unchanged. This is not a native
export/import timeout, and the change does not clear native job records,
declare background work complete, resume pending work, add client autoaccept or
speed up full-history exports.
The existing verified-stop Reader and the same checked archival backend used by
manual sync remain in place. There is no recursive CLI call or extra ordinary
runtime/configuration/credential preparation in the fallback. The explicit
interrupted-work and unconfirmed-background-completion warning remains.
Validation and experimental limits
Eighteen focused local regression methods and independent code/documentation
review covered the changed result, failure-guidance and cleanup policy. Release
CI and the guarded build-only workflow supply their own source, native and
package checks; their results are attached to this exact source, not a new
external-host acceptance.
The new exit-outcome policy has no clean formal external-host acceptance.
The historical 631d317 host runner remains failed/incomplete at 20/29 checks
because of its import PATH versus native session import PATH observer
mismatch. It recorded one guarded recovery and twelve native-verified archives;
a separate informational audit confirmed the retained source and original
destination logical table hashes. Missing original in-memory plugin, schema,
export/digest, warning/output and process baselines remain unavailable. Those
observations and the later 65bae6b successful fallback observation are not
reclassified as acceptance of this source.
Previously disclosed dashboard limits remain: full UI restore returned zero but
its later verifier refused manifest; portable UI was unarmed; remaining
three-scope Storage, reviewed ciphertext deletion, source-removal preservation,
final journal/attestation and manager Quit checks are unaccepted/unperformed.
Manual observations retain NOT_AUTOMATICALLY_PASSED. Rendered browser behavior
and actual host-gesture coverage are not implied by offline/native probes.
Historical 42-check history/readiness, 12/six recovery, vault, sharing and CLI
lifecycle reports retain their original source/native identities.
This prerelease does not promote master or stable, waive the outstanding
formal-acceptance work, or certify every timeout/project. Raw private fixture
evidence is not published.
Distribution
GitHub development prerelease and matching oc-box==1.7.224.dev0 package.
The publishing workflow's exact wheel, sdist, validated identity and checksums
are attached after successful publication. No LinkedIn announcement is approved.
1.6.101 — easier upgrades and refreshed getting-started guides
oc-box 1.6.101 — easier upgrades and refreshed getting-started guides
Stable release from master, source
43dc12bf8cf32c76ea1c9416aeaaf1d3bb6889f0
(1.6.101+g43dc12b, full-history commit count 130).
Highlights
- Add optional tooling during upgrades.
upgrade --vaultandupgrade --tui
are independent, additive dependency requests. Use either or both when
selecting a supporting development release, including from stable:
oc-box upgrade --devel --vault --tui. - Enable extras without reinstalling through curl. A selected release can
gain missing optional dependencies even when it is already installed. Requests
preserve existing supported extras, verify the installation owner and target
capabilities, and retain nonmutating--checkbehavior. - A clearer first-install experience. The README and task-oriented guides
now lead with the GitHub installation path, alongside illustrated development
TUI documentation and a separate retained OpenCode 1.x legacy guide. - Publishing and CI maintenance. Temporary Ubuntu CI configuration uses the
working HTTPS Azure mirror with IPv4, retaining certificate, archive-signature
and freshness checks. A per-release announcement opt-out prevents a duplicate
stable social post for a rollout already covered by its development release.
Upgrade
Existing channel-aware GitHub installations can select stable with:
oc-box upgrade --stableAfter updating to this launcher, add vault dependencies on the saved channel:
oc-box upgrade --vaultTo select development and add either or both independent extras:
oc-box upgrade --devel --vault
oc-box upgrade --devel --tui
oc-box upgrade --devel --vault --tui
Older launchers must perform their normal owning-manager update before accepting
the new flags. Recognized uv tool and pipx installations delegate to that
verified owner, not to the GitHub installer. Ambiguous source/plain-pip/shared
installations retain explicit manual guidance and all root/container refusals.
These flags install optional dependencies only: they do not initialize or unlock
a vault, change workspace credential policy, start a workspace or launch the UI.
Add --check for a nonmutating capability preview.
Stable/development boundary
The optional dashboard and other 1.7 development runtime features are not
promoted into stable. This stable package still provides the vault extra only;
an explicit TUI request against an unsupported stable target refuses. An
inherited TUI preference can survive a stable interval for a later return to
development.
Explicit channel switches can replace the launcher with an older release.
Launcher replacement does not roll back workspace/session state.
Validation and scope
- Source/package checks on Python 3.10 and 3.13, retained native OpenCode
1.19.5/2.2.6 integration, and the separate native 2.3.0 V2-only profile:
exact-source CI. - All seven supported distro package-provider checks:
distro matrix. - Clean-source wheel/sdist, optional-vault installation, source-identity,
checksum and build-only publication validation:
build-only gate. - Focused upgrade regressions include same-release additions, independent
vault/TUI requests, capability previews, ownership and downgrade refusals,
receipt verification, real offline Git/immutable installation and uv/pip
fixtures. The unavailable local native pipx fixture remains a recorded skip,
not a fabricated live pass.
Changes since the prior stable v1.6.94 are limited to upgrade selection/tooling,
guidance, documentation and CI/publication maintenance. Workspace execution,
history/recovery, credential delivery, backup/restore and dependency-provider
mappings are unchanged. Existing source-scoped host evidence retains its
original identity; no new Podman lifecycle, interactive UI, real-provider or
security-certification claim is made.
The release assets contain the publishing workflow's exact wheel and sdist,
validated-identity.json and SHA256SUMS; the matching packages are published
to the existing oc-box PyPI project.
oc-box v1.7.223.dev0 — combined development update
Experimental development update
This prerelease combines the card-dashboard, retained-subagent history-recovery,
and native/web attachment work on devel. Stable v1.6.94 / master remain
unchanged. This is not stable UI acceptance or a security certification.
What changed
- Native TUI image/PDF drops, enabled by default per workspace. Supported
direct Konsole/Kitty clients can import qualifying pasted image/PDF paths
without model tool calls or per-file confirmation.--no-host-dropsaves an
opt-out;--host-dropsaves enabled and strictly requires compatibility.
oc-box preferences --host-drop offchanges policy without opening another
client. Existing clients keep their current setting. - Correct web conversation and all open TUI tabs. A first-party tabstrip
surrounds one unmodified native iframe. Fresh cooperative TUI reports provide
the exact owning-TUI conversation and ordered open roots, including idle tabs.
web --session IDwins explicitly. Children retain their exact route and
native read-only behavior; root highlighting is separate. Older running owners
require explicit selection until a subsequent normal owning startup loads the
helper; attach never refreshes configuration or credentials. - Optional browser attachments.
oc-box web --attachmentsadds trusted File
drops and a chooser to that same native view. The native composer owns draft
handling and Send. No prompt is submitted automatically. - Responsive card dashboard. Navy/cyan host resource cards, workspace
context/inspector, inline session-only settings, compact switches and larger
clear-control hit targets retain the existing explicit operations, clipboard
and private-input boundaries. No new resource-control RPCs or telemetry. - Native 2.3.0 retained-subagent history fallback. The live owner still
refuses pending jobs. Checked persisted history may be recovered only after
verified shutdown through the existing guarded reader. The original warning
and nonzero result remain; jobs are not resumed, acknowledged or declared
completed.
Important disclosure and compatibility notes
A qualifying complete image/PDF pathname paste anywhere in an
importing-enabled native TUI authorizes capture, not just a physical drag into
the composer. Disable importing when that policy is inappropriate. The separate
confirmation-based attach --broker workflow remains available.
Konsole remains pathname-paste-only, with unchanged child output and no OSC 72
probes. Only the known Kitty profile reserves its audited structured-drop traffic.
TUI limits are 8 MiB/file, four files/16 MiB per batch and 32 files/64 MiB per
client. Browser limits are 20 MiB/file, eight files/40 MiB per drop.
PNG/JPEG/GIF/WebP/PDF are supported within their respective guards; DOCX
conversion is not provided. Model support varies.
Staging, native/browser history, provider processing, copies and backups can
retain disclosed bytes. Cleanup is best-effort, not recall or per-session
filesystem isolation. Mainline OpenCode remains unmodified; the native TUI,
server, tools, MCPs and plugins remain container-side.
Validation and known limitations
- Application runtime bytes match the fully green
9c614f7integration:
Python 3.10/3.13 source/package CI, native V1/V2 and 2.3.0 history checks, and
all seven distro jobs. The full local matrix ran 2,405 cases per interpreter
without failures (six skips on 3.10, three on 3.13); eight focused native
TUI/helper/web checks passed across unmodified 2.2.6/2.3.0. - The final combined rendered-browser gate remains incomplete. Earlier
explicit-selection Chromium checks passed 69 checks per native version on
eff0c60; later real-helper attempts established automatic non-first owner
selection and four actual ordered roots but remained partial. A subsequent
private PTY/watchdog timeout yielded no durable phase results. No final browser
pass or unforced cleanup is inferred from that attempt, and old results are
not promoted to this release. - Historical dashboard restore acceptance is still incomplete: UI full
restore returned 0, but its later integrity verifier refusedmanifest.
Portable UI was unarmed; remaining three-scope Storage, reviewed ciphertext
deletion, source-removal/preservation, final journal/attestation and manager
Quit checks remain unperformed or unaccepted. - No new physical Konsole/Spectacle/Kitty gesture, rootless-Podman lifecycle,
real-provider, comprehensive fault/race or security acceptance is claimed.
Earlier host reports retain their original source identities and scopes.
See the combined release notes and limitations
and command reference.
Upgrade
After publication completes, existing channel-aware installations can use:
oc-box upgrade --develGitHub and Python-package installation owners remain distinct. No workspace
reset, history reimport or credential-policy change is required. Running clients
and existing host installations are not live-updated by publishing this release.
Source identity
- Tag / public package:
v1.7.223.dev0/1.7.223.dev0 - Full CLI/resource identity:
1.7.223.dev0+g65bae6b - Commit:
65bae6bc1524557b818243a08212ae1f59884f4b - Absolute commit count:
252; original baseline:29 - Channel: development (
devel), not stable
Only the guarded publishing workflow's validated wheel/sdist, identity and
checksums are release artifacts. Development publication does not authorize a
LinkedIn post; any automatically generated announcement is preview-only.
LinkedIn highlights
- A fresh TUI 2.0 experience
- Screenshots, PDFs and shared web tabs
- Smoother workflows. Better history recovery.
LinkedIn post
oc-box 1.7.223.dev0 · development preview — experimental
Meet the new oc-box TUI 2.0: a fresh look, a clearer workspace, and less friction between you and your next idea.
This development update brings together:
• A redesigned TUI 2.0 dashboard with responsive cards, a workspace overview, and simpler everyday controls.
• New ways to bring screenshots, images, and PDFs into your native TUI and web workflows—so sharing context takes less effort.
• Your open TUI conversations in the web interface, with easier switching and a clearer view of where you’re working.
• More control over native file importing, with a saved setting for each workspace.
• Improved conversation-history recovery, helping you pick up where you left off.
• Smoother navigation, better draft continuity, and a collection of everyday usability fixes.
All around unmodified OpenCode, with your tools and integrations running together in a rootless Podman workspace.
Less context switching. More flow.
Explore the new interface and tell us what you think.
This is a development prerelease, not a stable recommendation.
Release notes: https://github.com/groopcd/oc-box/releases/tag/v1.7.223.dev0
#OpenSource #Linux #DeveloperTools #OpenCode #Podman
oc-box 1.7.173.dev0 — integrated development preview
oc-box 1.7.173.dev0 — integrated development preview
Successor to the incomplete v1.7.172.dev0 publication. This source fixes the newly exposed dashboard shutdown race and adds deterministic coverage. Version 172 never reached PyPI; its tag and failure evidence are unchanged.
Experimental development release, not stable promotion. This integrates the completed development TUI work, native image-preview opt-in, and the reviewed history-sync/native-UI continuity changes. Stable v1.6.94 and master are not advanced.
Highlights
- Workspace management: the optional seven-tab Textual dashboard brings Status, Settings, Sessions, Terminals, Logs, Storage and Backup/restore together, with source-aware navigation, adjustable monitoring, debounced search, clear-field controls and viewport-preserving refresh.
- Private backup workflows: workspace and native session-history create/inspect/restore flows stay in the dashboard, using masked nonselectable private editing and a separate pinned-runtime controlling PTY, with bounded progress, reviews, cancellation and real cleanup acknowledgement. Encrypted session-tree restores use fresh IDs and cleared privileges.
- Native terminal continuity: container-local CLI preferences survive V2 refreshes; closed tabs retain history without reopening automatically. Closing every tab can leave native home unbound, rather than fabricate a new conversation. Native stores tab membership/order, not the exact focused tab.
- Owner-lifetime image previews:
--image-previewenables supported native V2 prompt/transcript previews for the owning TUI generation and additional TUI clients through a minimal ephemeral overlay, without changing saved preferences or host settings. - Quieter sync and safe acceleration: one updating elapsed-time spinner replaces periodic duplicate lines. Quiet-eligible native 2.3.0 manual sync reuses one private source runtime, retaining checked exports, serial destination replacement, independent fresh verification and incremental success checkpoints.
- Development-only capabilities retained: temporary consent-based live host-file/text/image tools, experimental embedded native session terminals, explicit clipboard shortcuts, bounded activity/container-log views, scoped storage management and native encrypted session-tree backups.
Performance and safety boundaries
One paired native synthetic comparison with 109 unchanged sessions took 46.448 seconds → 19.052 seconds, about 59% less time / 2.44×. All 109 exports were checked, checkpoint bytes stayed unchanged, and source service starts fell from 110 to one. The five-session comparison saved 9.3% on first import, 37.8% unchanged and 23.5% with one changed session.
Those are source-qualified quiet-store measurements, not general production, startup or exit-sync guarantees. Known jobs/schedules and unsupported sources retain the slower path. No destination writer reuse or concurrent database mutation was enabled.
The original 30-second live-readiness timeout is not claimed fixed. Its checks and failure/interruption semantics remain; new fixed-category notices distinguish why automatic persisted-history recovery was skipped. Native job cleanup is not repaired or bypassed.
Validation and experimental limitations
- Exact final-source post-push devel CI passed: 2,028-test suites on Python 3.10/3.13 (six/five environment or stdlib skips respectively), retained native V1/V2 integration and package checks. The independent integration-branch CI also passed. All seven devel distro jobs passed.
- The guarded build-only gate passed with publish/LinkedIn skipped. Its exact source identity, 51 wheel runtime files and 225 sdist source files were checked. Clean local wheel/sdist, Twine, isolated TUI/vault checks and independent integration/copy/race-fix reviews passed.
- Queued workspace/session row messages are now ignored after app shutdown or table detachment. A deterministic four-case post-prune message matrix verifies dispatch without selection/render mutation. The validation matrix preserves mouse clicks and all original checks while disabling only its test button's animation timer, with proof that all 16 Apply messages arrived.
- Local native 2.3.0 history sync/recovery, sharing, X-close/reopen, real saved preferences and image-overlay lifetime checks retain their earlier
90b8baasource identity. Their corresponding native-launch/sync/preference/sharing modules are unchanged; the later production change is confined to the optional manager's two row-event guards. This is component evidence, not an old exact-source pass for this whole successor. - The incomplete
v1.7.172.dev0pipeline stopped before distribution build or PyPI upload. Its publication failure, post-push failure, immutable tag and source remain retained. The earlier stale-fixture native CI failure also remains failed evidence. No failure was waived, tag rewritten or production isolation flag removed.
These are source/package and synthetic local-native results, not a new external-host Podman/UI acceptance or a security certification. The earlier UI full-restore integrity verifier's manifest refusal and unperformed portable UI/Storage/removal/final-attestation/Quit checks keep their original identities and remain unaccepted; no retained fixture was resumed to manufacture a pass.
The private dashboard editor is deliberately inside the transient secret-memory trust boundary. It is not a guarantee of erasure or protection from a same-user debugger, swap or recording. Actual desktop notification delivery and terminal image rendering were not certified by the synthetic preference tests.
See the complete 1.7 notes, TUI guide, CLI reference, and testing scope.
Upgrade
On the host, as your regular user:
oc-box upgrade --devel
oc-box --version
GitHub installations enabling dashboard dependencies for the first time should use the channel-aware bootstrap:
curl -fsSL --proto '=https' --tlsv1.2 https://raw.githubusercontent.com/groopcd/oc-box/master/install.sh | sh -s -- --devel --with-tui --with-vaultOmit --with-vault if unused. No workspace reset or history reimport is needed. A launcher downgrade is not a workspace/session-state rollback.
Source identity
- Full identity:
1.7.173.dev0+gbd5a573 - Source:
bd5a5733a2aa79d8ea1526fc9a9eec4a20b4eb99 - Full-history count:
202; retained baseline:29 - Channel/tag:
devel/v1.7.173.dev0
LinkedIn highlights
- Seven-tab dashboard: sessions, terminals, logs and scoped storage.
- Private in-dashboard backups and fresh-ID encrypted session restores.
- Native UI continuity, opt-in images, live sharing and guarded manual sync.
LinkedIn post draft — awaiting owner approval
The development publisher creates a preview only. This text/card will not be sent to LinkedIn until reviewed and explicitly approved.
Complete announcement preview text
oc-box 1.7.173.dev0 · development preview — experimental
OpenCode workspaces in rootless Podman. Here’s what devel adds beyond stable 1.6.94:
• Optional Textual dashboard, separate from OpenCode’s native TUI: Status, Settings, Sessions, Terminals, Logs, Storage and Backup/restore. Resource meters, histories, themes and session-only preferences; custom 1–60s polling, debounced search, clear fields and scroll-preserving refresh.
• Source-aware V2 session management: host/workspace catalogs, private favorites, archive/unarchive, reviewed deletion and clearer loading/cancellation notices. Archived roots stay synchronized without automatic reopening. Scoped storage removal retains project files and host history; typed reviews remain for destructive actions.
• Embedded native session terminals with resize/detach, selection/screen-copy and in-app paste shortcuts, plus bounded activity logs and searchable opt-in container logs. The embedded emulator remains experimental.
• Encrypted backups inside the dashboard: create, inspect and restore through masked private editing backed by the pinned runtime’s PTY, with stage/elapsed progress and cancellation. The UI also adds encrypted session-tree backups, restoring with fresh IDs and cleared privileges. Full/portable workspace backups gain dashboard workflows—not a new CLI backup format.
• Temporary live host-file tools: explicitly share a file/folder for directory listing, UTF-8 text and image reads, without a mount, project copy or workspace restart. Read-only access is still disclosure; disconnect cannot recall data already read.
• Native OpenCode TUI continuity: preserve container-local settings and open-tab membership; closed tabs stay closed without deleting history, and closing the last can leave native home on relaunch. Owner-lifetime --image-preview enables supported native prompt/transcript previews without changing saved preferences.
• Quieter CLI progress and eligible manual-sync acceleration: a single-line elapsed-time spinner, clearer recovery-skip reasons and private source-runtime reuse.
This is a development prerelease,...
oc-box 1.7.172.dev0 — integrated development preview
Superseded — use v1.7.173.dev0. Its exact GitHub/PyPI distributions are now published and anonymously byte-verified. Version 172 never reached PyPI; its immutable source/tag and the failed checks below remain preserved. The successor remains experimental, not stable UI promotion.
Publication incomplete — do not treat this as the completed combined release.
The release-event build stopped at dashboard regression tests before distribution build or PyPI upload. The post-push Python 3.10 run also reported a late dashboard event during teardown. Earlier clean-source CI passed, but these new failures are under investigation; they are not waived or relabeled as passes. No PyPI publication or LinkedIn announcement occurred. The immutable tag/source and original failure evidence are retained.Failed runs: publication build, post-push source CI.
oc-box 1.7.172.dev0 — integrated development preview
Experimental development release, not stable promotion. This integrates the completed development TUI work, native image-preview opt-in, and the reviewed history-sync/native-UI continuity changes. Stable v1.6.94 and master are not advanced.
Highlights
- Workspace management: the optional seven-tab Textual dashboard brings Status, Settings, Sessions, Terminals, Logs, Storage and Backup/restore together, with source-aware navigation, adjustable monitoring, debounced search, clear-field controls and viewport-preserving refresh.
- Private backup workflows: workspace and native session-history create/inspect/restore flows stay in the dashboard, using masked nonselectable private editing and a separate pinned-runtime controlling PTY, with bounded progress, reviews, cancellation and real cleanup acknowledgement. Encrypted session-tree restores use fresh IDs and cleared privileges.
- Native terminal continuity: container-local CLI preferences survive V2 refreshes; closed tabs retain history without reopening automatically. Closing every tab can leave native home unbound, rather than fabricate a new conversation. Native stores tab membership/order, not the exact focused tab.
- Owner-lifetime image previews:
--image-previewenables supported native V2 prompt/transcript previews for the owning TUI generation and additional TUI clients through a minimal ephemeral overlay, without changing saved preferences or host settings. - Quieter sync and safe acceleration: one updating elapsed-time spinner replaces periodic duplicate lines. Quiet-eligible native 2.3.0 manual sync reuses one private source runtime, retaining checked exports, serial destination replacement, independent fresh verification and incremental success checkpoints.
- Development-only capabilities retained: temporary consent-based live host-file/text/image tools, experimental embedded native session terminals, explicit clipboard shortcuts, bounded activity/container-log views, scoped storage management and native encrypted session-tree backups.
Performance and safety boundaries
One paired native synthetic comparison with 109 unchanged sessions took 46.448 seconds → 19.052 seconds, about 59% less time / 2.44×. All 109 exports were checked, checkpoint bytes stayed unchanged, and source service starts fell from 110 to one. The five-session comparison saved 9.3% on first import, 37.8% unchanged and 23.5% with one changed session.
Those are source-qualified quiet-store measurements, not general production, startup or exit-sync guarantees. Known jobs/schedules and unsupported sources retain the slower path. No destination writer reuse or concurrent database mutation was enabled.
The original 30-second live-readiness timeout is not claimed fixed. Its checks and failure/interruption semantics remain; new fixed-category notices distinguish why automatic persisted-history recovery was skipped. Native job cleanup is not repaired or bypassed.
Validation and experimental limitations
- Final-source Python 3.10/3.13, retained native V1/V2 and package CI passed, as did all seven distro jobs.
- The guarded build-only gate passed with publication and LinkedIn jobs skipped. Its exact source identity, 51 wheel runtime files and 225 sdist source files were checked. Clean local wheel/sdist, Twine, isolated TUI/vault checks and independent integration/copy reviews passed.
- Both 2,027-test local suites passed (Python 3.10: six environment/stdlib skips; Python 3.13: three environment skips). Native 2.3.0 history sync/recovery, sharing, X-close/reopen, real saved preferences and image-overlay lifetime checks passed on the byte-identical production runtime at
90b8baa. - The only successor change is a strict native fixture-envelope correction requiring the production
python3 -I -S -cbridge. The corrected transport and all six downstream scripts passed locally and in final-source CI. The earlier failed90b8baaCI remains failed evidence, not a pass. No production safeguard was relaxed.
These are source/package and synthetic local-native results, not a new external-host Podman/UI acceptance or a security certification. The earlier UI full-restore integrity verifier's manifest refusal and unperformed portable UI/Storage/removal/final-attestation/Quit checks keep their original identities and remain unaccepted; no retained fixture was resumed to manufacture a pass.
The private dashboard editor is deliberately inside the transient secret-memory trust boundary. It is not a guarantee of erasure or protection from a same-user debugger, swap or recording. Actual desktop notification delivery and terminal image rendering were not certified by the synthetic preference tests.
See the complete 1.7 notes, TUI guide, CLI reference, and testing scope.
Upgrade
On the host, as your regular user:
oc-box upgrade --devel
oc-box --version
GitHub installations enabling dashboard dependencies for the first time should use the channel-aware bootstrap:
curl -fsSL --proto '=https' --tlsv1.2 https://raw.githubusercontent.com/groopcd/oc-box/master/install.sh | sh -s -- --devel --with-tui --with-vaultOmit --with-vault if unused. No workspace reset or history reimport is needed. A launcher downgrade is not a workspace/session-state rollback.
Source identity
- Full identity:
1.7.172.dev0+gc88d800 - Source:
c88d800c5512c8b371c3717d24ec406681f2c260 - Full-history count:
201; retained baseline:29 - Channel/tag:
devel/v1.7.172.dev0
LinkedIn highlights
- Seven-tab dashboard: sessions, terminals, logs and scoped storage.
- Private in-dashboard backups and fresh-ID encrypted session restores.
- Native UI continuity, opt-in images, live sharing and guarded manual sync.
LinkedIn post draft — awaiting owner approval
The development publisher creates a preview only. This text/card will not be sent to LinkedIn until reviewed and explicitly approved.
Complete announcement preview text
oc-box 1.7.172.dev0 · development preview — experimental
OpenCode workspaces in rootless Podman. Here’s what devel adds beyond stable 1.6.94:
• Optional Textual dashboard, separate from OpenCode’s native TUI: Status, Settings, Sessions, Terminals, Logs, Storage and Backup/restore. Resource meters, histories, themes and session-only preferences; custom 1–60s polling, debounced search, clear fields and scroll-preserving refresh.
• Source-aware V2 session management: host/workspace catalogs, private favorites, archive/unarchive, reviewed deletion and clearer loading/cancellation notices. Archived roots stay synchronized without automatic reopening. Scoped storage removal retains project files and host history; typed reviews remain for destructive actions.
• Embedded native session terminals with resize/detach, selection/screen-copy and in-app paste shortcuts, plus bounded activity logs and searchable opt-in container logs. The embedded emulator remains experimental.
• Encrypted backups inside the dashboard: create, inspect and restore through masked private editing backed by the pinned runtime’s PTY, with stage/elapsed progress and cancellation. The UI also adds encrypted session-tree backups, restoring with fresh IDs and cleared privileges. Full/portable workspace backups gain dashboard workflows—not a new CLI backup format.
• Temporary live host-file tools: explicitly share a file/folder for directory listing, UTF-8 text and image reads, without a mount, project copy or workspace restart. Read-only access is still disclosure; disconnect cannot recall data already read.
• Native OpenCode TUI continuity: preserve container-local settings and open-tab membership; closed tabs stay closed without deleting history, and closing the last can leave native home on relaunch. Owner-lifetime --image-preview enables supported native prompt/transcript previews without changing saved preferences.
• Quieter CLI progress and eligible manual-sync acceleration: a single-line elapsed-time spinner, clearer recovery-skip reasons and private source-runtime reuse. One quiet native-2.3.0 synthetic test with 109 unchanged se...
oc-box 1.7.117.dev0 — OpenCode 2.3.0 history recovery
OpenCode 2.3.0 exit-history recovery backport
This experimental development prerelease brings the audited OpenCode 2.3.0 persisted-history recovery extension from master to devel. It does not update the stable release.
- Enables the existing guarded post-stop recovery path for exact native 2.3.0, alongside 2.2.6 and 2.2.7. Unaudited versions still fail closed.
- Uses one shared exact-version allowlist for recovery eligibility and the isolated reader.
- Retains the original live timeout, nonzero exit and interrupted-work warning. This saves checked persisted history; it does not repair/delete native jobs, resume work or refresh credentials.
- Ports the focused guard regressions and ownership-safe native fixture from
328f83e/7f441b8. No unrelated stable runtime, host-fixture, CI-orchestration or dashboard changes are merged.
Validation and limitations
Local validation was deliberately focused: 68 guard/process tests and the unmodified OpenCode 2.3.0 native recovery fixture passed. The native fixture reproduced the held-shell timeout, used a verified local producer-stop/reap barrier, recovered through one isolated reader with real archive/import verification, preserved durable jobs/schedules/transcripts, and refused all eight source and eight destination scheduler cases.
The required guarded package workflow separately validates the exact clean source, wheel/sdist, optional TUI/vault installation, identity and checksums before PyPI publication. The release assets are that publishing run's exact distributions, validated-identity.json and SHA256SUMS.
Completed candidate CI: guarded build-only, Python 3.10/3.13, package and retained V1/V2 native integration, and all seven distro jobs.
The single guarded publishing run completed successfully. Its exact artifacts are attached here and the package is on PyPI. Anonymous public GitHub and PyPI downloads were compared byte-for-byte with those validated artifacts; the wheel and sdist SHA-256 values match SHA256SUMS.
No new external-host Podman or dashboard acceptance is claimed. Earlier evidence remains bound to its original source/native identities. The dashboard full-restore integrity verifier's manifest refusal and the unperformed portable UI/Storage/removal/final-attestation/Quit checks remain experimental limitations, not passes. See the complete 1.7 notes.
Upgrade
For an existing channel-aware installation, run on the host as your regular user:
oc-box upgrade --devel
oc-box --version
For a GitHub installation enabling the optional dashboard for the first time:
curl -fsSL --proto '=https' --tlsv1.2 https://raw.githubusercontent.com/groopcd/oc-box/master/install.sh | sh -s -- --devel --with-tui --with-vaultOmit --with-vault if unused. No workspace reset or history reimport is required. A launcher downgrade is not a workspace/session-state rollback. Stable installations remain on the stable channel unless explicitly switched.
Source identity
- Public version/tag:
1.7.117.dev0/v1.7.117.dev0 - Full identity:
1.7.117.dev0+g2f113ff - Source:
2f113ff0c4e46c13a01cbeec11b048c7ecbce4bd - Full-history commit count: 146; retained baseline: 29
- Channel:
devel, GitHub prerelease and PyPI.dev0, not a stable promotion.