Repository navigation
Tinyload v7.0

Tinyload v7.0
- Encrypted product strings — help text, CLI flags, and version strings XOR encrypted at rest.
- Hidden overlay signature — "TINYLD60" marker XOR'ed with per-file stubKey derived from .text section.
- Encrypted overlay metadata — origSz, packSz, flags, dispKey, vmCodeSz, and canary fields individually XOR'ed with stubKey-derived keys.
- Encrypted VM bytecode — VM program blob XOR-encrypted with stubKey stream, appearing as uniform noise in the overlay.
- Encrypted tail offset — 4-byte EOF pointer XOR'ed with stubKey. Overlay start position not readable from a hex dump.
- Zero-filler interleave — overlay interleaved with zero bytes at 3:1 ratio. Entropy drops from ~7.96 to ~6.73 bits/byte, blending with normal PE section entropy.
- Canary corridor — 8 chained integrity checks embedded in VM bytecode after decryption. Each canary's expected value depends on the previous actual value. Failures escalate a cumulative corruption mask (1→8 bits) XOR'ed into the plaintext.
- VEH page-fault decryption — all PE section pages encrypted at runtime and set to PAGE_NOACCESS. Vectored exception handler decrypts on first access. Watchdog re-encrypts cold pages after 200ms idle. LRU cache (256 slots) with thread safe eviction.
- Overlay chunk splitting — payload split into 4 chunks scattered across the file with random junk gaps (128–640 bytes).
- Bug fixes — LDB_I/STB_I bounds checks, SizeOfImage==0 rejection, NumberOfSections cap, readVarInt signed-shift UB fix, relocation type validation, import truncation detection, vmCodeSz/origSz key de-duplication, keystream seed hardened with QueryPerformanceCounter.
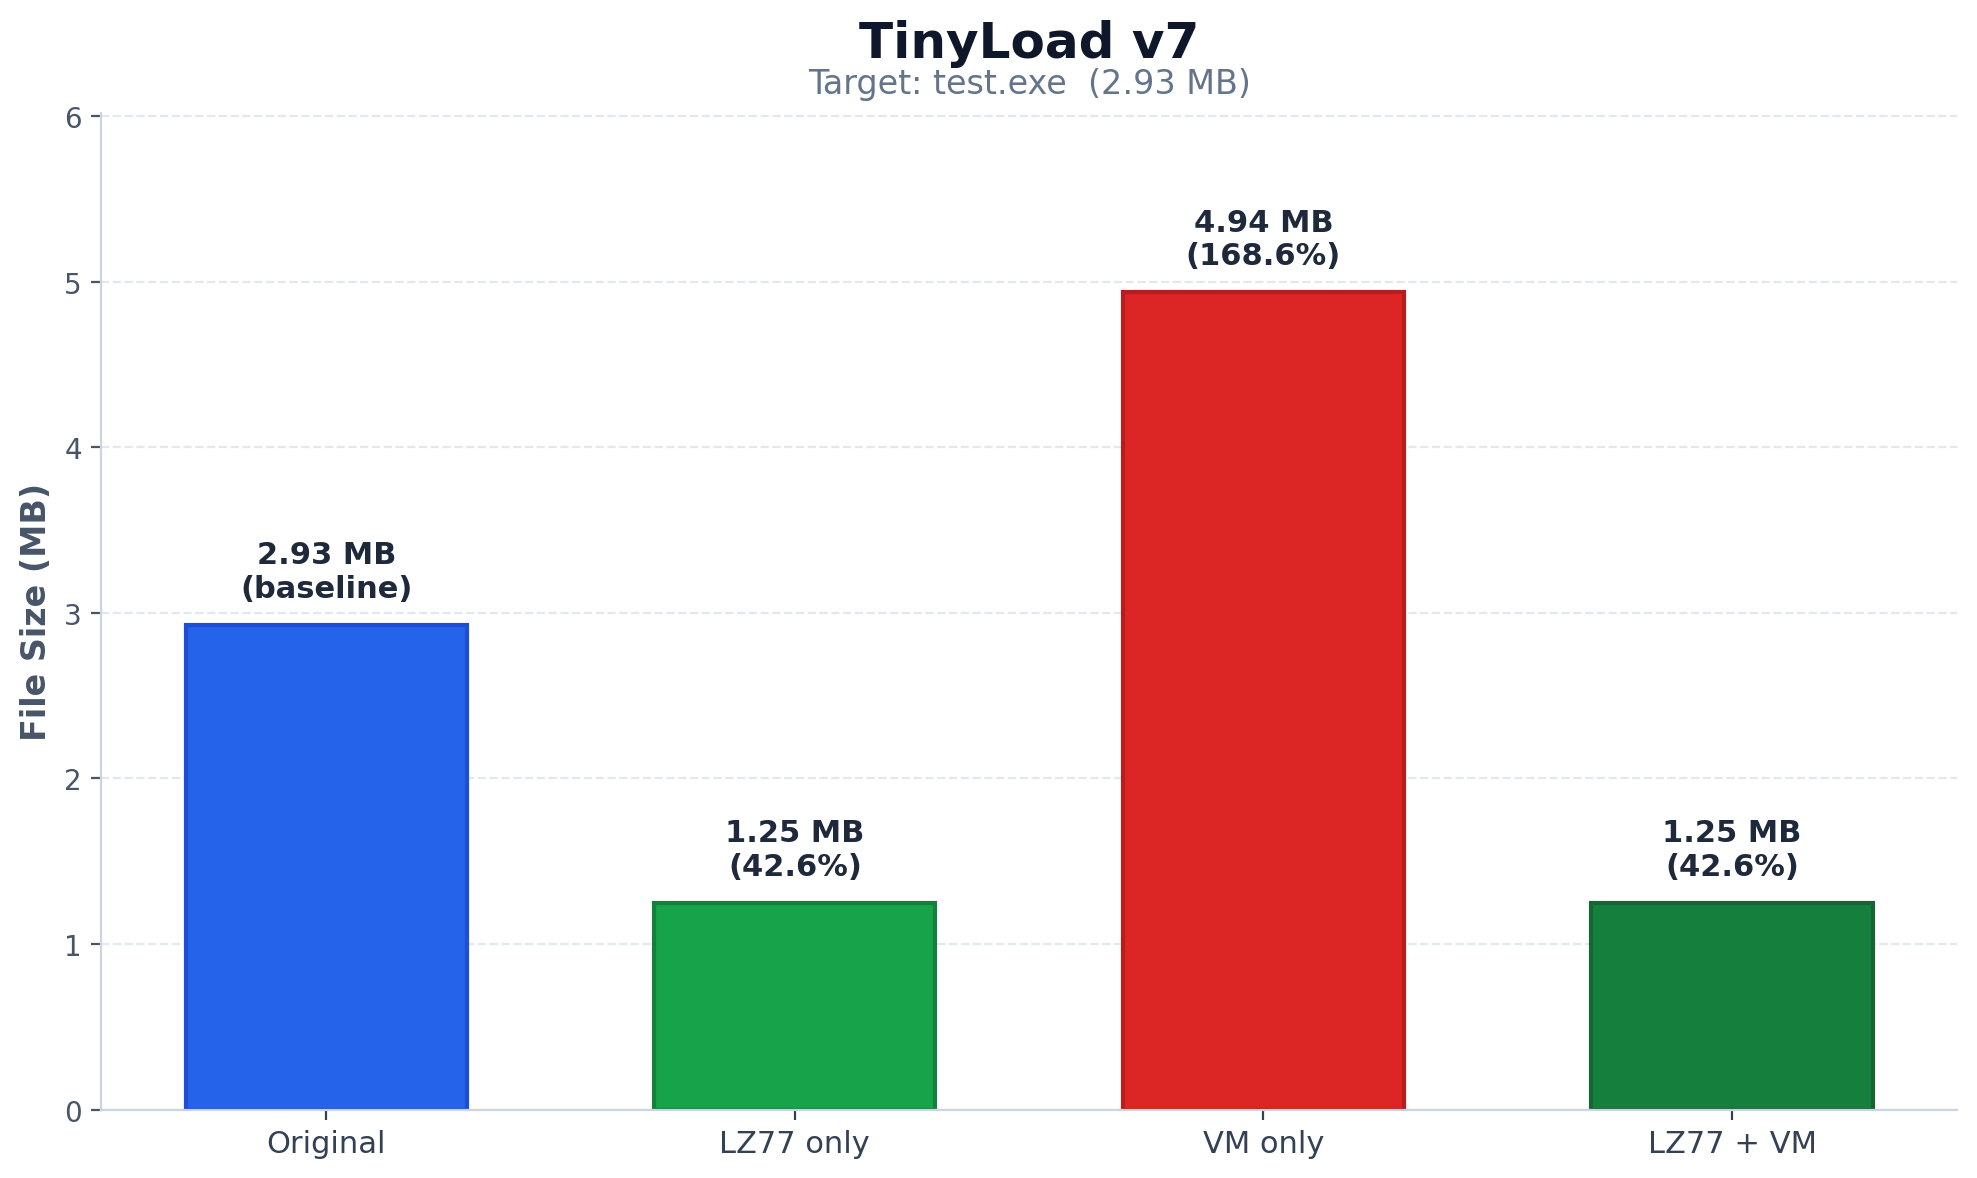
Graph: