Repository navigation

Release v0.2.0
Date: 2026-11-18
Milestone: Release v0.2.0
Summary
v0.2.0 delivers the core trial engine, fail-closed shape validation, metadata stabilization, the real_cases dataset framework, the benign_cases pipeline, and community cross-check adapters (bounty-scope and pgp-verify) backed by automated CI policy enforcement.
Architecture after this release: aura-pipeline-v4 (source: docs/diagrams/aura-pipeline-v4.mmd).
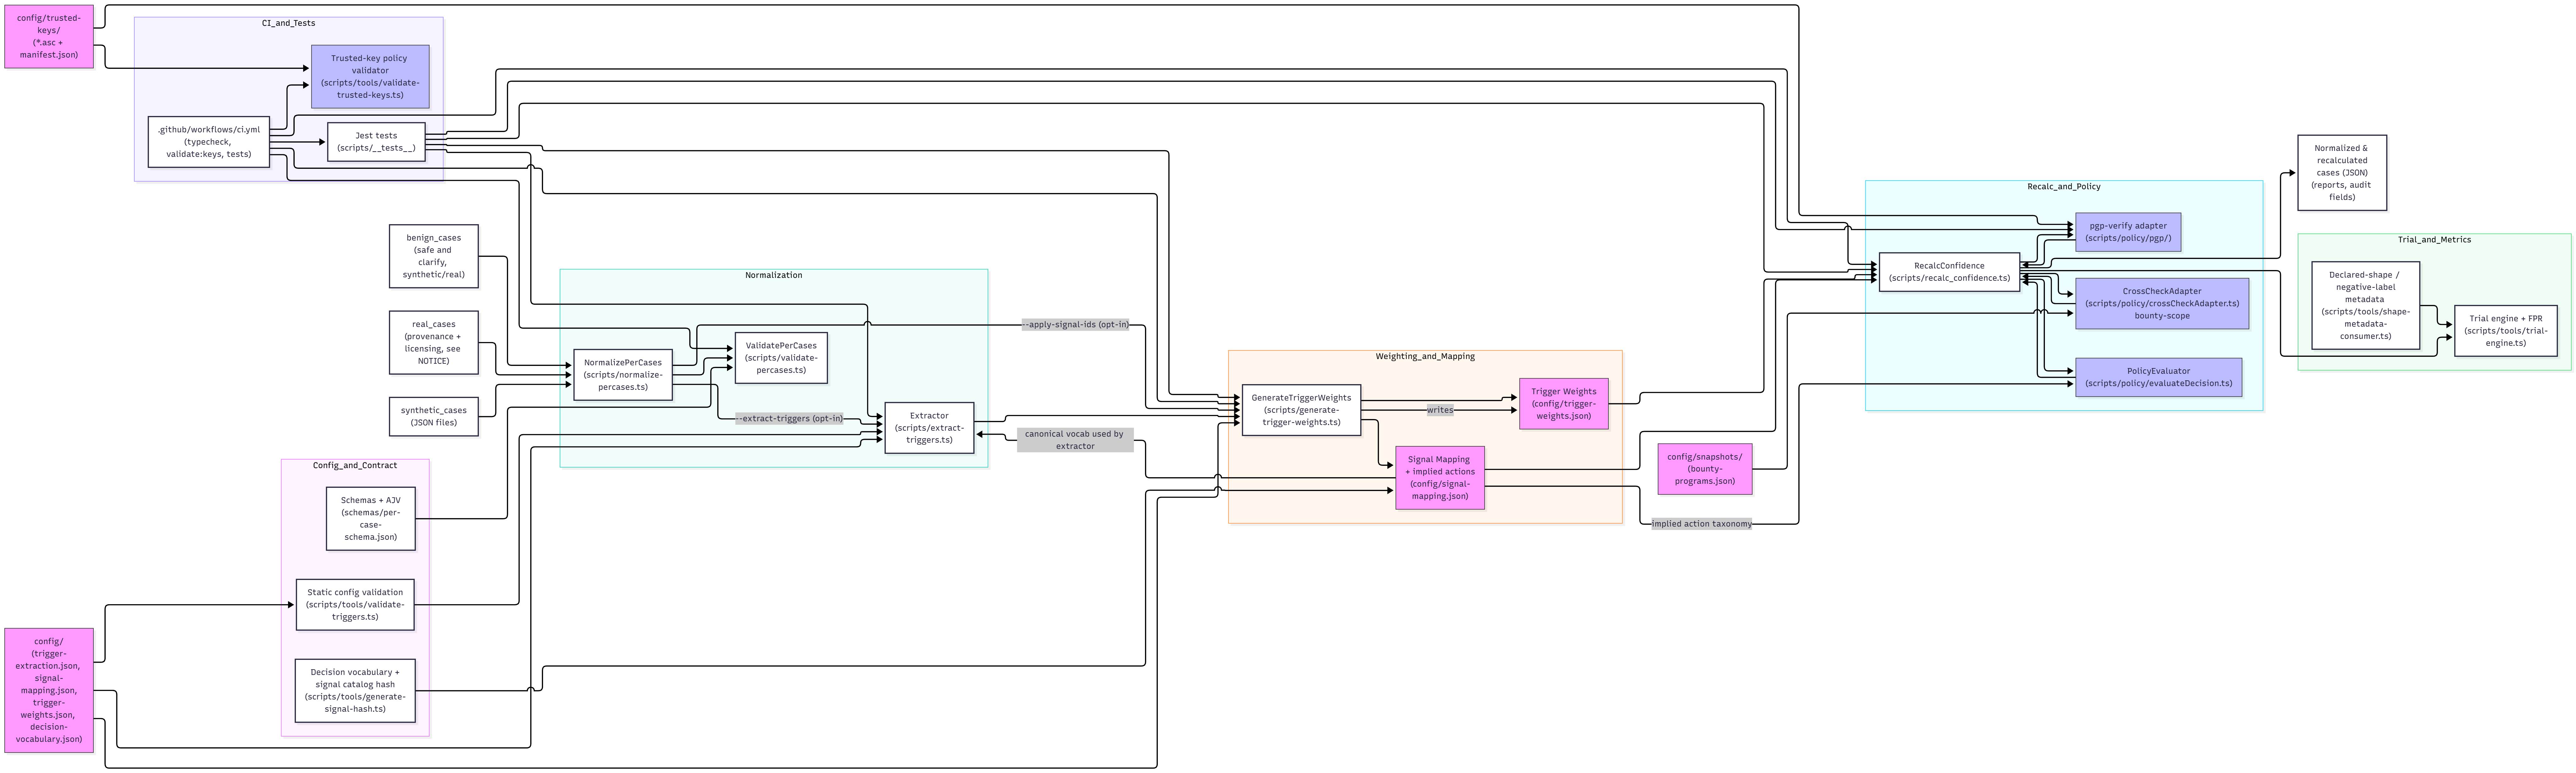
Key Features & Epics
1. Community Adapters for Cross-Check Enforcement (Epic #28)
adapter:bounty-scope(#87): Offline, snapshot-based verification of bug bounty program metadata (HackerOne, Bugcrowd) using local snapshots (config/snapshots/bounty-programs.json). Implemented in #90.adapter:pgp-verify(#88): Cryptographic PGP signature verification against a static local allowlist (scripts/policy/pgp/, openpgp 6.3.2). Implemented in #117.- Policy-as-Code Validation (#89): CI gate (
npm run validate:keys) that checks manifest/directory synchronization, ASCII-armor format, fingerprint integrity, a 2-year maximum validity window, RSA ≥ 3072 bits, approved elliptic curves (Ed25519, NIST P-256/P-384/P-521), and rejects SHA-1 and MD5 signatures. Implemented in #141.
2. Real Cases Dataset & Pipeline (Epic #84)
- Source/license audit, data-handling policy, and provenance fields per case (#78, #79).
- Unified directory targeting (
--dir/CASES_DIR) withreal_casesvalidation in CI (#80). - Licensing split and third-party attribution in
NOTICE(#81). - Pilot: 15 real prompts analyzed end to end, case ID scheme, and trigger cleanup (#82).
- Documentation: README, contributor guide, and differences from
synthetic_cases(#83).
3. Engine Robustness & Performance
- Async Bulk I/O & Caching (#37): Resource caching and bounded concurrency for large dataset evaluations.
- Strict Schema & Validation (#35, #38, #39): Tightened per-case schema with AJV validation, overlap detection for trigger/signal configs, and CI failure on unexpected silent errors.
- Race fix (#34):
updateCase()calls are awaited, so persisted confidence is no longer stale. - Recalc regression coverage (#36): Integration and regression tests for the recalc pipeline.
- Metadata & Vocabulary Stability (#68, #69, #70): Versioned decision vocabulary and signal-catalog hash, action-type binding for egress checks, and declared-shape metadata with False Positive Rate (FPR) evaluation. Trial engine FPR integration: #104.
- Dataset Separation (#106, #139): Renamed
public_casestosynthetic_casesand introduced thebenign_casespipeline (safe and clarify cases).
Pull Requests Without a Linked Issue
- #1 Compact signal IDs, structured categories, migration tools, docs and infra updates.
- #11 Decision vs. confidence: policy mapping and schema.
- #18 Confidence normalization, trigger weight retuning, removal of legacy fields, pipeline diagram.
- #22 Policy evaluator fixes: veto, evasion, pending, thresholds.
- #27 Machine-readable cross-check requirements and enforcement adapter.
- #30 and #33 Rule-based trigger extraction and its hardening.
- #55 Tiered TF-IDF trigger weighting.
- #58 License changed to BSL-1.1 (dual with Apache on the change date).
- #65
examples/CLI demo and sample case. - #73 and #119 Trigger-weight regeneration.
- #74 Reduced duplicate traffic workflow runs.
- Automated traffic report and history updates (
Update traffic ...workflow commits).
Known Limitations
- RSA key size in the PGP validator: the policy minimum is RSA ≥ 3072 bits. openpgp.js cannot generate keys below 2047 bits, so the weak-RSA test uses RSA-2048 (rejected by the loader). The original spec example used RSA-1024.
- Trusted-key allowlist is empty (
config/trusted-keys/manifest.json,keys: []) by design until the first keys are approved. - npm audit reports 42 advisories (1 critical, 40 high, 1 moderate) in the development toolchain (mainly
jest,ts-jest,@types/jest) and their transitive dependencies. They are not addressed in this release and are tracked in #142. They affect the build and test tooling, not the runtime code.
Upgrade Notes
package.jsonversion is updated to0.2.0.- Run
npm run validate:keyslocally to verify PGP trust-store changes. - References to
public_casesshould be updated tosynthetic_casesin local custom scripts.