Repository navigation
Should renovate consider trust? #11228

Replies: 1 comment 4 replies

|
Really interesting topic. I'm not an expert on signing in particular and don't have a strong opinion, but I'd say that in most cases I've learnt that visibility is important even if an upgrade is not acceptable for some reason. As in: it's usually useful to know that an upgrade exists which you're not taking, rather than it being simply invisible. And I'd say especially so if the release is rejected due to reasons which might be security-related. So one simple question you touched on is: If Renovate was agnostic to signing and it required another tool to do a CI check of Renovate's PRs, then is there much downside to that? One argument in favor of not doing it in Renovate: you probably want to be doing signing verifications in CI regardless of whether Renovate created the PR or a developer. One reason why you might want Renovate to be signing-aware would be if e.g. you are on |

I agree - if signature handling does fit in Renovate, perhaps it belongs later in the process than the That might also clarify the expectations in the case you mentioned: Renovate will follow existing versioning, but any PR proposing
From a holistic perspective, Renovate having a definition/interface for signing might drive alignment between those downstream tools. Projects should be releasing signed artifacts, and Renovate is a potential force to incentivize. Who wouldn't want a ✅ in a potential new "Signature Verified" column. Customers of hosted Renovate might like the idea that potentially malicious releases are filtered from CI, which might have additional permissions or be in-house.
Agreed here too! One shouldn't trust Renovate, but it would be interesting if Renovate could present signature verification results. |

I like this idea better. e.g it could be an optional, additional status check.
Good point, although this idea perhaps expands the scope a little. e.g. going from user-configure per-package "verify these signatures" to the idea that Renovate adds a check automatically, similar to GitHub marking commits as "Verified"?
FYI at WhiteSource we acquired and are now extending a security service called "Diffend". The idea of it is to flag suspicious packages in real-time and then manually review them as quickly as possible. Switching from signed to unsigned or verified to unverified would definitely be the type of signal which fits in there. One of the concepts of Diffend is that it integrates with the package managers itself to protect all systems (developer, CI, even Renovate) from downloading suspicious packages. It is therefore more wider protection than Renovate itself filtering/skipping.
Actually I wasn't meaning directly not to trust Renovate (but don't object to the point). I was meaning that Renovate might not be the only source of package additions or upgrades in a CI system and therefore you need all PRs reviewed/scanned and not only Renovate's. Maybe Renovate could be the one to do that, or maybe it's a separate concept. |
I was thinking as part of the current To populate that column, Renovate would need to:
Sorry for the poor phrasing, that's exactly what I meant too! Renovate is an awesome tool, I trust it with my repo contents. "One shouldn't special case Renovate's PRs" is 💯 . |
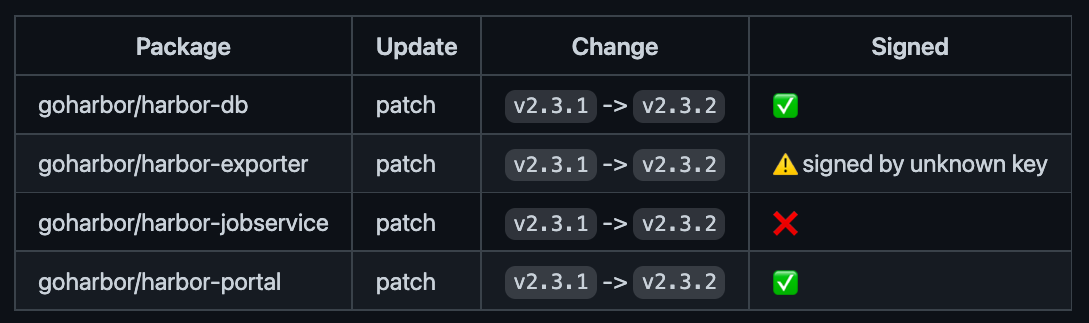
|
I think what we're looking for is incremental improvement, by which I mean:
I would prefer not to "fail" neutral ones because it might create too much noise that you miss the important ones which get worse. BTW Renovate tends to not run commands like
^^ Point being, it may require a rearchitecture to e.g. use Bundler's out of the box trust policy capabilities. Another approach: assuming most registries are immutable, that should mean that "was this release signed or not?" should be immutable too. In other words, we only need to calculate it once, and calculation should be independent of the repo which happens to be run by Renovate first. We could probably validate signing once-per-release within datasources as long as we can cache it indefinitely (unlike release lists themselves, which we typically cache for 15-60 minutes). Related to that: #11232 |


Uh oh!
There was an error while loading. Please reload this page.
Systems like Docker Content Trust and sigstore provide an additional means to verify artifacts were published by a trusted source, focused on the
dockerecosystem. PGP adds an additional layer of trust to git (commit/tag signing), github-releases (e.g. tianon/gosu), or some future datasource that fetches releases from a http file listing e.g. (apache ant) / sample implementation from a Go codebase.If Renovate were to consider artifact trust, it could not propose upgrades to unsigned/untrusted versions.
One approach would be filtering untrusted artifacts in the
Datasourceabstraction. In another archived Go codebase, I found swapping querying a Docker registry with a Notary server to be a smooth transition. Cosign also seems capable of listing versions from the signature database, potentially avoiding the Docker registry.Reasons not to: scope creep.
gpgorcosignbinaries.I suspect Renovate doesn't want this scope, but I didn't see any other discussions/issues so I raised this idealogical question: should Renovate include dependency provenance, or should that be left to the repo?
All reactions