Repository navigation

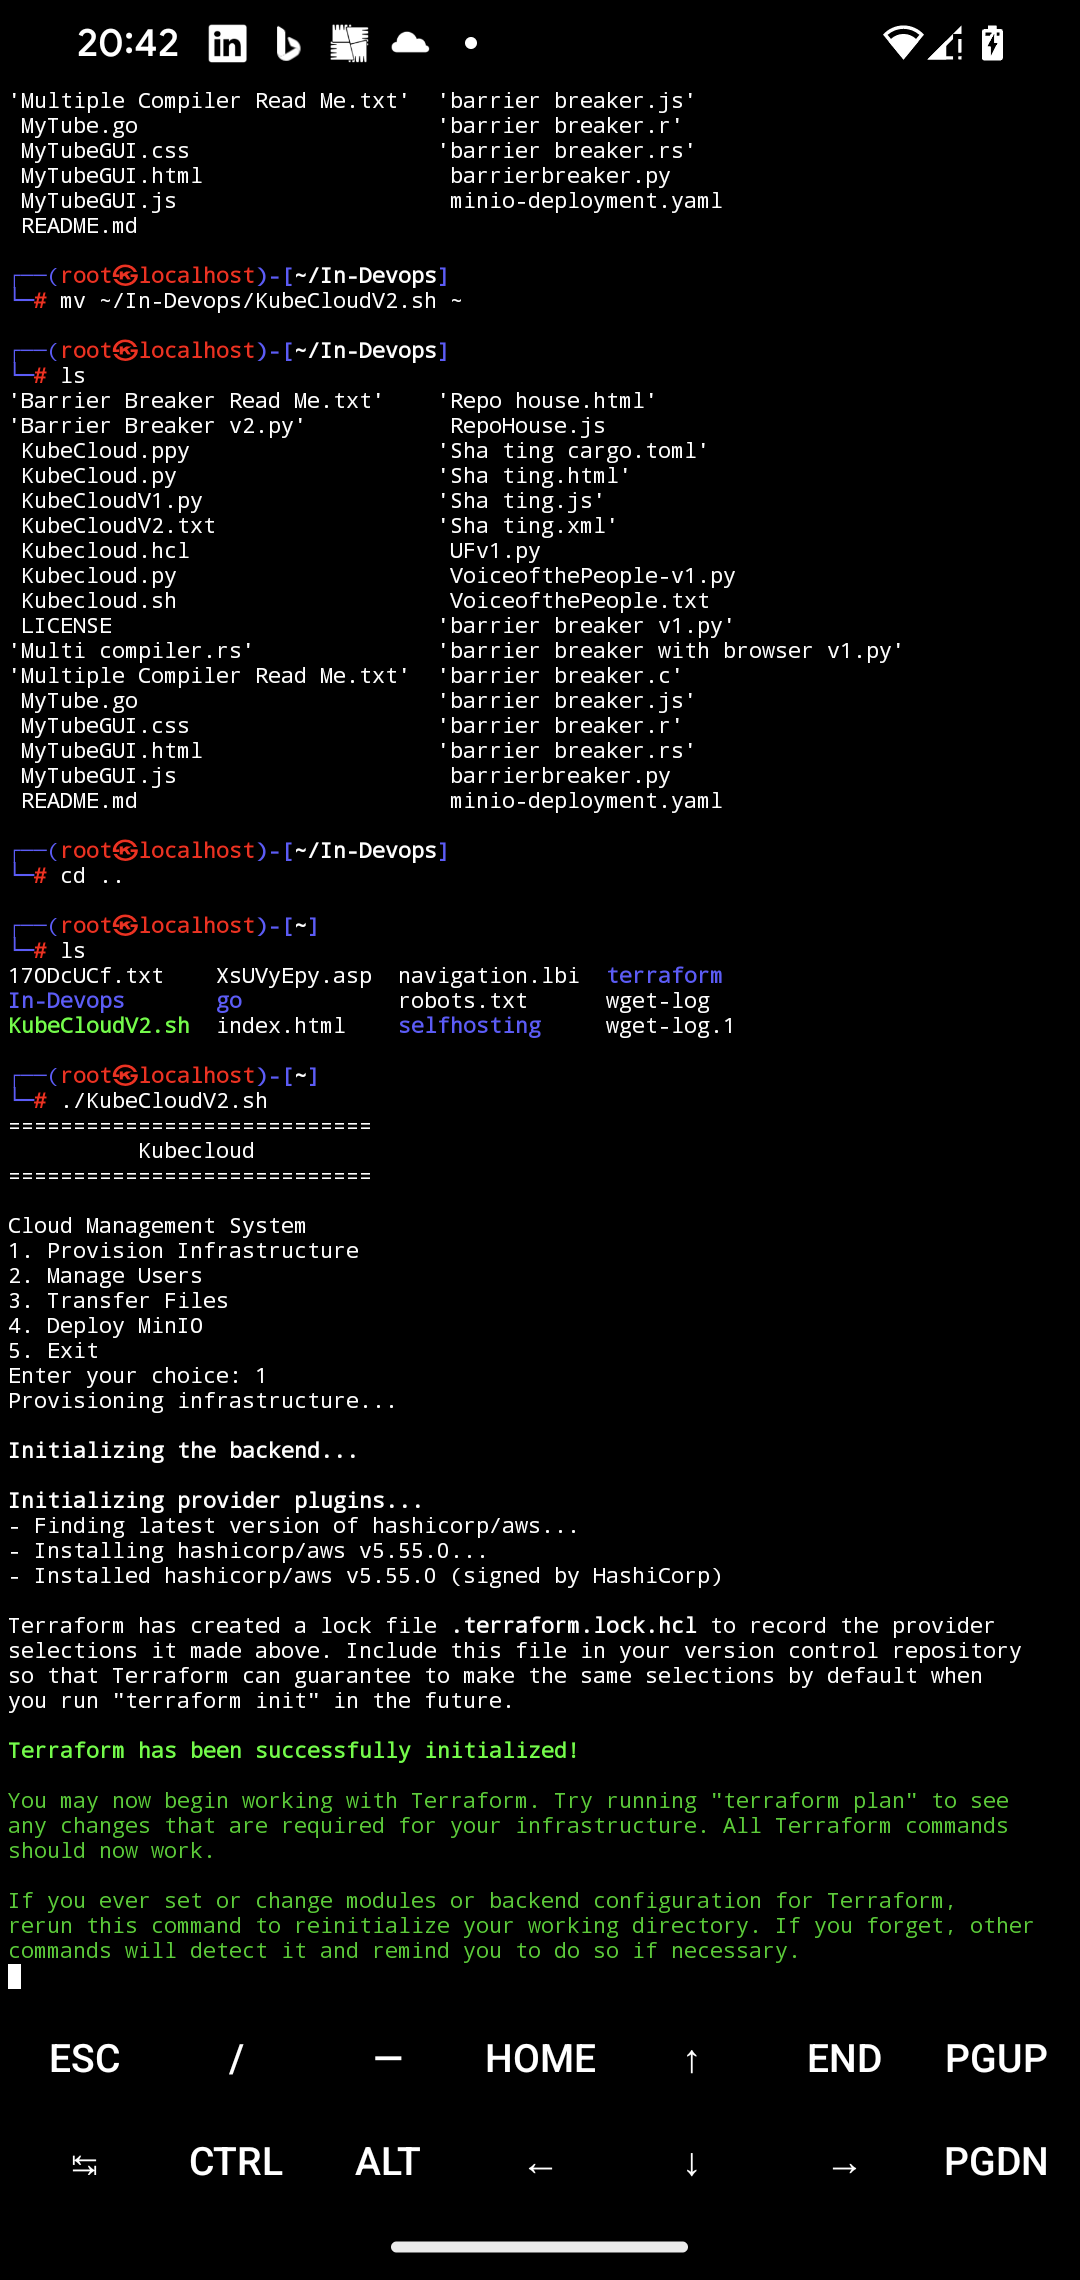
Kubecloud
The stolen AWS keys allow the attacker to:
Provision AWS Resources: Unauthorized EC2 instances can lead to unexpected charges, security risks, and potential data exfiltration.
Deploy Applications (MinIO): Unauthorized deployments can result in unauthorized data storage and exposure, with the attacker gaining full control over MinIO storage.
Alter or Destroy Infrastructure: Malicious scripts could terminate or modify resources, impacting the availability and integrity of the AWS environment.
Data Exfiltration: MinIO or other deployed services could be used to store and exfiltrate sensitive data, impacting confidentiality.