Repository navigation
stable-20261008: LTS

Variants promoted
| Variant | Tag | Digest |
|---|---|---|
bluefin-lts |
:stable |
sha256:0338d7be5c0f |
bluefin-lts-nvidia |
:stable |
sha256:45456f1c43ca |
bluefin-lts and bluefin-lts-nvidia use the Fedora CoreOS stable kernel. The Kernel (LTS) version above applies to both.

Key components
| Component | Version | Change |
|---|---|---|
| Kernel (LTS) | 7.1.8-200 |
|
| GNOME Shell | 50.0-3.el10 |
|
| Flatpak | 1.18.0-2.el10 |
|
| bootc | 1.16.13-1.el10 |
28 updated since the previous release. 1566 packages total.
Package changes
↑ 28 updated packages
| Package | From | To |
|---|---|---|
c-ares |
1.34.6-4.el10 |
1.34.8-1.el10 |
gnome-remote-desktop |
49.3-12.el10 |
49.3-13.el10 |
gtk-update-icon-cache |
3.24.43-5.el10 |
3.24.52-1.el10 |
gtk3 |
3.24.43-5.el10 |
3.24.52-1.el10 |
insights-core |
3.8.1-1.el10 |
3.8.2-1.el10 |
insights-core-selinux |
3.8.1-1.el10 |
3.8.2-1.el10 |
kernel-headers |
6.12.0-271.el10 |
6.12.0-273.el10 |
kernel-tools |
6.12.0-271.el10 |
6.12.0-273.el10 |
kernel-tools-libs |
6.12.0-271.el10 |
6.12.0-273.el10 |
libsolv |
0.7.33-6.el10 |
0.7.33-7.el10 |
mdadm |
4.4-5.el10.1 |
4.6-1.el10 |
nvme-cli |
2.16-2.el10 |
2.16-3.el10 |
pcre2 |
10.44-1.el10.3 |
10.44-1.4.el10 |
pcre2-syntax |
10.44-1.el10.3 |
10.44-1.4.el10 |
pcre2-utf16 |
10.44-1.el10.3 |
10.44-1.4.el10 |
pcre2-utf32 |
10.44-1.el10.3 |
10.44-1.4.el10 |
pipewire |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-alsa |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-gstreamer |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-jack-audio-connection-kit |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-jack-audio-connection-kit-libs |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-libs |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-plugin-libcamera |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-pulseaudio |
1.6.1-100.el10 |
1.6.9-1.el10 |
pipewire-utils |
1.6.1-100.el10 |
1.6.9-1.el10 |
python3-perf |
6.12.0-271.el10 |
6.12.0-273.el10 |
tailscale |
1.102.5-1 |
1.104.1-1 |
tzdata |
2026c-1.el10 |
2026e-1.el10 |
Desktop Screenshot
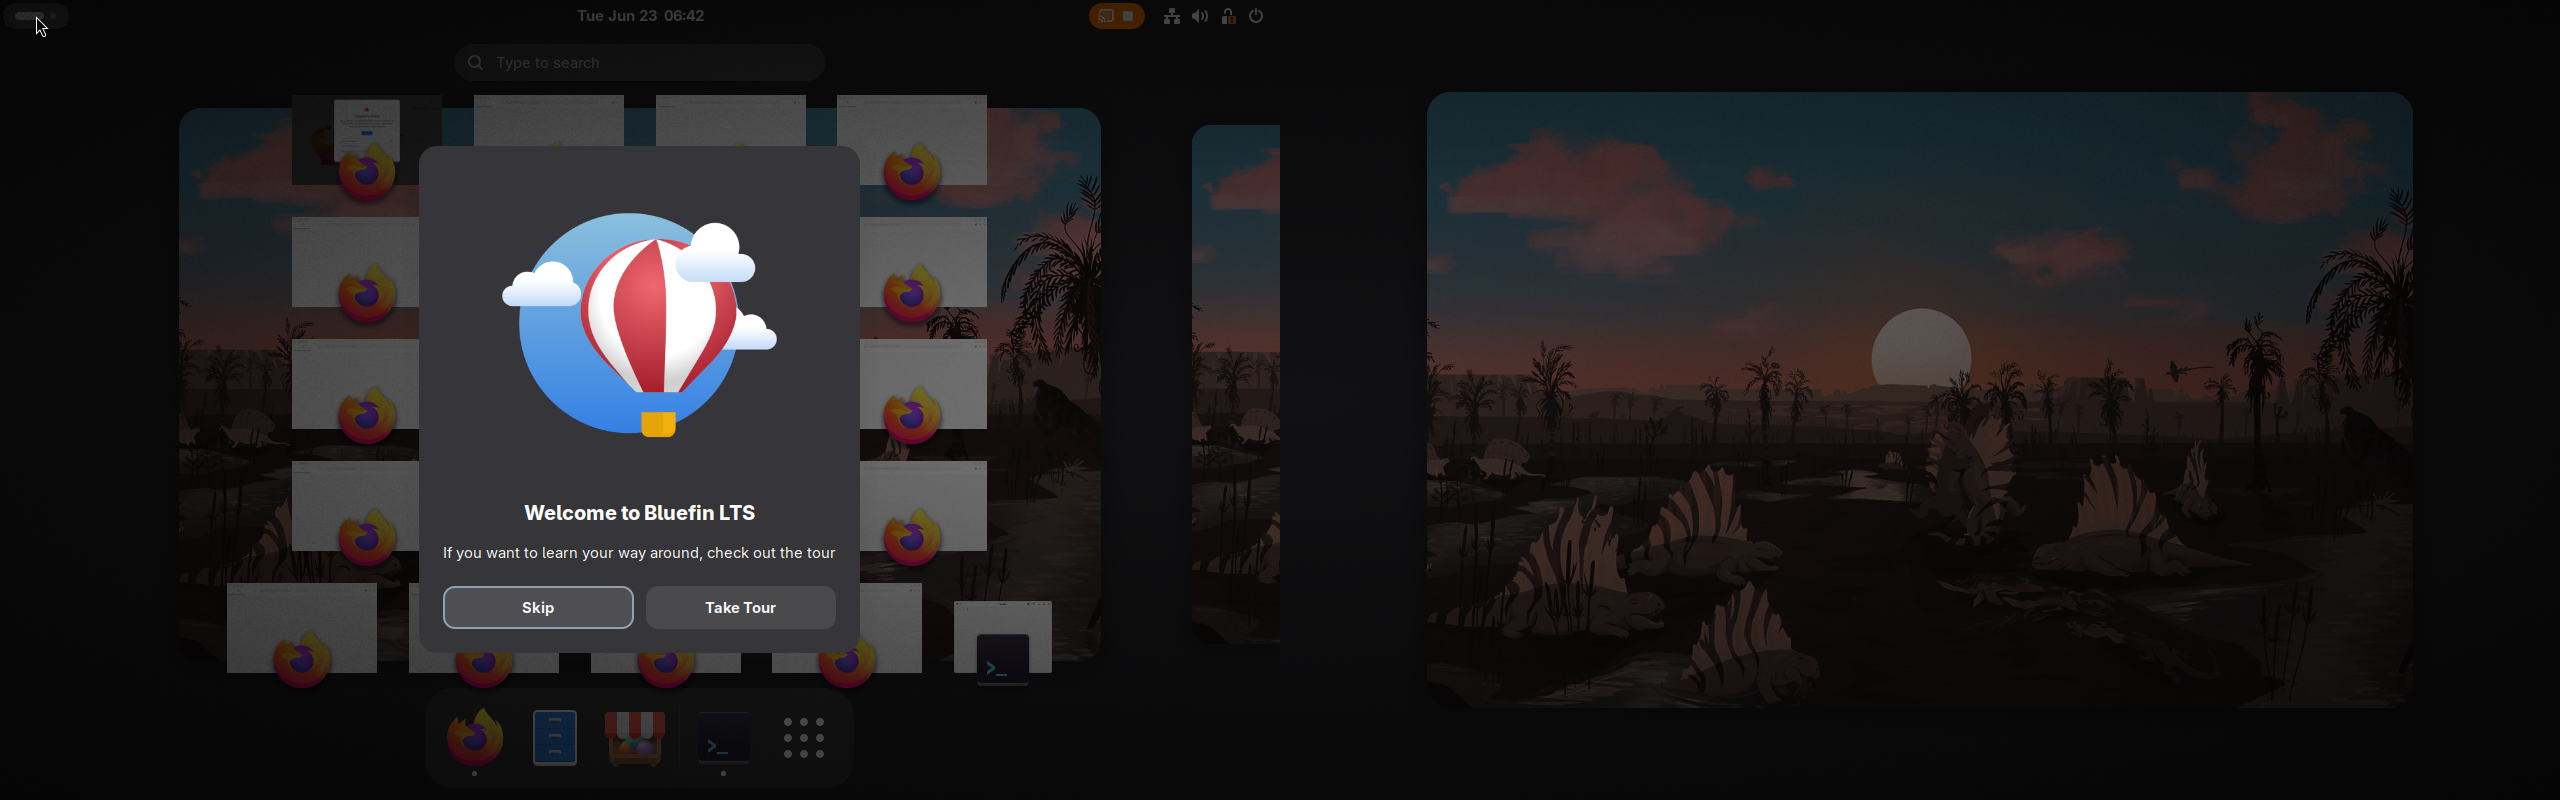
Captured from bluefin-lts:testing during automated e2e validation — testsuite
Supply chain verification
Supply chain
This image is signed, attested, and ships a full SPDX-JSON SBOM.
Every artifact below is verifiable without trusting this release page.
Tools required — install via Homebrew or see links in each section:
brew install cosign oras slsa-verifier1 — Verify the image signature
cosign (Sigstore) verifies the keyless
OIDC signature created by GitHub Actions at build time.
cosign verify \
  --certificate-identity-regexp '^https://github\.com/projectbluefin/(bluefin-lts|actions|execute-release)/\.github/workflows/' \
  --certificate-oidc-issuer 'https://token.actions.githubusercontent.com' \
  ghcr.io/projectbluefin/bluefin-lts@sha256:0338d7be5c0fcb72072ef3f43666508703307b78005e783cc29e5e9987e4f993
A valid response lists the certificate subject and OIDC issuer. Any tampered
image will produce a verification error.
2 — Fetch and inspect the SBOM
The SBOM (SPDX 2.3 JSON) is attached to the image as an
OCI referrer using
ORAS (CNCF graduated project).
# Discover the attached SBOM referrer
oras discover \
  --artifact-type application/vnd.spdx+json \
  ghcr.io/projectbluefin/bluefin-lts@sha256:0338d7be5c0fcb72072ef3f43666508703307b78005e783cc29e5e9987e4f993

# Pull the SBOM to disk (replace SBOM_DIGEST with the digest from above)
oras pull \
  --artifact-type application/vnd.spdx+json \
  ghcr.io/projectbluefin/bluefin-lts@<SBOM_DIGEST>
The SBOM is also attached to this release as
bluefin-lts.spdx.json.
3 — Verify the SBOM attestation
The SBOM is also stored as a signed
GitHub SBOM attestation
in the Sigstore transparency log.
cosign verify-attestation \
  --type https://spdx.dev/Document \
  --certificate-identity-regexp '^https://github\.com/projectbluefin/(bluefin-lts|actions|execute-release)/\.github/workflows/' \
  --certificate-oidc-issuer 'https://token.actions.githubusercontent.com' \
  ghcr.io/projectbluefin/bluefin-lts@sha256:0338d7be5c0fcb72072ef3f43666508703307b78005e783cc29e5e9987e4f993 \
  | jq -r '.payload | @base64d | fromjson | .predicate.name'
4 — Verify SLSA Build L2 provenance
slsa-verifier (OpenSSF)
checks that this image was built by the expected workflow on the expected
source repository — not on a developer's laptop or a forked CI runner.
slsa-verifier verify-image \
  ghcr.io/projectbluefin/bluefin-lts@sha256:0338d7be5c0fcb72072ef3f43666508703307b78005e783cc29e5e9987e4f993 \
  --source-uri 'github.com/projectbluefin/bluefin-lts' \
  --source-versioned-tag 'stable-20261008'
You can also inspect the raw provenance:
cosign verify-attestation \
  --type slsaprovenance1 \
  --certificate-identity-regexp '^https://github\.com/projectbluefin/(bluefin-lts|actions|execute-release)/\.github/workflows/' \
  --certificate-oidc-issuer 'https://token.actions.githubusercontent.com' \
  ghcr.io/projectbluefin/bluefin-lts@sha256:0338d7be5c0fcb72072ef3f43666508703307b78005e783cc29e5e9987e4f993 \
  | jq -r '.payload | @base64d | fromjson | .predicate'
Full changelog and verification guide → https://docs.projectbluefin.io/changelogs
Full changelog → https://docs.projectbluefin.io/changelogs