Repository navigation
How CAESAR works
CAESAR runs primarily on a technology called Two-Factor Authentication (2FA). This requires the user to have a smartphone with a special app, which generates PINs that change every thirty seconds. A user must enter the current PIN shown on their device to decrypt any encrypted files. This system provides an extra layer of security to any preexisting encryption system.
A user's 2FA account code needs to be sufficiently secured. The current plan is to encrypt the account code with DPAPI (in the scope of the user's local Windows account), convert the resulting byte array into a Base64 string, and store it via CAESAR's Properties.Settings class. The information in this class persists between runs of the application. When a user attempts to decrypt a file, the account code is pulled from the settings file, decrypted, and is used to verify the PIN the user enters. If the PIN checks out, the file is decrypted, and everyone's happy.
The Properties.Settings class will also contain another necessary bit of information: whether the application is on it's first run. Ultimately, this is used to provide the user with the best experience. It facilitates the creation of an account code and corresponding backup code on the first startup, and can alert CAESAR to problems when something unexepected occurrs.
CAESAR will compare both the 'first run' information and the 2FA data on start and select an appropriate course of action according to the following table:
| First run? | 2FA data? | Possible causes | Action taken |
|---|---|---|---|
| true | false | Initial startup | CAESAR will generate a new account code for the user, and walk them through adding it to their device. Alternatively, the user can opt to import a backup account file into the application, should they possess one. In either case, normal operation commences once the account is set up. |
| false | true | Normal usage | CAESAR proceeds with normal operation. |
| false | false | Alteration by a malicious entity; user ingorance/error | The 2FA data has been erased or corrupted. CAESAR will begin the backup process, if the user remembers the backup code supplied to them when they first created the account. If they do not have the backup code, they will have to create a new account code; all files currently encrypted will be indecipherable at this point. |
| true | true | External modification | 2FA data exists, but CAESAR thinks that this is its first run. Either the 'first run' flag was manually set to 'true' after the first run, or 2FA data was inserted before the first run. CAESAR will alert the user of this anomaly, and ask whether to accept the 2FA data in the file. If the user chooses to accept the data, operation proceeds as normal. If not, a new account code is generated. |
"What if someone deletes my existing 2FA data and changes the account code, are my encrypted files still safe?"
In most cases, yes. Only the account code that was used to encrypt the files can decrypt them. An attacker would have to know your password and have physical access to your computer in order to decipher your files.
"Would I be able to access my files again?"
Yes, under two conditions:
- The backup account data has not been tampered with
- You remember your backup code
If either of these conditions are not met, you will no longer be able to access any encrypted files you may have. But then, neither will anyone else. This project is being developed on the principle of CIA:
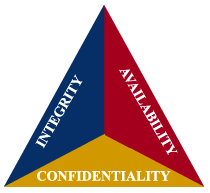
Confidentiality means your data is secure. Only you should be able to access it. Integrity means your data hasn't been tampered with. Availability means you can readily access your data once it is decrypted.