Repository navigation
Does the Leaf App Server expose a web API? #474


|
We're engaged in a Security Risk Assessment for Leaf, so I need to describe its architecture and data flow. The Leaf architecture contains an App Server which performs all DBMS access and exposes a Leaf API. Does the App Server also expose a web API? That is, can an authenticated http client issue http requests to the App Server and obtain DBMS query results? Thanks |
Replies: 1 comment 3 replies

|
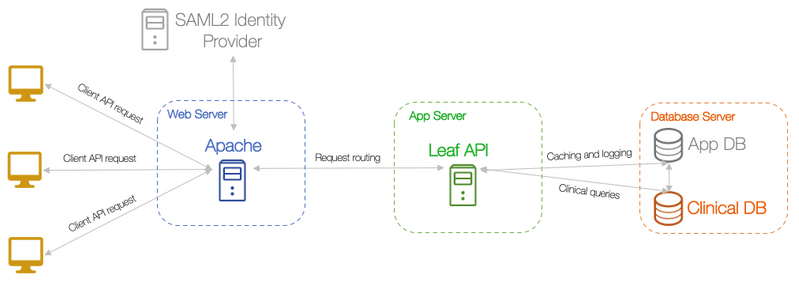
Right, in a typical 3-tier setup, the Leaf API runs on the App Server, and user HTTP requests are reverse-proxied to the API:
Leaf uses a standard RESTful API, and most endpoints by and large are protected and only accept requests if a given HTTP request includes an
In other words, the flow is:
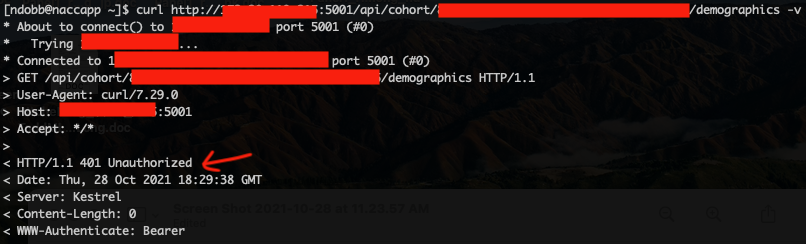
This flow holds true whether calling from the Leaf web client (i.e., client -> Web Server -> App Server), directly via a shell within the App Server, or wherever. If the requester fails in either step (1) or step (2), the API will never allow them to do (3). In other words, the API is hardened, and sensitive endpoints will only trust requests that originate with an authenticated user and For example, However I cannot do so with Please let me know if this makes sense or if you have other questions, Arthur. Best, |


|
Thanks for the rapid, informative and extensive response, @ndobb . This is definitely an answer. |
|
However, the architecture diagram is a bit misleading. The Shibboleth module used by Apache doesn't communicate directly with the SAML Identity Provider. Instead, it communicates through the client (e.g. browser) via redirects to the SAML Identity Provider. |

|
That's true, and perhaps we can update to make that more clear. That diagram mostly exists to help new sites trying to make sense of Leaf at a high level grasp what it does, so it's not the best technical representation of auth procedures. |


Right, in a typical 3-tier setup, the Leaf API runs on the App Server, and user HTTP requests are reverse-proxied to the API:
Leaf uses a standard RESTful API, and most endpoints by and large are protected and only accept requests if a given HTTP request includes an
AccessToken(example:/api/cohort/count). There is one and only one API.AccessTokensare generated for a user only after they first are authenticated and retrieve aUserToken, after which they can request anAccessToken, which is valid for only 6 minutes.In other words, the flow is:
UserToken(i.e., authenticates), which is successful if and only if the request contains expected shibboleth headers with user…