Releases: zackabrah/scopeglass
Release list
v0.2.0

Scopeglass v0.2.0
Website: https://zackabrah.github.io/scopeglass/
Diagnostic ruleset version 2. Reports keep schema version 1, but ruleset-observable behavior changed — scopeglass check outcomes can differ from v0.1.0 on the same tree. Review the changes below before upgrading in CI gates.
- Ruleset version: 2 (was 1)
- Report schema version: 1 (unchanged)
- Supported Node.js:
>=22.17.0 - License: MIT
- Package integrity (sha512):
sha512-rWiJ78+6zuuFVF/7yb+crUgKR9q7eNbKMSn75YxdRNPWgEDJ9dnSf0c/q7ZqnomKF1jaVO8tE2NWyIdIrpe9Dg==
Changed (behavioral — can affect check)
- A symlinked or junctioned
AGENTS.mdis now followed when it resolves to a regular file inside the analysis root (the commonAGENTS.md -> CLAUDE.mdlayout). Broken links, links escaping the root, and links resolving to non-files remain fatalunsafe-symlinkerrors; the resolved file passes the same open-descriptor identity checks. - Only root-level headings update the section stack. A heading nested inside a blockquote or list item no longer relabels later instructions.
- Same-line instruction ordering ties now break on the numeric instruction ordinal instead of lexicographic ID comparison.
- The npm package no longer ships
tasks/plan.md(still in the repository).
Fixed
- HTML report no longer overflows horizontally at extreme text zoom (200% on a 320px viewport): the hero title, instruction cards, eyebrow labels, and scope-heading metadata now wrap instead of pushing their grid tracks wider than the container. Verified across Chromium, Firefox, and WebKit.
Documentation
- Clarified that the parser-sensitive syntax budgets, not the byte limits, are the practical input ceiling, and that exceeding any hard limit is fatal rather than a diagnostic.
- Redesigned the README (theme-aware logo, benefits-first overview, badges, quick navigation); logo ships in
docs/assets/. - Restyled the HTML report and logo on a monochrome, geometric design system with a single green accent; the report follows the OS color scheme (light/dark) while print output stays light.
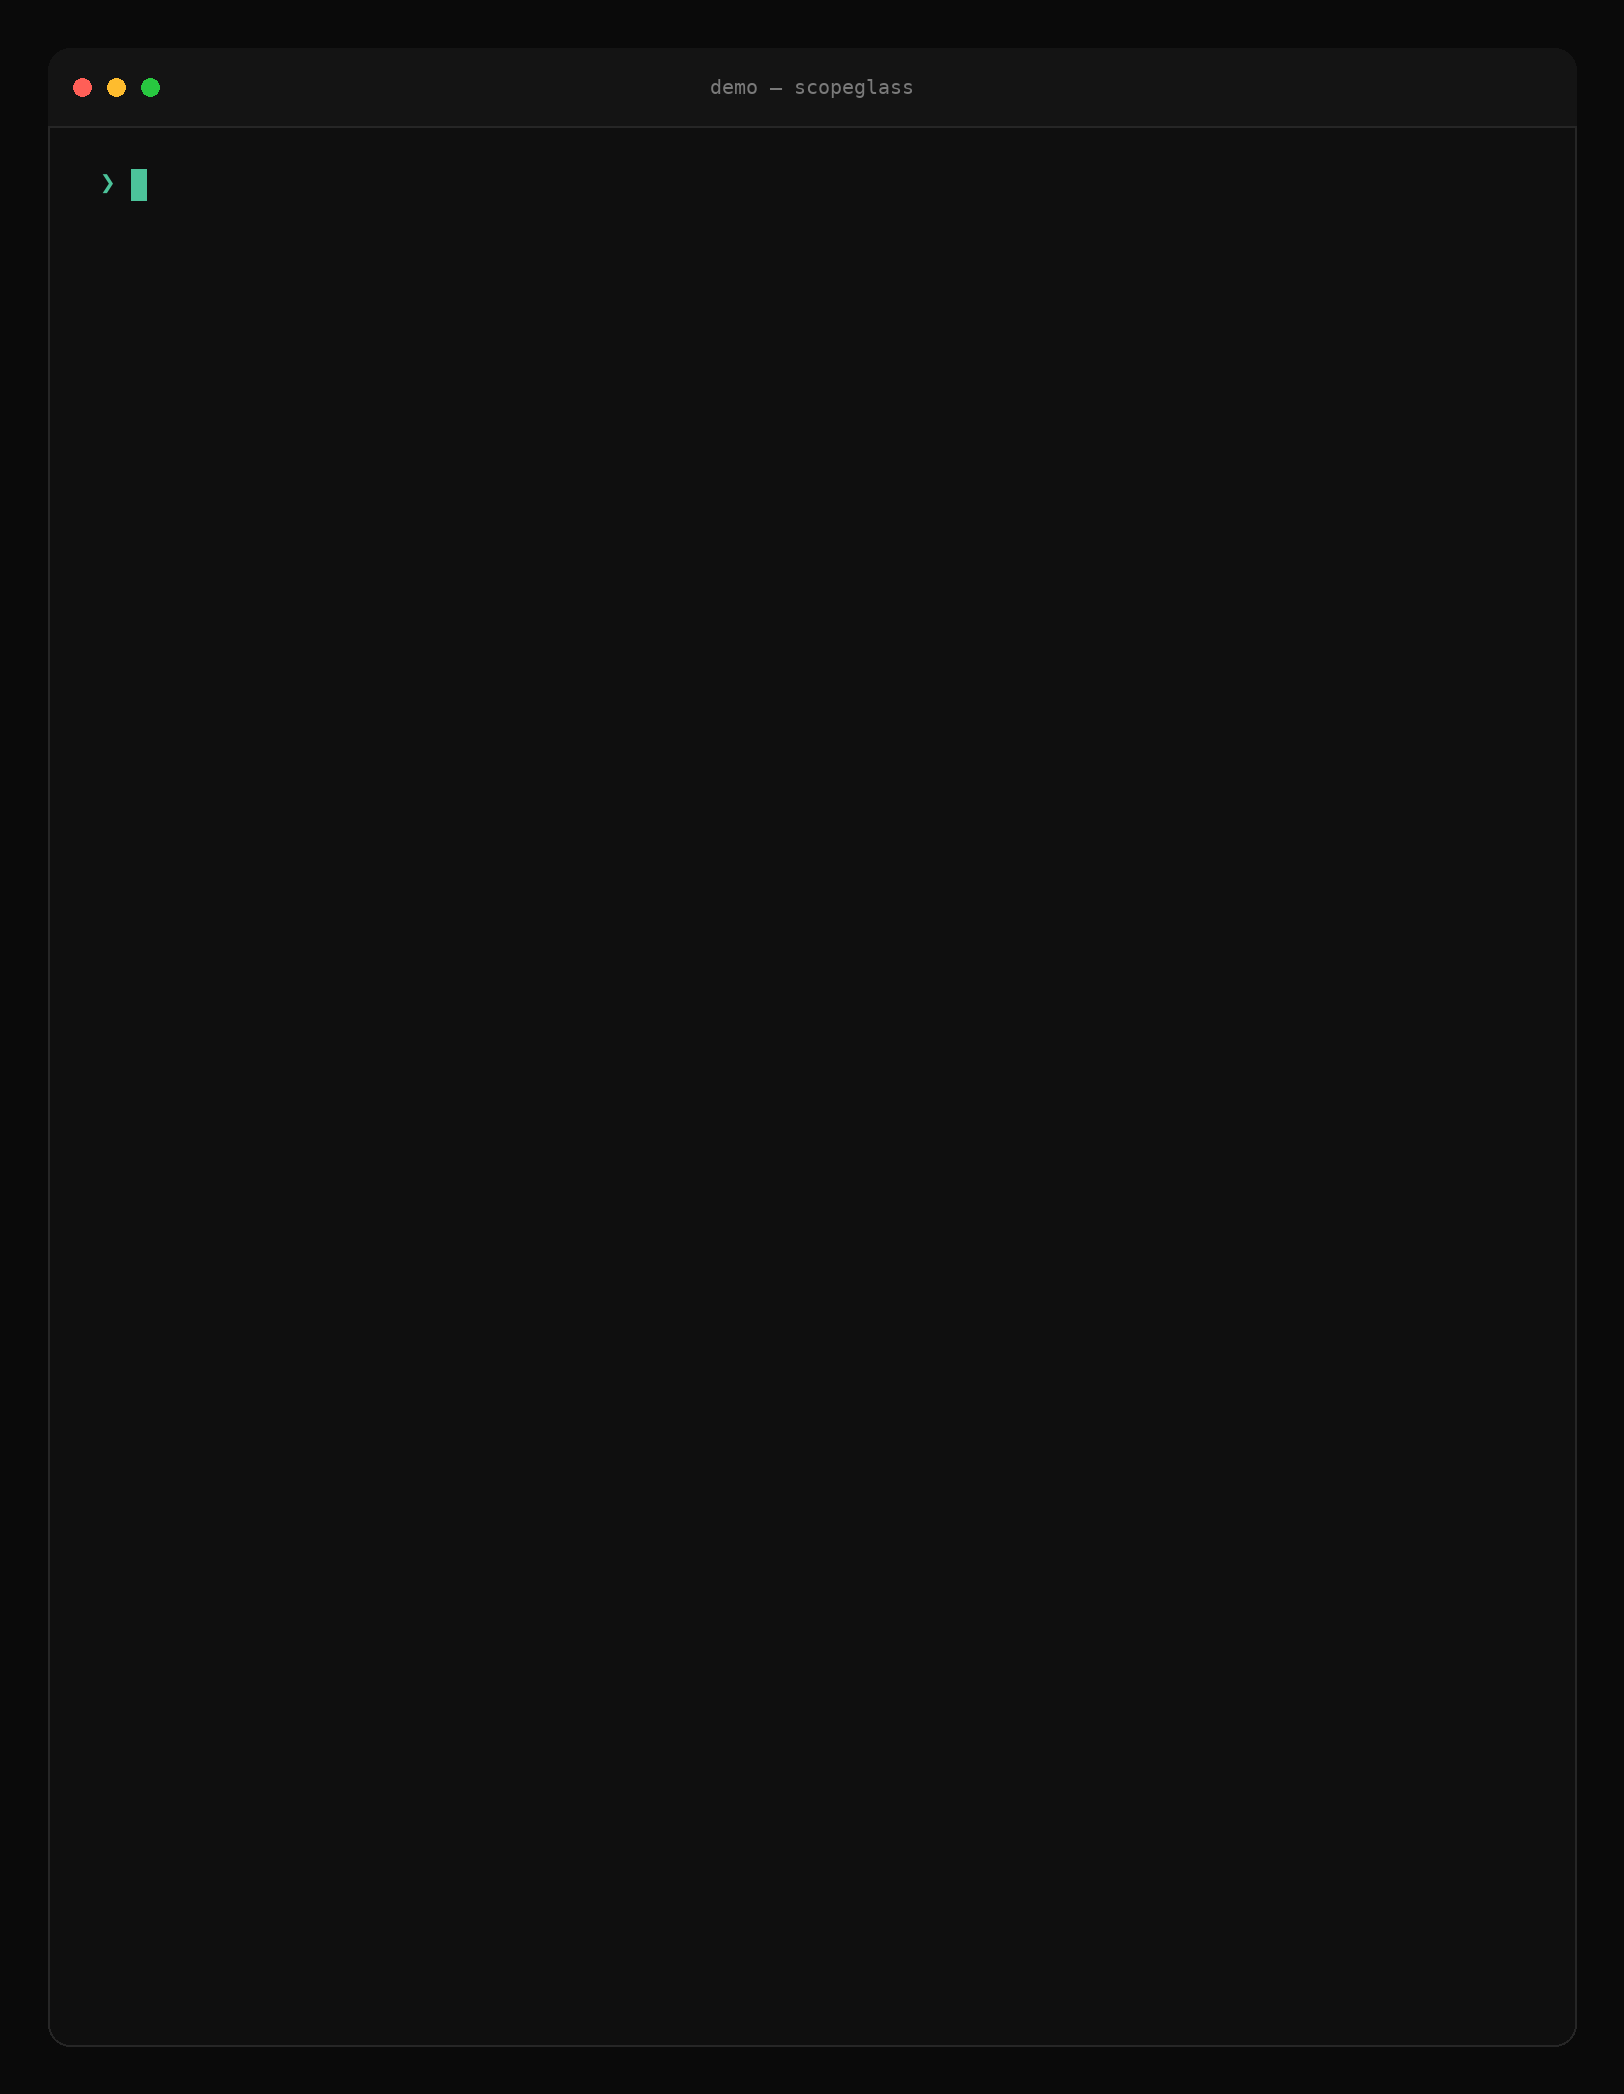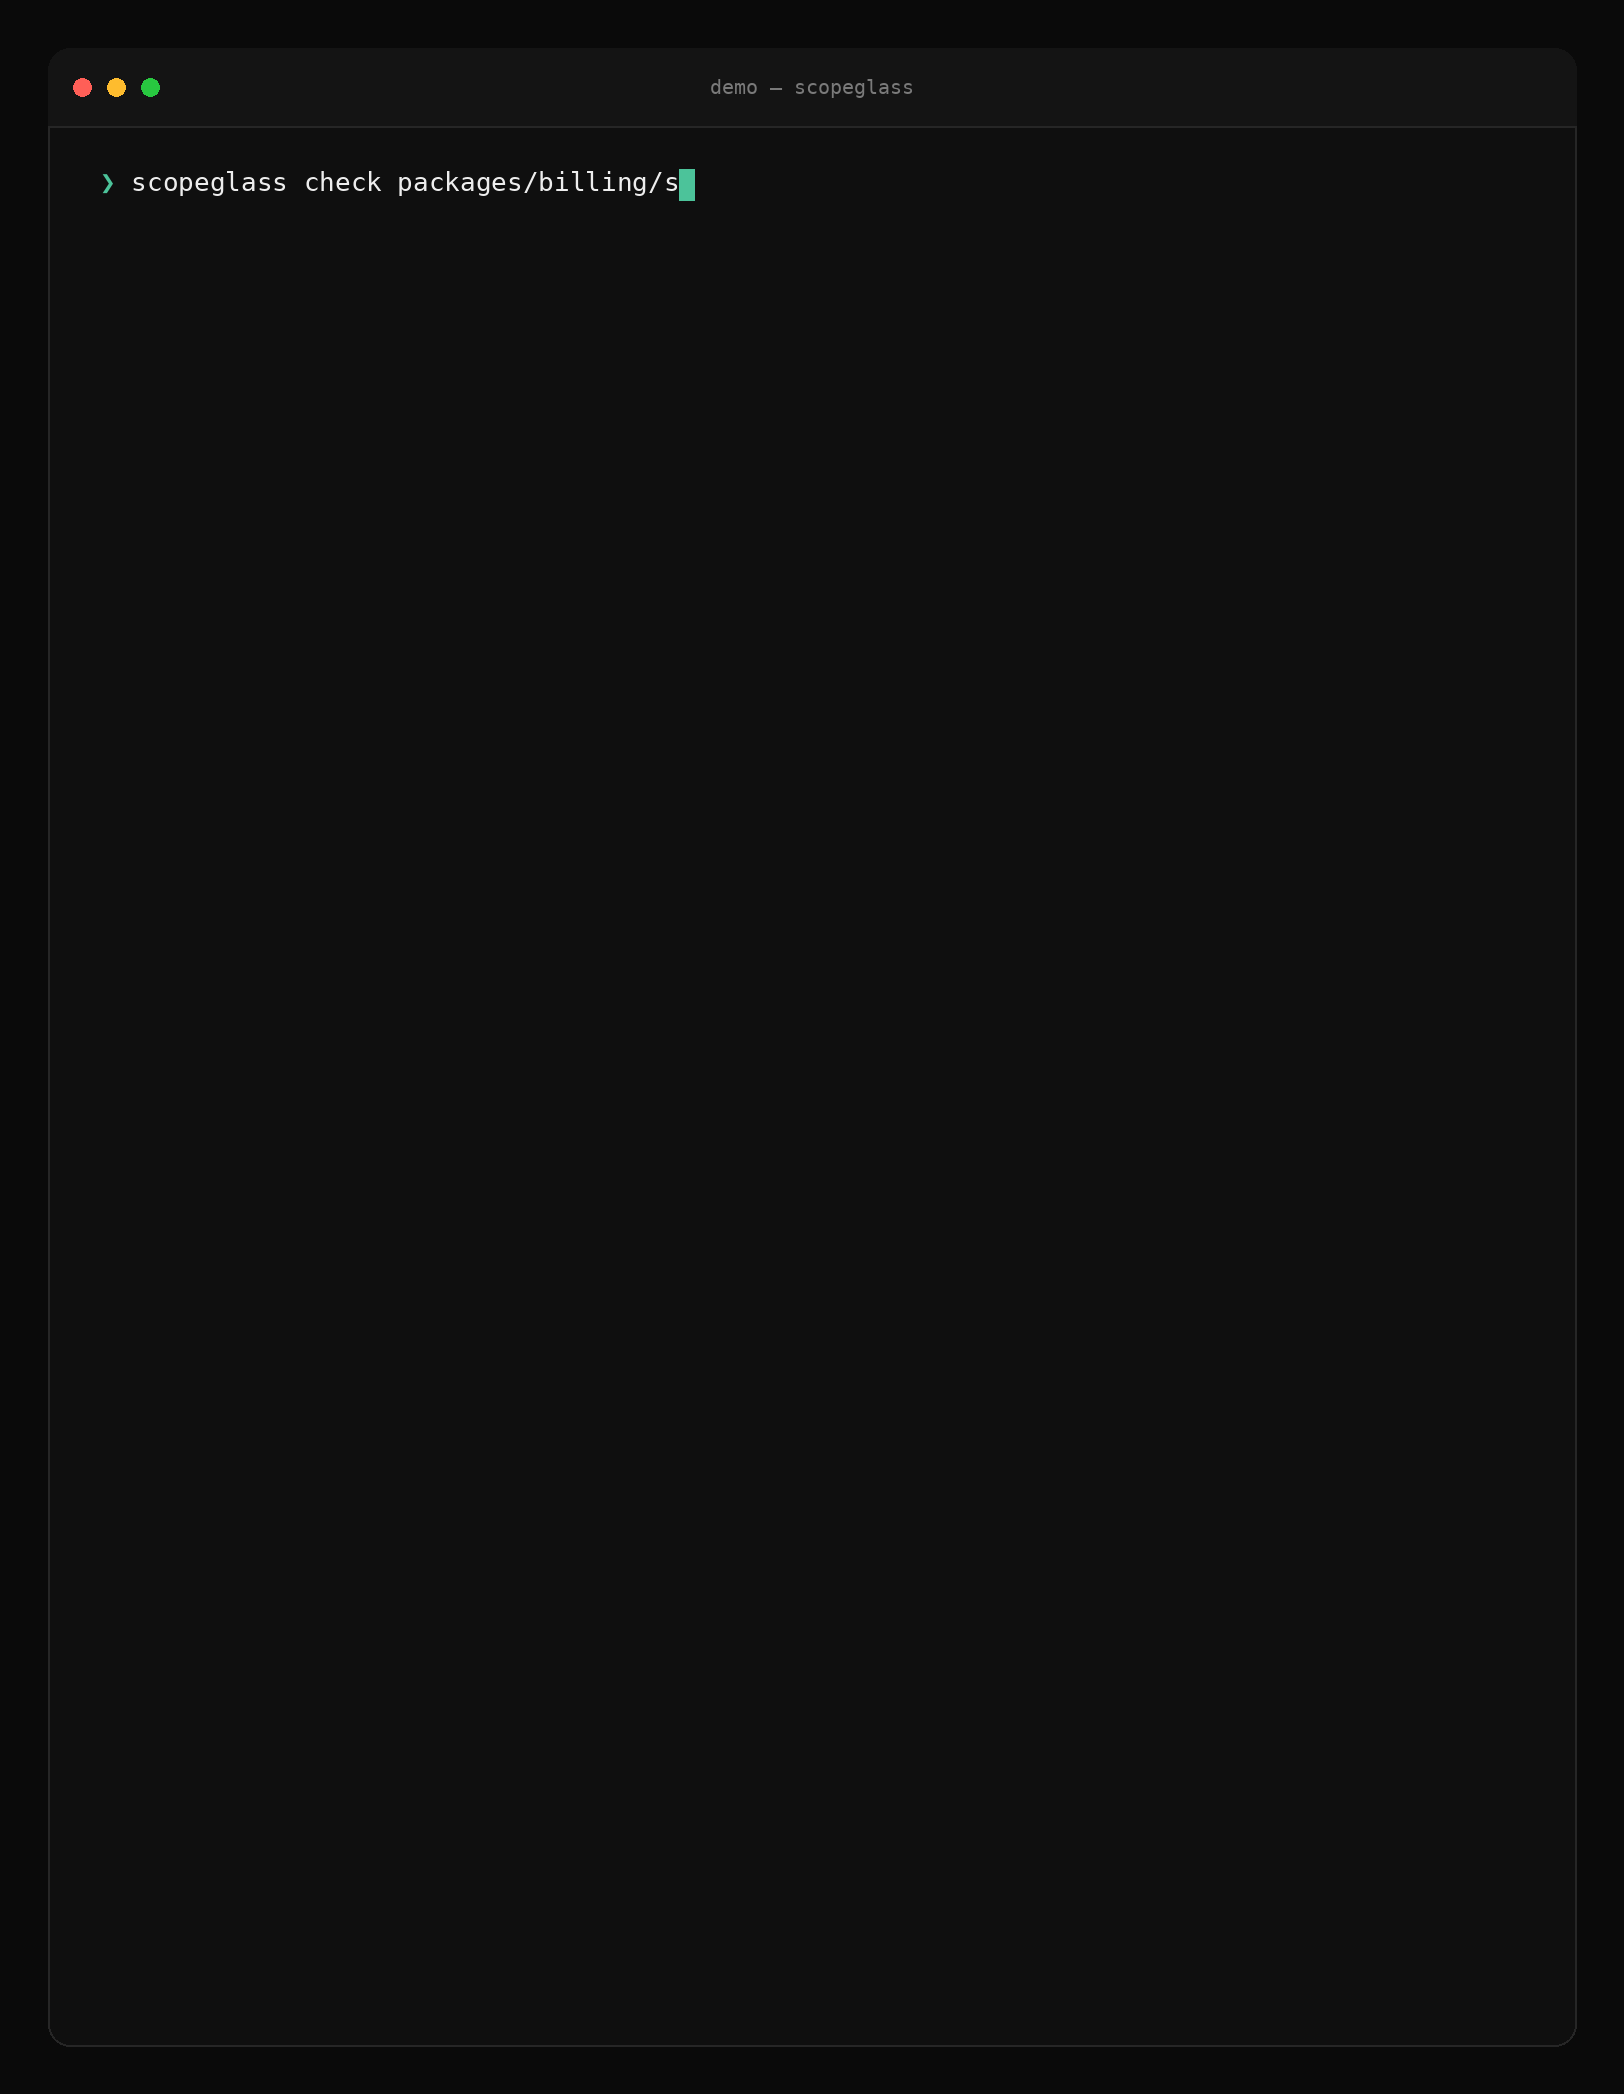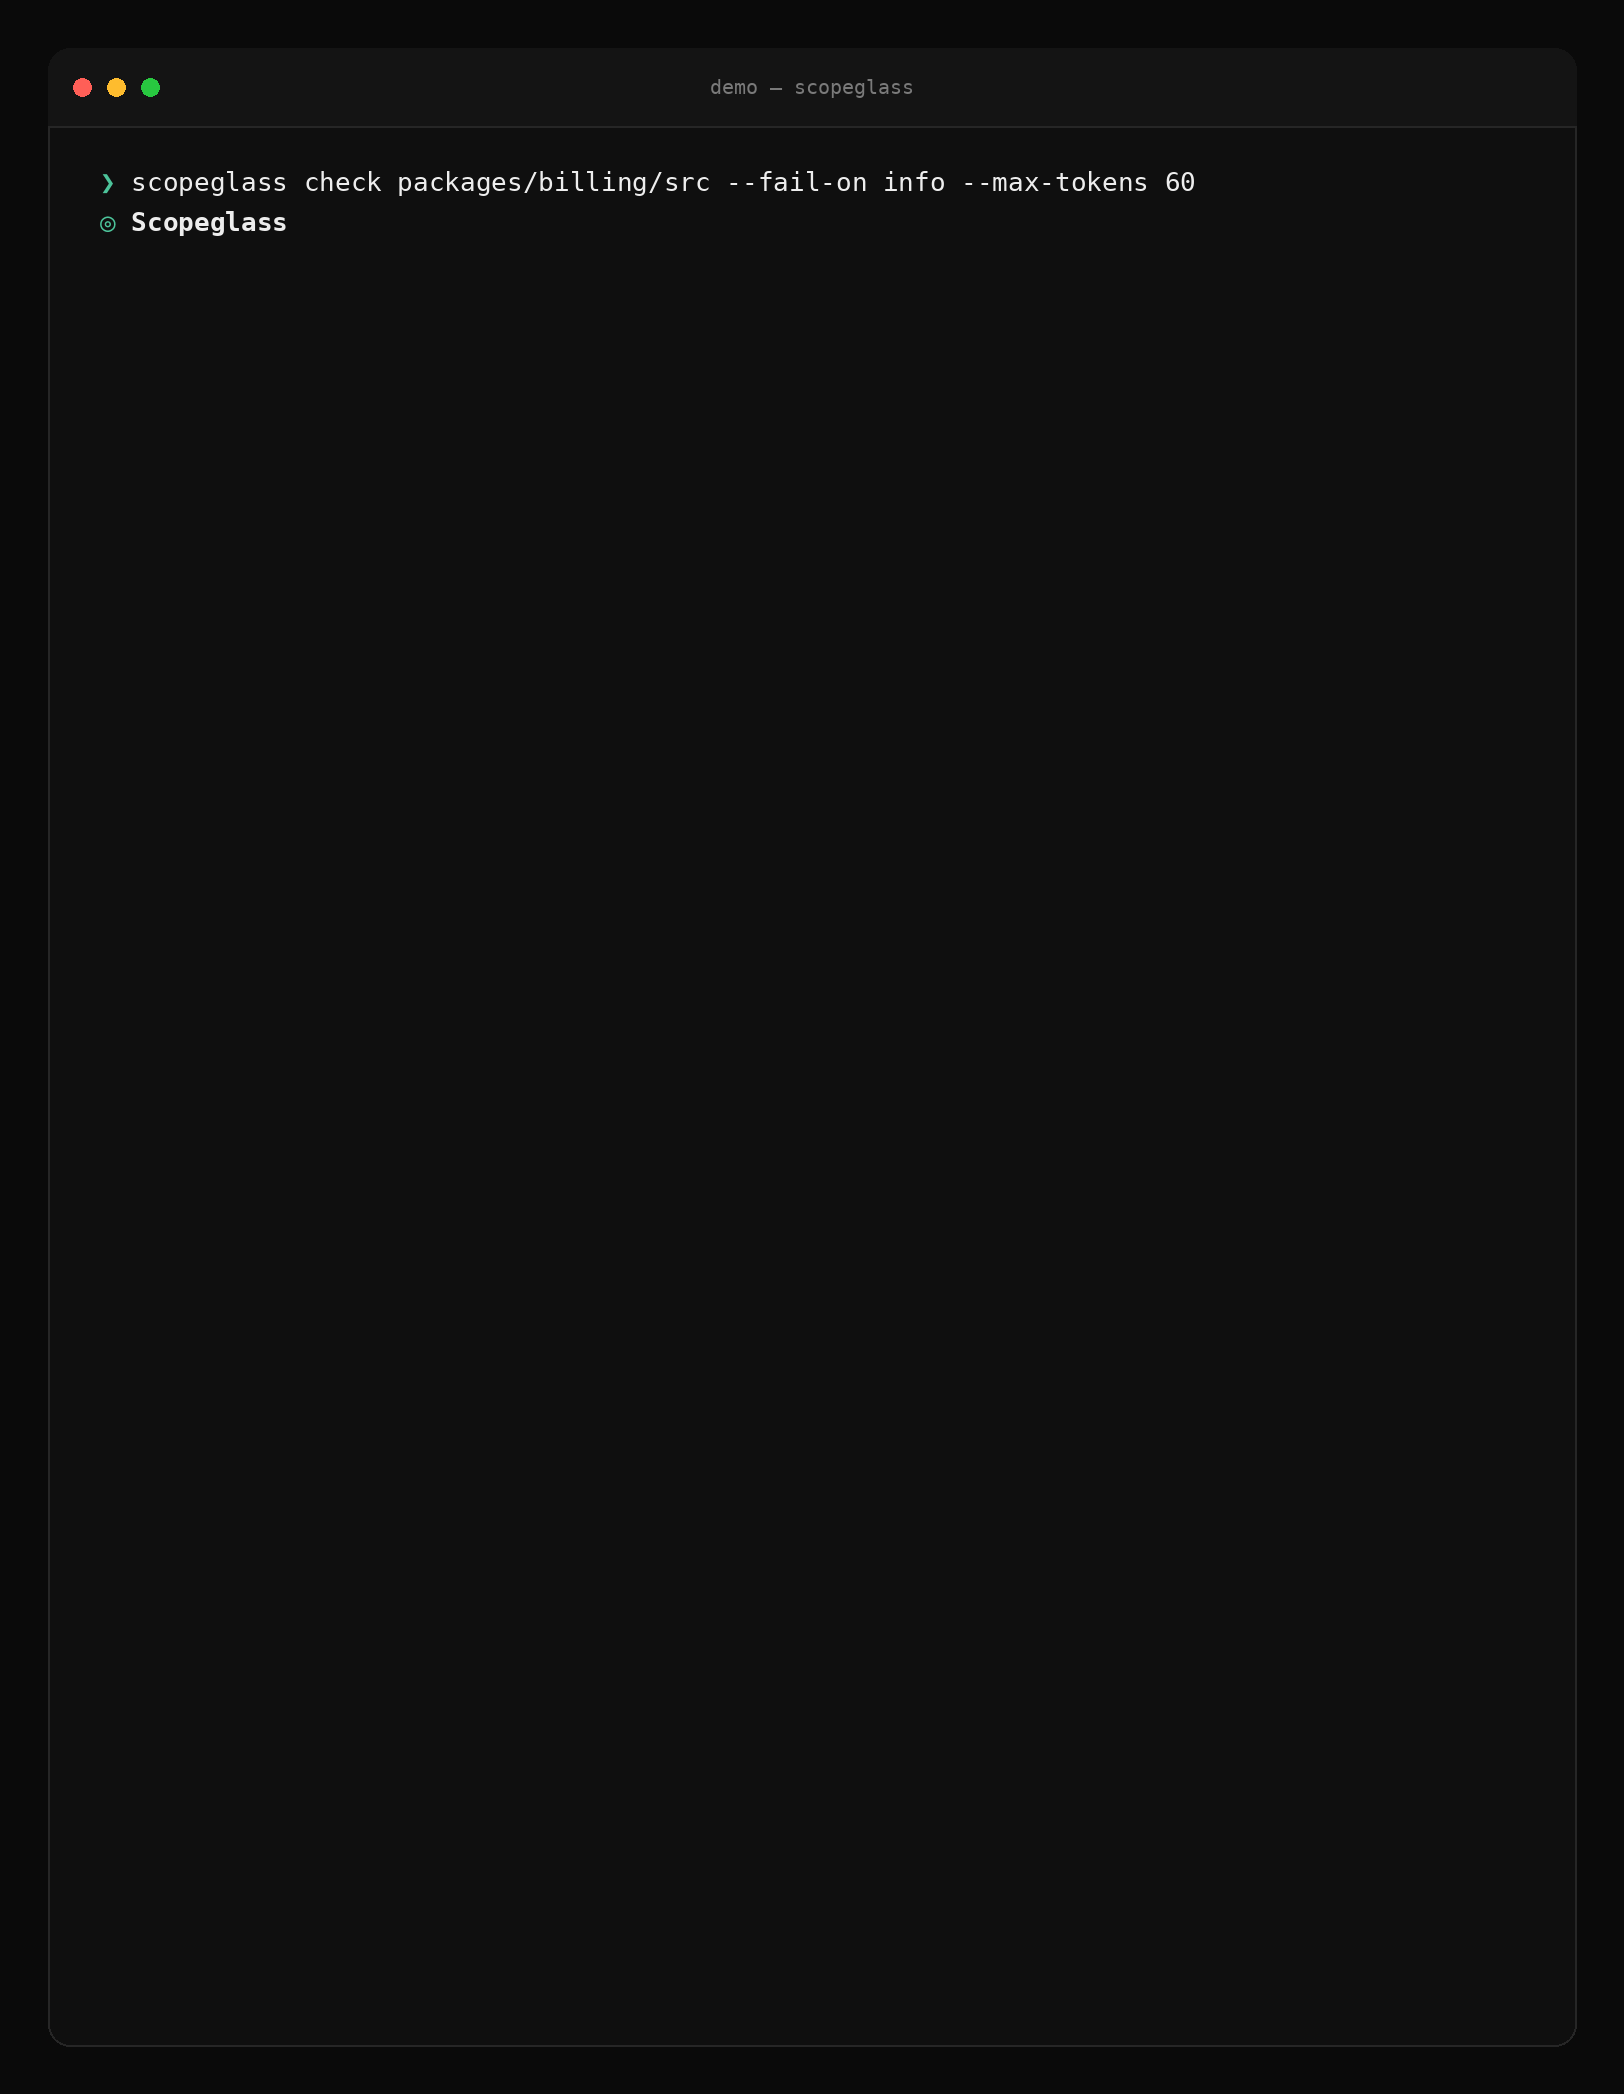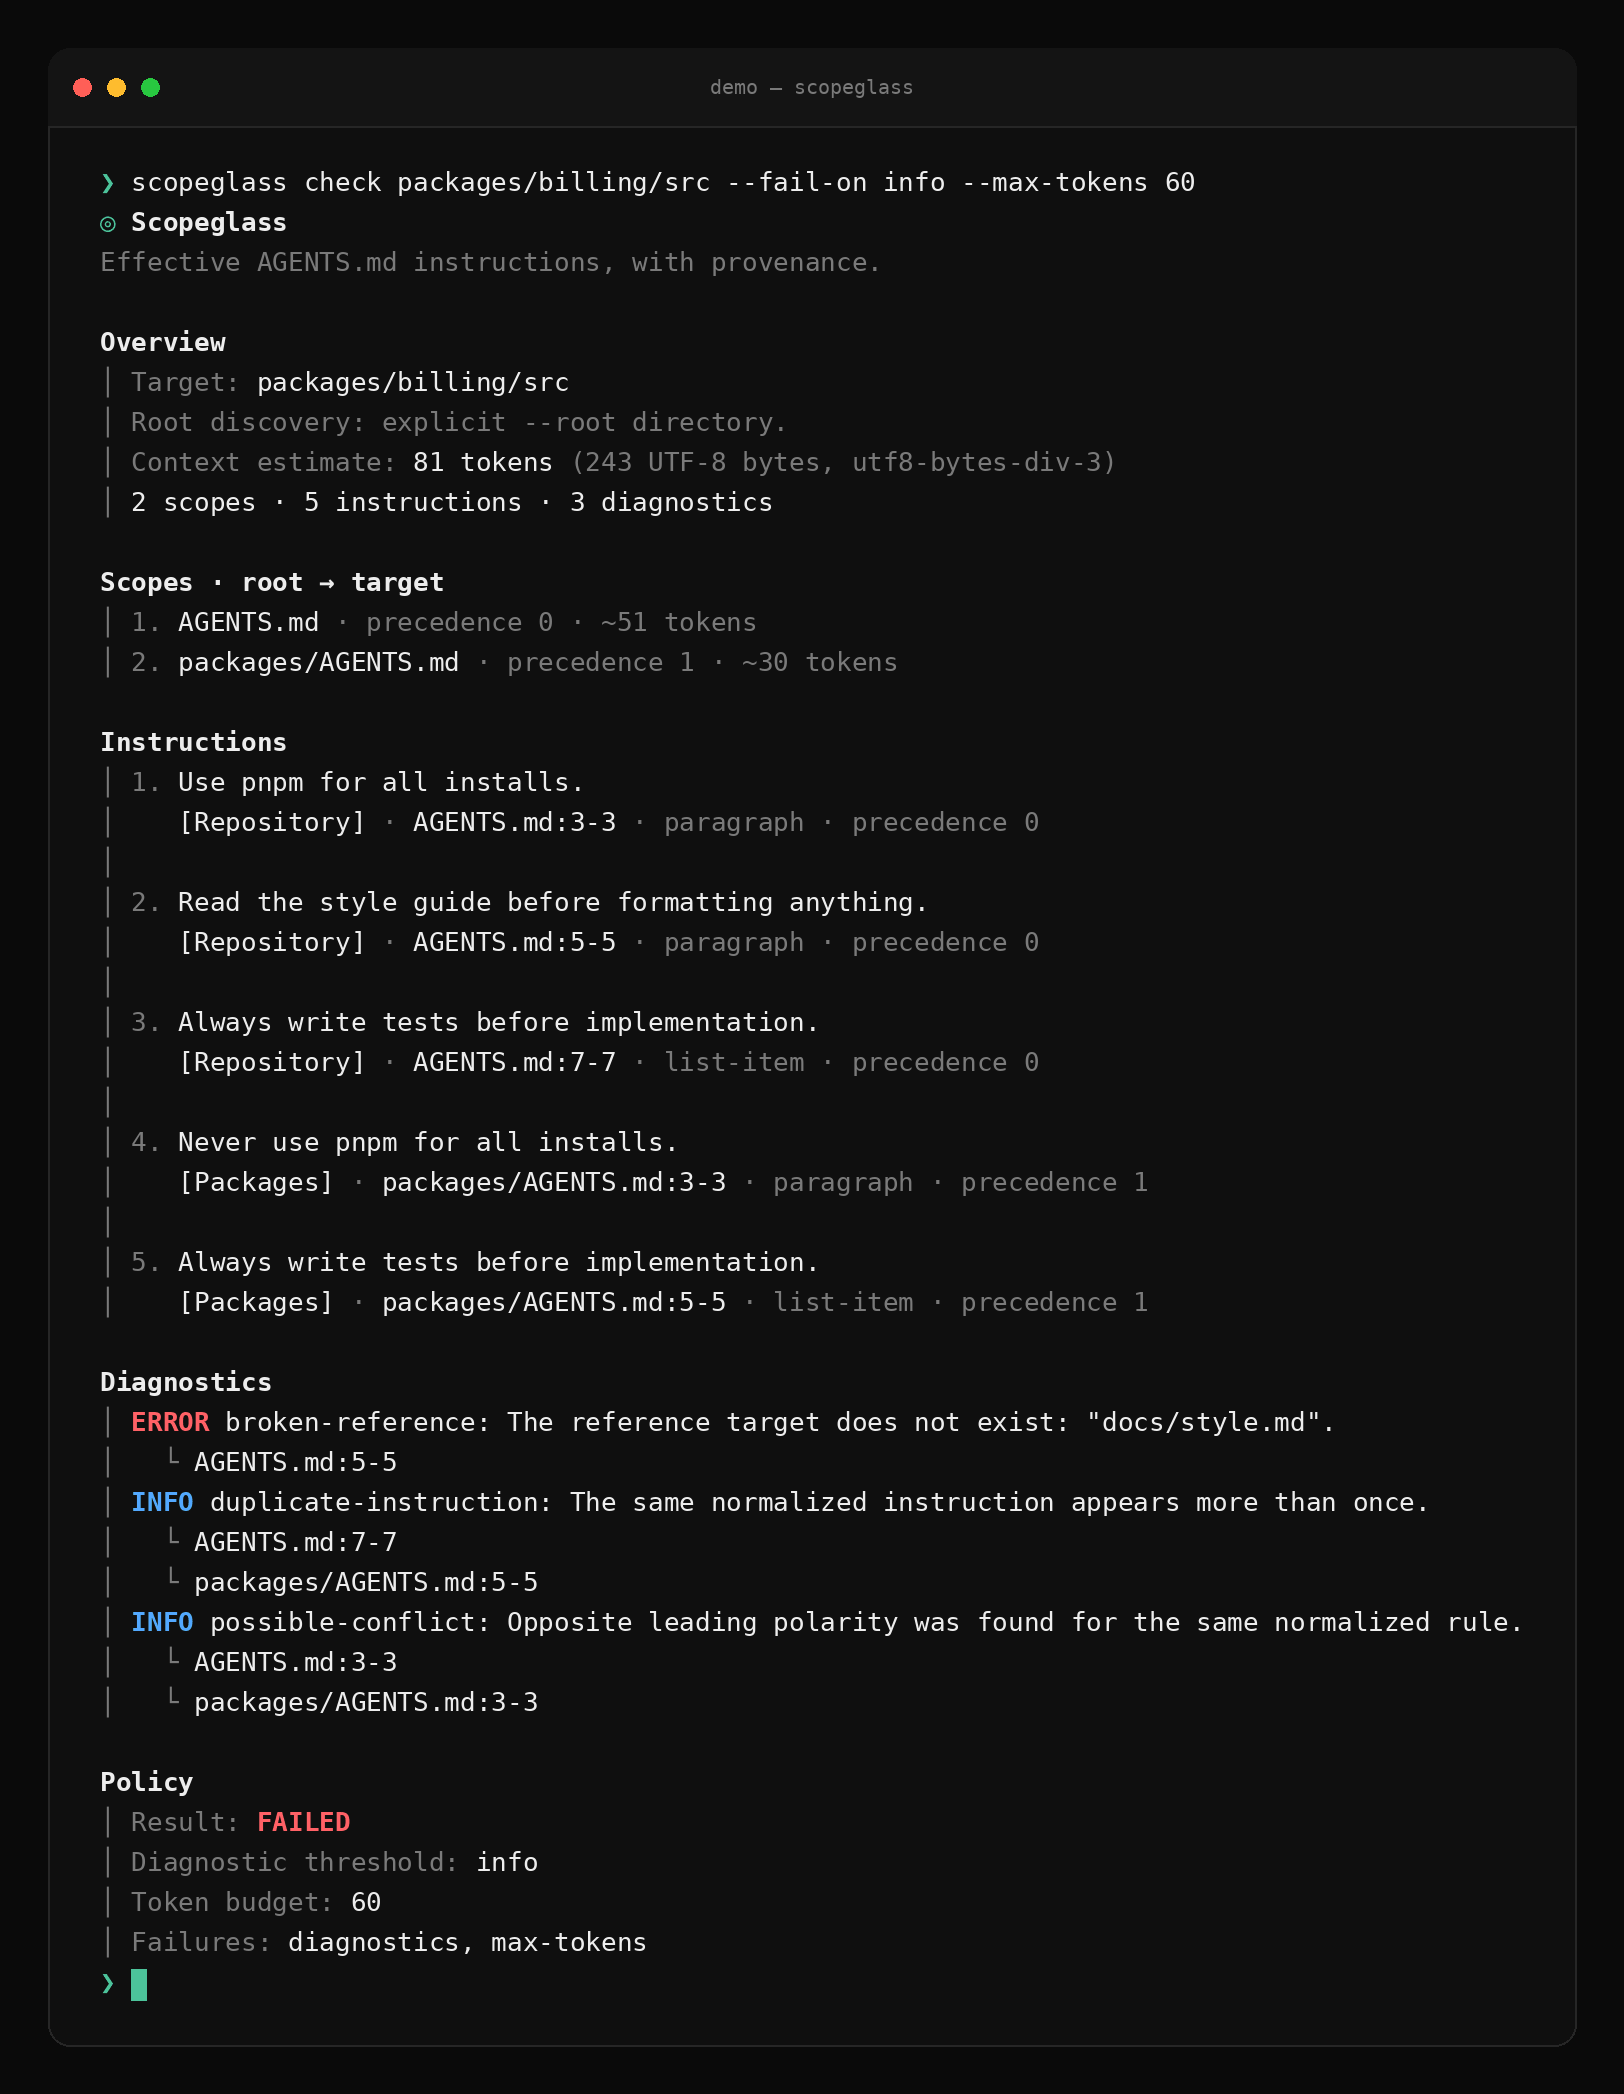
- Redesigned the terminal layout: instruction text leads each entry with section, source, kind, and precedence on a metadata line beneath it; entries are separated by a gutter rule; ordinals align past nine entries; diagnostic sources use tree connectors; and the policy block is separated from the report. Color applies only to Scopeglass-owned structure; repository text stays escaped and unstyled.
Known limitations
- Ruleset v2 can change
checkresults versus v0.1.0 on an unchanged tree — treat this as a gating-behavior bump, not a no-op patch. - Practical input size is bounded by parser-sensitive syntax budgets, not the raw byte limits; exceeding any hard limit is fatal (no diagnostic).
- Local Markdown reference checks resolve relative links from the scope's recorded (display) directory. For a symlinked
AGENTS.md, that is the symlink's directory, not the link target's — by design, matching the reportedscope.path.
Security
Report suspected vulnerabilities privately via GitHub Security Advisories:
https://github.com/zackabrah/scopeglass/security/advisories/new
Verify after install
npm install --global scopeglass@0.2.0
scopeglass --version   # 0.2.0
npm view scopeglass@0.2.0 dist.integrity   # compare with the approved staged candidate
Full changelog: v0.1.0...v0.2.0
Scopeglass v0.1.0
Scopeglass v0.1.0 is the first public release: a local, deterministic way to see every AGENTS.md instruction that applies to a path, in precedence order and with line-level provenance.
Highlights
- Discover the canonical root-to-target
AGENTS.mdscope chain for files and directories, including Git worktree markers. - Extract paragraphs, list items, and blockquotes with source-line attribution.
- Flag broken or unsafe local references, exact duplicate instructions, and conservative possible conflicts.
- Render terminal, versioned JSON, and self-contained static HTML reports.
- Use
inspect,report, and policy-orientedcheckcommands, or the small ESManalyze()API. - Keep repository content local: Scopeglass does not execute, import, fetch, or send repository content off-device.
Install
npm install --global scopeglass
scopeglass --help
For the ESM API and exported JSON Schemas:
npm install scopeglassCompatibility and contracts
- Node.js:
>=22.17.0 - Module format: ESM
- Report schema version:
1 - Diagnostic ruleset version:
1 - JSON Schema: Draft 2020-12
Verified release evidence
- Protected-main commit:
f974745c9602a471152730f5e502a3945b74168a - Package:
scopeglass-0.1.0.tgz(94,620 bytes; 24 files) - SHA-256:
00ae4ec8f9a448a149759906e29d7d6a706655689c7acda5ec824732b9463def - Integrity:
sha512-h+Rw+X9TG+dqQbpU930d17kXoN9FpPSLC5t9KklwiANTNTRDjfKCj1+FHlQkOpkhdQCkG9iBuSW7dO0vOdDfXg== - Protected release workflow
- npm package
- SLSA provenance attestation
The local candidate, preserved GitHub Actions artifact, npm staged tarball, and public registry tarball were compared byte-for-byte before this release was created. Clean registry CLI, API, schema, audit, signature, and provenance checks passed.
Known limits
- Scopeglass reports expected instruction scope; it cannot reveal a vendor's private prompt or prove model compliance.
- Possible-conflict detection is deliberately narrow and does not determine which natural-language instruction semantically overrides another.
- Analysis is local and bounded. See the documented hard limits for scope files, file sizes, instructions, references, Markdown depth, and diagnostics.
Please report security issues privately through GitHub Security Advisories.
See CHANGELOG.md for the complete release record.