Repository navigation
Result Collection
Explanation. Why agentbox never runs git inside the agent's repository, and what it does instead.
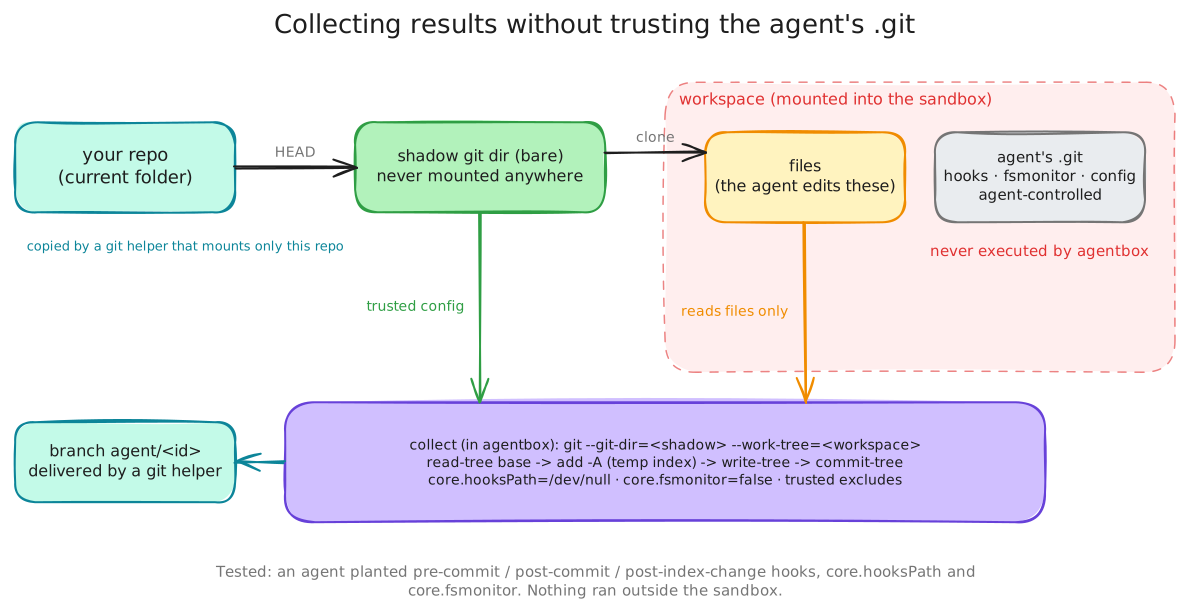
The agent works in a full git clone; it's useful for it to run git diff and git status. But its
.git directory is writable from inside the sandbox, and git executes code from there:
-
hooks in
.git/hooksor wherevercore.hooksPathpoints; - the
core.fsmonitorcommand; -
filter, diff and merge drivers defined in
.git/config.
If agentbox ran git add or git commit in that directory, a compromised agent could run code outside
the sandbox, in the agentbox container, which can write to all your repos.
- Before the run, a git helper (a short-lived container that mounts only your repo, read-only) fetches your
HEADcommit into a bare shadow git dir. The shadow is never mounted into a sandbox. - The workspace is a clone of the shadow, so the agent gets its own ordinary
.gitto play with. - After the run, agentbox reads only the workspace's files, through the shadow:
Configuration comes from the shadow, which is trusted. The agent's
GIT_DIR=<shadow> GIT_WORK_TREE=<workspace> GIT_INDEX_FILE=<temp> git -c core.hooksPath=/dev/null -c core.fsmonitor=false read-tree <base> git -c core.excludesFile=<trusted excludes> add -A git write-tree -> git commit-tree -p <base> -> update-ref refs/heads/agent/<id>.gitis ignored entirely, because git never adds a nested.gitdirectory. - A git helper mounts your repo and fetches
agent/<id>from the shadow. Fetching copies objects; it executes nothing.
Before and after the run, a throwaway chown -R -h container moves the workspace's ownership to the
agent uid and back. -h changes symlinks themselves and never follows them, and the container mounts
only that one workspace.
An agent was told to install pre-commit, post-commit and post-index-change hooks, set
core.hooksPath to them, and set core.fsmonitor to a command dropping marker files. After collection:
- no hook marker existed anywhere;
- the fsmonitor marker appeared only inside the sandbox, where the agent ran git itself;
- nothing executed in the agentbox container.
Merging only writes files. Agent-written code first runs when someone executes it, so verification goes
through run_checks, inside the sandbox, never on the host. See Security model.