WOW64 Split
A 32-bit process and a 64-bit process do not read the same registry view on Windows. The 32-bit side reads the redirected WOW6432Node view. TrustMeBro uses that split to poison 32-bit signature checks while the native 64-bit view stays clean.
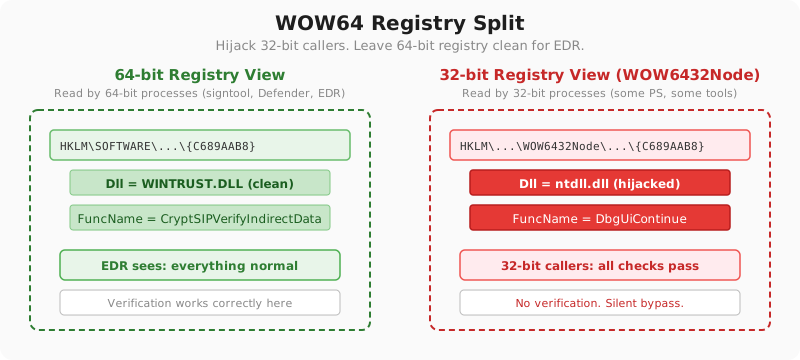
Default SIP hijack writes both registry views. --wow64-only writes only the 32-bit view:
- Native 64-bit path:
HKLM\SOFTWARE\Microsoft\Cryptography\OID\EncodingType 0\CryptSIPDllVerifyIndirectData\{GUID}
- WOW64 path:
HKLM\SOFTWARE\WOW6432Node\Microsoft\Cryptography\OID\EncodingType 0\CryptSIPDllVerifyIndirectData\{GUID}
Result:
- 32-bit callers of
WinVerifyTrusthit the hijacked SIP entry. - 64-bit callers still hit the original registry entry.
- 64-bit EDR or admin tooling that inspects only the native hive sees no SIP hijack.
After a --wow64-only install, native 64-bit Get-AuthenticodeSignature returned HashMismatch while 32-bit PowerShell returned Valid. Only HKLM\SOFTWARE\WOW6432Node\... changed. A 64-bit EDR that reads the native view sees no hijack.