Repository navigation
From Request to SQL
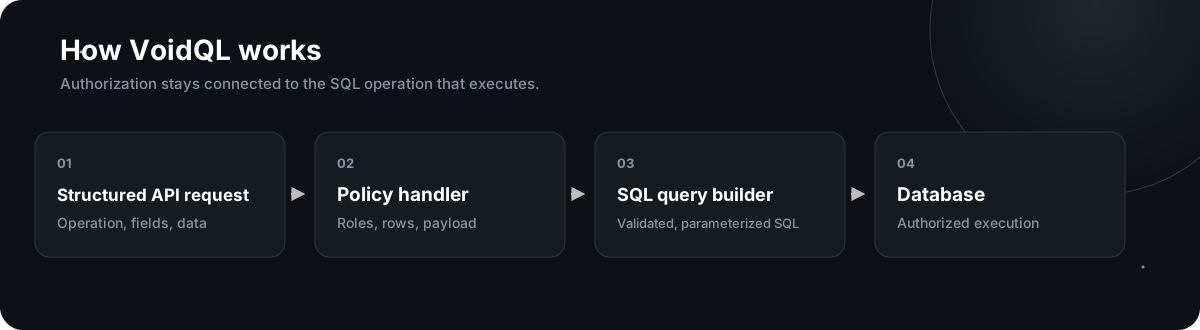
query.table selects an entry from the Structure. query.type selects the corresponding endpoint. Missing tables, endpoints, or role entries are rejected.
VoidQL reads allowed/allow and disallowed/deny from the selected role. It validates requested fields against the table map and applicable endpoint policy.
The request's where clause is combined with policy-derived conditions. Policy conditions are not a post-query filter: they participate in the built database operation.
Values such as $user, $data, column references, and trigger-stage values are resolved using the current request context.
The current implementation executes a single built query inside db.transaction. Before triggers run first; the selected GET, POST, PUT, or DELETE operation follows; after triggers run last.
Calling compile produces a plan with execute(). A single request returns { ok, data } or { ok: false, error }. Phase requests return nested phase results.