Live Demo State
This page is a durable record of the three live objects the Tier 2 demo provisions in the demo tenant (MngEnvMCAP675646.onmicrosoft.com, aa93b9d9-037d-4f08-a26d-783cff0e2369). Capture it before any teardown so the exact live state is preserved. Every object here is reversible with the scripts listed at the end.
Captured 2026-07-06 while signed in as admin@MngEnvMCAP675646.onmicrosoft.com.
| Object | Identifier | Live value | Reverses with |
|---|---|---|---|
| Replay gate (App Service setting) |
Demo__EnableReplay on croesus-api
|
true |
teardown-app-registrations.sh (resets to false) |
| Conditional Access policy | 9c213f84-601b-4fb9-8366-a3828d9e4ede |
report-only, enabled | teardown-ca-policy.sh |
| SPA to Graph delegated grant | oauth2PermissionGrant kMoYHyDjs0GSyifXhf5Q6OrnkKCBIgVMnFXPmDBqesU
|
User.Read granted |
teardown-app-registrations.sh (revokes grant) |
The provisioning state file .demo-state.json (git-ignored, local to the operator) records the grant id and policy id that the teardown scripts read:
{
  "spaGraphGrant": "kMoYHyDjs0GSyifXhf5Q6OrnkKCBIgVMnFXPmDBqesU",
  "caPolicyId": "9c213f84-601b-4fb9-8366-a3828d9e4ede"
}The gated Tier 2 replay endpoint (POST /api/replay) is mapped only when this setting is true. Captured live via ARM:
[
  {
    "name": "Demo__EnableReplay",
    "slotSetting": false,
    "value": "true"
  }
]
Reproduce: az webapp config appsettings list -g rg-croesus -n croesus-api --query "[?name=='Demo__EnableReplay']" -o json.
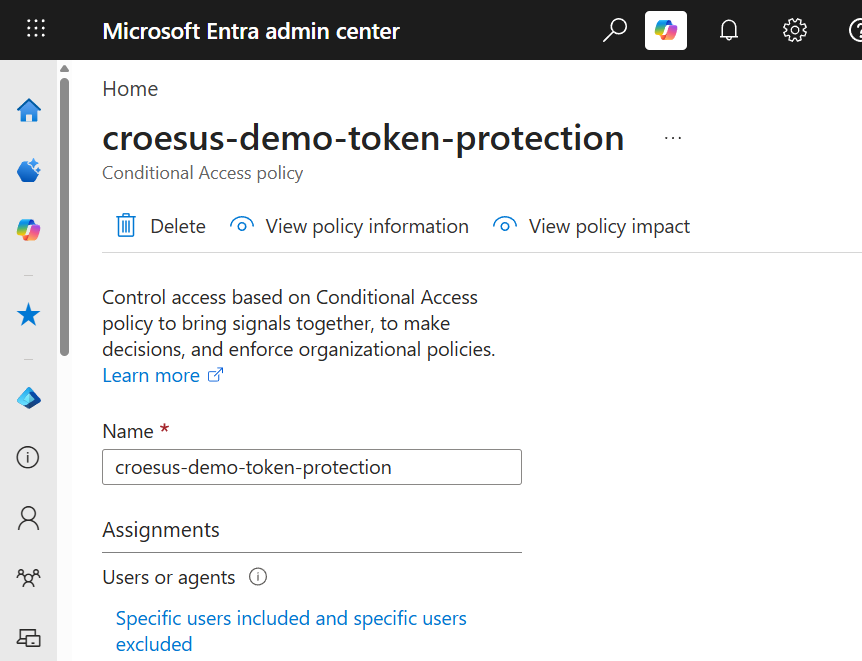
The report-only policy that surfaces the Token Protection evaluation into the sign-in logs.
- displayName:
croesus-demo-token-protection - id:
9c213f84-601b-4fb9-8366-a3828d9e4ede - state:
enabledForReportingButNotEnforced(report-only, does not block) - sessionControls.secureSignInSession.isEnabled:
true(Require token protection for sign-in sessions) - conditions.clientAppTypes:
["mobileAppsAndDesktopClients"] - conditions.platforms.includePlatforms:
["windows", "macOS", "iOS"] - conditions.applications.includeApplications:
["00000002-0000-0ff1-ce00-000000000000"](Office 365 Exchange Online) - conditions.users.includeUsers:
["54119dd2-572f-4f40-ac16-0c6fb419f24f"](single scoped test user) - conditions.users.excludeUsers:
["b785230a-4af4-418a-acd9-aea99894d37a"](break-glass exclusion)
The authoritative definition lives in scripts/provision-ca-policy.sh. Portal confirmation:
Reproduce the JSON (requires an interactive Graph token): az rest --method GET --uri "https://graph.microsoft.com/beta/identity/conditionalAccess/policies/9c213f84-601b-4fb9-8366-a3828d9e4ede".
To let the SPA acquire a real Graph token and forward it to POST /api/replay, the demo adds a delegated User.Read grant for the SPA against Microsoft Graph (oauth2PermissionGrant id kMoYHyDjs0GSyifXhf5Q6OrnkKCBIgVMnFXPmDBqesU). Portal confirmation of the SPA app permissions:
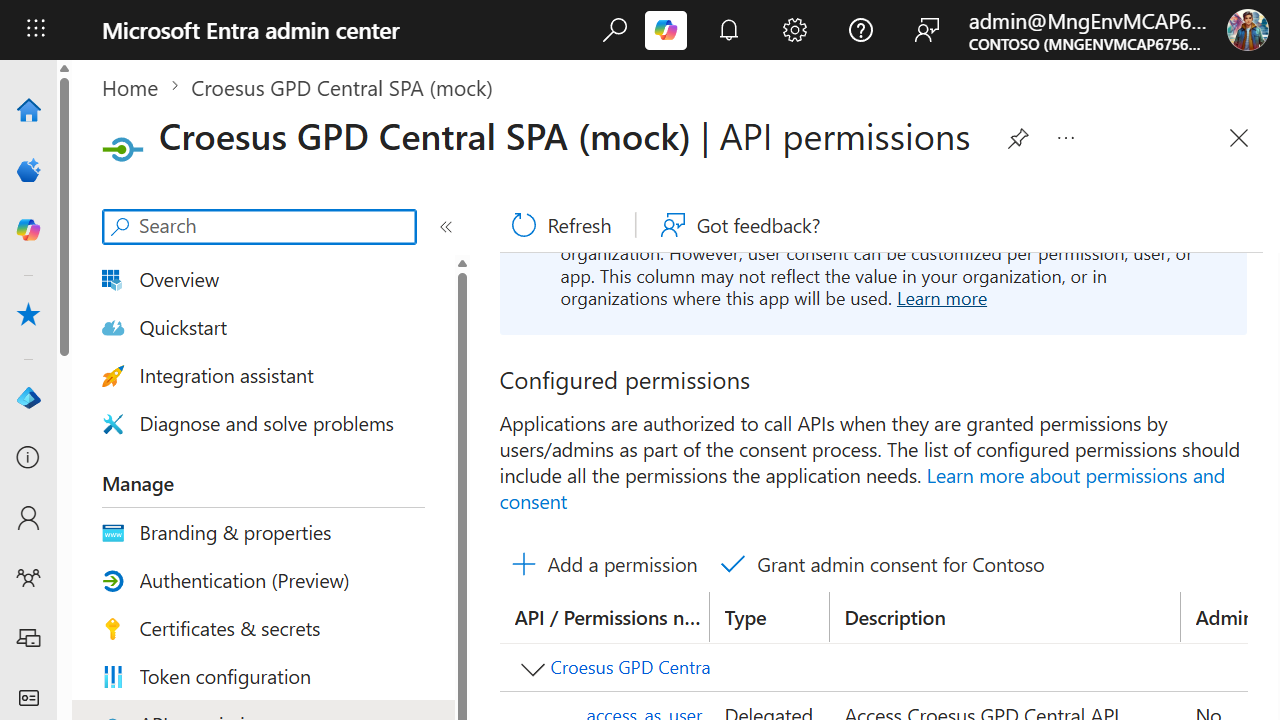
- SPA application: Croesus GPD Central SPA (mock), appId
06ef7c0a-9df3-4bcd-8b6f-ee275ca0adc2 - API resource: Croesus GPD Central API (mock), appId
bc6338a5-a02a-4ddf-b1f4-9a9234bed8a8, delegated scopeaccess_as_user - Added grant: Microsoft Graph
User.Read(delegated)
Every object above reverses cleanly. Run from the repository root:
-
scripts/teardown-ca-policy.sh deletes the CA policy by recorded id, with a
croesus-demo-prefix sweep as a fallback. -
scripts/teardown-app-registrations.sh revokes the SPA-to-Graph delegated grant, resets the live
Demo__EnableReplaysetting tofalse, and removes thereplay-labfederated credential. It does not delete any pre-existing registration. - scripts/verify-clean.sh is read-only and exits non-zero if any residue remains.
Preserve .demo-state.json until teardown: the scripts read the grant id and policy id from it.