Token Protection 1008 Evidence
This page captures reproduction proof of the Conditional Access Token Protection "unbound / 1008" signal — the same signature the customer (Desjardins) reported for the second, non-interactive sign-in arriving from the Croesus AWS backend.
Token Protection records a TokenProtectionStatusDetails object on the sign-in event with a signInSessionStatus (bound or unbound) and a signInSessionStatusCode:
-
0= bound: the token is cryptographically tied to the device (device-bound refresh token / PRT). -
1008= unbound: "the request is unbound because the client isn't integrated with the platform broker, such as Windows Account Manager (WAM)." A process that presents a bearer token without device/broker binding evaluates as unbound — exactly the shape attributed to a server-side token replay.
Sign-in logs for the Croesus demo application show both states on the same user and source IP — a device-bound sign-in (code 0) and an unbound sign-in (code 1008):
| Time (UTC) | User | App to resource | IP | signInSessionStatus | code |
|---|---|---|---|---|---|
| 2026-07-06T20:59:42Z | emknafo@microsoft.com | Croesus GPD Central SPA (mock) to Croesus GPD Central API (mock) | 172.200.70.89 | bound | 0 |
| 2026-07-06T21:29:54Z | emknafo@microsoft.com | Croesus GPD Central SPA (mock) to Croesus GPD Central API (mock) | 172.200.70.89 | unbound | 1008 |
The bound baseline (code 0) versus the unbound line (code 1008) is the reproduction of the customer's reported signature.
Microsoft Entra admin center, Sign-in logs, filtered on Token Protection - Sign In Session StatusCode equals 1008. The single matching interactive sign-in is the Croesus demo flow.
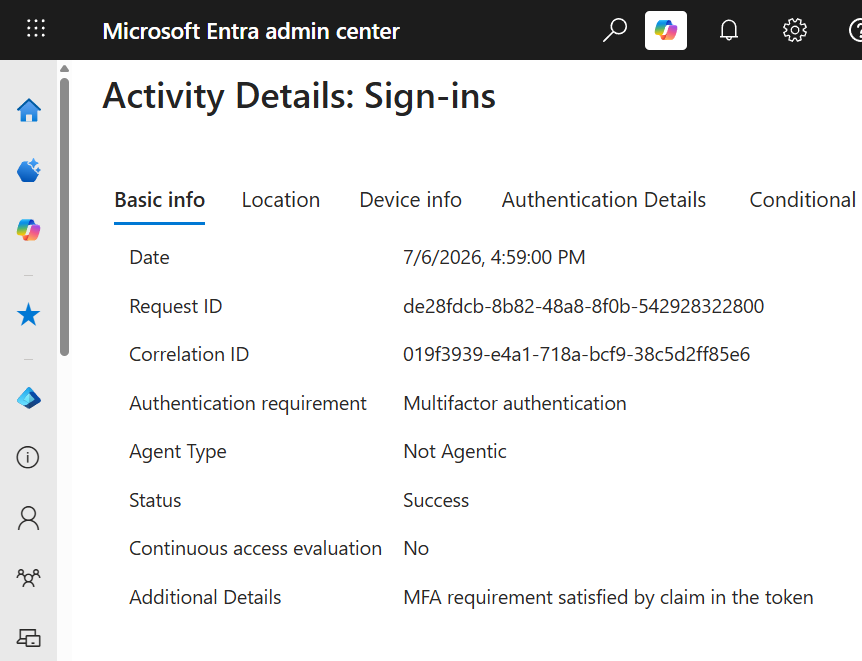
The sign-in event basic info (date, request id, correlation id, status):
The identity: guest user Emmanuel Knafo (emknafo@microsoft.com, B2B collaboration) signing in to the Croesus app:

The Token Protection verdict on the resource leg — Unbound (statusCode: 1008) — against resource Croesus GPD Central API (mock) (bc6338a5-...) in the demo tenant (aa93b9d9-...), from a Browser client:

This is the same unbound / 1008 signal the customer reported, captured live in the Entra portal for the Croesus reproduction.
Run against the croesus-law Log Analytics workspace (Entra sign-in logs are streamed via a diagnostic setting):
SigninLogs
| where TimeGenerated > ago(3d)
| where AppDisplayName startswith "Croesus"
| extend tp = parse_json(TokenProtectionStatusDetails)
| project TimeGenerated, UserPrincipalName, AppDisplayName, ResourceDisplayName,
          IPAddress, ResultType,
          bind = tostring(tp.signInSessionStatus),
          code = tostring(tp.signInSessionStatusCode),
          CorrelationId
| order by TimeGenerated asc
Filter to just the unbound signal:
SigninLogs
| where TimeGenerated > ago(7d)
| extend tp = parse_json(TokenProtectionStatusDetails)
| where tostring(tp.signInSessionStatusCode) == "1008"
| project TimeGenerated, UserPrincipalName, AppDisplayName, ResourceDisplayName, IPAddress
Also inspect non-interactive sign-ins (the leg attributed to the server-side replay):
AADNonInteractiveUserSignInLogs
| where TimeGenerated > ago(7d)
| where isnotempty(TokenProtectionStatusDetails)
| extend tp = parse_json(TokenProtectionStatusDetails)
| where tostring(tp.signInSessionStatusCode) == "1008"
| project TimeGenerated, UserPrincipalName, AppDisplayName, ResourceDisplayName, IPAddressA Conditional Access policy croesus-demo-token-protection is provisioned in report-only mode so it surfaces the token-binding evaluation into the sign-in logs without blocking anyone:
- state:
enabledForReportingButNotEnforced(report-only) - session control:
secureSignInSession.isEnabled = true(Require token protection for sign-in sessions) - client app types:
mobileAppsAndDesktopClients - platforms: windows, macOS, iOS
- resource: Office 365 Exchange Online
- scoped to a single test user with a break-glass exclusion
The policy is created and torn down by scripts/provision-ca-policy.sh and scripts/teardown-ca-policy.sh (reversible).
- The unbound (1008) line is the fingerprint of a token that is not device/broker bound — the behavior of a server-side replay of a user token.
- The correct pattern (On-Behalf-Of) mints a fresh, audience-bound token from a confidential client, which does not present as an unbound replay. See API reference for the live
/api/me(OBO) and gated/api/replayoperations.
Microsoft Entra admin center to Monitoring to Sign-in logs to the flagged entry to Basic info to "Token Protection - Sign In Session" (shows Bound or Unbound with the status code). Filter by application "Croesus GPD Central SPA (mock)" and the timestamps above.