Repository navigation
Execution Print
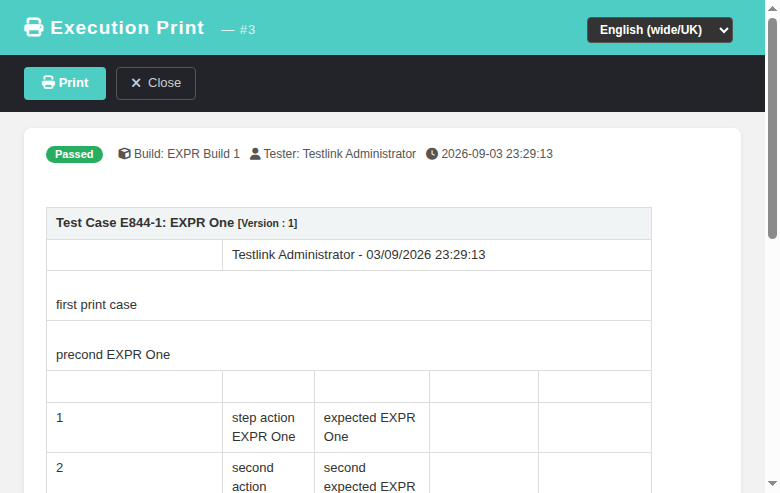
Modernization of the legacy Execution Print popup (lib/execute/execPrint.php), which renders
a printable document for a single execution row: the linked test-case definition (summary, author,
importance, preconditions, steps with execution results/notes, custom fields, keywords,
requirements), overall execution status, build, tester, dates and the direct-linked public
execution URL. GitHub issue #844.
Replaced by a standalone Dashio page gui/templates/execute/execPrint.html backed by a plain-PHP
REST BFF API api/executionprint/index.php.
Path: Execute Tests (execTest.html) or Execution History (execHistory.html) → execution row →
Print → popup.
URL: gui/templates/execute/execPrint.html?id=<execution_id>
BFF API:
-
GET ?action=print&id=N→{ status, exec_id, page_title, body_html, meta{status, execution_ts, build_name, tester, tproject_id, tplan_id} } -
POST ?action=delete_attachment&id=N&deleteAttachmentID=M→{ status, deleted, exec_id }(destructive action — POST only, same-origin-guarded; ownership-checked against the execution's own attachment list)
Rights: authenticated session + testplan_execute on the owning test project (403 otherwise);
unknown / forged execution id → 404 (probed before render, no E_WARNING events).
-
Print body — generated server-side by
lib/functions/print.inc.phprenderExecutionForPrinting()(the exact functionexecPrint.phpcalled): test-case header table, author/date, summary, preconditions, step table with execution-notes + execution-status columns, execution type/duration, execution notes, and theDirect Link:share URL.setPaths()guarantees$_SESSION['basehref']for the renderer. - Meta line — status badge (passed/failed/blocked/not-run), build name, tester, timestamp above the print body.
-
Print — toolbar Print →
window.print(); print CSS hides header/toolbar/footer. -
Attachment delete — the legacy render embeds an inline
<form>per execution-step attachment (POSTdeleteAttachmentIDtoexecPrint.php). The modern screen intercepts the submit in JS and routes it through the BFFdelete_attachmentroute, then re-renders.
Legacy execPrint.php opened testlinkInitPage($db,false,true) — callable without a session for
the external-direct-link use case. The modern screen runs inside the authenticated app, so the BFF
requires a session user + testplan_execute. The public anonymous share link (lnl.php)
intentionally keeps using legacy execPrint.php.
Test suite 844 (12/12 PASS) in tmp/TLU_Test_Cases.md — BFF print OK (200 + body), 404 unknown
execution, 400 missing id, 403 no-rights, front-end render + 404/403 banners, Print handler,
delete_attachment guards, i18n in all 10 bundles, in-app link switch, Event Viewer clean.