Repository navigation
Modernize Execution Notes execNotes
TestLink 2.0.1 modernization — issue 1551.
Update (#1807, bug #1808) — the read-only half of this pair was NOT covered by #1551 and has since been modernized separately:
lib/execute/getExecNotes.phpauthorized nothing but a session (no right, no ownership), so any authenticated user — role 3<no rights>included — could read the notes of any execution on any test project by enumerating?exec_id=, and it rendered the stored RichEdit blob through the web editor. It is now the read-only viewerexecNotesReadonly, backed byapi/execnotesreadonly/index.php, and this editable screen is the "Open editable notes" target it links to.
The legacy two-screen Execution Notes flow — lib/execute/execNotes.php (edit) and lib/execute/getExecNotes.php (readonly view) — is modernized as a single standalone Dashio screen backed by a REST BFF (gui/templates/execute/execNotes.html + api/execnotes/index.php).
The TODO section of docs/MODERNIZATION-STATUS.md is empty: every ASIDE entry was already verified to map to a modern screen + BFF. Per the modernize.yml guidance (if the TODO section is empty, say so in one line, then pick the smallest coherent one), the Execution Notes flow was chosen — the last lib/execute/* controller pair with no dedicated modern screen.
- Screen: Dashio popup, teal header, execution meta card (test case / test plan / build / platform / localized status / executed-on), readonly notes box, Edit toggle with Save/Cancel, empty state, missing-
exec_idaccess-denied card, toast feedback. - BFF
api/execnotes: GET/PUT/{exec_id}with session auth +bffSameOriginGuard(401 anon / 403 CSRF / 404 unknown exec); status charp/f/bmapped client-side toexecprint.status{Passed,Failed,Blocked}. -
Server-side rights (IDOR guard): each route resolves the execution's
testplan_id→testproject_idand enforces legacy rights viatlUser::hasRight— view =exec_edit_notesORexec_ro_accessORtestplan_execute; edit =exec_edit_notes. Denied → 403. - i18n:
execnotes.*(15 keys) in all 10 locale bundles. - Link switch
$actions->execNotesViewinlib/functions/common.php(execute area, afterexecExport,tplan_id > 0).

Execution 4 — test case Case With Notes, plan Plan EXN, build v1.0, platform Win11, status Passed, notes box filled.
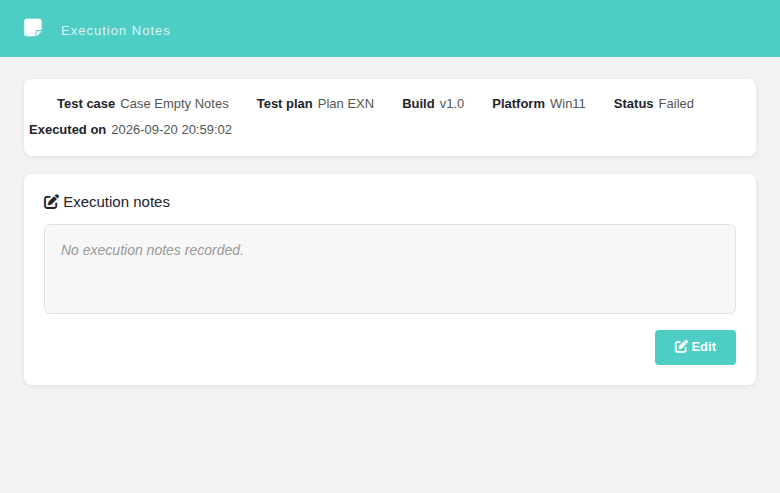
Execution 5 — empty state \No execution notes recorded.\ (status Failed shown in meta).

Edit / Save form with textarea and Cancel + Save buttons.
- Browser (admin session): view with existing notes, Edit → Save → toast \Notes saved.\ + reload, empty-notes state, missing id → access-denied card; console clean (0 error/warn).
- BFF curl contract: 401 anon GET/PUT, 403 CSRF without same-origin proof, 403 rights (role-3 user on GET and PUT), 404 unknown exec, 200 + persistence round-trip.
- Event Viewer clean after the run (AUDIT only, 0 ERROR/WARNING).
Suite 1551 (11 cases) in tmp/TLU_Test_Cases.md — full pass.