Repository navigation
Edit Execution
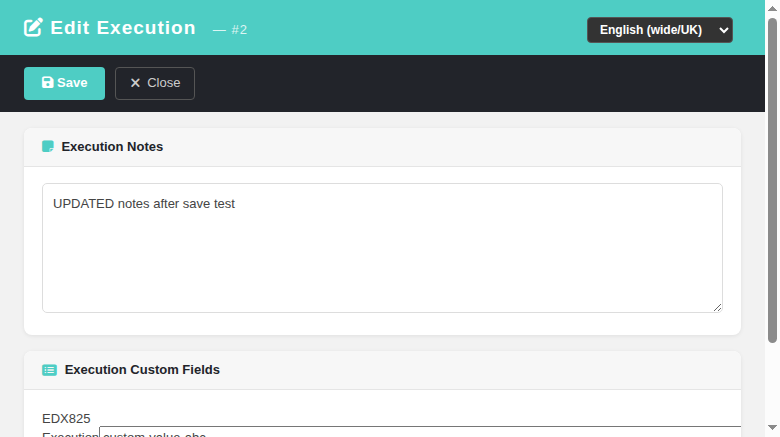
Modernize the legacy Edit Execution popup (lib/execute/editExecution.php) — a tester edits
the execution notes and the execution-level custom fields of an already-recorded execution.
GitHub issue #825.
Replaced by a standalone Dashio page gui/templates/execute/editExecution.html backed by a
plain-PHP REST BFF API api/executionedit/index.php.
Path: Execute Tests (execTest.html) or Execution History (execHistory.html) → execution row →
edit-notes (pencil) icon → popup.
URL: gui/templates/execute/editExecution.html?exec_id=<id>&tproject_id=..&tplan_id=..
BFF API:
-
GET ?action=init&exec_id=N→{ exec_id, tcversion_id, tplan_id, tproject_id, notes, can_edit, build_is_open, exec_cfields_html, exec_cfields } -
POST ?action=update(JSON body{ exec_id, notes, custom_field_* }) →{ status, updated }
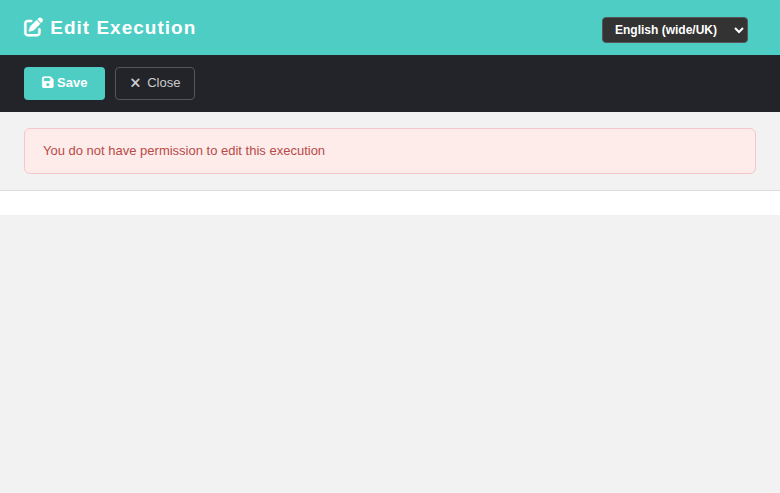
Rights: testplan_execute AND exec_edit_notes — both required (legacy checkRights());
a tester that can execute but not edit notes gets 403.
-
Notes via
get_execution()+updateExecutionNotes(). -
Execution custom fields rendered through the same legacy helper as the old popup
(
html_table_of_custom_field_inputs(tcversion_id, null, 'execution', '_cf', exec_id, tplan_id, tproject_id)), name contractcustom_field_<type>_<id>_<tcaseId>preserved; persisted viacfield_mgr->execution_values_to_db(). - Forged CF names (type,id) not linked to the TC version are ignored.
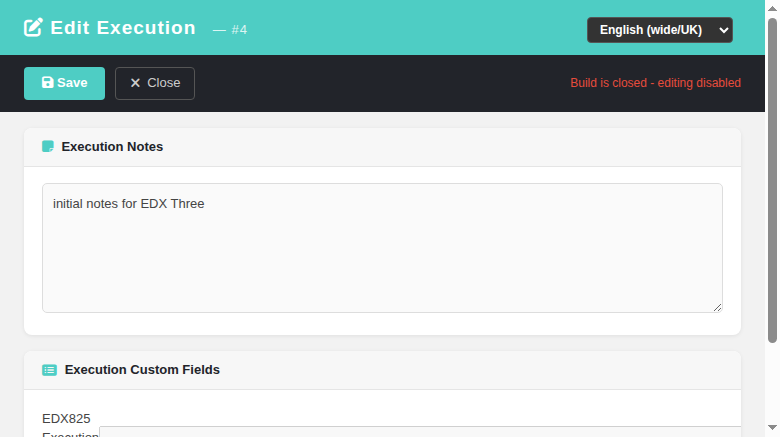
- Closed build → editor read-only (Save disabled), update route 400.
Suite 825 (12/12 PASS) in tmp/TLU_Test_Cases.md. One bug found & fixed during the run:
the popup loaded jQuery from a non-existent local path (/gui/javascript/jquery-1.8.3.js, 404 →
$ is not defined killed the page); fixed to the CDN https://code.jquery.com/jquery-3.6.0.min.js
(same as execSetResults.html / execTest.html).
The modern screen + BFF built for #825
were already live, but lib/execute/editExecution.php was still a full Smarty renderer: a
hand-typed deep link (or the legacy openExecEditWindow() helper) opened the old 1.9.20 popup.
#1911 closes that gap.
lib/execute/editExecution.php is now a session-guarded, non-mutating launcher:
-
Anonymous →
checkSessionValid()bounces to the login screen preserving the destination. -
Authenticated browser navigation (
GET/HEAD,Sec-Fetch-Dest: documentorAccept: text/html) → 302 togui/templates/execute/editExecution.htmlpreservingexec_id,tcversion_id,tplan_id,tproject_id. -
Any write verb (
POST doAction=doUpdate) or non-document/XHR caller → 405modern_endpoint_only(writes only via/api/executionedit/index.php?action=update). - Scalars are
is_scalar-guarded against?exec_id[]=…E_WARNING.
openExecEditWindow() in gui/javascript/testlink_library.js now targets the modern screen.


Tests: Suite Issue #1911 (26/26 PASS) appended to tmp/TLU_Test_Cases.md.