Repository navigation
Domain Persistence
Purpose: Once Domain Admin (or equivalent) is achieved, this checklist covers ways to keep that access alive through password rotations, incident response, and partial remediation - the difference between a compromise that's fixed by resetting one password and one that requires a full domain rebuild to be certain it's gone. Every item here is specifically an AD-native persistence mechanism, not a general Windows backdoor.
Function: Entries span a spectrum of stealth and durability: Golden Certificate and Golden Ticket forge Kerberos trust material directly from the krbtgt/CA keys, surviving individual password resets; AdminSDHolder and machine account abuse hijack legitimate AD protection mechanisms to silently maintain privileged group membership; Shadow Credentials and Diamond Ticket are additional paths defenders should inventory; detectability depends on implementation, telemetry, and environment, so validate detection notes against your own lab and data.
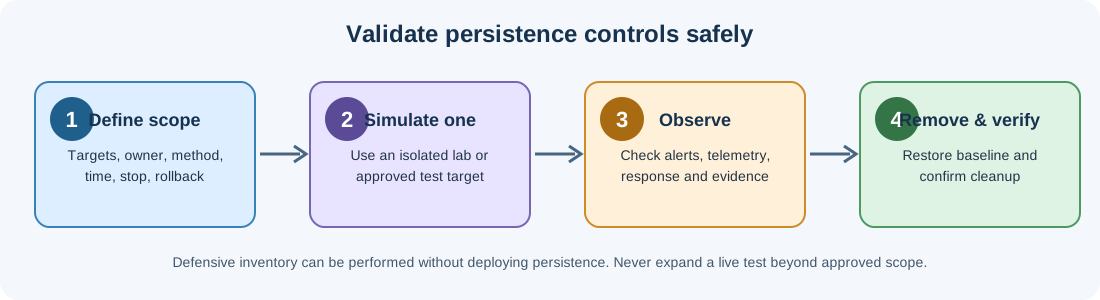
Goal: Help defenders inventory domain persistence paths and validate recovery coverage. In an explicitly approved exercise, simulate only the minimum needed to test detection and remediation, preferably in an isolated lab or dedicated test domain, with a documented rollback and cleanup check.
When & how to use this: Use once you already hold Domain Admin or equivalent rights, as the natural next step after Domain Escalation. For a red-team exercise, use an isolated lab or a specifically approved simulation with explicit target, technique, duration, rollback, and cleanup criteria. Do not treat deployment of multiple live persistence mechanisms as a default test step. During defensive work, use this as your "did we actually get all of it" checklist after any AD compromise.
📖 Full deep-dive with detection/defense guidance: Tradecraft/active-directory.md
📄 PDF references: AD_Attacks_.pdf · AD_Post_Exploitation.pdf
| Code | Technique | Mitre |
|---|---|---|
| DP-01 | Golden Certificate | NA |
| DP-02 | AdminSDHolder | NA |
| DP-03 | Golden Ticket | NA |
| DP-04 | DCShadow | NA |
| DP-05 | Machine Account | NA |
| DP-06 | Shadow Credentials | NA |
| DP-07 | Diamond Ticket | NA |
📖 Use These Checklists Responsibly: Authorization is MANDATORY
Attack techniques are powerful - use them ethically and legally.
Repository: ULTIMATE CYBERSECURITY MASTER GUIDE
Maintained by: Pacific Northwest Computers
⭐ Star this repo if you find it useful! ⭐
📄 Source: Checklists/Domain-Persistence.md | ✏️ Suggest an edit | ⬅️ Back to Checklists