Repository navigation
Web App Security
Methodology, OWASP Top 10, and tooling for authorized web application security assessment
Part of the ULTIMATE CYBERSECURITY MASTER GUIDE


Related application security references: OWASP Cheat Sheet Series, awesome-appsec and the PNWC source map.
External developer docs: Older web-vulnerability examples: Cypherpunk toolkit curation links the archived SQLi/browser/HTTP exercises as history; use current OWASP testing standards for assessments.
Beautiful Docs-derived reference index links to FastAPI and Django documentation for owned API labs. Pair implementation details with OWASP API Security, not framework docs alone.
API inventory and safe testing references: Curated Security API Catalog includes APIs.guru, Postman Echo, GitGuardian and disclosure-management services. Use synthetic data and written scope; public OpenAPI specifications do not confer testing authorization.
Assessment standards and approved automation: OWASP ASVS/WSTG mapping and Nuclei template review adds versioned verification requirements, test evidence and safe scanner selection; follow the client findings lifecycle for remediation and retesting.
Dedicated home for web application security - the OWASP Top 10, a repeatable assessment methodology, and the tooling (Burp Suite, API/GraphQL testing) used to find and fix web vulnerabilities during authorized engagements.
Indexes the Web Application Security section: an OWASP Top 10 deep-dive (2025 final edition, mapped to the superseded 2021 edition) and a full web application penetration testing methodology covering reconnaissance, mapping, the Burp Suite workflow, injection and access-control testing, business-logic flaws, and API/GraphQL testing - each paired with defensive guidance.
Give practitioners a single canonical web-AppSec reference: understand each risk class, test for it methodically, and remediate it - rather than the web content being scattered across the master guides.
- Scoping or executing an authorized web application penetration test
- Looking up a specific OWASP Top 10 category (how it works, how to test, how to fix)
- Building a repeatable methodology / Burp workflow for web assessments
- Reviewing a web app or API defensively against the current OWASP risks
Web applications are the most exposed part of most organizations' attack surface, and web AppSec is one of the most frequently referenced topics across this repository - but it previously had no dedicated home. This section consolidates it: what the current risks are, how to test for them, and how to defend.
The material is dual-use - every risk class pairs the offensive perspective (how it is found and exploited) with the defensive one (how to prevent and detect it), mirroring the Tradecraft convention.
| File | Description | Status |
|---|---|---|
| owasp-top-10.md | OWASP Top 10:2025 final-edition deep-dive - each category with exploitation, testing, and defense, plus a 2021→2025 mapping | ✅ Complete |
| methodology.md | Web app pentest methodology: recon, mapping, Burp Suite workflow, injection/access-control/business-logic testing, API & GraphQL testing, reporting | ✅ Complete |
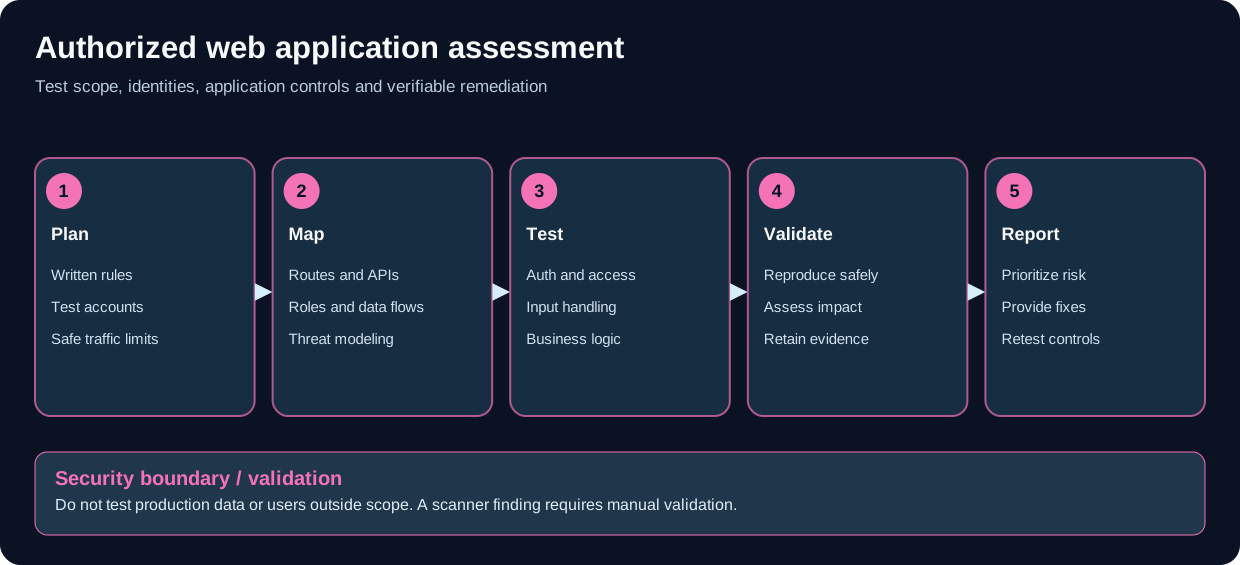
Use written rules of engagement and validate scanner findings.
A web assessment generally proceeds in phases (detailed in methodology.md):
- Recon & mapping - enumerate content, endpoints, technologies, and roles.
- Configuration & deployment - TLS, headers, exposed files, default creds.
- Authentication & session - login flaws, session handling, MFA, JWT.
- Authorization - horizontal/vertical access control (the #1 risk class).
- Input handling - injection (SQLi, command, template), XSS, deserialization.
- Business logic - abuse of legitimate functionality and workflows.
- APIs - REST and GraphQL-specific testing.
- Reporting - reproducible findings mapped to OWASP / CWE with remediation.
Caution
Authorized use only. The techniques here are for authorized penetration testing, education, and defensive research. Testing a web application you do not own or lack explicit written permission to assess is illegal (e.g. the U.S. Computer Fraud and Abuse Act and equivalents elsewhere). Always work within a signed scope and rules of engagement. See LEGAL.md.
-
/Tradecraft- Offensive/defensive deep-dives (AD, C2, evasion) that pair with web AppSec -
/Checklists- Quick-reference assessment checklists -
/OSINT- Reconnaissance that precedes a web assessment -
/Scripts- Automation and payload references -
ultimate_cybersecurity_master_guide.md- Web Application Reconnaissance / Vulnerabilities (summary sections) -
advanced_techniques_part2.md- Advanced Web Application Attacks
- OWASP Top 10 - the current final risk list (2025; 2021 superseded)
- OWASP Web Security Testing Guide (WSTG) - the definitive testing methodology
- OWASP Application Security Verification Standard (ASVS) - verifiable security requirements
- OWASP Cheat Sheet Series - concise defensive guidance per topic
- PortSwigger Web Security Academy - free, hands-on labs
- MITRE CWE - weakness taxonomy referenced by findings
Repository: ULTIMATE CYBERSECURITY MASTER GUIDE
Maintained by: Pacific Northwest Computers
- owasp-top-10.md - OWASP Top 10:2025 deep-dive with testing and defense
- methodology.md - Web application penetration testing methodology
- ../GLOSSARY.md - Acronyms and terms (OWASP, CWE, SSRF, XSS…)
- ../LEGAL.md - Legal notice and authorized-use terms
- OWASP Standards, Test Cases and Nuclei Template Review
- 🔟 OWASP Top 10 - Deep Dive
- 🧭 Web Application Penetration Testing Methodology
📂 Folder: WebAppSecurity | ✏️ Suggest an edit | 🗺️ Browse by Topic