Repository navigation
Persistence
Windows persistence techniques mapped to MITRE ATT&CK, covering registry, service, scheduled task, and application-based persistence mechanisms. Source: Pentest Laboratories.
Purpose: A defensive inventory of Windows mechanisms that can make code re-execute after reboot, logon, or another trigger. It is host-level persistence (surviving a reboot or logoff), distinct from Domain Persistence, which covers persistence at the AD/domain level.
Function: The techniques cluster into families based on what triggers re-execution: logon-time (Winlogon Helper, Registry Run Keys, PowerShell Profile, Screensaver), service-based (New/Modified Service, Port Monitors, Time Providers - all run as SYSTEM), event-driven (WMI Event Subscription - fires on arbitrary system conditions, not just boot/logon), and hijacking-based (DLL Search Order, COM Hijacking, Netsh Helper DLL, DLL Proxy Loading - abuse how Windows locates and loads code rather than registering a new autostart entry at all). Visibility varies by mechanism and telemetry; hijacking techniques can alter legitimate load paths and may require targeted checks.
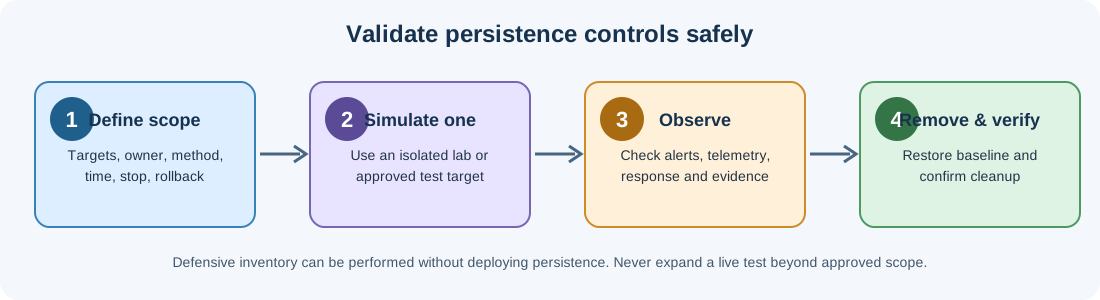
Goal: Help defenders inventory relevant autostart locations and validate detection and recovery coverage. This list is not exhaustive; coverage depends on Windows versions, configuration, and telemetry. During a controlled exercise, simulate only the mechanisms necessary to answer a defined test question.
When & how to use this: During red-team work, use a lab or a specifically approved simulation, one mechanism at a time, with a documented rollback and cleanup verification. Do not plant multiple live mechanisms as the default test approach. During defensive/hunt work, use this as a structured sweep list - most EDR "autoruns"-style tooling covers the registry/service/scheduled-task items natively, but the hijacking-family items (DLL search order, COM hijacking) usually require manual or purpose-built hunting since they don't register in a conventional autostart location.
📖 Use These Checklists Responsibly: Authorization is MANDATORY
Attack techniques are powerful - use them ethically and legally.
Repository: ULTIMATE CYBERSECURITY MASTER GUIDE
Maintained by: Pacific Northwest Computers
⭐ Star this repo if you find it useful! ⭐
📄 Source: Checklists/Persistence.md | ✏️ Suggest an edit | ⬅️ Back to Checklists