Repository navigation
Open Source Intelligence OSINT
Historical OSINT/CTF recon reading: Cypherpunk toolkit curation flags outdated people-search links and separates public challenge research from live-person targeting.
A comprehensive collection of OSINT tools, techniques, methodologies, and resources
Part of the ULTIMATE CYBERSECURITY MASTER GUIDE


Adjacent research ecosystems: h4cker OSINT, threat-intelligence and security collections; use the curated Awesome OSINT reference for evidence-first collection.
Outbound proxy choices: Proxy trust, Froxy and DNS-leak reference distinguishes disposable public-proxy research from vetted, contractual OSINT egress. For active client tests use stable, auditable and authorized source addresses; see anonymity layering.
Security API companion: Curated Public APIs catalog distinguishes existing OSINT providers from future integrations, with authentication, quota and client-data cautions.
Quick Reference Resources
| Reference | Description |
|---|---|
| OSINT Investigator Cheat Sheet | Fast syntax and field references |
| Cheat Sheet & Reference Index | Cross-section reference inventory |
For evidence handling, verification and case files, use the investigation playbook.
Evidence provenance: Bellingcat Toolkit and source-verification workflow covers independent corroboration, UTC capture, integrity and uncertainty; see the OSINT case playbook.
Expanded curated sources: Awesome OSINT List investigation guide integrates company/beneficial-ownership, imagery, geolocation, transport, domain intelligence, evidence preservation and training sources without duplicating the core catalog.
OSINT section index - covering open source intelligence tools, methodologies, and investigative playbooks for cybersecurity professionals, investigators, and threat intelligence analysts.
Indexes the OSINT section: basic guide, comprehensive cheat sheet, tools catalog, Argus toolkit setup, the OSINT Investigator Playbook, and recon scripts for domain/IP, email, and phone investigation.
Provide a complete OSINT reference hub that takes practitioners from initial reconnaissance through structured investigation workflows, with documented manual procedures and selected scripts; the linked case-directory shell menu is a partially implemented operator toolkit, not a finished automated investigator. It can manage cases and run selected evidence-preserving collectors, but its numbered report submenu and web UI are incomplete; see the feature matrix.
- Starting an OSINT investigation and navigating to the right sub-guide
- Onboarding to the OSINT Investigator Playbook for scam/fraud investigations
- Reviewing what tools and scripts are available before a recon engagement
This directory contains comprehensive Open Source Intelligence (OSINT) resources curated for cybersecurity professionals, researchers, investigators, and students. The content focuses on practical application of OSINT techniques for legitimate security research, threat intelligence, and authorized investigations.
What You'll Find Here:
- 📚 Complete OSINT methodology and frameworks
- 🛠️ 400+ categorized OSINT tools with usage examples
- 📖 Step-by-step investigation workflows
- 🖥️ VM setup guides and automation scripts
- 🔐 OPSEC and privacy best practices
- ⚖️ Legal and ethical guidelines
- 📝 Cheat sheets and quick references
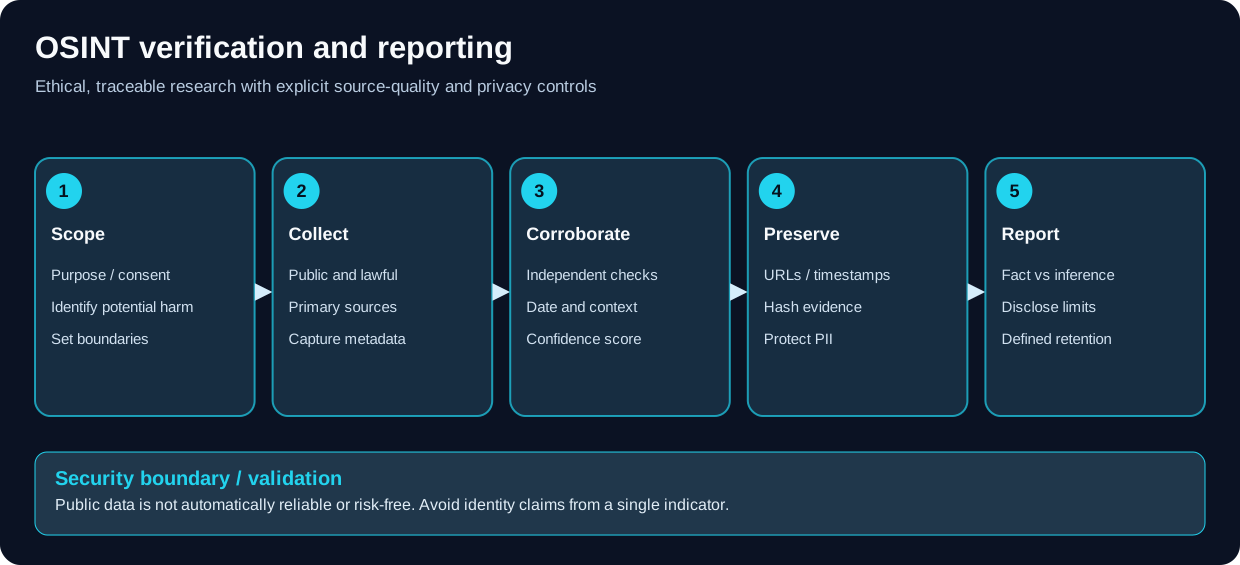
Verify provenance and distinguish facts from inference.
Open Source Intelligence (OSINT) is the collection and analysis of information gathered from publicly available sources. OSINT is used for:
- Cybersecurity: Threat intelligence, vulnerability research, attack surface mapping
- Penetration Testing: Reconnaissance phase of security assessments
- Incident Response: Threat actor attribution and IOC correlation
- Corporate Security: Due diligence, brand protection, competitive analysis
- Law Enforcement: Investigations and intelligence gathering
- Research: Academic and investigative journalism
✅ Publicly Available: Only collect information accessible to the public
✅ Legally Obtained: No hacking, unauthorized access, or circumvention
✅ Ethically Collected: Respect privacy laws and terms of service
✅ Properly Documented: Maintain chain of custody and source attribution
| File | Description | Status |
|---|---|---|
| OSINT Guide | 📘 Master OSINT Guide - Comprehensive reference covering methodology, tools, workflows, and best practices | ✅ Complete |
| OSINT Playbook | Manual investigation guide plus case management, selected evidence-preserving lookup modules and optional integrations; unfinished report submenu and missing web UI are documented in the feature matrix | Prototype |
| Toolkit FAQ | Questions on scope, case state, provider and feature limits | Maintained |
| Toolkit Installation | Dependencies and installation preflight | Check actual version |
| Toolkit Compatibility | Platform targets and validation limitations | Not all lab-tested |
| Toolkit Troubleshooting | Diagnostic steps for failed/partial collection, missing tools and unfinished features | Maintained |
| OSINT Tools | 🛠️ Detailed tool catalog with installation guides | ✅ Complete |
| OSINT Cheatsheet | ⚡ Quick reference commands and techniques | ✅ Complete |
| Guide | Focus Area | Status |
|---|---|---|
| OSINT_socialmedia.md | Social media investigation techniques | ✅ Complete |
| Email_OSINT.md | Email enumeration and analysis | ✅ Complete |
| Domain_IP_Recon.md | Domain and infrastructure reconnaissance | ✅ Complete |
| Phone_OSINT.md | Phone number investigation methods | ✅ Complete |
| Geolocation_OSINT.md | Image analysis and geolocation | 🔨 Planned |
| People_Search.md | Person investigation methodologies | 🔨 Planned |
| argus_osint.md | How-to for installing the Argus OSINT Python Utility | ✅ Complete |
| Tsurugi Linux OSINT Guide | Verified Tsurugi LAB setup, OSINT profile, native tools, case and evidence workflows | ✅ Complete |
| Directory / File | Contents | Status |
|---|---|---|
| Playbook/ | Menu-driven osint_investigator.sh + case management |
✅ |
| Playbook/scripts/ | Audit & report scripts (below) | ✅ |
| Playbook/abuse_report_generator.sh | Auto-drafts IC3 / FTC / registrar abuse reports | ✅ |
| Playbook/toolkit_integration.sh | Wires external tools into the playbook | ✅ |
| Playbook/tools_api.md | Tool + API reference | ✅ |
| Playbook/branding.conf.example | Operator branding template (copy to local config) | ✅ |
| templates | Report templates and investigation forms | 🔨 Planned |
| Script | Purpose |
|---|---|
scammer_audit.sh |
Full scam/fraud infrastructure workup (domain + IP + email) |
email_audit.sh |
Email enumeration, breach, reputation |
phone_audit.sh |
Phone number intelligence |
username_audit.sh |
Username search across platforms |
domain_monitor.sh |
Baseline + change detection for DNS / WHOIS / SSL / CT |
whois_bulk.sh |
Batch WHOIS lookups |
ssl_cert_audit.sh |
SSL/TLS certificate analysis |
crypto_audit.sh |
BTC / ETH / LTC / DOGE / XMR / XRP / BCH on-chain + scam-DB checks |
threat_feed_check.sh |
Parallel threat-intel feed IOC scoring |
metadata_stripper.sh |
Evidence metadata extract + strip |
screenshot_archive.sh |
Automated screenshots / page archival |
case_report_generator.sh |
Rolls a case directory into one report |
Setup: copy
Playbook/branding.conf.exampleto~/.config/osint-investigator/branding.confand add your details; API keys go in~/.config/osint-investigator/api_keys.conf(never committed).
| Study | Description | Status |
|---|---|---|
| case-studies/ | Real-world OSINT investigation examples | 🔨 Planned |
- Start Here: Read the OSINT_GUIDE.md introduction
- Learn the Methodology: Understand the OSINT intelligence cycle
- Set Up Your Environment: Follow the VM setup guide; for Tsurugi LAB use the Tsurugi Linux OSINT Guide
- Practice: Try the investigation workflows on authorized targets
- Stay Legal: Review the legal and ethical considerations section
- Tool Reference: Jump to the Core OSINT Tools section
- Advanced Workflows: Review domain/company investigation procedures
- Automation: Check the scripts directory for time-saving tools
- Cheat Sheets: Use quick reference guides for common commands
# Core OSINT toolkit (Top 10)
1. theHarvester - Email/subdomain harvesting
2. Sherlock - Username search across platforms
3. Recon-ng - Reconnaissance framework
4. Amass - Network mapping (OWASP)
5. SpiderFoot - Automated OSINT
6. Maltego - Link analysis and visualization
7. Photon - Fast web crawler
8. H8mail - Email breach hunting
9. Holehe - Email account enumeration
10. PhoneInfoga - Phone number intelligence
See OSINT_GUIDE.md - VM Setup for complete installation instructions.
⚠️ LEGAL USE ONLY ⚠️

This content is provided for:
✅ Educational purposes
✅ Authorized security research
✅ Legal investigations with proper authority
✅ Ethical intelligence gathering within legal boundaries

STRICTLY PROHIBITED:
🚫 Stalking, harassment, or doxxing
🚫 Unauthorized access to systems or data
🚫 Violations of privacy laws (GDPR, CCPA, etc.)
🚫 Circumventing security measures
🚫 Social engineering or pretexting
🚫 Any illegal activities

ALWAYS:
- Obtain proper authorization before investigations
- Respect all applicable laws and regulations
- Follow website terms of service
- Consider privacy and ethical implications
- Document your sources and methods
- Consult legal counsel when in doubt
- United States: Computer Fraud and Abuse Act (CFAA), Electronic Communications Privacy Act (ECPA)
- European Union: General Data Protection Regulation (GDPR)
- California: California Consumer Privacy Act (CCPA)
- State Laws: Various state privacy and computer crime statutes
- International: Laws vary by jurisdiction - know your local regulations
Accessing a computer without the authorization required by applicable law may be unlawful. The legal outcome depends on the conduct, scope, facts and jurisdiction; this guide does not determine authority for a specific investigation.
- Understand OSINT principles and methodology
- Learn basic Google dorking
- Practice username enumeration
- Set up basic OSINT tools
- Master subdomain enumeration
- Conduct full domain reconnaissance
- Perform social media investigations
- Use automation frameworks (Recon-ng, SpiderFoot)
- Dark web investigation techniques
- Advanced geolocation analysis
- Threat intelligence correlation
- Custom script development
- Complex case investigations
- Tool development and customization
- Advanced OPSEC and counter-OSINT
- Teaching and mentoring others
- Contributing to OSINT community
- IntelTechniques by Michael Bazzell - Books, training, tools
- Trace Labs - OSINT for missing persons, CTF competitions
- SANS SEC487 - Professional OSINT training
- TCM Security OSINT Course - Practical OSINT training
- "Open Source Intelligence Techniques" by Michael Bazzell ⭐ Must Read
- "OSINT Handbook" by i-intelligence (Free)
- "Social Engineering" by Christopher Hadnagy
- "The Art of Invisibility" by Kevin Mitnick
- Reddit: r/OSINT, r/SocialEngineering
- Discord: Trace Labs, OSINT Curious
- Twitter: #OSINT hashtag
- Blogs: Bellingcat, IntelTechniques, Sector035
- Trace Labs CTF - Missing persons OSINT competitions
- OSINT Exercises (Gralhix) - gralhix.com/list-of-osint-exercises
- TryHackMe - OSINT learning paths
- Sector035 Quizzes - Weekly OSINT exercises
This OSINT knowledge base is continuously growing. Contributions are welcome!
- Tools: Submit new OSINT tools with descriptions and examples
- Techniques: Share investigation methodologies and workflows
- Scripts: Contribute automation scripts or improvements
- Case Studies: Submit anonymized investigation examples (with authorization)
- Documentation: Improve existing guides, fix errors, add clarifications
- Resources: Share training materials, articles, or tutorials
- ✅ Only submit legally and ethically obtained information
- ✅ Test all tools and commands before submission
- ✅ Provide proper attribution and credits
- ✅ Include warnings for sensitive or advanced techniques
- ✅ Follow markdown formatting standards
- ✅ Redact any sensitive or personal information
Submit via: Pull requests on the main repository or open an issue with suggestions
- OSINT Framework - Comprehensive tool directory
- Awesome OSINT - Curated GitHub list
- Bellingcat's Toolkit - Investigative resources
- IntelTechniques Tools - Free OSINT tools
📁 Total Files: Growing collection
🛠️ Tools Documented: 400+
📖 Guides: Core guide complete, more coming
🔄 Last Updated: November 2024
👥 Maintained by: Pacific Northwest Computers (PNWC)
This OSINT collection supports:
- Penetration testing reconnaissance
- Vulnerability research
- Threat intelligence gathering
- Attack surface mapping
- Background checks (authorized)
- Due diligence research
- Fraud investigations
- Missing persons cases (with authority)
- Academic research
- Investigative journalism
- Open source intelligence studies
- Security awareness training
- Learning OSINT methodologies
- Practicing ethical hacking skills
- Preparing for certifications (CEH, OSCP, GPEN)
- Building security career skills
Editorial status checked November 11, 2026. Individual commands, APIs and target websites require their own verification.
| Area | Published Resource | Current Limitation |
|---|---|---|
| Structured Investigation & Evidence | Investigator Playbook | Case management and selected collectors exist, but not all report-menu actions or the web interface |
| Methodology & Verification | OSINT Master Guide and Source Verification | Validate source provenance, rights, dates and provider restrictions for each case |
| Curated External Resources | Tools Catalog and Awesome OSINT Curation | Third-party tools and service availability change; index inclusion is not live testing |
| Automation & Scripts | OSINT Scripts and Playbook Scripts | Some examples and adapters are historical or incomplete; inspect before running |
| Toolkit Installation & Support | Installation, Compatibility, FAQ, Troubleshooting | Confirm versions and inspect errors before calling a lookup completed |
Open development priorities: implement/report the unfinished numbered reports menu, design and test a secured local web UI if needed, improve input and provider adapter validation, add reproducible offline fixtures for third-party integrations, and capture independent verification results. Avoid declaring these complete before tests exist.
- Open an issue on GitHub
- Check existing documentation first
- Be specific about your use case
- Include relevant details (OS, tools, errors)
- Suggest new tools to document
- Propose new investigation workflows
- Request specific guides or tutorials
- Share ideas for improvements
- Join discussions on GitHub
- Share your OSINT successes (ethically)
- Help others in the community
- Contribute back to the project
This OSINT resource collection is part of the ULTIMATE CYBERSECURITY MASTER GUIDE:
- Compiled by Pacific Northwest Computers (PNWC)
- Content sourced from 70+ professional cybersecurity books
- Tools and techniques from industry-leading researchers
- Community contributions from OSINT practitioners
All tools referenced are property of their respective creators. This is an educational resource compilation under fair use. Purchase original books and support tool developers.
THE AUTHORS AND CONTRIBUTORS PROVIDE THIS CONTENT "AS IS" WITHOUT
WARRANTY OF ANY KIND, EXPRESS OR IMPLIED. USE AT YOUR OWN RISK.

The maintainers assume no liability for:
- Misuse of information or tools
- Legal consequences of unauthorized activities
- Privacy violations or harm caused
- Accuracy of third-party resources
- Outcomes of OSINT investigations

Users are responsible for:
- Complying with all applicable laws
- Obtaining proper authorization
- Ethical use of techniques
- Consequences of their actions
This OSINT collection wouldn't exist without:
- Michael Bazzell - IntelTechniques, Buscador VM
- Trace Labs Community - OSINT VM, CTF competitions
- Bellingcat - Open source investigative journalism
- Sector035 - OSINT education and resources
- Christian Martorella (theHarvester)
- Sherlock Project Team
- Steve Micallef (SpiderFoot)
- Tim Tomes (Recon-ng)
- OWASP Team (Amass)
- ProjectDiscovery Team (Subfinder, Nuclei)
- And 400+ other tool creators
- OWASP Foundation
- SANS Institute
- IntelTechniques
- Trace Labs
- Open Source Intelligence Community
Thank you for making OSINT accessible to everyone.
📖 Start Your OSINT Journey: Read the Master Guide
Use this knowledge responsibly, ethically, and legally.
Repository: ULTIMATE CYBERSECURITY MASTER GUIDE
Maintained by: Pacific Northwest Computers
Unauthorized computer access or related conduct can carry criminal or civil consequences when the elements of an applicable law are met. The CFAA defines multiple offenses with different elements and penalties; there is no single penalty for every unauthorized use.
For an engagement, document permission, target scope, allowed methods, time window, data handling and stop conditions. Public-source research also requires attention to privacy, contractual, platform and jurisdiction-specific limits.
⭐ Star this repo if you find it useful! ⭐
OSINT involves collecting publicly available information - but "public" does NOT mean "unrestricted use."
ALWAYS comply with applicable laws:
- Computer Fraud and Abuse Act (CFAA): 18 U.S.C. § 1030 defines several offenses involving protected computers, including specified conduct without authorization or exceeding authorized access. Statutory elements and penalties differ by subsection; DOJ's charging policy is guidance for federal prosecutors, not a complete statement of every applicable law.
- Electronic Communications Privacy Act (ECPA): Protects electronic communications and stored data
- State Privacy Laws: Many states have additional privacy and anti-stalking statutes
- California Consumer Privacy Act (CCPA): Regulates collection and use of California residents' data
-
General Data Protection Regulation (GDPR): Article 3 sets territorial scope, including processing in the context of an EU establishment and certain processing by organizations outside the EU when offering goods or services to people in the Union or monitoring their behavior there. A person's location or residence alone does not automatically make every processing operation subject to GDPR.
- Where GDPR applies, assess lawful basis, purpose limitation, data minimization, retention and security in context.
- Data subject rights, including erasure under Article 17, have conditions and exceptions.
- Laws vary significantly by jurisdiction
- Some countries restrict OSINT activities more strictly than others
- Cross-border investigations may trigger multiple legal frameworks
⚠️ Violating website Terms of Service can result in:
- Legal action from the website operator
- Account termination and IP bans
- Civil lawsuits for damages
- Potential CFAA violations in some cases
Many websites explicitly prohibit:
- Automated scraping or data collection
- Creating fake accounts or misrepresentation
- Accessing data through unauthorized means
- Commercial use of collected data
ALWAYS review and comply with ToS before collecting data from any platform.
Authorized and Legitimate Uses:
- ✅ Cybersecurity Threat Intelligence: Identifying threats to your organization
- ✅ Authorized Penetration Testing: Reconnaissance phase with written authorization
- ✅ Incident Response: Threat actor attribution and IOC correlation
- ✅ Corporate Due Diligence: Business intelligence with proper authorization
- ✅ Law Enforcement Investigations: With proper legal authority and warrants
- ✅ Missing Persons Cases: Authorized search and rescue operations (e.g., Trace Labs)
- ✅ Investigative Journalism: Public interest reporting within legal bounds
- ✅ Academic Research: Ethical research with IRB approval
- ✅ Personal Security: Monitoring your own digital footprint
- ✅ Background Checks: With consent and for legitimate purposes
- ✅ Fraud Prevention: Protecting your organization from fraud
- ✅ Competitive Intelligence: Ethical business research from public sources
- ✅ Educational Purposes: Learning in controlled, authorized environments
- ✅ CTF Competitions: Authorized OSINT challenges (Trace Labs, etc.)
The activities below are harmful and prohibited for use of this guide; depending on the facts and jurisdiction, they may also violate criminal or civil law, privacy duties, platform terms or professional standards:
- 🚫 Stalking or Harassment: Using OSINT to follow, intimidate, or harass individuals
- 🚫 Doxxing: Publishing private information with intent to harm
- 🚫 Identity Theft: Using collected information to impersonate or defraud
- 🚫 Blackmail or Extortion: Threatening to release information for gain
- 🚫 Unauthorized Private Investigation: Operating without proper licensing
- 🚫 Invasion of Privacy: Collecting information beyond legal scope
- 🚫 Corporate Espionage: Using illegal methods for competitive advantage
- 🚫 Unauthorized Access: Circumventing security or authentication
- 🚫 Social Engineering: Pretexting or deception to obtain information
- 🚫 Child Endangerment: Any activity that could harm minors
- 🚫 Discrimination: Using OSINT for discriminatory purposes
- 🚫 Revenge or Retaliation: Personal vendettas or grudges
- Respect Privacy: Collect only what is necessary for your legitimate purpose
- Do No Harm: Consider the potential consequences of your investigation
- Transparency: Understand who you're working for and why
- Legal Compliance: Follow all applicable laws and regulations
- Professional Standards: Maintain objectivity, accuracy, and integrity
- Data Minimization: Collect the minimum information needed
- Proper Storage: Protect collected data from unauthorized access
- Responsible Disclosure: Report security issues through proper channels
Ask yourself:
- Do I have legal authority or authorization for this investigation?
- What is my legitimate purpose for collecting this information?
- Am I respecting individual privacy and dignity?
- Could my actions cause harm to individuals or organizations?
- Am I complying with all applicable laws and regulations?
- Am I following ethical guidelines for my profession?
- Would I be comfortable if my methods were made public?
Choose controls from the investigation's threat model, approved scope and organizational policy. A VPN shifts trust to its operator; Tor protects only applications configured to use it, and Tor Project recommends its own browser for web use. Neither tool authorizes access, defeats platform restrictions, nor guarantees anonymity.
- ✅ Use an approved, patched and isolated environment appropriate to the investigation; record snapshots and network controls when they affect evidence.
- ✅ Select direct organizational egress, a vetted VPN, or Tor only when permitted and suitable for the case.
- 🚫 Do not rotate IP addresses, circuits or user-agent strings to evade rate limits, blocks or abuse controls. If authorized testing requires multiple source addresses, document the approved range and schedule.
- ✅ Use only accounts and access methods allowed by the engagement and platform rules; document approval for any account activity.
- ✅ Avoid personal-account use when possible, but do not create burner accounts or personas by default.
- 🚫 Do not impersonate people or create sock-puppet identities without explicit approval, a defined purpose and review of platform rules.
- ✅ Minimize identifiers shared with third-party services and record what information a provider receives.
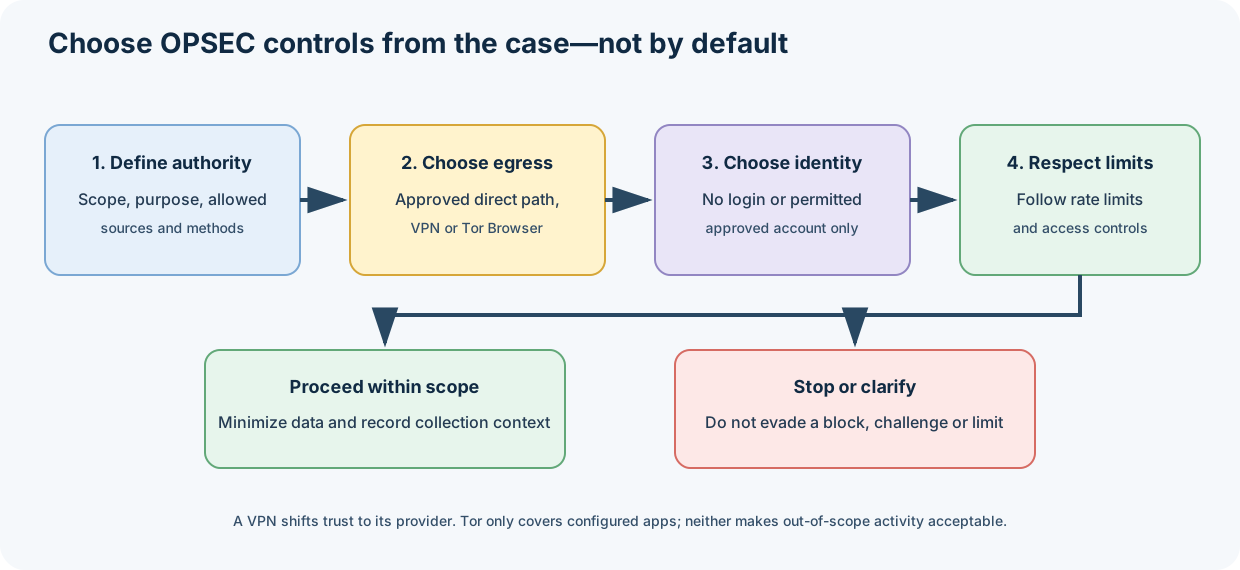
Choose egress and account use from approved scope and the threat model. Stop or seek clarification when a platform blocks or challenges the activity; do not evade the control.
- ✅ Encrypt all collected investigation data
- ✅ Use secure storage with access controls
- ✅ Maintain proper chain of custody for evidence
- ✅ Securely delete data when no longer needed
- ✅ Follow data retention policies and regulations
Proper documentation is essential:
- 📝 Screenshot everything with timestamps
- 📝 Capture locally first and record URL, UTC time, tool/version, omissions and hash; submit to a public archive only after a separate privacy, terms and authorization review (see the evidence preservation procedure)
- 📝 Record video for dynamic content
- 📝 Log all commands and queries used
- 📝 Document sources for all information
- 📝 Calculate and verify file hashes
- 📝 Maintain detailed investigation notes
- 📝 Preserve metadata where relevant
- Maintain unbroken documentation of evidence handling
- Use write-blockers for forensic data
- Store multiple copies in different locations
- Follow proper legal procedures for evidence preservation
OSINT crosses borders - laws vary:
- 🌍 Jurisdiction Matters: Different countries have different privacy laws
- 🌍 Data Protection: EU GDPR, UK DPA, Brazil LGPD, etc.
- 🌍 Cultural Sensitivity: Respect cultural norms and expectations
- 🌍 Legal Authority: Some techniques legal in one country may be illegal in another
- 🌍 Export Controls: Some tools may be restricted for international use
🔴 Automated actions that violate ToS
🔴 Circumventing authentication or security measures
🔴 Accessing protected or private information without authorization
🔴 Social engineering, pretexting, or deception
🔴 Creating accounts with false information (unless authorized)
🔴 Distributed denial of service or system disruption
🔴 Exploiting vulnerabilities without authorization
🔴 Sharing collected intelligence for illegal purposes
🔴 Conducting investigations for stalking or harassment
🔴 Using OSINT to facilitate any illegal activity
⚠️ IMPORTANT LEGAL NOTICE ⚠️

The authors, contributors, and maintainers of this OSINT resource:

- Provide this content "AS IS" without warranty of any kind
- Assume NO liability for misuse of information or tools
- Are NOT responsible for legal consequences of unauthorized activities
- Do NOT endorse any illegal or unethical use of these techniques
- Strongly advocate for legal, ethical, and authorized OSINT only

USERS ARE SOLELY RESPONSIBLE FOR:
✓ Ensuring their activities comply with all applicable laws
✓ Obtaining proper authorization before conducting investigations
✓ Understanding and following ethical guidelines
✓ Respecting individual privacy and dignity
✓ Consequences of their actions and investigations

This content is for educational purposes and authorized security research only.
Unauthorized or unethical use is strictly prohibited.

WHEN IN DOUBT, CONSULT LEGAL COUNSEL.
Some jurisdictions require licensing for:
- Private investigation services
- Security consulting
- Background check services
- Due diligence research
Check your local requirements before offering OSINT services commercially.
If you discover:
- ❗ Criminal activity during OSINT investigations
- ❗ Child endangerment or exploitation
- ❗ Threats to public safety
- ❗ Security vulnerabilities in critical systems
Take appropriate action:
- Document findings securely
- Report to appropriate authorities (law enforcement, CERT, etc.)
- Follow responsible disclosure practices
- Consult with legal counsel if uncertain
This OSINT resource collection has zero tolerance for misuse. We strongly condemn:
- Stalking, harassment, and doxxing
- Privacy violations and unauthorized surveillance
- Discrimination and hate crimes
- Any illegal or unethical activities
Use OSINT for good. Protect people. Respect privacy. Follow the law.
┌─────────────────────────────────────────────────────────────┐
│                                                             │
│  OSINT is a powerful capability that must be used           │
│  responsibly and ethically.                                 │
│                                                             │
│  With great power comes great responsibility.              │
│                                                             │
│  Your actions can impact real people's lives.              │
│                                                             │
│  Always operate within legal and ethical boundaries.       │
│                                                             │
│  When in doubt - DON'T.                                    │
│  Consult legal counsel and ethical guidelines.             │
│                                                             │
└─────────────────────────────────────────────────────────────┘
Last Updated: November 2025
Review this disclaimer regularly as laws and regulations evolve.
- OSINT_GUIDE.md - Basic/general OSINT methodology guide
- OSINT_CHEATSHEET.md - Quick-reference tool and command cheat sheet
- OSINT_TOOLS_CATALOG.md - Full toolkit catalog
- OSINT_socialmedia.md - Social media investigation methodology and per-platform collection
- Playbook/README.md - OSINT Investigator Playbook for fraud investigations
- ../Tradecraft/osint-threat-intel.md - Advanced OSINT and threat intelligence techniques
- ../Cryptography/Classical/ - Decoding leetspeak, homoglyphs, Morse, and classical ciphers found during investigations
- Argus Recon Toolkit - Installation Guide
- Awesome OSINT List — curated tools and verification workflows
- Bellingcat Toolkit and OSINT Source Verification
- 🔍 Comprehensive OSINT Investigator Cheat Sheet
- 🛠️ Core OSINT Toolkit
- OSINT (Open Source Intelligence) Basic/General Guide
- 🕵️ Social Media OSINT
- Tsurugi Linux OSINT Investigation & Workstation Guide
- 🛠️ Core OSINT Toolkit
- OSINT Investigation Procedures Guide
- OSINT Investigator Playbook — Case Management & Evidence Collection
- Installation Guide
- OSINT Investigator — Frequently Asked Questions
- OSINT Investigator — Troubleshooting & Failure Diagnosis
- Platform Compatibility
- Domain / IP Recon Investigation Script
- Email OSINT Investigation Script
- Phone Number OSINT Investigation Script
📂 Folder: OSINT | ✏️ Suggest an edit | 🗺️ Browse by Topic