Repository navigation
SIEM Deployment Guides
Self-hosted SIEM build guides — centralize logs, detect threats, and hunt adversaries
Part of the ULTIMATE CYBERSECURITY MASTER GUIDE · Incident Response section


| Resource | Description |
|---|---|
| ThreatHunter-Playbook | Community threat-hunting and detection research |
| Awesome Detection Engineering | Detection engineering resources |
| Curated Source Mapping | How external projects relate to local guides |
Validate source content and rules before production use.
| Reference | Description |
|---|---|
| Honeypot → Wazuh JSON Integration | Forward OpenCanary, Cowrie and DIY decoy metadata |
| Kismet + Wazuh | Wireless alert telemetry and SIEM correlation |
| nzyme + Wazuh | Additional wireless event source and correlation |
Container deployment support: Docker CLI / Compose operations reference provides safe diagnostics for containerized SIEM services, volume inventories, log exposure and privilege boundaries. Check the SIEM-specific installation guide for its supported platform and storage requirements.
External enrichment for SIEM workflows: Security API Catalog identifies candidate threat-intelligence and vulnerability feeds and recommends normalized, time-stamped events with explicit error states. No third-party API connector or production automation is installed by that document.
Detection engineering: Sigma, Elastic and native Wazuh validation details rule provenance, decoder/field mapping and positive/negative synthetic tests; Atomic Red Team exercises add controlled, explicitly authorized behavioral validation.
Index for the SIEM sub-section — self-hosted deployment guides for the four most common security log-aggregation platforms (ELK Stack, Wazuh, Splunk, Graylog), so a blue teamer can pick a platform and stand it up for a homelab or small SOC.
Links to a full build guide per platform — server prep, Docker/package deployment, firewall rules, Windows/Linux agent enrollment, data inputs, dashboards, and detection rules — plus a comparison table and a decision aid for choosing between them.
Enable a practitioner to deploy a working SIEM that ingests endpoint, server, and network telemetry and surfaces security-relevant events through dashboards and alerts — without wading through four separate vendor doc sites.
- Standing up a SIEM or centralized log server from scratch in a homelab or small environment
- Choosing between ELK, Wazuh, Splunk, and Graylog for a given use case
- Enrolling Windows (Winlogbeat/Sysmon) or Linux (Filebeat/auditd) agents into a log pipeline
- Building detection rules and dashboards after telemetry is flowing
- Overview
- Platform Comparison
- Deployment Guides
- Which SIEM Should I Choose?
- Deployment Workflow
⚠️ Security, Privacy & Legal Warning- Contributing
- Resources
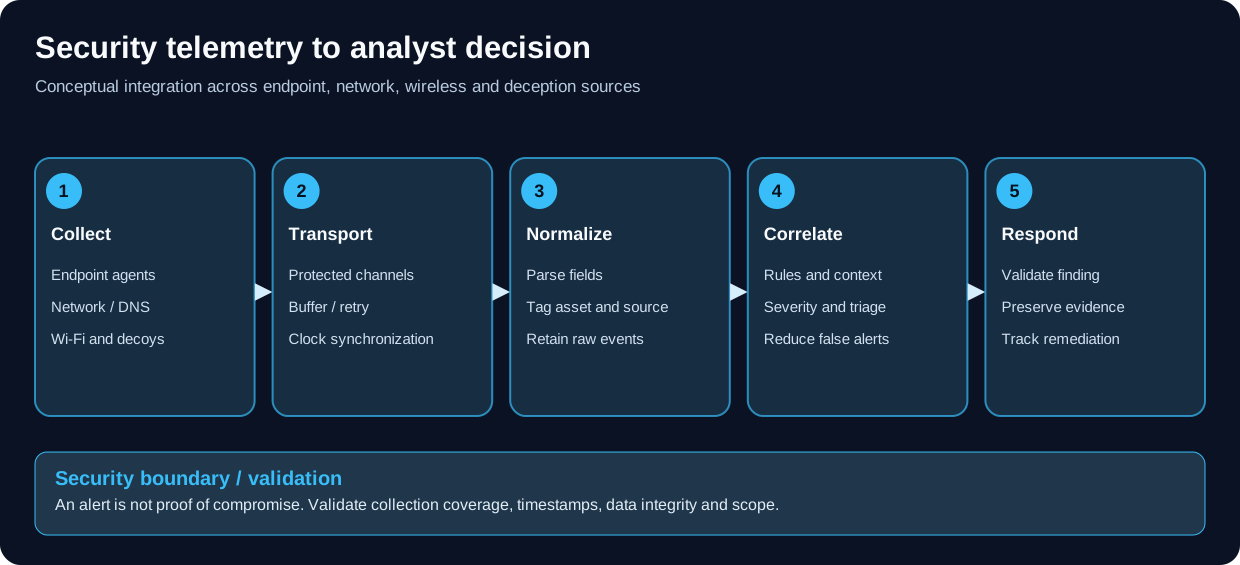
Conceptual telemetry pipeline; a detection must be corroborated.
A SIEM (Security Information and Event Management) platform is the central nervous system of a blue-team operation: it ingests logs from endpoints, servers, and network devices, normalizes them, and lets you search, correlate, alert, and hunt across the whole environment.
This sub-section provides hands-on, self-hosted build guides for the four platforms you are most likely to run in a homelab or small SOC. Each guide is standalone — server preparation, deployment, firewalling, agent enrollment, and initial detections — and each pins known-good versions so the walkthrough stays internally consistent.
Tip
New to log aggregation? Start with the visibility prerequisite in ../log_agg.md, then pick a platform below. Wazuh (all-in-one) and Splunk Free are the gentlest starting points.
| Platform | Guide | Stack / Engine | Deployment Complexity | Best For |
|---|---|---|---|---|
| 🦁 Wazuh | wazuh.md | Wazuh manager + OpenSearch/Elasticsearch | 🟡 MEDIUM | Unified SIEM/XDR: detection, FIM, vuln scan & compliance in one tool |
| 🔷 Splunk | splunk.md | Splunk indexer + Universal Forwarders | 🟢 LOW | Fastest to stand up; SPL search power; Free tier (500 MB/day) |
| 🦌 ELK Stack | elk_stack.md | Elasticsearch + Logstash + Kibana + Beats | 🟡 MEDIUM | Maximum flexibility and custom dashboards/pipelines |
| 🟢 Graylog | graylog.md | Graylog + MongoDB + OpenSearch | 🟡 MEDIUM | Lightweight, stream-based routing; clean log-management UX |
🦁 Wazuh
Unified SIEM/XDR on a single open-source platform. Covers all-in-one install, agent enrollment (Windows/Linux), built-in detection rules, File Integrity Monitoring (FIM), vulnerability detection, active response, and compliance dashboards (PCI-DSS, GDPR, HIPAA, CIS), plus OpenSearch/Elasticsearch integration. The most feature-complete single-package option.
🔷 Splunk
Deploys Splunk Free (500 MB/day) or Enterprise trial. Covers indexer/search-head install, Universal Forwarder setup for Windows/Linux, index and sourcetype design, SPL query writing (stats, eval, transaction, lookup), Splunk Security Essentials, saved searches/alerts, and BOSS of the SOC (BOTS) training data. Lowest barrier to a first working search.
The classic Elasticsearch + Logstash + Kibana stack via Docker Compose. Covers cluster setup, Beats deployment (Filebeat/Winlogbeat/Auditbeat), Logstash pipelines, index lifecycle management, Kibana Lens dashboards, Elastic SIEM detection rules, and performance tuning. Most flexible, most assembly required.
🟢 Graylog
A lighter-weight log-management platform (Graylog + MongoDB + OpenSearch). Covers server setup, GELF/Syslog/Beats inputs, streams and processing pipelines for routing security logs away from operational noise, alert conditions/notifications, dashboards, and index rotation/retention.
Want the most in one package (SIEM + EDR + FIM + compliance)?
  └─> Wazuh — single agent, built-in rules, compliance dashboards.

Brand new and want a working search fastest?
  └─> Splunk Free — easiest install, best query language (SPL), 500 MB/day cap.

Want maximum control over ingestion, parsing, and dashboards?
  └─> ELK Stack — most flexible, but you assemble the pieces.

Want lightweight log management with clean stream routing?
  └─> Graylog — gentler on resources than full ELK.
Note
All four are production-capable. For a homelab first SIEM, Wazuh or Splunk Free get you to value fastest; choose ELK or Graylog when you need custom pipelines or want to learn the Elastic/OpenSearch ecosystem directly.
1. Prerequisites
   └─> Provision a VM (see the per-guide sizing; SIEMs are RAM-hungry).
   └─> Read the visibility primer in ../log_agg.md.

2. Stand up the platform
   └─> Follow one guide end-to-end (server prep → deploy → firewall).

3. Enroll agents
   └─> Windows: Winlogbeat + Sysmon.   Linux: Filebeat + auditd (or Wazuh agent).
   └─> Confirm events are indexing in the dashboard.

4. Detect & hunt
   └─> Add detection rules / saved searches; generate test attacks from a lab
       VM and trace the chain. Pair with the IR playbooks in ../../PlayBooks/.
See also endpoint instrumentation: Osquery for SQL-based host telemetry that feeds any of these platforms.
═══════════════════════════════════════════════════════════════
                    ⚠️  BLUE-TEAM DATA HANDLING  ⚠️
═══════════════════════════════════════════════════════════════

SIEMs aggregate highly sensitive data. Operate them responsibly.

1. DATA PRIVACY & COMPLIANCE (PII/PHI)
   ► Logs routinely capture credentials, PII, and PHI.
   ► Never upload real organizational logs to public repos or sandboxes.
   ► Sanitize/anonymize before sharing for educational purposes.
   ► Mishandling can breach GDPR, HIPAA, CCPA, and PCI-DSS.

2. AUTHORIZATION
   ► Only deploy agents/forwarders on systems you own or are explicitly
     authorized (in writing) to monitor. Covert monitoring can be construed
     as unlawful interception/wiretapping.

3. EXPOSURE
   ► SIEM web UIs and Elasticsearch/OpenSearch APIs must never be exposed to
     the internet unauthenticated — follow the firewall steps in each guide.
═══════════════════════════════════════════════════════════════
Contributions from SOC analysts and detection engineers are welcome.
What we accept:
- ✅ Detection content (SIGMA rules, SPL, KQL, Elastic/OpenSearch queries)
- ✅ Parser/pipeline configs (Logstash, Graylog pipelines, Wazuh decoders)
- ✅ Dashboards and hardening/tuning tips
- ✅ Version-compatibility updates as platforms release new majors
Guidelines:
- Sanitize any sample logs of real PII/credentials.
- Document the platform version your config was tested against.
- Submit a PR describing the defensive value.
- Sigma (detection rules): https://github.com/SigmaHQ/sigma
- Wazuh docs: https://documentation.wazuh.com/
- Elastic Security docs: https://www.elastic.co/guide/en/security/current/index.html
- Splunk Docs & SPL reference: https://docs.splunk.com/
- Graylog docs: https://go2docs.graylog.org/
- MITRE ATT&CK (detection mapping): https://attack.mitre.org/
- ⬅️ Incident Response section
- 📥 Log Aggregation primer
- 👁️ Osquery endpoint visibility
- 📘 Blue Team Playbooks
- 📖 Glossary (SIEM, EDR, IoC, SOAR, Sigma…)
- 🏠 Main Repository
🛡️ Visibility is the foundation of defense — deploy these tools ethically and legally.
Maintained by Pacific Northwest Computers (PNWC)
⬅️ Back to Master Index | 🎯 Role Navigation | Legal Notice
📄 Source: IncidentResponse/SIEM/README.md | ✏️ Suggest an edit | ⬅️ Back to Incident Response