Repository navigation
Illustrations and Visual Resources
Visual placements updated: 2026-11-19. Historical visual content has not been re-authenticated against live equipment.
Return to the main guide or the visual reference notes.
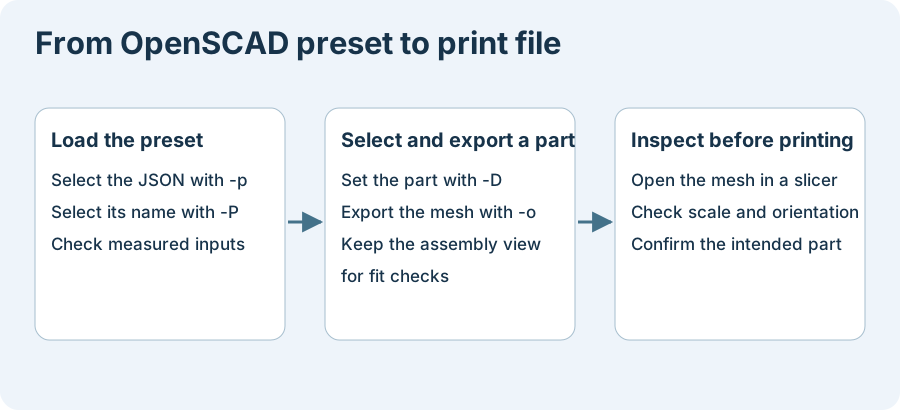
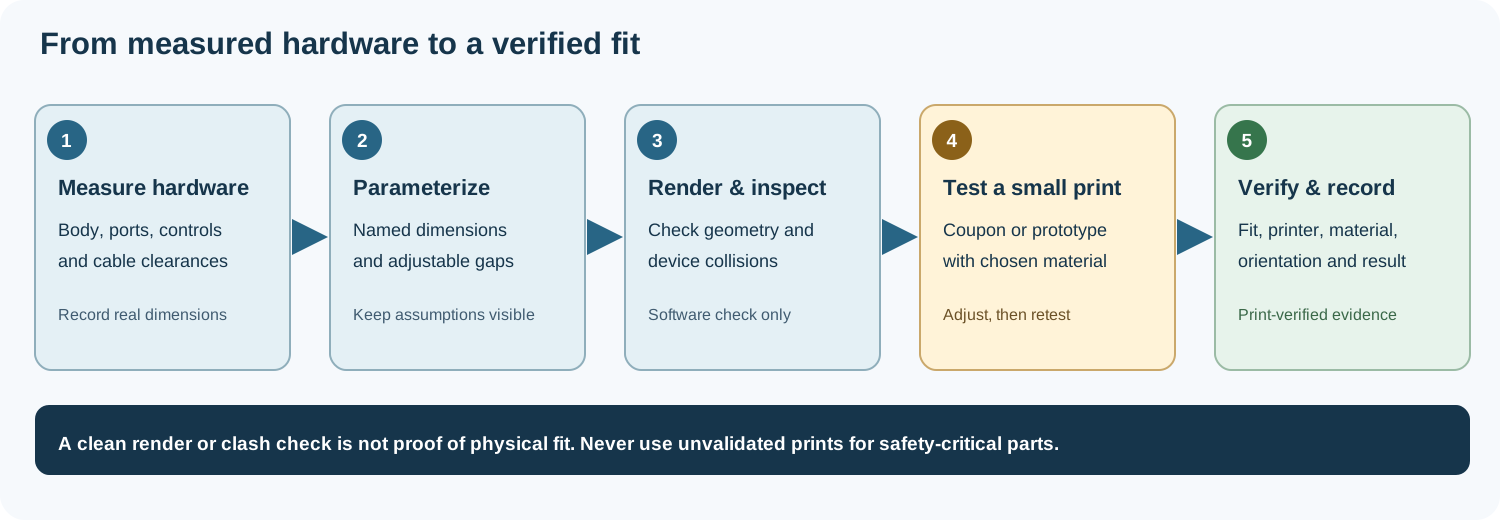
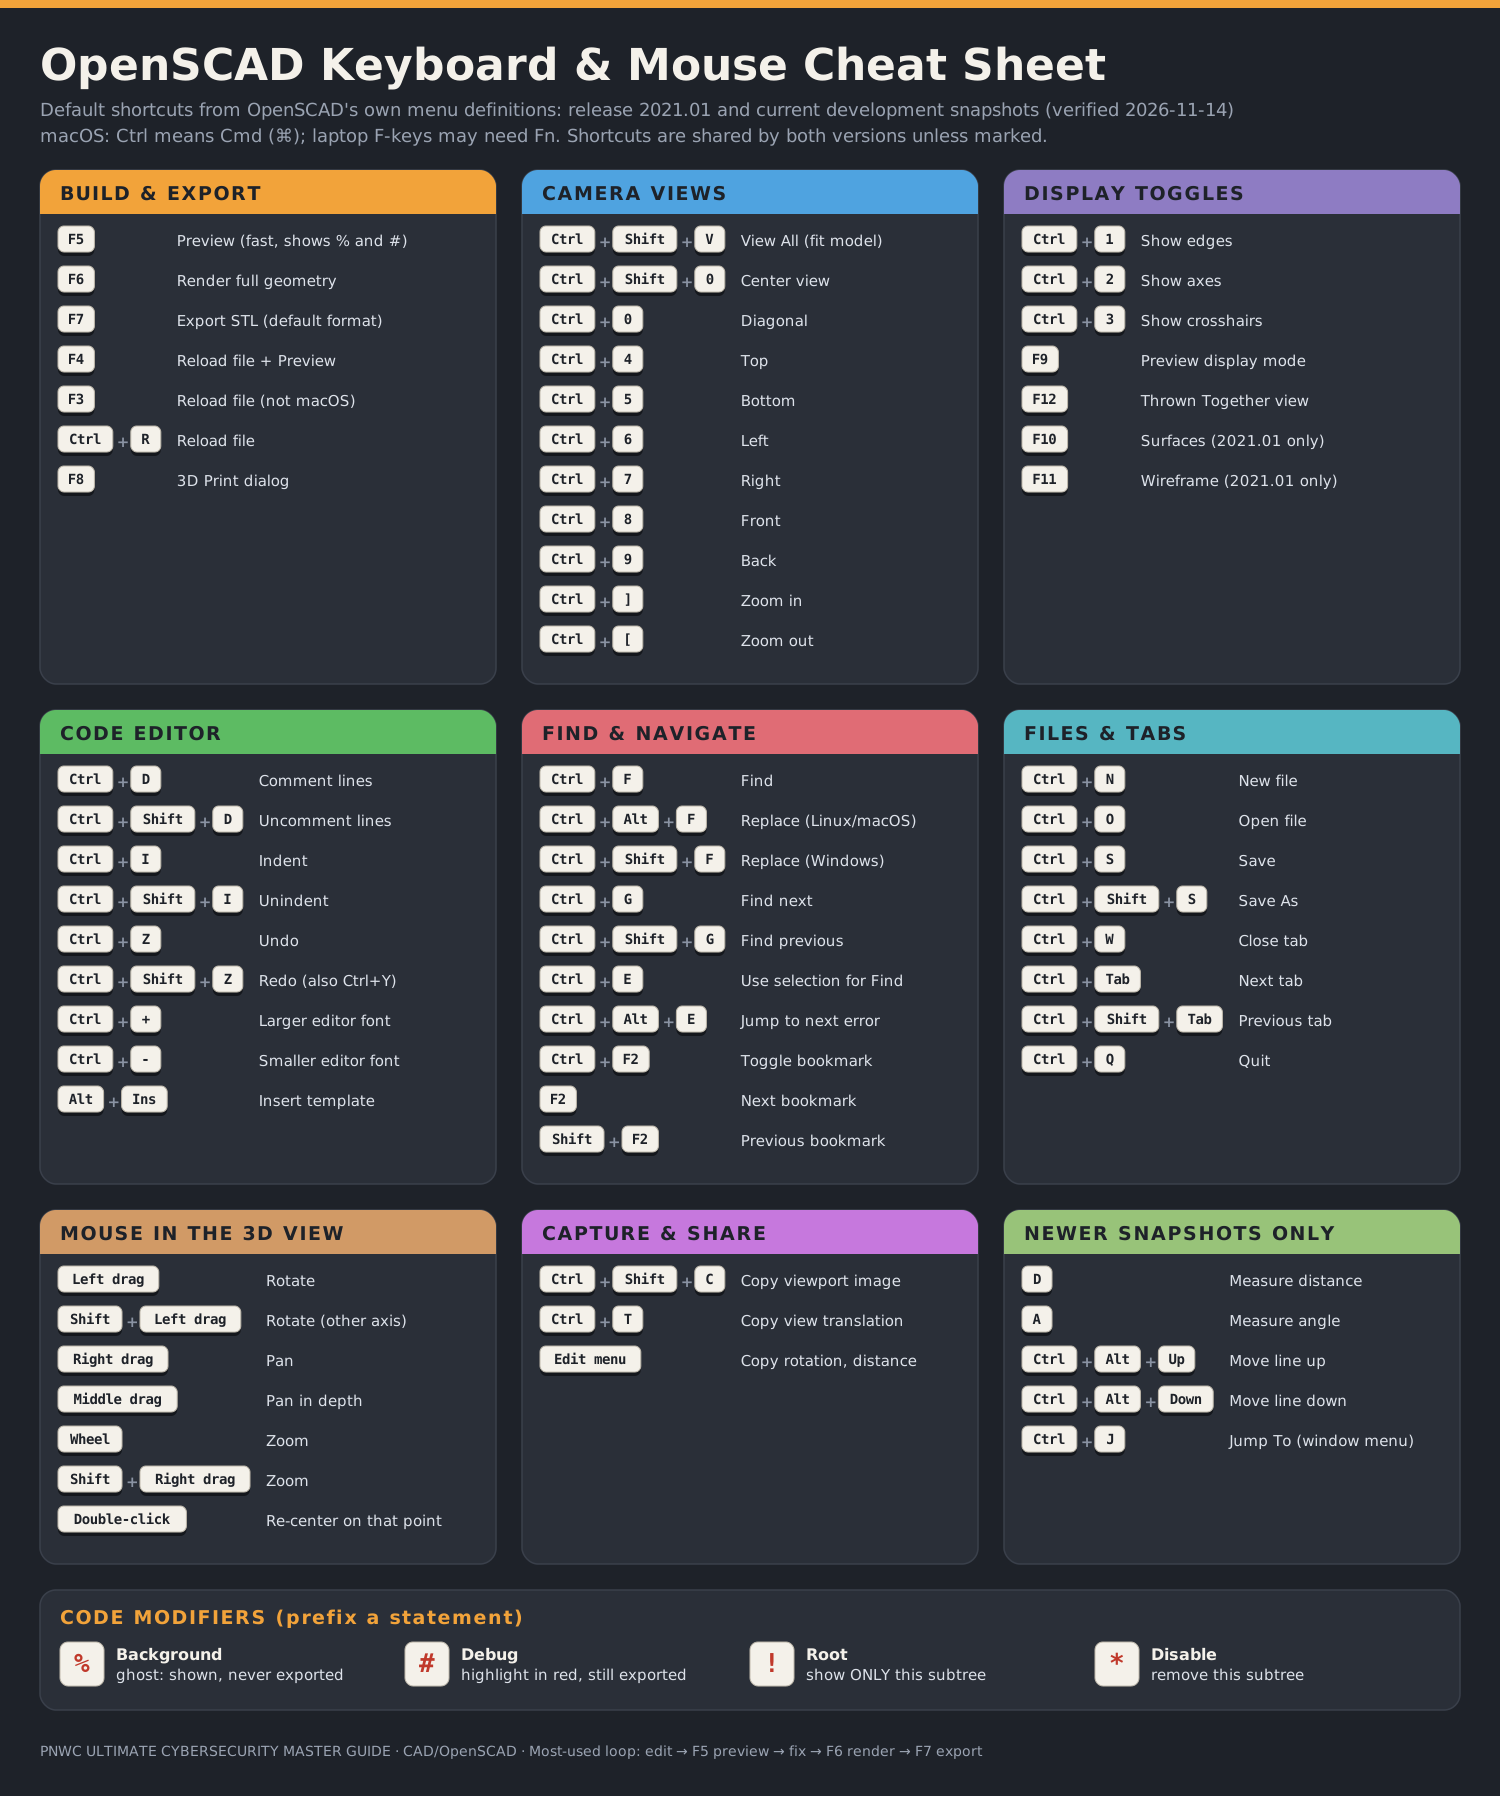
This folder stores diagrams as shared assets. Embed them in the topic guide where they clarify a specific procedure rather than repeating the same figure across multiple unrelated README pages. Captions should identify a diagram as conceptual when it does not describe a validated PNWC deployment.
| Diagram | Where embedded | Why it belongs |
|---|---|---|
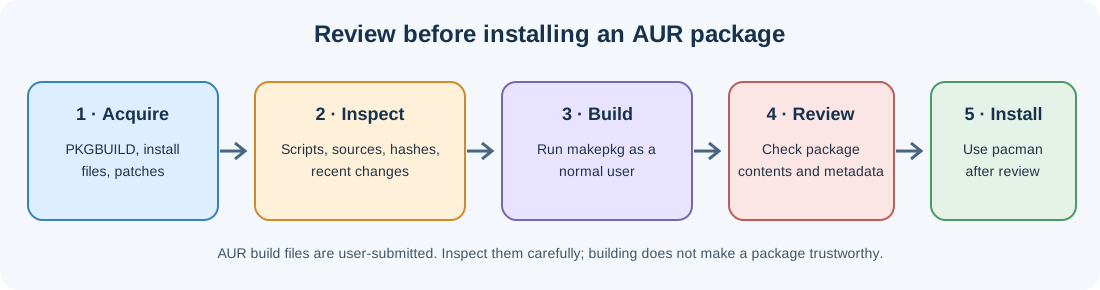
| AUR package review | Arch Linux cheat sheet | Source and build review before installation |
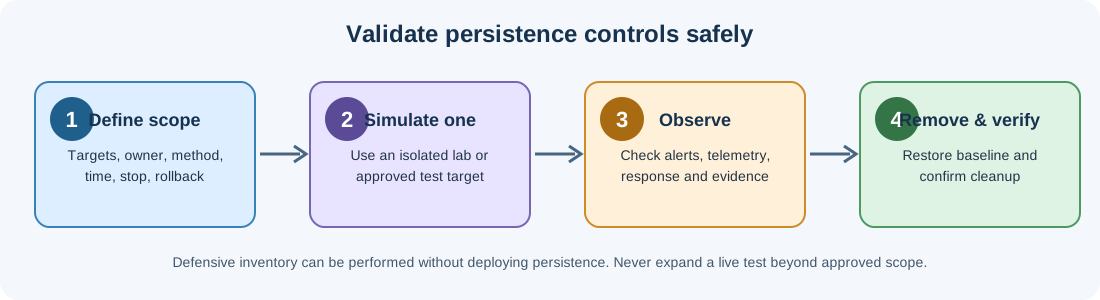
| Persistence validation safety | Domain persistence checklist, persistence checklist | Authorization, cleanup, and verifying restored state |
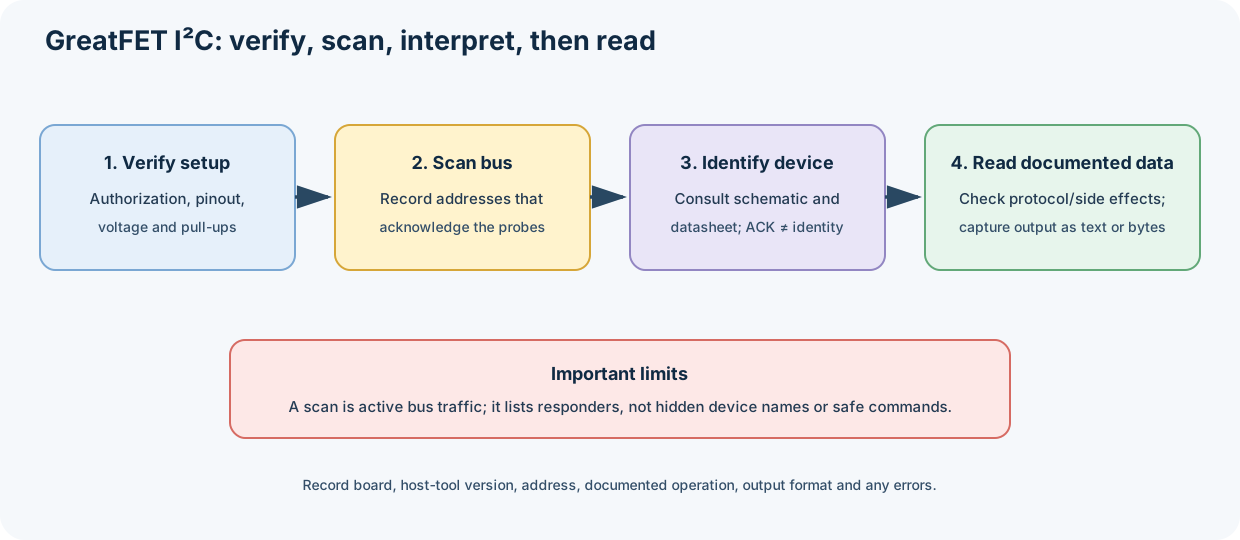
| GreatFET I2C observation | GreatFET One | Bus ownership, voltage, and observation gates |
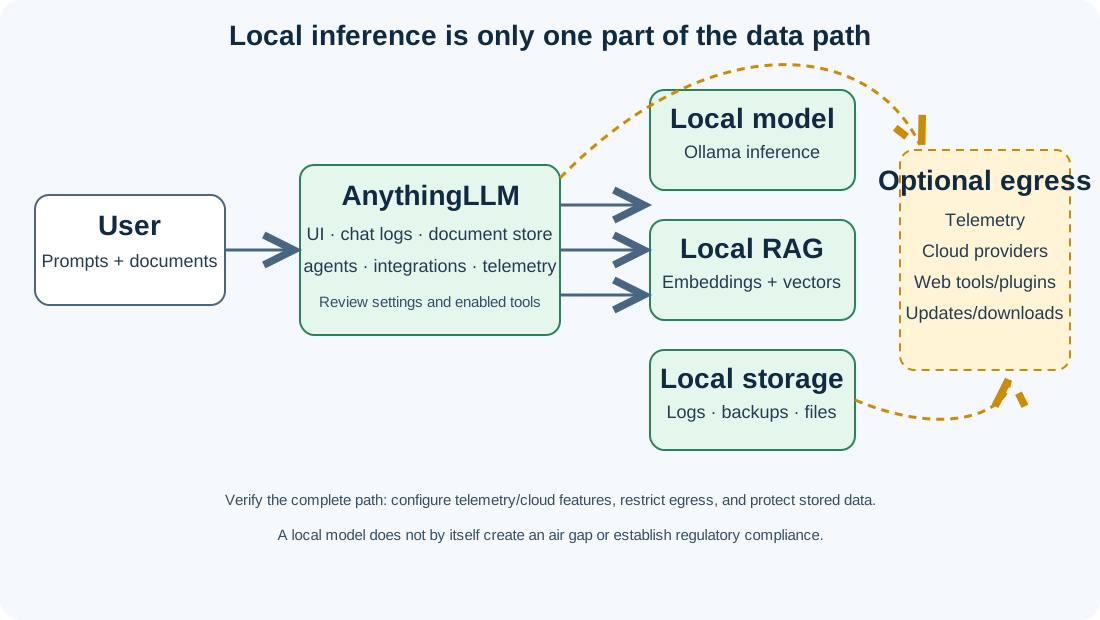
| Local LLM data paths | Offline LLMs | Local, remote, and optional network data paths |
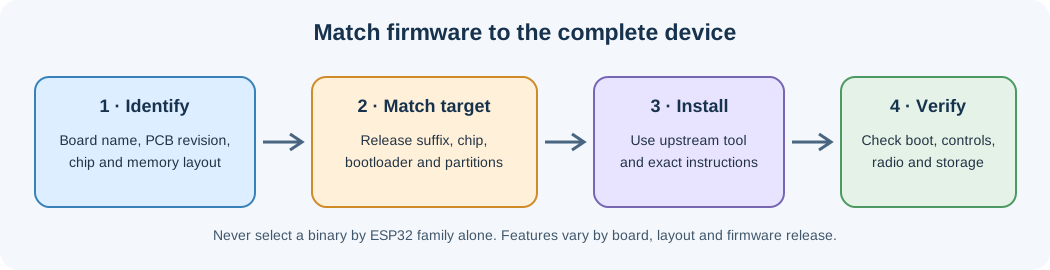
| Marauder firmware selection | Wi-Fi Marauder guide | Board compatibility and firmware verification |
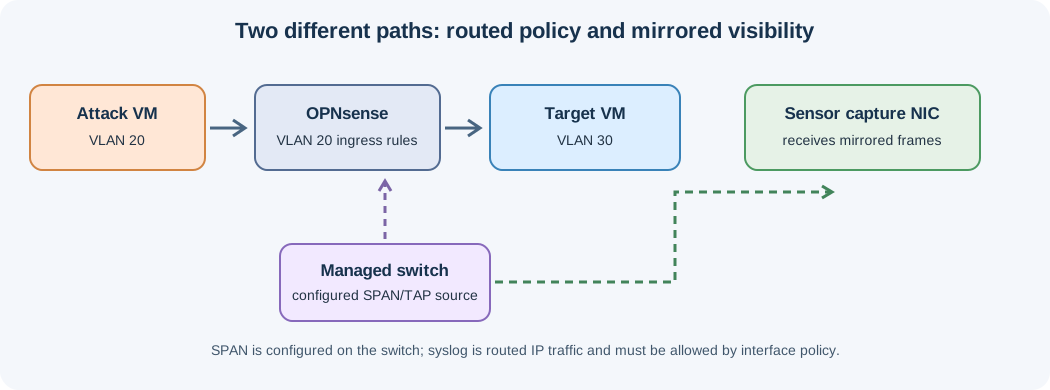
| OPNsense rules and SPAN visibility | Homelab setup | Distinguishes firewall enforcement from sensor visibility |
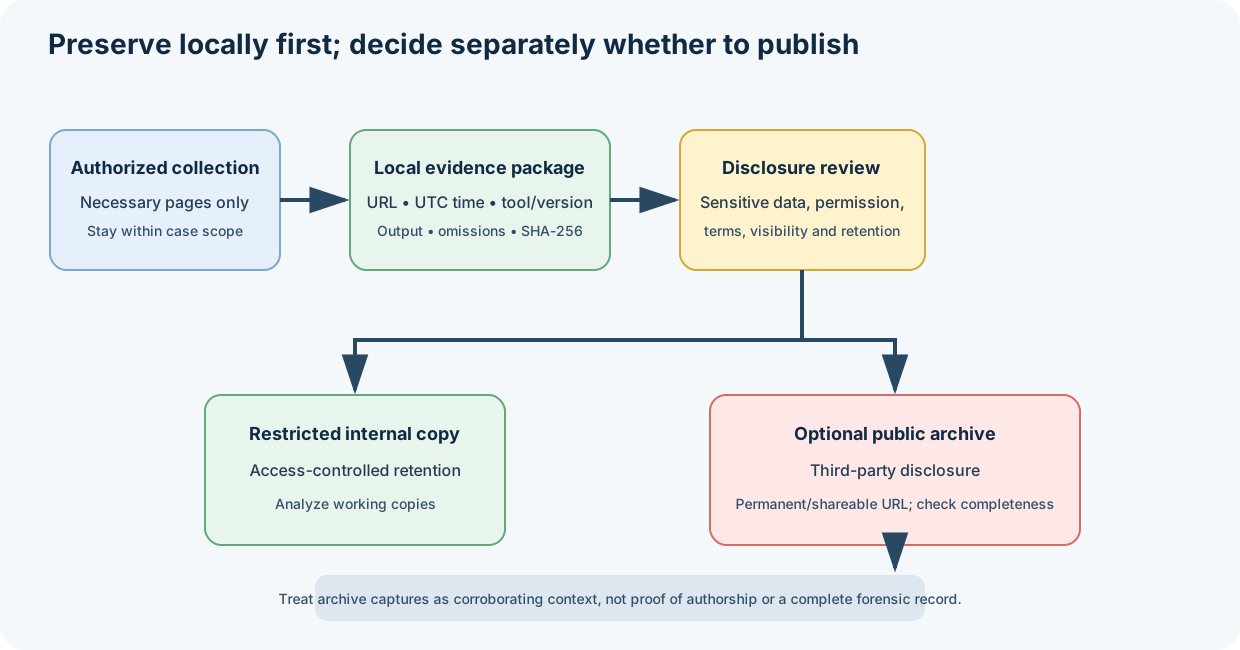
| OSINT evidence publication | OSINT guide | Source corroboration and release review |
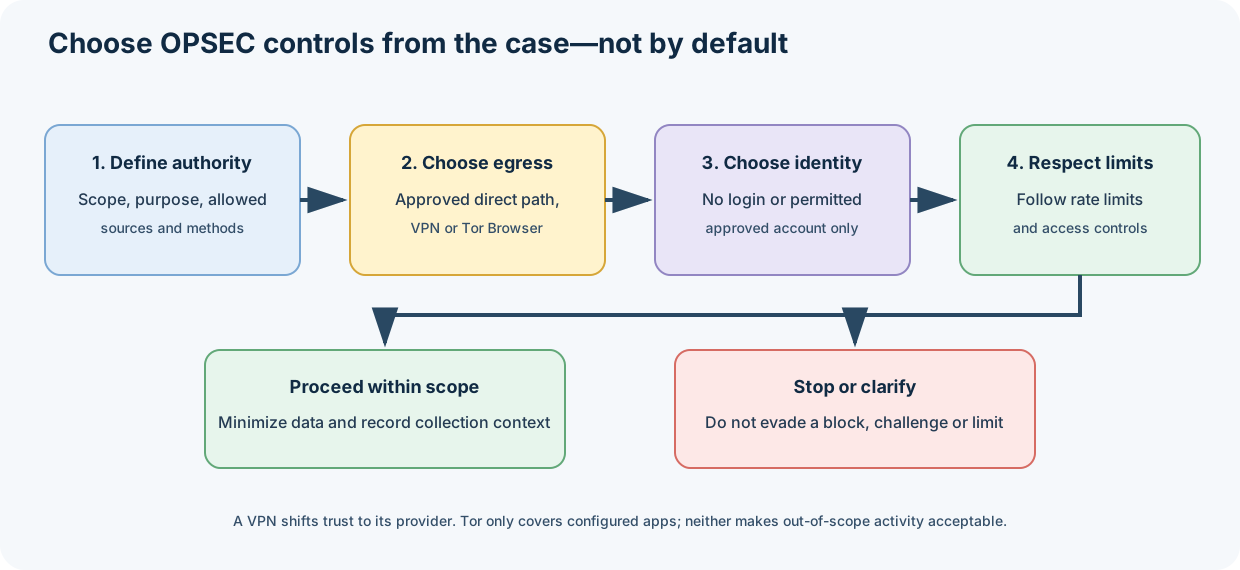
| OSINT scope and collection | Linux cheat sheet, OSINT index | Scope checks and permitted collection |
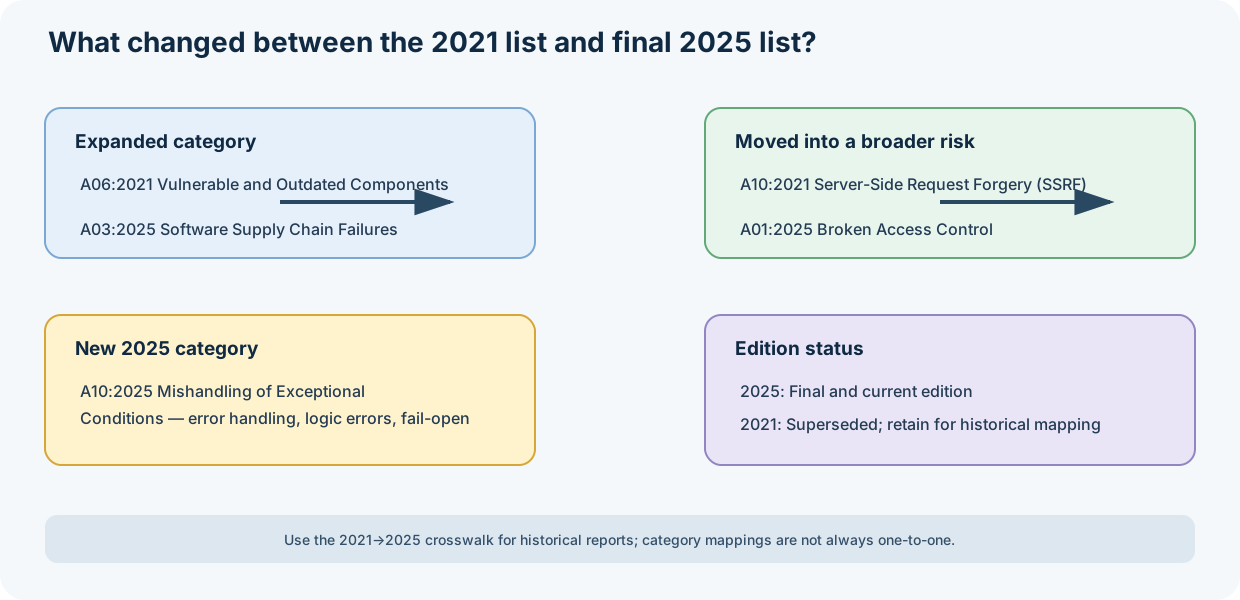
| OWASP Top 10 category changes | OWASP Top 10 | Category changes between editions |
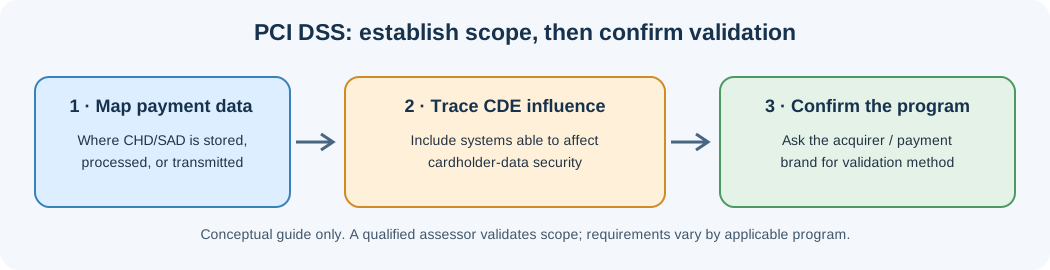
| PCI DSS scope and validation | Compliance overview | Scope, applicability, and validation evidence |
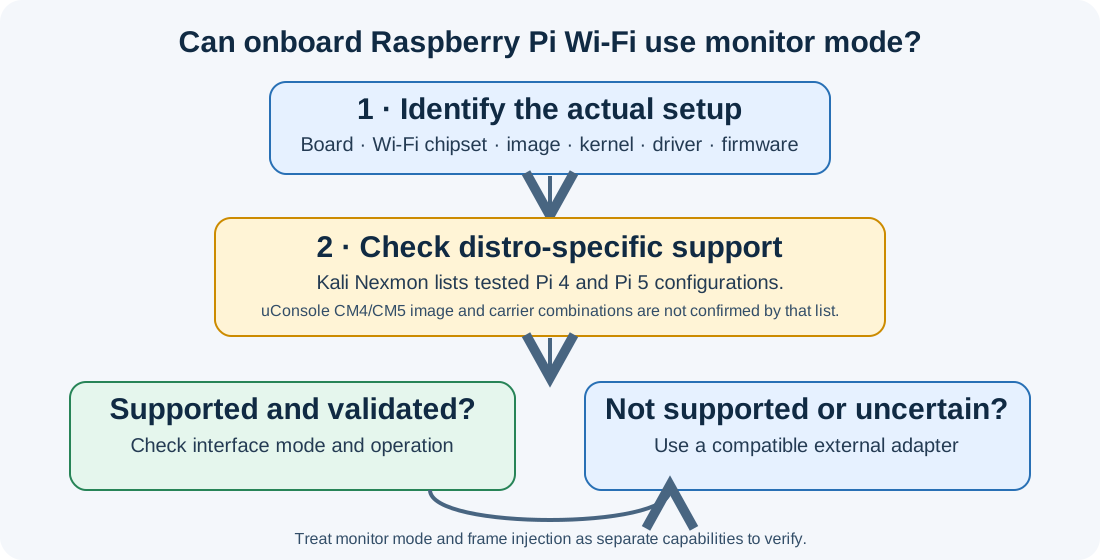
| Raspberry Pi onboard Wi-Fi support | Specialized Topics, CM5 setup | Board, chipset, and driver compatibility checks |
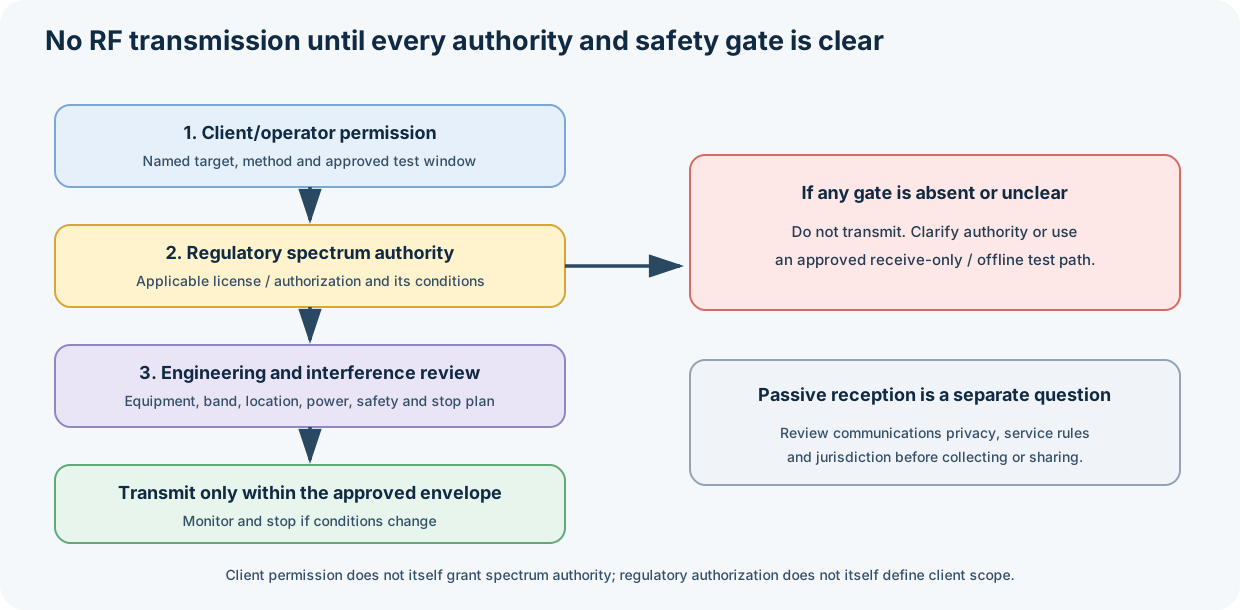
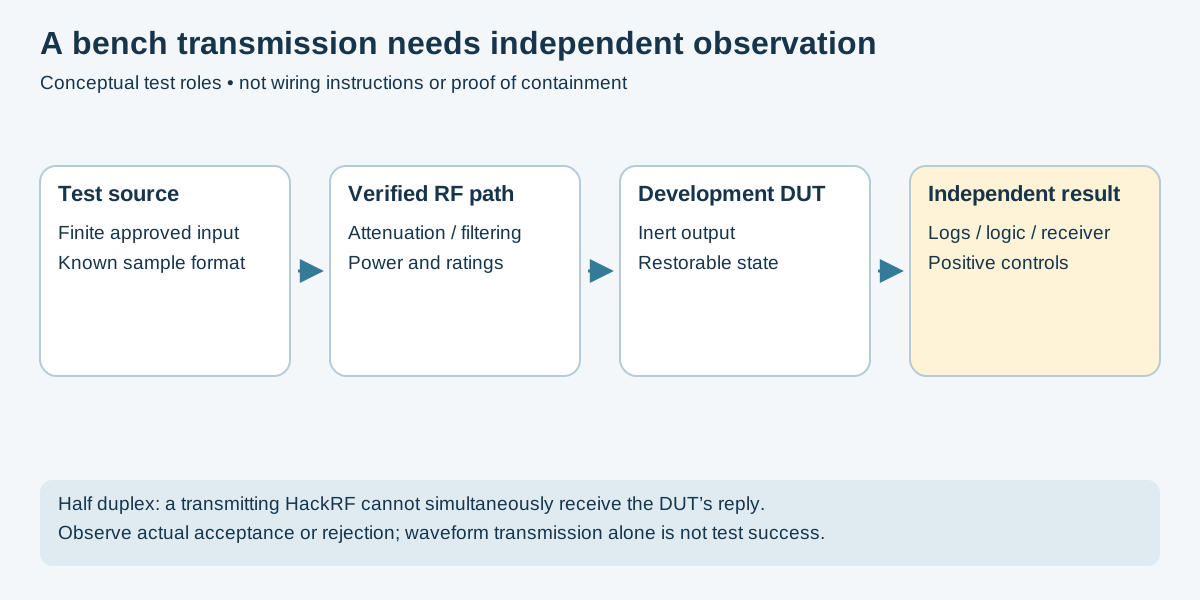
| Space RF testing authorization | Space Security Part I | Boundaries for receive-only observation and authorized transmission |
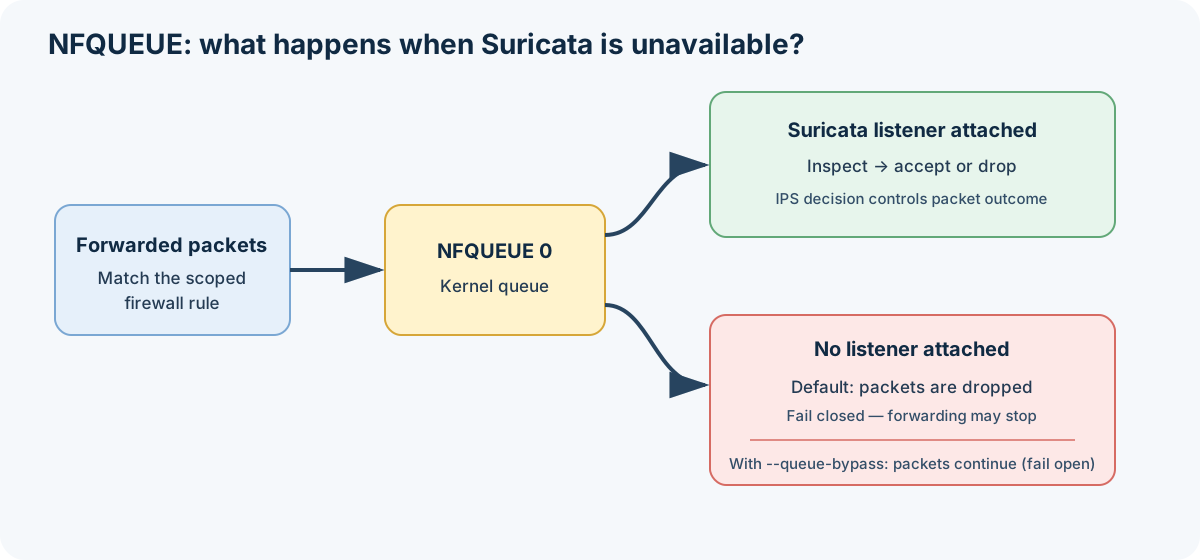
| Suricata NFQUEUE failure modes | Suricata and Zeek | Packet handling when the inspection path is unavailable |
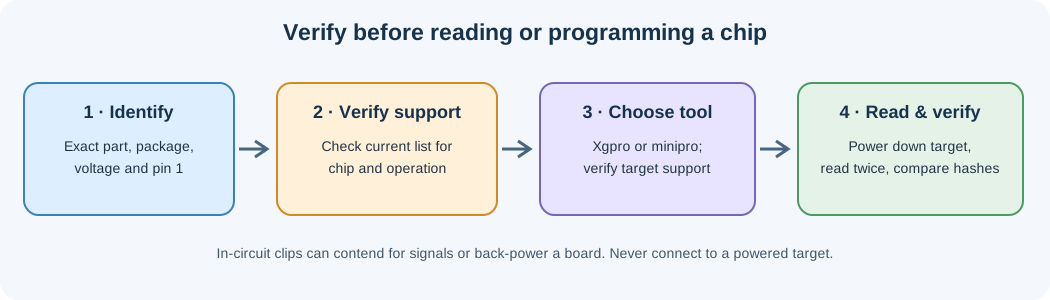
| T48 supported chip reading | T48 programmer | Part identification, voltage, and readback verification |
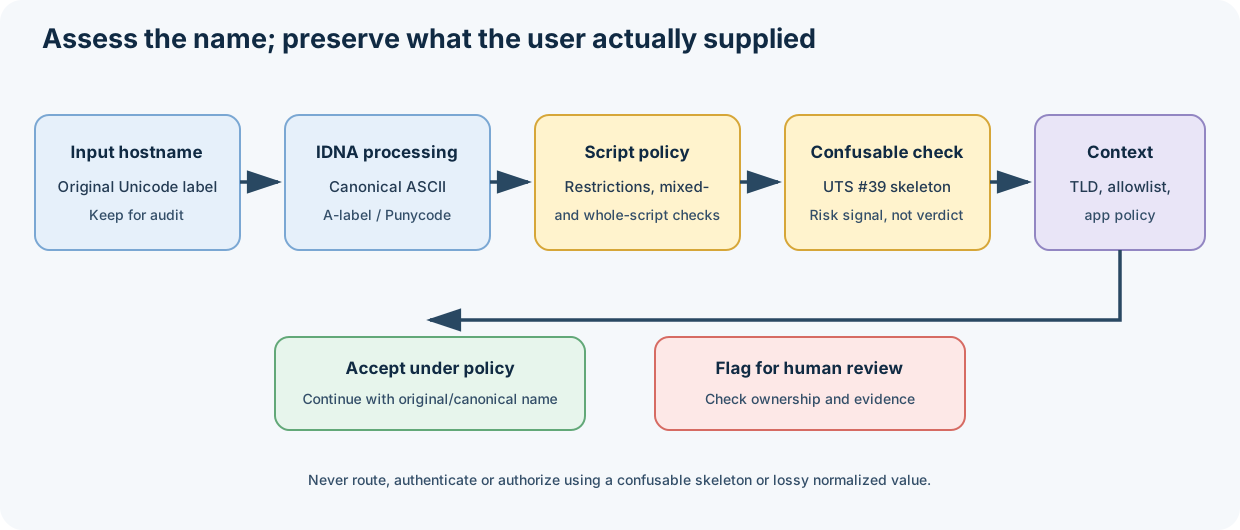
| Unicode and IDN risk assessment | Classical cryptography security | Interpretation of visual similarity in identifiers |
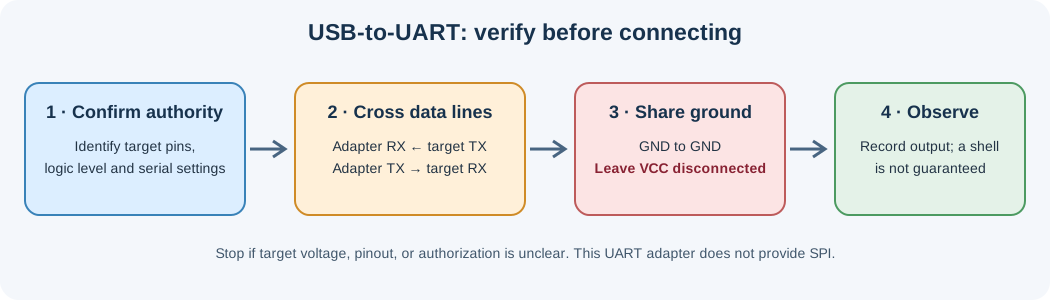
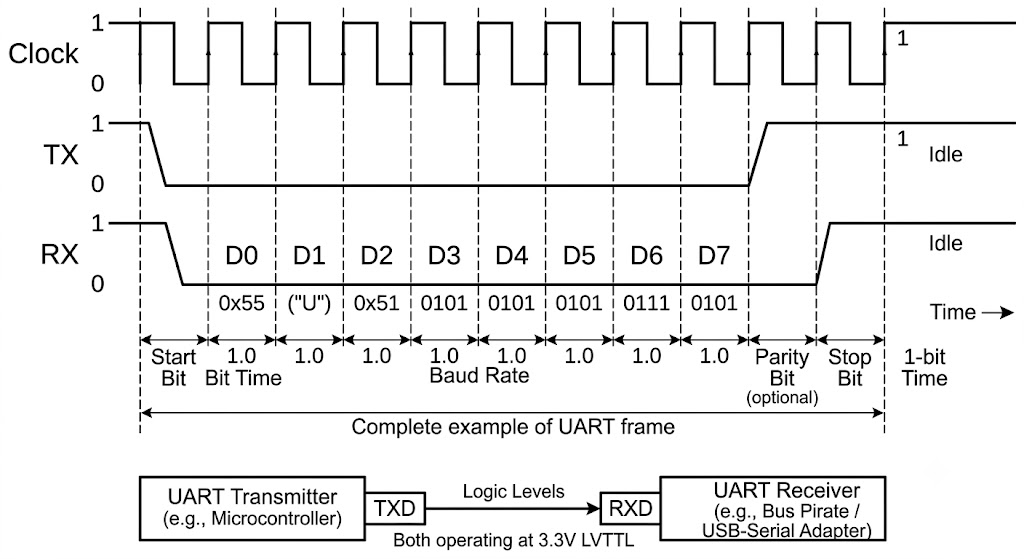
| USB-to-UART safe observation | BitPirate | Voltage checks and receive-only observation |
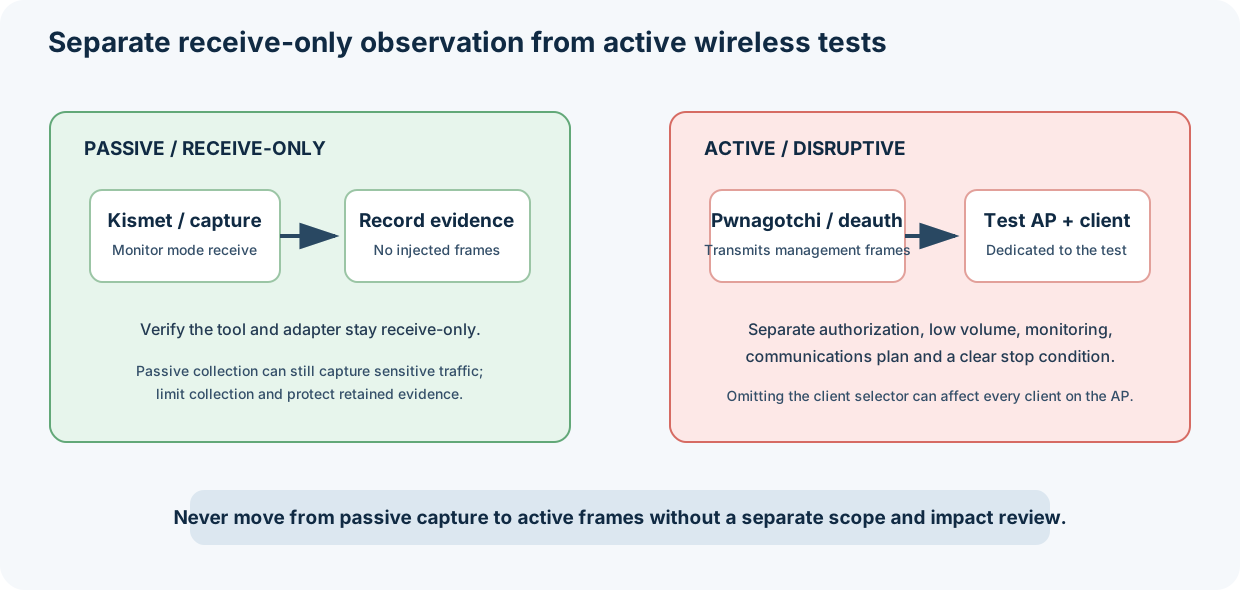
| Passive and active wireless scope | Network audit playbook | Separates passive observations from actions requiring approval |
| Diagram | Where embedded | Why it belongs |
|---|---|---|
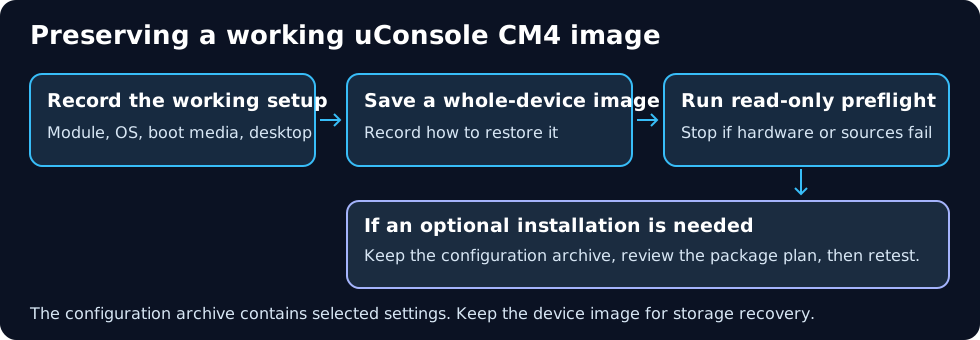
| Preserving a working CM4 image | CM4 first-boot audit | Distinguishes whole-device recovery, read-only preflight and optional configuration archives |
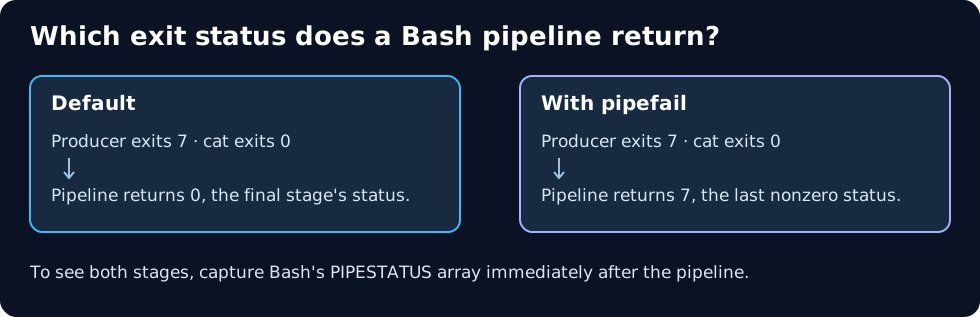
| Bash pipeline exit status | CLI field reference | Shows where a successful final stage can mask an earlier failure |
| Diagram | Where embedded | Why it belongs |
|---|---|---|
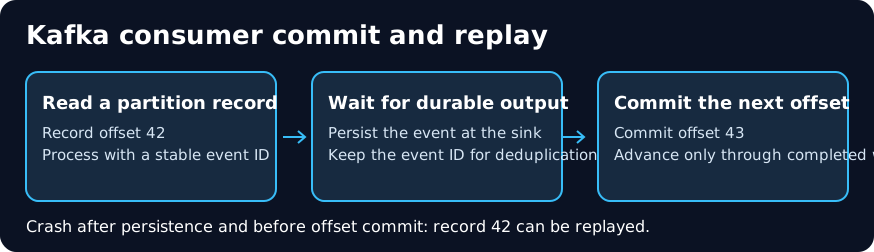
| Kafka consumer commit and replay | Kafka delivery | Shows the replay window between a durable output and committing the next offset |
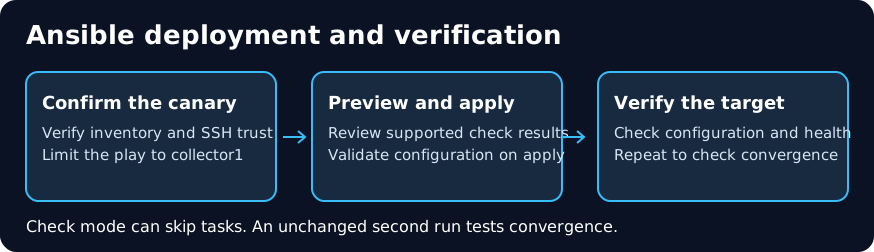
| Ansible deployment and verification | Ansible deployment | Shows target selection, limited preview, application, and independent verification |
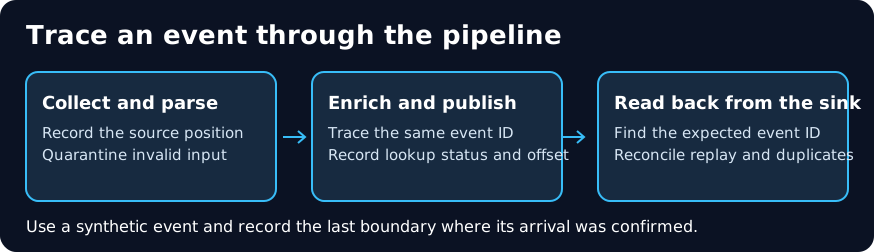
| Trace an event through the pipeline | Integrated pipeline | Shows how to reconcile a synthetic event across processing and sink persistence |
| Diagram | Where embedded | Why it belongs |
|---|---|---|
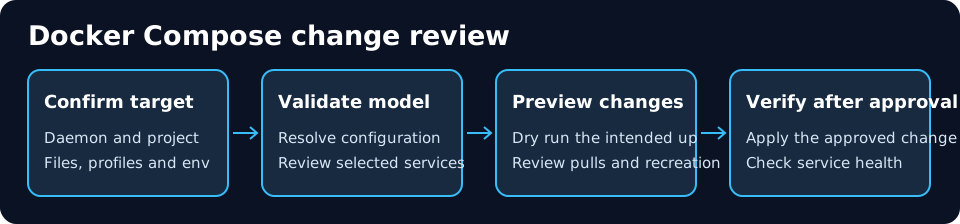
| Compose change review | Docker CLI Operations | Connects target selection, model validation, dry run and post-change health checks |
These are editable SVG reference diagrams embedded within the relevant chapter. They distinguish source-supported architecture from unverified production operation.
| Diagram | Where embedded | Why it belongs |
|---|---|---|
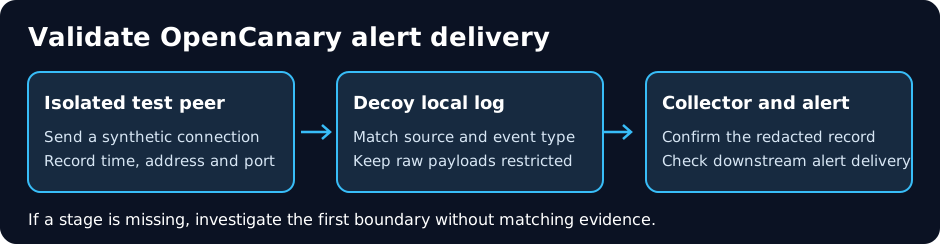
| OpenCanary alert validation | OpenCanary | Confirms a synthetic event at the local log and the alert destination |
| Wazuh Honeypot Telemetry Evidence Path | Wazuh Honeypot Integration | Separate logs, agent collection, manager rules, index and analyst review |
| CDC Snapshot/Offset Replay Boundary | Streaming & Change Data Capture | Explain coordinated snapshot handoff, source positions, tombstones and idempotent replay |
| RPO/RTO & Recovery Timeline | Backup, Replay & Disaster Recovery | Distinguish trusted backup point, retained changes, restore time and verified cutover |
| Web Application Authorization Matrix | Web Application Testing Methodology | Horizontal ownership checks, vertical privileges and server-side subject-object-action decisions |
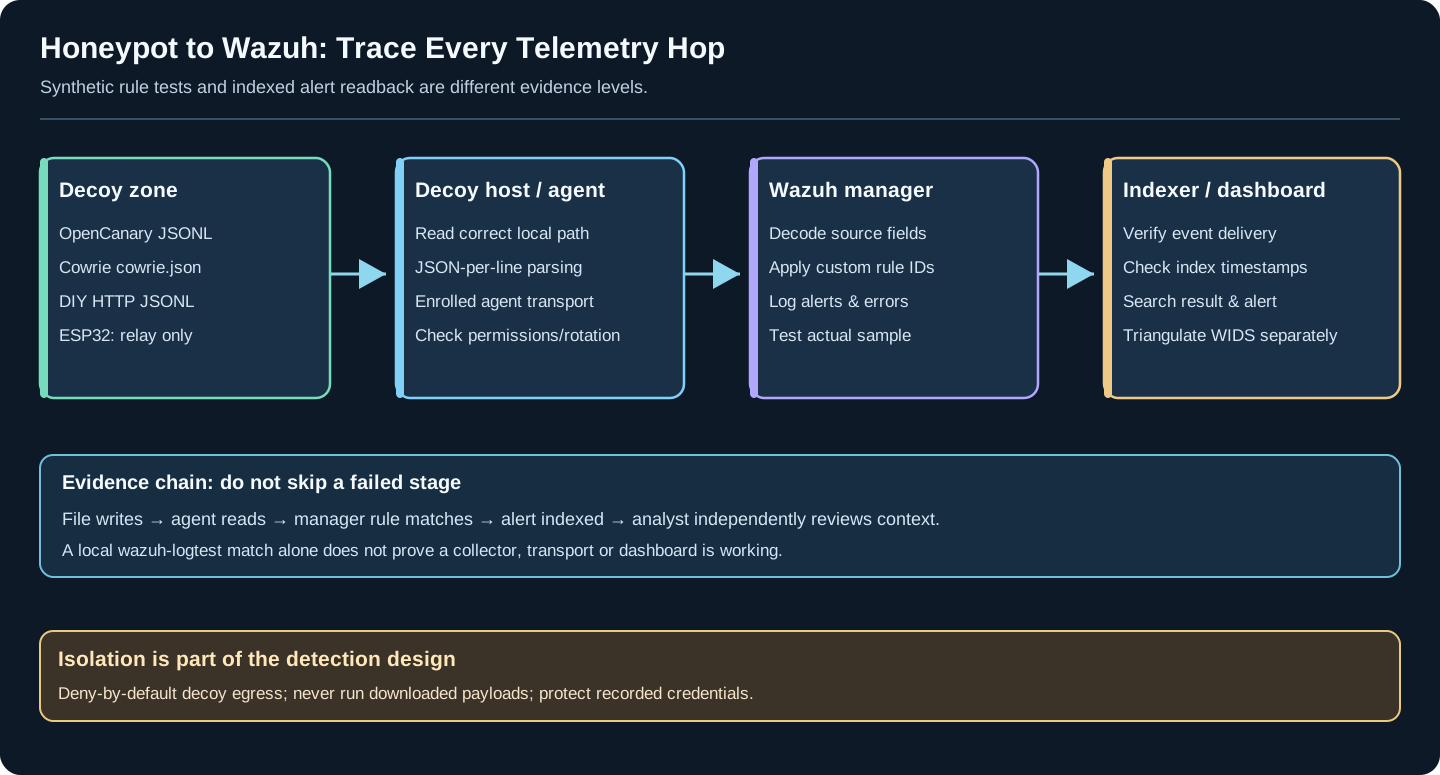
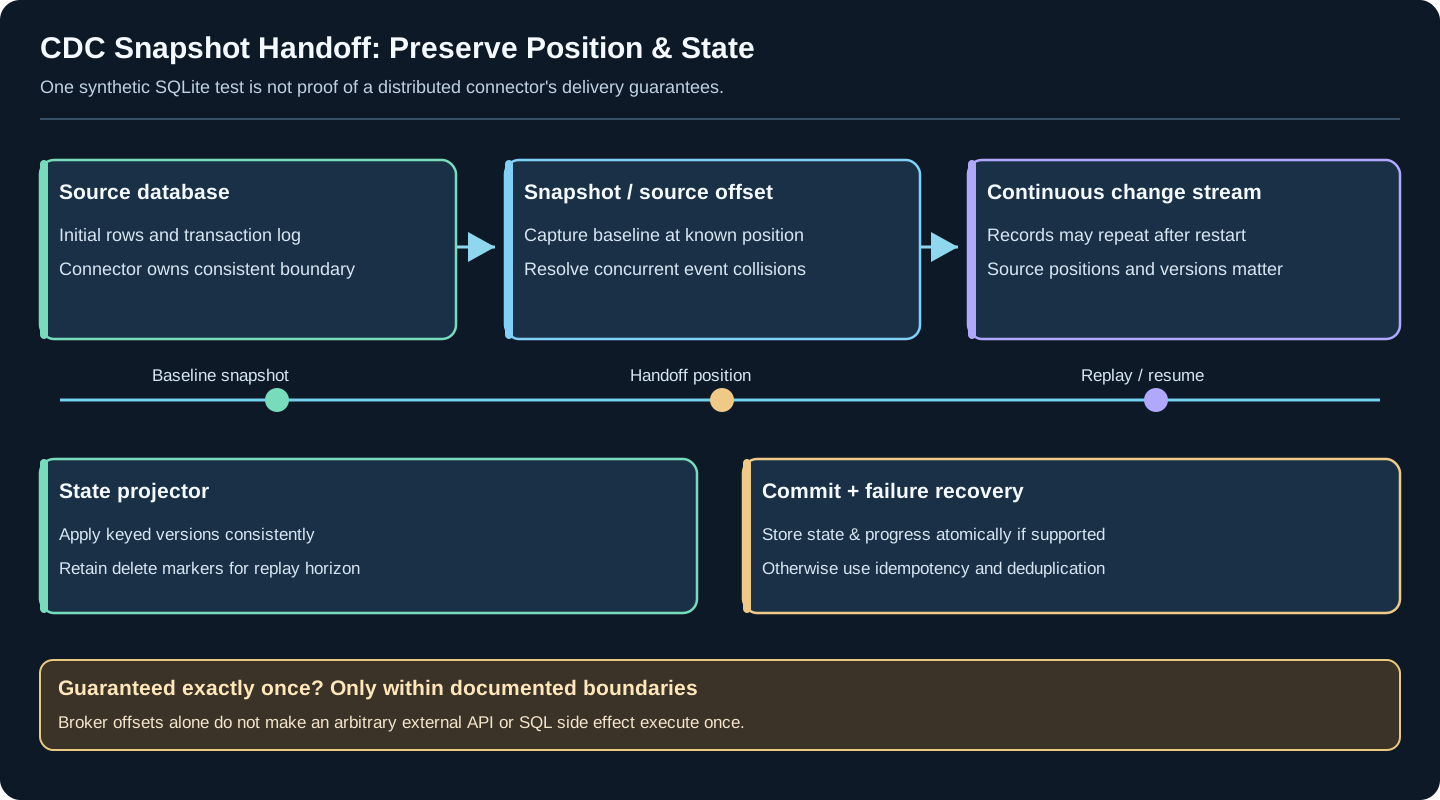
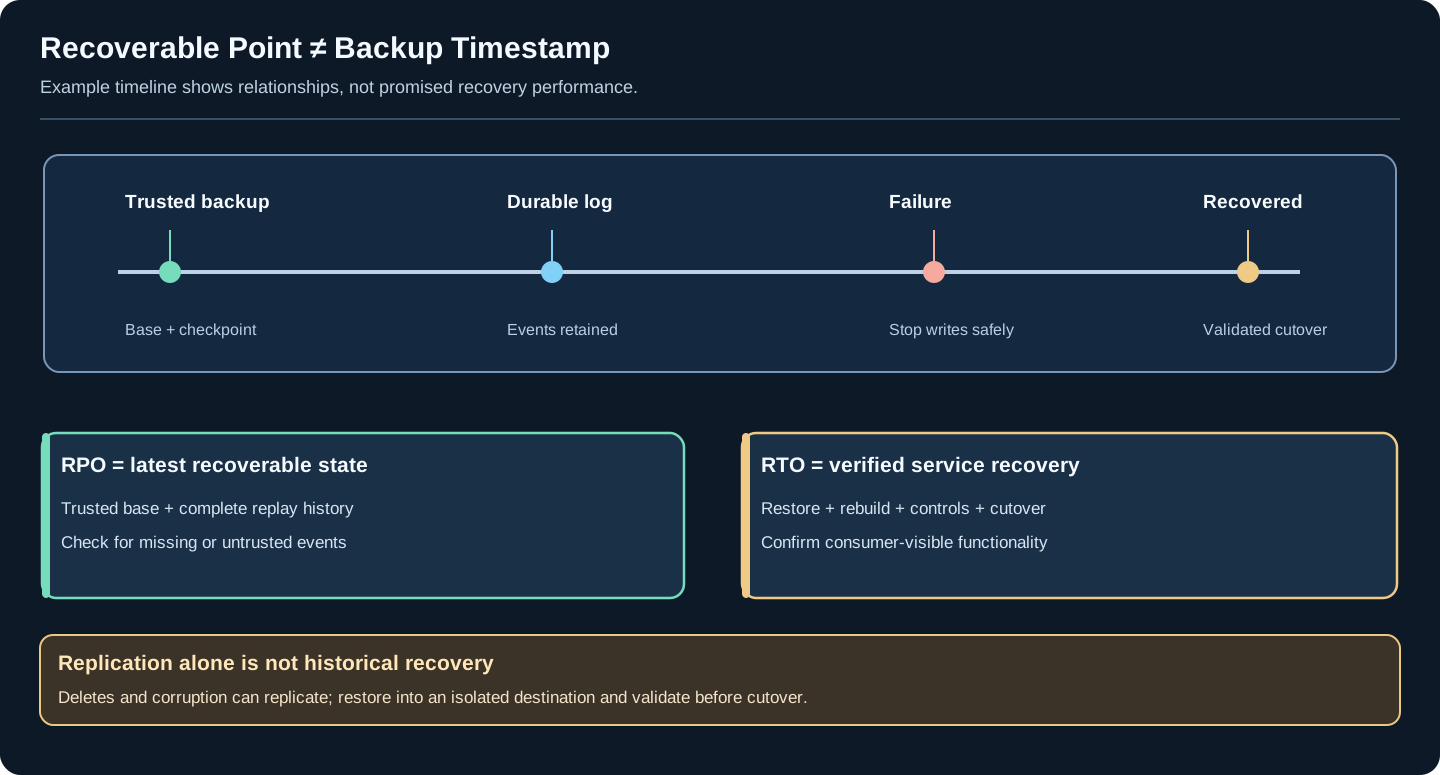
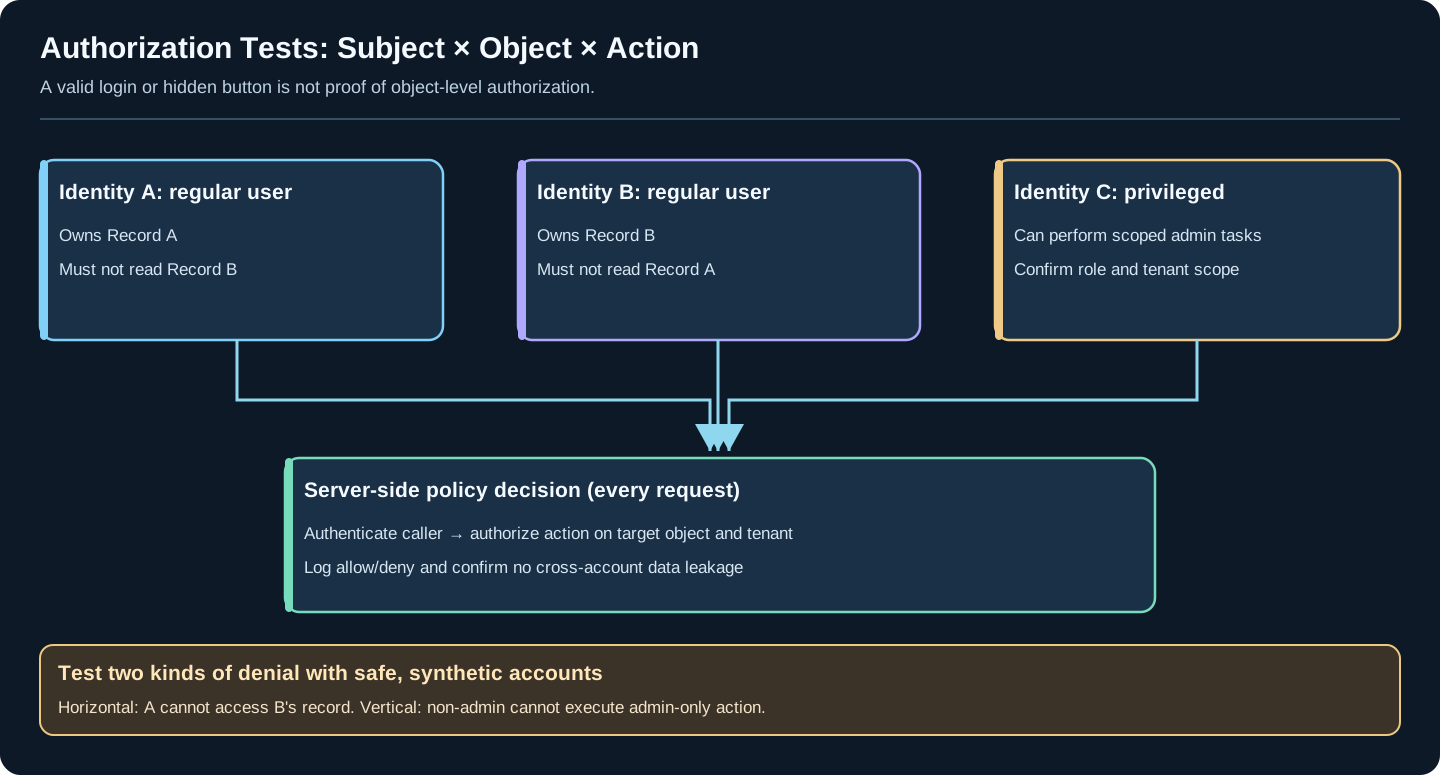
| Diagram | Embedded Guide | Why It Helps |
|---|---|---|
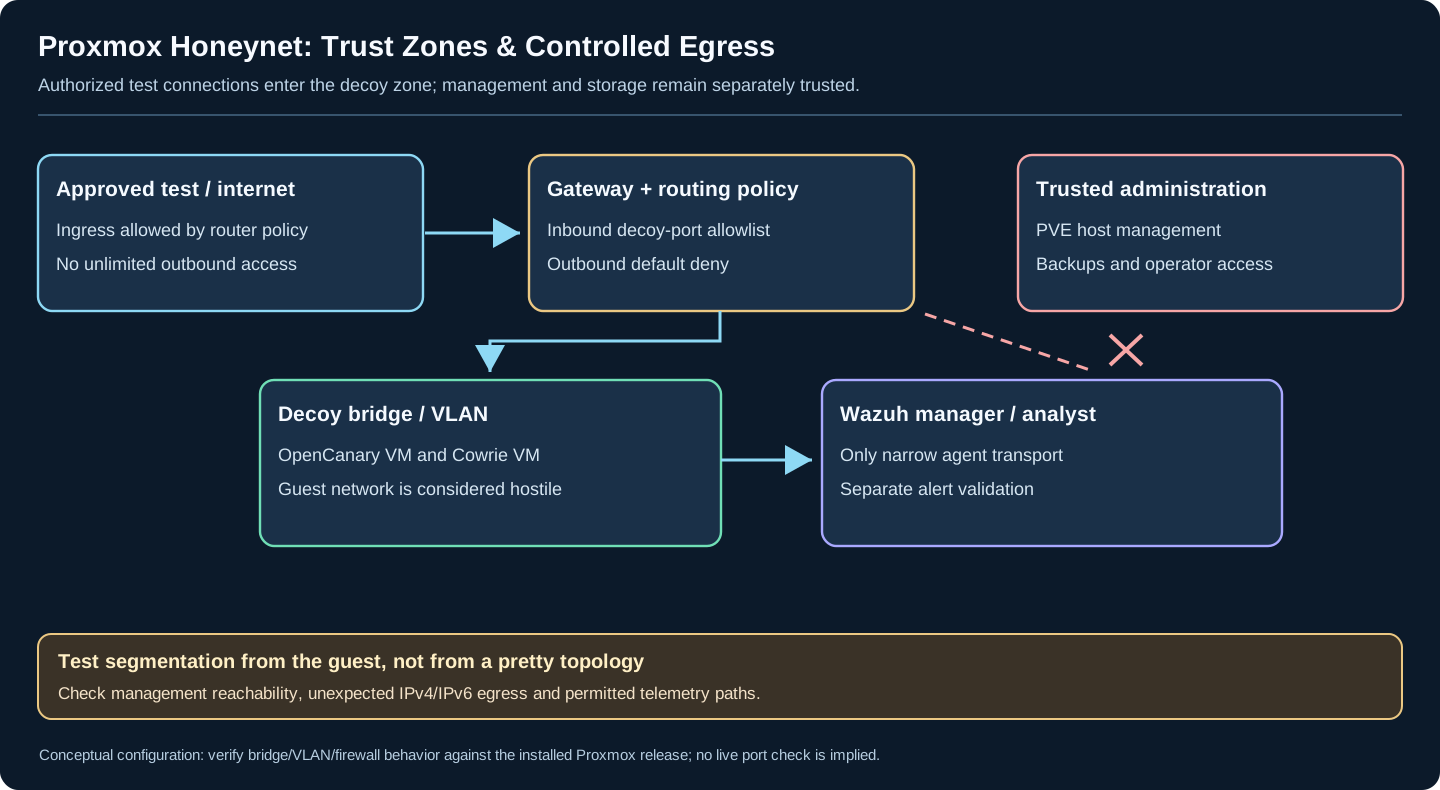
| Proxmox Honeynet Trust Zones | Proxmox VM Honeynet | Shows restricted decoy ingress, agent telemetry path and protected management plane |
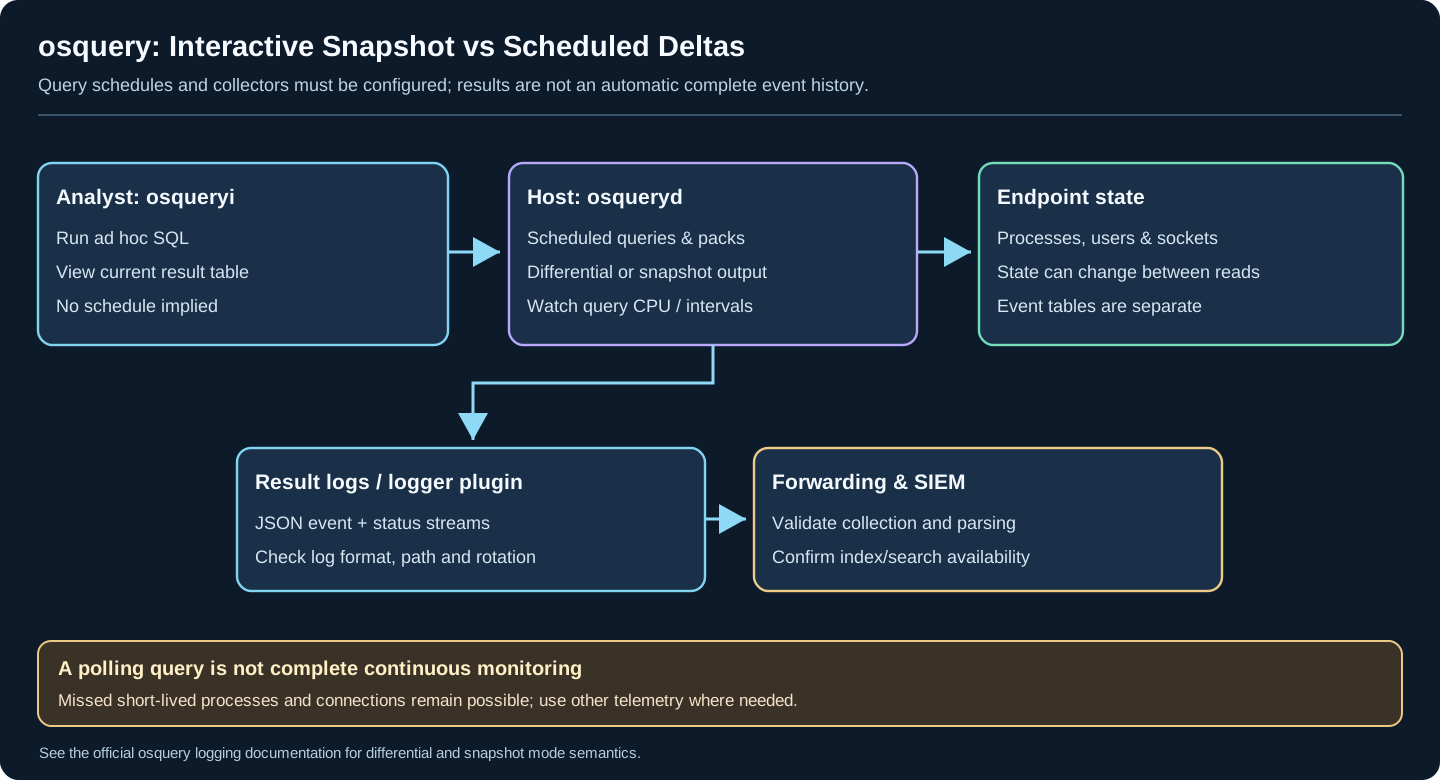
| osquery Interactive vs Scheduled Results | Linux osquery Deployment | Differentiates interactive snapshots, scheduled differential results, logger and SIEM visibility |
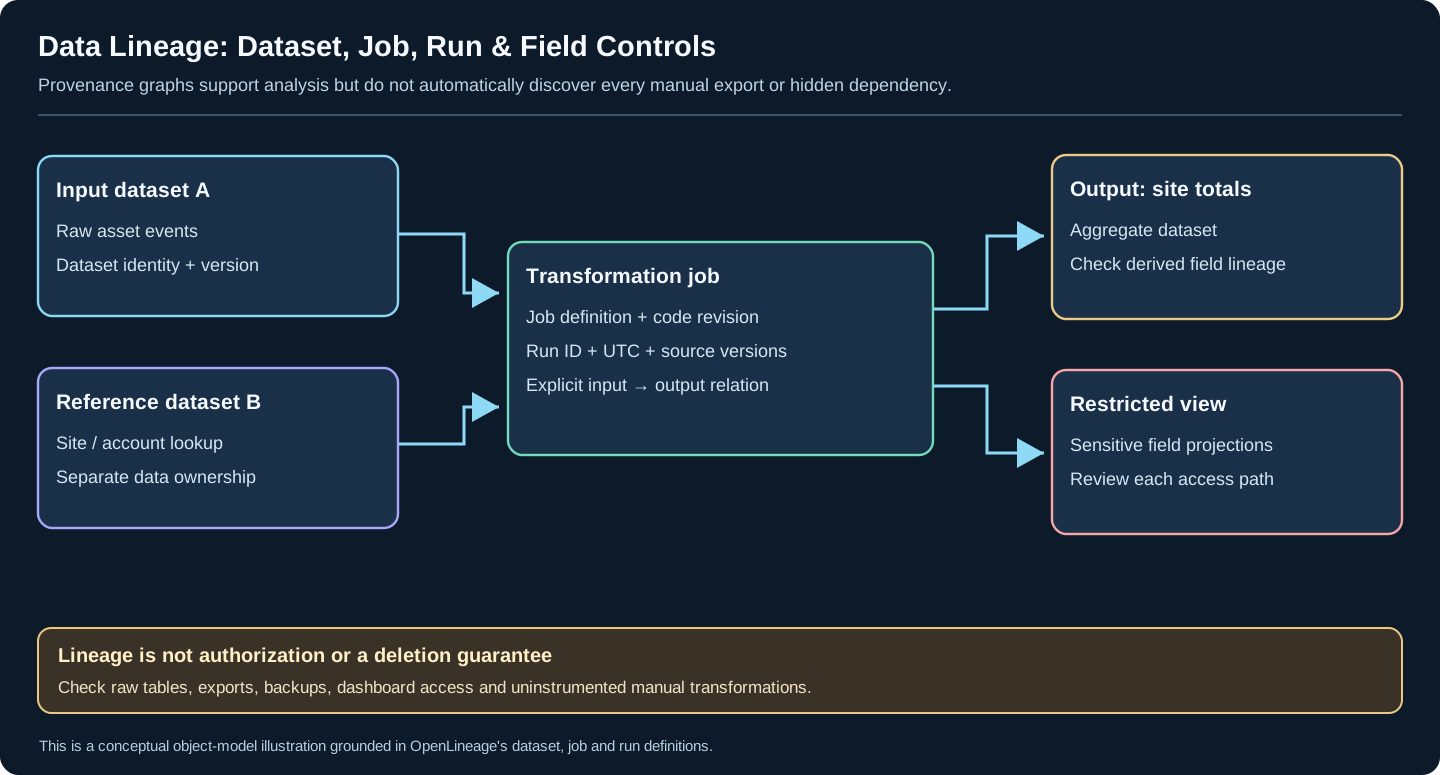
| Dataset / Job / Run Lineage & Access | Data Governance & Lineage | Multi-input transformations, run provenance, restricted outputs and controls outside graph |
| Diagram | Embedded Guide | Reference Concept |
|---|---|---|
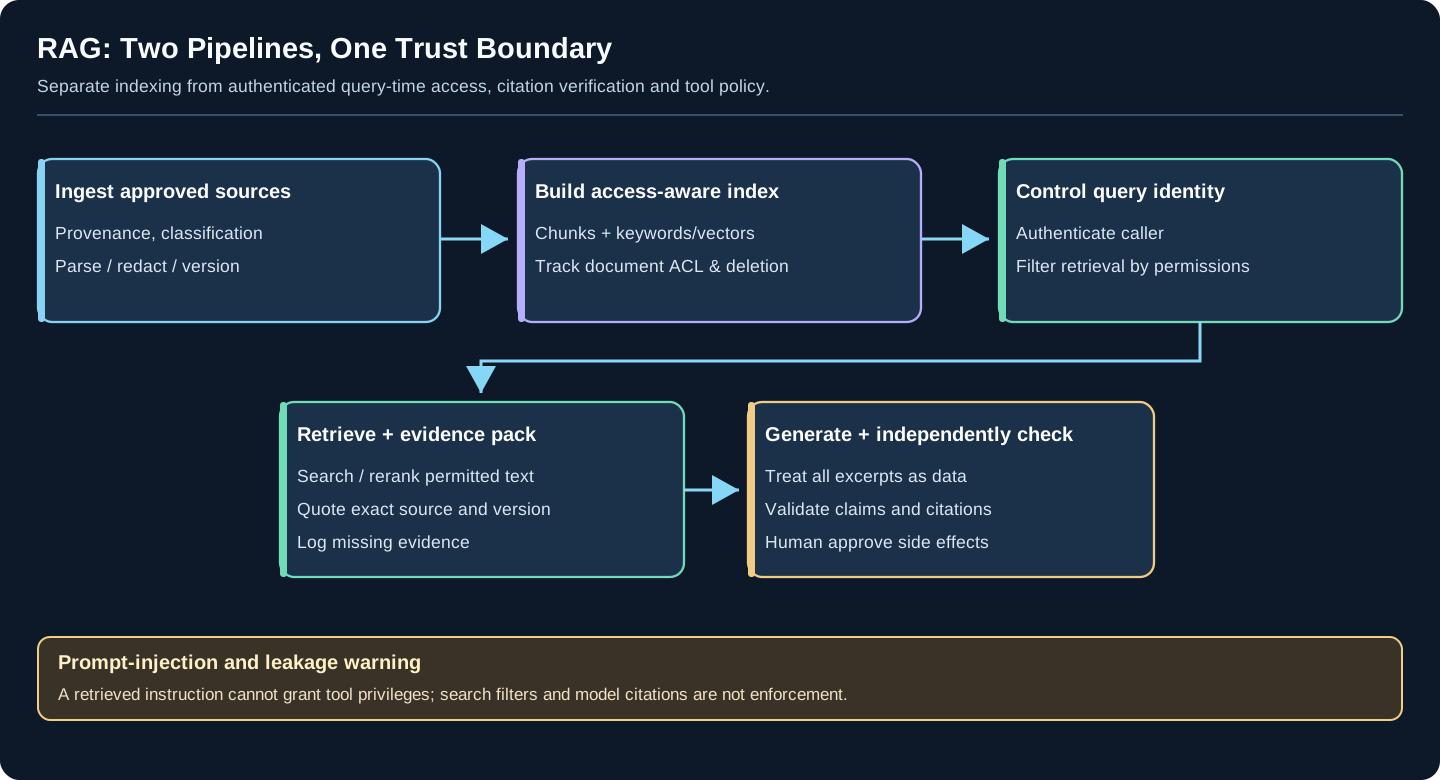
| RAG Ingestion & Retrieval Permission Boundaries | RAG & Knowledge Engineering | Authorized ingestion, access-aware indexes, untrusted retrieved text, citation and approval |
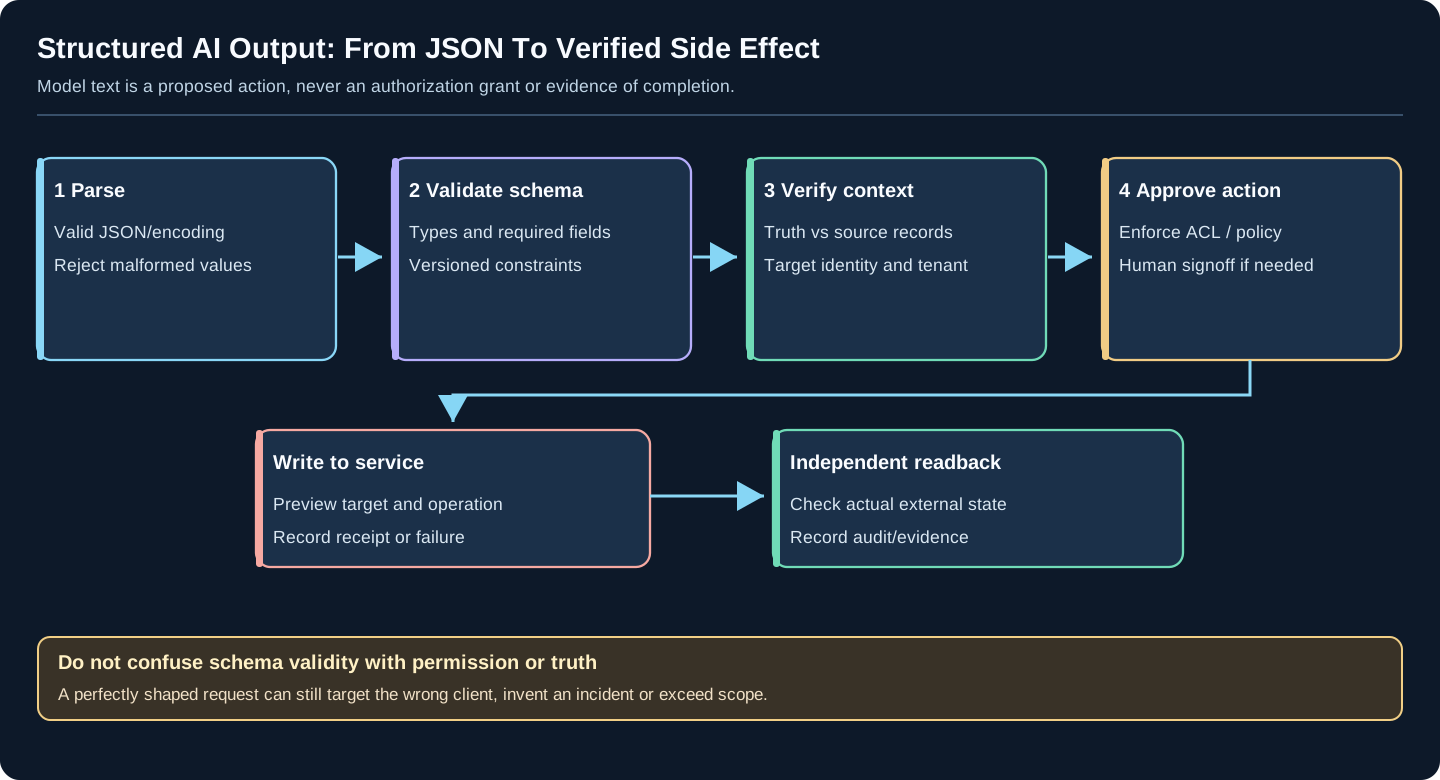
| Structured AI Action Gates | Structured Outputs & Data Contracts | Separate JSON syntax/schema from factual checks, ACL, external writes and readback |
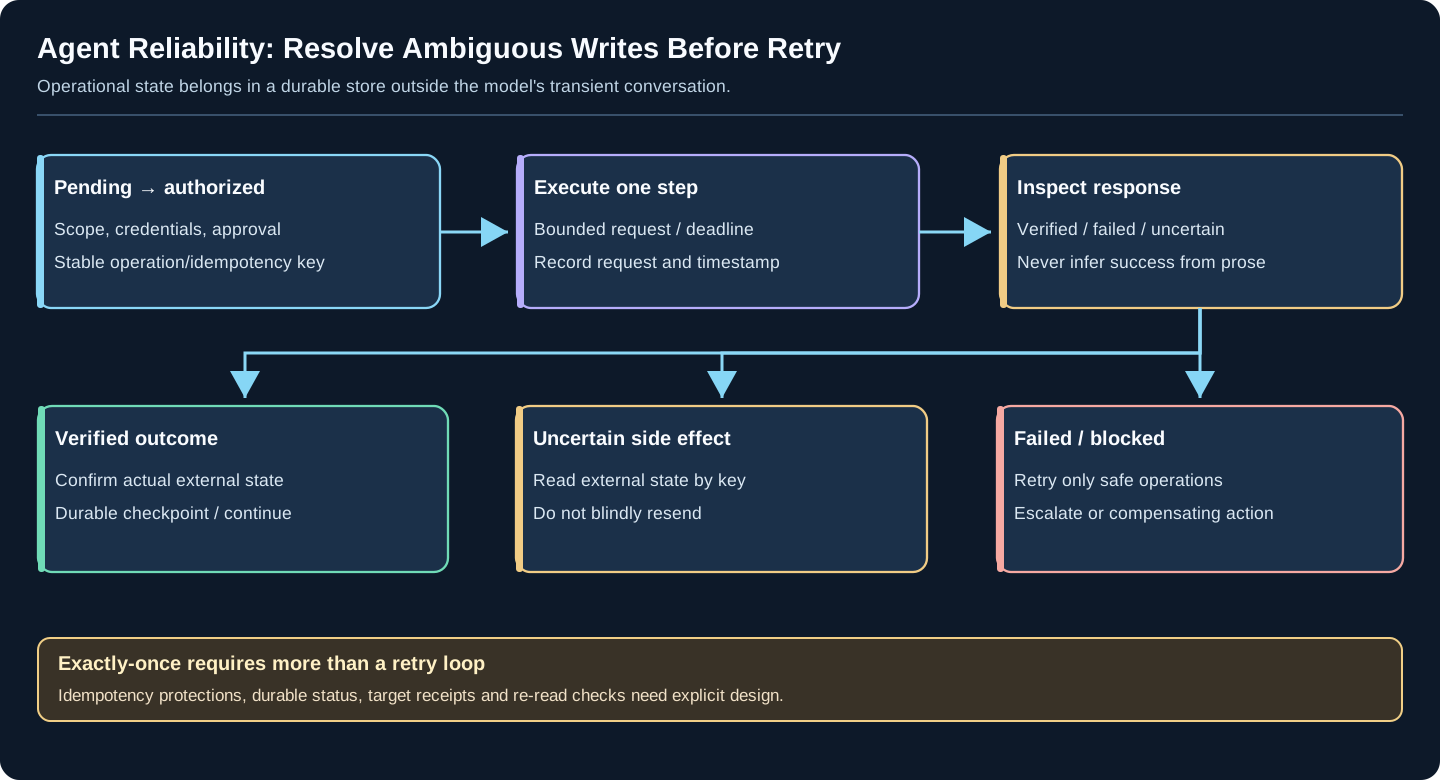
| Agent Ambiguous-Write Reconciliation | AI Reliability & Failure Recovery | Durable state, verified outcome, uncertainty and safe retry with idempotency key |
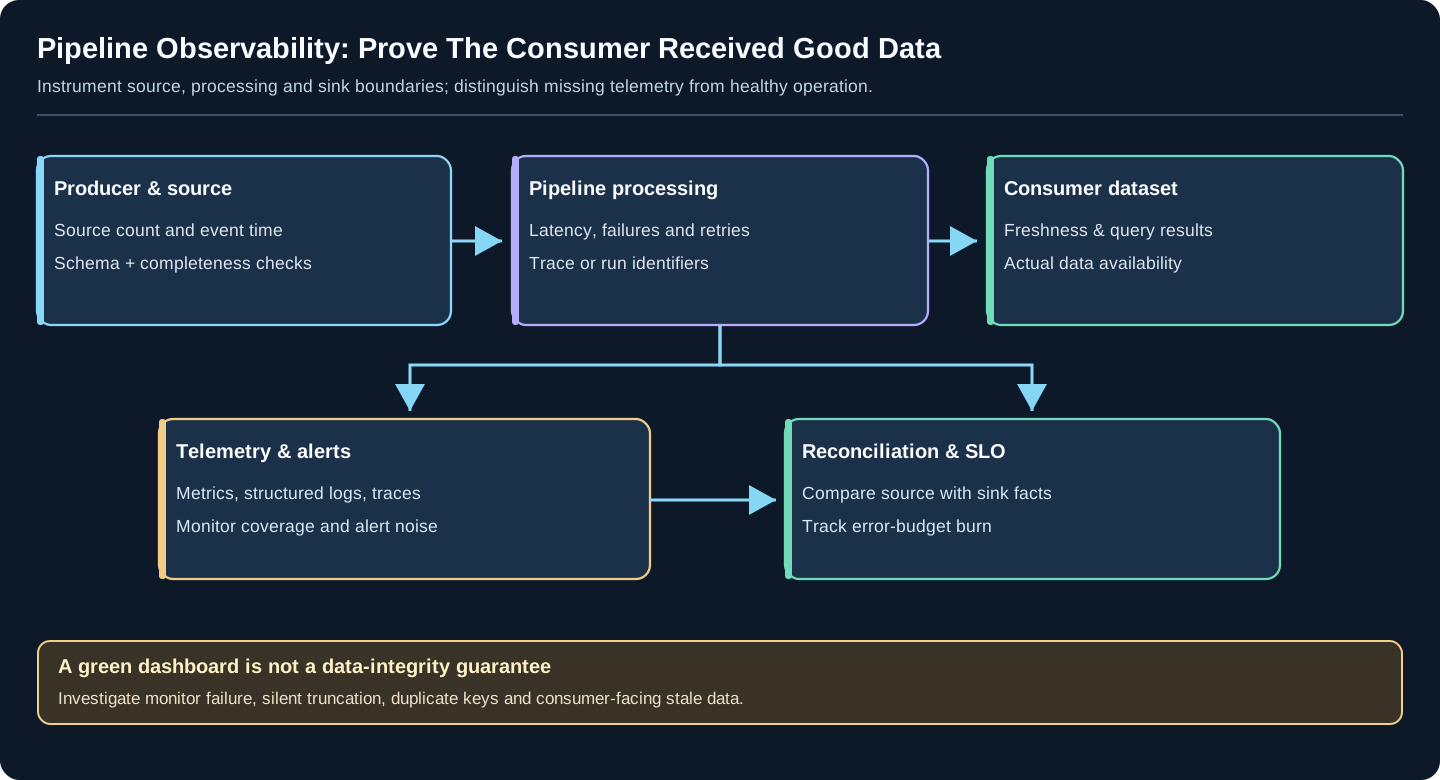
| Pipeline Observability & Reconciliation | Pipeline Observability & Reliability | Production/processing/consumer telemetry, reconciliation, actionable alerts and service objectives |
| Image | Embedded Guide | Source-Checked Boundary |
|---|---|---|
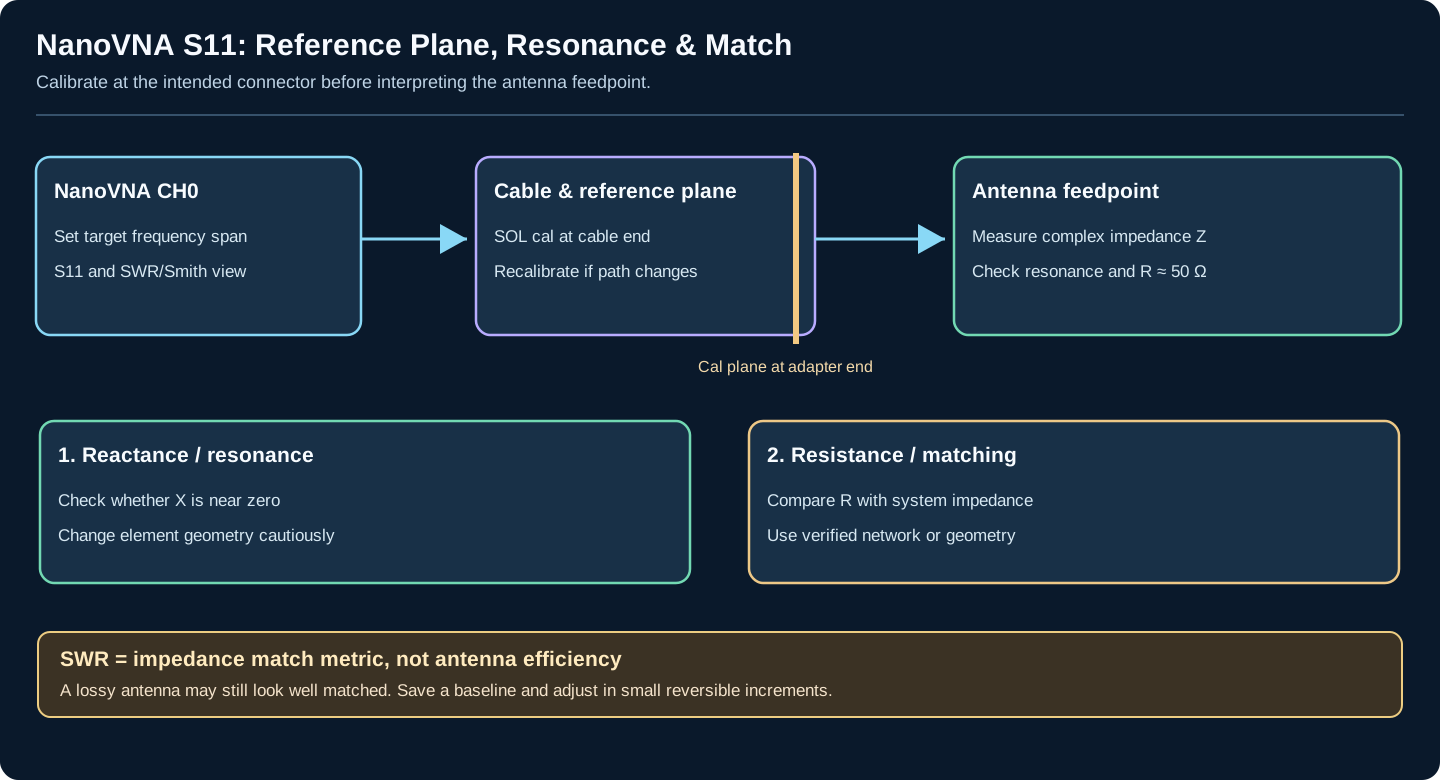
| NanoVNA S11: Resonance & Match | NanoVNA Antenna Tuning & Matching | Calibrated reference plane, complex impedance and distinction between VSWR and radiation efficiency |
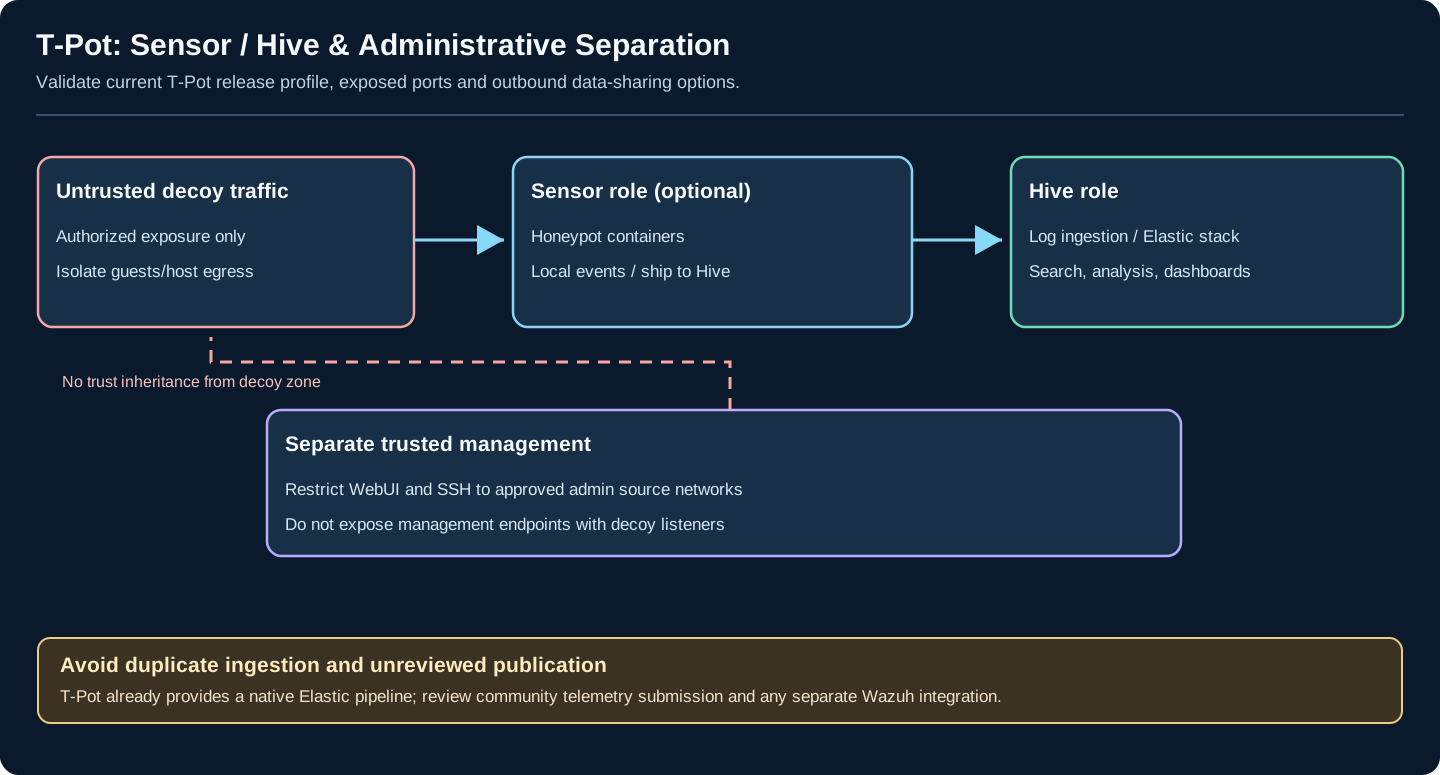
| T-Pot Hive, Sensor & Administration | T-Pot Deployment | Decoy ingress and local sensor logs, optional Hive aggregation, isolated management and community sharing |
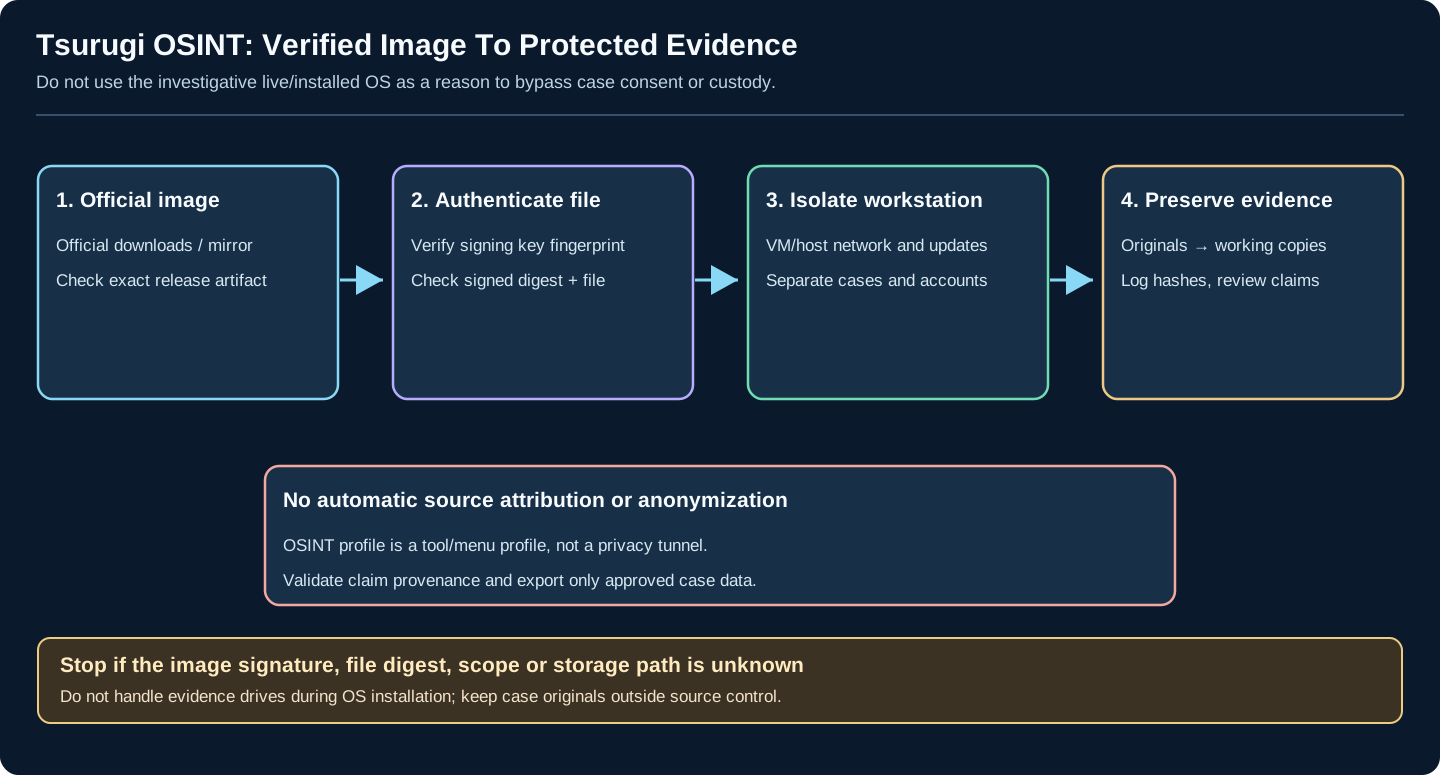
| Tsurugi OSINT Image & Evidence Flow | Tsurugi Linux OSINT Workstation | Official image, verified signed digest, isolated workstation, case-original evidence and reporting |
| Diagram | Embedded guide |
|---|---|
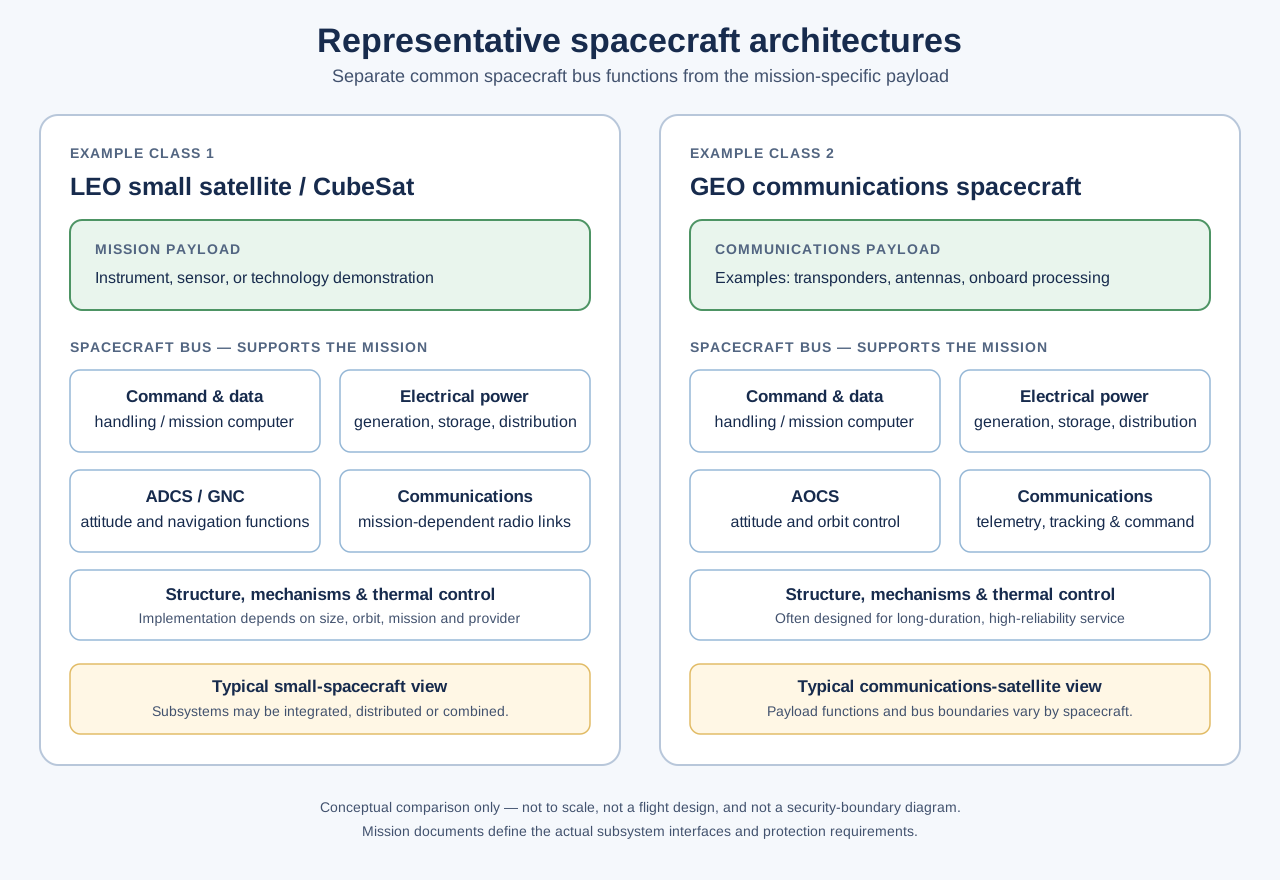
| Spacecraft bus and payload comparison | Space Security appendices |
| Diagram | Embedded Guide | Verified Visual Subject |
|---|---|---|
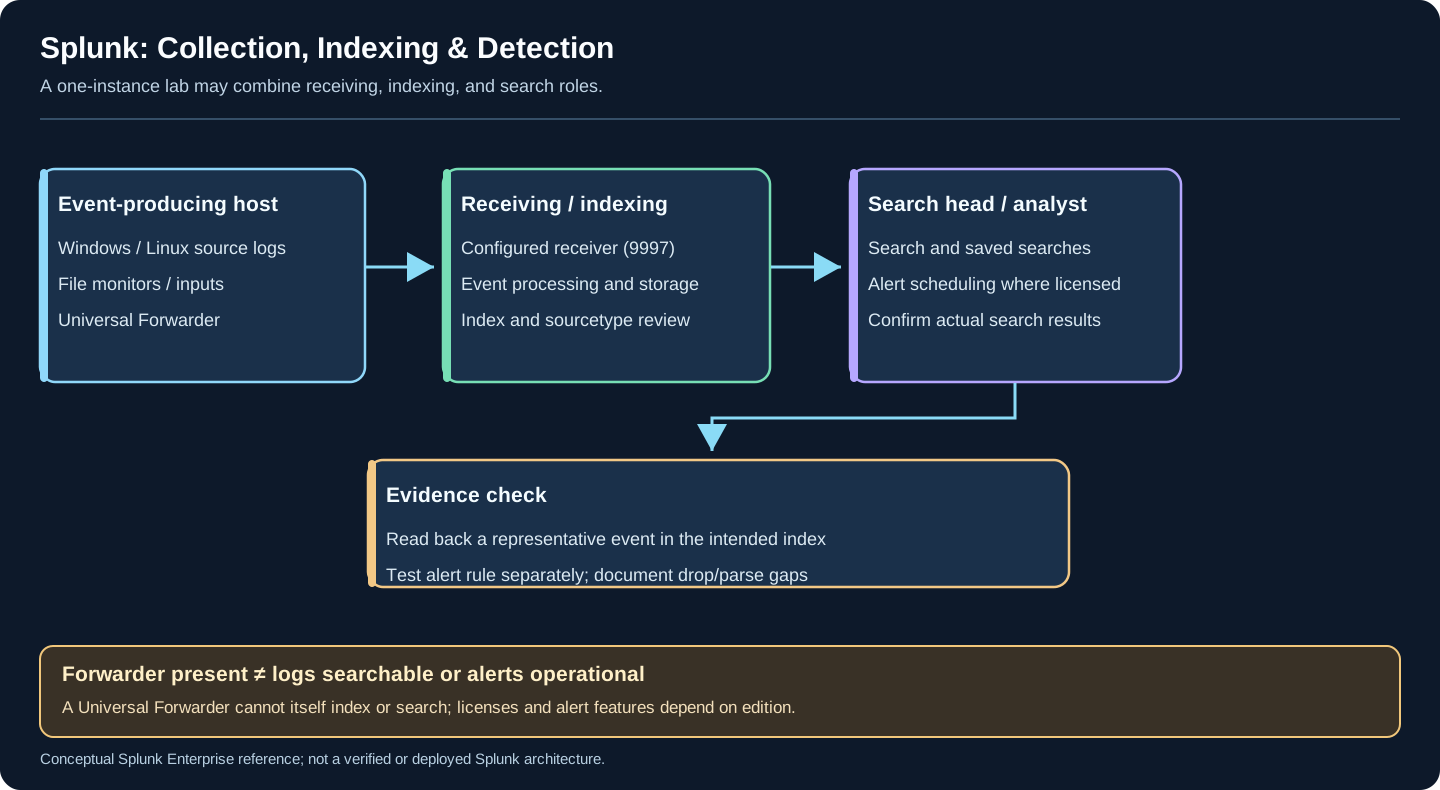
| Splunk Universal Forwarder → Indexer → Search | Splunk SIEM Deployment | Universal Forwarder cannot index or search; storage/search/alerting are independently checked |
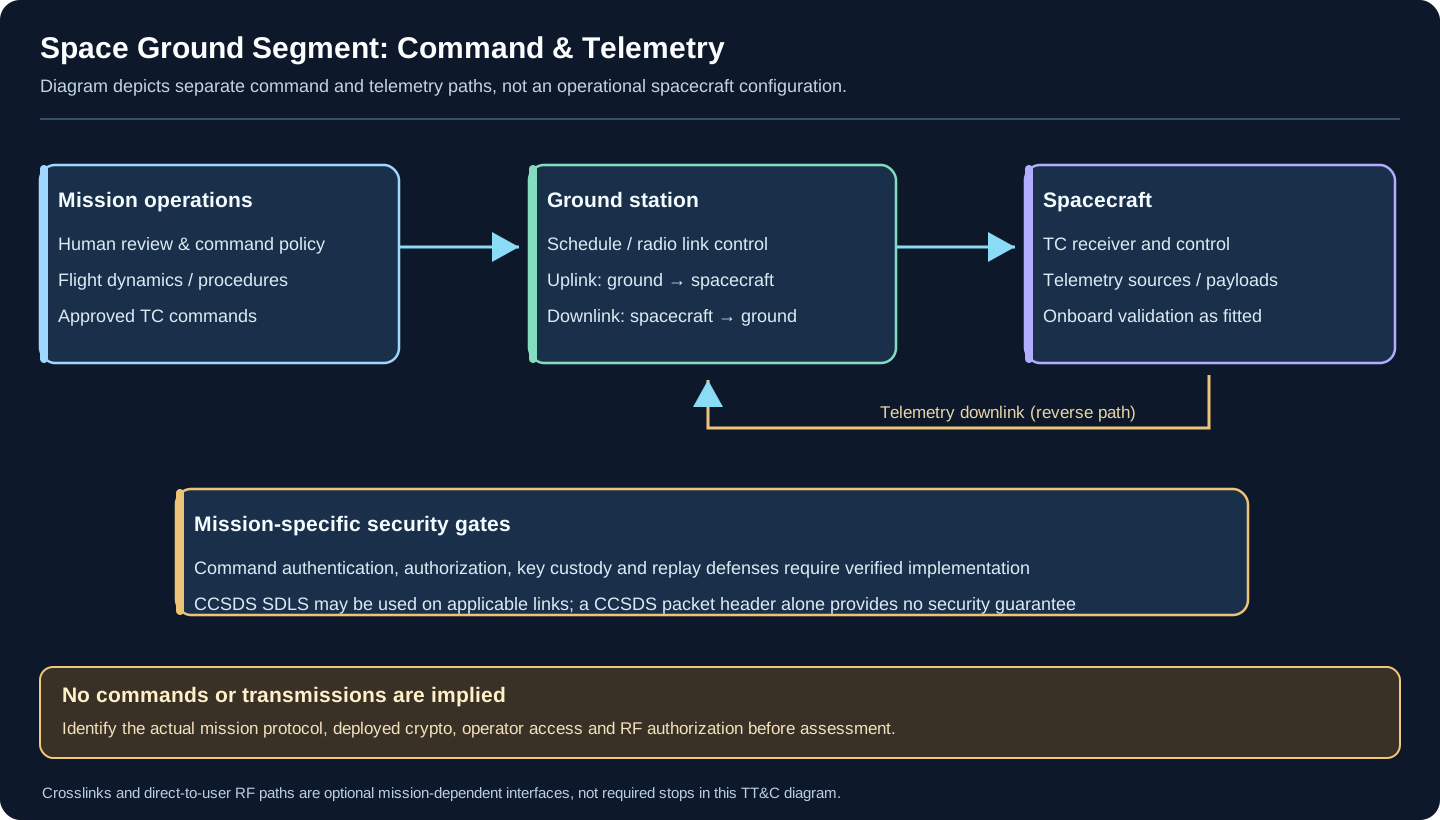
| Ground-Space Command & Telemetry | Space Security: Ground Segment | Mission authorization, telecommands, telemetry, and mission-dependent CCSDS SDLS controls |
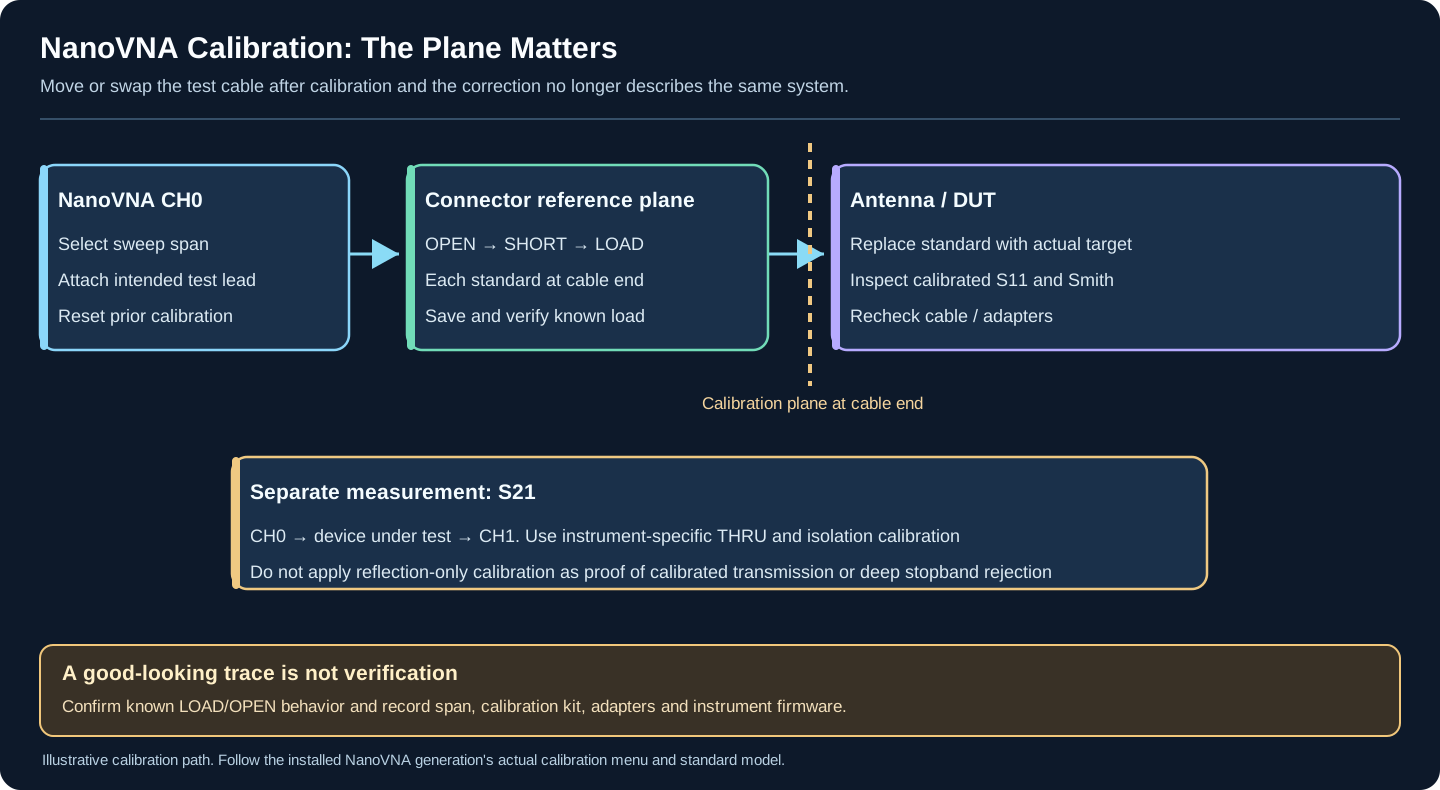
| NanoVNA S11/S21 Calibration Planes | NanoVNA Calibration & Reference Planes | OPEN/SHORT/LOAD on S11 plane and separate instrument-specific S21 calibration |
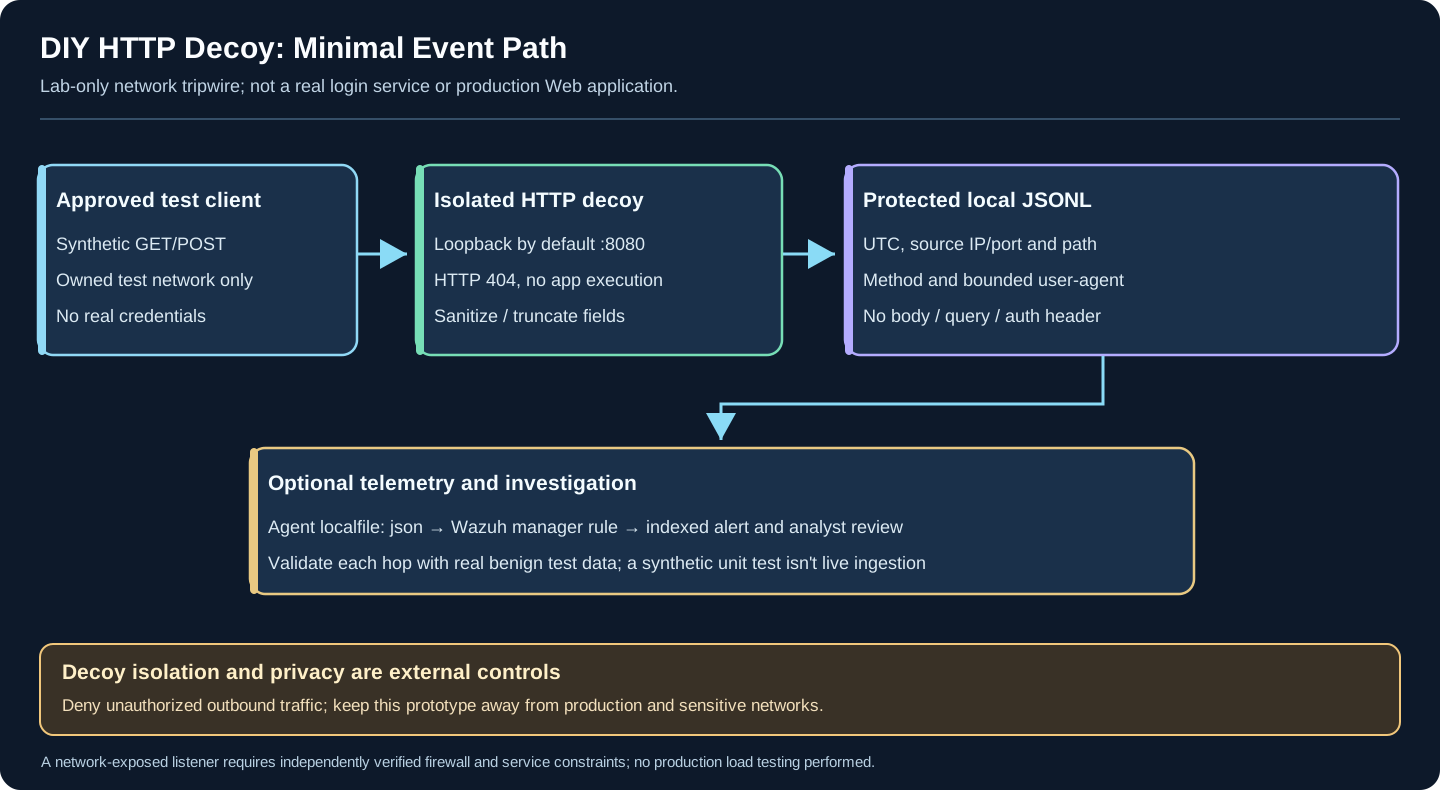
| DIY HTTP Decoy JSONL → Wazuh | Minimal HTTP Honeypot Lab | Lab-only request metadata capture, 404 response, JSONL localfile and optional Wazuh forwarding |
| Image | Embedded Guide | Verified Learning Objective |
|---|---|---|
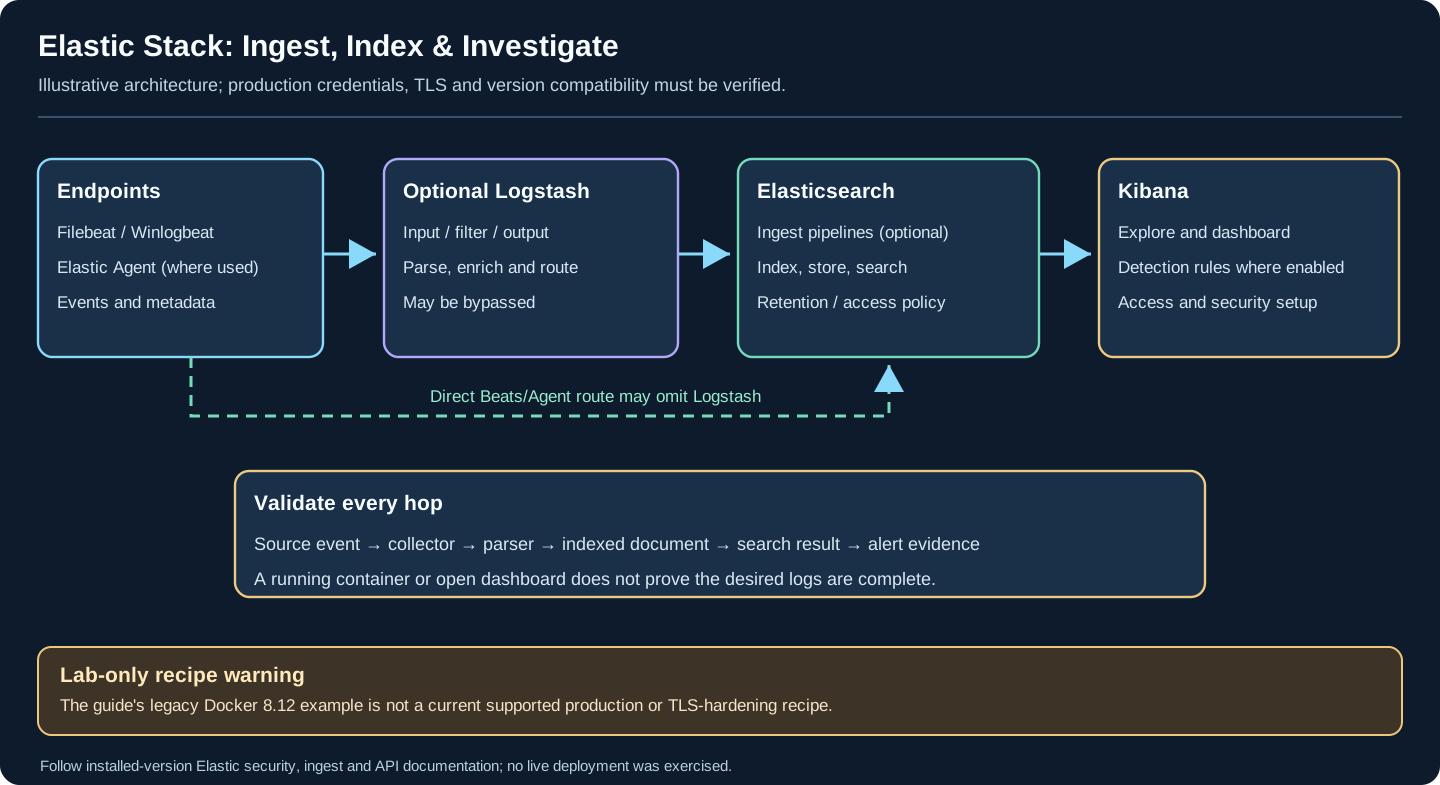
| Elastic Ingest, Index & Kibana | Elastic Stack SIEM | Shows optional Logstash versus direct shipping, Elasticsearch processing, Kibana investigation and evidence validation |
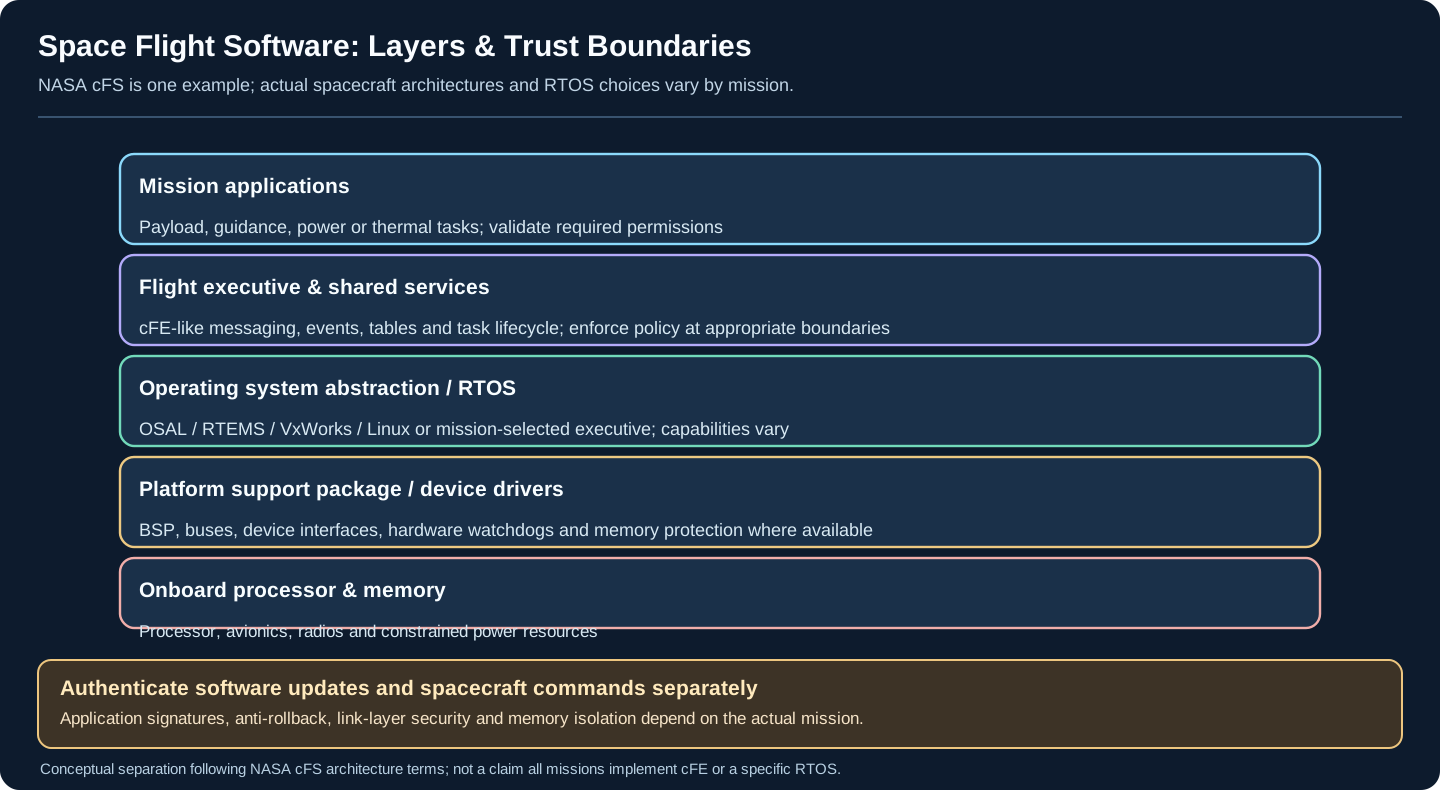
| Space Flight Software Layers | Space Security: Flight Software | NASA cFS-like mission app, executive, OS abstraction, BSP/driver and onboard hardware boundary |
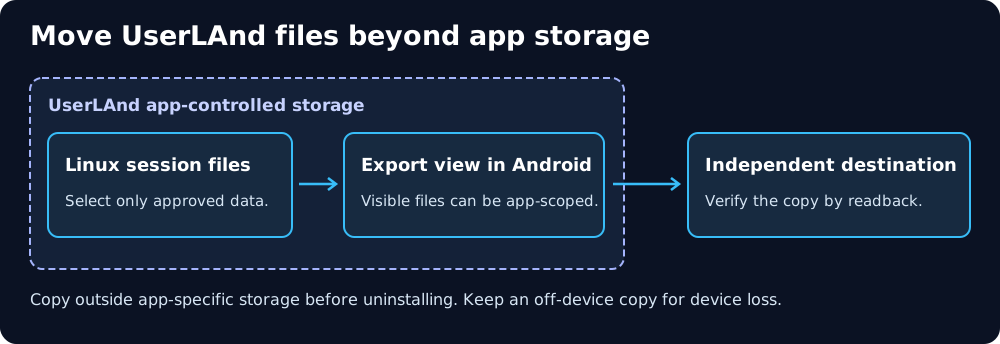
| UserLAnd independent file export | UserLAnd files and backups | Shows why a visible export folder can still be app-scoped |
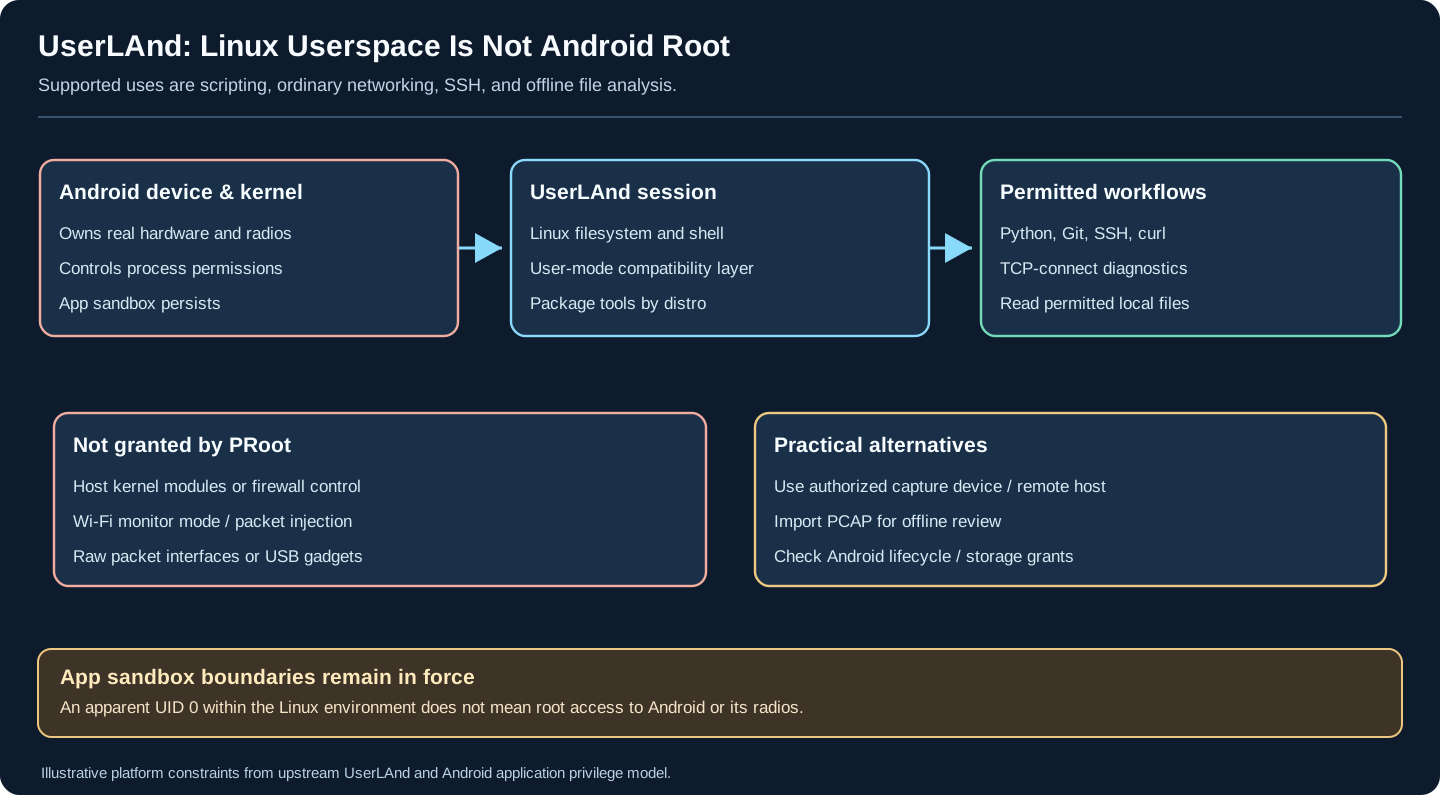
| UserLAnd Android Permission Boundary | UserLAnd Linux on Android | Distinguishes no-root Linux userspace tools from unavailable host kernel/raw-radio privileges |
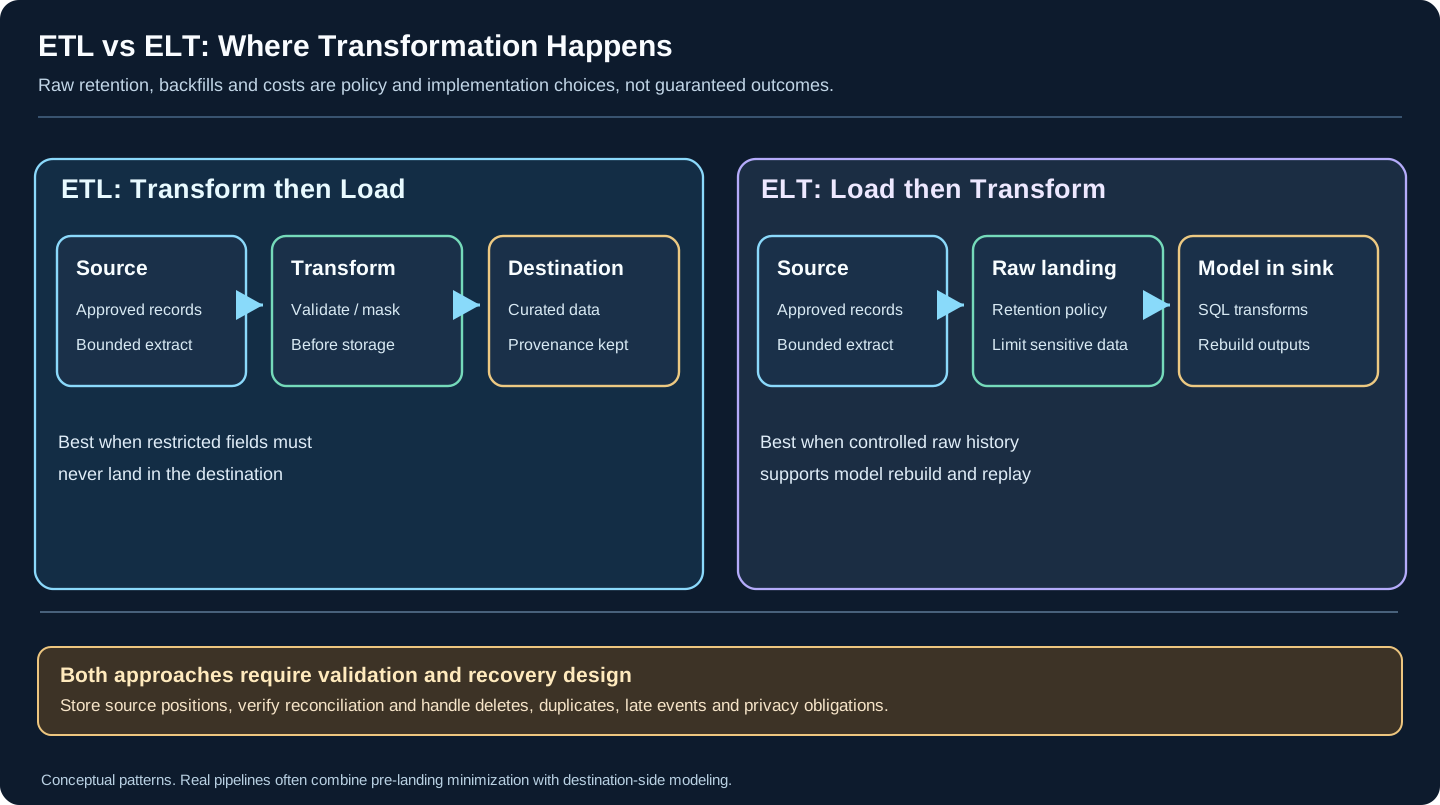
| ETL Versus ELT Data Paths | ETL & ELT Pipeline Design | Preload vs in-destination transforms, and why raw retention and security are independent choices |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
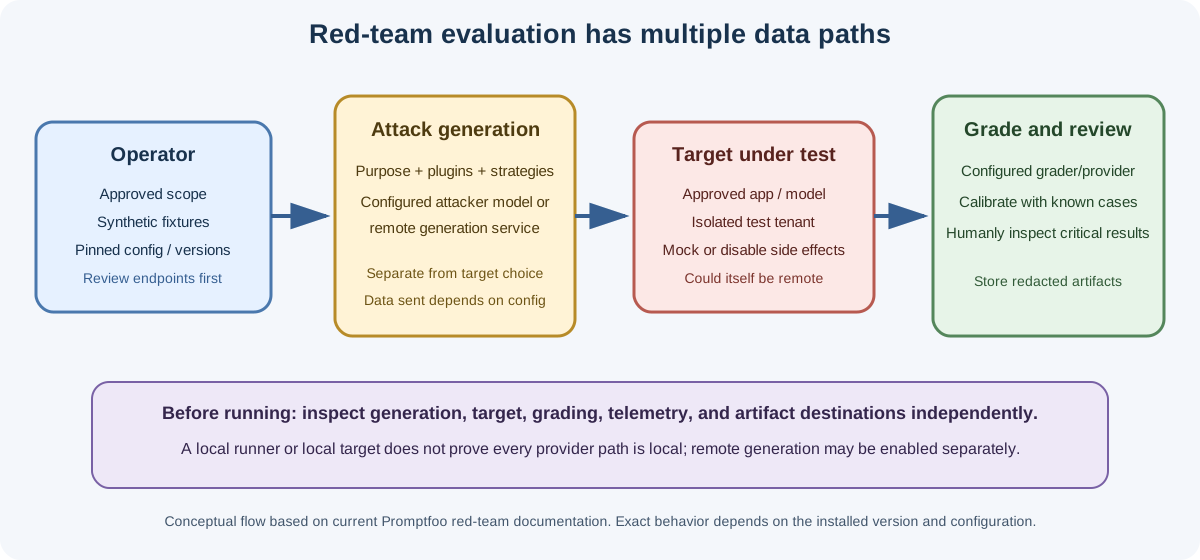
| Promptfoo red-team provider data paths | LLM and Agent Security Evaluations with Promptfoo | Separates attack generation, target, grader, telemetry, and artifact paths before approved evaluations |
| Diagram | Embedded guide |
|---|---|
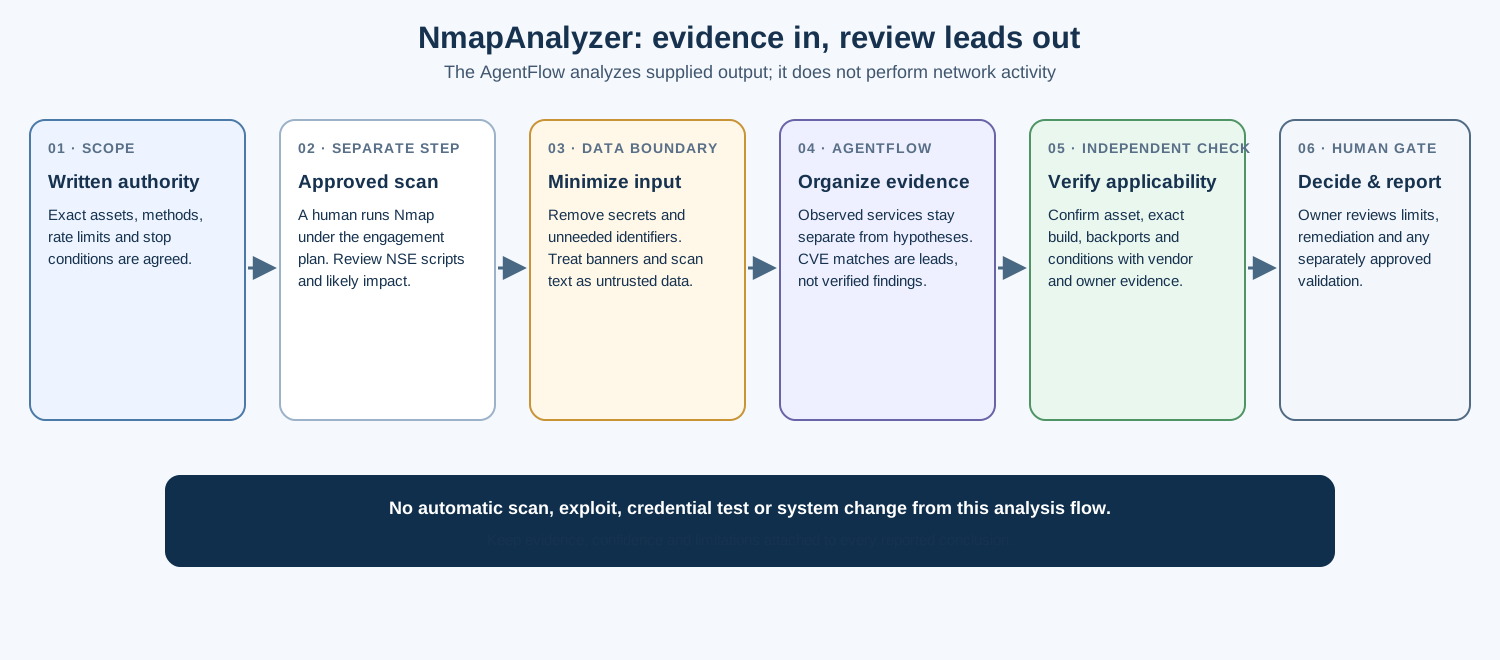
| Nmap analysis evidence gates | AnythingLLM Nmap Analyzer |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
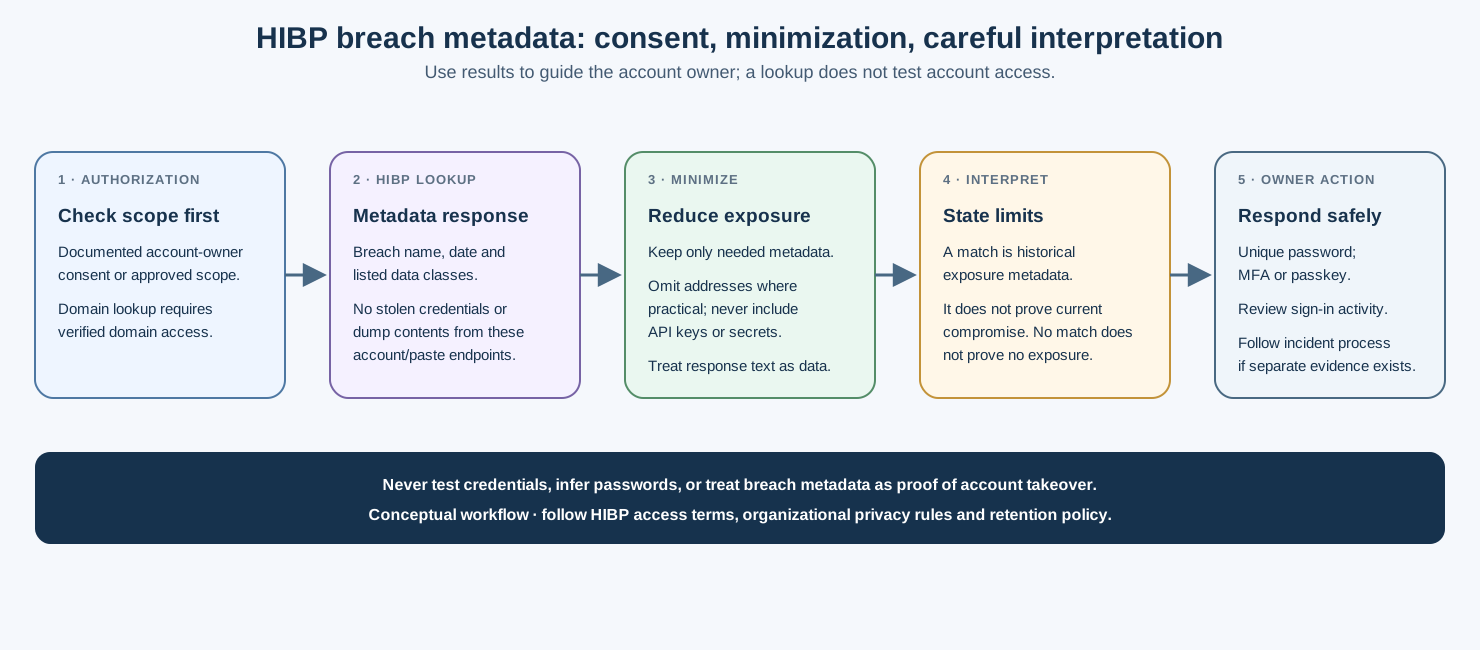
| HIBP metadata privacy workflow | Breach Exposure Check AgentFlow; Email Account Exposure Review | Shows consent, metadata minimization, interpretation limits, and owner-directed next steps for related HIBP account checks |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
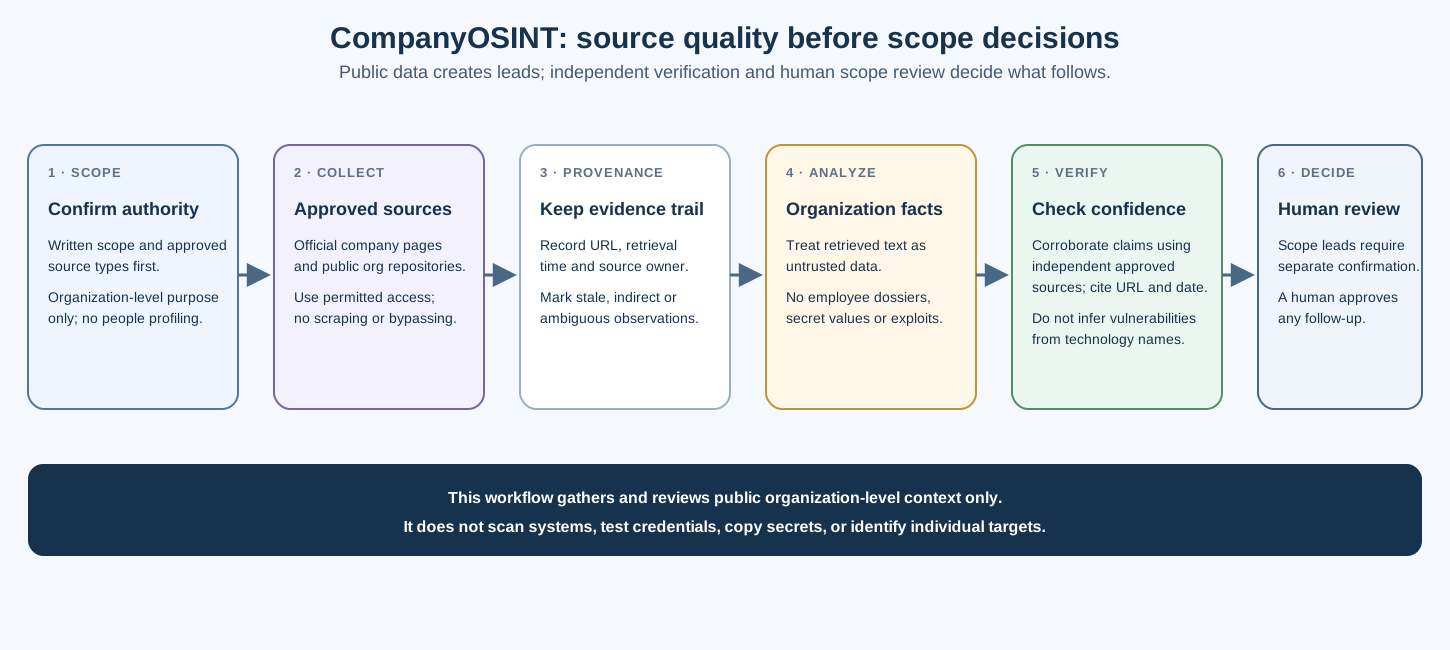
| Company OSINT source confidence and scope | CompanyOSINT AgentFlow | Separates permitted sources, provenance, organization-only analysis, independent verification, and human scope review |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
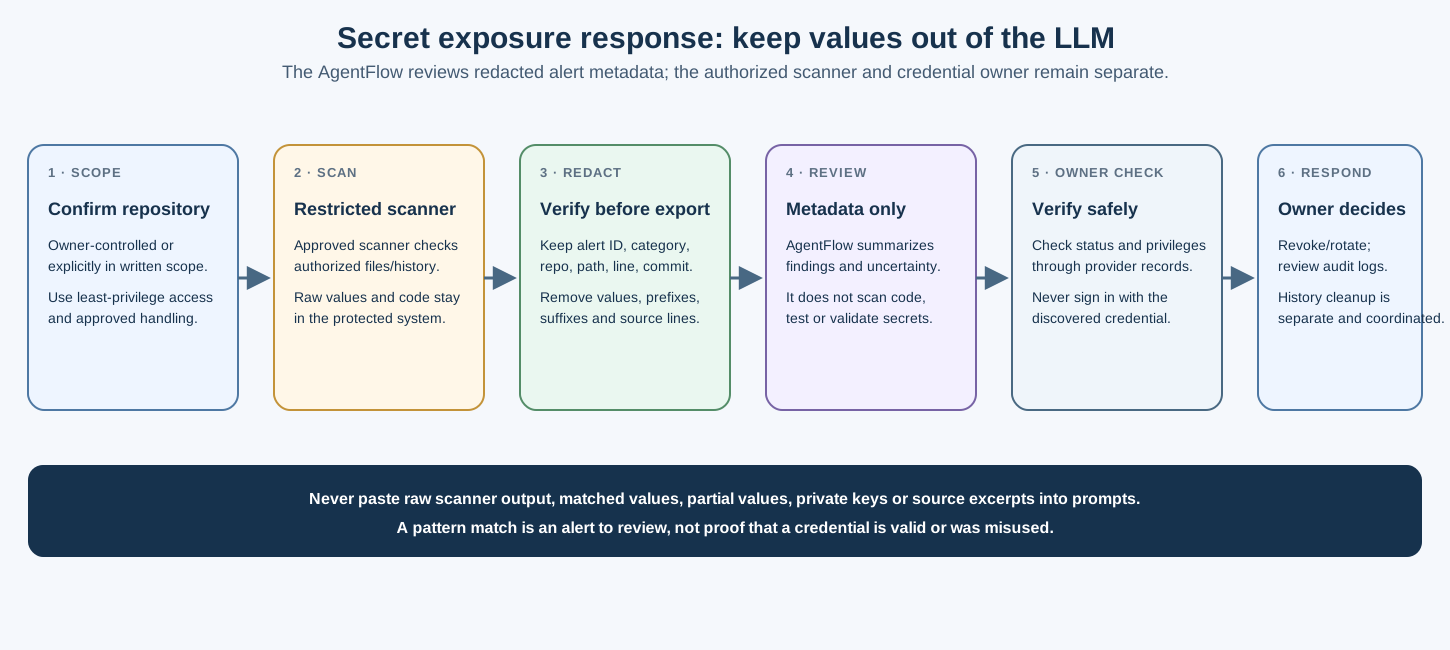
| GitHub secret alert redaction workflow | GitHubSecrets AgentFlow | Keeps credential values in restricted scanner systems, separates the metadata-only AgentFlow, and leaves verification and response with the authorized owner |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
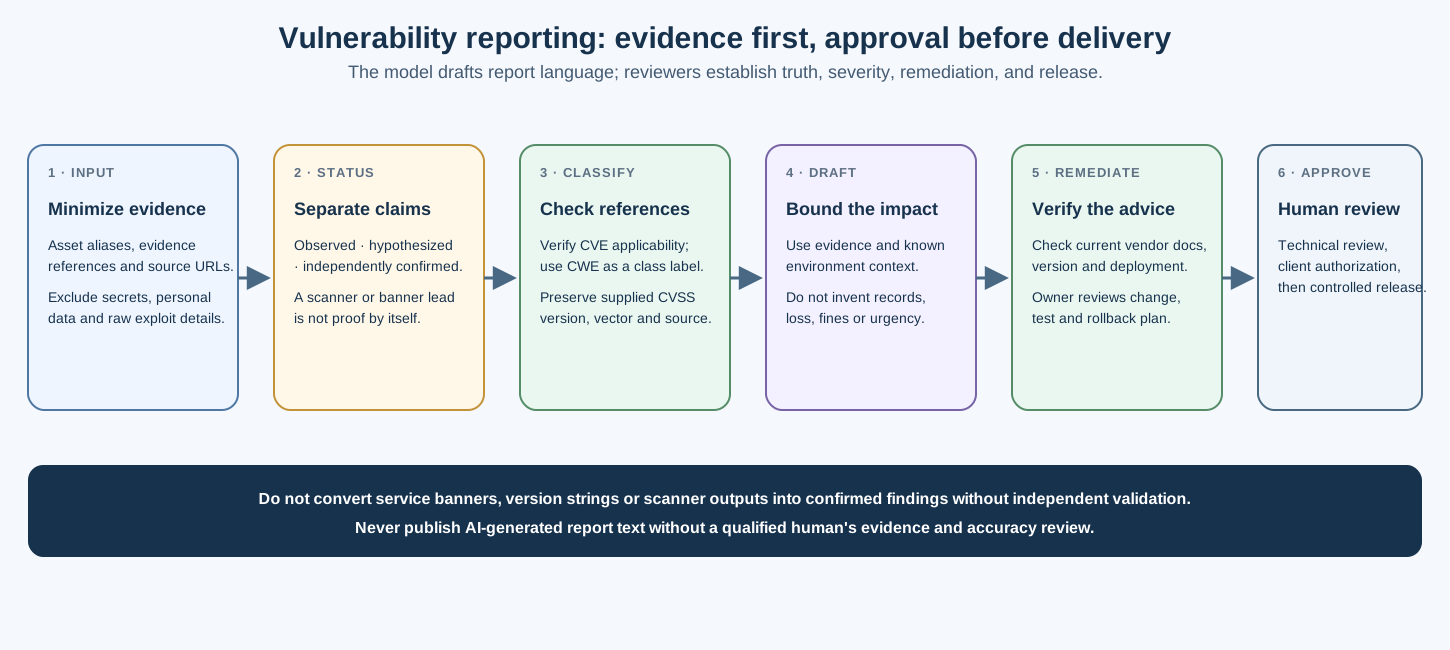
| Vulnerability report evidence review | VulnReportGenerator AgentFlow | Separates evidence status, scoring sources, impact bounds, remediation review, and human approval |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
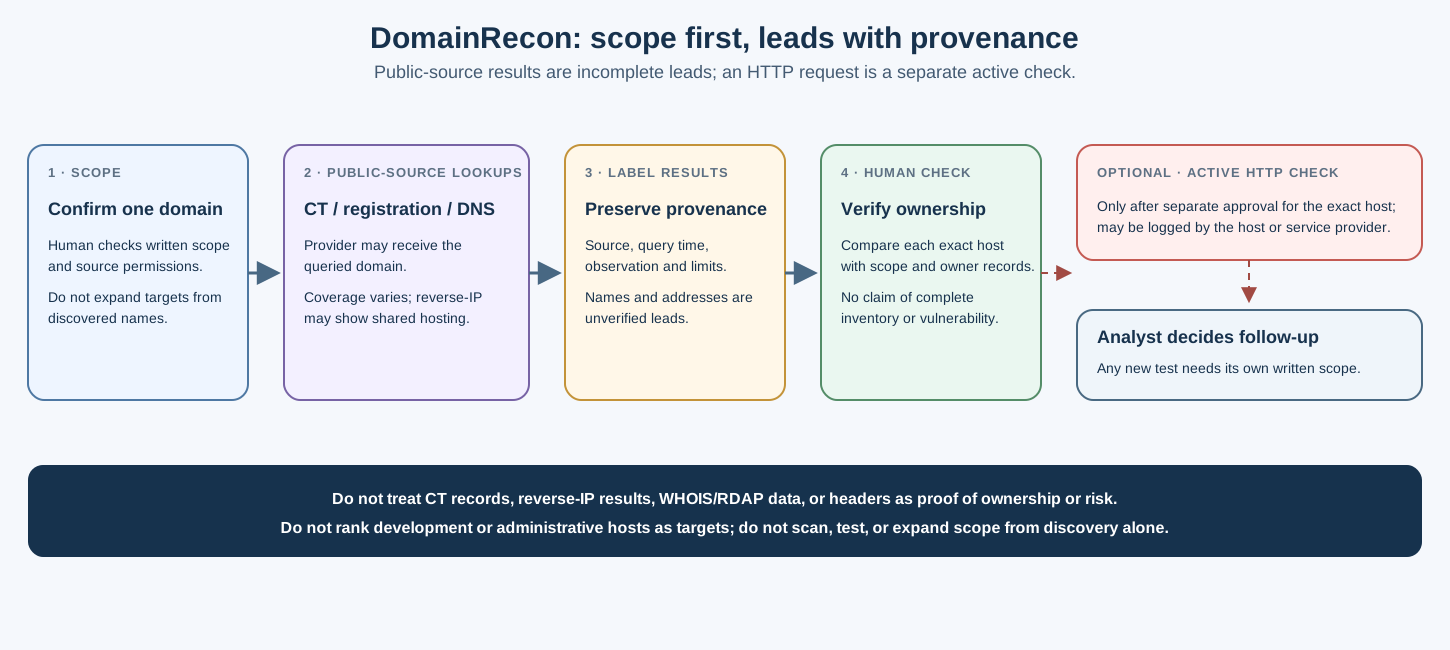
| Domain reconnaissance scope and evidence flow | DomainRecon AgentFlow | Separates third-party public-source queries, unverified leads, an optional active HTTP check, and human scope confirmation |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
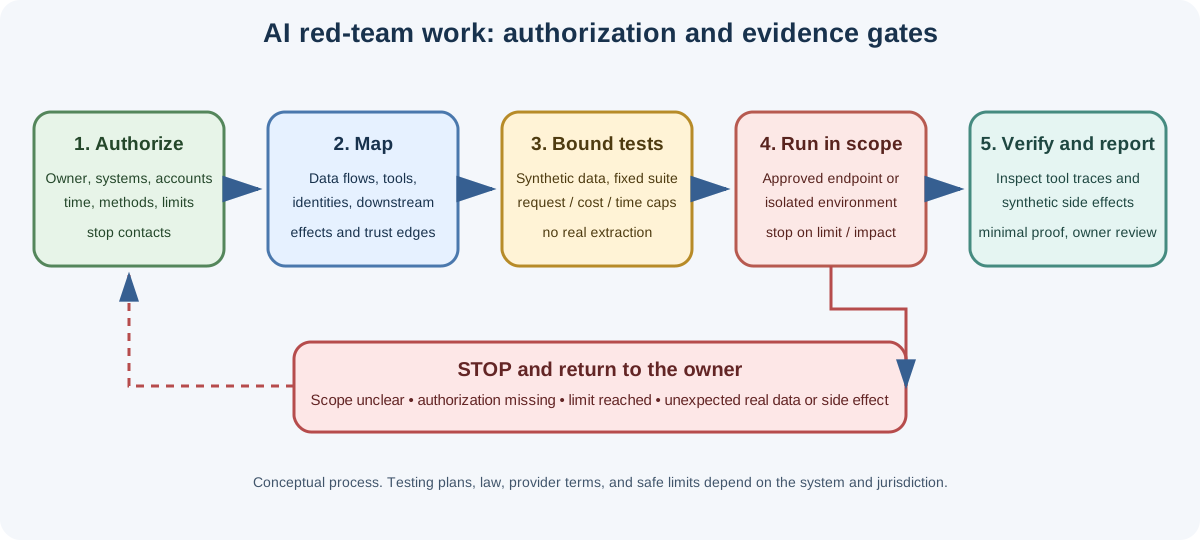
| Authorized AI red-team engagement gates | Offensive AI | Connects written scope, bounded synthetic tests, stop conditions, safe validation, and reporting |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
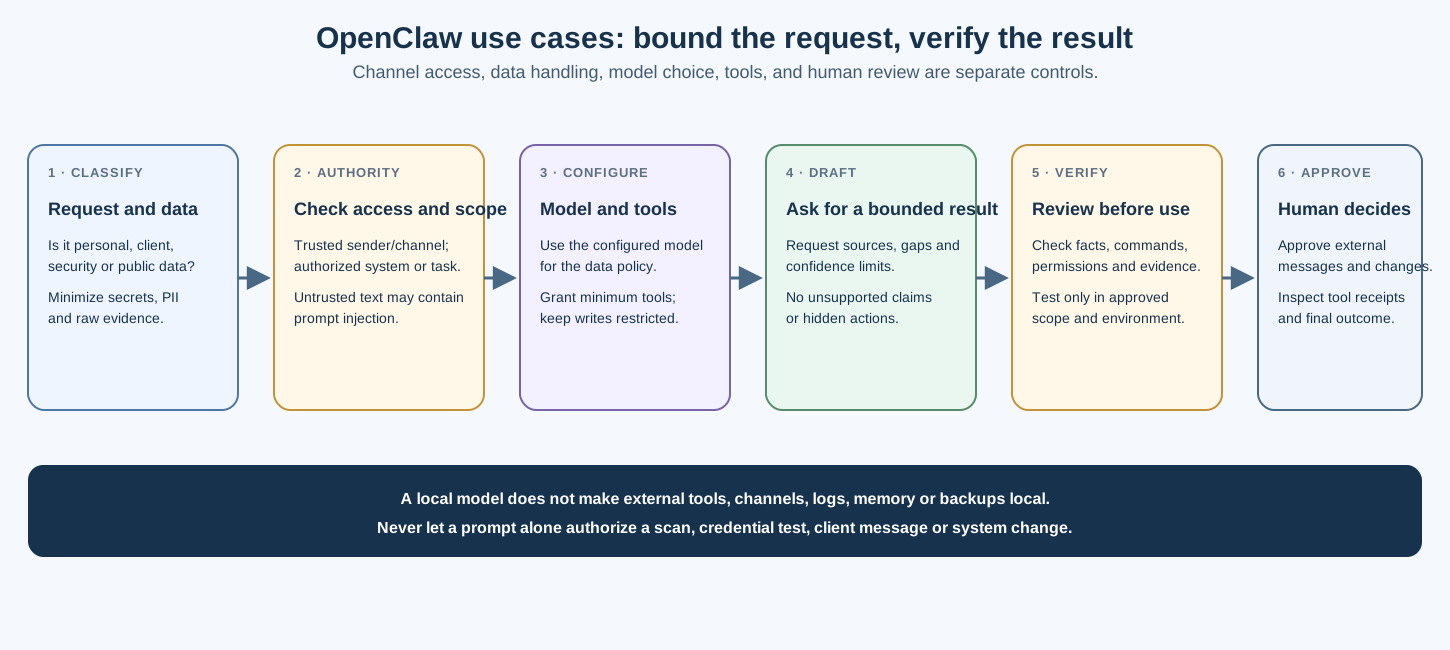
| OpenClaw use-case safety workflow | OpenClaw Use Cases | Connects data minimization, channel/scope checks, least-privilege tools, verification, and human approval |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
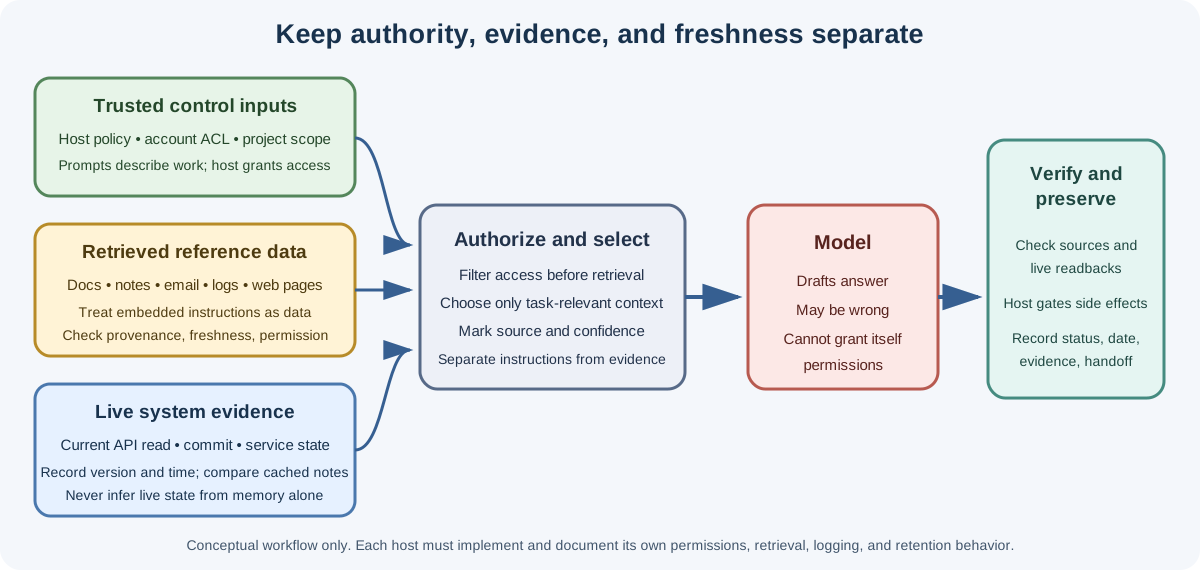
| Context authority, evidence, and freshness | Context Engineering & Memory Management | Separates trusted host policy, untrusted retrieved material, live state, model output, and verified handoff |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
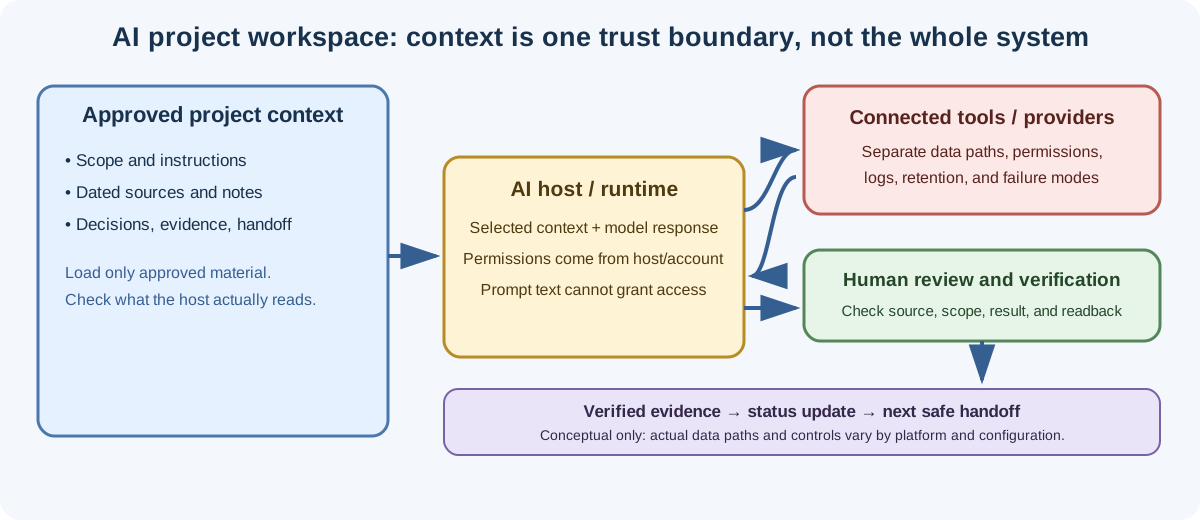
| AI project workspace trust boundaries | AI Projects, Notebooks, GPTs, Plugins and Reusable Assistants | Separates project context from host permissions, connected tools, provider data paths, human verification, and evidence handoff |
| Diagram | Embedded guide | Why it belongs |
|---|---|---|
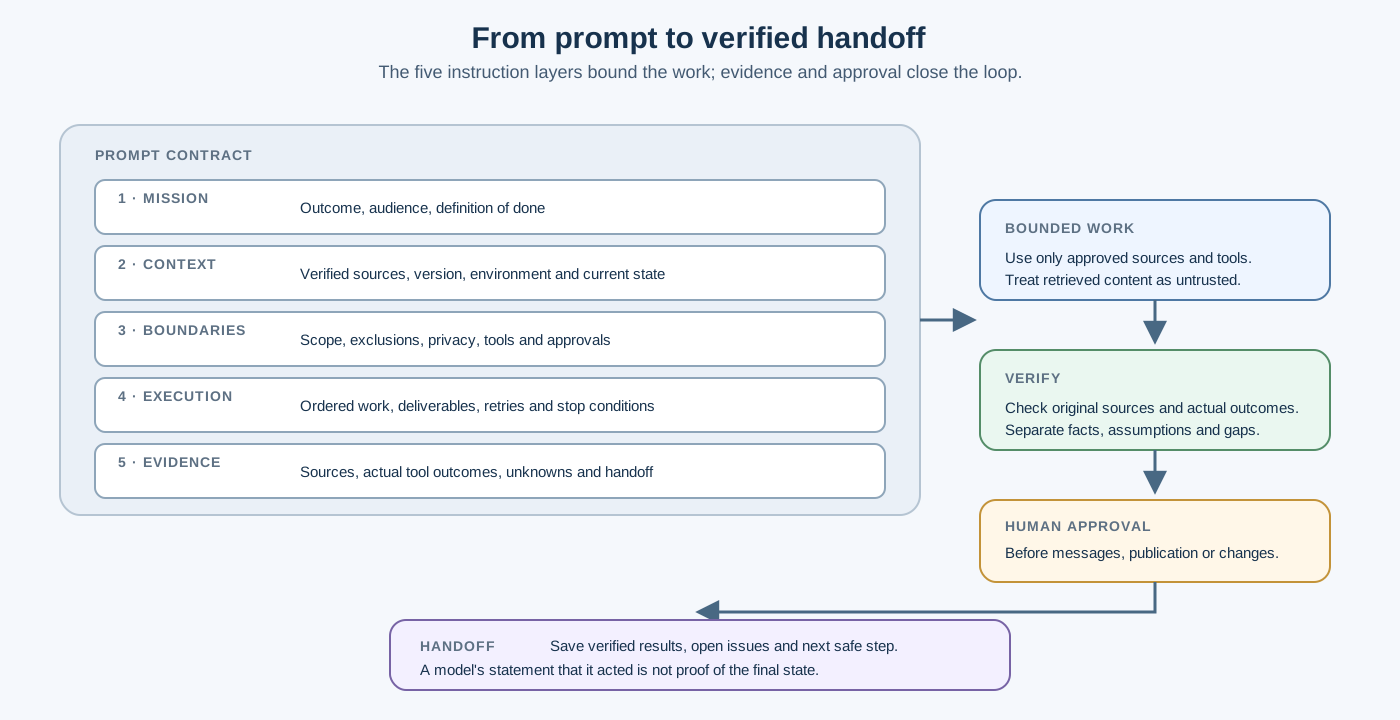
| Five-layer prompt to evidence handoff | Practical AI Usage and Interaction Guide | Shows how mission, context, boundaries, execution, and evidence connect to verification, approval, and handoff |
| Visual | Embedded Guide | Source-Aligned Concepts |
|---|---|---|
| Multi-Agent Delegation & Review | Multi-Agent Orchestration | Scoped ownership, independent verification, final integrated test and human approval |
| Project Status, Evidence & Handoff | AI Project & Agent Workflows | Charter rules, current decisions, reproducible evidence and explicit context reload |
| Orchestrator Logical Interval & Publish Gate | Data Workflow Orchestration | DAG dependencies, source versions, ready/blocked states and consumer acceptance |
| API Ingestion Cursor, Retry & Reconciliation | API & File Ingestion | Authenticated source contract, cursor semantics, rate-limit handling and exact batch evidence |
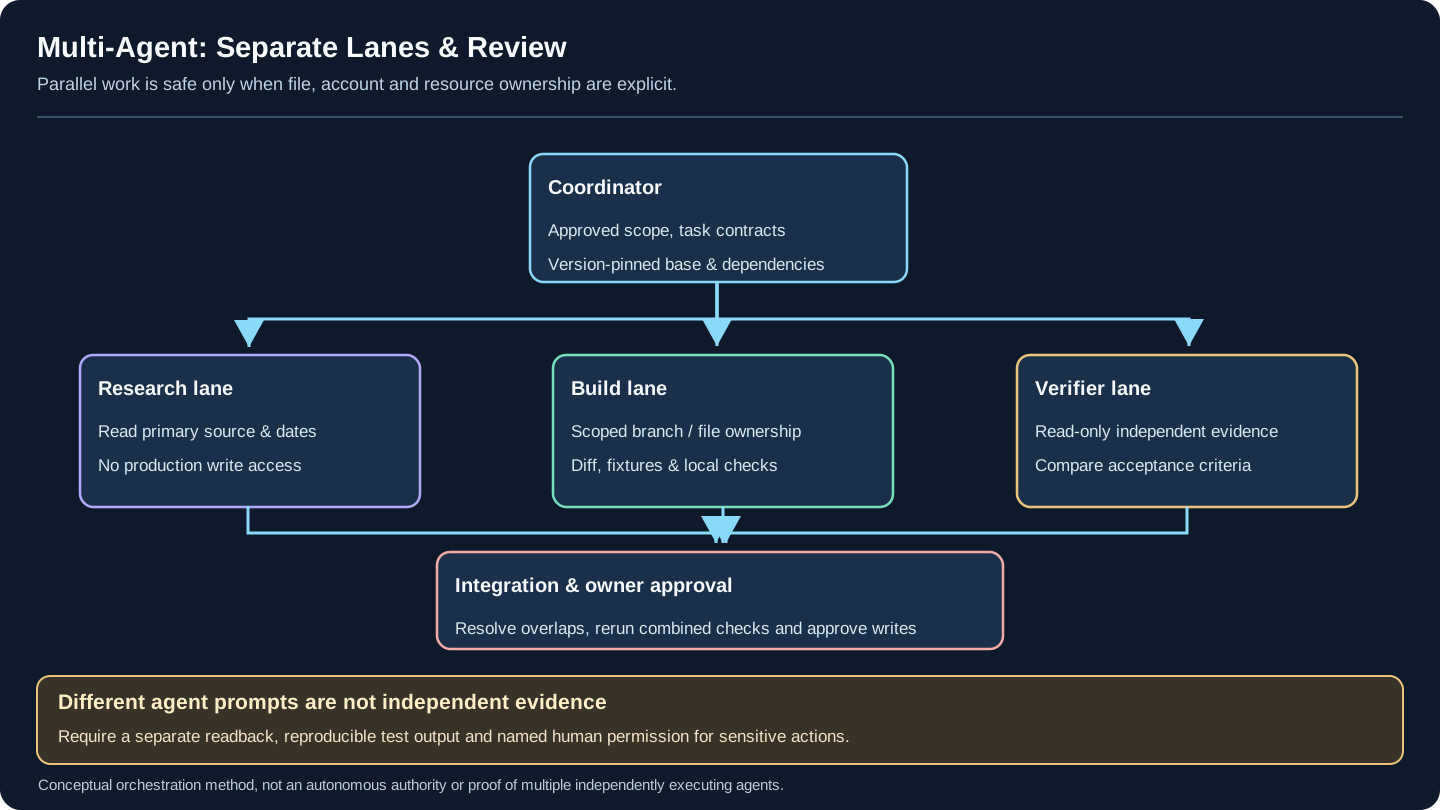
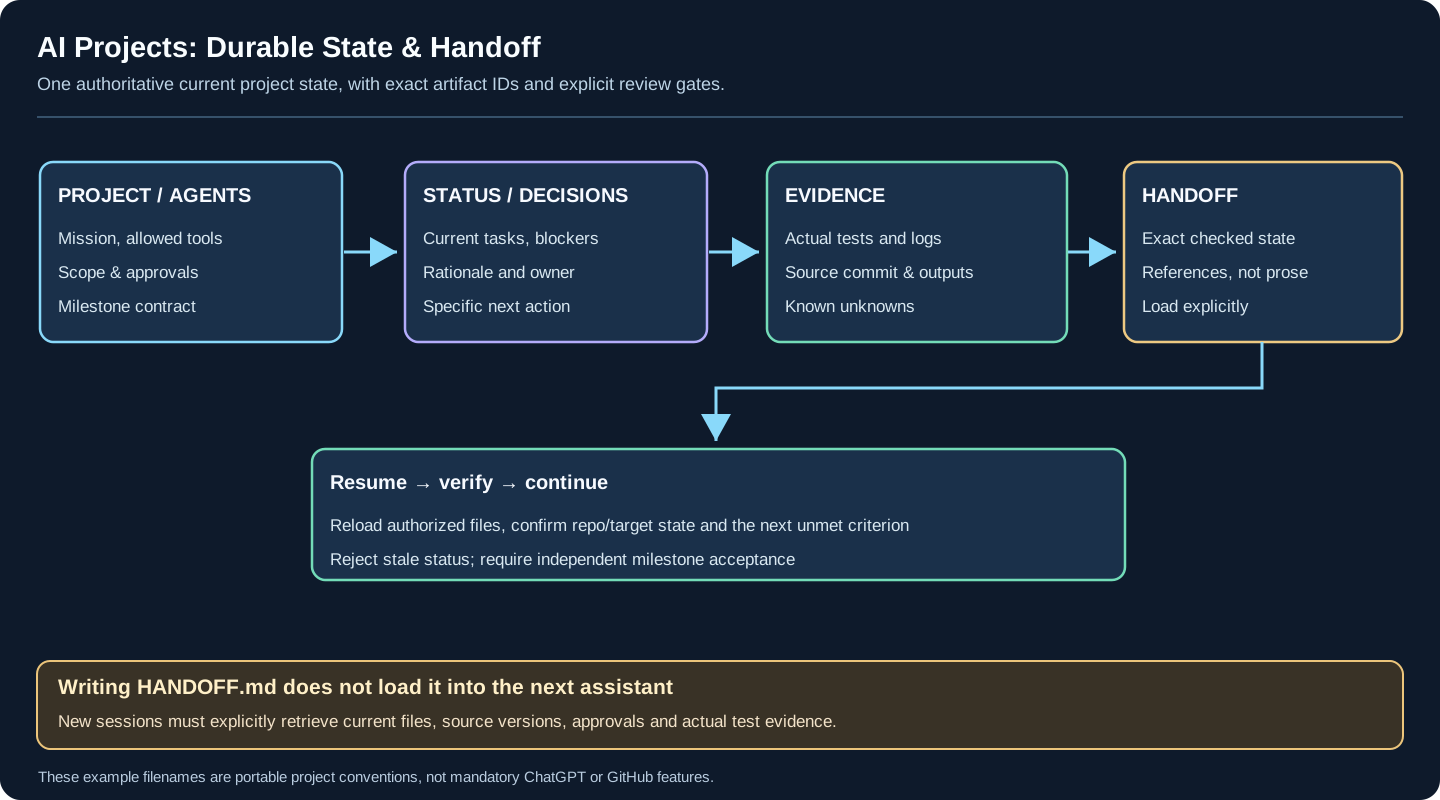
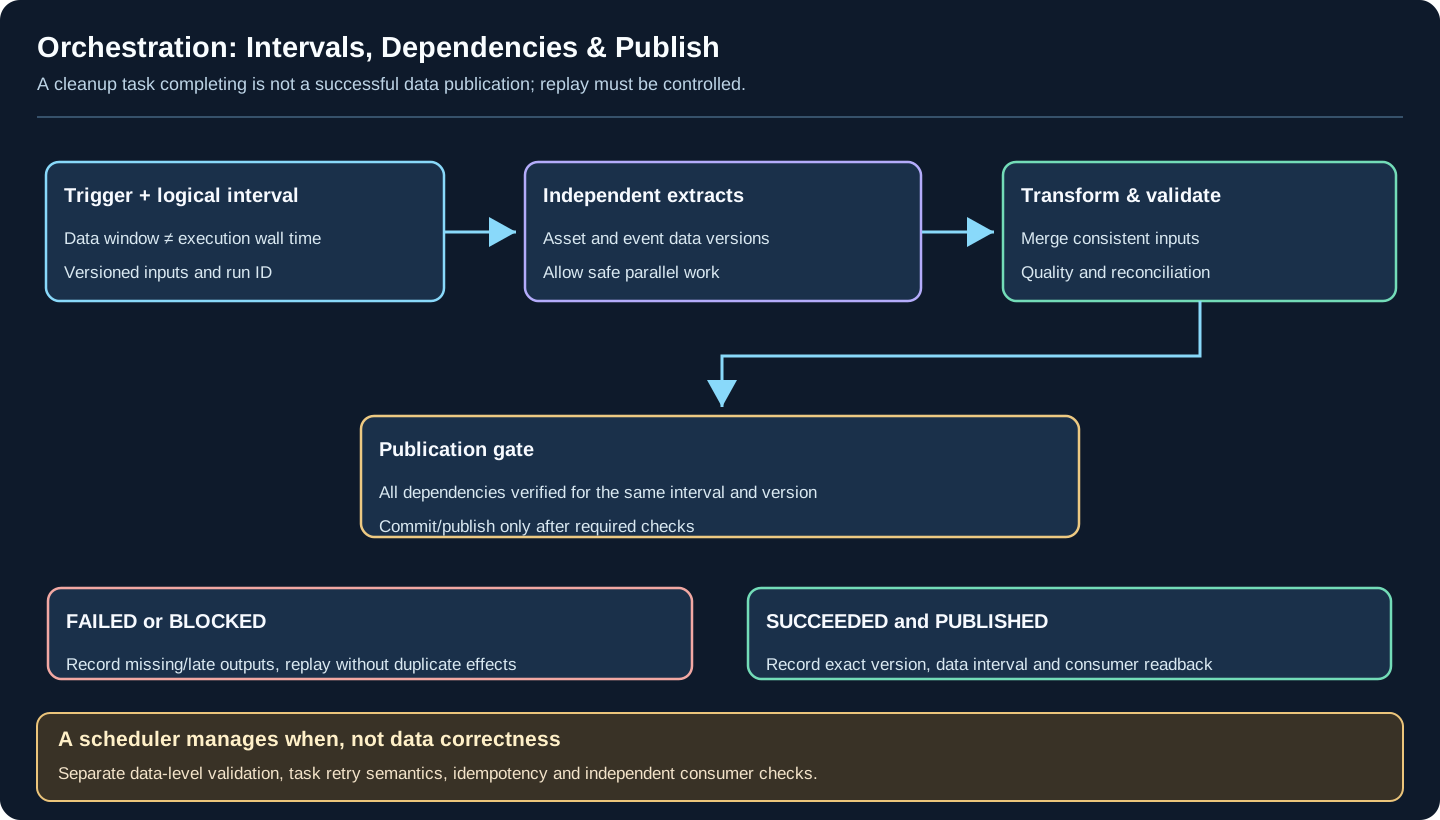
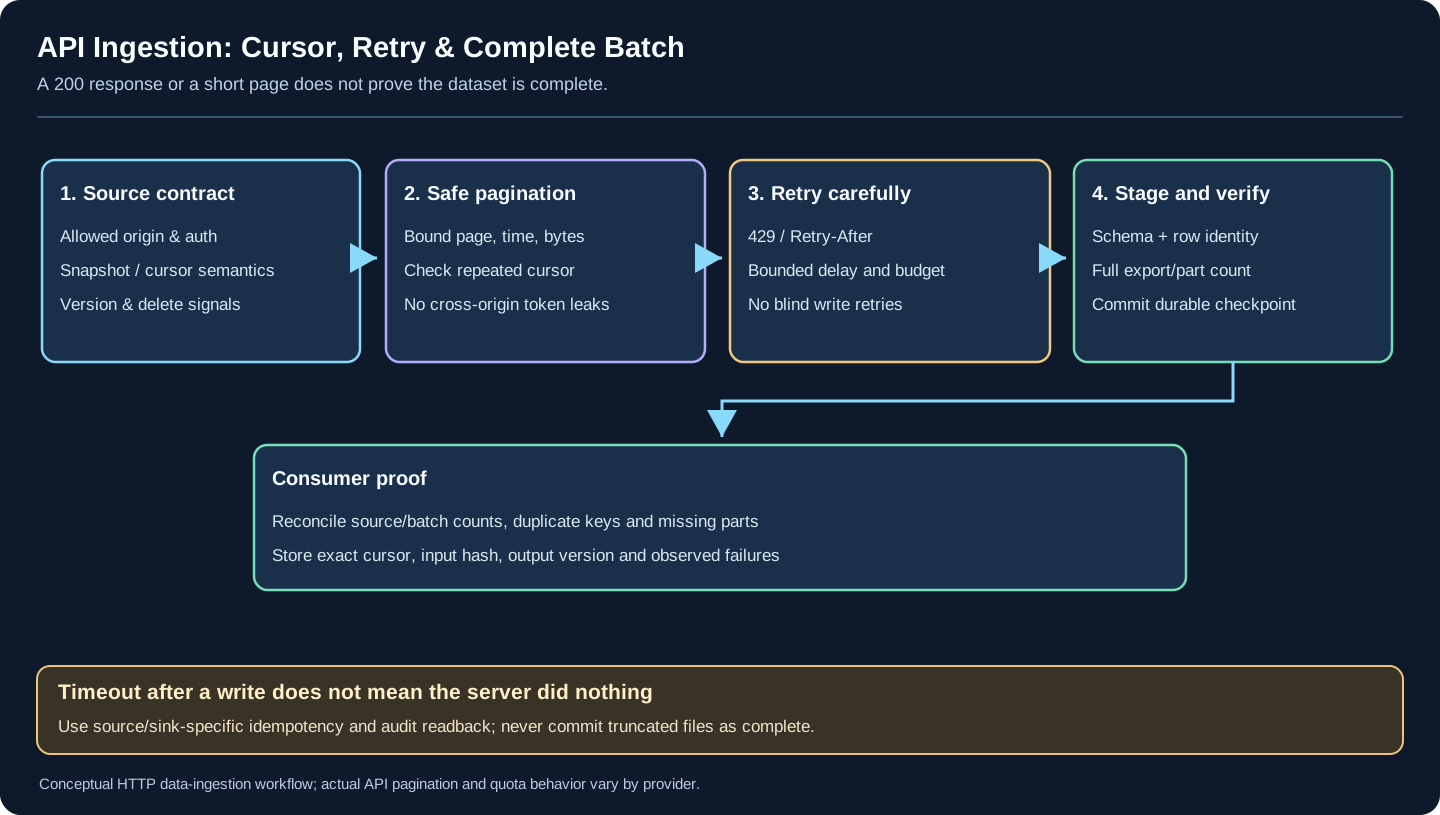
| Image | Embedded Guide | Source-Checked Content |
|---|---|---|
| 802.11 Deauth, Disassoc & PMF | Wi-Fi Deauthentication Defensive Analysis | Authentication state versus association, negotiated protected management frames, channel visibility and AP/client corroboration |
| BLE Sniffle Modes & Capture | Sniffle BLE Capture | Compatible TI device, advertisement capture versus connection following, encrypted-content and missed-packet limitations |
| Active Directory Ticket Trust & Recovery | Active Directory Checklist | KDC/KRBTGT trust, detection evidence and coordinated compromise recovery |
| Android Static, Dynamic & Backend Tests | Android Application Checklist | Distinguishes static artifact inspection, runtime testing and API authorization checks |
| Social Account Source Provenance | Social Media OSINT | Matching handles and profile images are leads until independently corroborated |
| uConsole CM5 Display Recovery | CM5 Display Recovery | Exact image, session versus rotation diagnosis, package side effects and hardware validation |
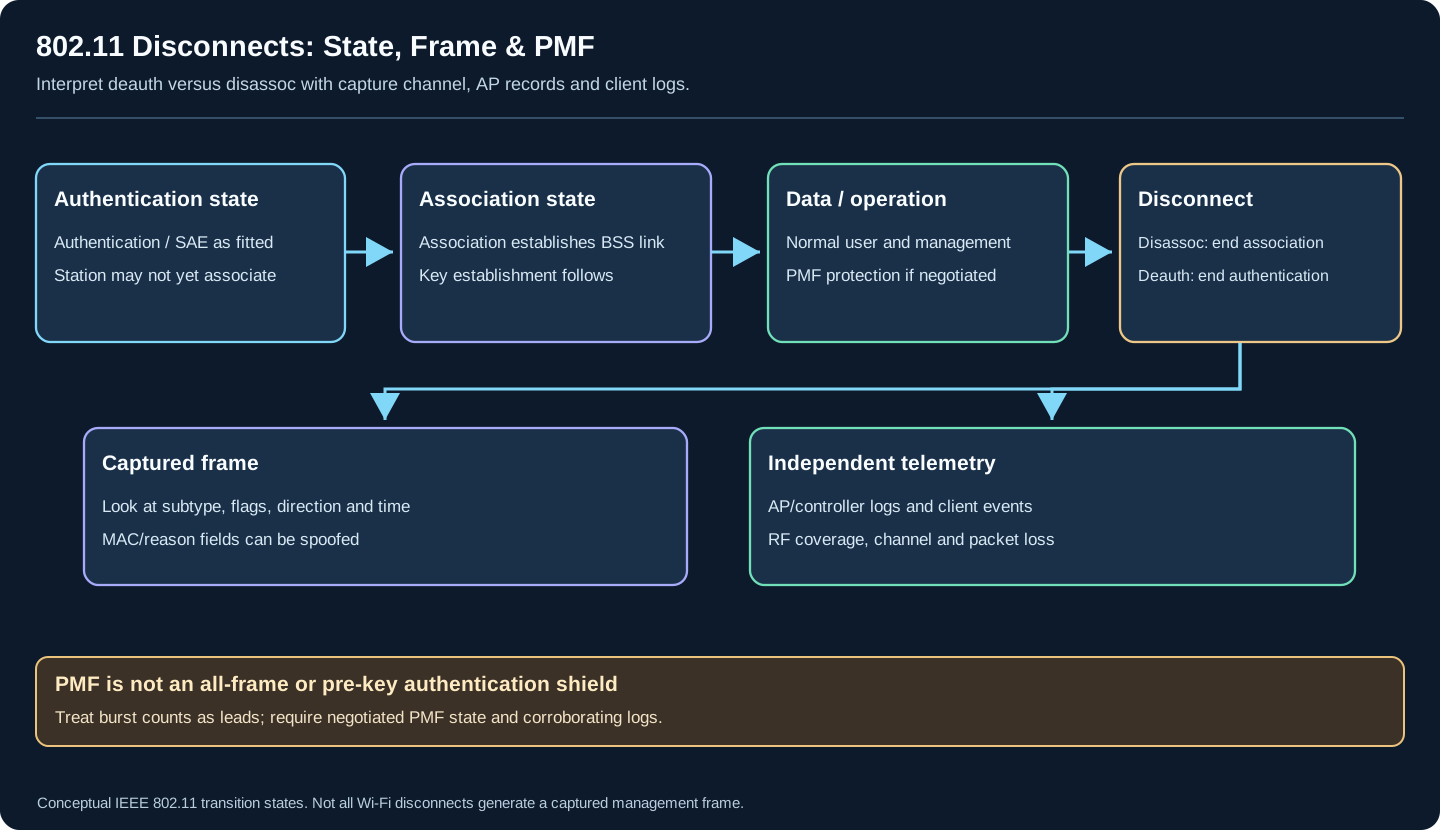
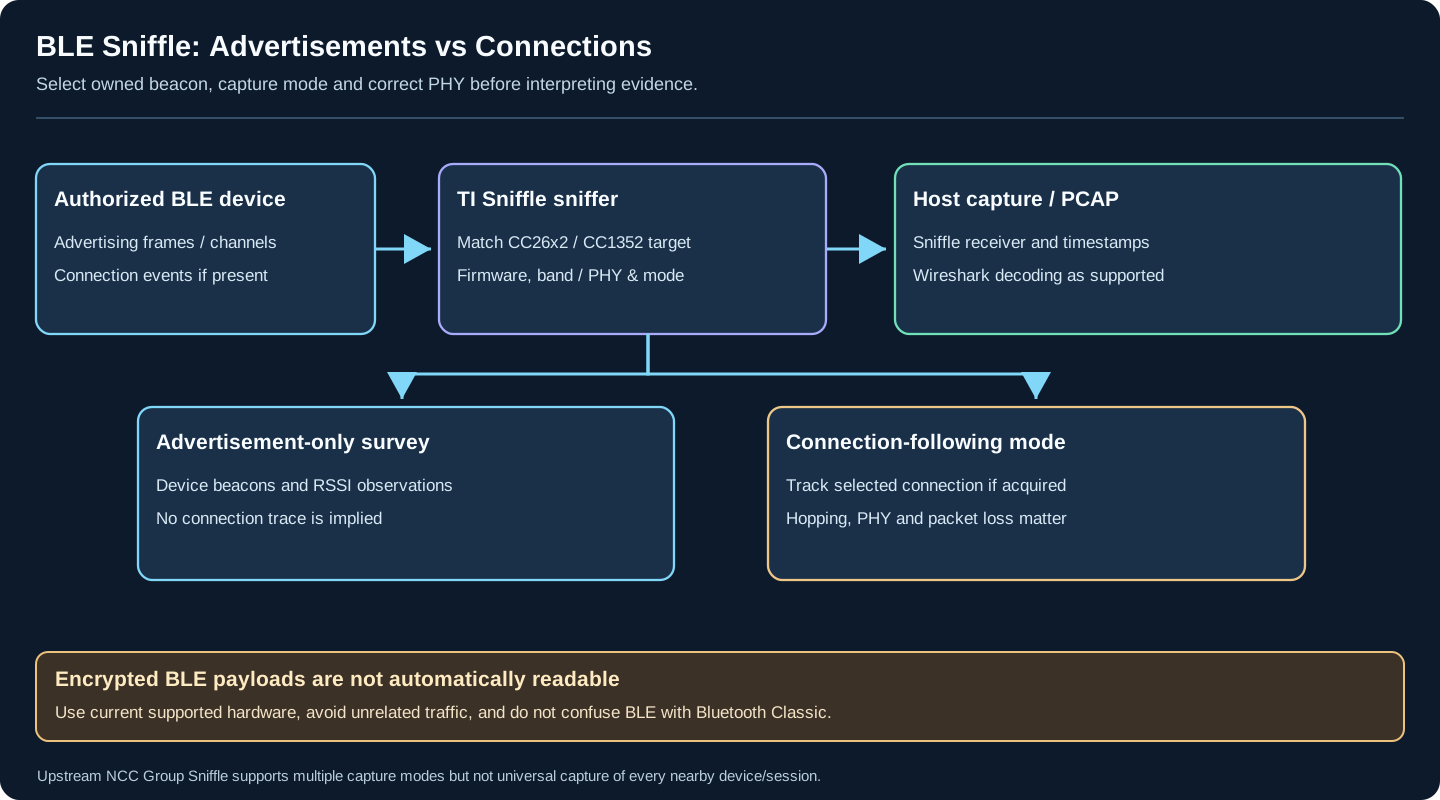
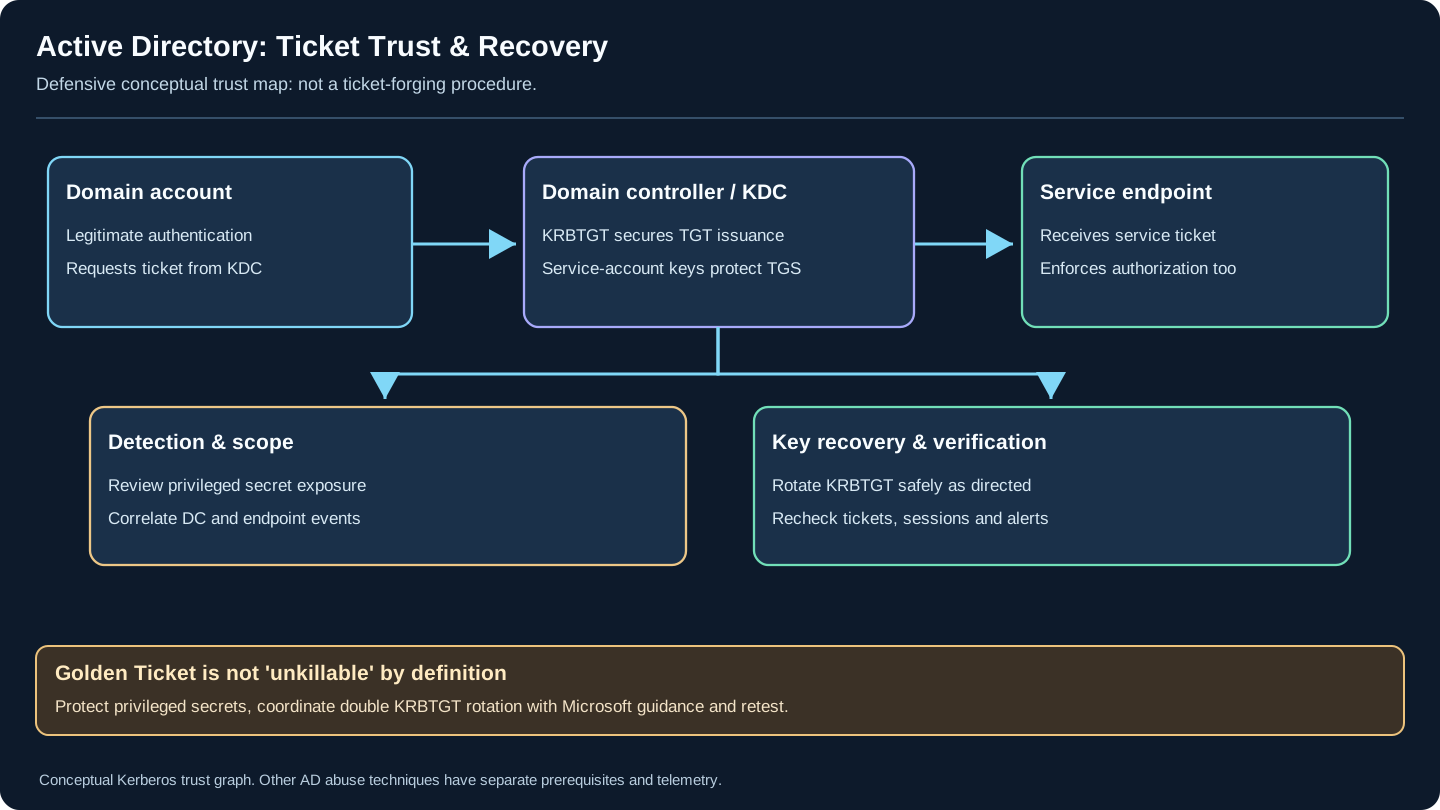
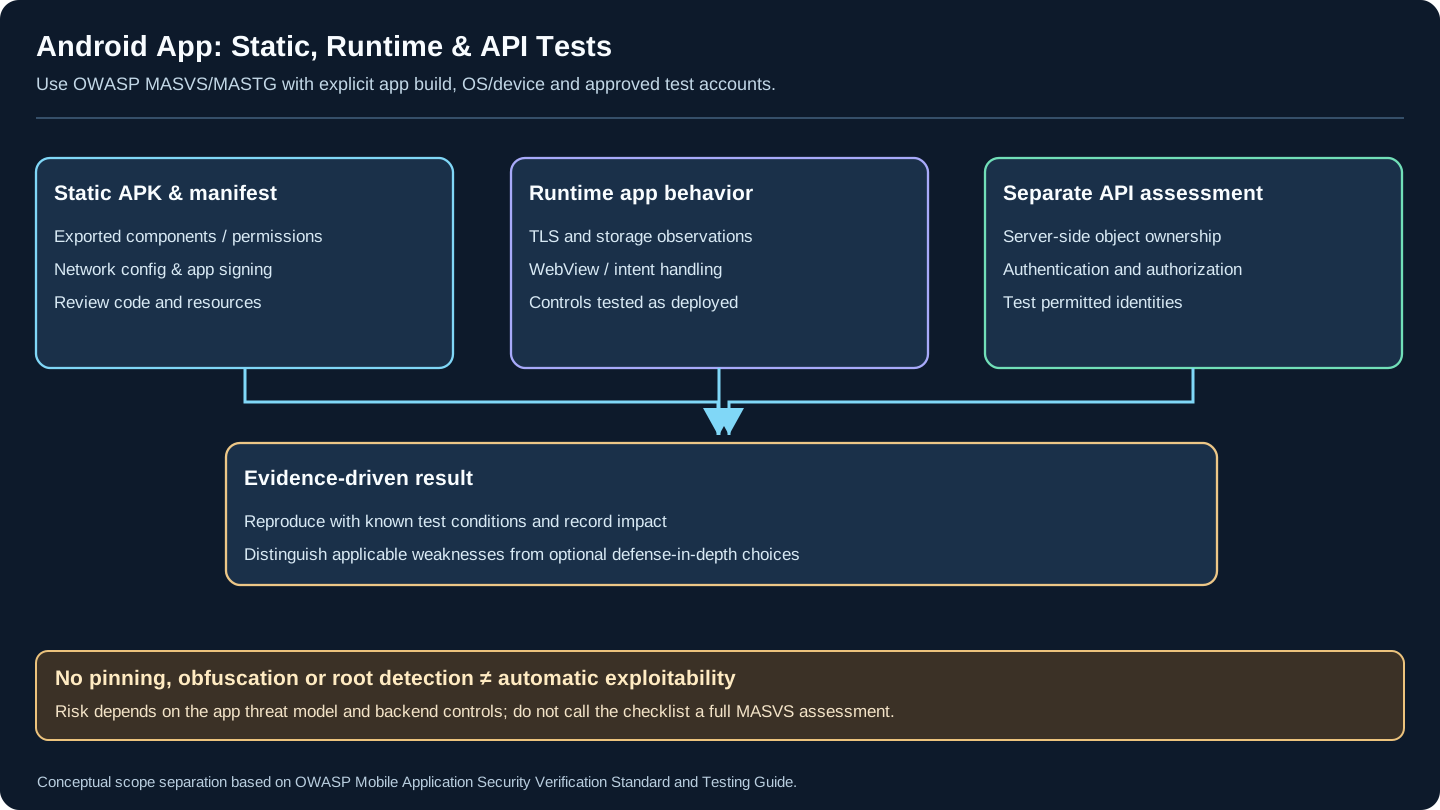
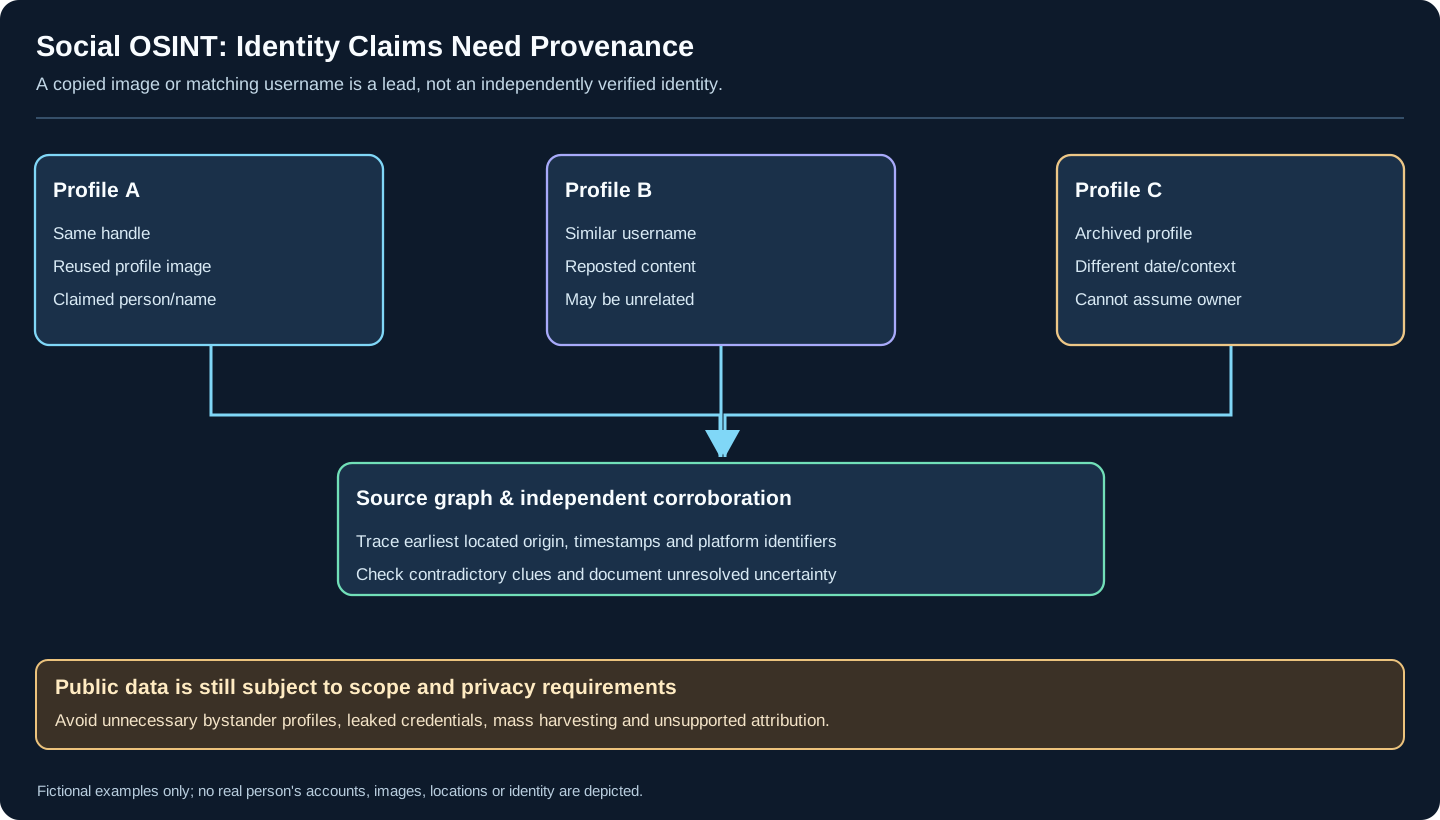
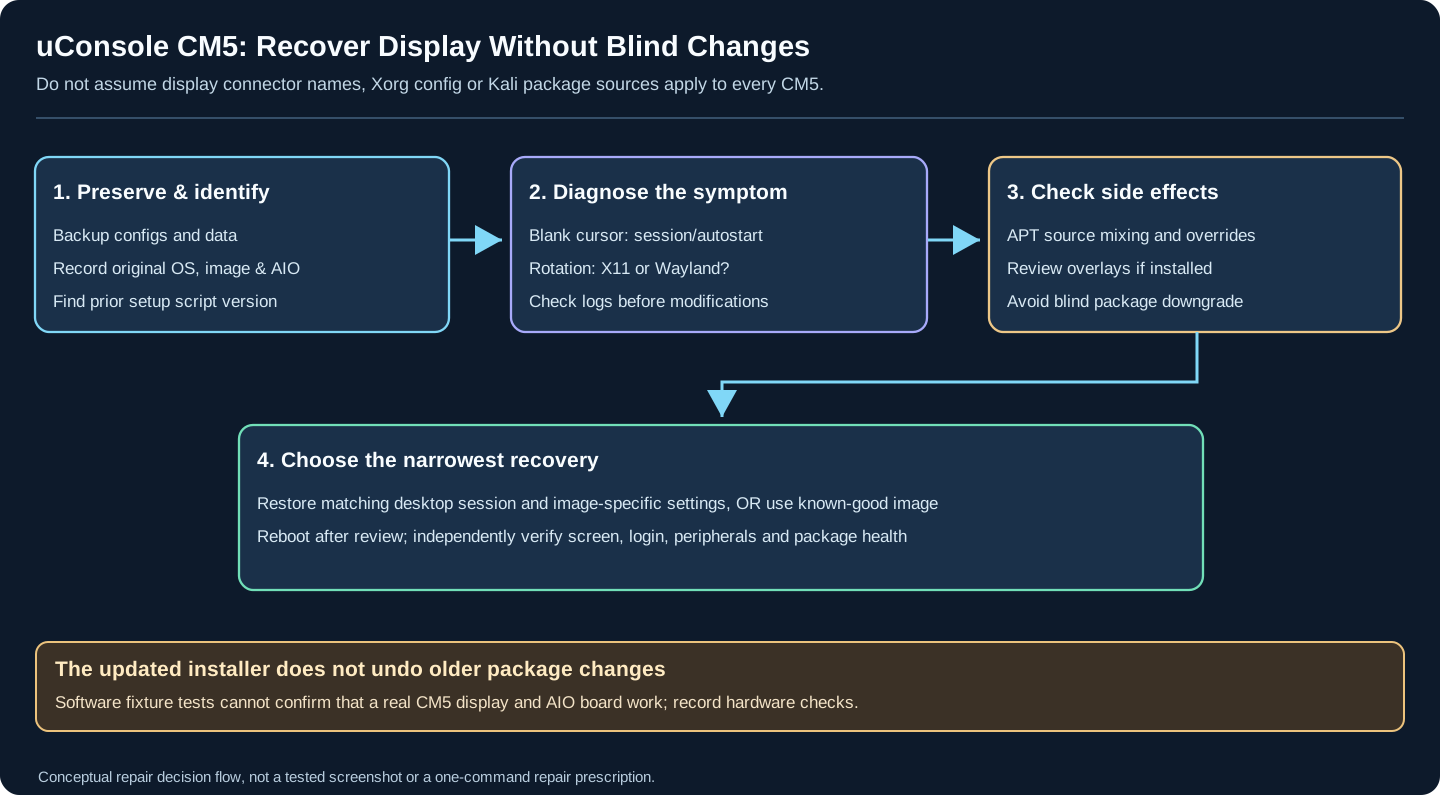
These original accessible diagrams are embedded in their canonical chapters and include explicit limitations on capture modes, physical measurements, protocol scope or test evidence.
| Image | Embedded Guide | Visual Purpose |
|---|---|---|
| Network Sensor Placement & Evidence | Network Detection & Packet Analysis | WAN/DMZ/east-west vantage points, packet acquisition, Zeek/Suricata processing, SIEM validation |
| Pin-Tumbler Shear Line Cutaway | Locksport Mechanical Fundamentals | Side-by-side locked/appropriately keyed pin-stack alignment |
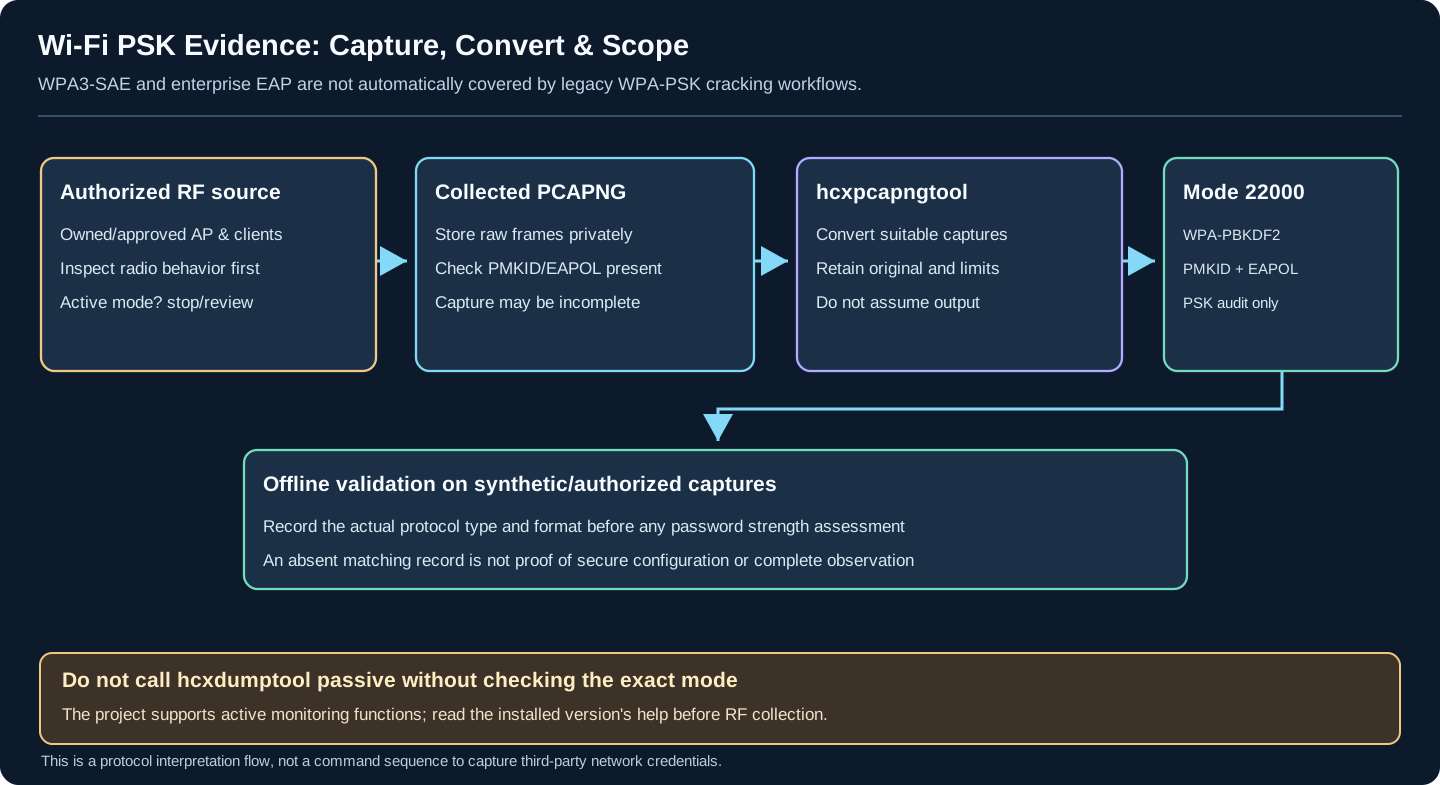
| WPA-PBKDF2 PMKID/EAPOL Audit Boundaries | HCXTools & Hashcat Reference | RF active/passive mode gates, original PCAPNG, offline conversion and Hashcat 22000 applicability |
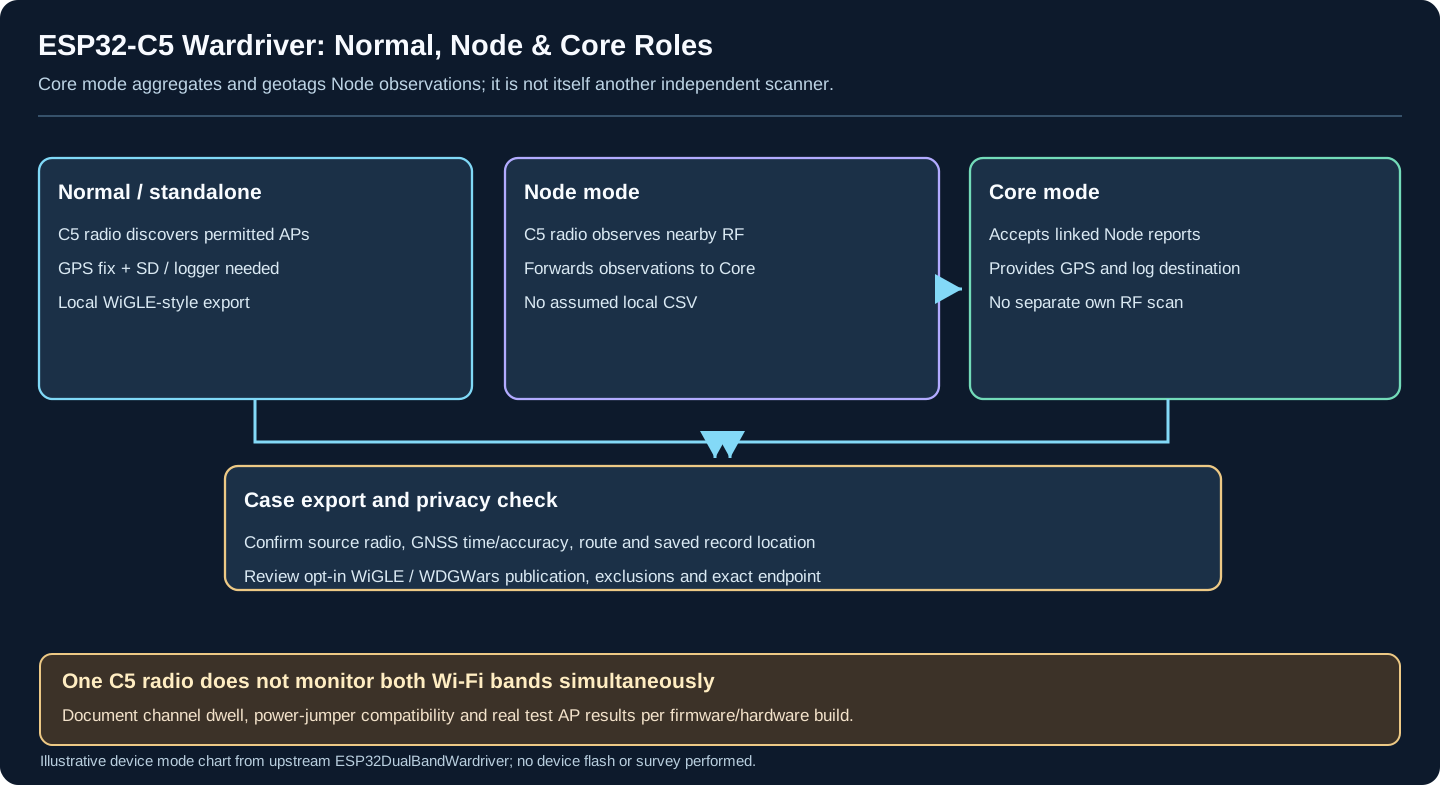
| ESP32-C5 Normal, Node & Core | ESP32-C5 Wardriver | Device roles, GNSS/SD logging, Node observations and Core aggregation |
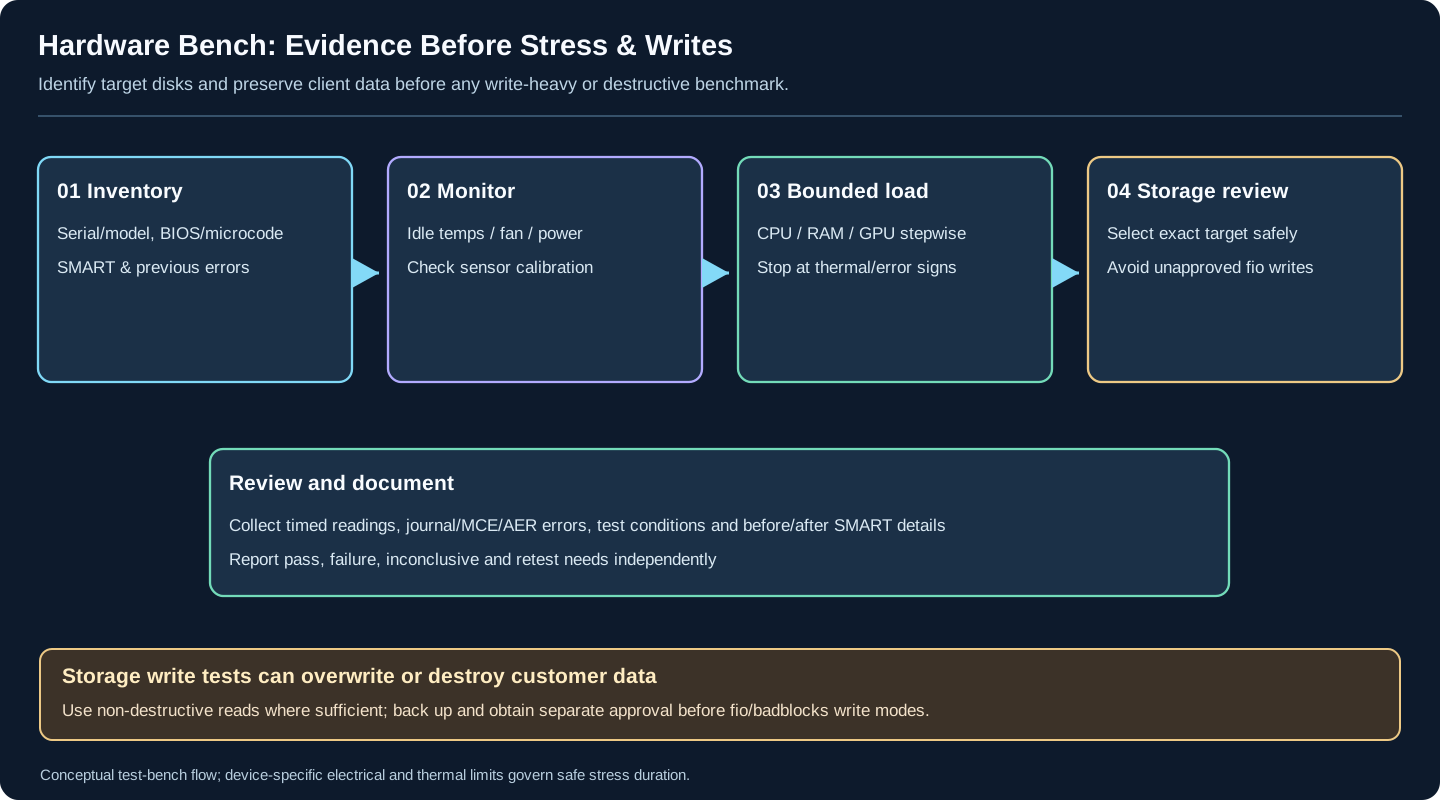
| Hardware Bench Diagnostic & Write Safety | Manjaro Intel Hardware Test Bench; Python test scripts | Baseline, telemetry, bounded stress, write-test permission and reproducible results |
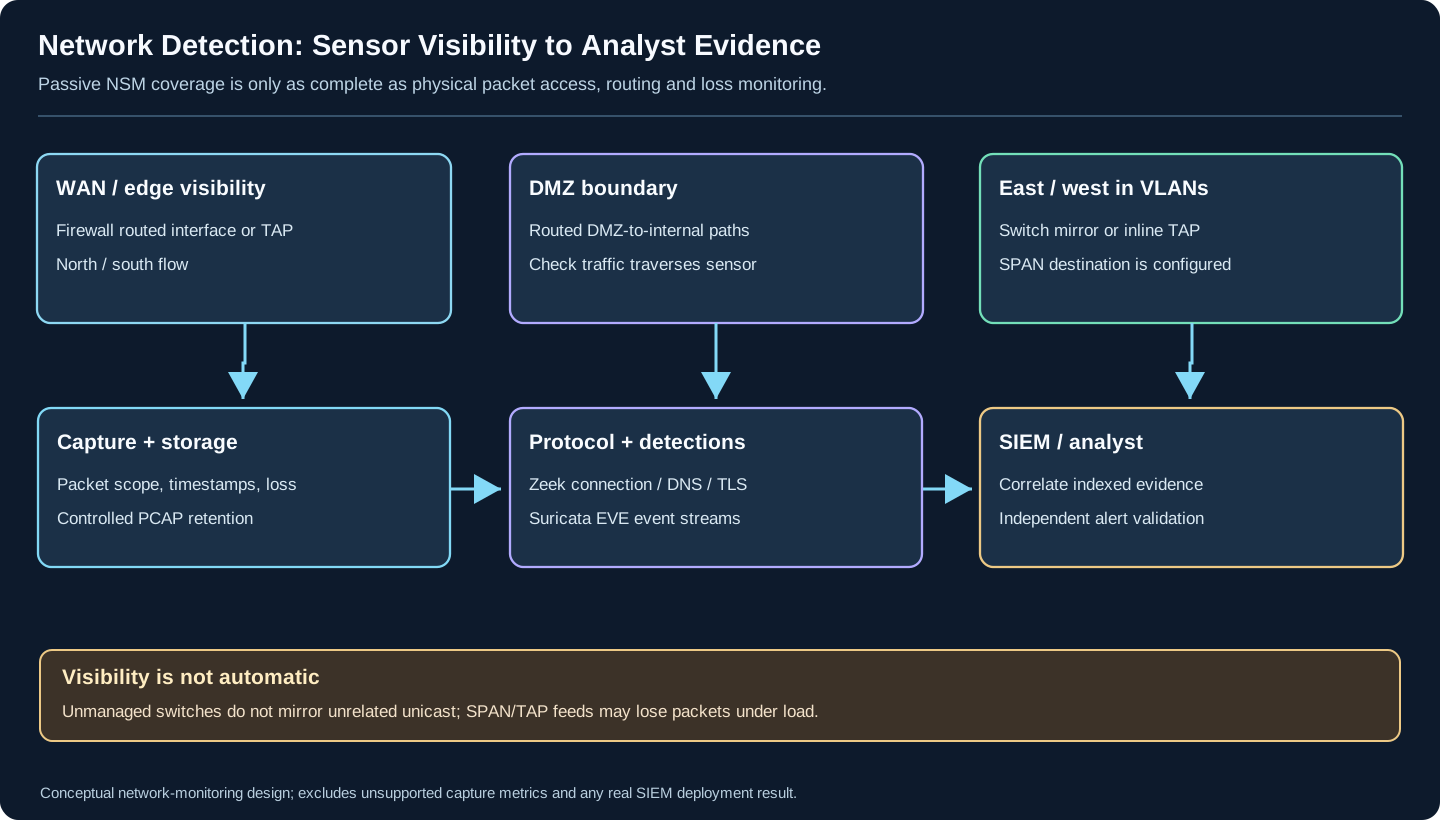
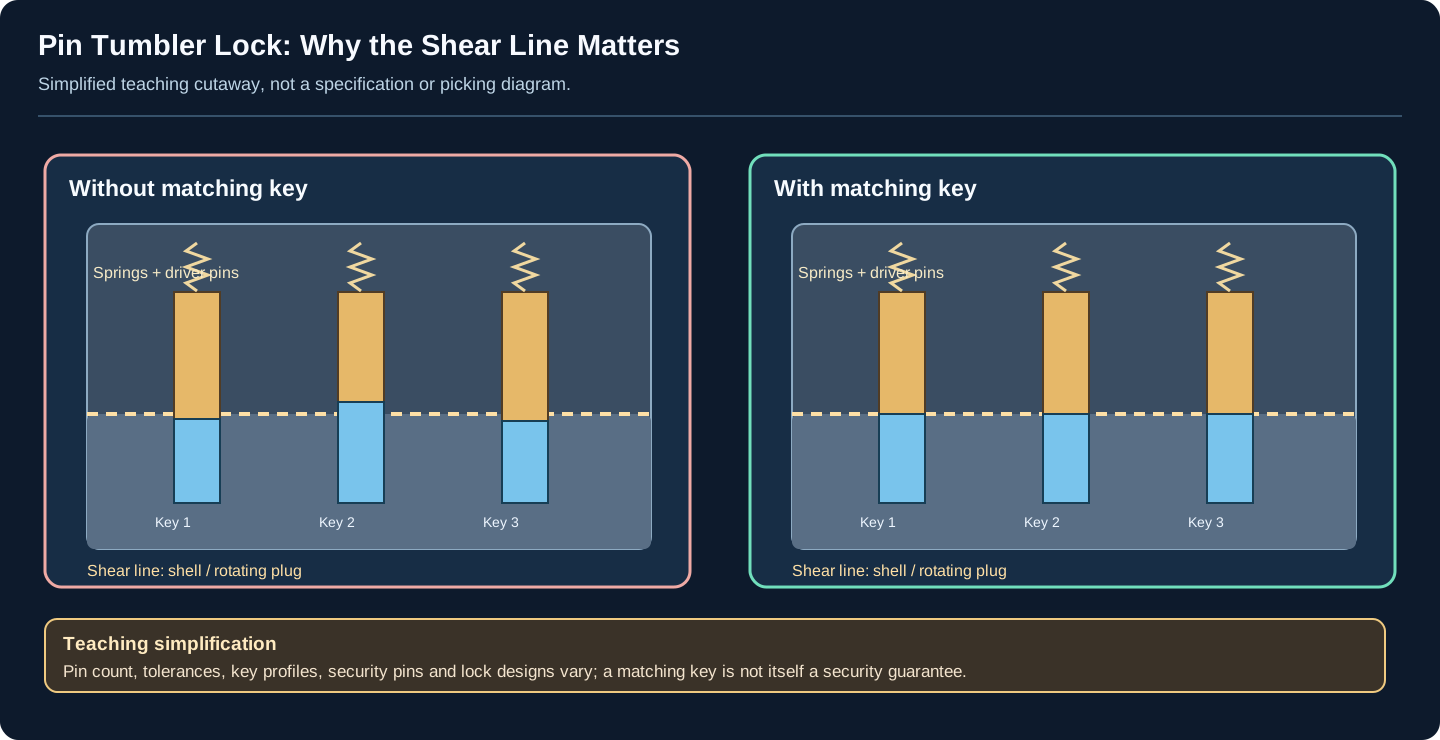
| New Diagram | Embedded Guide | Fact-Checked Scope |
|---|---|---|
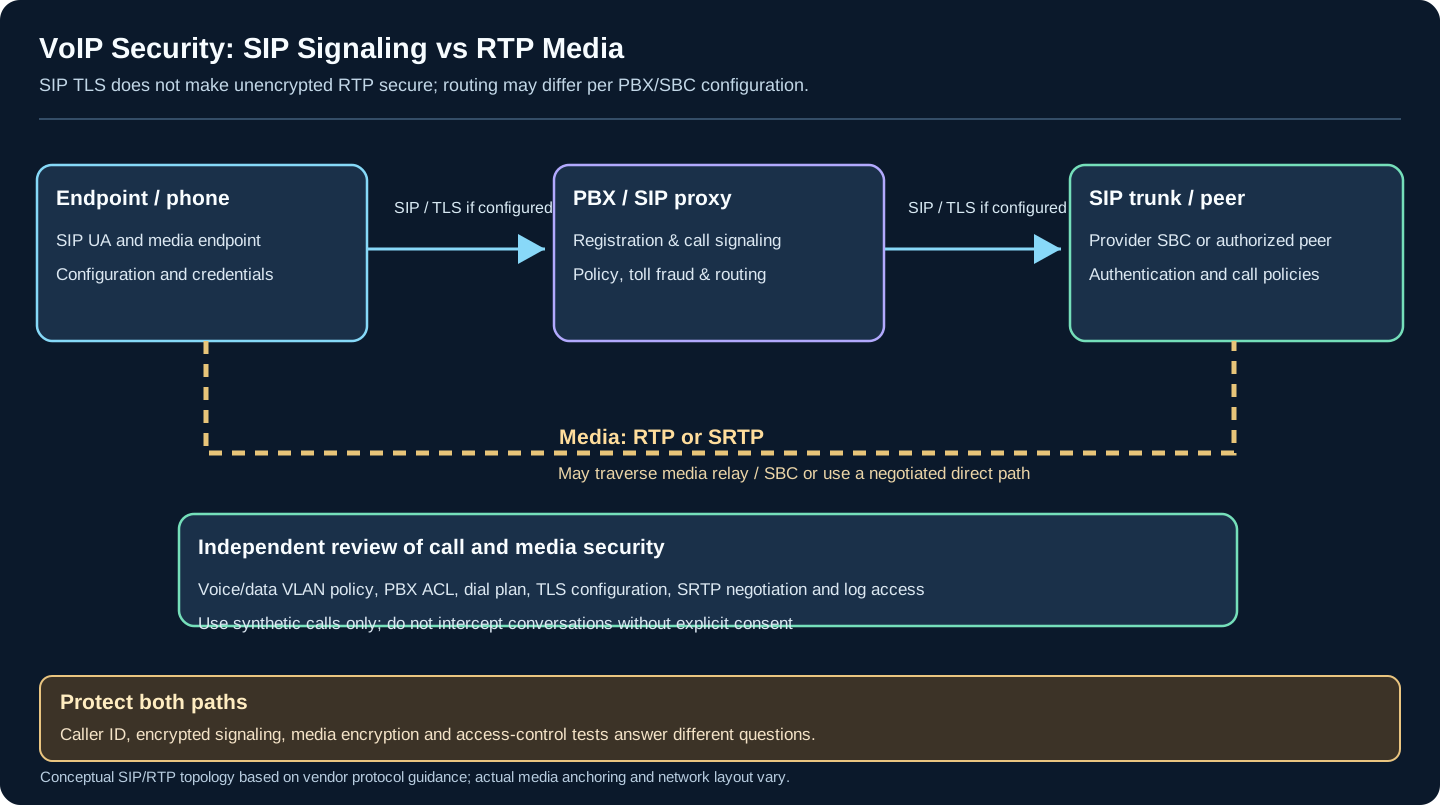
| SIP Signaling vs RTP Media | VoIP Assessment Checklist | Asterisk TLS-protected signaling versus separately negotiated SRTP media and PBX/SBC routing |
| Linux Privilege & Vendor Patch Triage | Linux Privilege Escalation Checklist | Versioned vendor CVEs, distro backports, effective sudo/SUID/cron checks and safe remediation |
| Arduino Board, Port & Bootloader Diagnostics | Arduino IDE Multi-Platform Setup | Installed board core, physical USB interface and upload protocol must be diagnosed separately |
| OSINT/CTI Source Quality to Detection | OSINT & Threat Intelligence Deep Dive | Source provenance, corroboration, time-sensitive IOCs, behavior mapping and detected-outcome evidence |
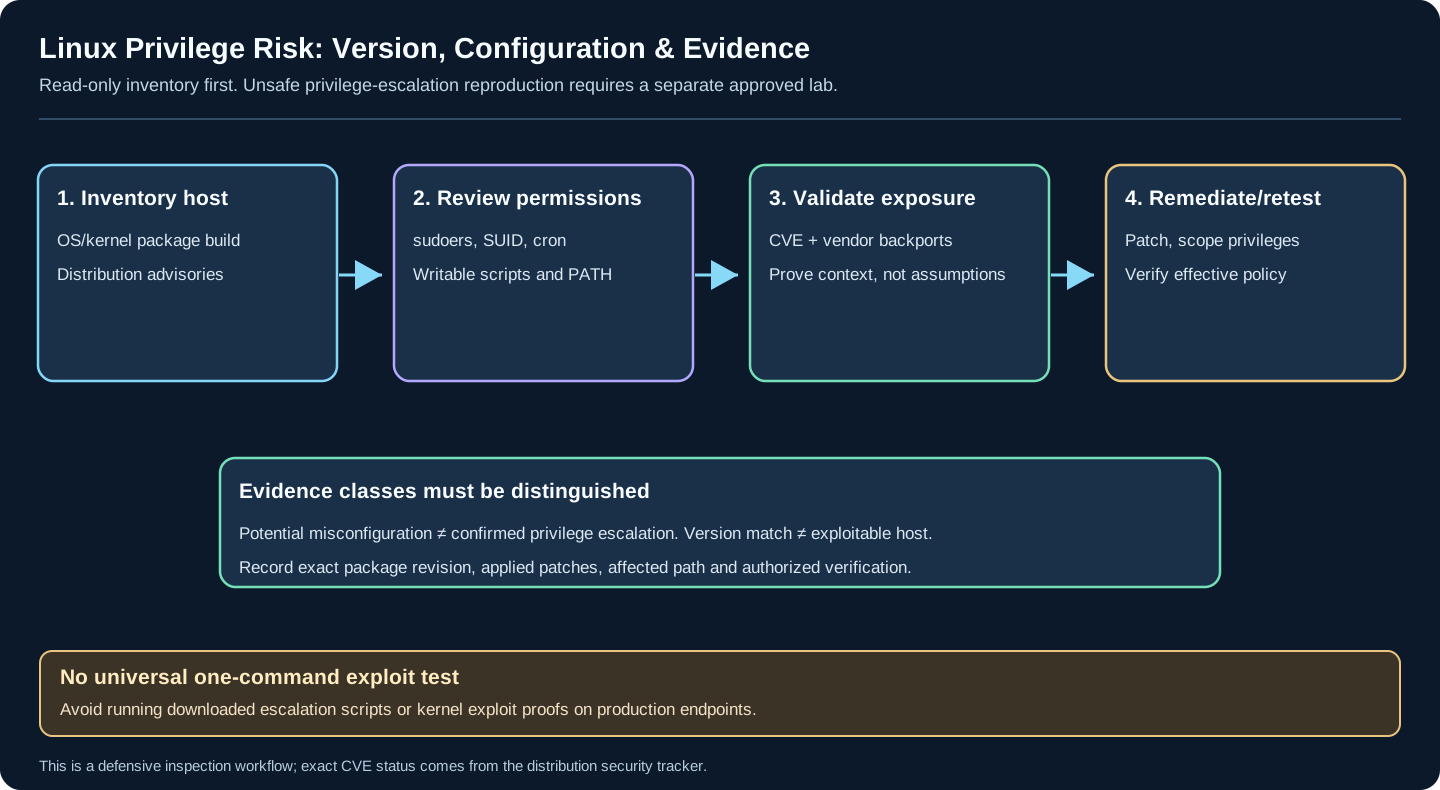
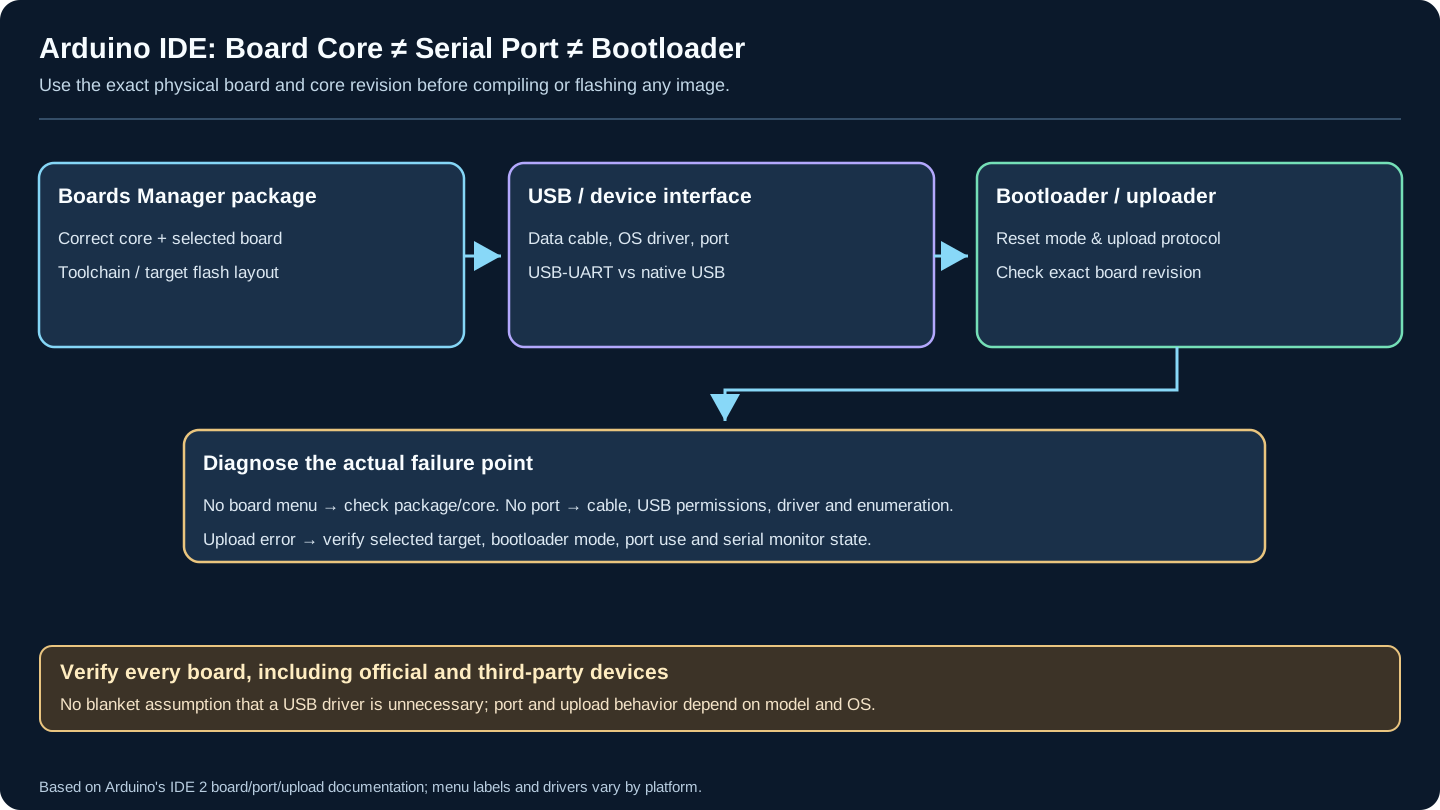
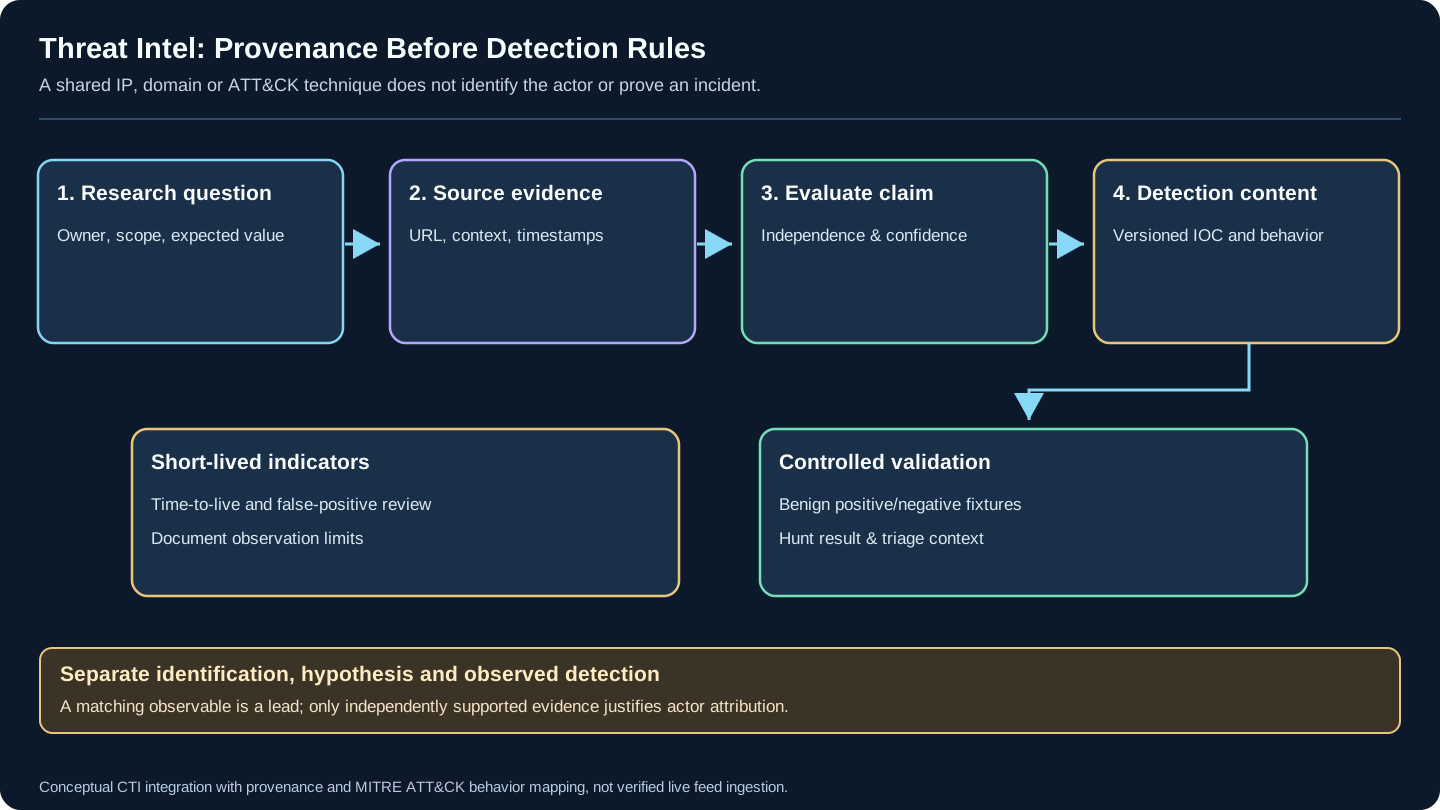
Original, editable SVG figures are placed in the relevant guides. Captions distinguish conceptual design from live evidence and link to official sources where available.
| Diagram | Embedded Guide | What the Diagram Clarifies |
|---|---|---|
| Ghidra Analysis and Validation | Ghidra Master Guide | Inferred control flow and decompilation are hypotheses requiring independent analyst checks |
| REMnux Isolation Boundaries | REMnux Malware Analysis, vx-underground | Evidence intake, static-analysis guest, optional isolated execution VM and safe export |
| Kismet GPS and Log Retention | Kismet Wireless Survey | Wireless observations, location-fix gate, additive log types and sharing approval |
| Identity Alert Investigation | Unauthorized Access Playbook | Corroborate access events and contextual identity risk before containment |
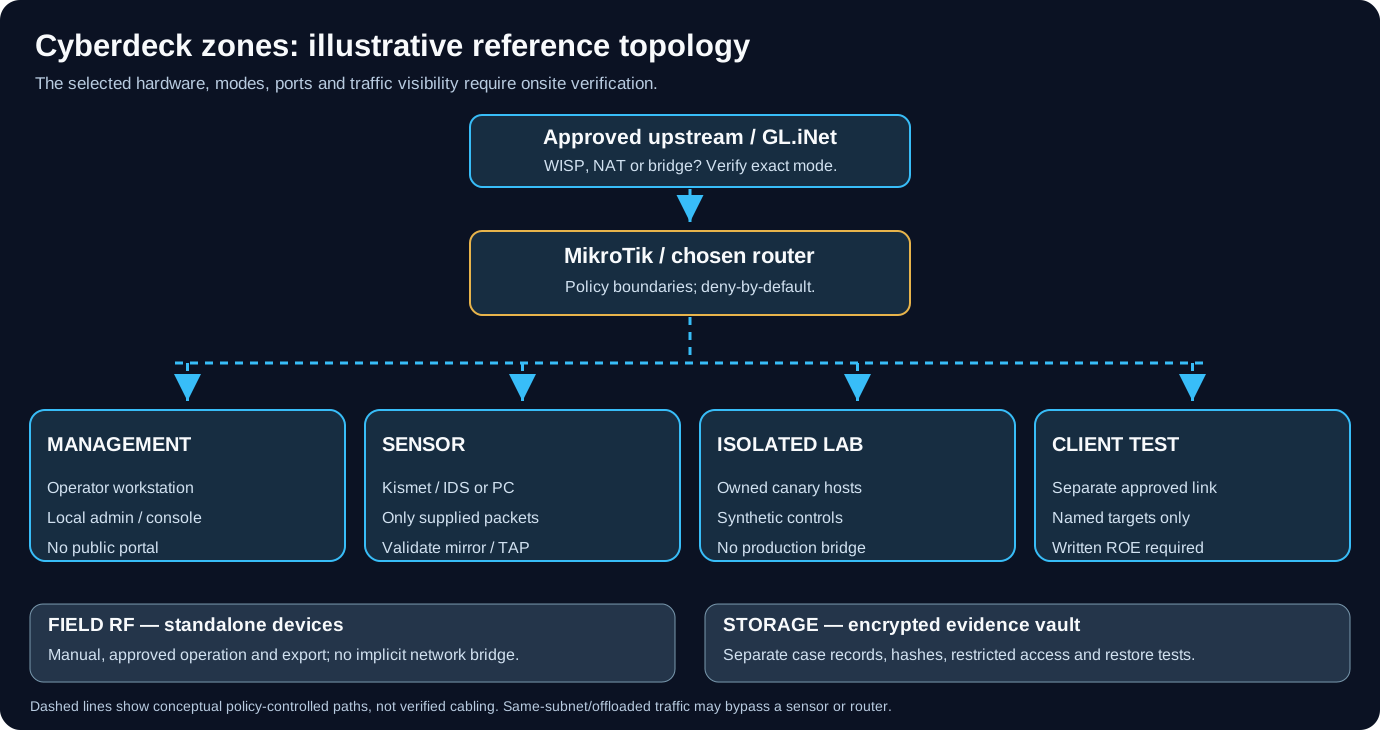
| Cyberdeck Trust Boundaries | Cyberdeck Public Reference | Logical GL.iNet/MikroTik path, intended zones and hardware validation caveat |
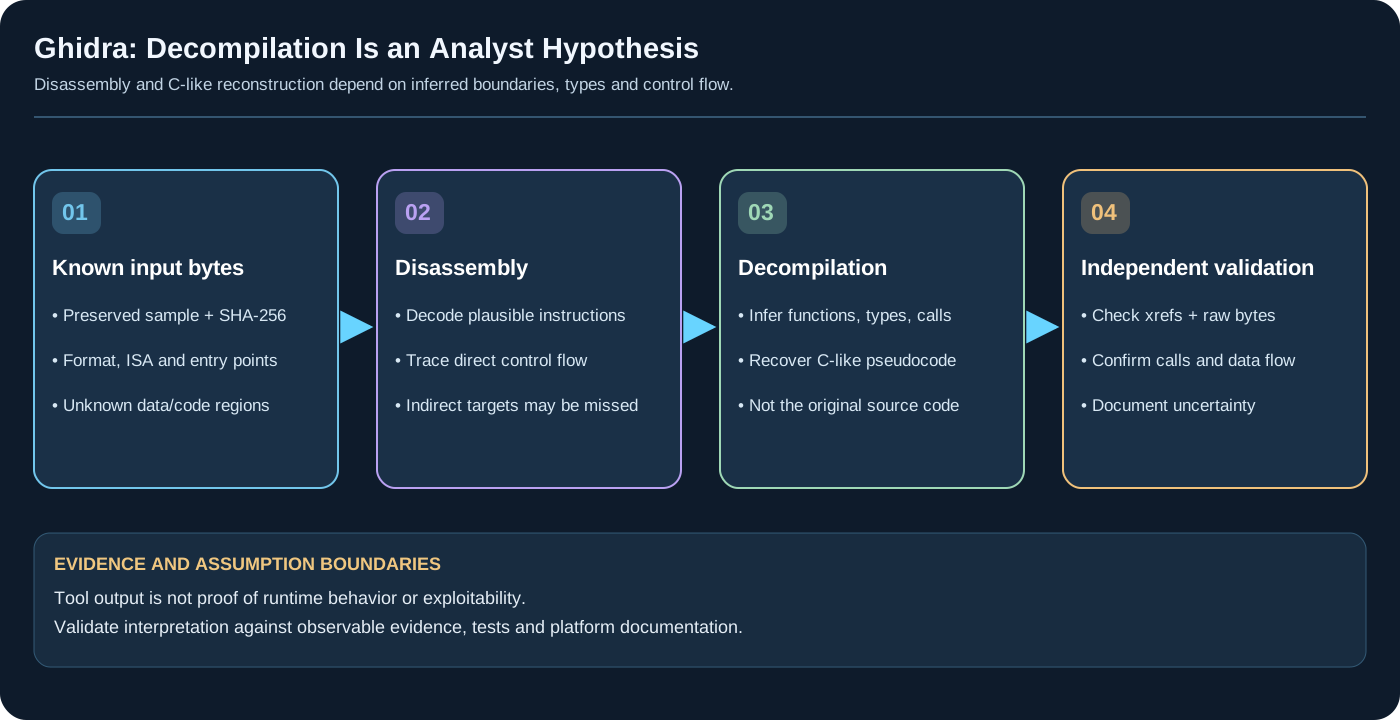
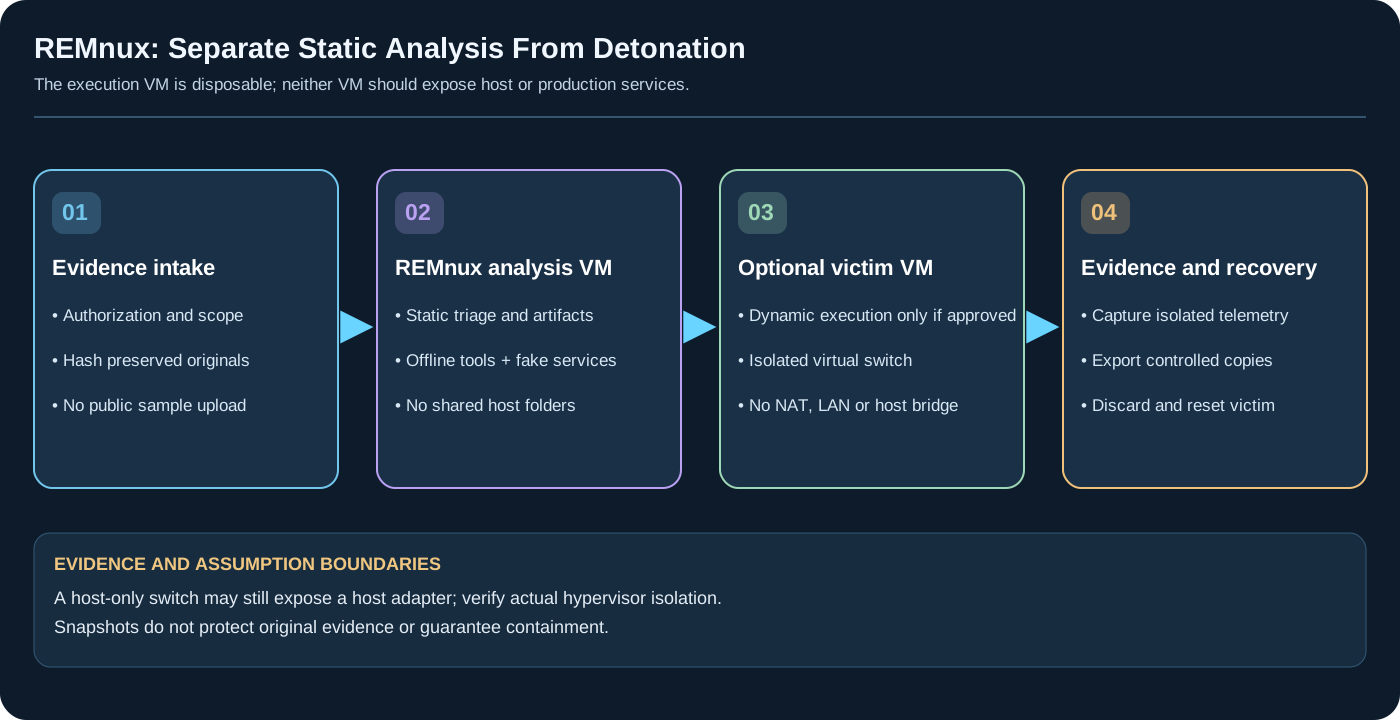
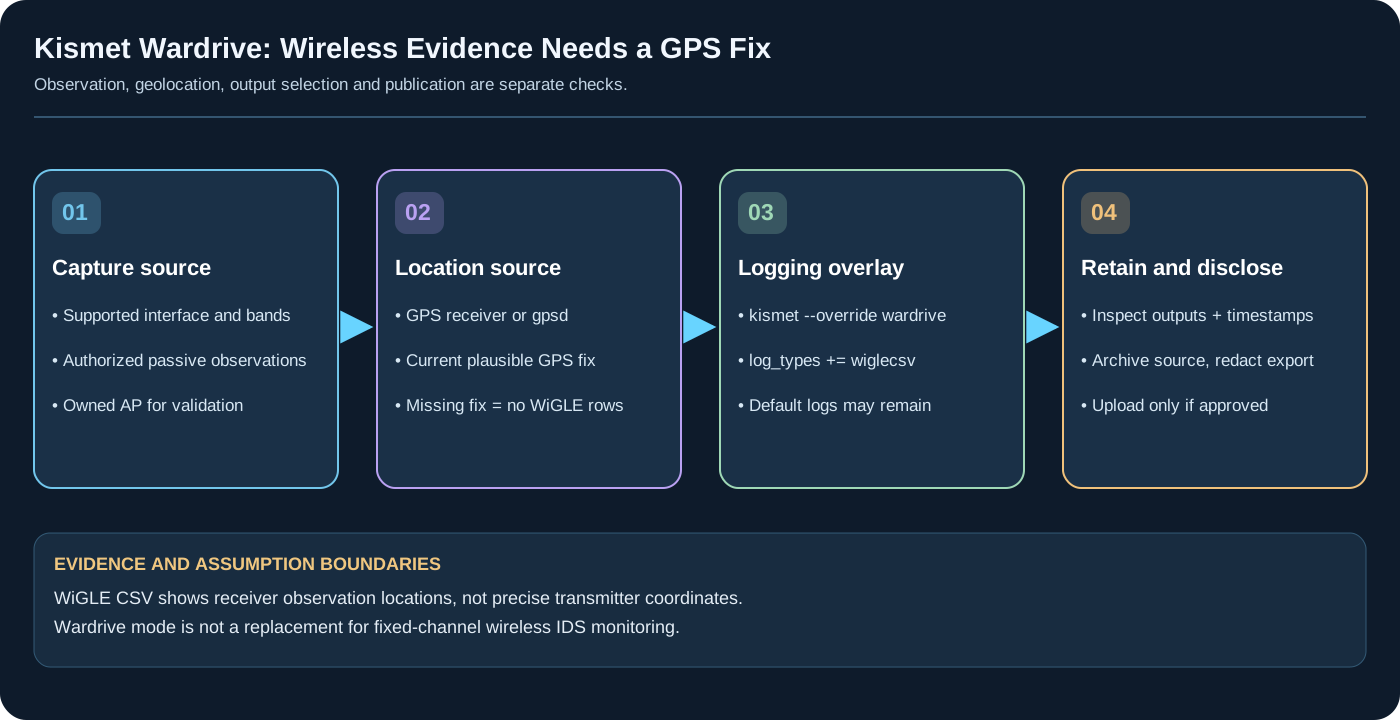
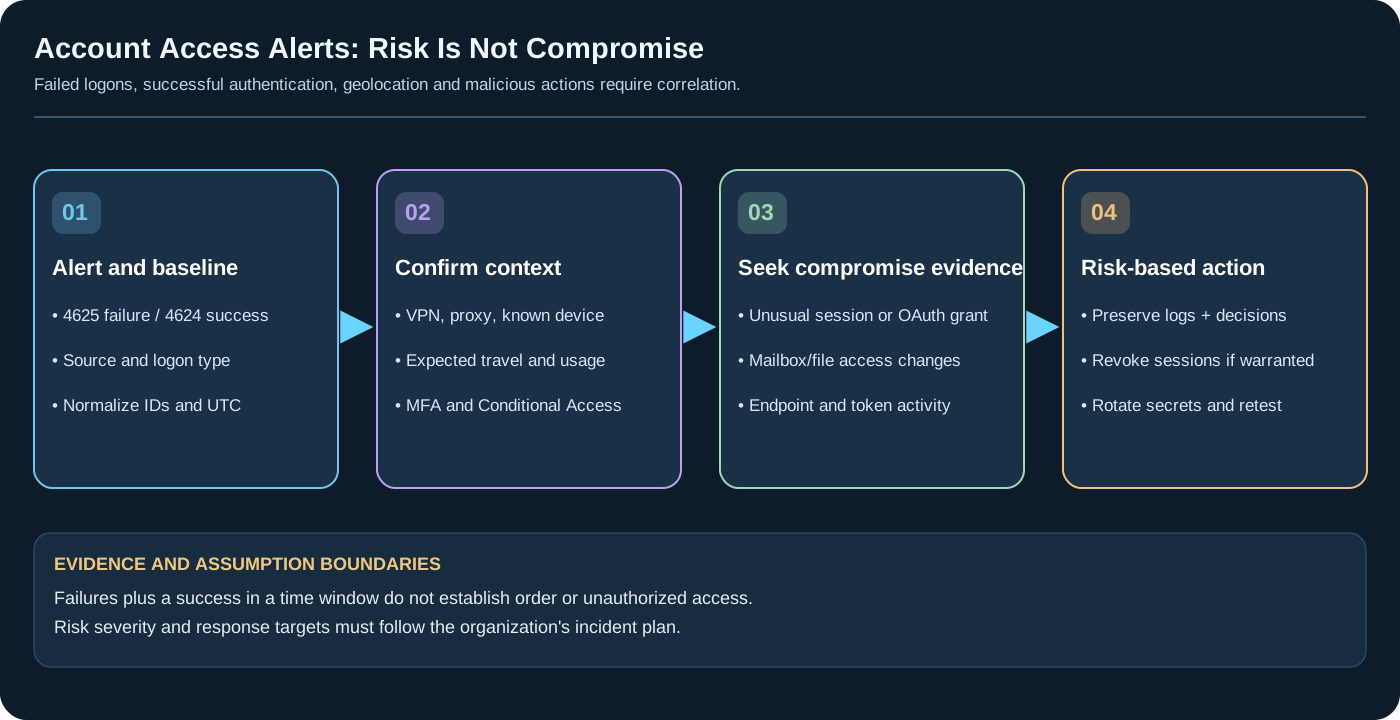
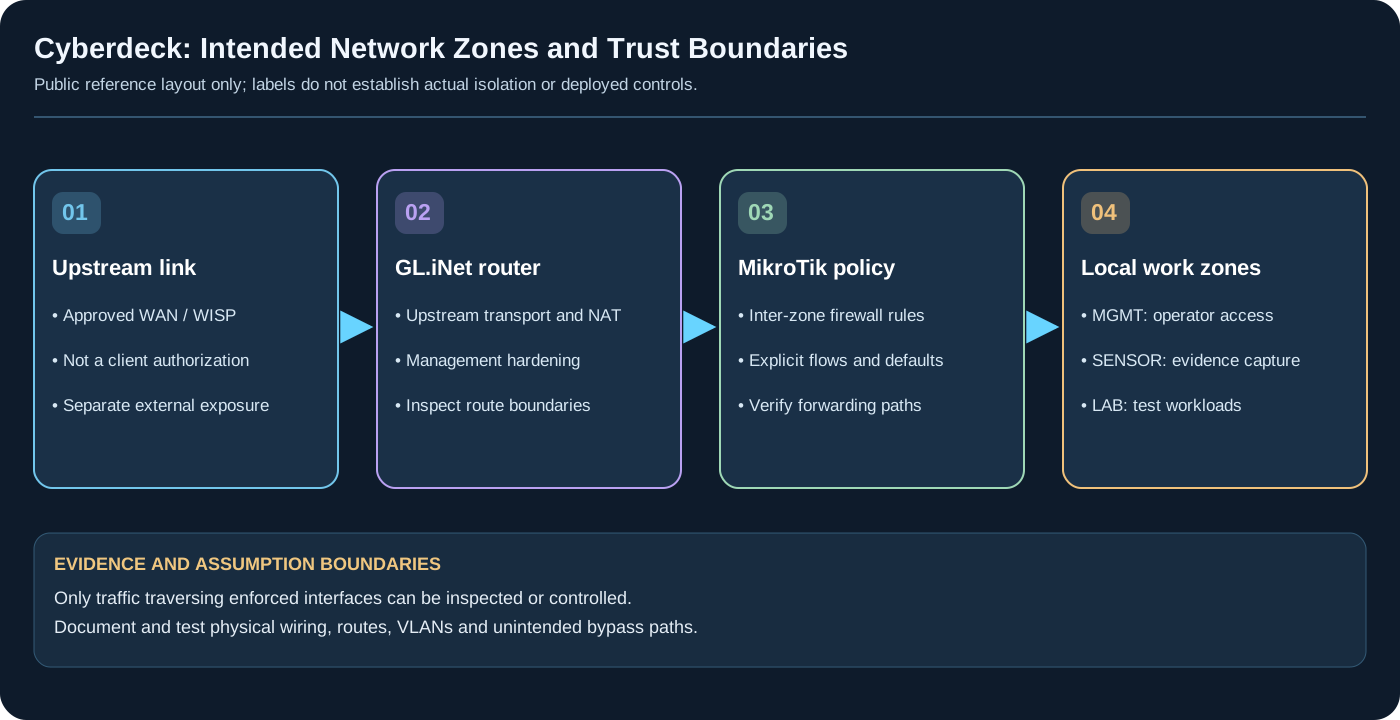
These editable original SVGs are embedded in their explanatory chapters and paired with appropriate source references and caveats.
| Diagram | Embedded Guide | Verified Scope |
|---|---|---|
| NIST 800-61 Rev. 3 & CSF 2.0 Incident Response | Enhanced Incident Response Playbook | Current NIST framework, locally defined operating steps and explicit non-certification |
| Independent AI Evidence Audit | Verification & AI Audits | Distinguish source claims, actual tool receipts and confirmed end state |
| Historical Cipher Analysis | Classical Cryptanalysis | Substitution versus repeating-key tests, misleading peaks and ambiguity |
| Safe Bash Execution Gates | Bash Scripting Cheat Sheet | Validate optional args, quoting, syntax checks, side-effect boundaries |
| ESP32 Firmware Acceptance Gates | ESP32 Security Firmware Catalog | Chip/board-specific builds, flash layouts, recovery and post-boot qualification |
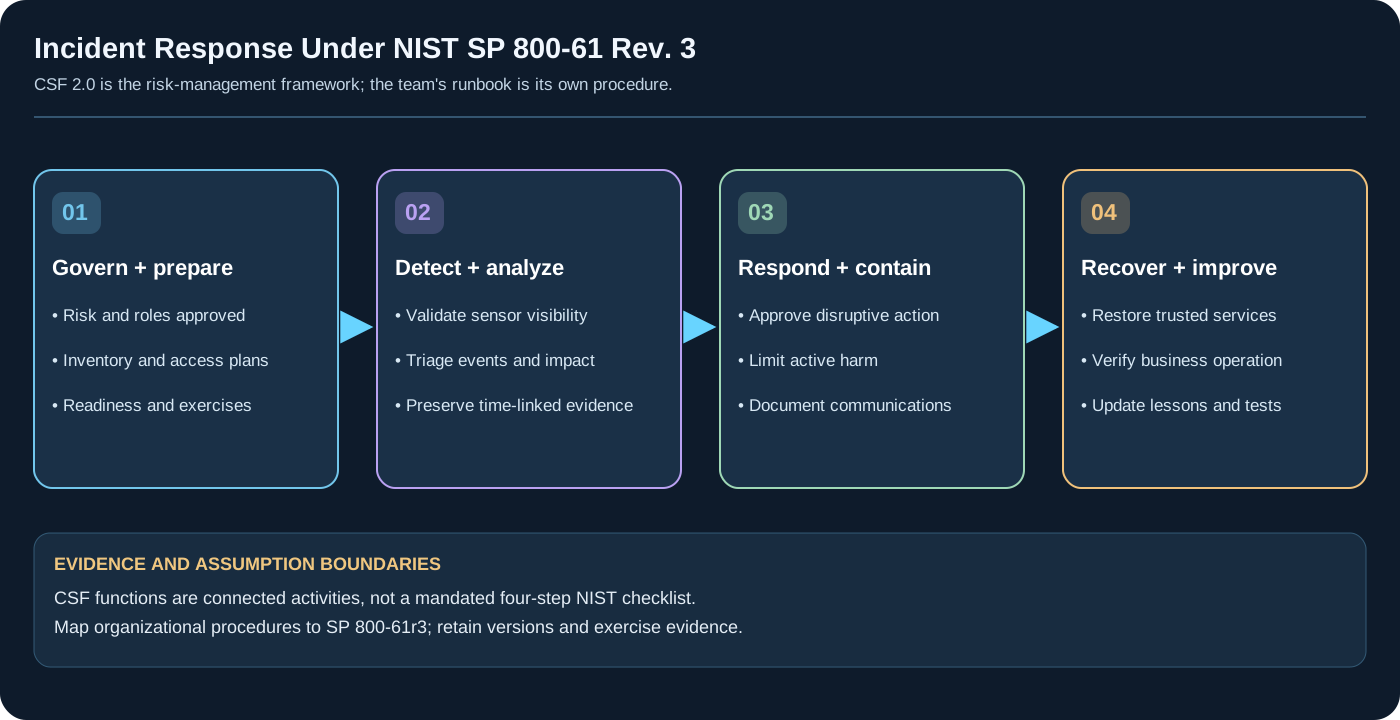
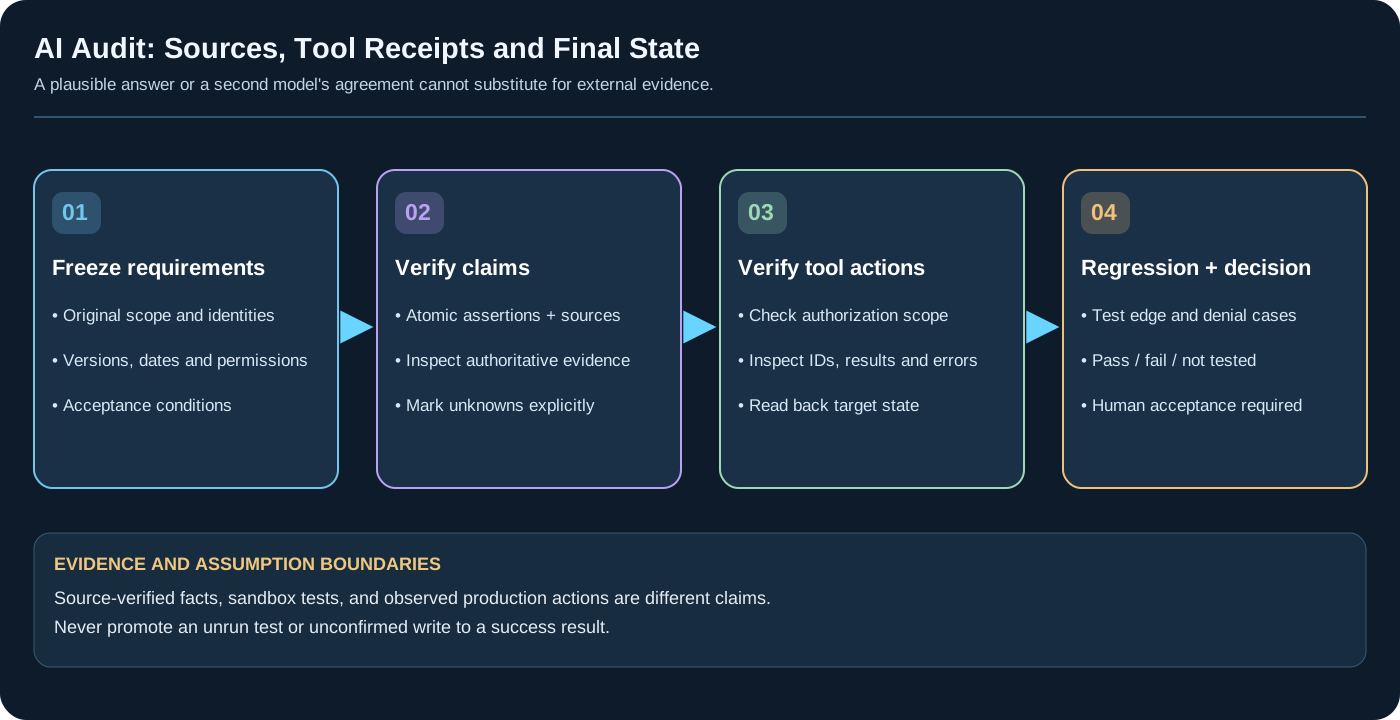
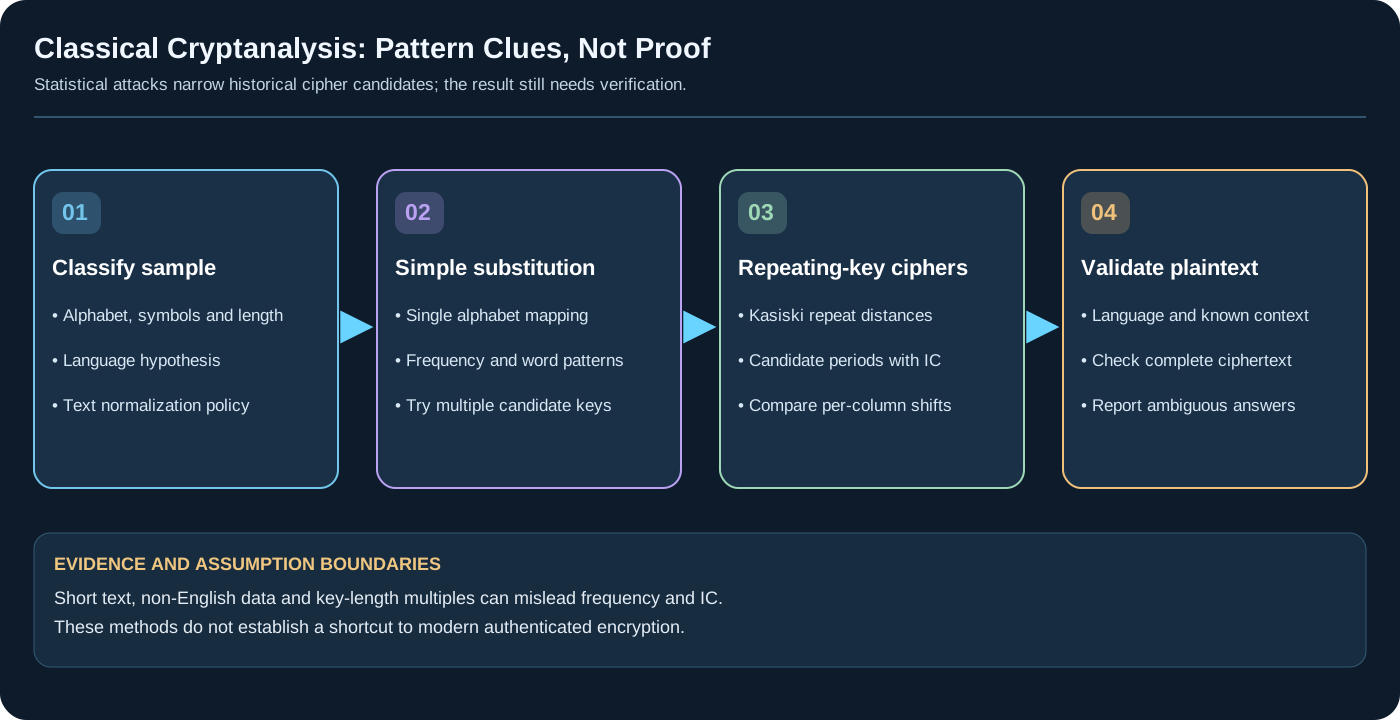
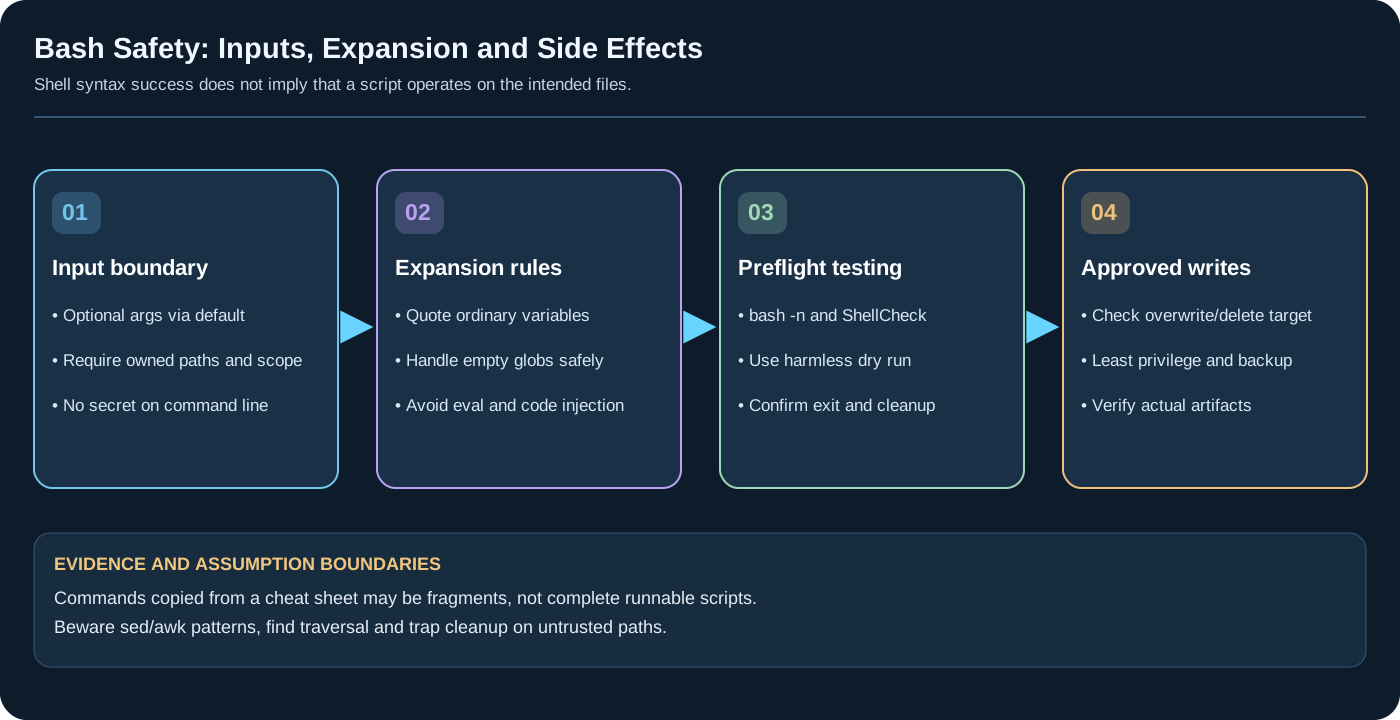
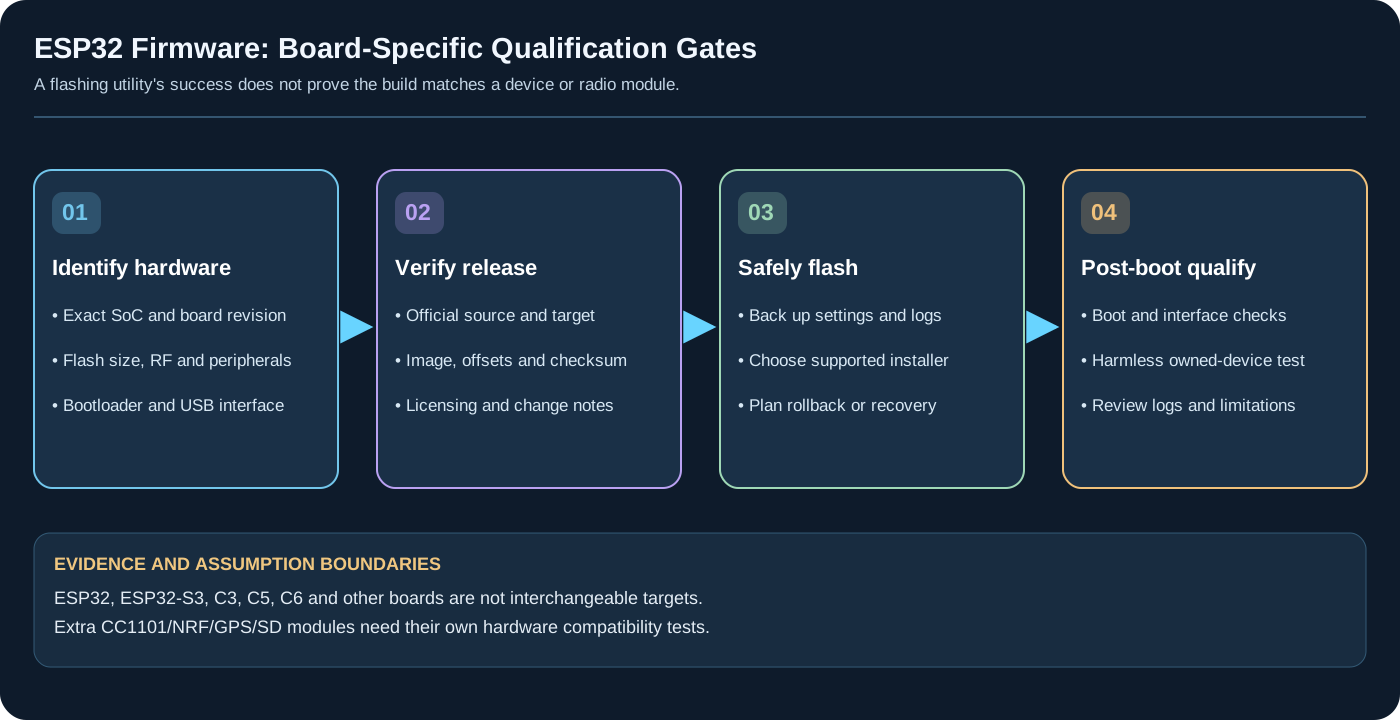
Original, editable diagrams embedded directly into the related technical chapters. Their captions distinguish educational models from any untested device/runtime scenario.
| Diagram | Embedded Guide | Core Limit |
|---|---|---|
| Python Security Example Qualification | Python Security Cheat Sheet | Windows native prototypes, legacy API versions, safe local probes and observed outcomes |
| Classical Cipher Family Comparison | Classical Ciphers | Distinguishes codes, substitution, transposition, periodic shifts and OTP requirements |
| Pentoo Deployment & Portage Gates | Pentoo Linux Field Guide | Distinguishes live image, installed system, Gentoo overlay and hardware validation |
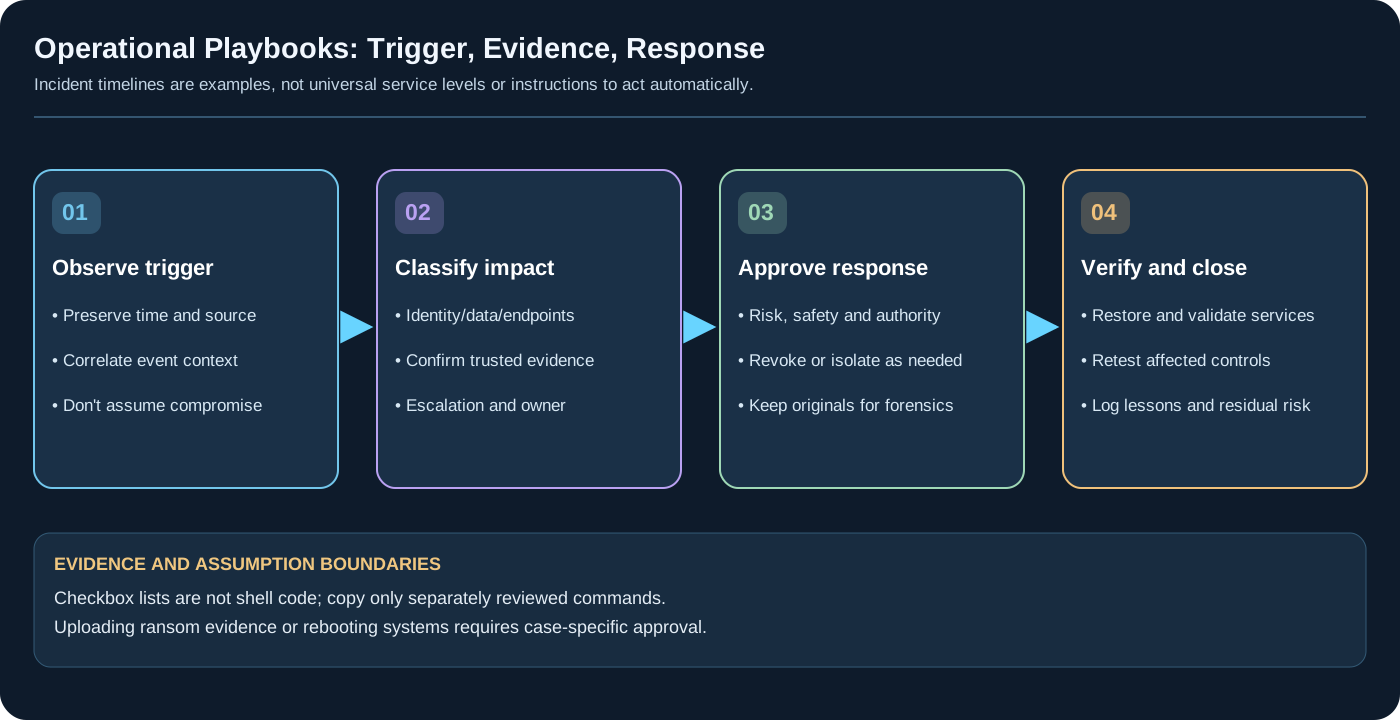
| Incident Casebook Evidence and Approval | Operational Playbook Library | Correlate event evidence and authority before containment, recovery and notification |
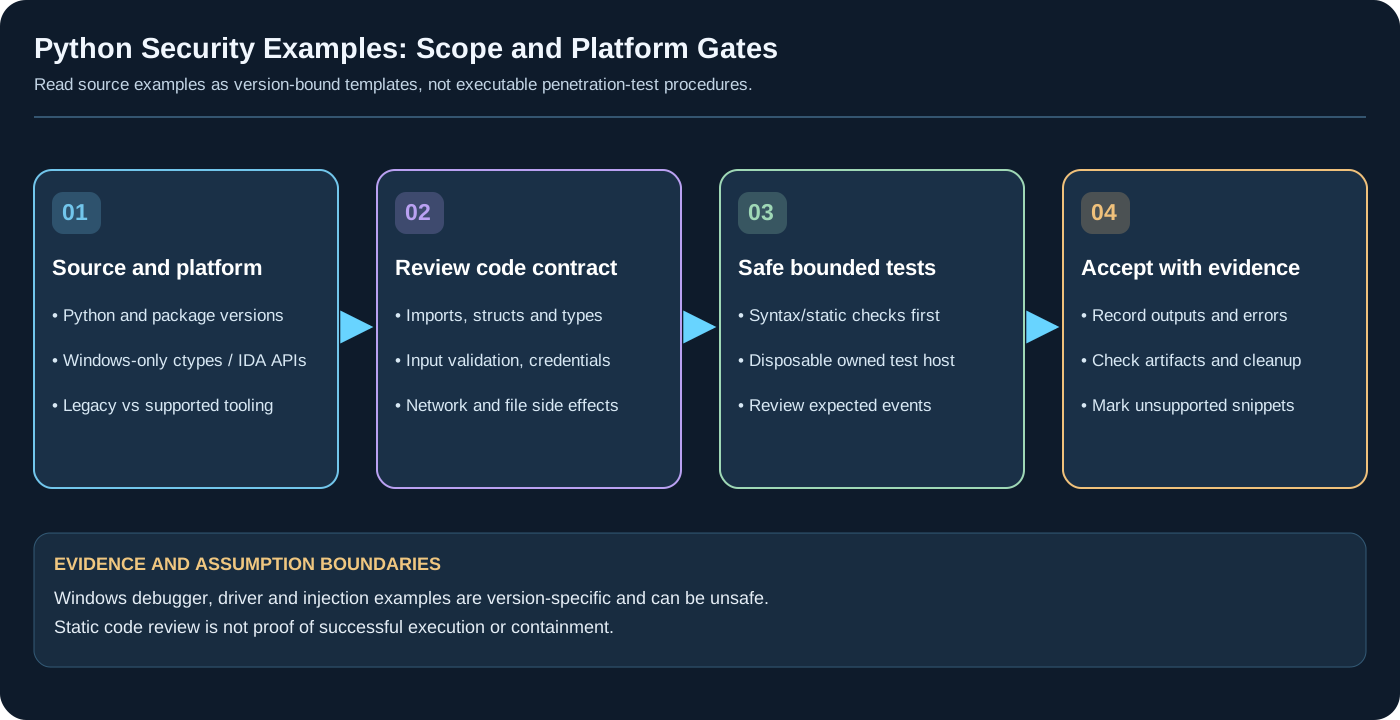
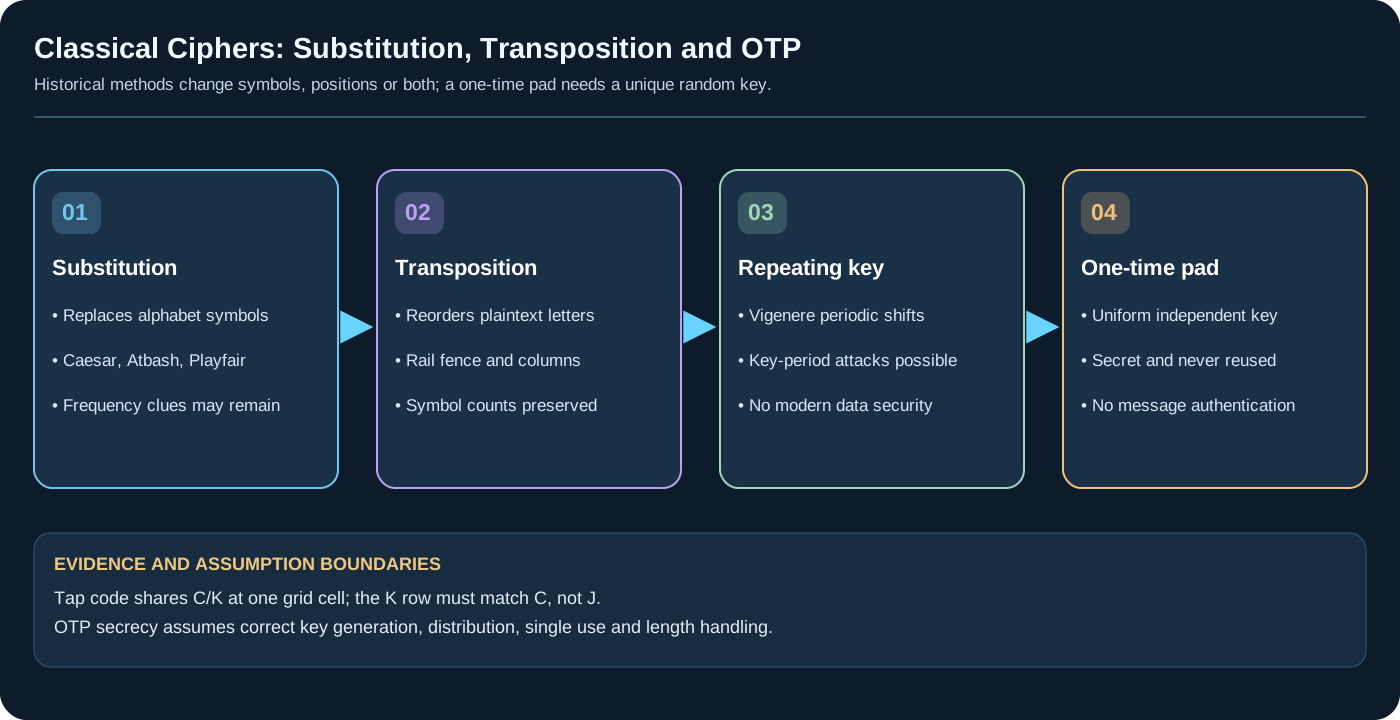
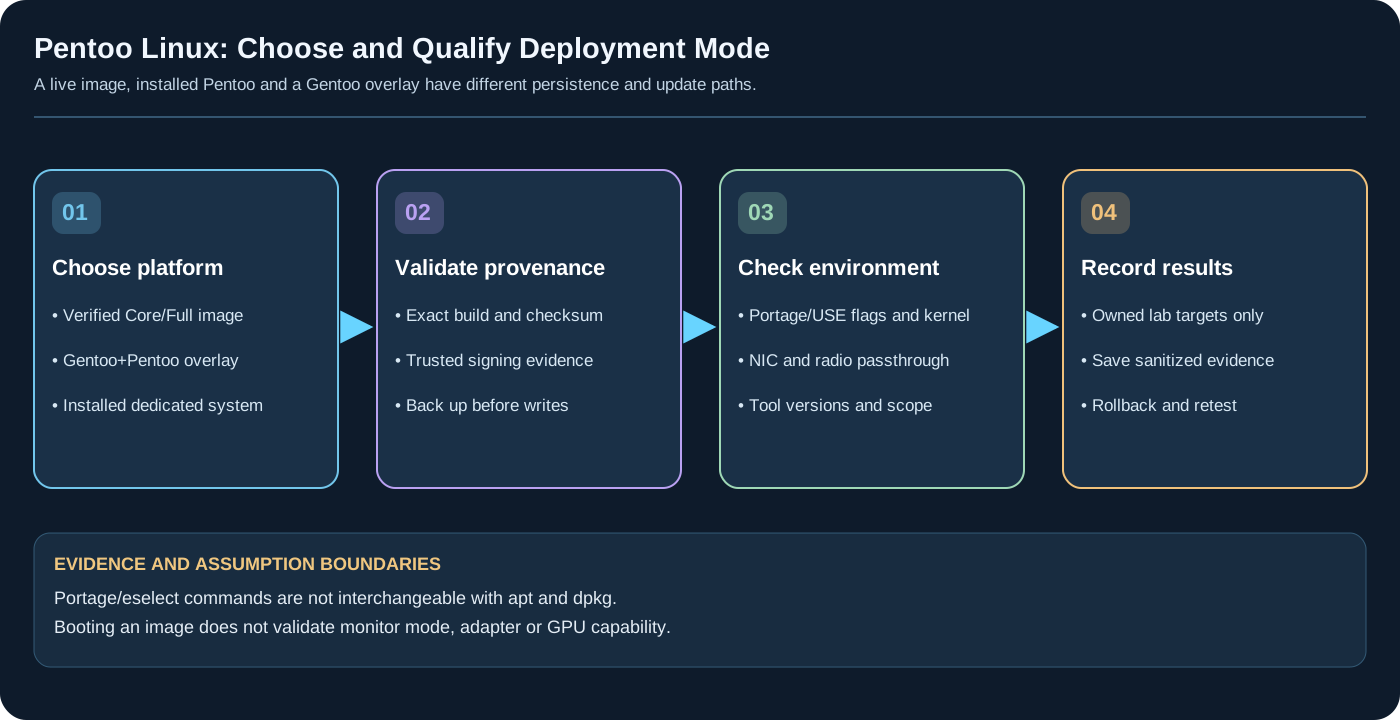
| Diagram | Embedded Guide | Scope |
|---|---|---|
| Whole-repository evidence gates | Repository Verification & Content Completeness Protocol | All-file inventory, static checks, fact/source review, lab verification and independently reviewed corrections |
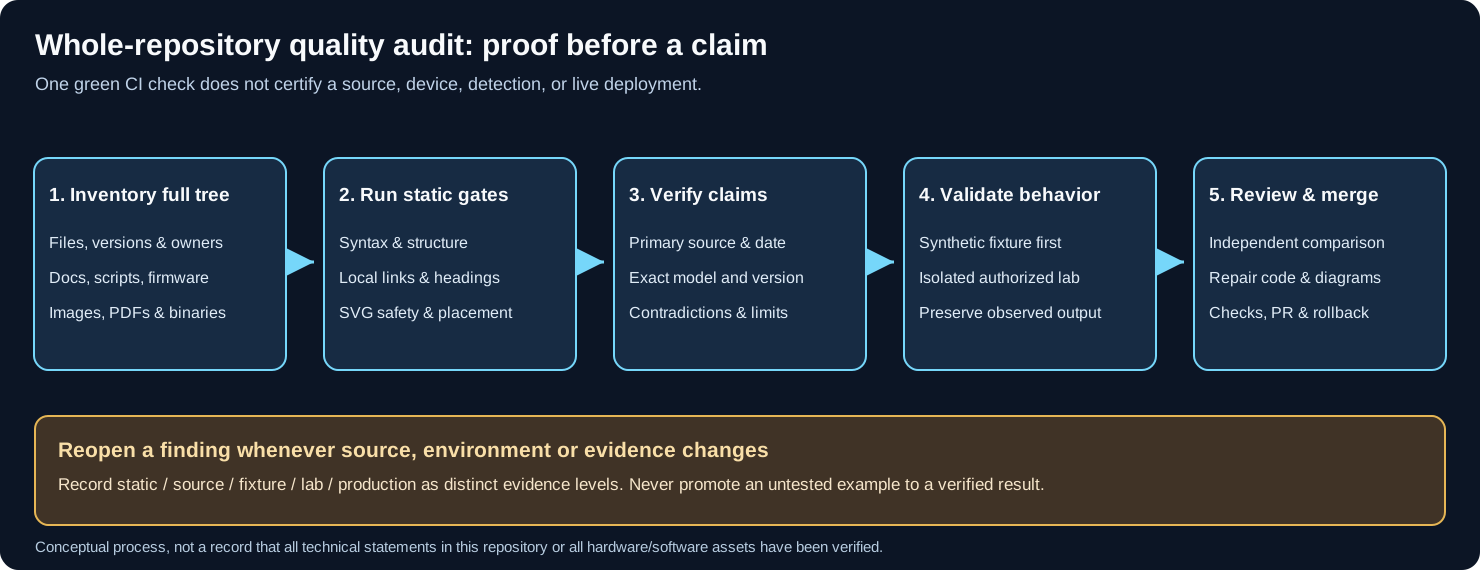
This diagram illustrates the verification method, not a certification that any individual claim or system was tested. Coverage reports are generated by the visual audit tool.
These figures illustrate the actual decision points in their respective guides; they are not claims of tested hardware, live provider integrations, or completed assessments.
| Diagram | Embedded Guide | Visual Purpose |
|---|---|---|
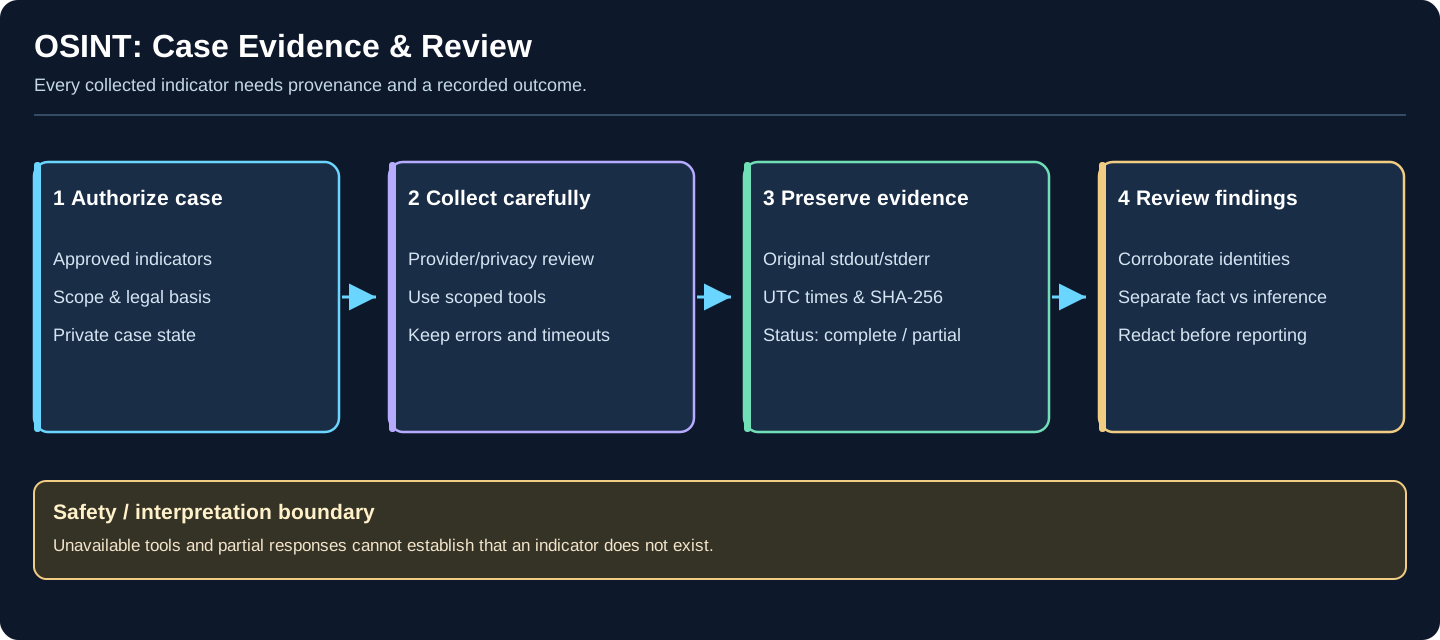
| OSINT Case Evidence & Review | OSINT Investigator Playbook | Authorized indicators, scoped collection, raw evidence, source verification, incomplete-result handling |
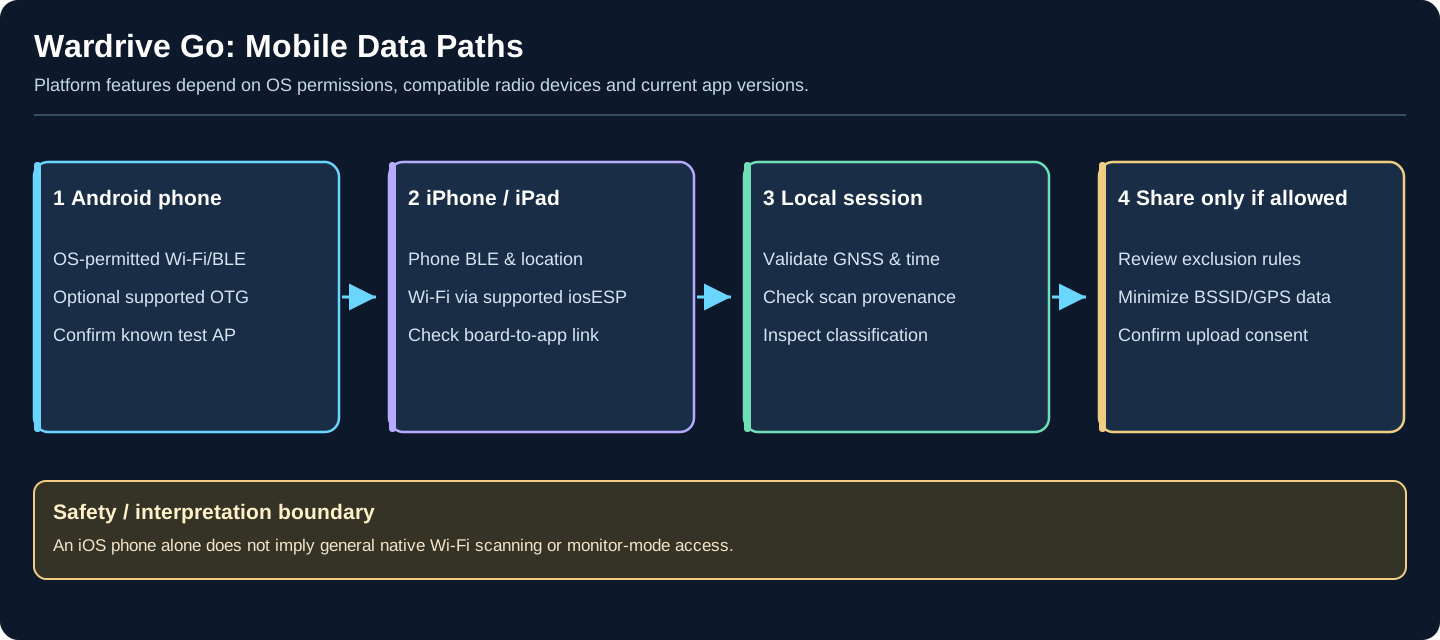
| Wardrive Go Platform Collection Boundaries | Wardrive Go Mobile Surveys | Android and iOS radio paths, optional external receiver, GPS session review, privacy before upload |
| Cyberdeck Assessment Gates | Cyberdeck Assessment Workflow | Four visual groups summarizing the seven manual assessment stages |
| MCP Trust & Approval Gates | MCP Tooling & Secure Permissions | Separate untrusted input, host policy, server-side permissions, and human approval of effects |
| Wireless Survey Data & Privacy Gates | Wardriving Data Handling | Authorized survey records, protected originals, minimized derivatives and upload review |
| Cyberdeck Evidence & Redaction Lifecycle | Cyberdeck Evidence & Privacy | Offline case, SHA-256 integrity inventory, redacted derivative and controlled retention |
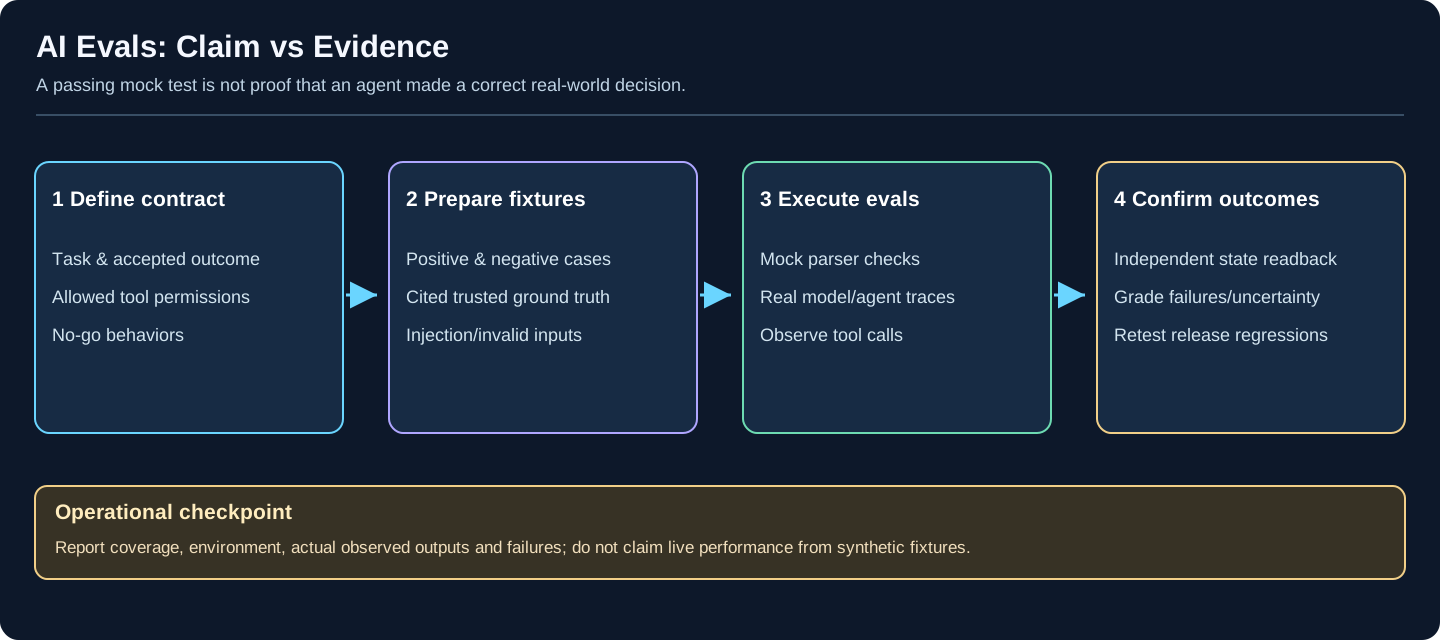
| AI Evaluation Evidence Matrix | AI Evaluation & Regression Testing | Separate deterministic tests, live agent behavior and independent end-state validation |
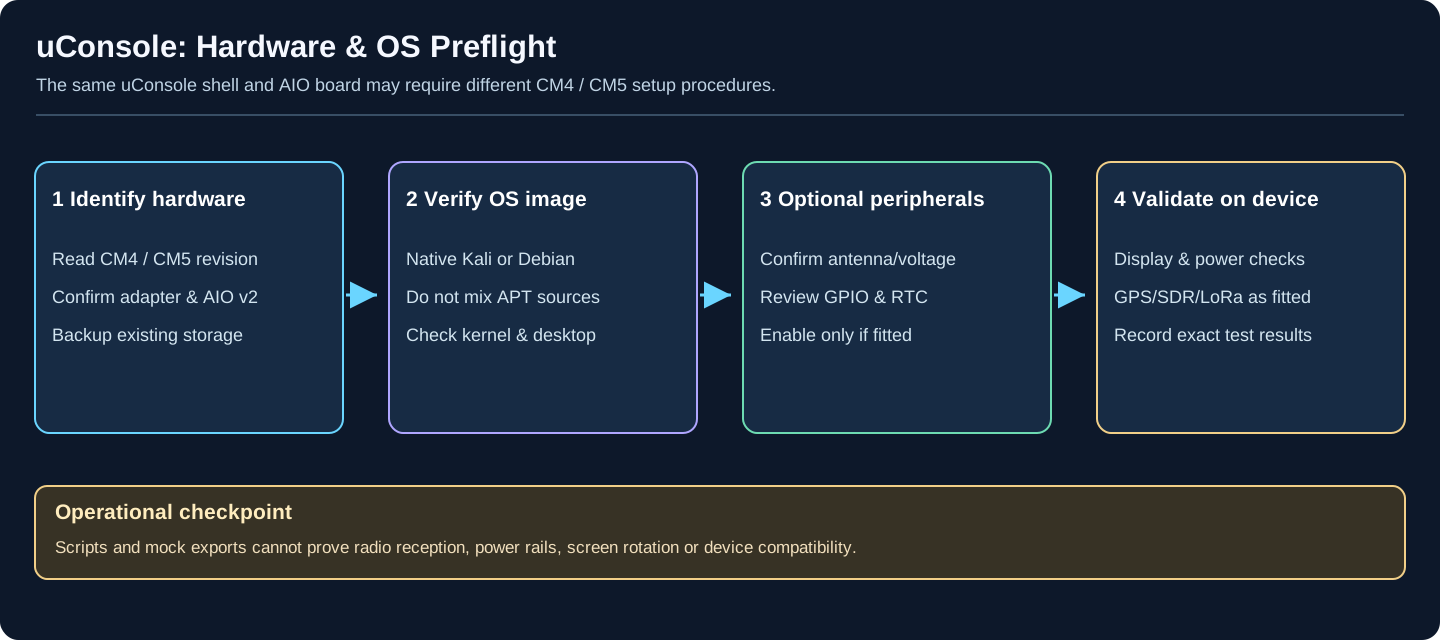
| uConsole Hardware & OS Preflight | uConsole Setup | CM4/CM5 distinction, native OS image, optional peripherals and physical readback |
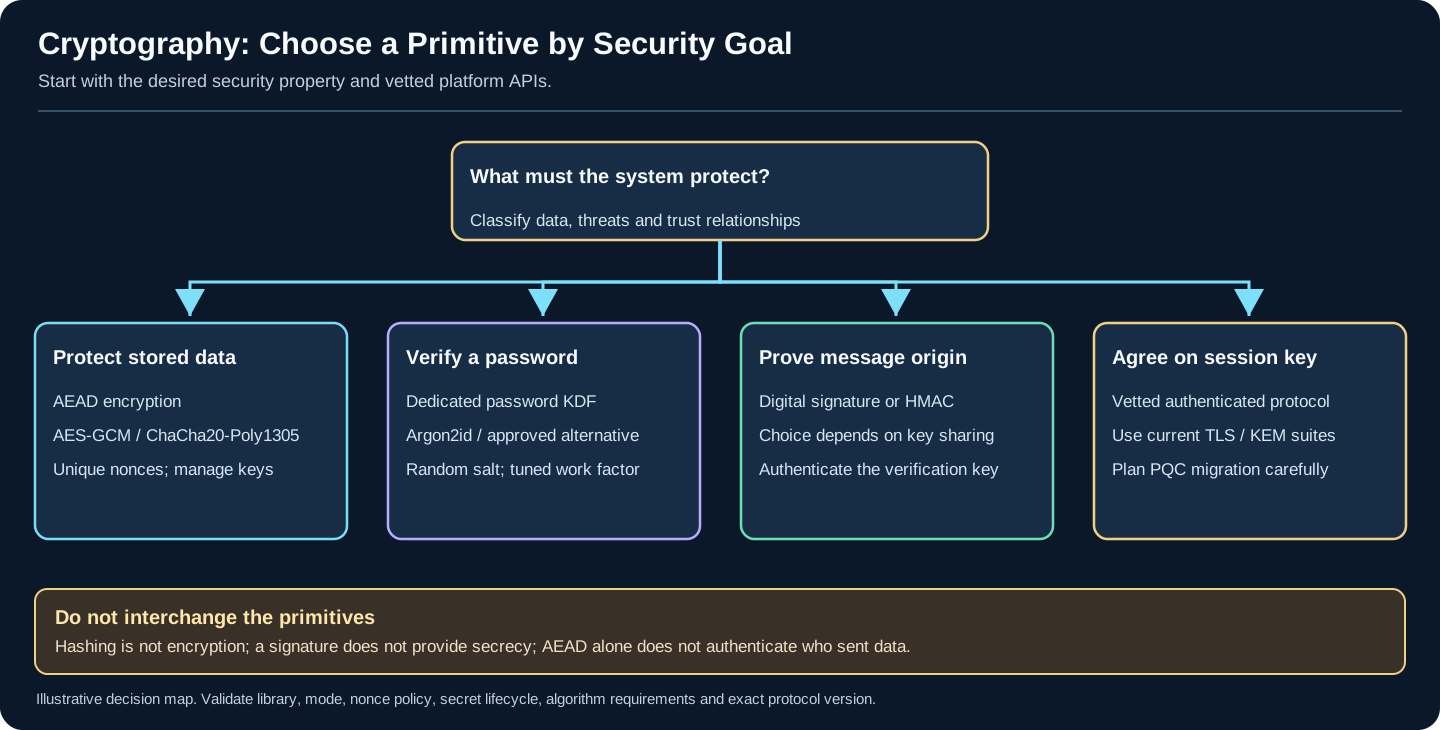
| Cryptography Primitive Decision Map | Cryptography Overview | Four distinct security goals: AEAD, password KDF, signatures/HMAC and key establishment |
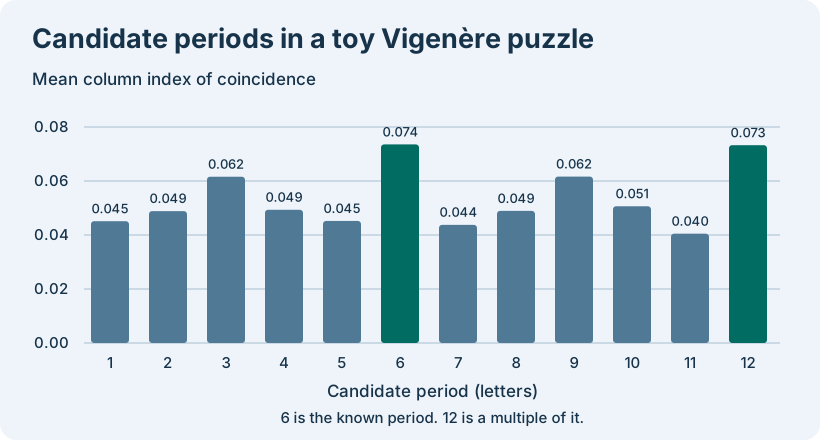
| Vigenère candidate periods | Classical cryptanalysis | Mean column IC values for a reproducible synthetic repeating-key example |
| Passive IDS Network Visibility | Homelab Networking & Isolation | Unmanaged switch visibility limitation vs configured managed SPAN; inline TAP is a separate physical option |
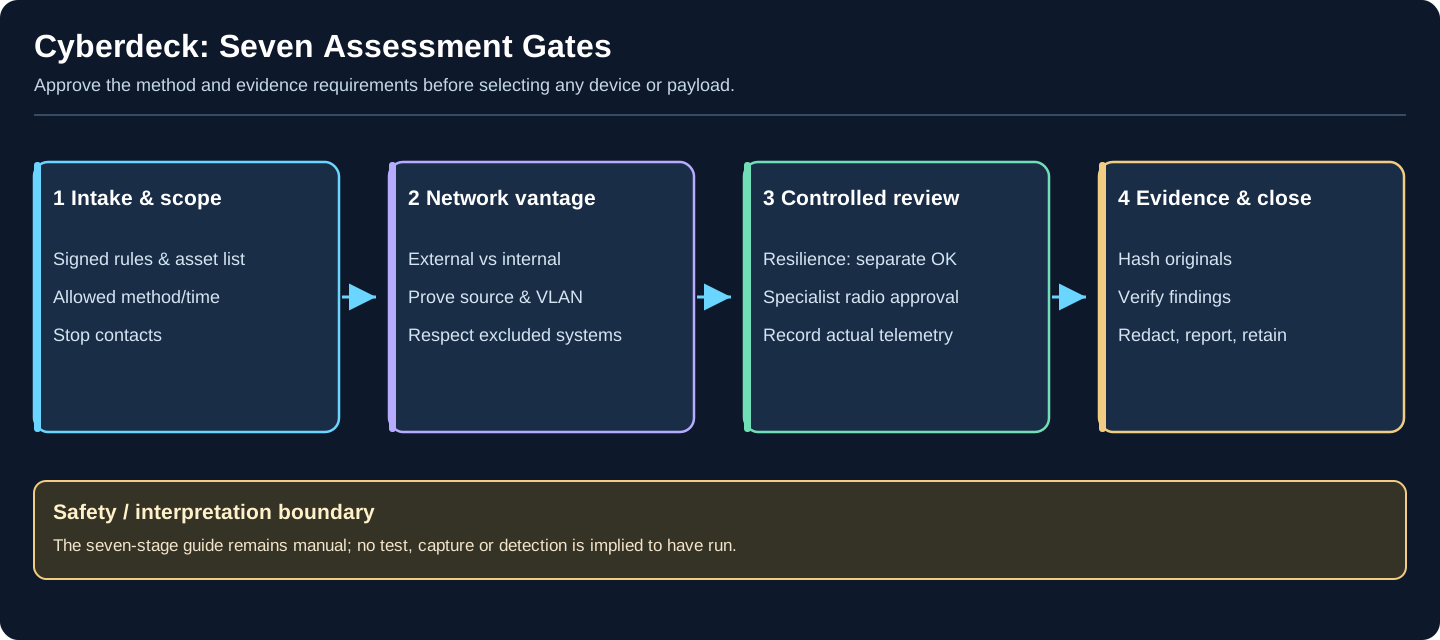
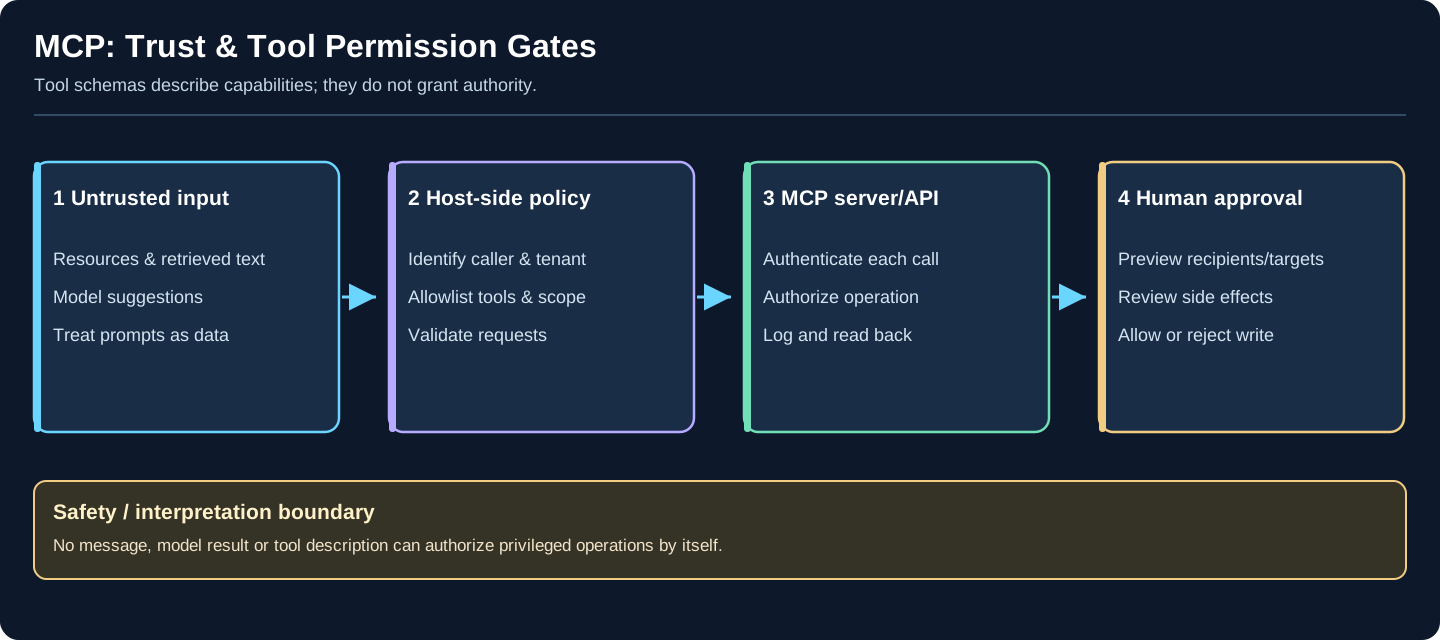
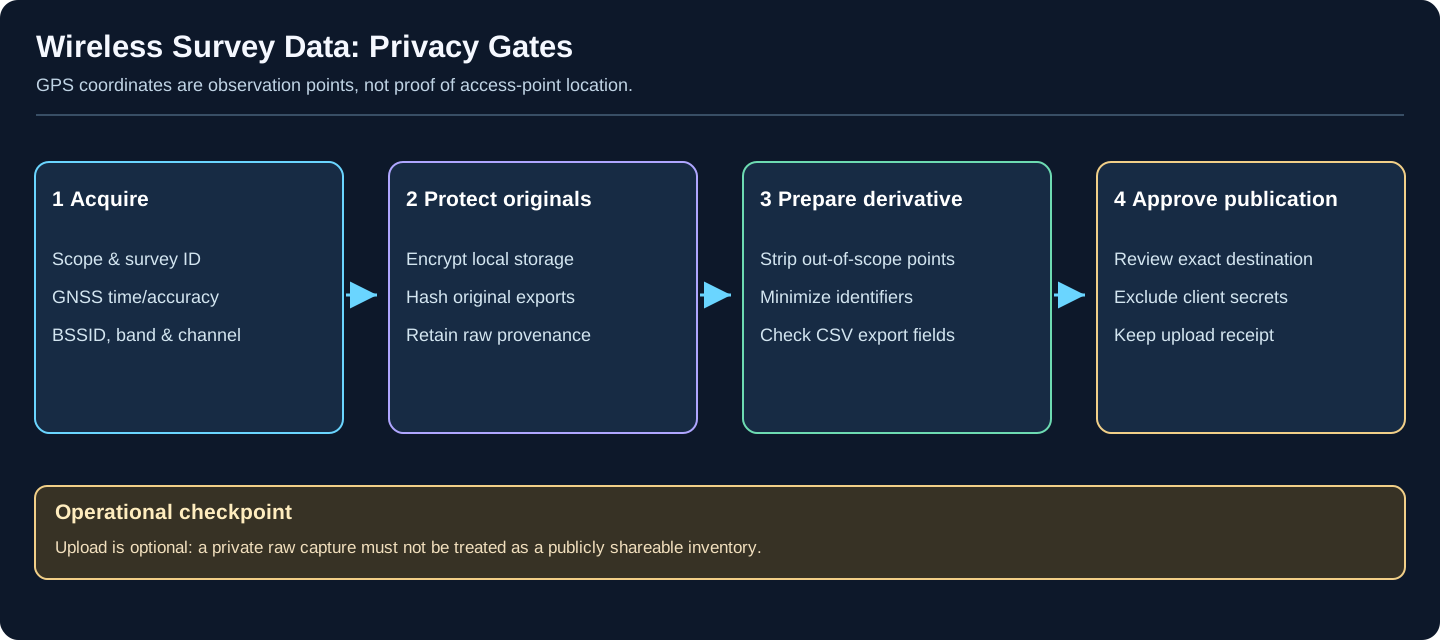
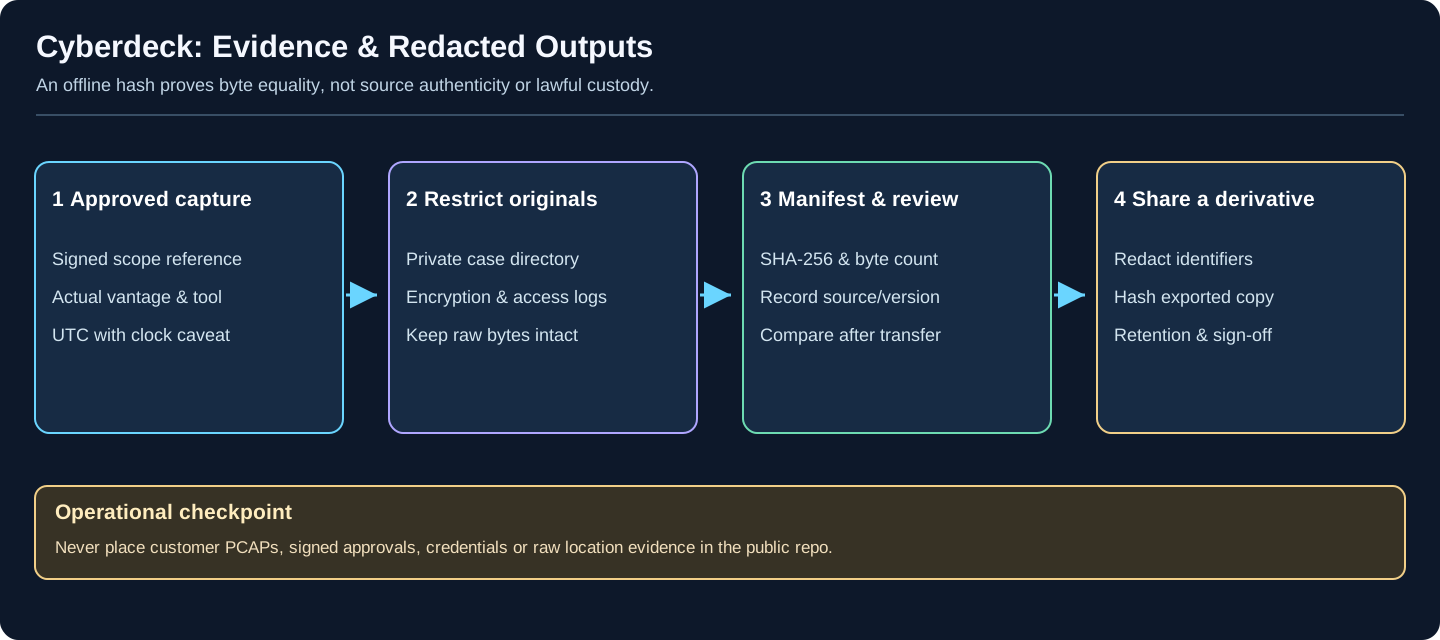
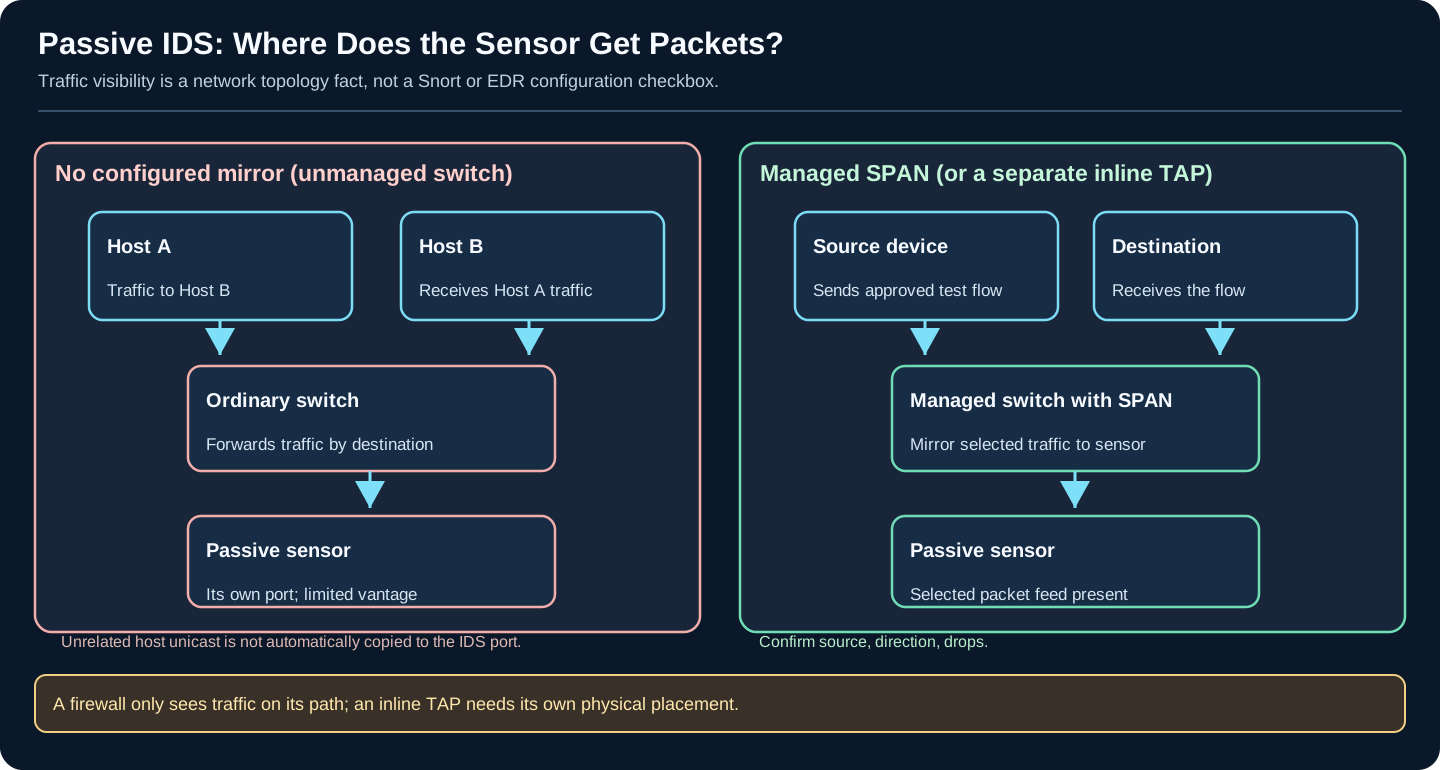
New original technical reference diagrams appear inside their canonical guides, with explicit boundaries between source-verified principles, device-specific configuration and untested physical behavior.
| Diagram | Embedded Guide | Visual Focus |
|---|---|---|
| Firmware Flashing Verification Gates | Firmware Web Flashers & Installers | Verify exact MCU/revision, approved release, installer route and post-boot feature checks |
| Device-First Firmware Compatibility | Device-First Firmware List | Target matrix, board image versus controller/FAP artifact, flash layout, stop on mismatch |
| Portable Cyberdeck Device Roles & Artifacts | Cyberdeck Portable Wireless Field Devices | Flipper external Marauder, standalone boards, alternate Plus2 firmware and separate Pineapple interface |
| Virtual Lab Network Isolation Paths | Complete Homelab Setup | Virtual internal versus host-only and routed networks; host access, egress and production-risk boundaries |
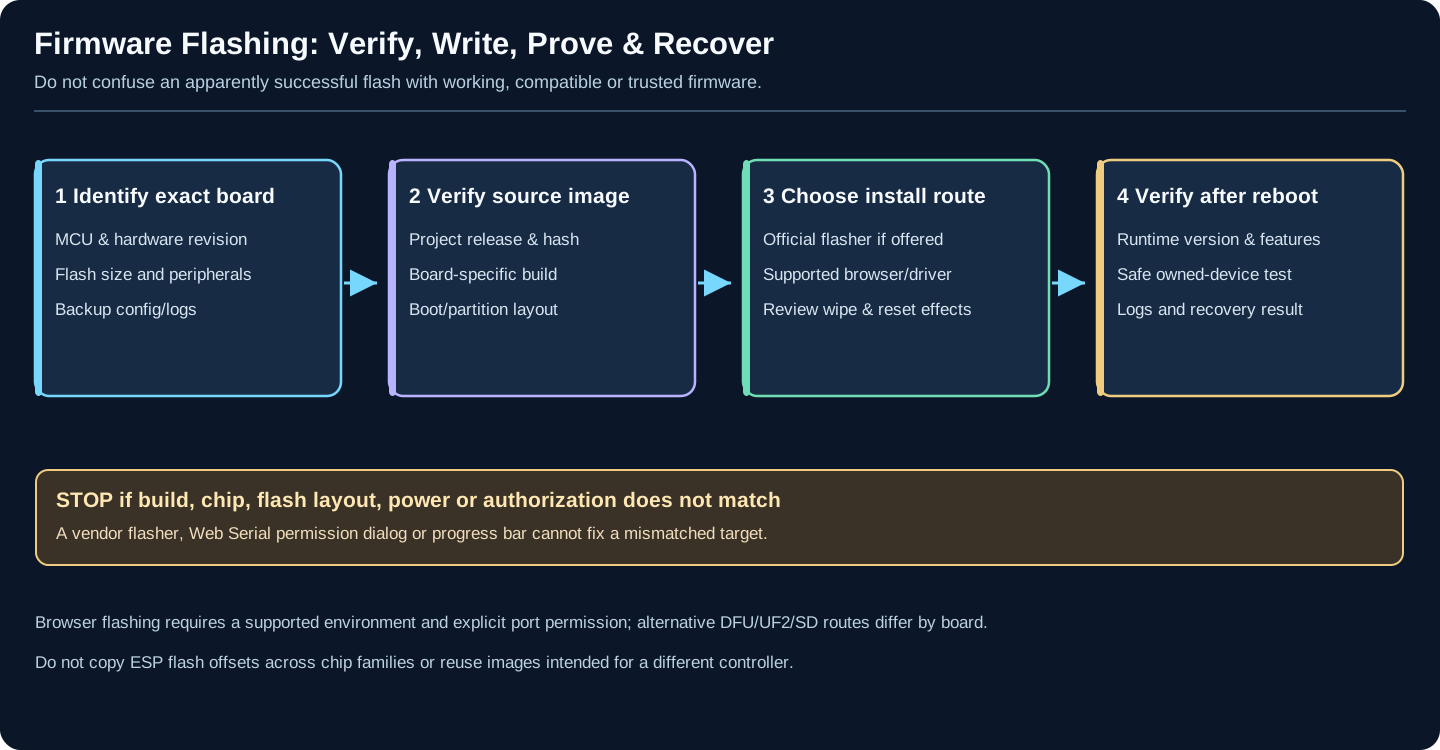
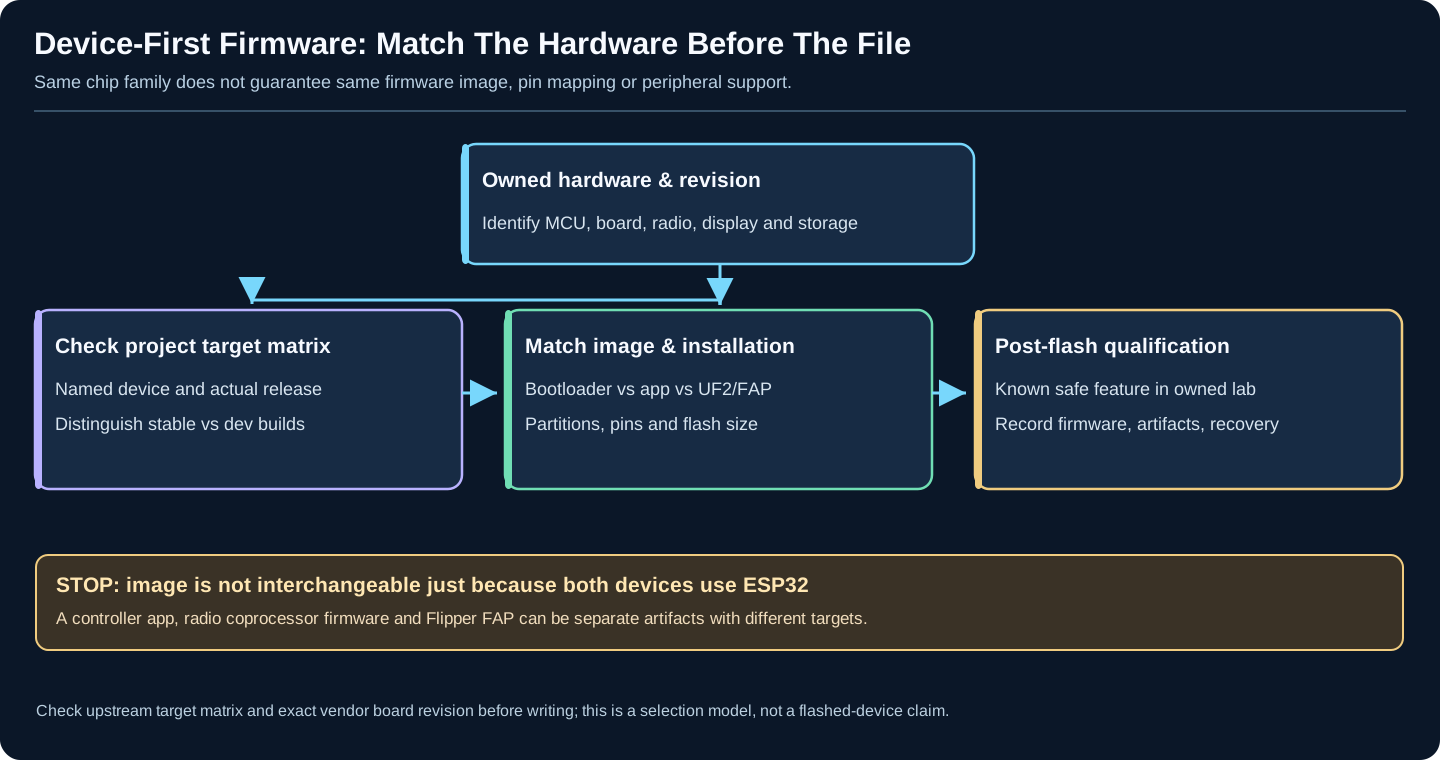
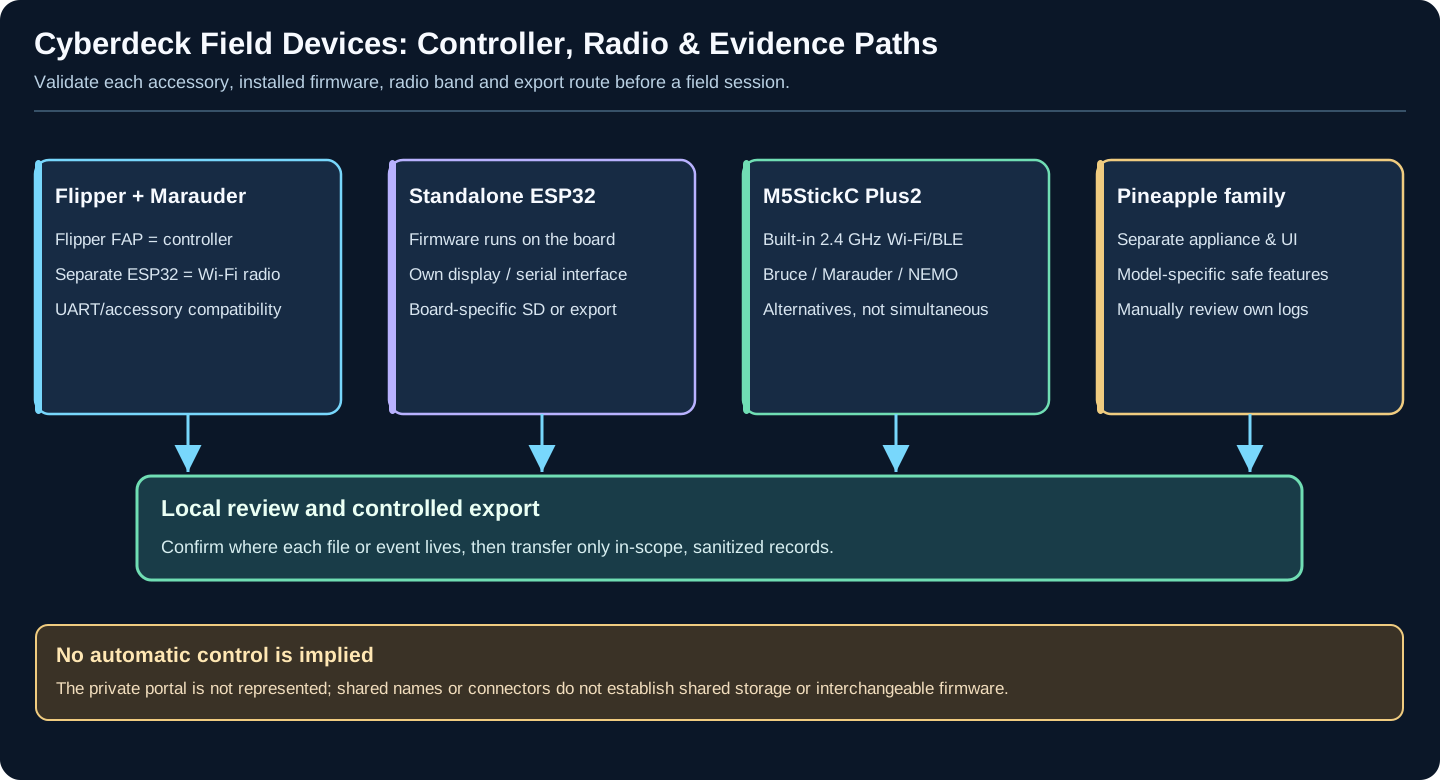
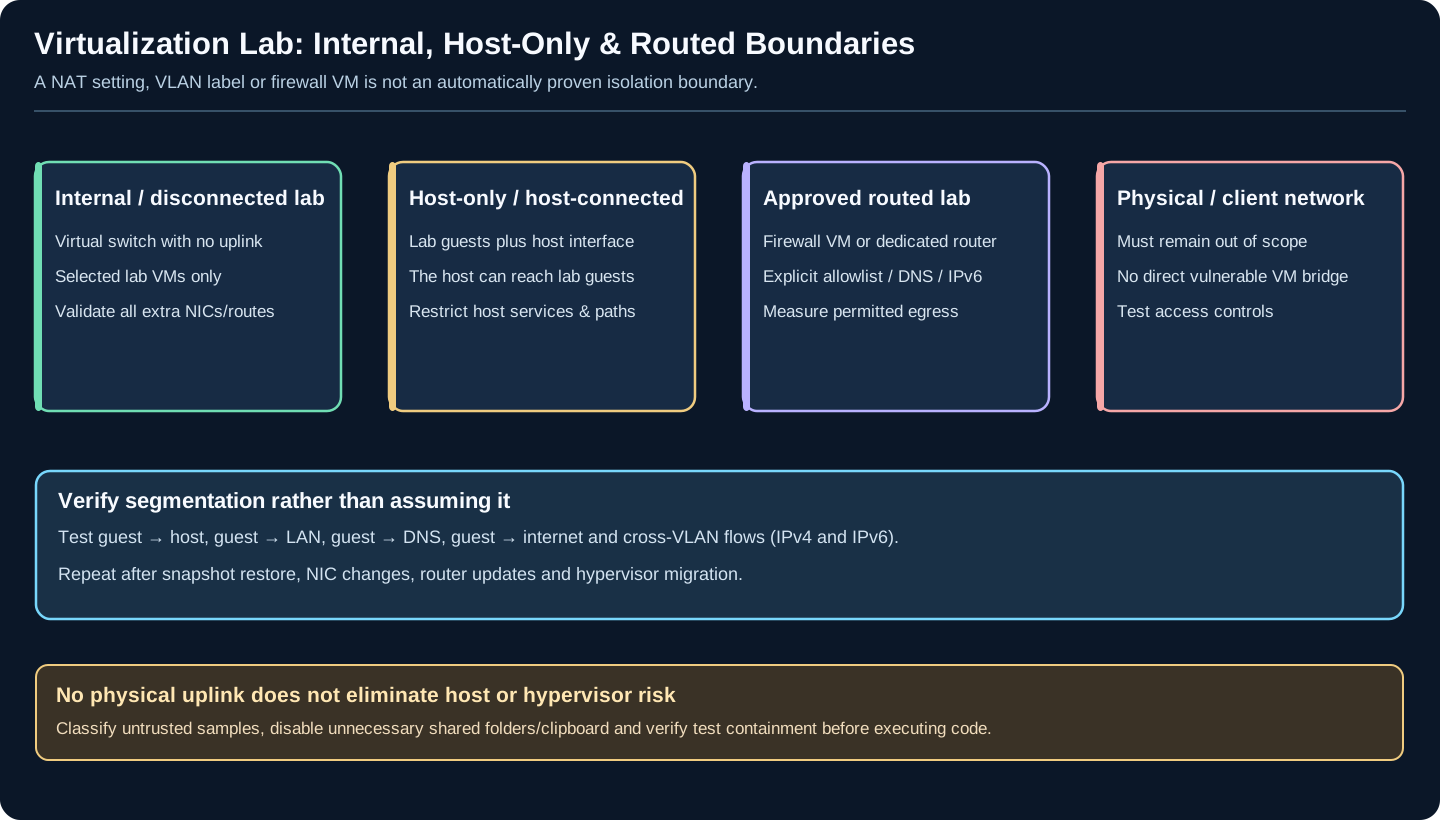
These original SVGs are embedded in the corresponding procedural chapter and distinguish planned actions from completed, observed or independently accepted outcomes.
| Diagram | Embedded Guide | Technical Boundary |
|---|---|---|
| AI Notes, Hooks & Evidence | Notes, Memory, Hooks & Automation | Reference context cannot execute; host events require permissions and independent result checks |
| AI Milestone Independent Acceptance | Milestones & Acceptance Criteria | Tasks and commits are not accepted outcomes without real test evidence and review |
| OSINT Fraud Case Source Confidence | OSINT Investigation Procedures | Registration is not geolocation; search output is not identity; reposts require provenance |
| Wardriving Field Quality & Acceptance | Wardriving Field Procedure | Calibration, passive behavior, GPS evidence, explicit STOP and per-case acceptance |
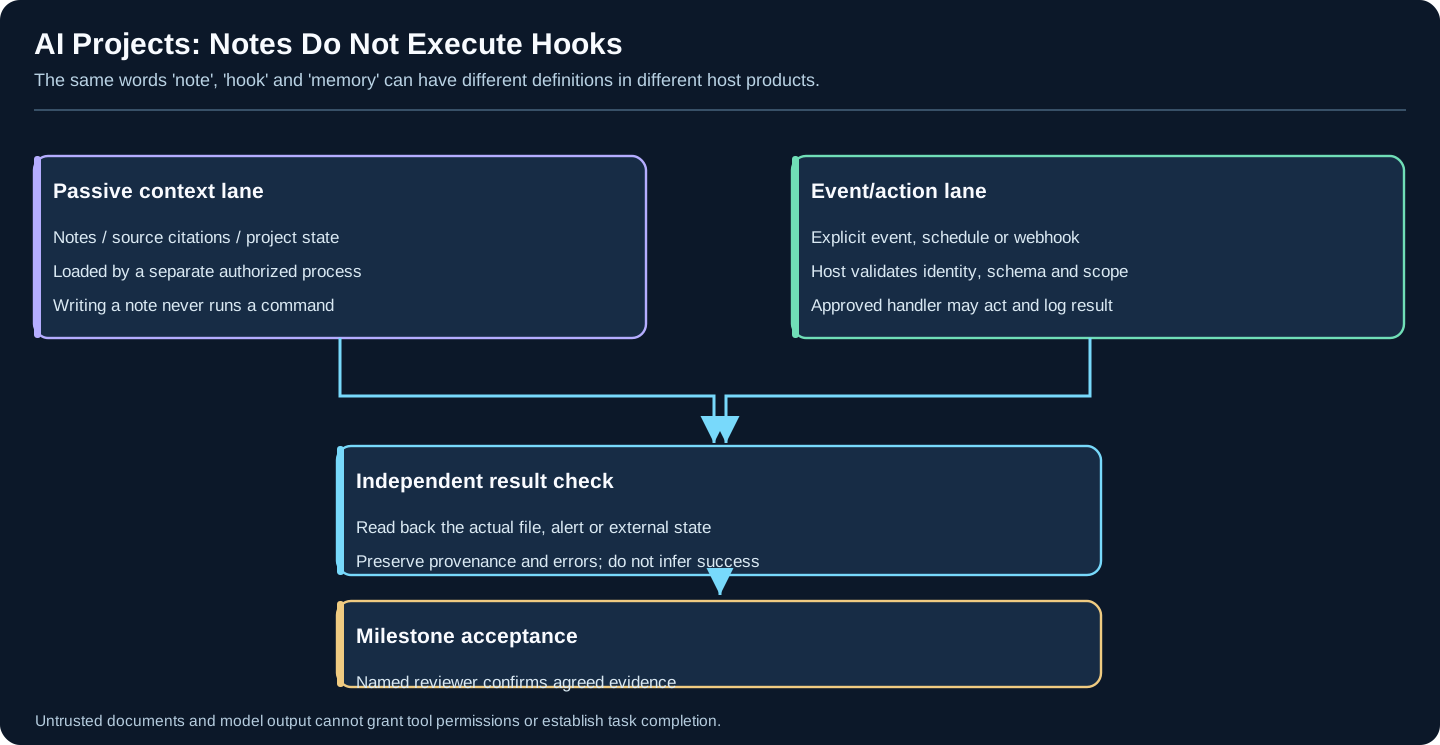
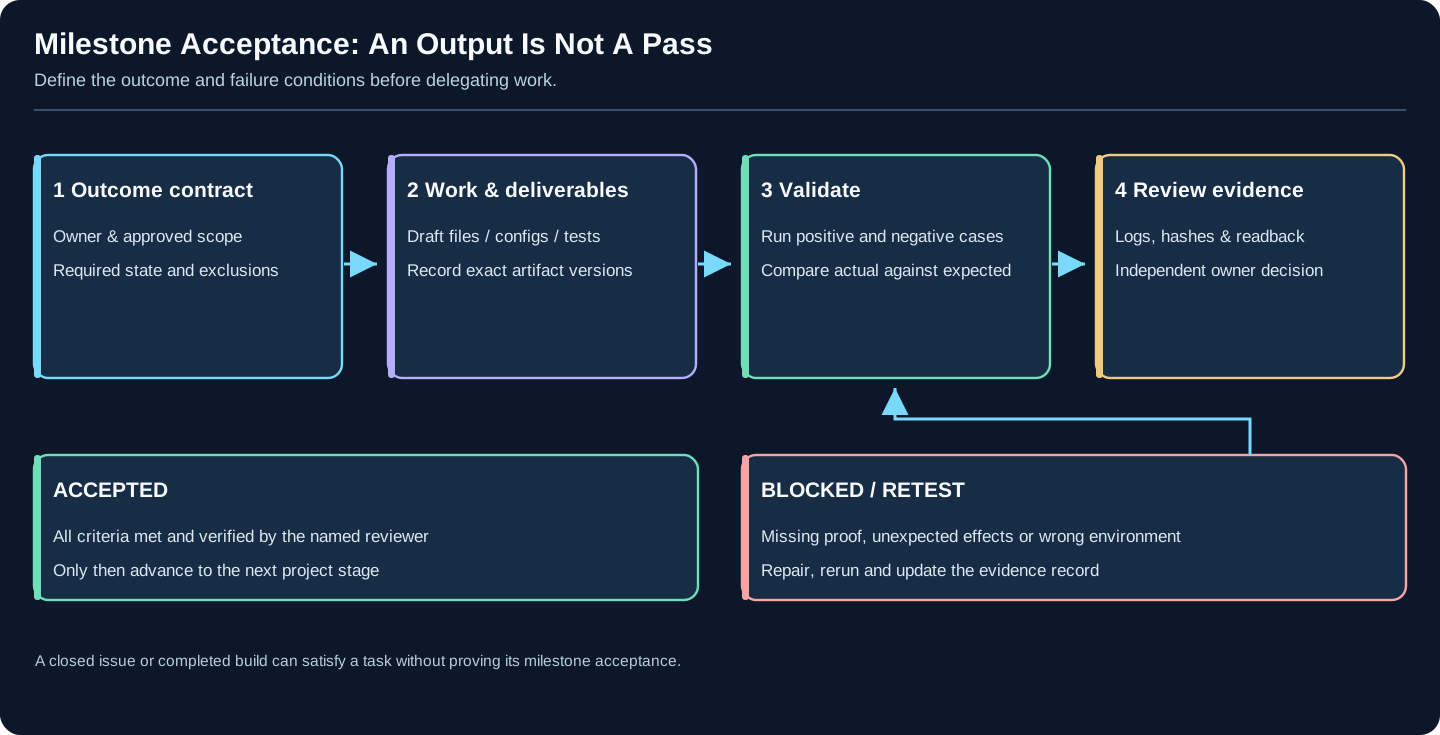
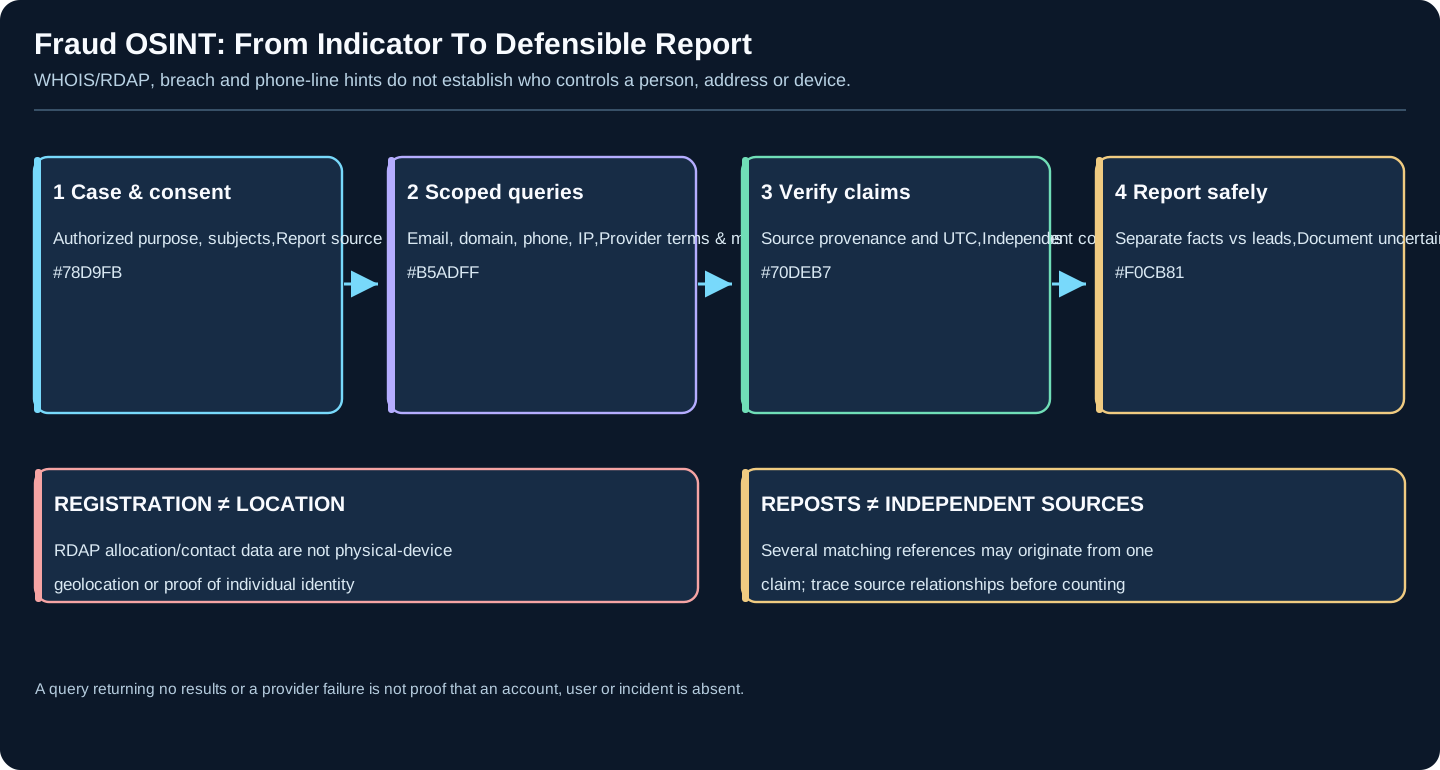
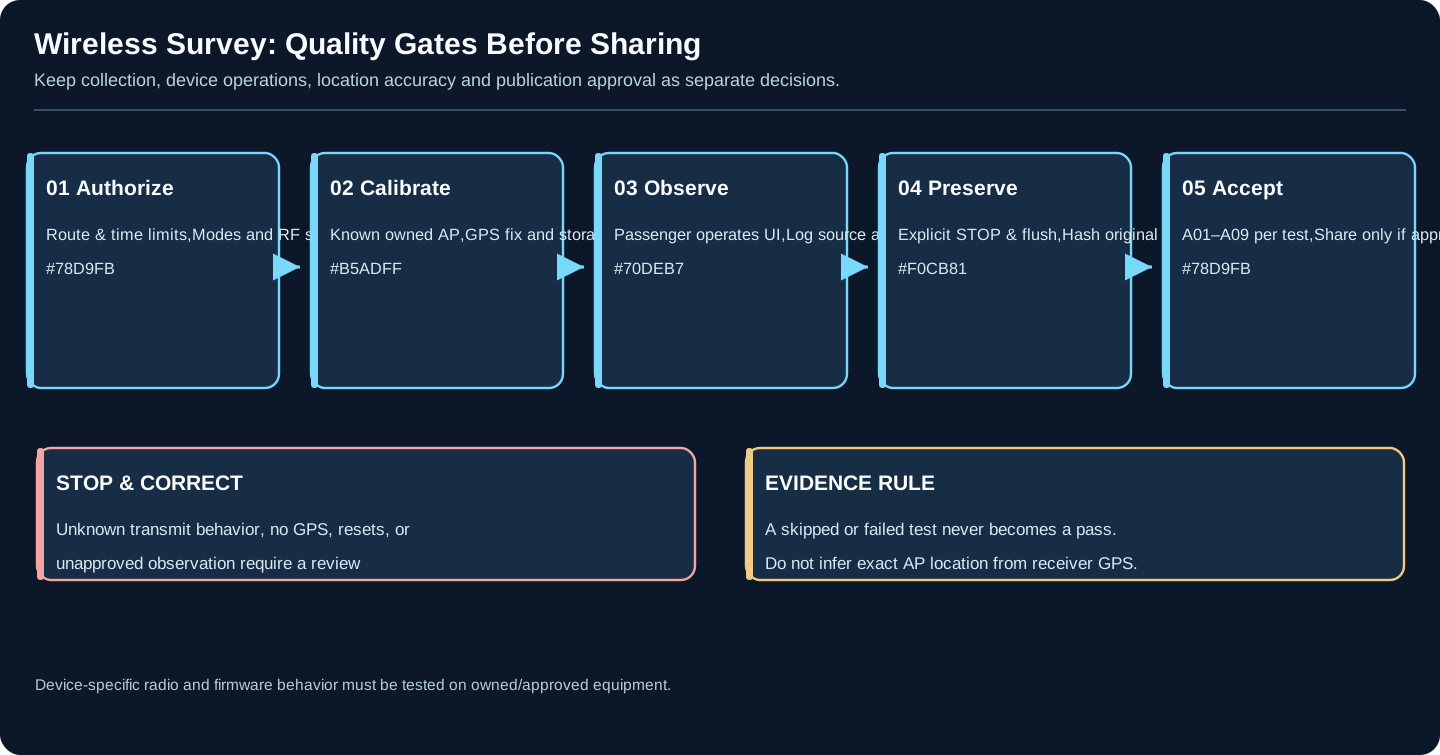
| Diagram | Embedded Guide | Source-Checked Scope |
|---|---|---|
| Graylog Ingest, Search & Metadata Roles | Graylog SIEM Guide | Graylog inputs/processing, recommended Data Node or compatible self-managed backend and MongoDB metadata |
| Live Response Volatility & Evidence Gates | Live Response Collection | Case-dependent volatility, operational safety, original preservation and independent analysis |
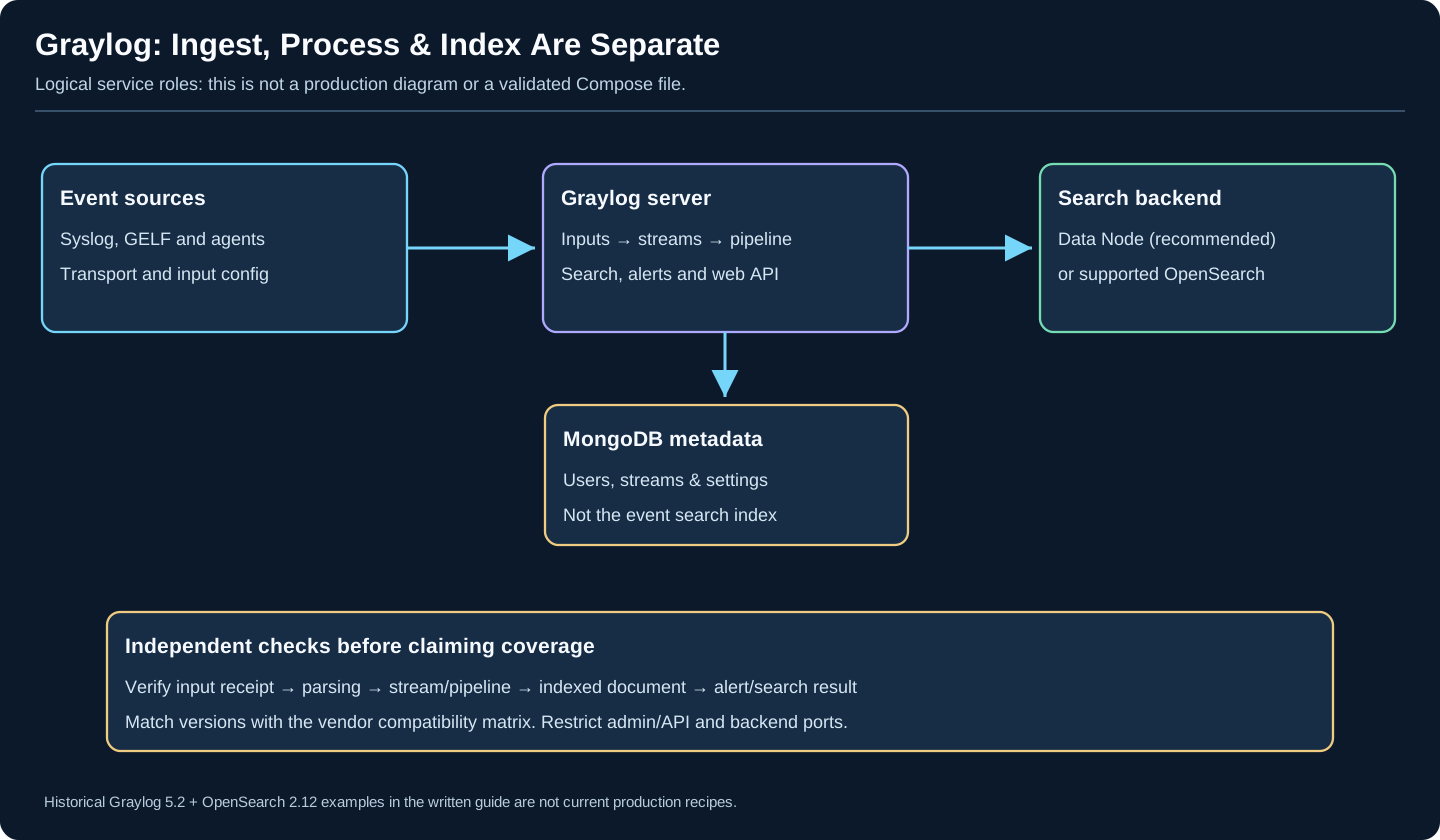
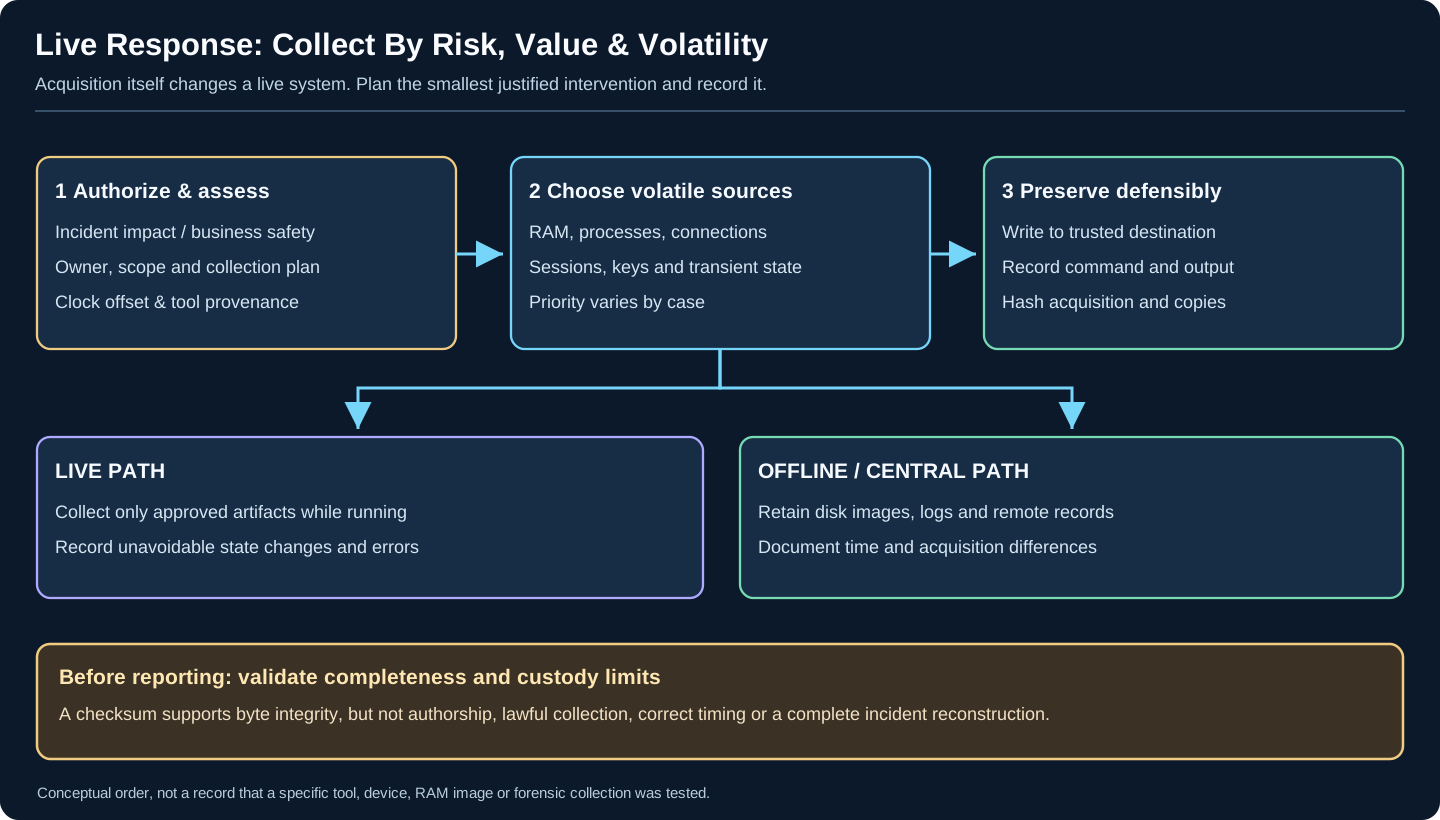
Original, accessible SVGs for workflow comprehension. They are conceptual only: none certify a specific deployment, vendor rule, collection interface, or completed lab exercise.
| Diagram | Embedded Guide | Scope |
|---|---|---|
| Purple Team emulation & detection loop | Detection validation playbook and detailed playbook | Scope, approval, safe canary, telemetry, alert, tune/retest |
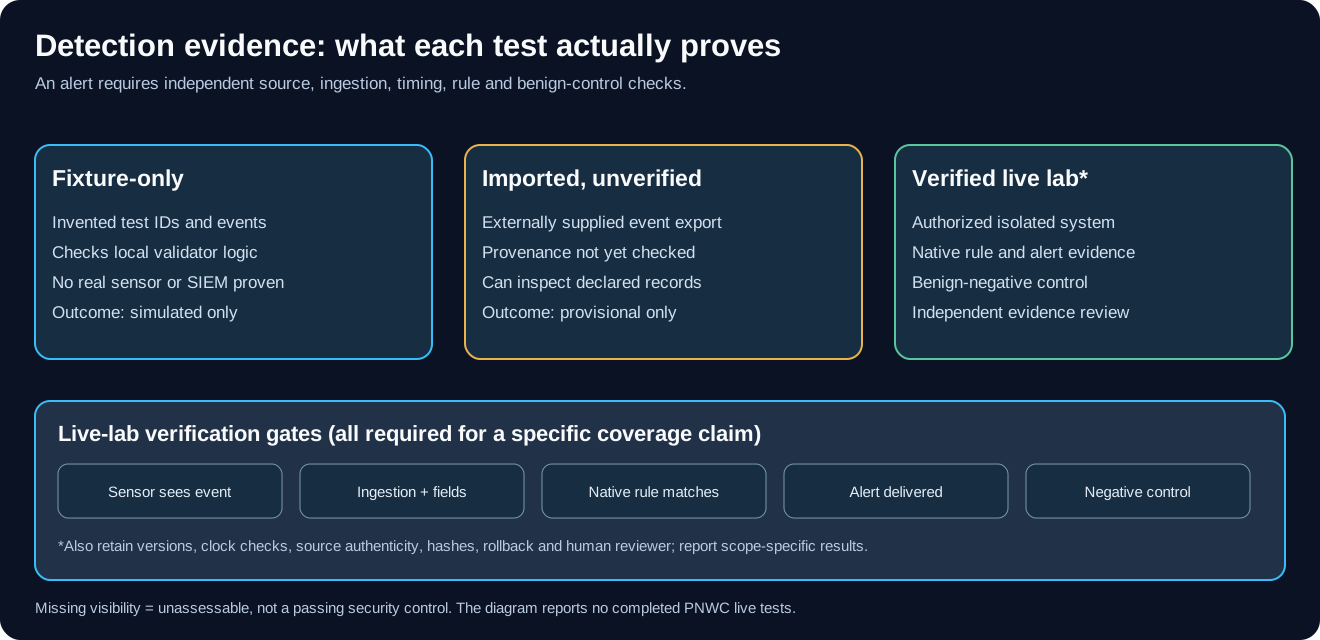
| Detection evidence verification gates | SIEM detection content and offline canary validator | Fixture vs imported vs verified lab evidence |
| Cyberdeck policy zones | Public Cyberdeck architecture | Conceptual router/zone boundaries, field RF, evidence storage |
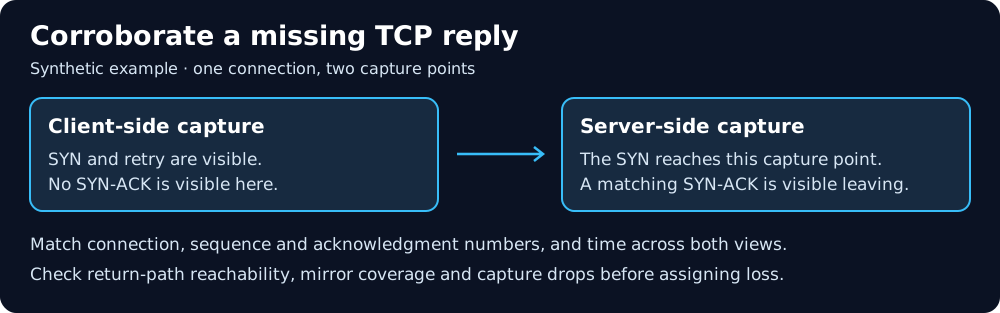
| Wireshark two-point TCP reply check | Wireshark master filter list | Corroborates missing-handshake evidence across capture points |
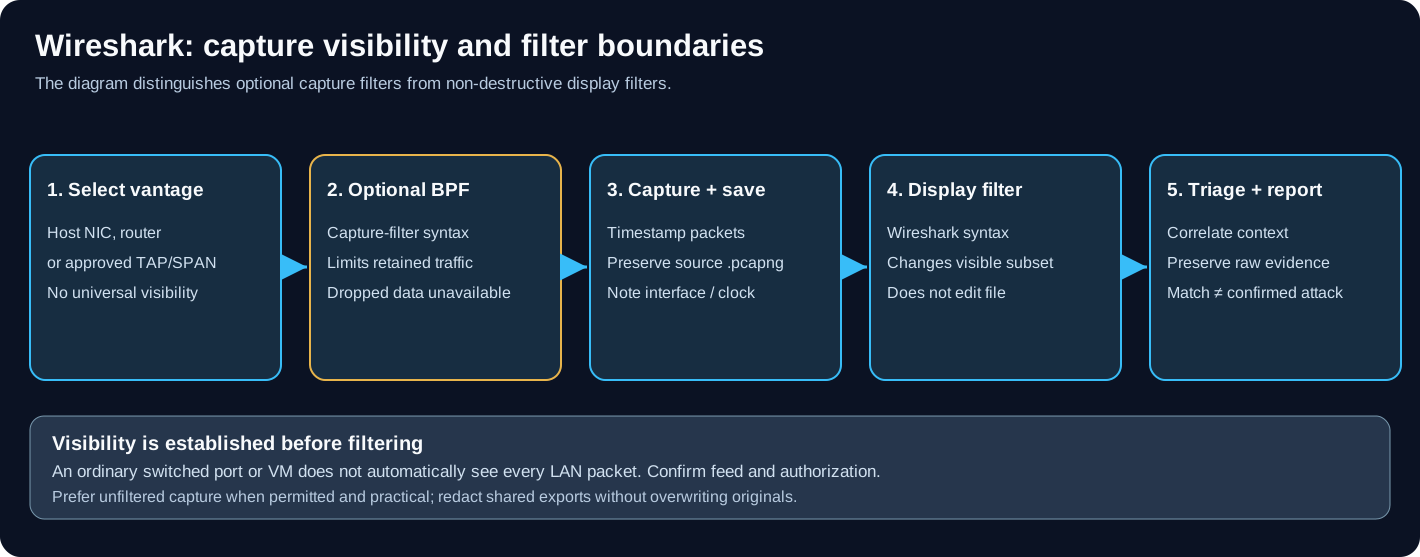
| Wireshark capture & display boundaries | Advanced Wireshark reference | Vantage point, optional BPF, PCAP, display filter, analyst validation |
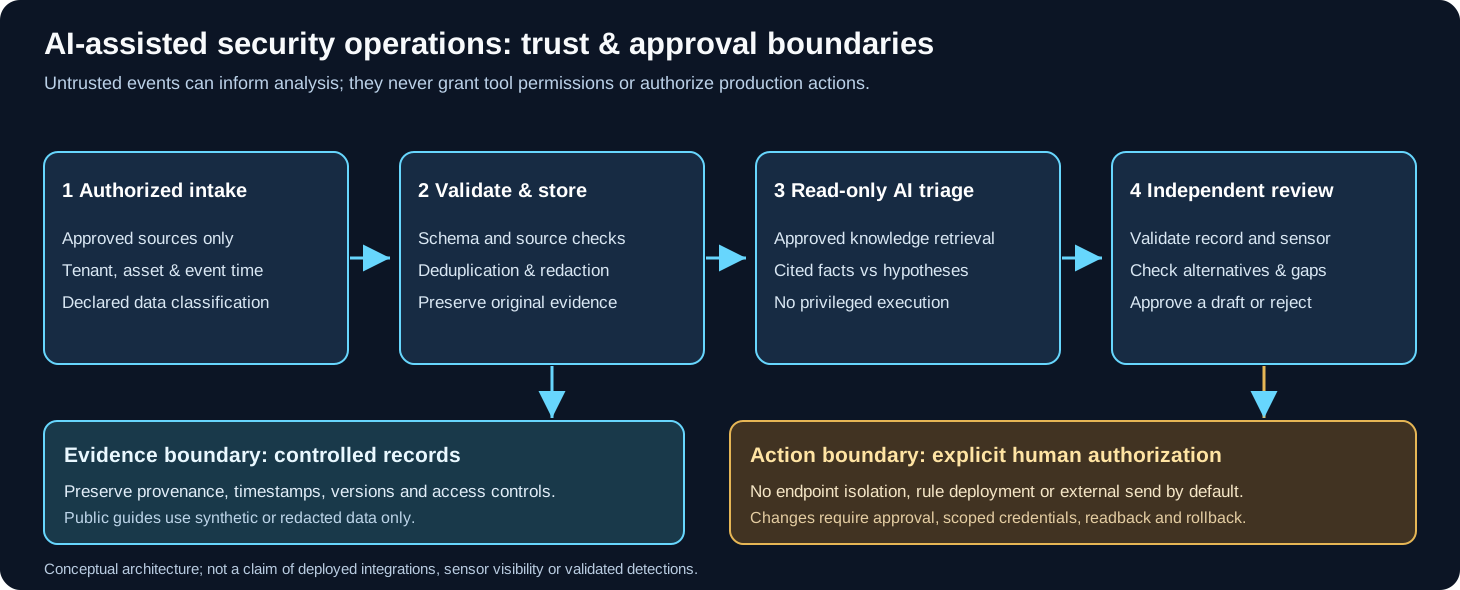
| AI-SOC trust & approval boundaries | AI-augmented security operations | Authenticated intake, schema/evidence boundary, read-only AI, independent review and privileged-action approval |
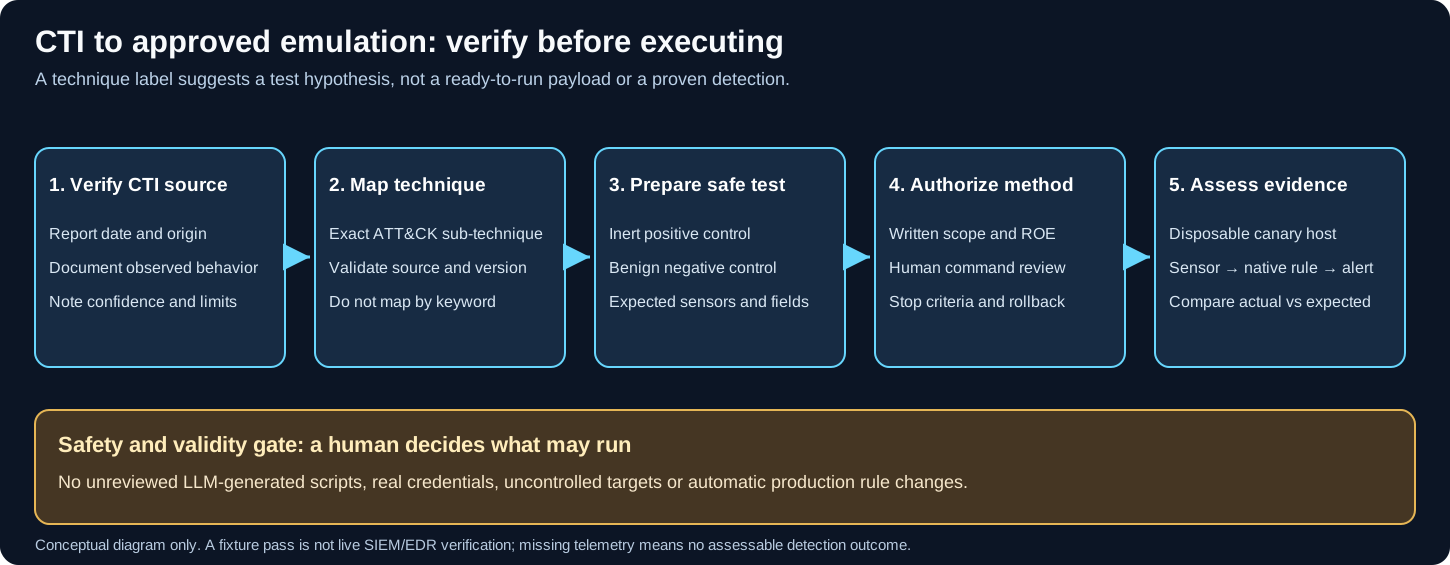
| CTI-to-approved-emulation gates | Detailed Purple Team playbook | Independently verify CTI, map ATT&CK, prepare benign controls, obtain human authorization, assess observed evidence |
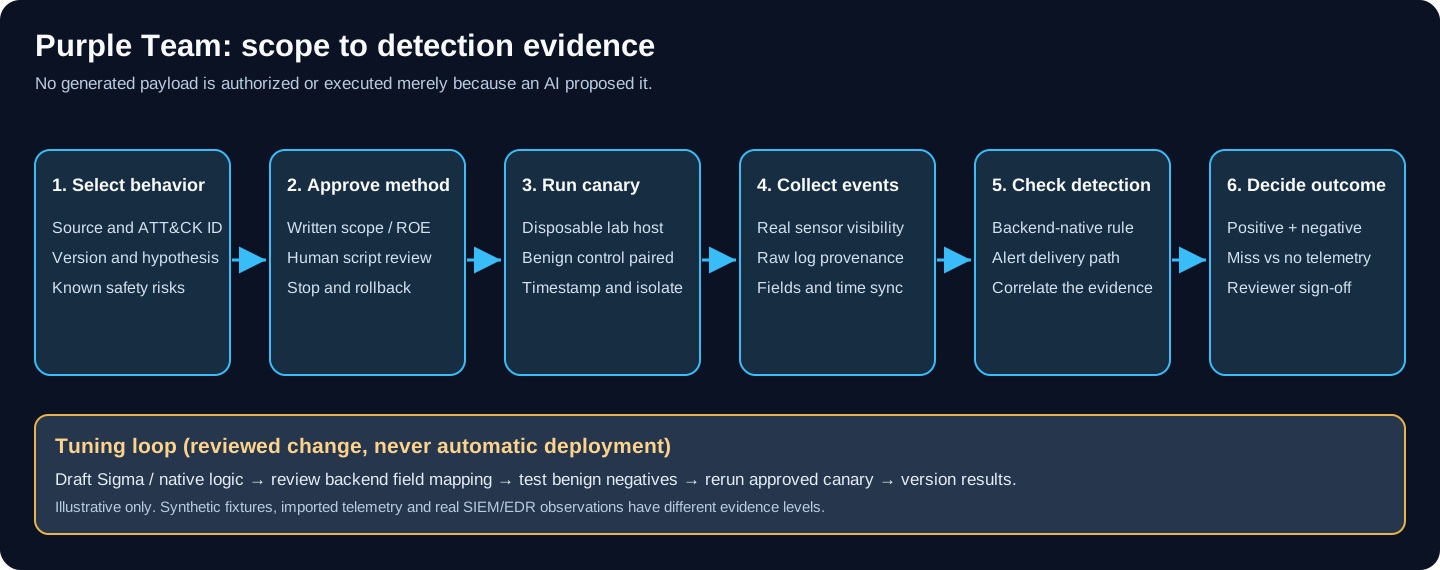
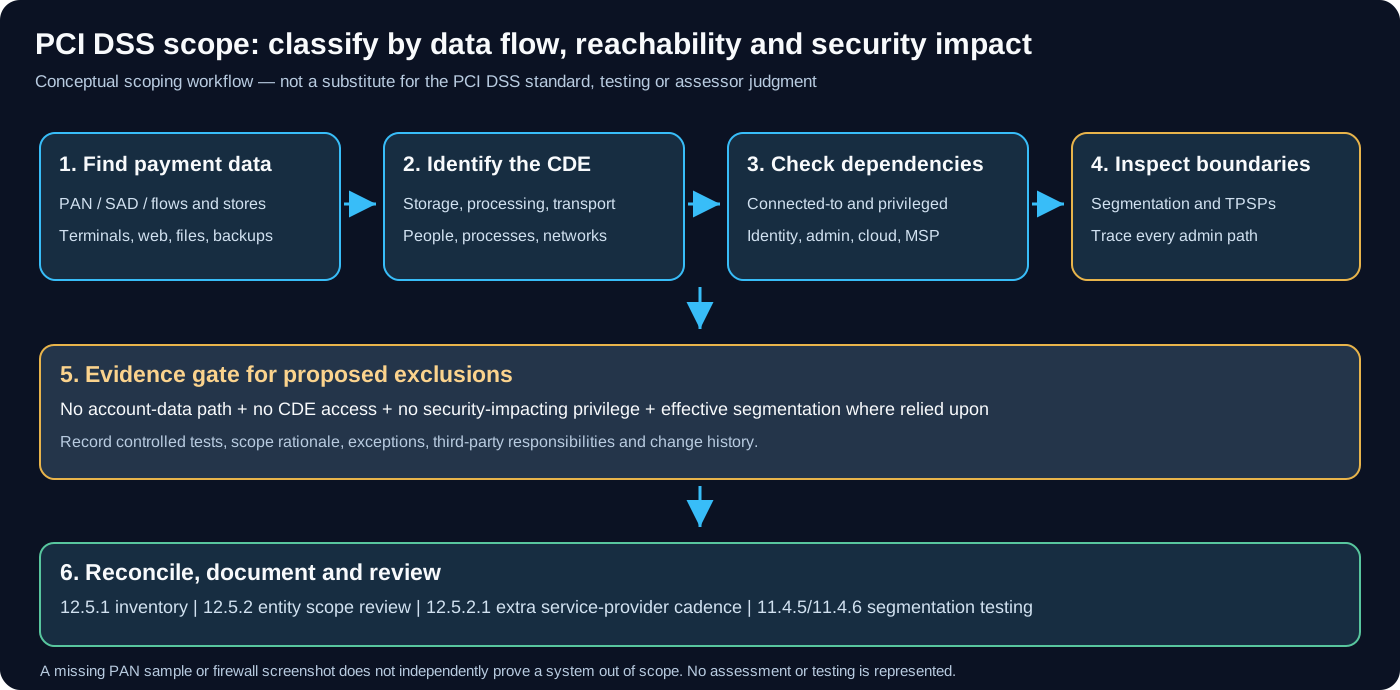
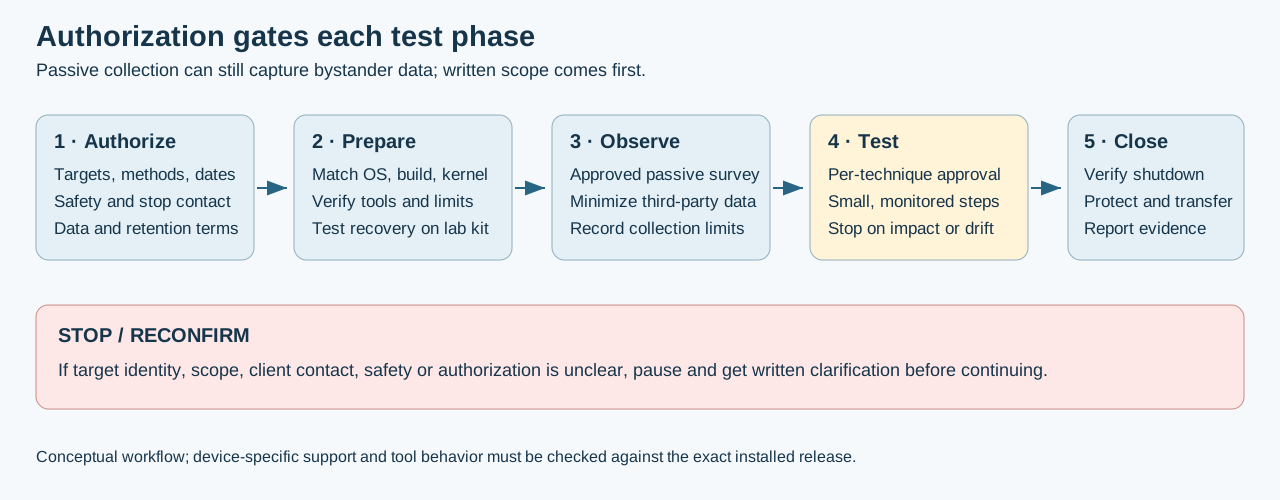
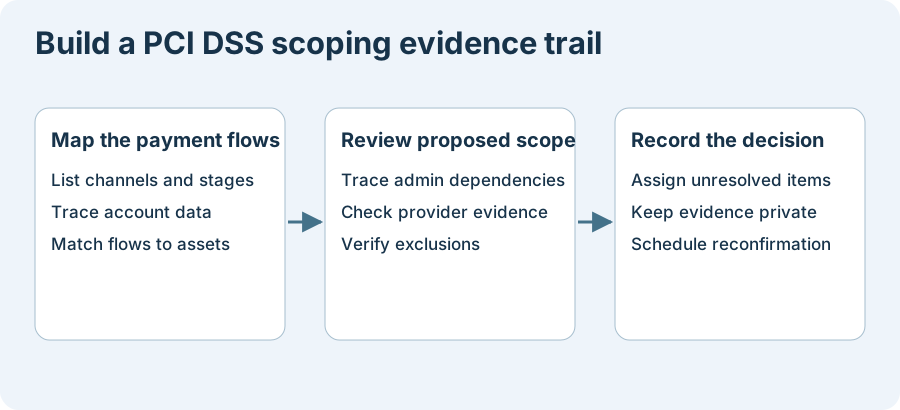
Original conceptual scope-classification workflow; this diagram does not certify any real CDE or confirm that a service is outside scope.
| Diagram | Embedded guide |
|---|---|
| PCI DSS scope & evidence gates | PCI DSS scoping field guide |
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| security key recovery paths | Guide |
| security key protocol boundaries | Guide |
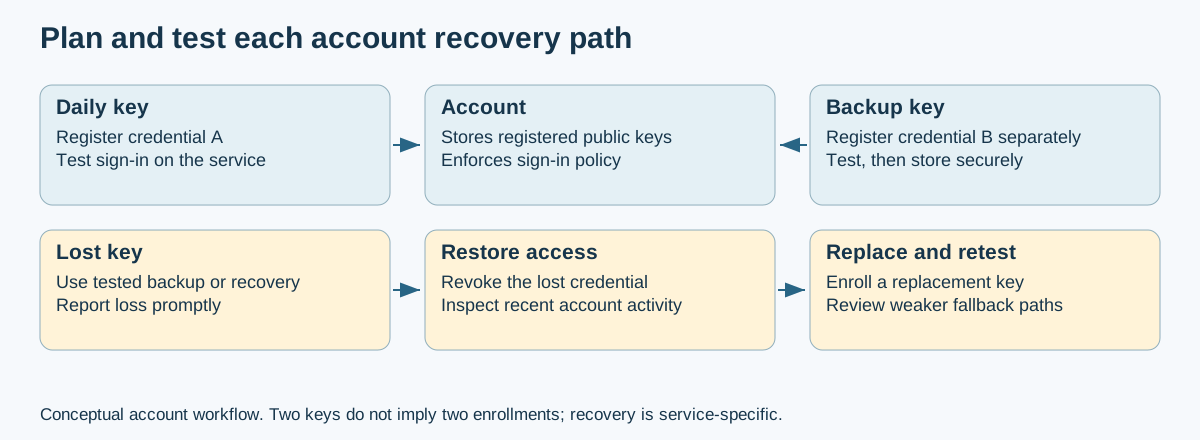
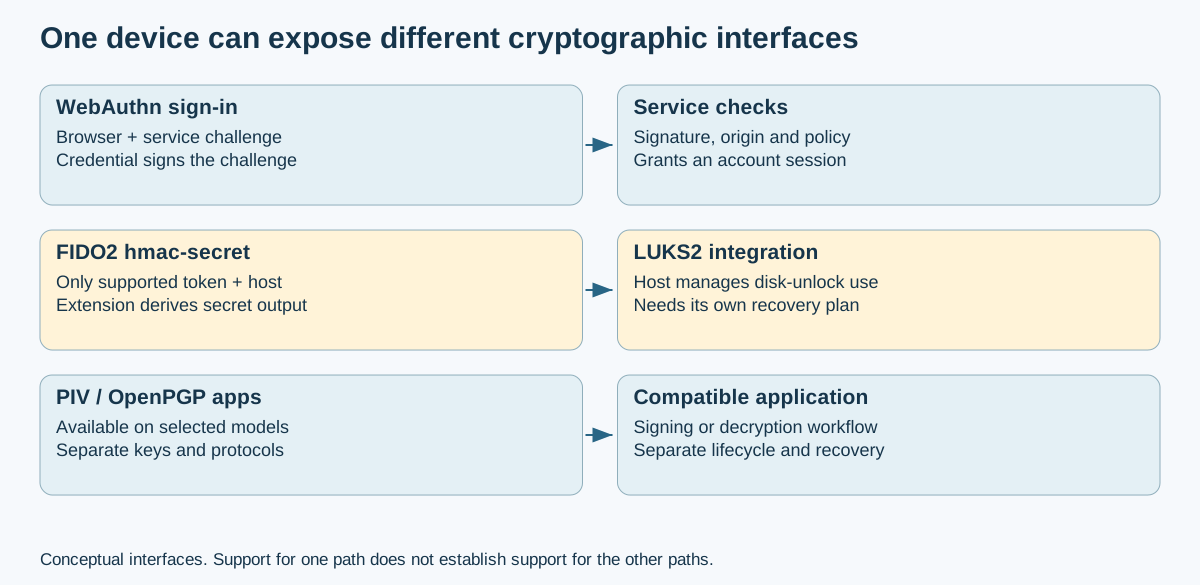
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| encrypted storage status questions | Guide |
| encrypted storage recovery components | Guide |
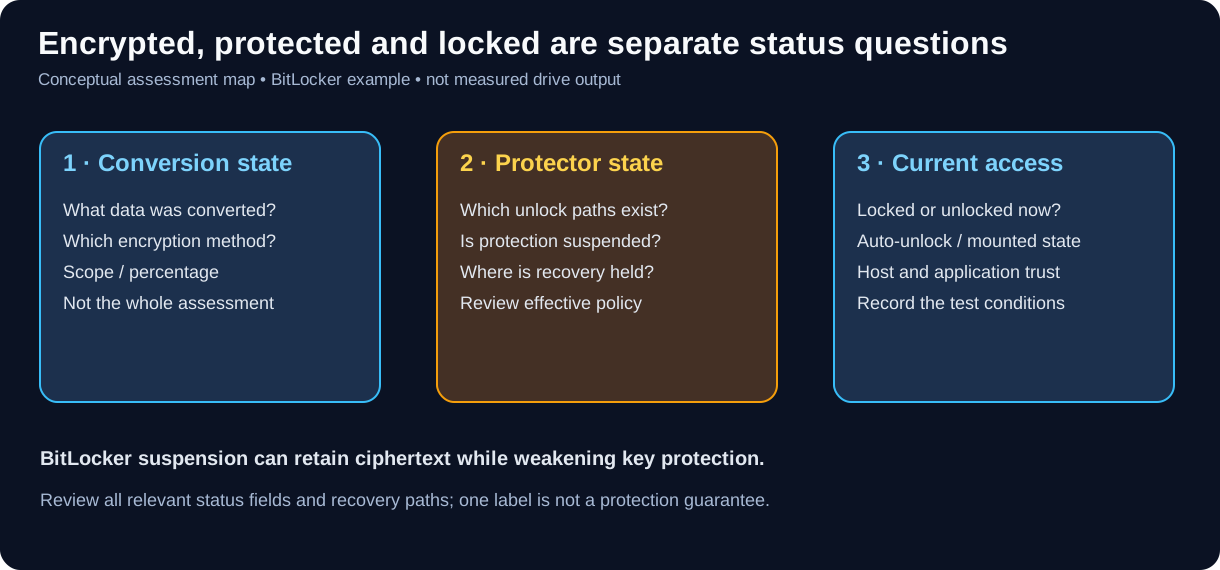
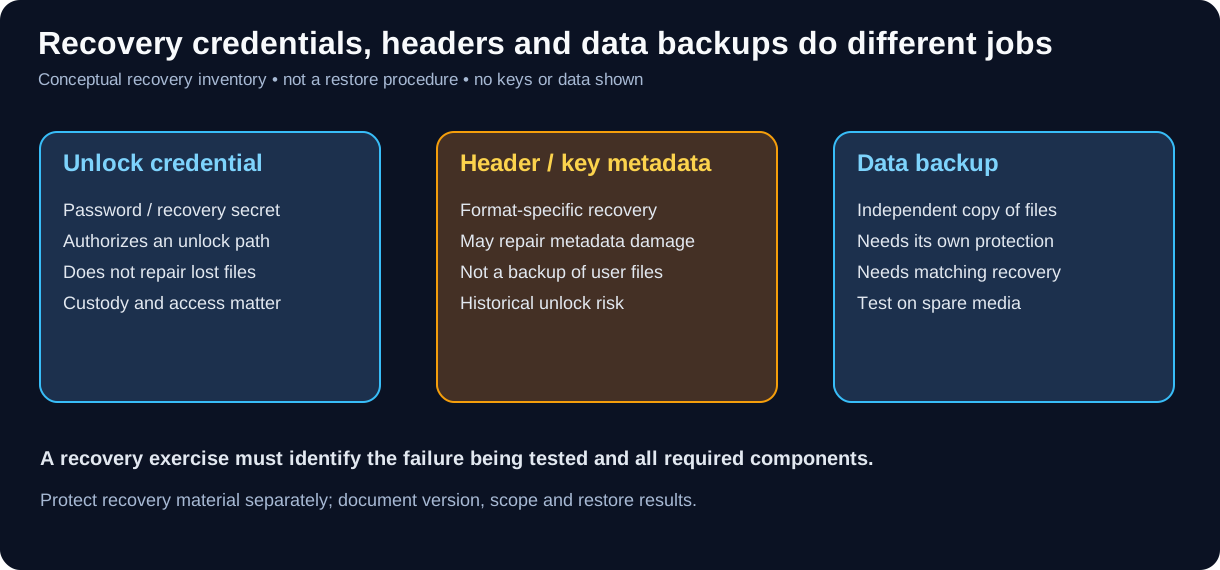
Original conceptual figures; source links and evidence limits appear in the guide captions.
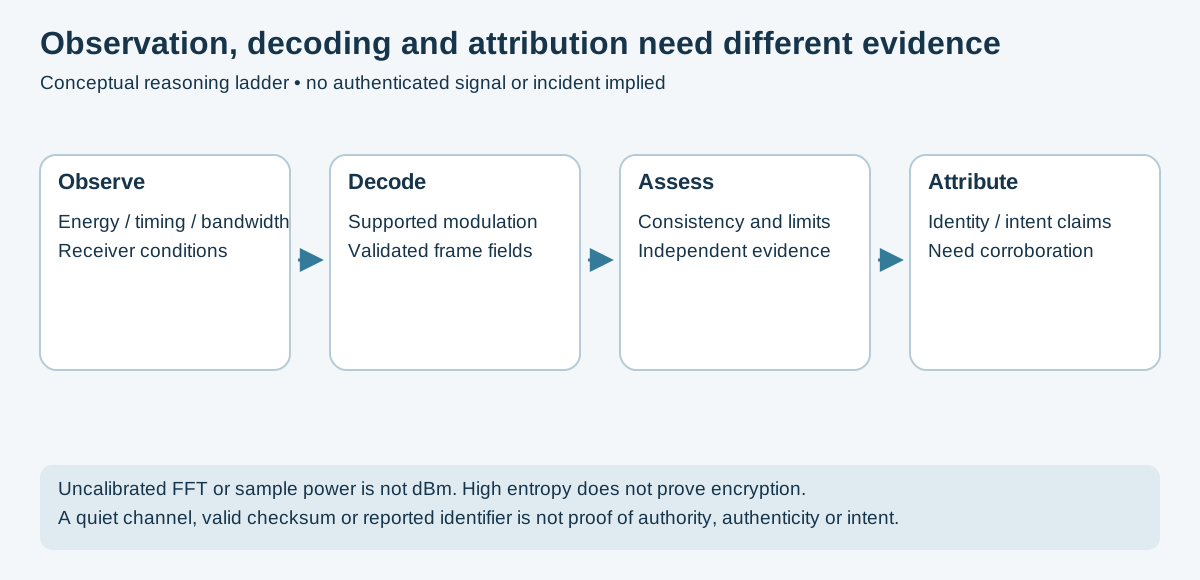
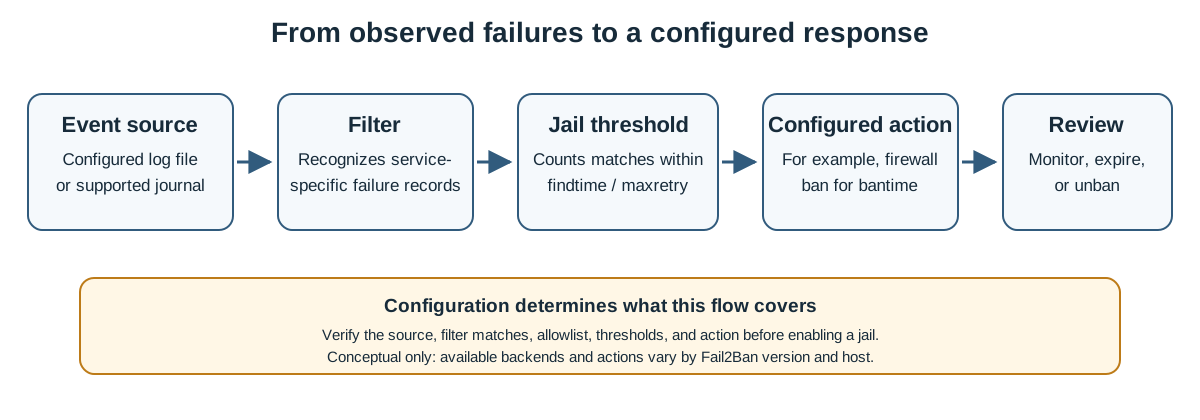
Original conceptual flow; actual coverage depends on the configured source, filter, jail thresholds, and action.
| Diagram | Embedded guide |
|---|---|
| Fail2Ban event-to-action flow | Fail2Ban guide |
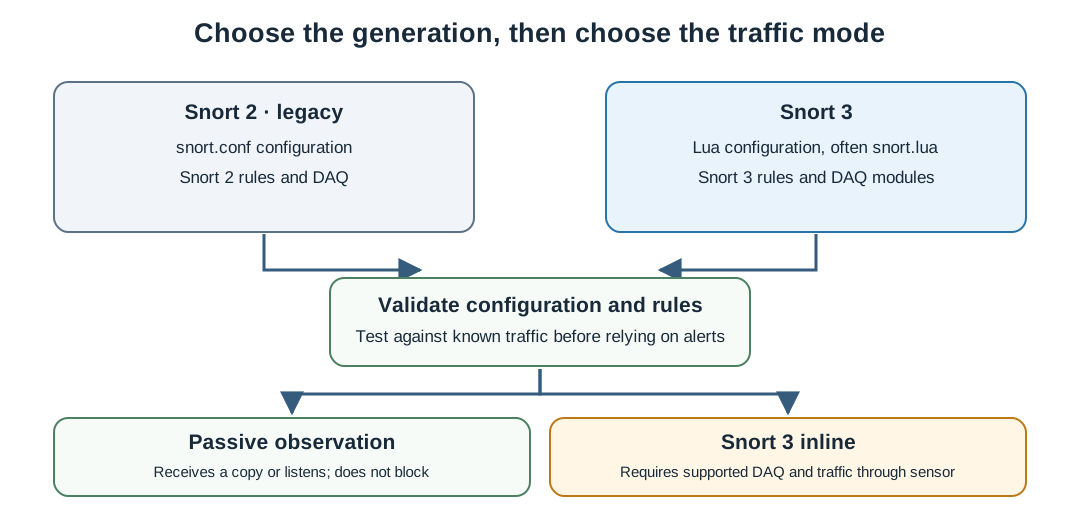
Original conceptual map separating Snort 2 and Snort 3 configuration, then passive and inline traffic modes.
| Diagram | Embedded guide |
|---|---|
| Snort generation and traffic modes | Snort guide |
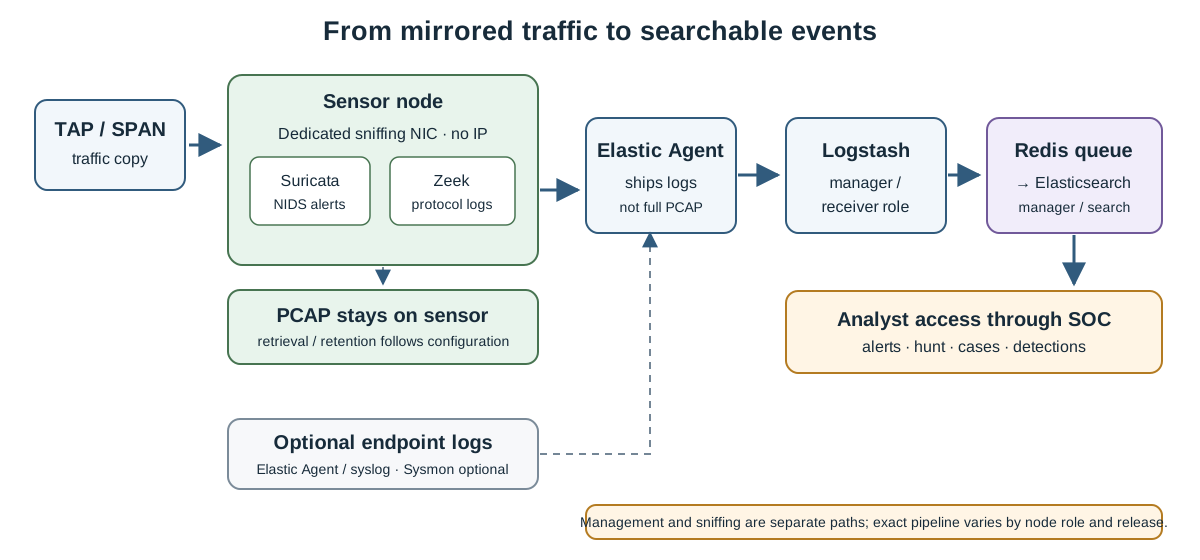
Original conceptual topology separating sniffing, sensor processing, event transport, search, packet capture, and analyst access.
| Diagram | Embedded guide |
|---|---|
| Security Onion sensor-to-search data flow | Security Onion guide |
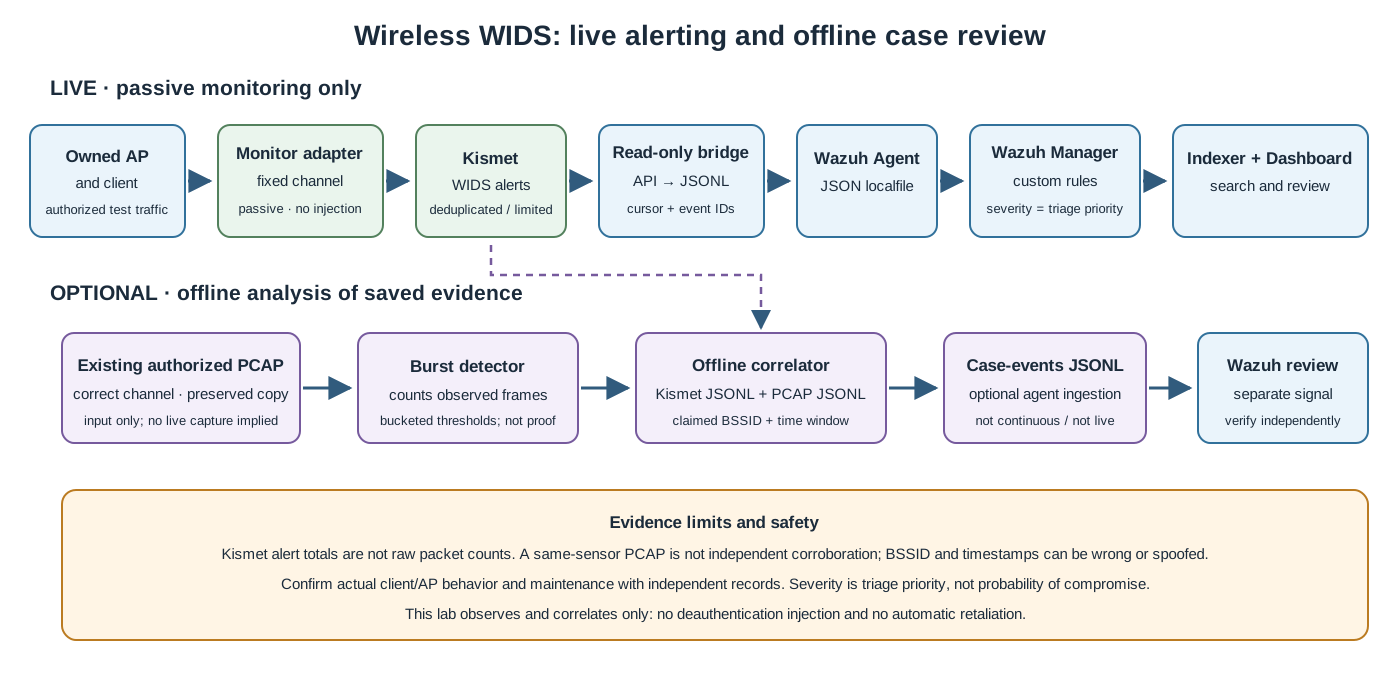
Original conceptual figure separating passive live alerting from optional offline PCAP analysis and case correlation.
| Diagram | Embedded guide |
|---|---|
| Kismet and Wazuh live and offline flows | Wireless intrusion detection lab |
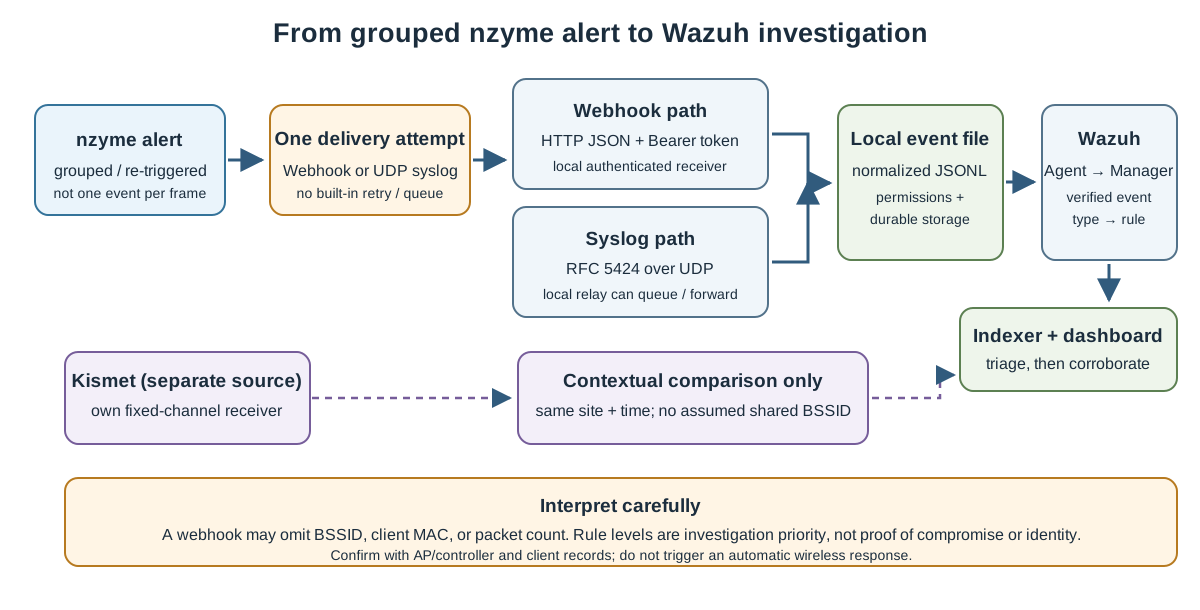
Original conceptual diagram separating one-shot nzyme actions, local durable collection, Wazuh rule mapping, and optional contextual Kismet comparison.
| Diagram | Embedded guide |
|---|---|
| nzyme event ingestion into Wazuh | nzyme + Wazuh integration |
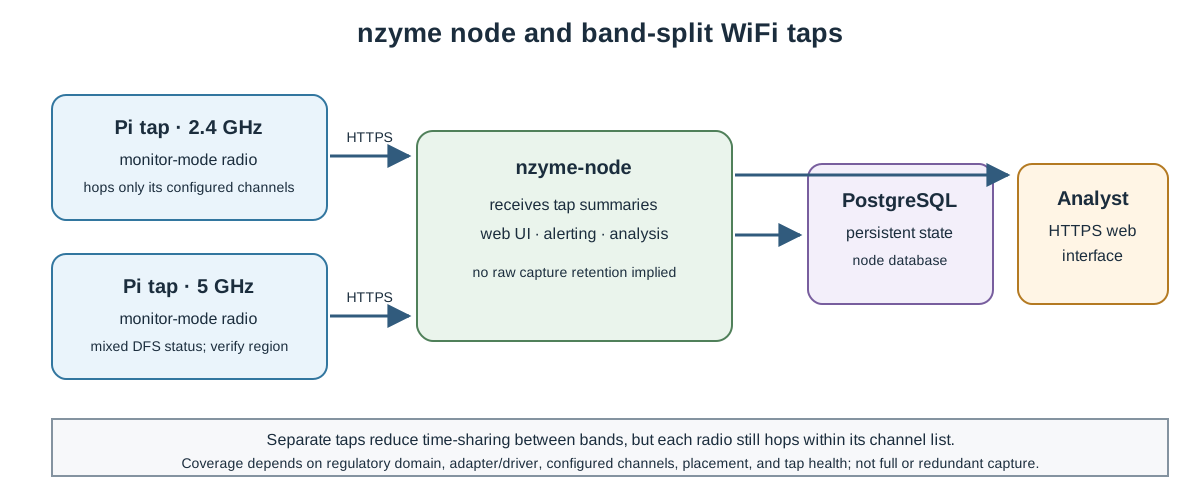
Original conceptual topology for two band-split WiFi taps sending summarized data to a node and PostgreSQL; channel hopping and regional channel limits remain.
| Diagram | Embedded guide |
|---|---|
| nzyme band-split tap architecture | DIY WiFi intrusion detection with nzyme |
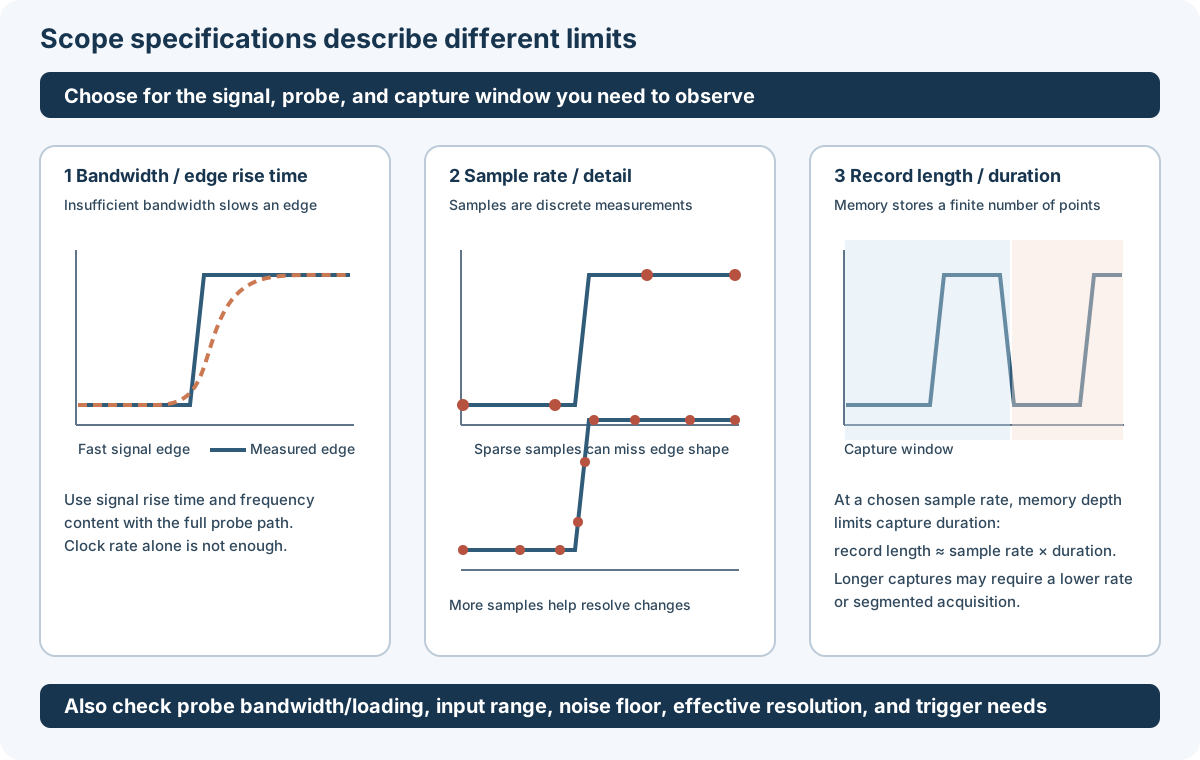
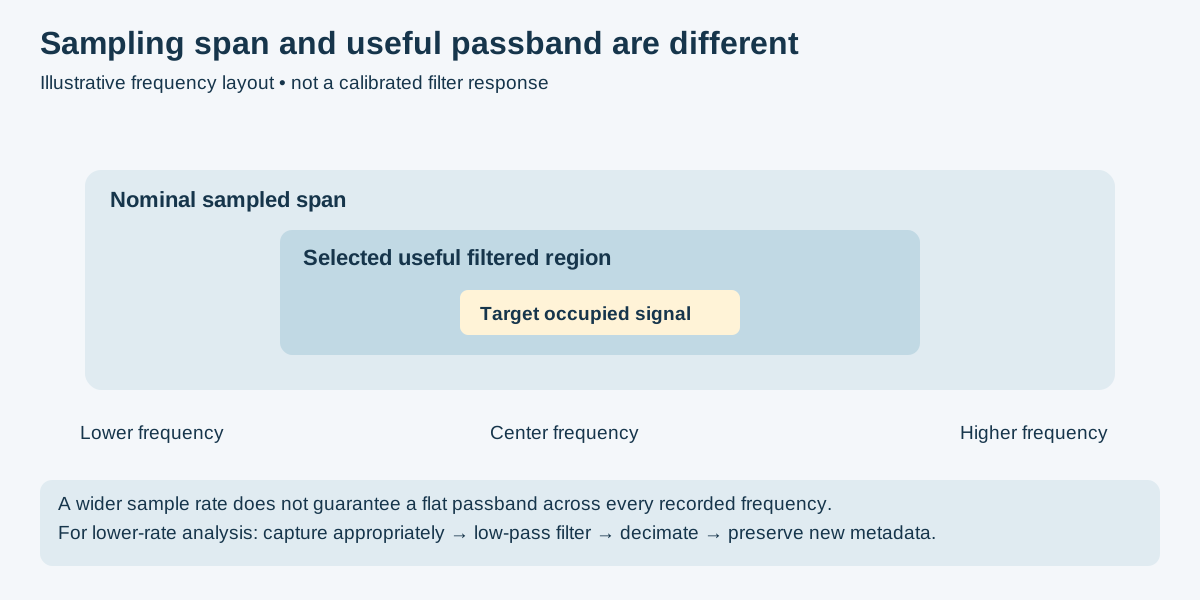
Original conceptual comparison of analog bandwidth, sample rate, record length, and probe limits. It does not recommend a specific scope model or describe a tested setup.
| Diagram | Embedded guide |
|---|---|
| Oscilloscope bandwidth, sampling, and record length | Electrical Fundamentals — Oscilloscope Selection |
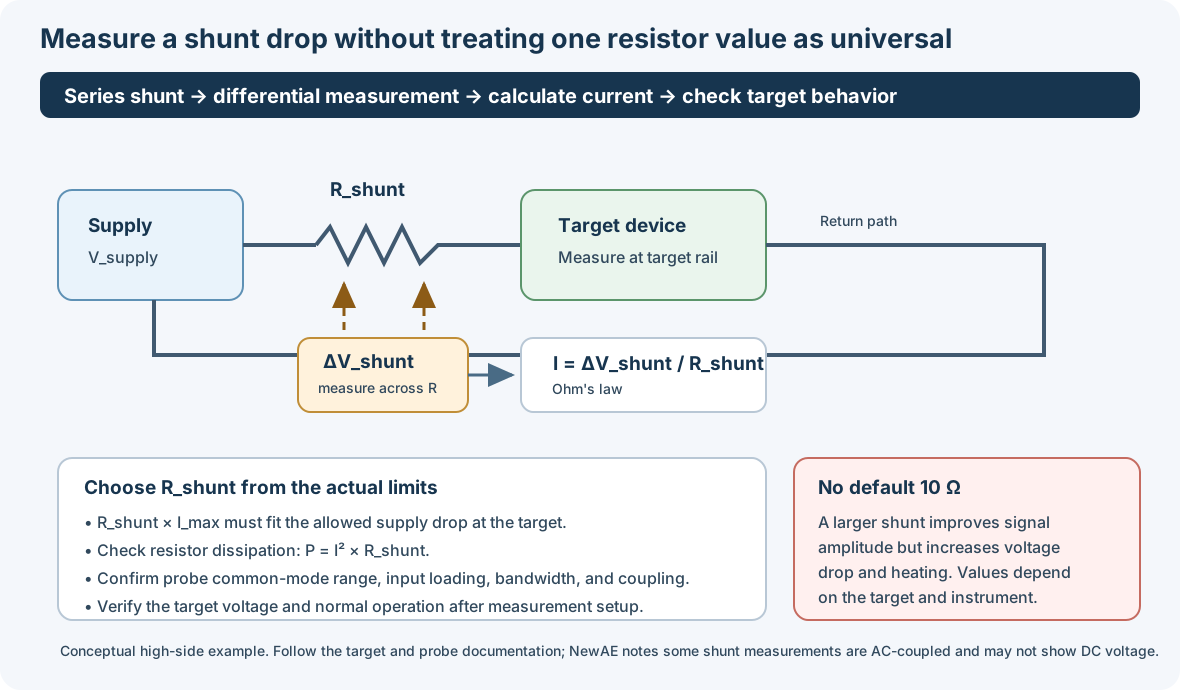
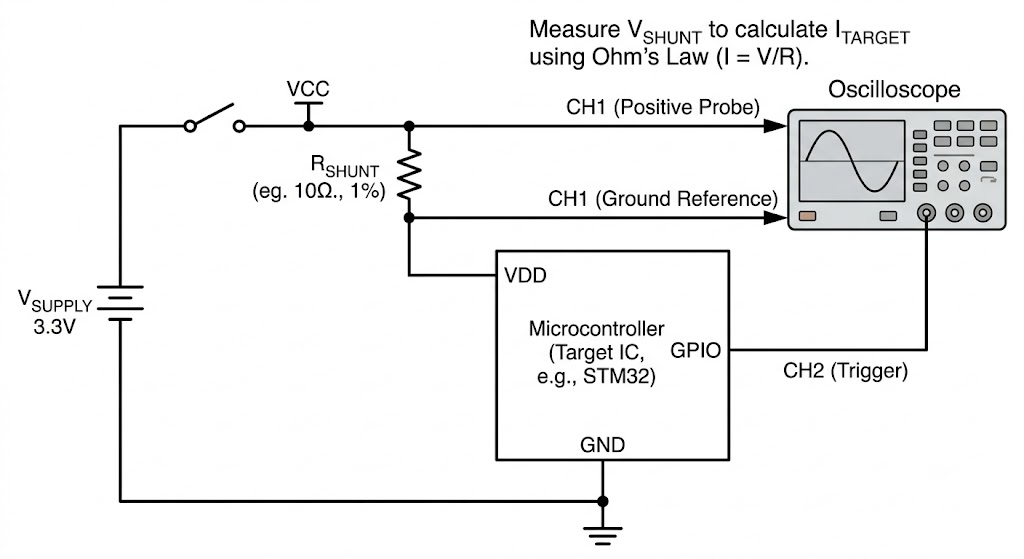
Original conceptual shunt-measurement figure; the resistor value depends on target current, allowable voltage drop, power dissipation, and instrument limits.
| Diagram | Embedded guide |
|---|---|
| Shunt current measurement | Electrical Fundamentals — Shunt Resistors |
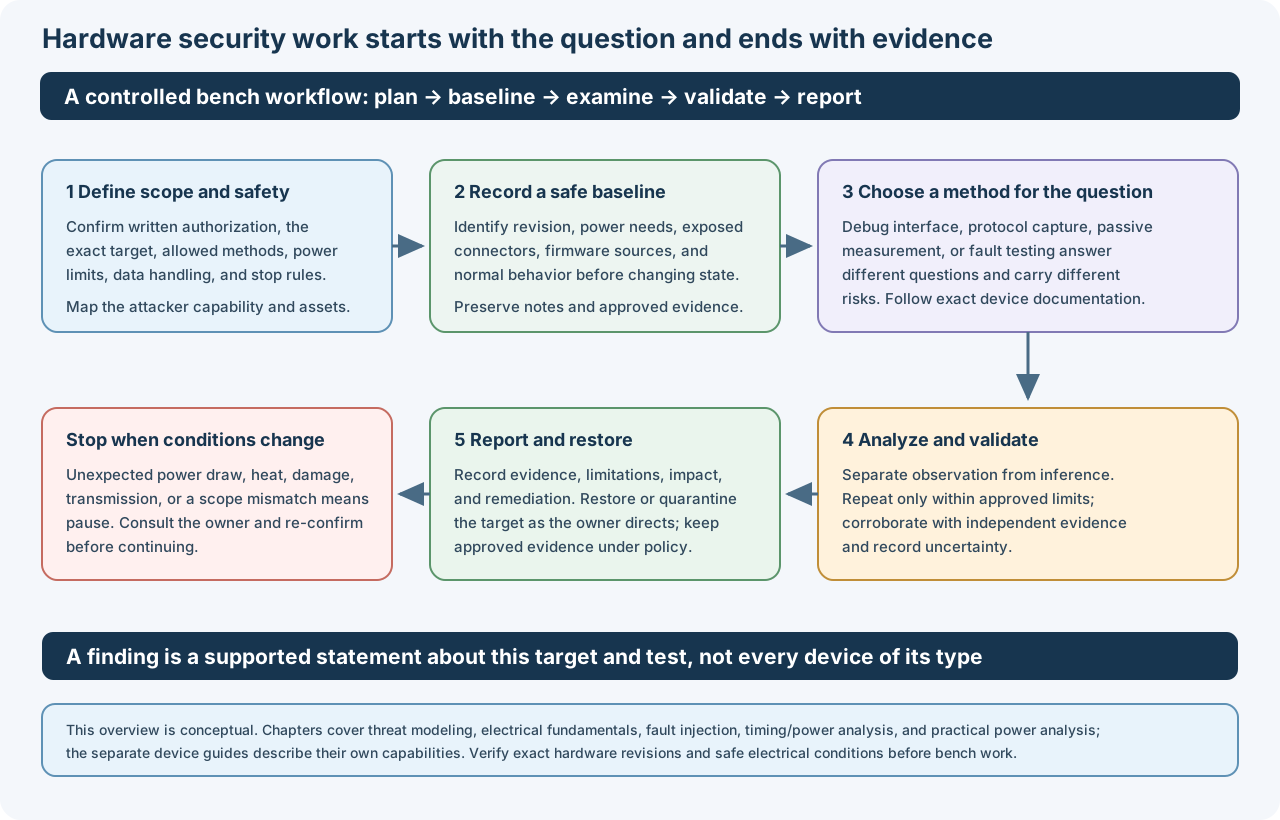
Original conceptual workflow; the exact test method and safe limits depend on the authorized target and its documentation.
| Diagram | Embedded guide |
|---|---|
| Hardware security bench workflow | Hardware Hacking overview |
| Image | Used in | Explanation |
|---|---|---|
| Tradecraft scope-to-detection loop | Tradecraft index | Conceptual flow from written authorization to controlled testing, observable telemetry, defensive validation, and reporting |
| AD attack paths | AD attacks and defenses | Kerberos and AD risk-path illustration |
| AI agent architecture | AI section | Conceptual file-system-first agent/tool boundaries |
| Hardware diagnostics | Hardware Testing | Reference board-level diagnostic workflow |
| Network architecture | Homelab | Example segmented design, not a verified live topology |
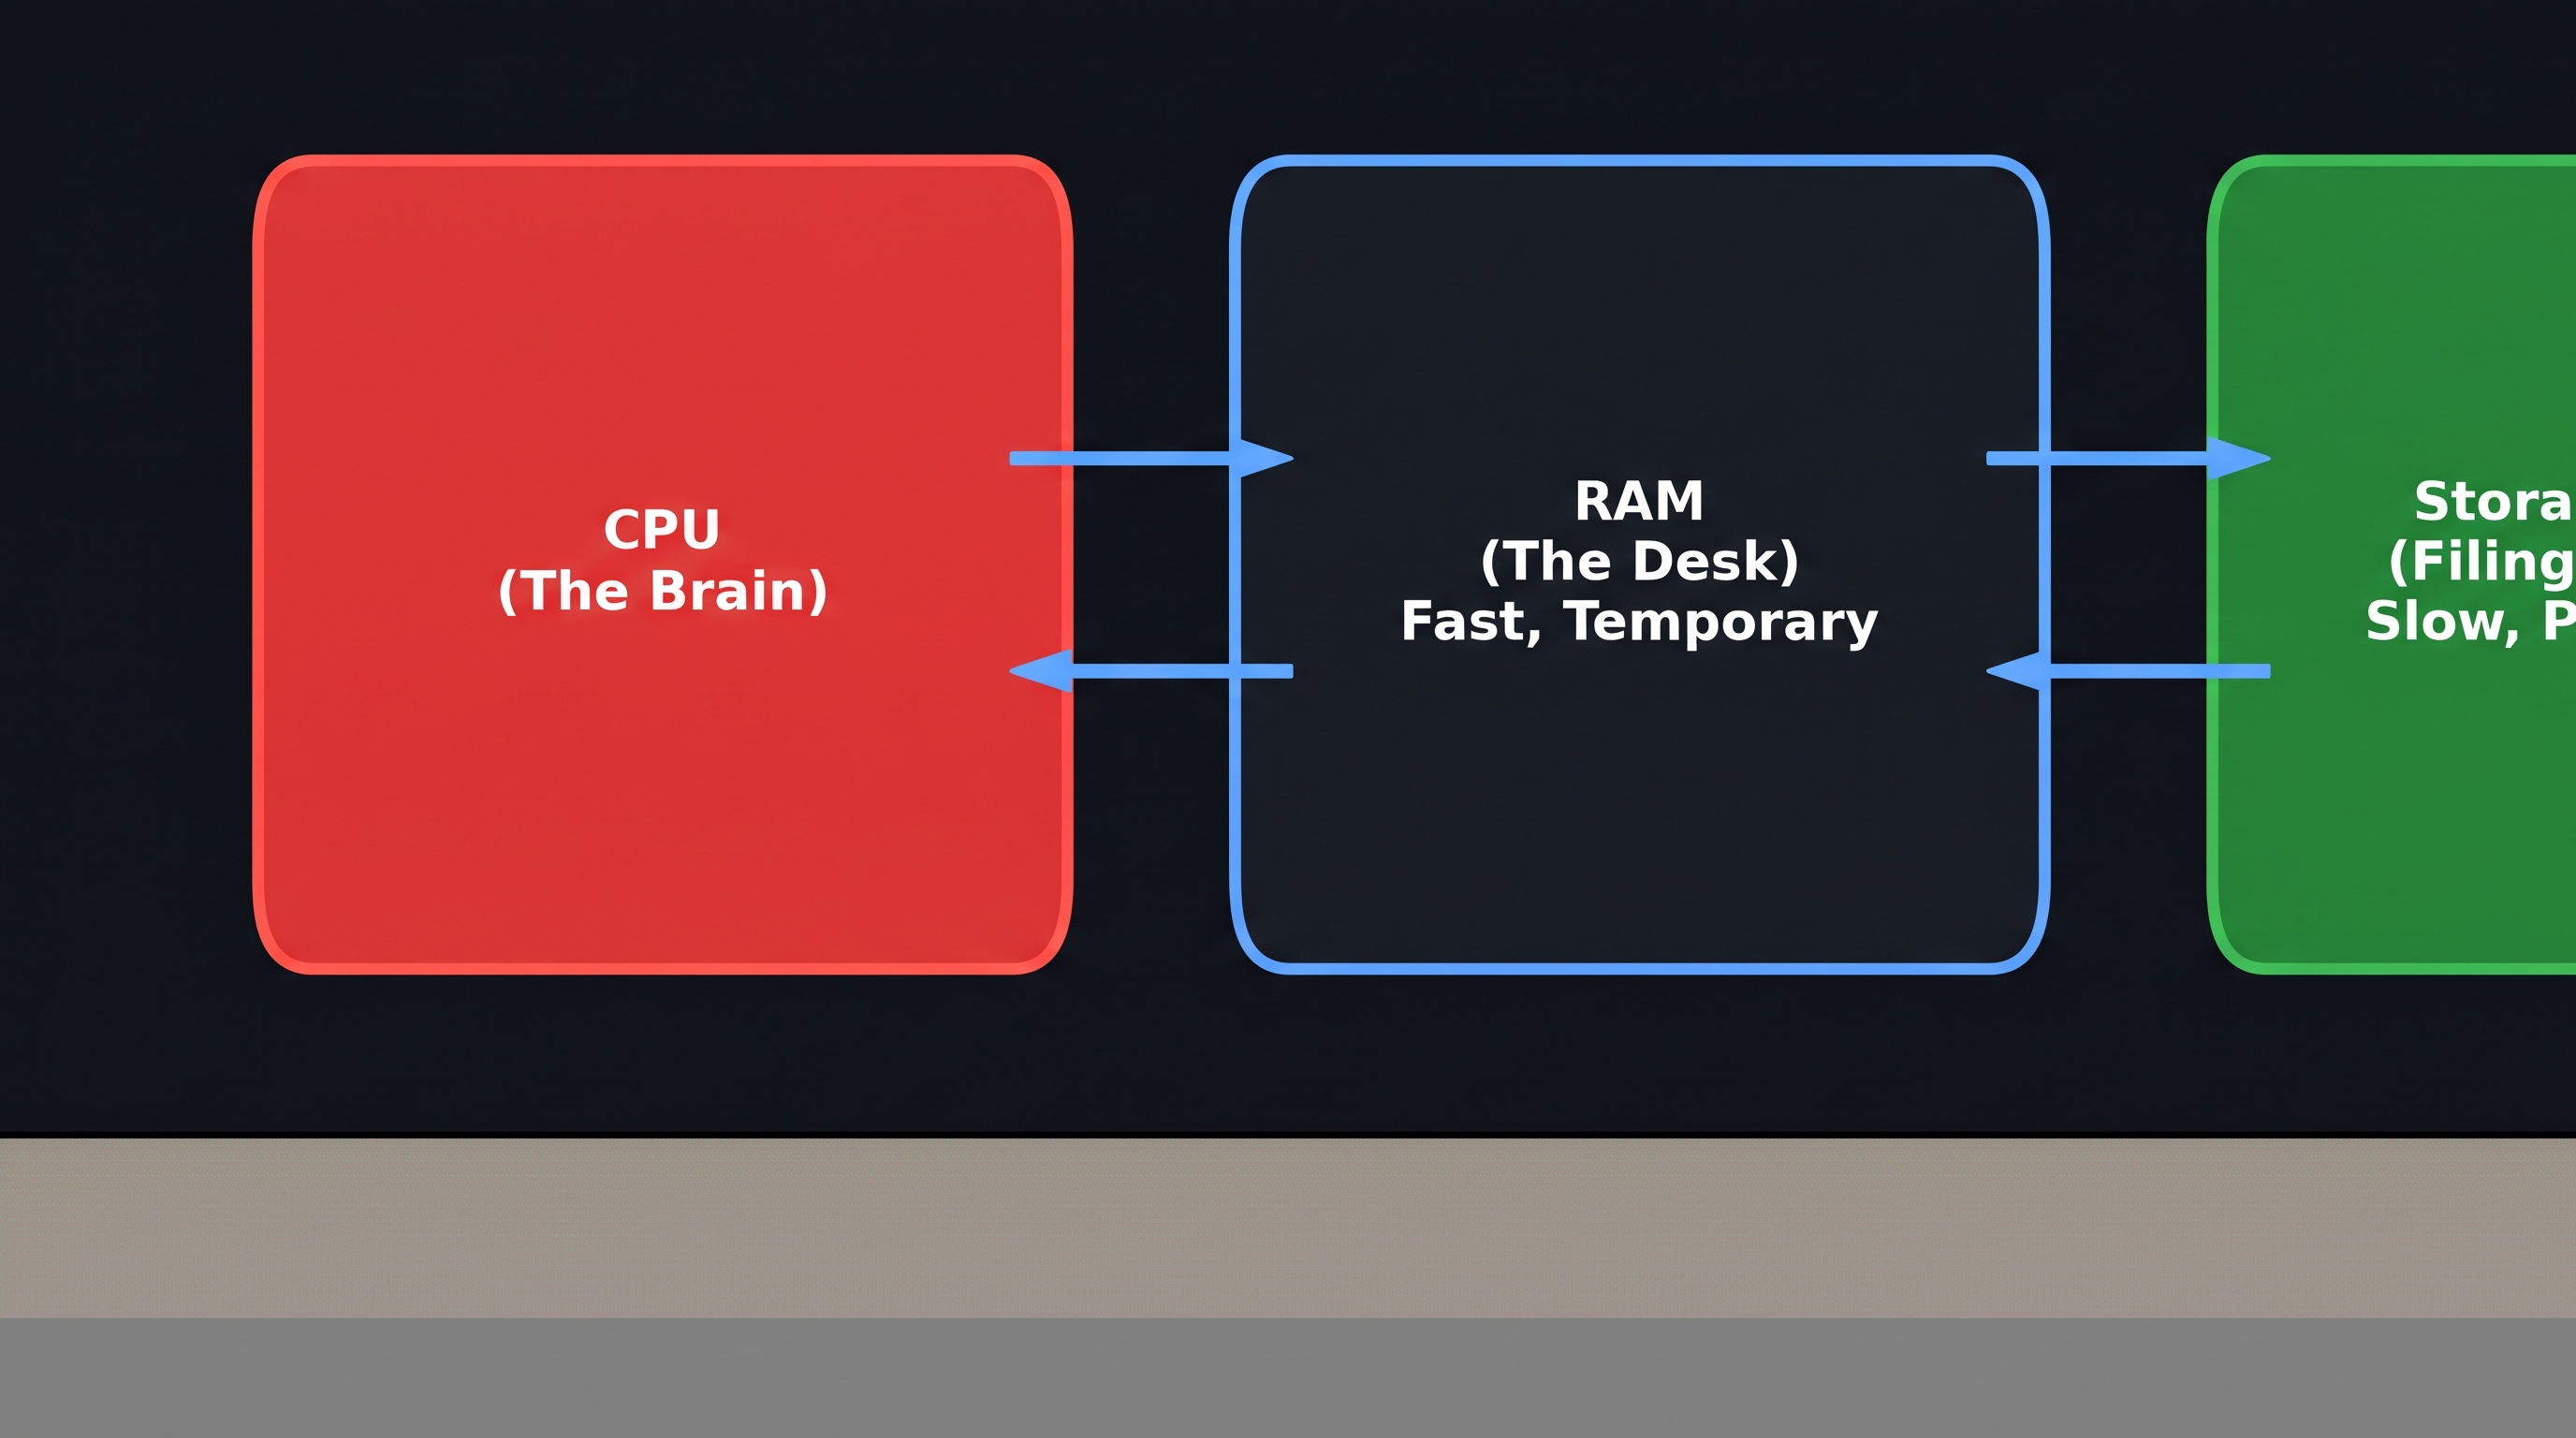
| RAM versus storage | Manjaro test bench | Introductory CPU/RAM/storage mental model |
| VM compartmentalization | OPSEC guide | Boundary illustration with important host/guest limitations |
| Wireless auditing | Network Audit Playbook | Wireless engagement workflow |
| Penetration-test lifecycle | Playbooks | Assessment lifecycle overview |
| JWrapper abuse case study | Incident Response | Illustrative remote-access-software abuse path, not proof of infection |
| FIDO2 / passkey authentication | Hardware keys and passkeys | New accessible vector figure, showing registration and sign-in |
| Encrypted storage boundaries | Encrypted storage | New accessible vector figure, locked versus unlocked data and backup limitations |
| Journalist source-data lifecycle | Press freedom / source protection | New accessible vector figure, preservation holds and approved disposition |

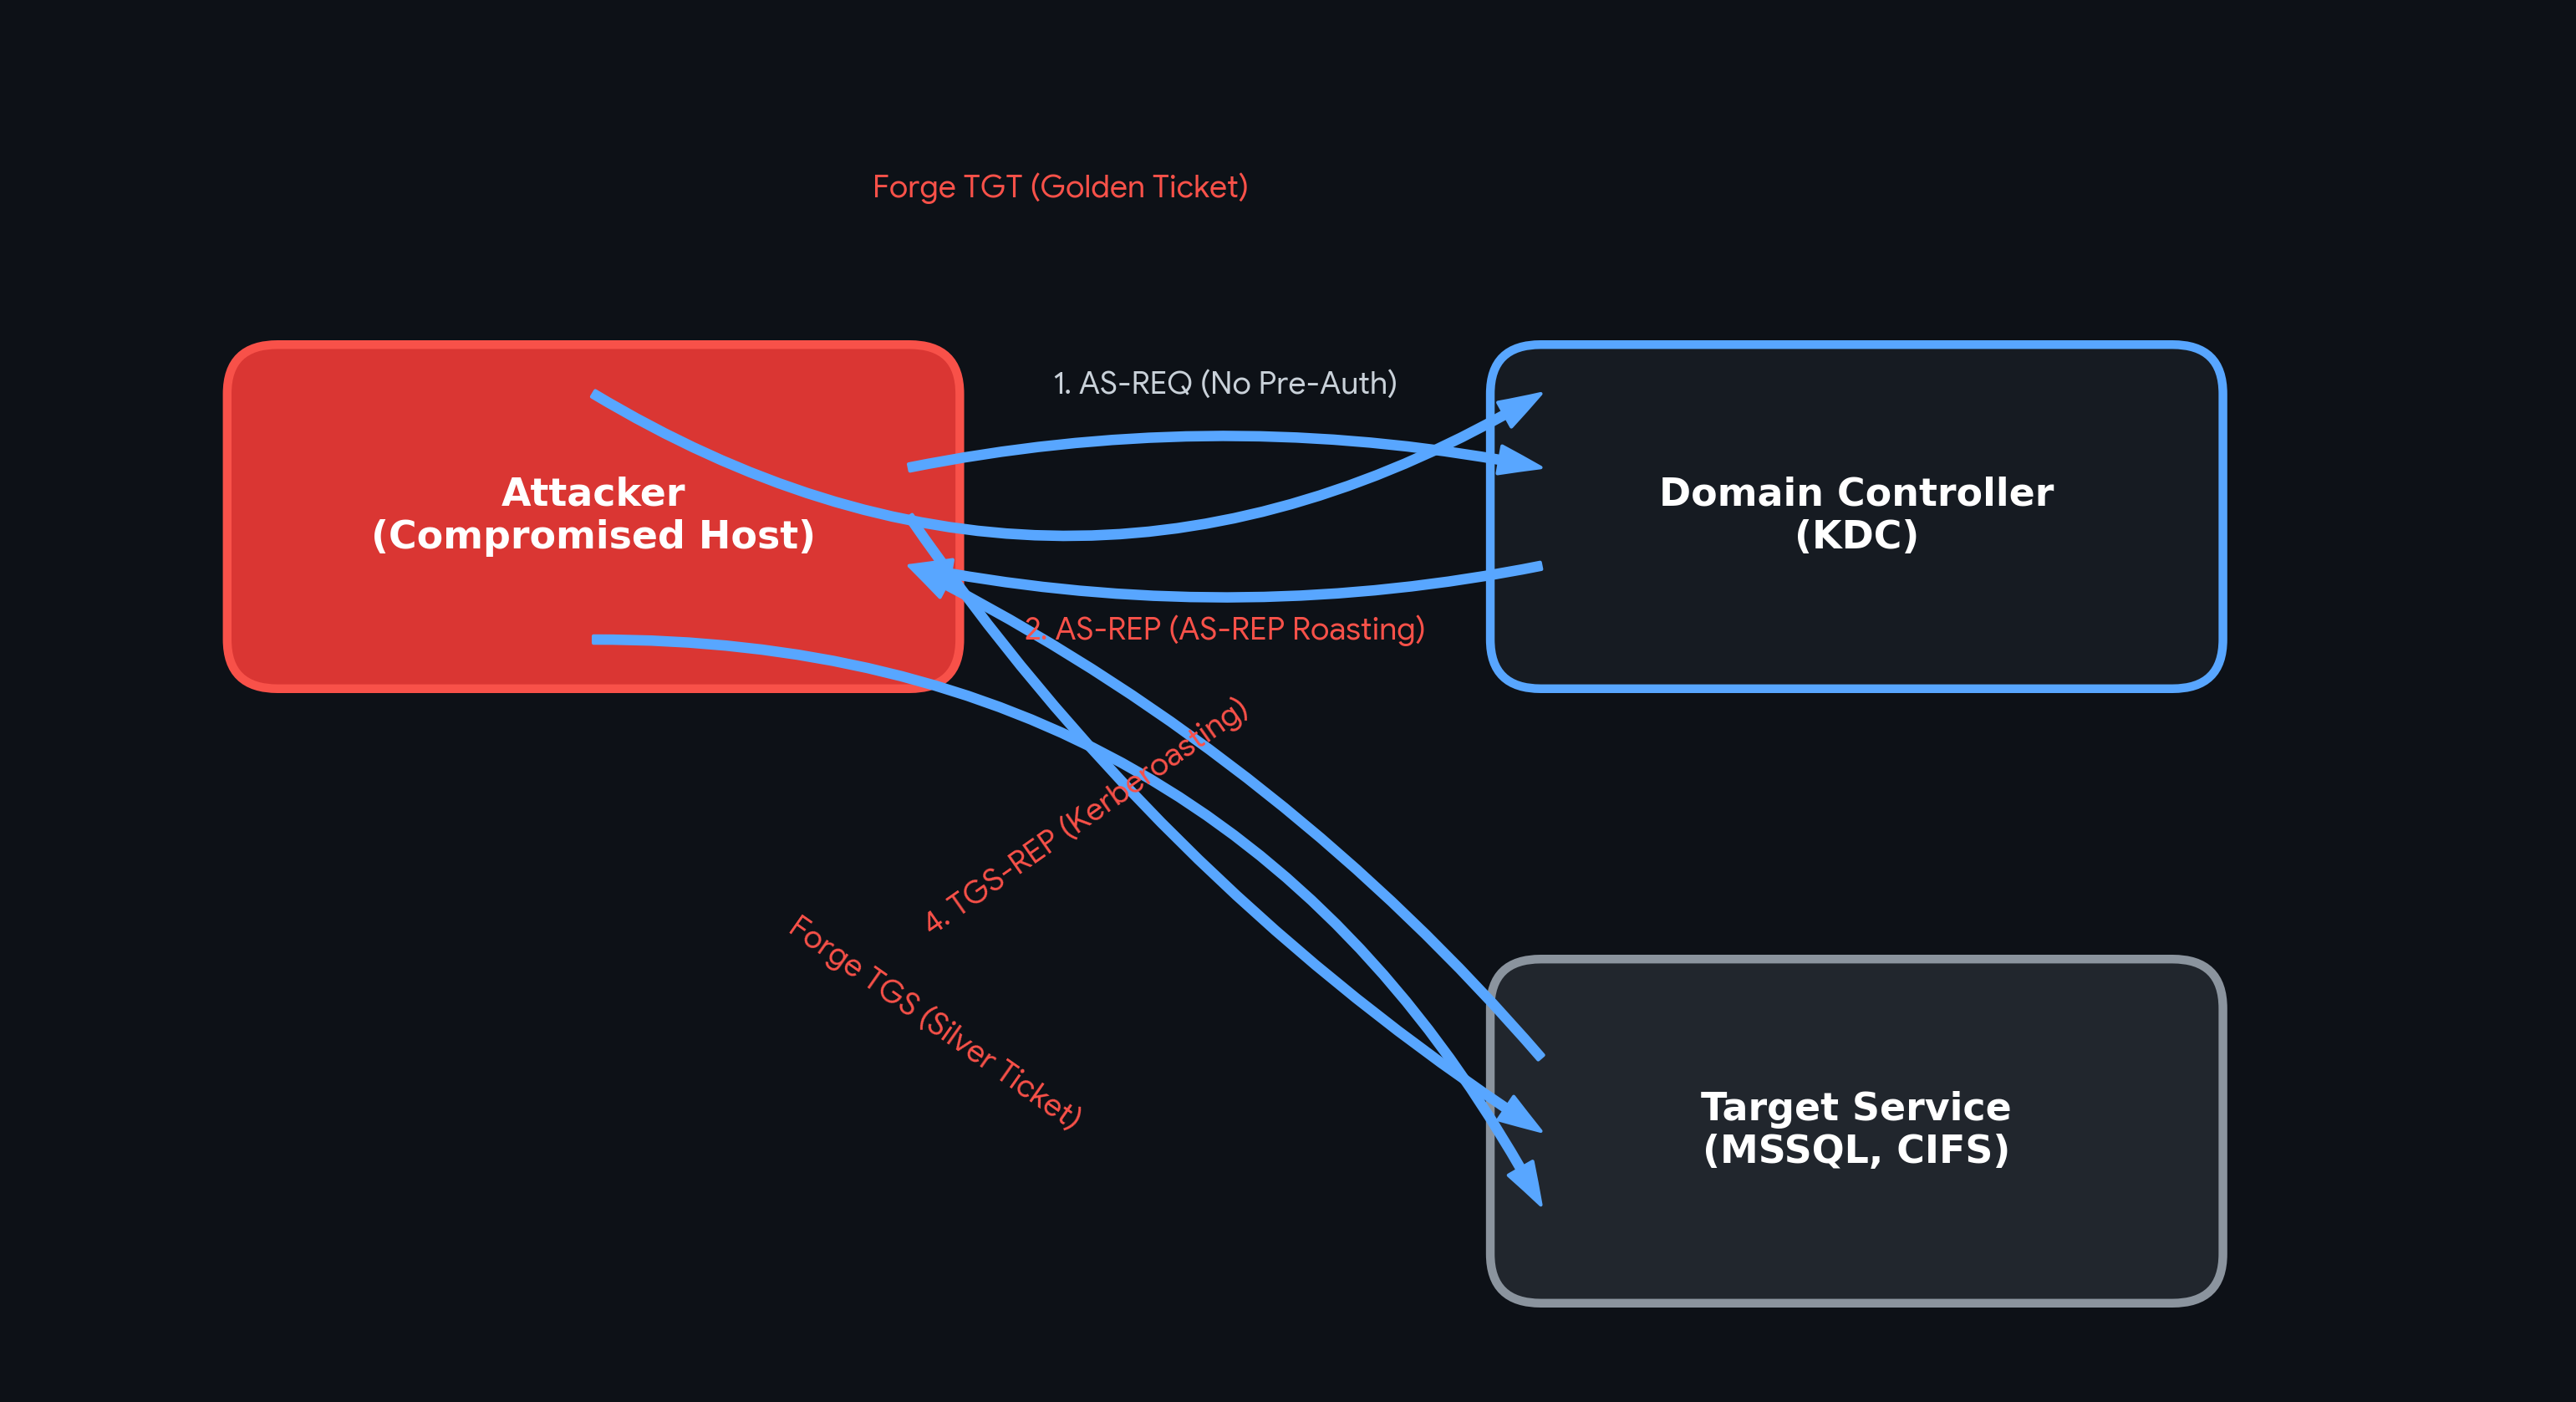
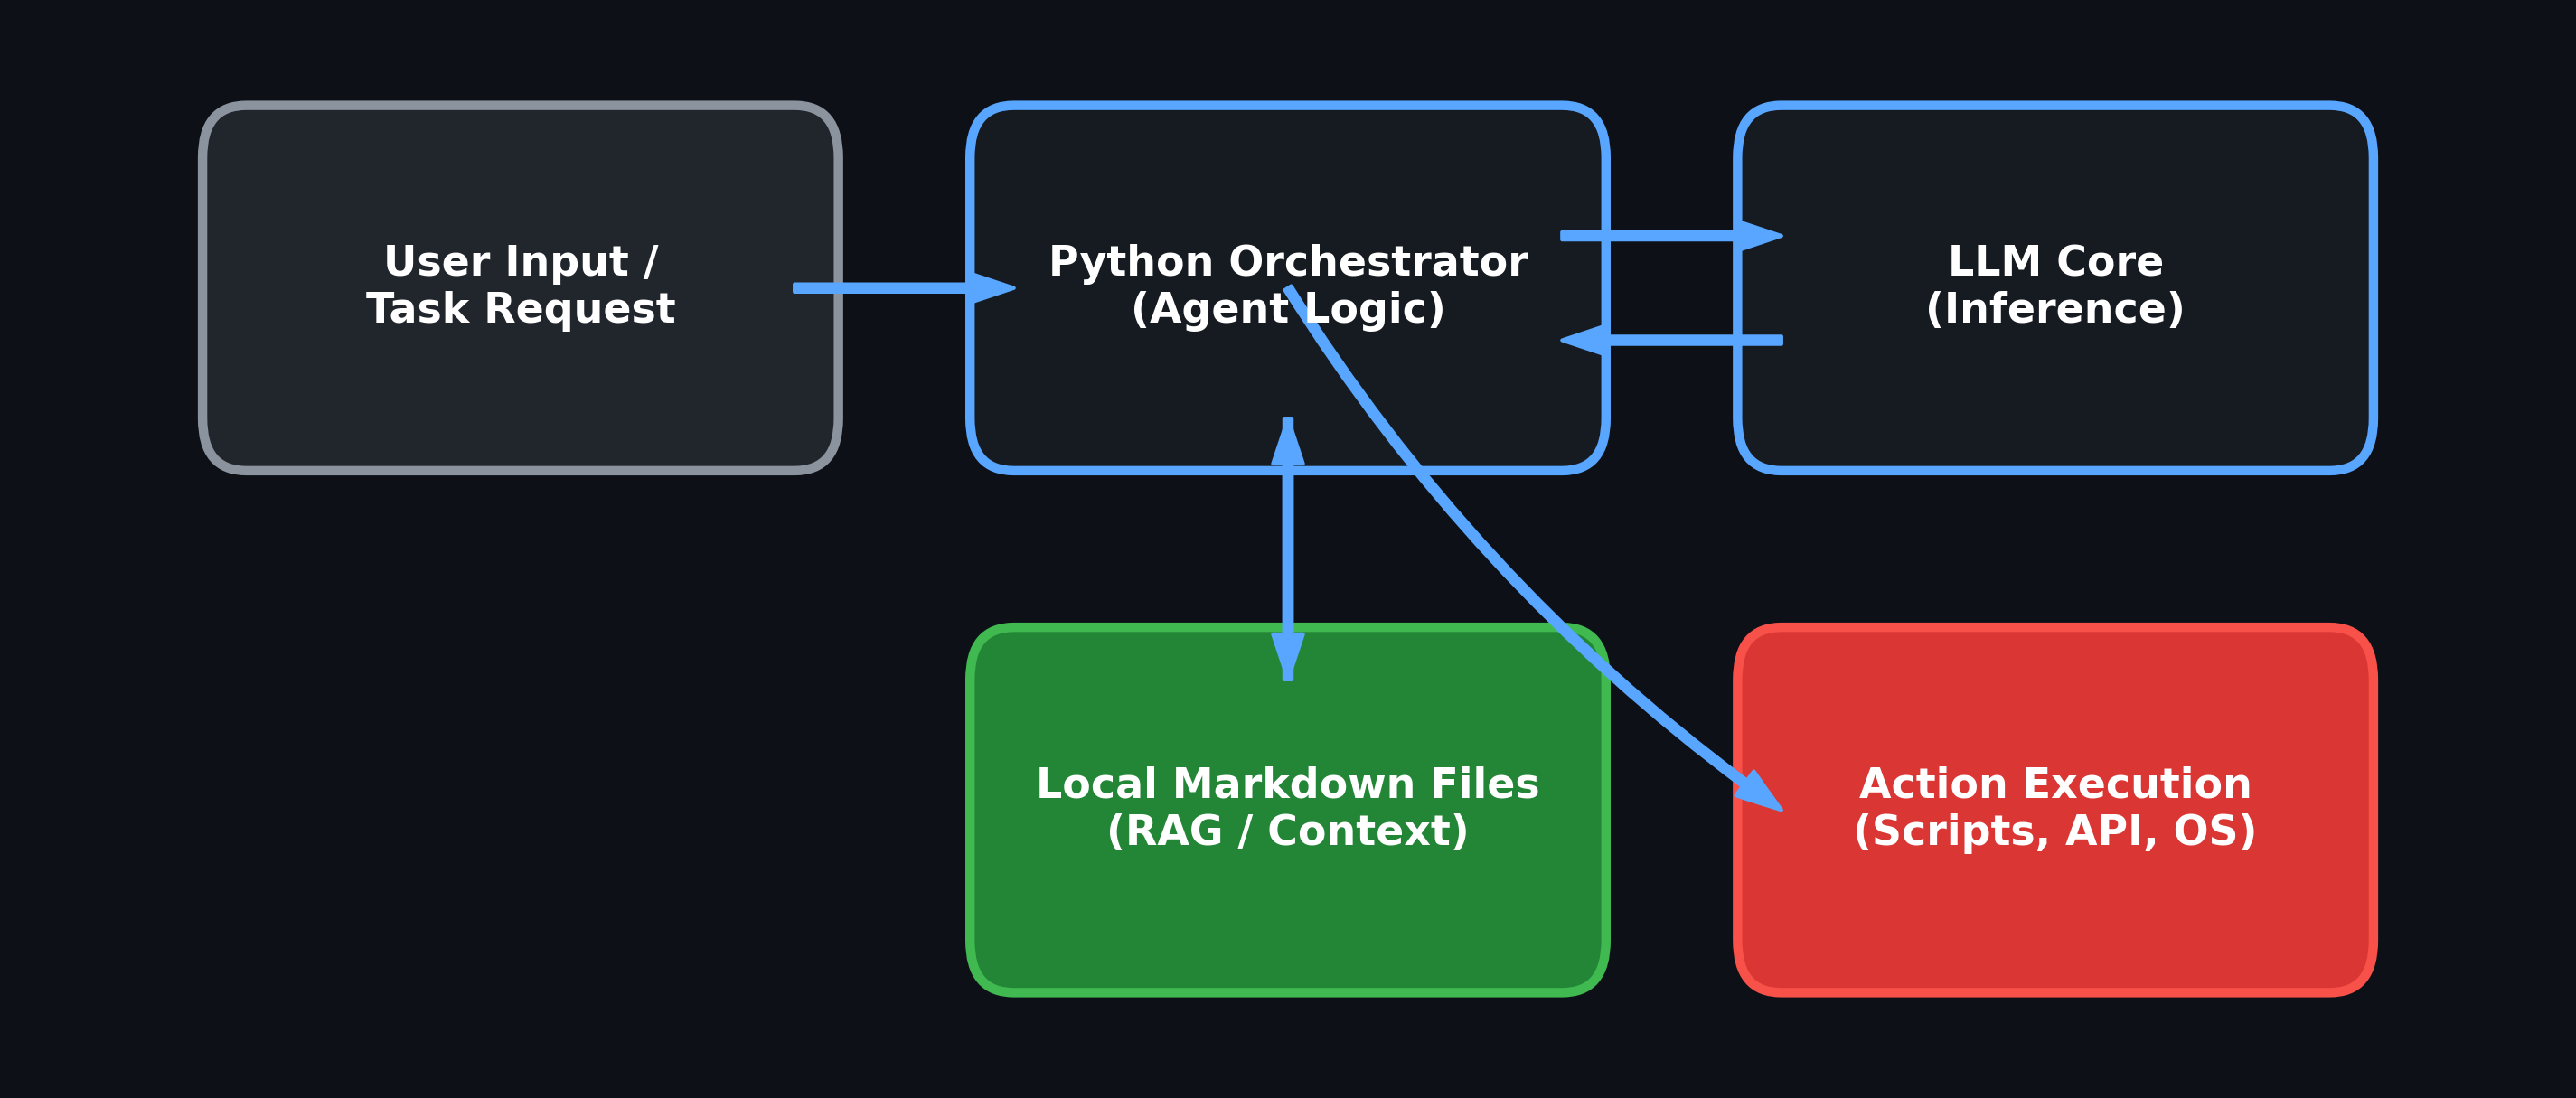
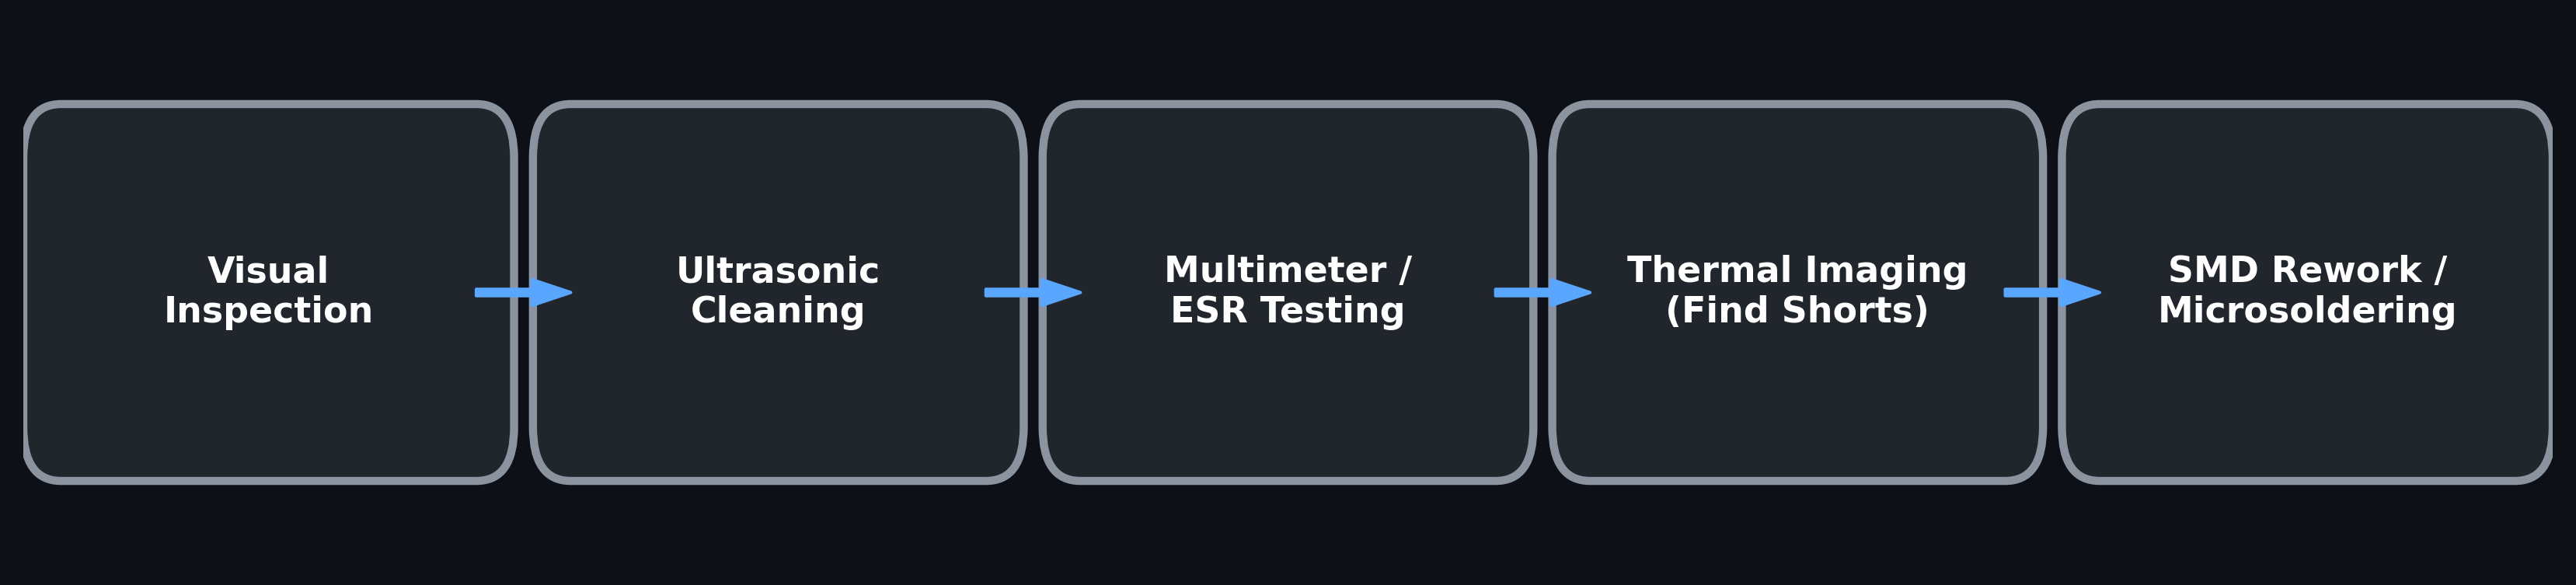
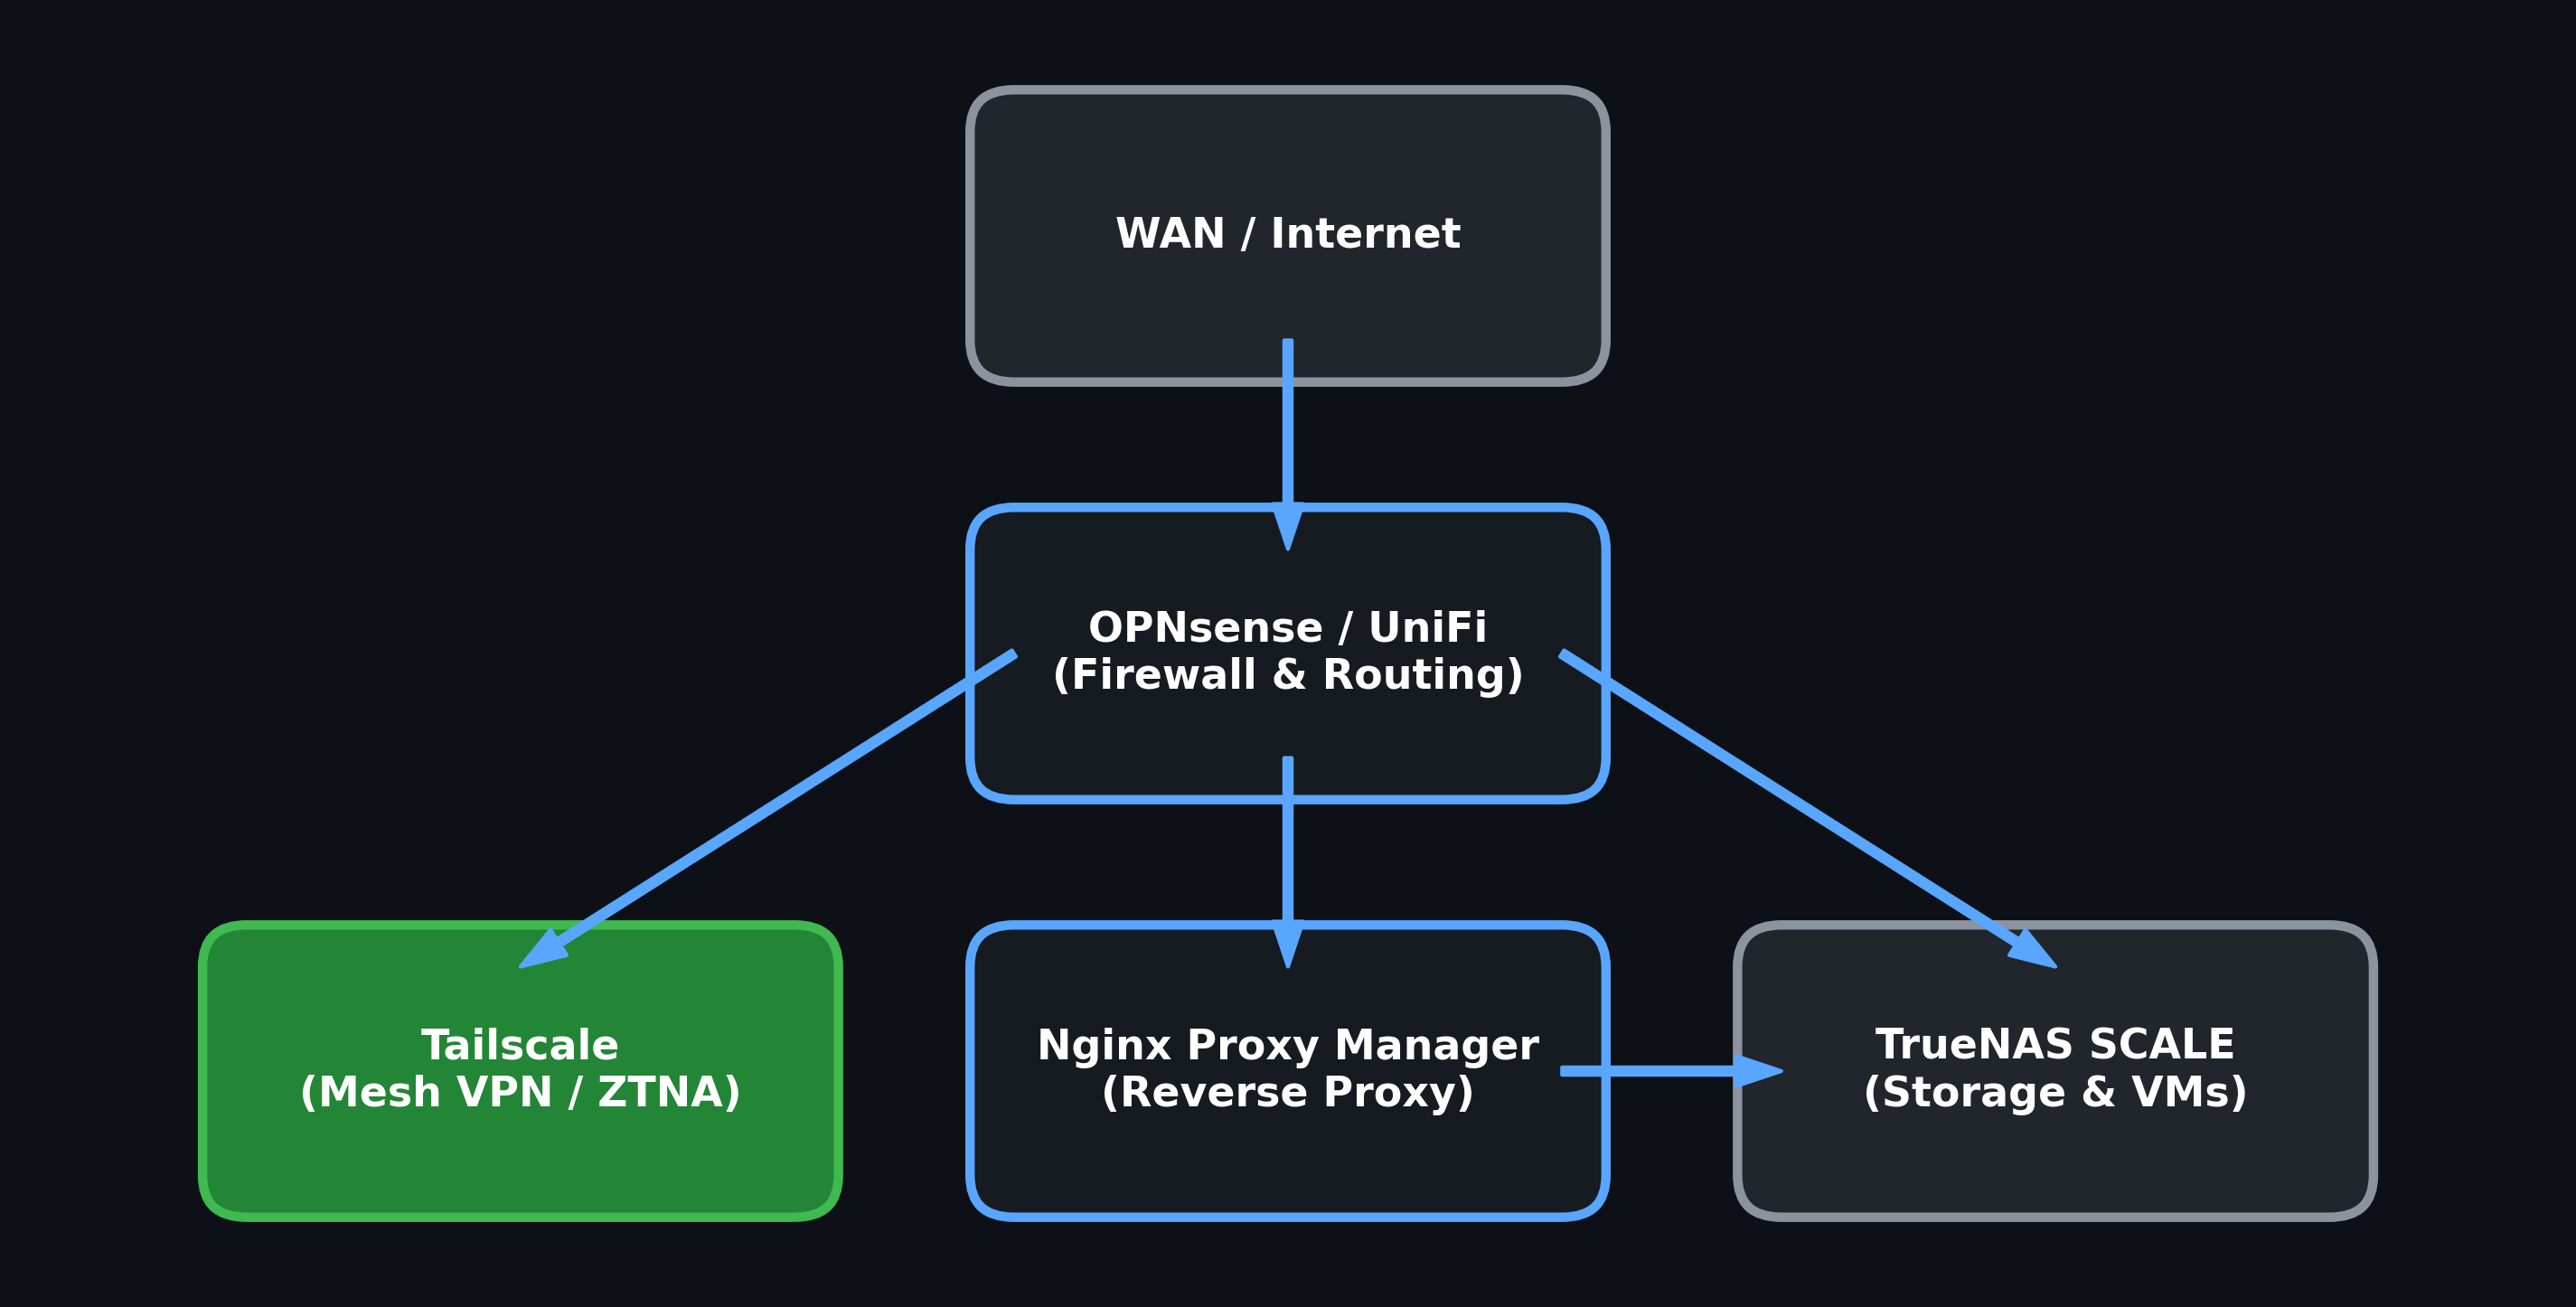
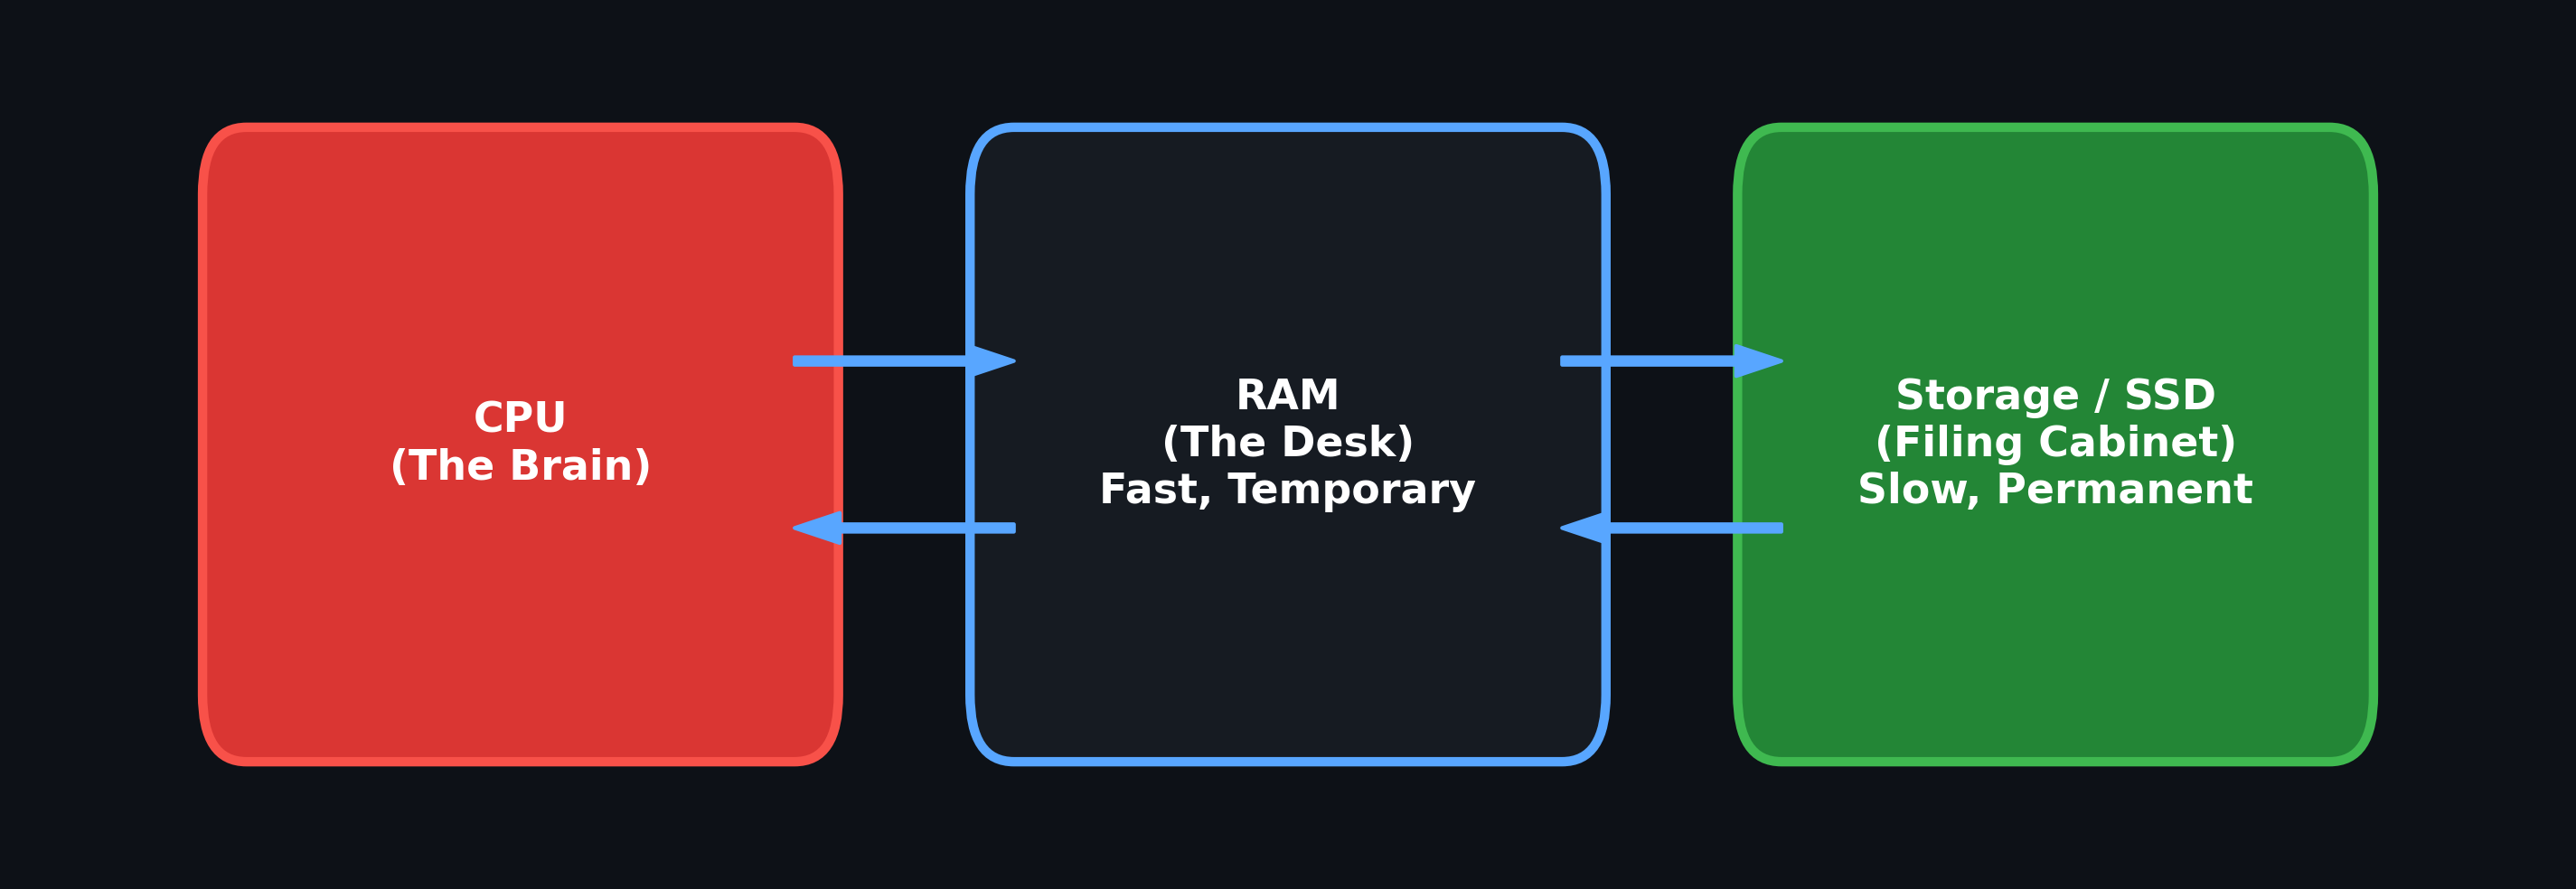
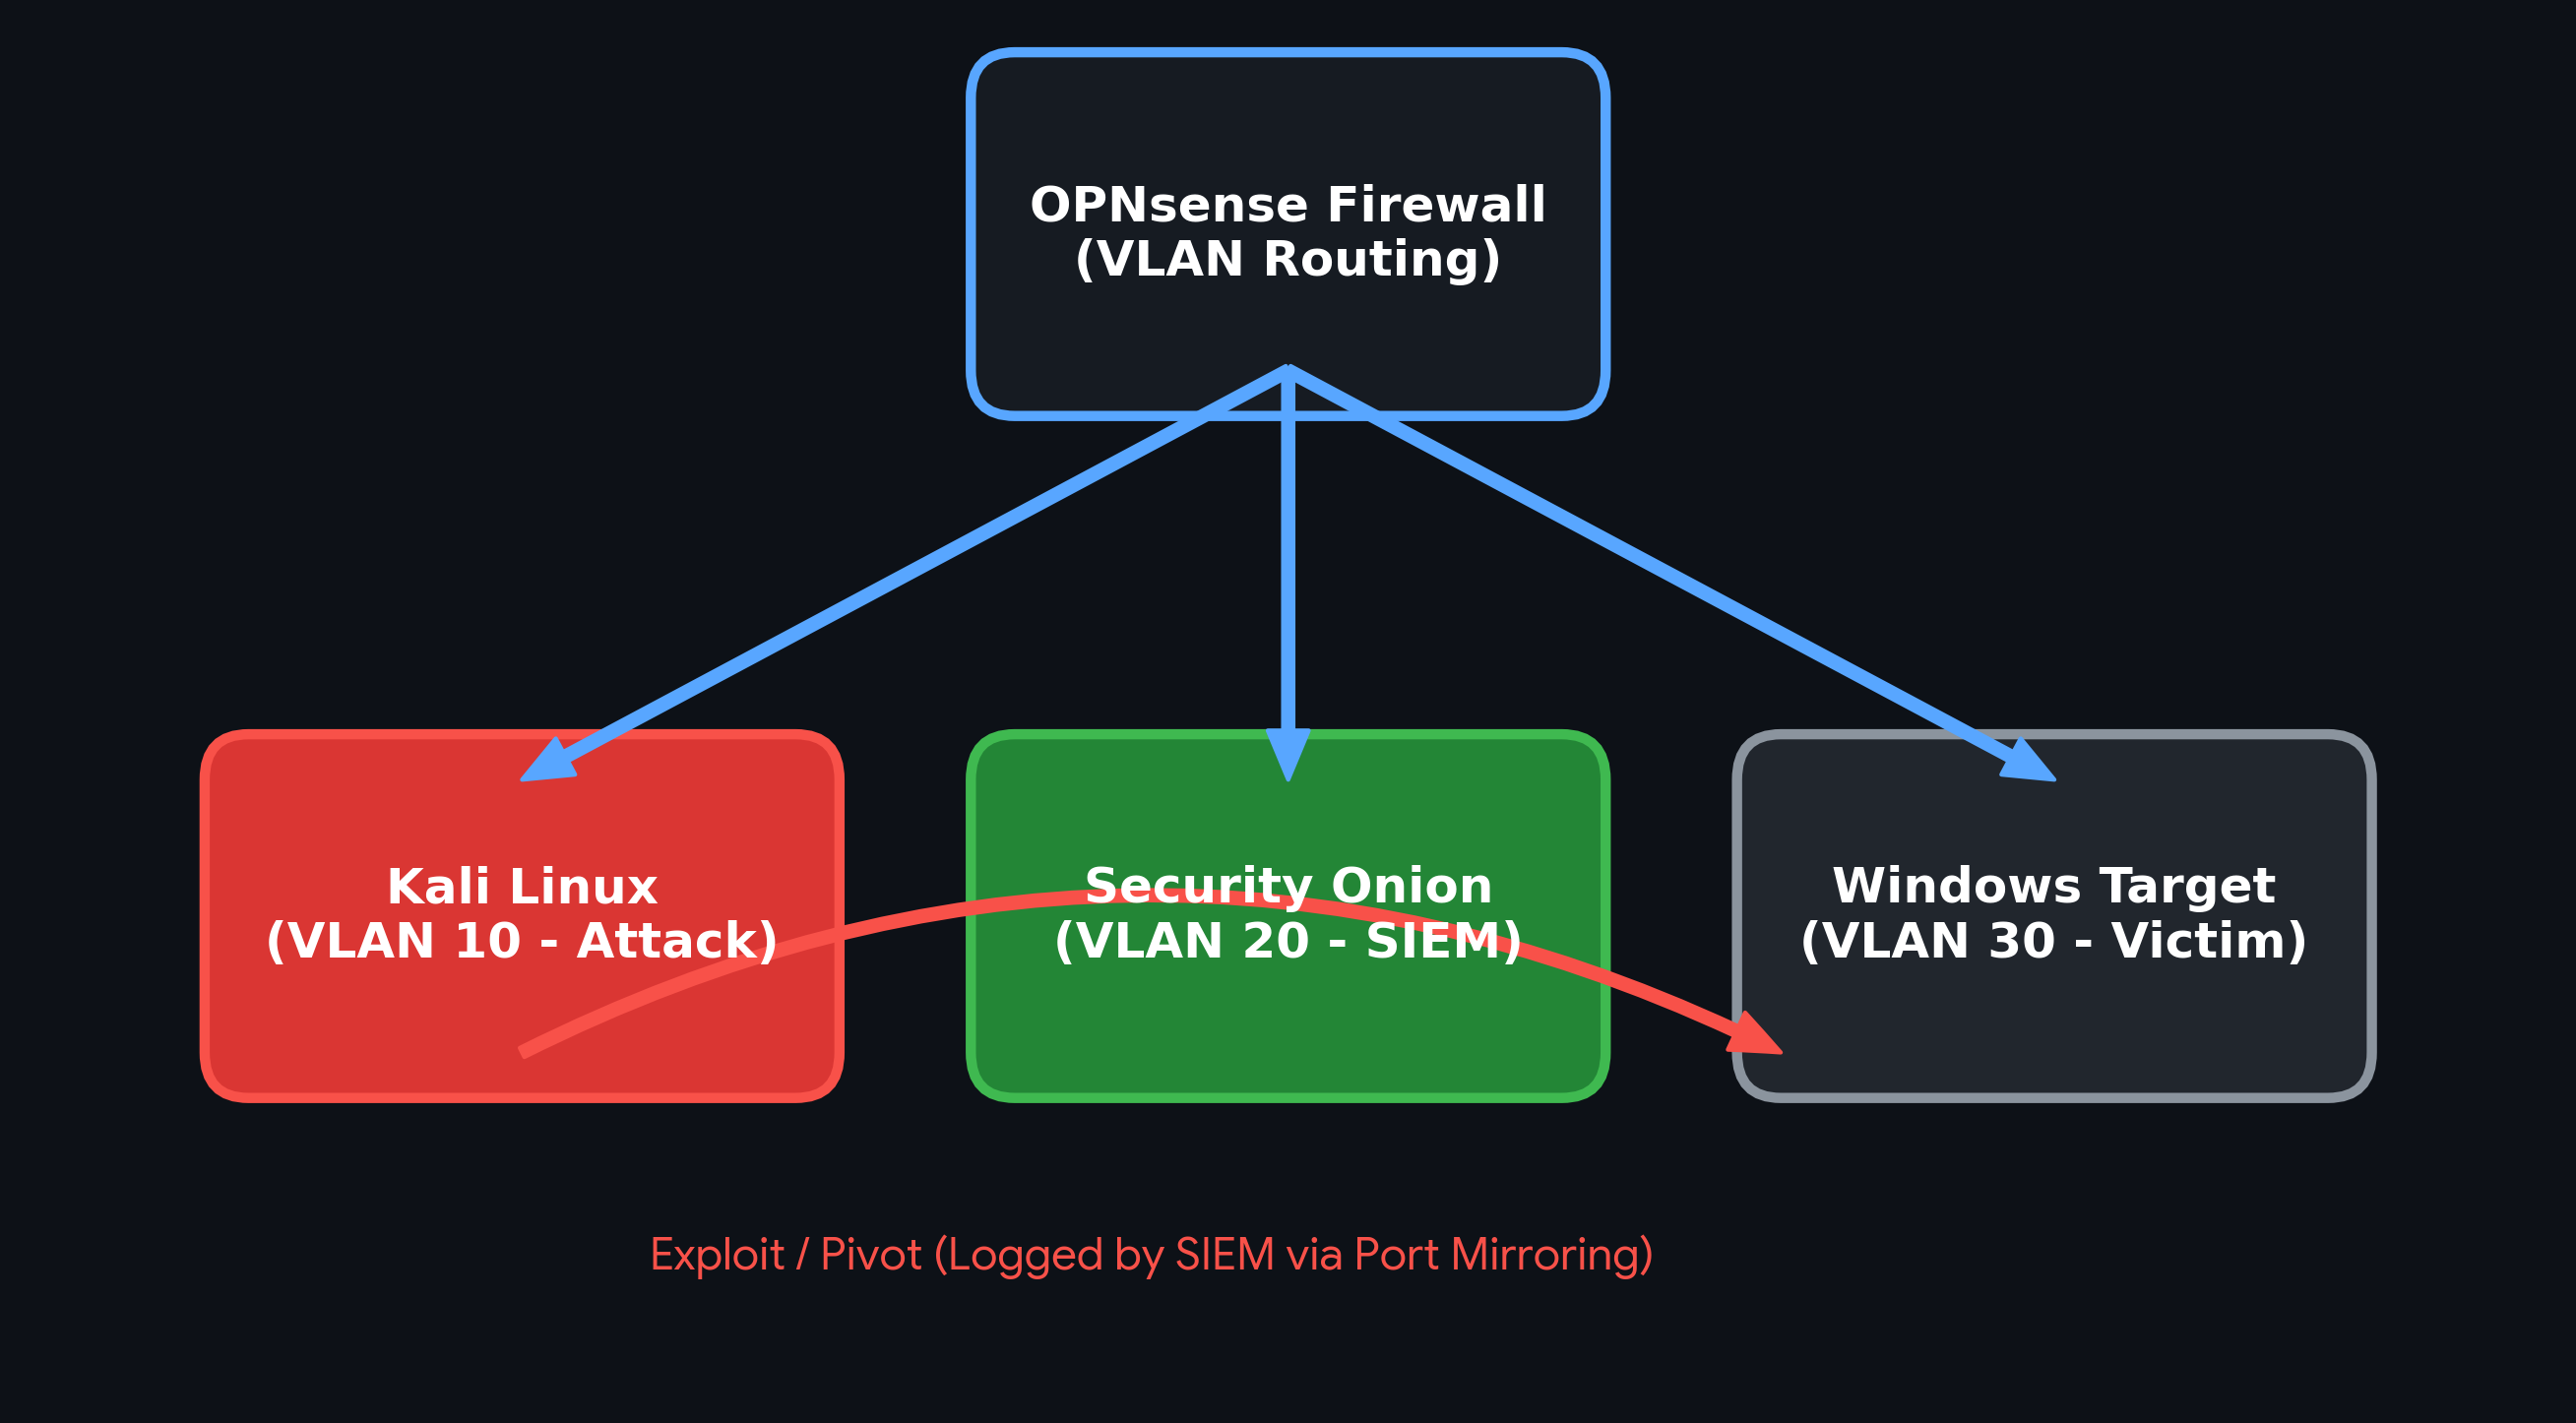
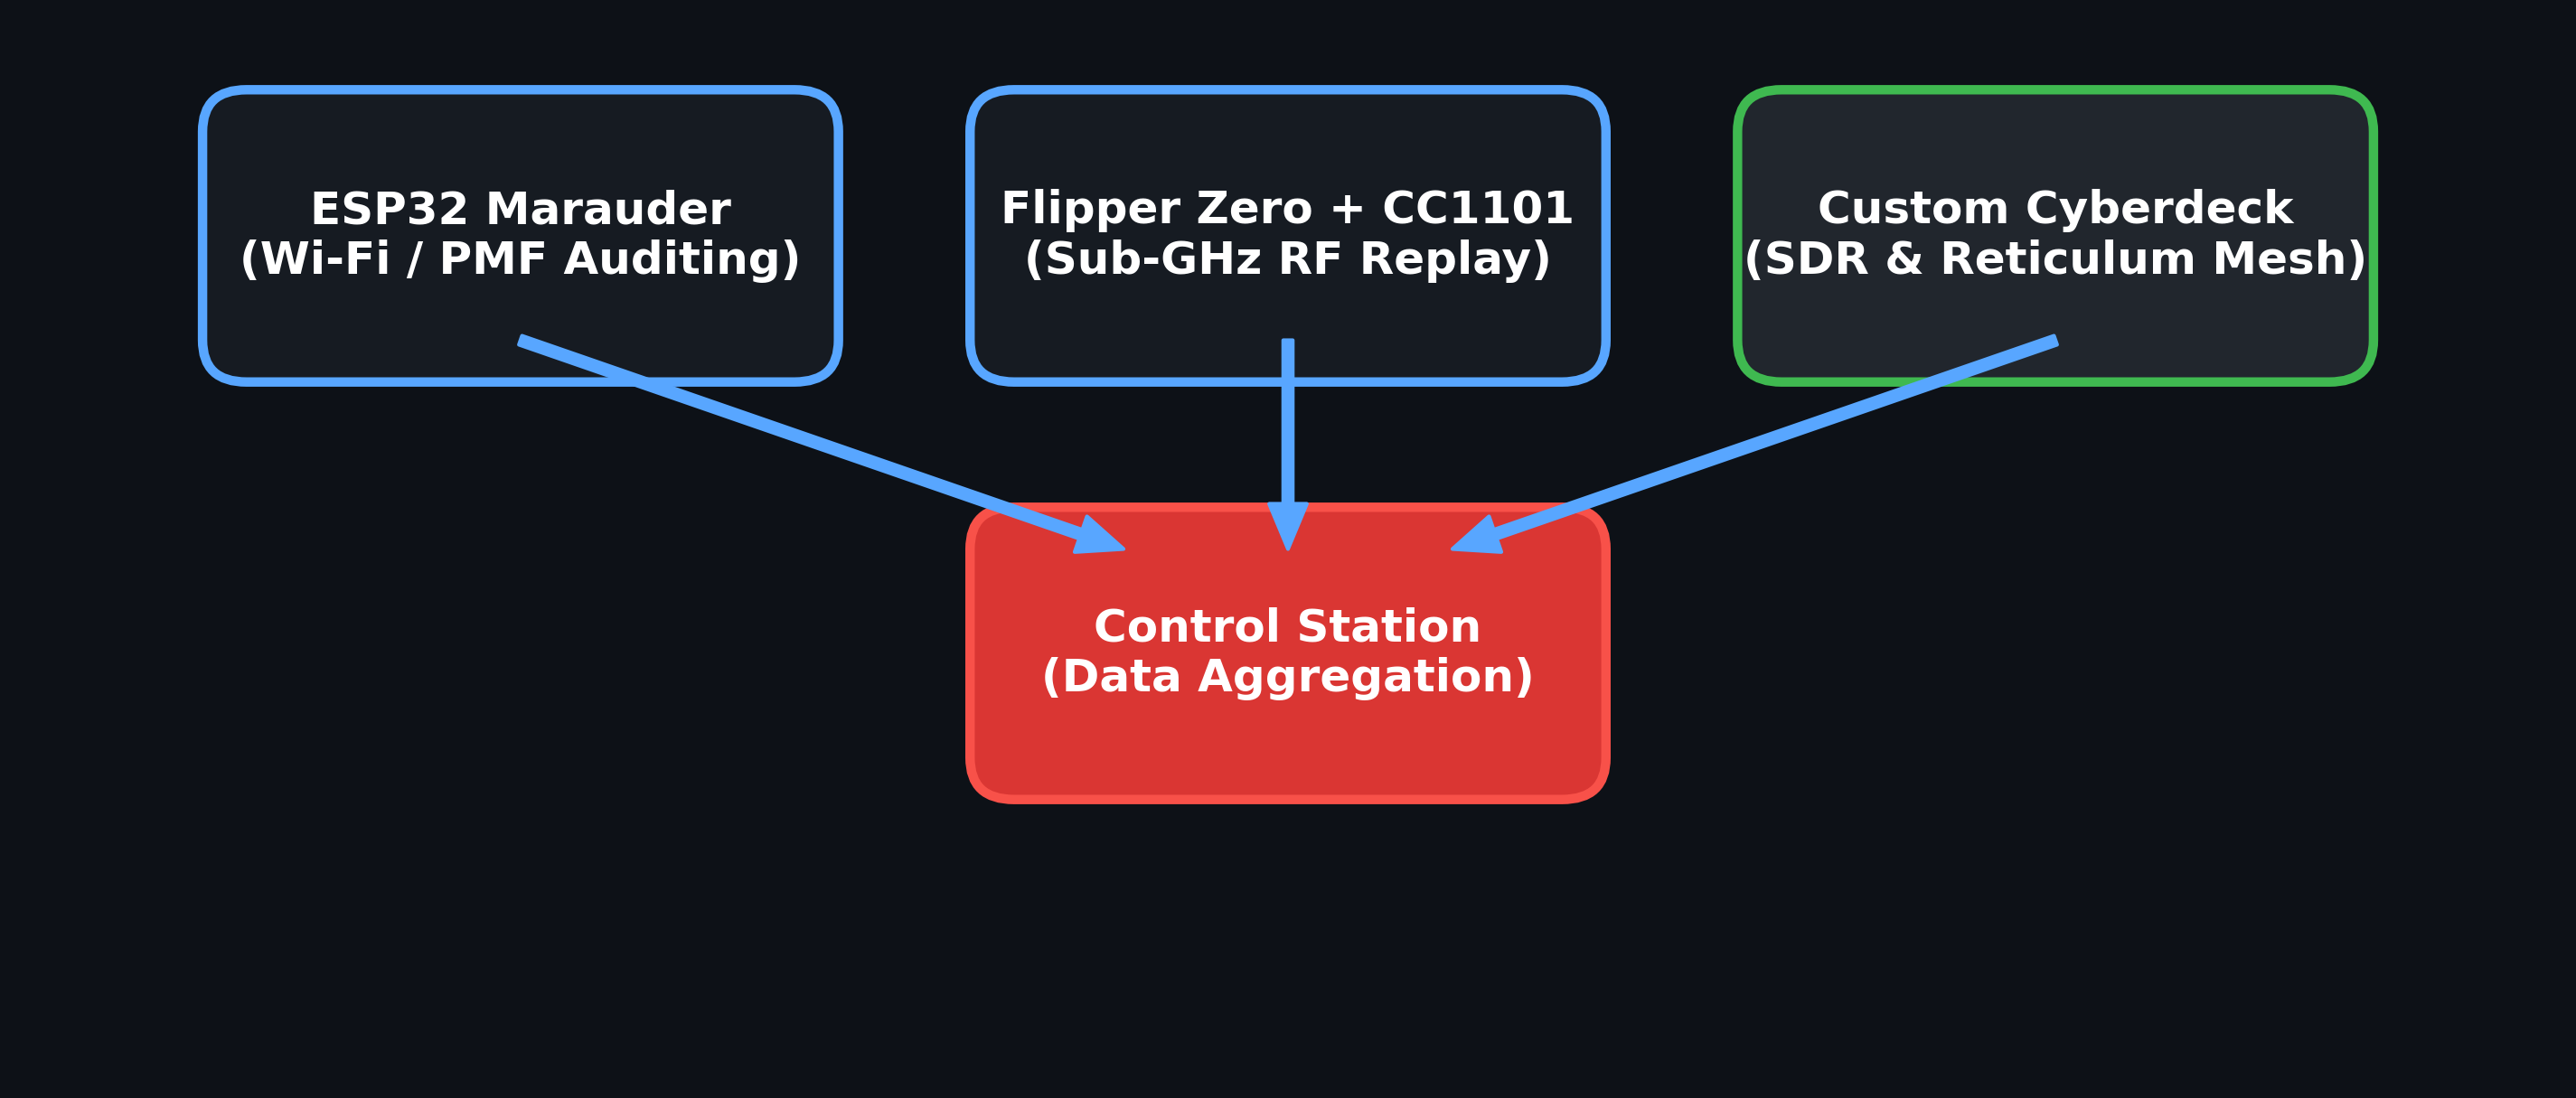
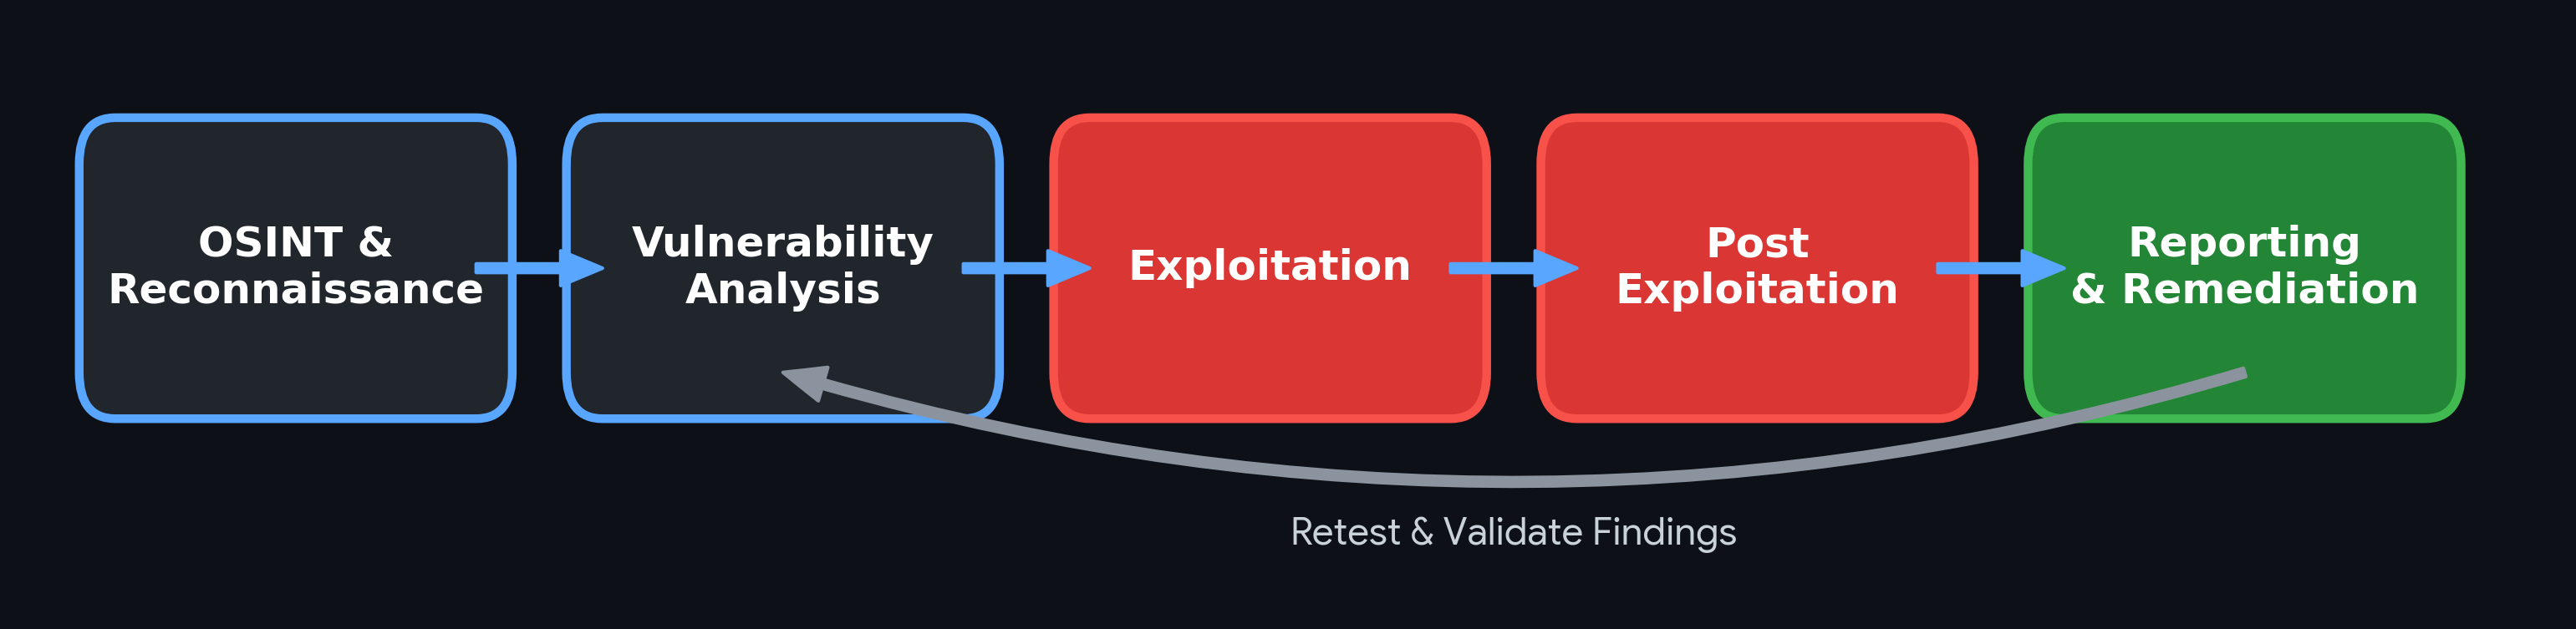
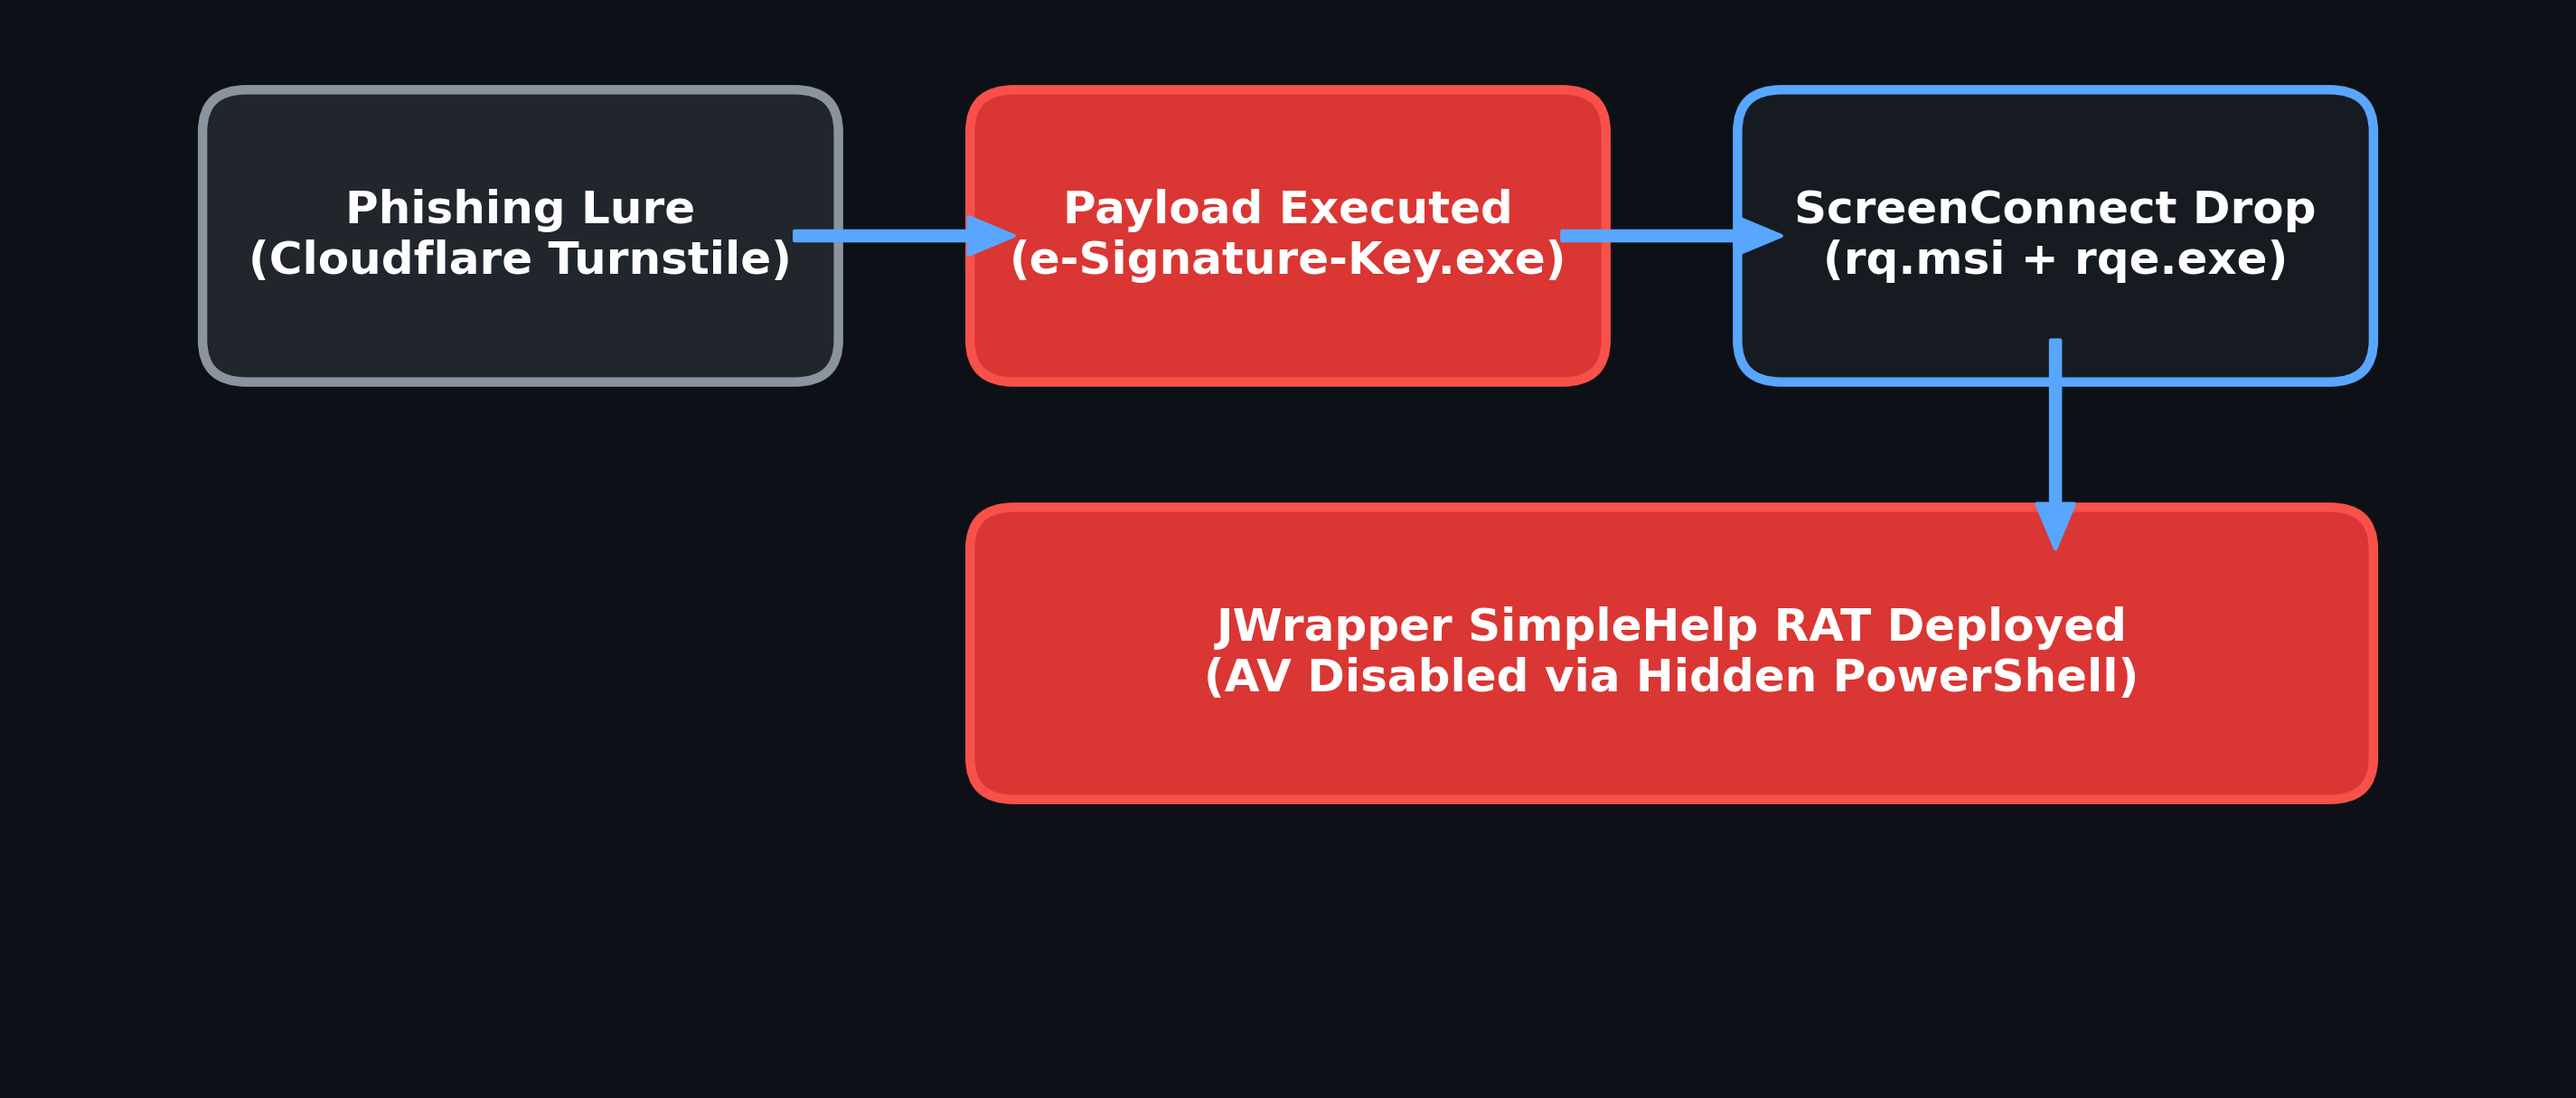
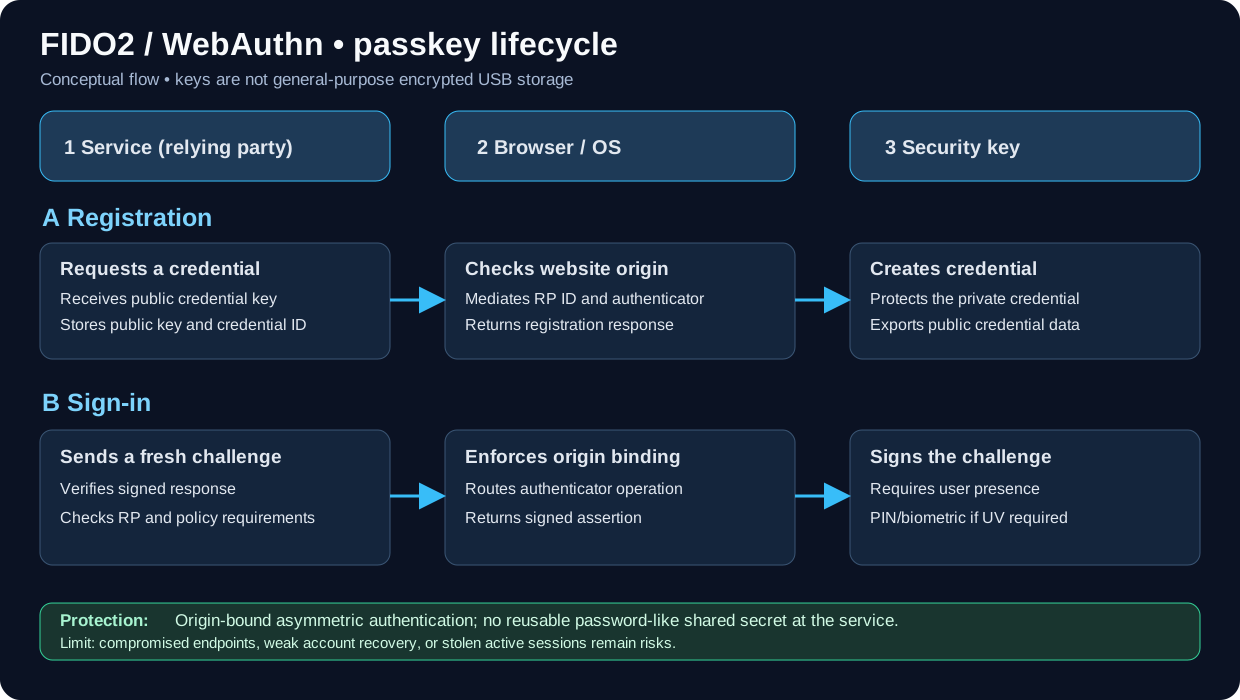
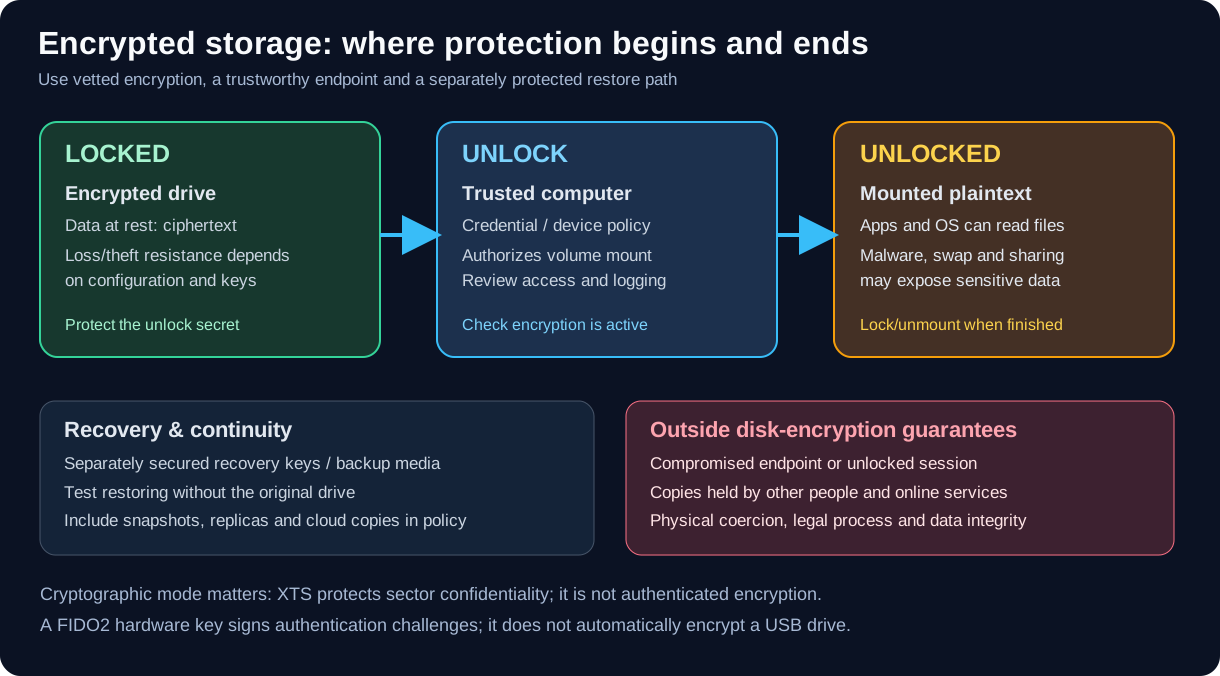
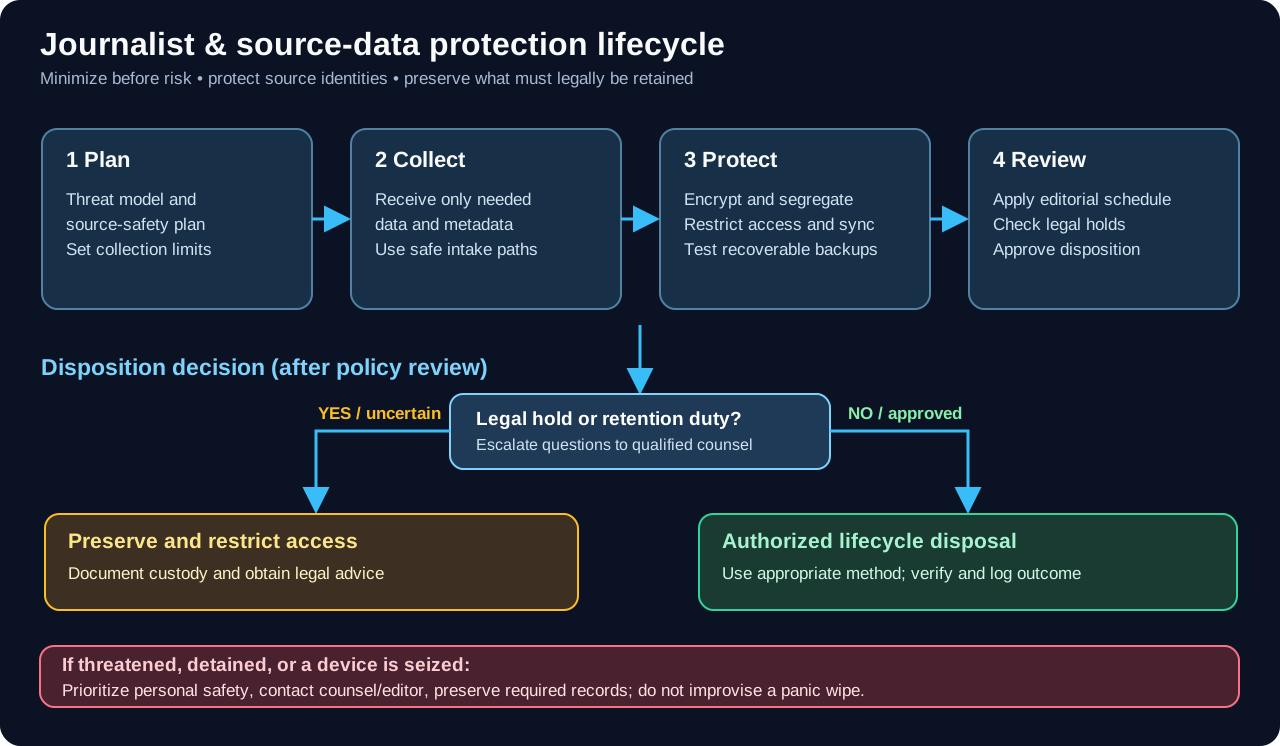
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| opsec vm network choices | Guide |
| opsec malware lab boundaries | Guide |
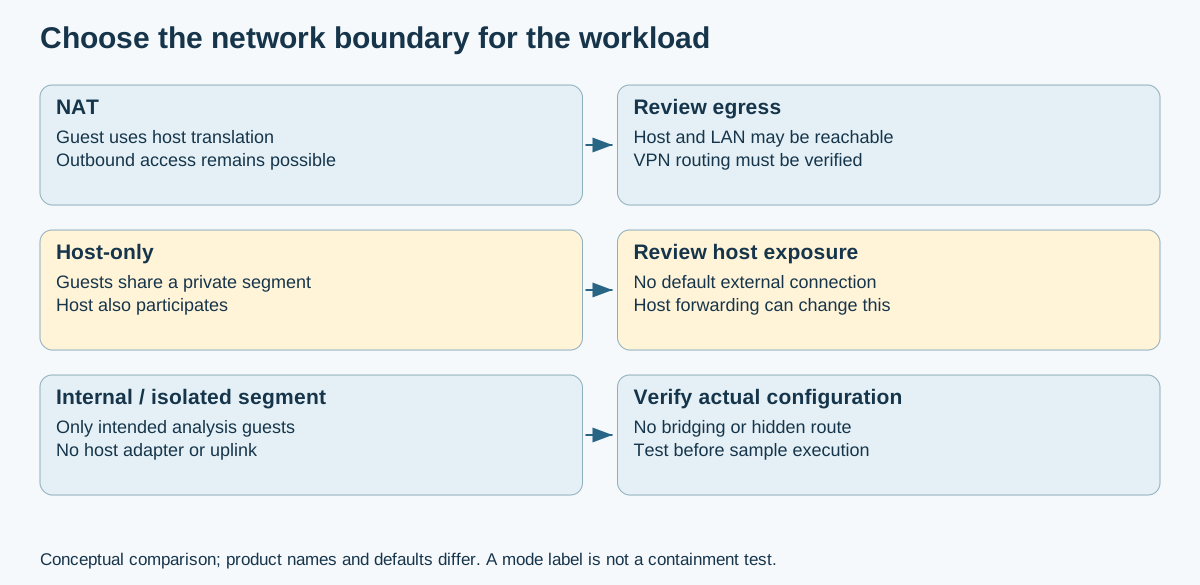
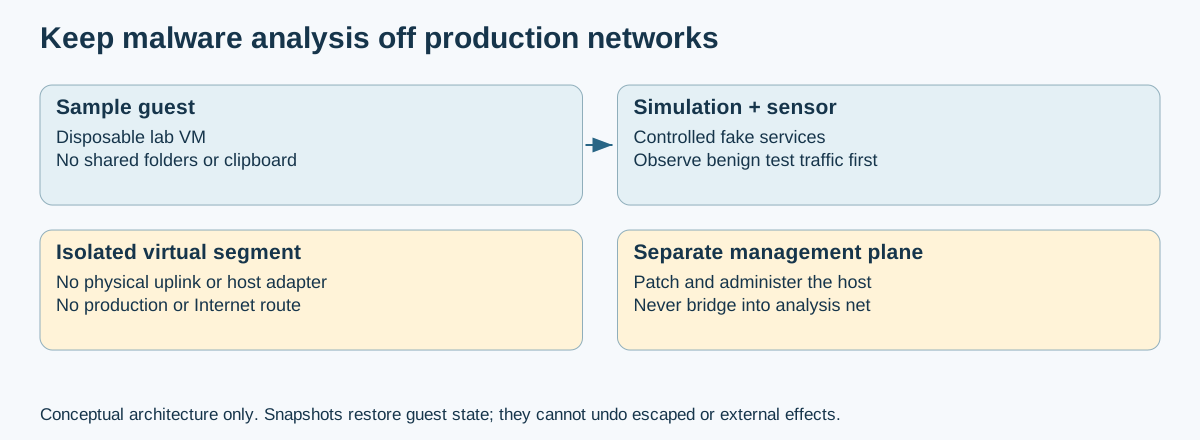
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| docker operations data lifetimes | Guide |
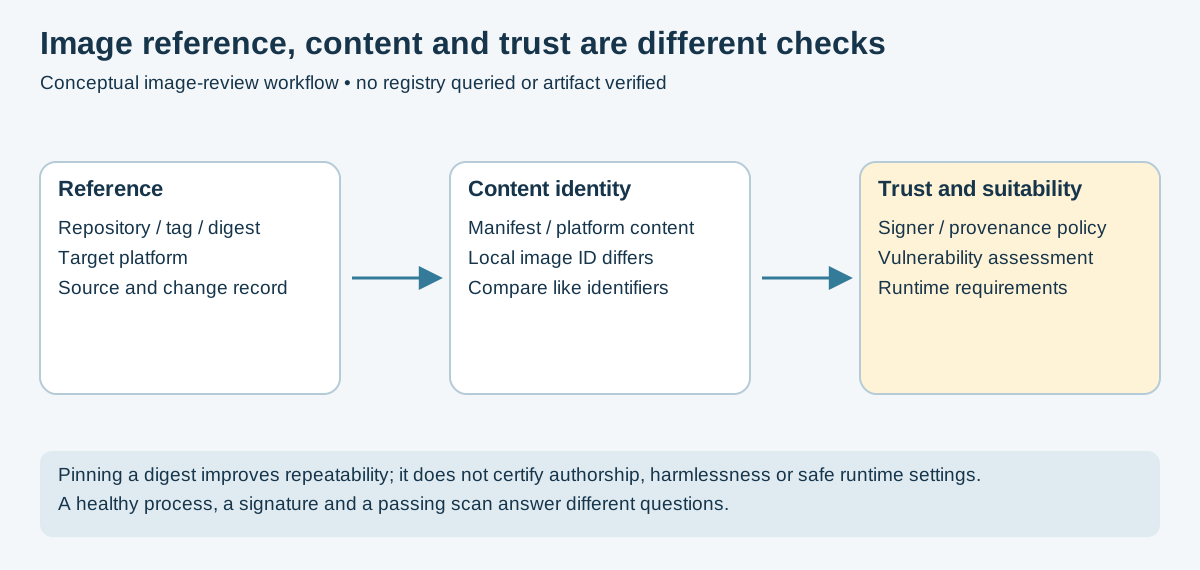
| docker operations image review | Guide |
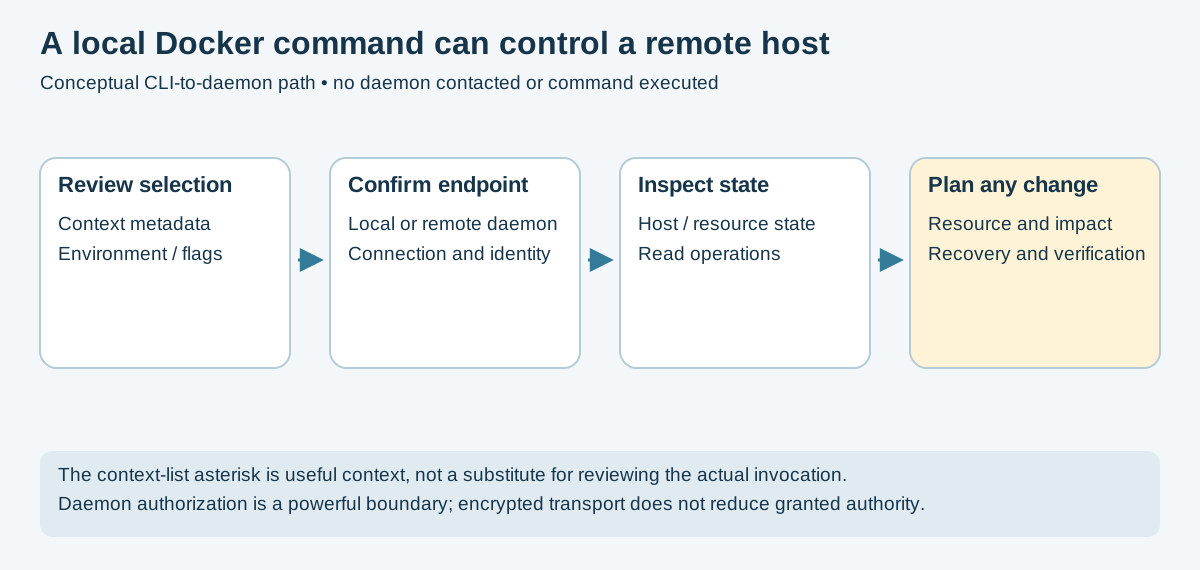
| docker operations context control | Guide |
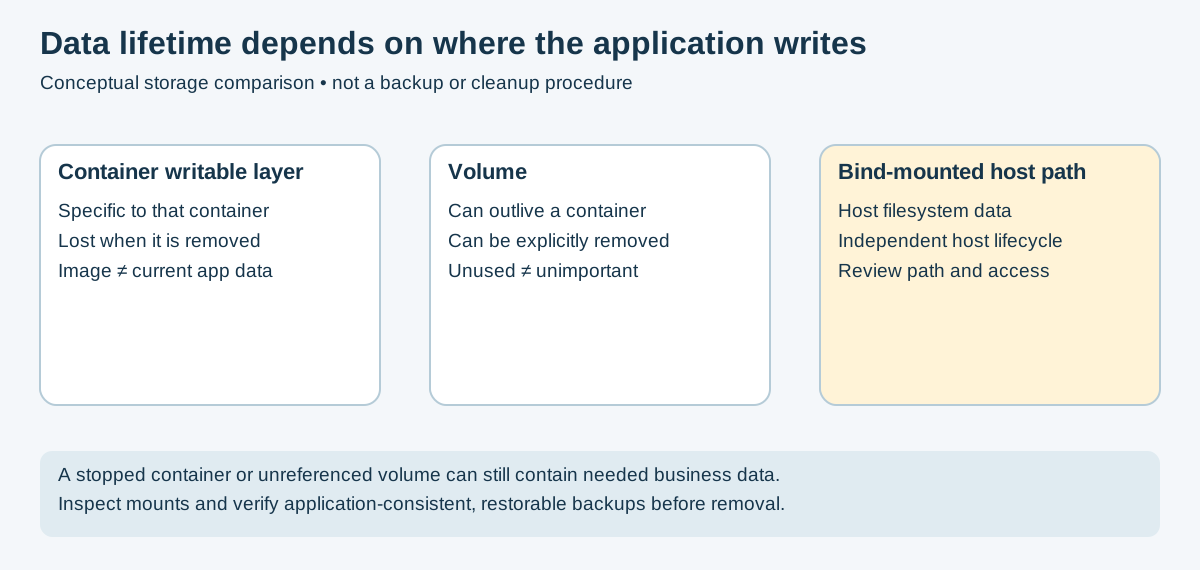
| Diagram | Embedded guide |
|---|---|
| Volatility evidence triage | Volatility 3 memory forensics |
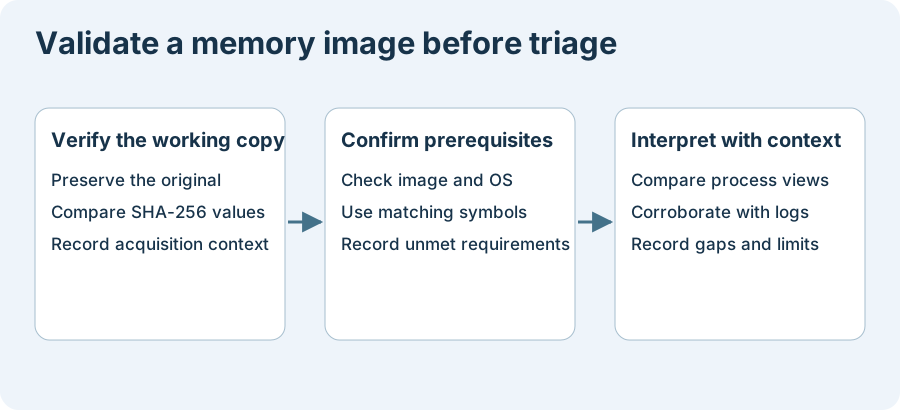
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| applied crypto tls boundaries | Guide |
| applied crypto envelope rotation | Guide |
| applied crypto presence verification | Guide |
| applied crypto authentication records | Guide |
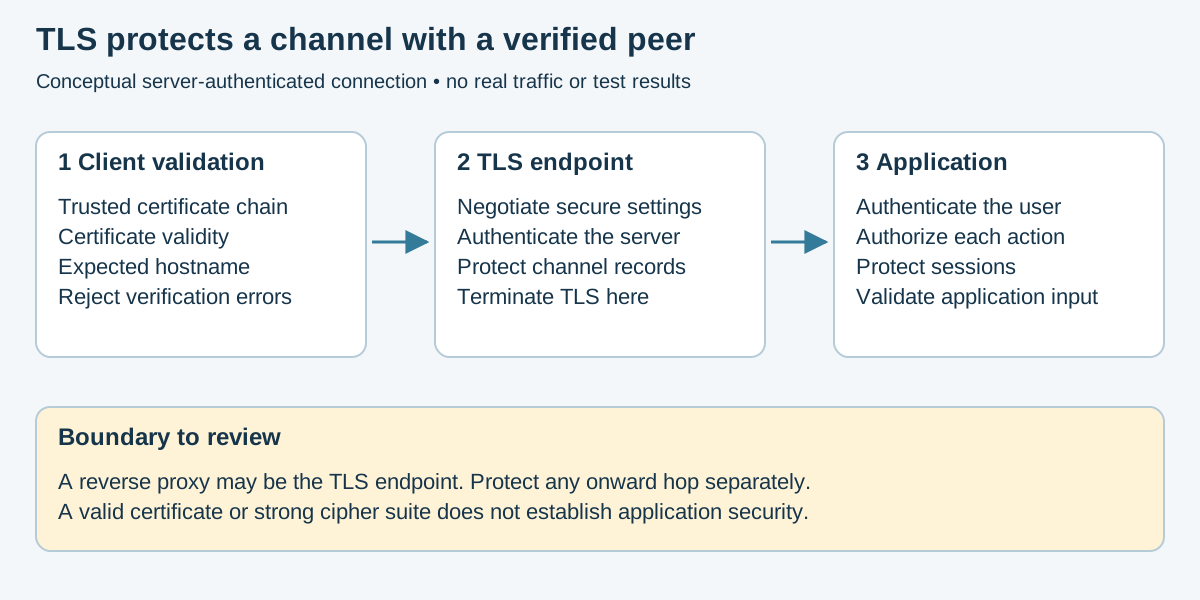
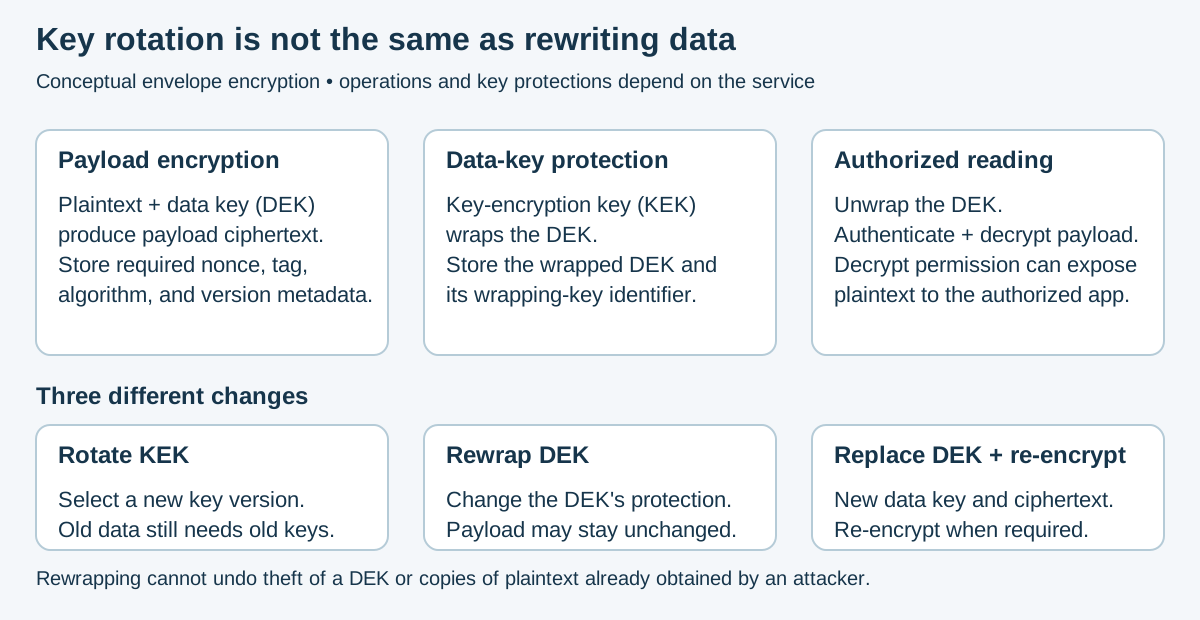
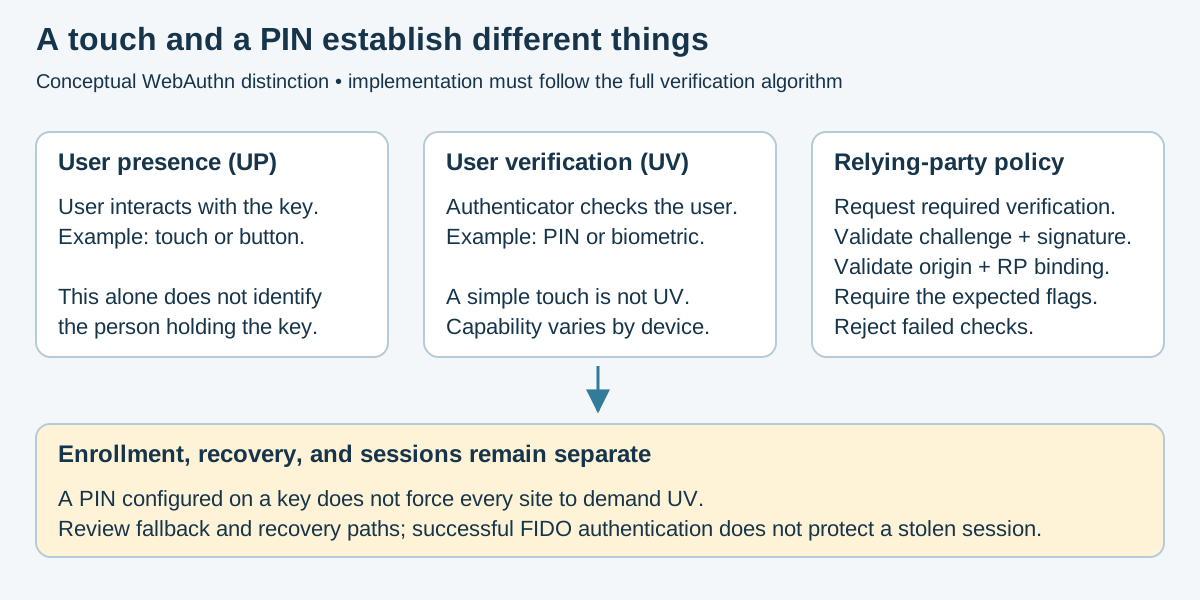
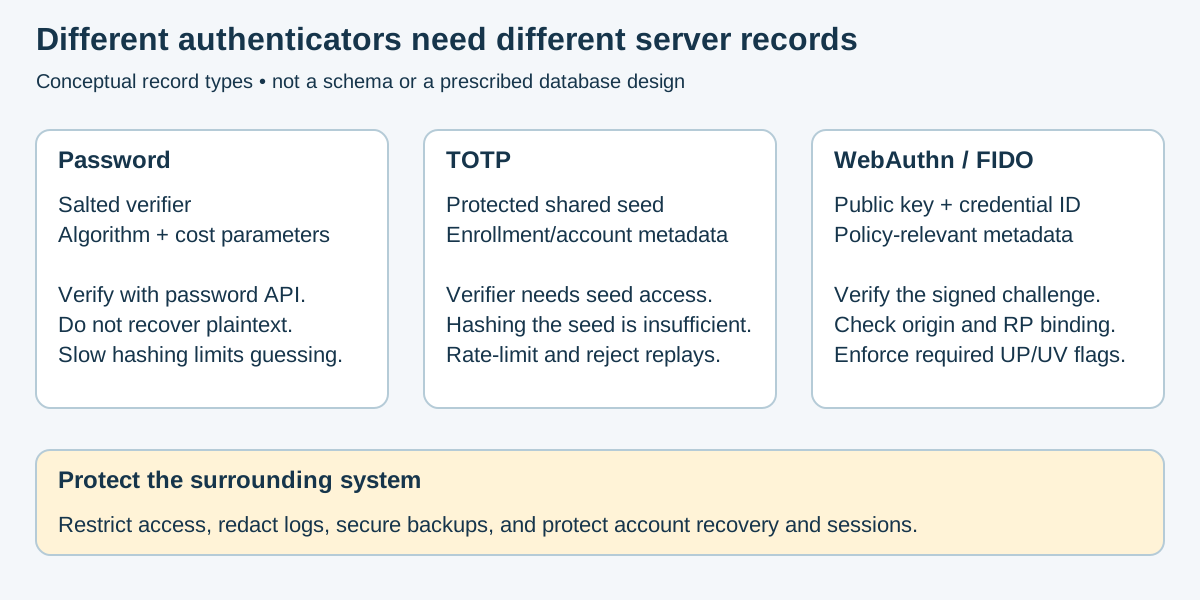
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Where embedded | Why it belongs |
|---|---|---|
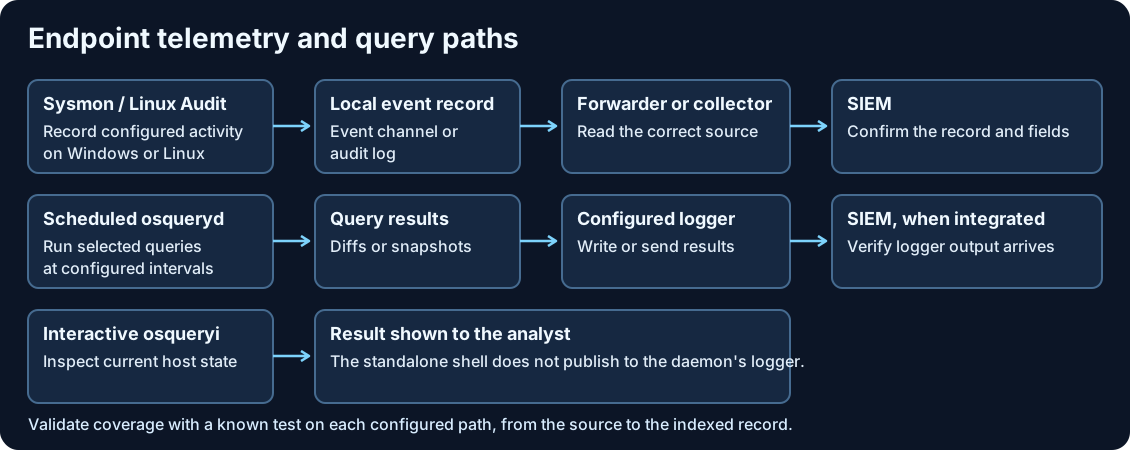
| Endpoint telemetry and query paths | Endpoint Visibility index | Distinguishes event streams, scheduled query logging, and interactive results |
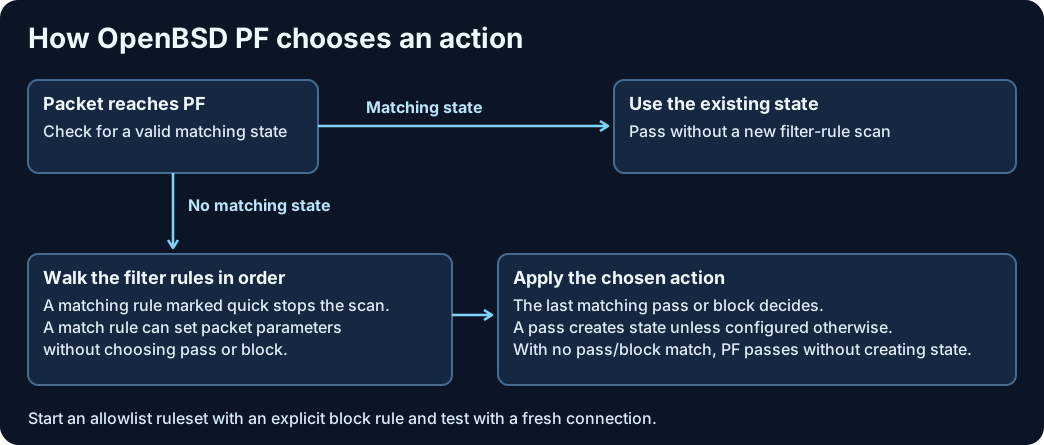
| OpenBSD PF state and rule flow | OpenBSD PF guide | Shows when PF uses existing state and when ordered filter rules decide the action |
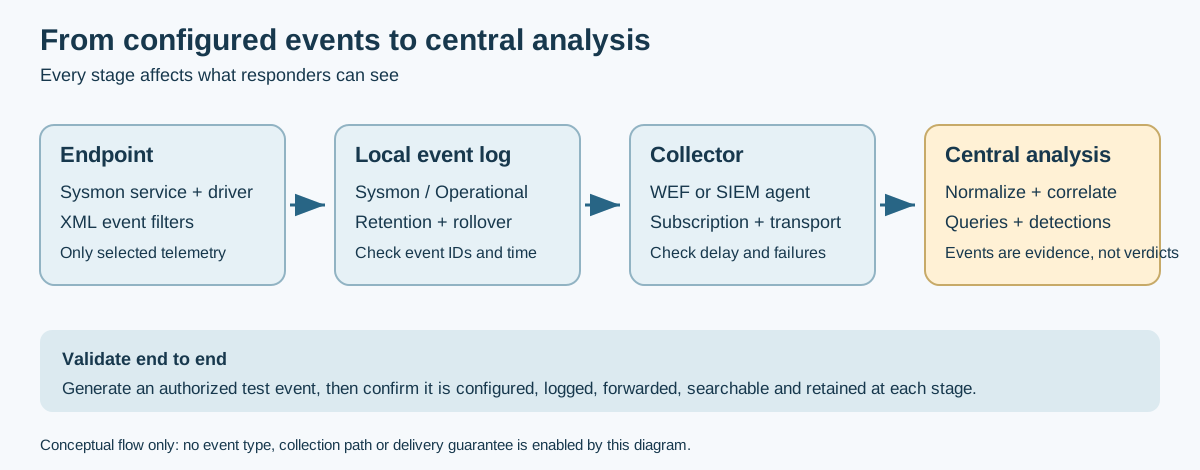
Original conceptual flow of configured events through Windows Event Log to a collector; actual coverage depends on configuration and retention.
| Diagram | Embedded guide |
|---|---|
| Sysmon telemetry coverage flow | Windows Sysmon Deployment Guide |
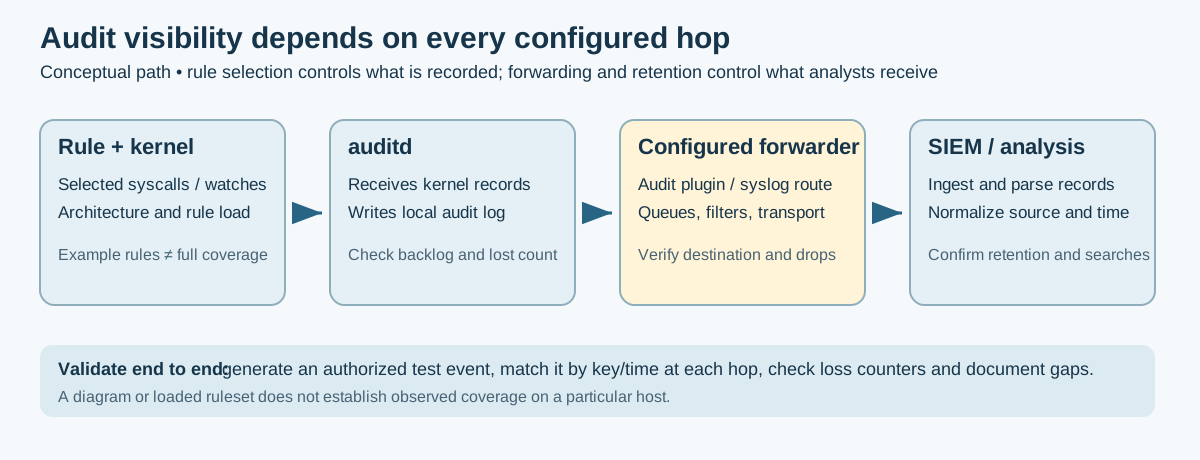
Original conceptual flow from audit rules through local collection and configured forwarding; verify every hop and document losses.
| Diagram | Embedded guide |
|---|---|
| Linux audit event flow | Linux Auditd & Syslog Hardening Guide |
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| log aggregation transport controls | Guide |
| log aggregation pipeline contracts | Guide |
| log aggregation time provenance | Guide |
| log aggregation end to end validation | Guide |
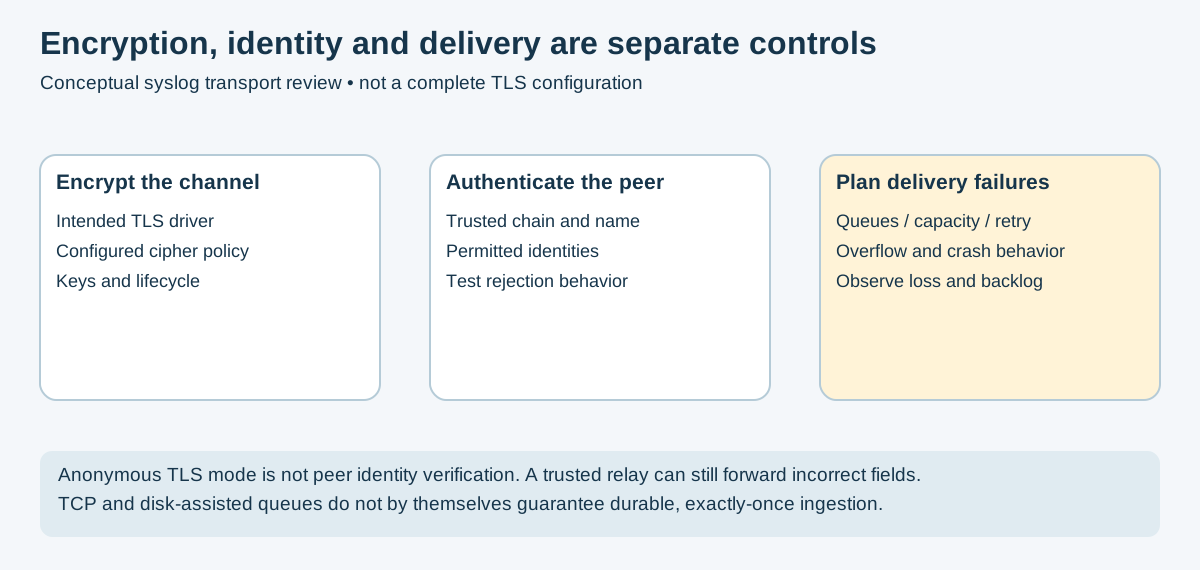
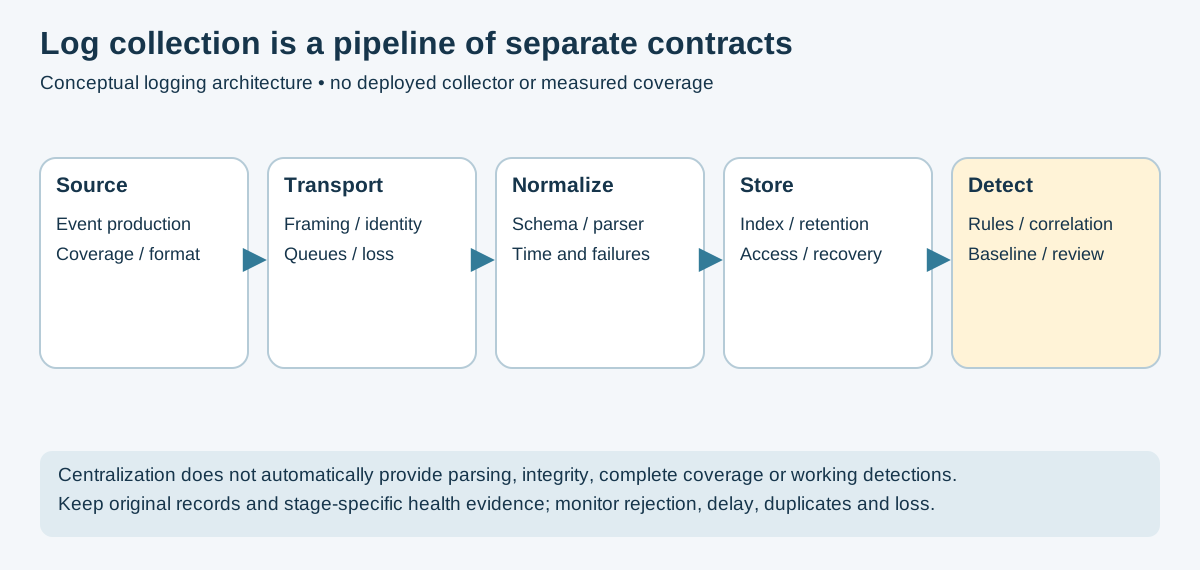
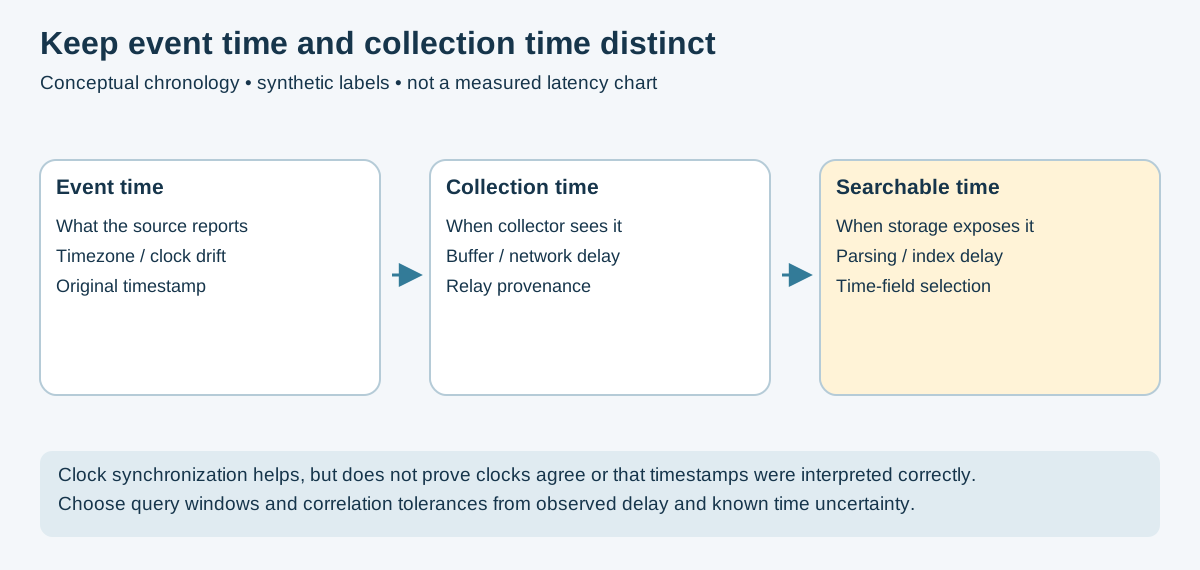
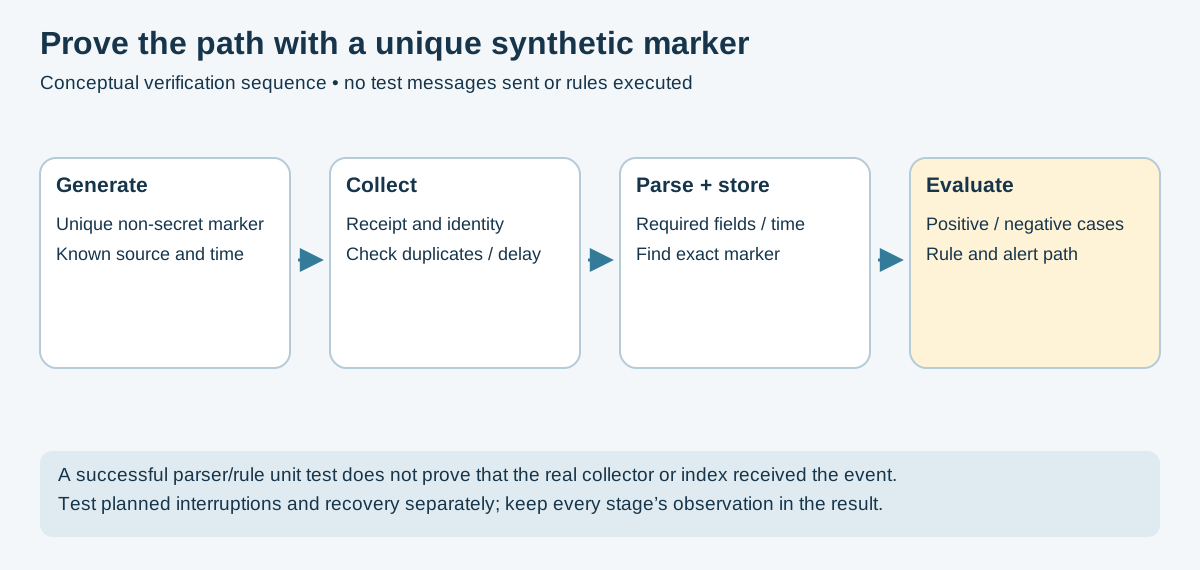
These 19 newly authored diagrams provide short conceptual overviews beside the relevant guide sections. Each SVG contains a built-in title and description, uses local fonts and shapes only, and deliberately avoids asserting that a particular device, network or lab was tested.
| Diagram | Embedded guide | Purpose |
|---|---|---|
| SIEM telemetry correlation | IncidentResponse/SIEM/README.md | Collect, normalize, correlate and validate events |
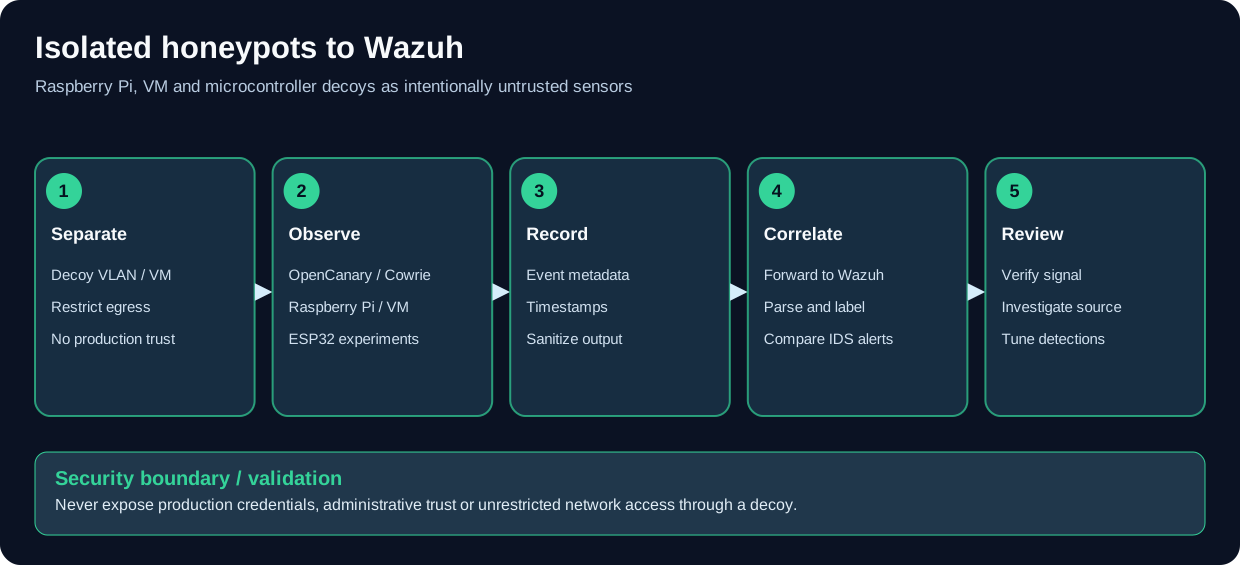
| Honeypot sensor isolation | IncidentResponse/HoneyPot/readme.md | Decoy isolation, log ingestion and safe triage |
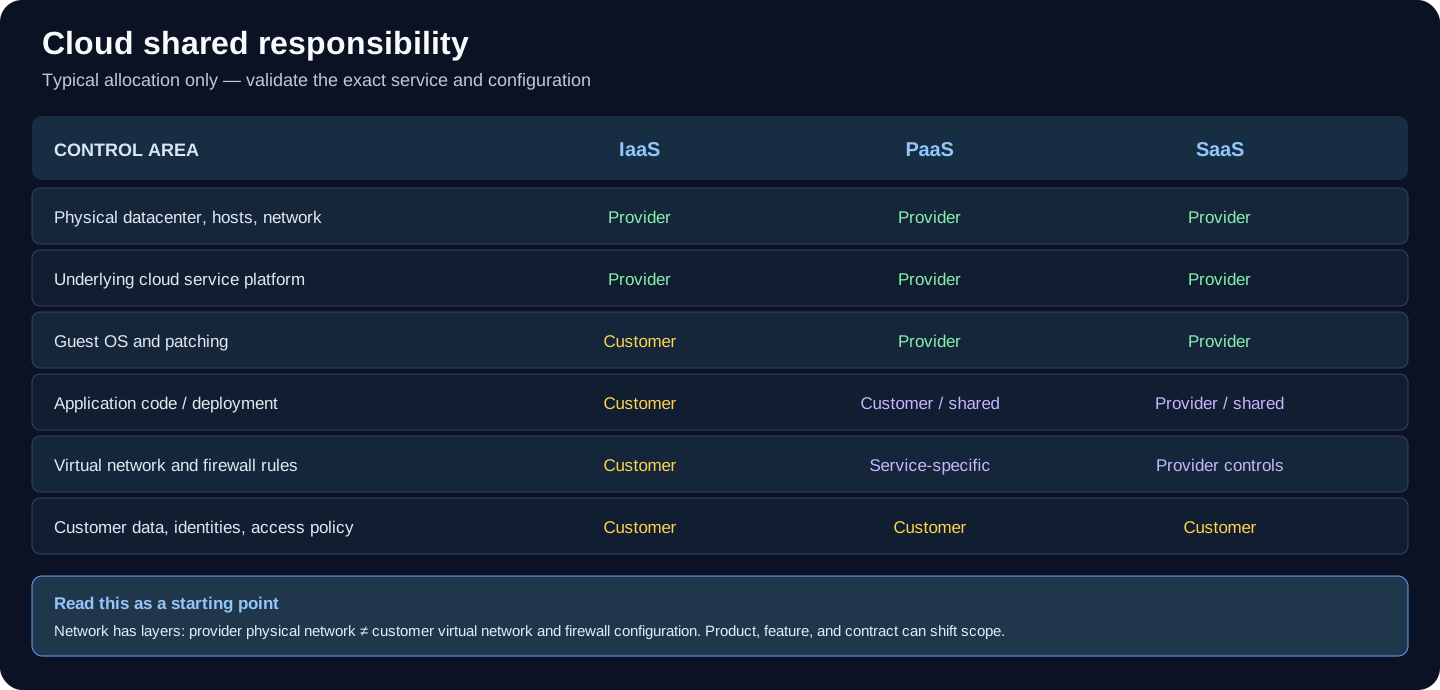
| Cloud shared responsibility | Cloud/README.md | Provider/customer security responsibilities |
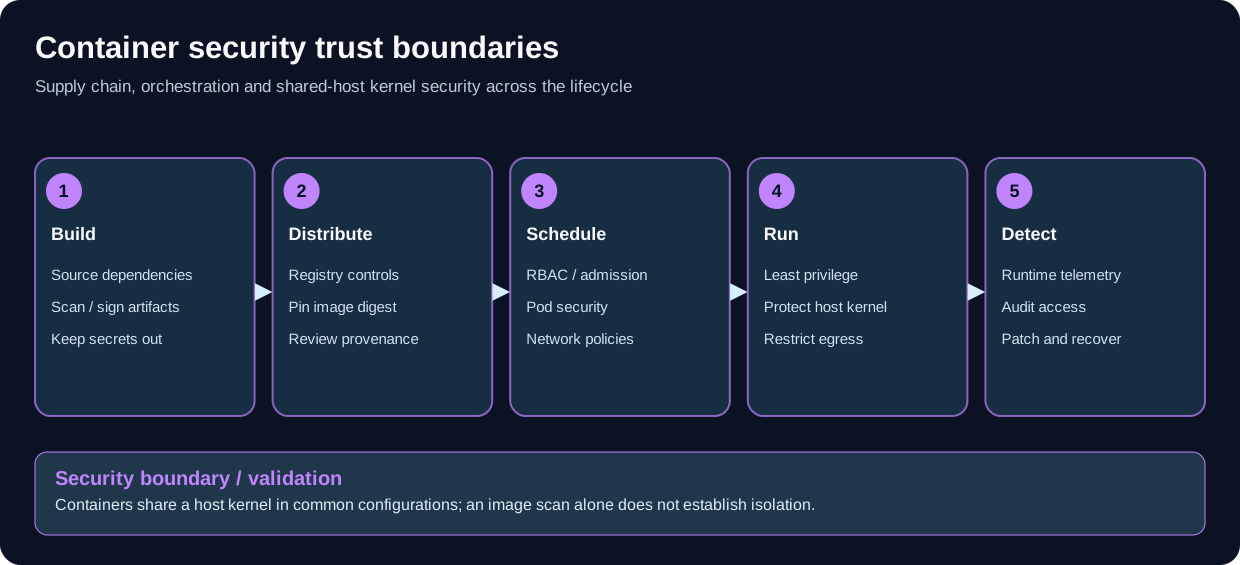
| Container trust boundaries | ContainerSecurity/README.md | Supply chain and shared-kernel risks |
| DFIR evidence lifecycle | IncidentResponse/Digital-Forensics/README.md | Authorize, collect, verify, analyze and preserve |
| Autopsy and KAPE evidence workflows | Autopsy + KAPE guide | Separate disk imaging from selective artifact triage |
| OSINT verification | OSINT/README.md | Scope, corroborate, protect sources and report |
| Wireless IDS correlation | IncidentResponse/IDS&IPS/readme.md | Kismet/nzyme event correlation and evidence checks |
| Web application testing | WebAppSecurity/README.md | Scope through retest with safe validation |
| GRC control evidence | Compliance/README.md | Risk, mapping, control implementation and testing |
| Reverse engineering | ReverseEngineering/README.md | Sample intake to defensible findings |
| Space system segments | SpaceSecurity/README.md | Ground, comms, spacecraft and user trust boundaries |
| GNSS authentication and integrity boundaries | SpaceSecurity GNSS chapter | Distinguish message authentication, integrity checks, and interference indicators |
| Wardriving data handling | Wardriving/README.md | Passive survey quality, privacy and disclosure |
| Data pipeline reliability | Data-Engineering/Phase2/README.md | Contract, transformations, security and replay |
| NanoVNA calibration | SDR/nanovna/README.md | Measurement reference plane and uncertainty |
| Mobile security layers | Mobile/README.md | Device, account, app, network and backups |
| Incident response stages | IncidentResponse/README.md | Preparation through recovery and improvement |
| Assessment checklist lifecycle | Checklists | Authorization, coverage, evidence, QA and closure |
| Safe script execution | Scripts | Code review, scope approval, rollback and results |
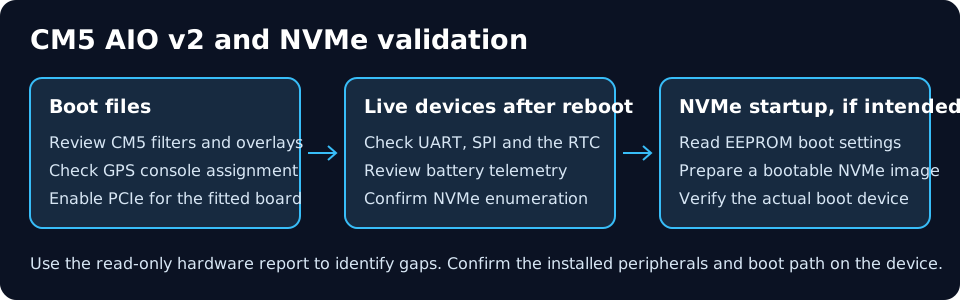
| CM5 AIO v2 and NVMe validation | CM5 Setup | Boot-file settings, live peripheral checks, and optional NVMe startup validation |
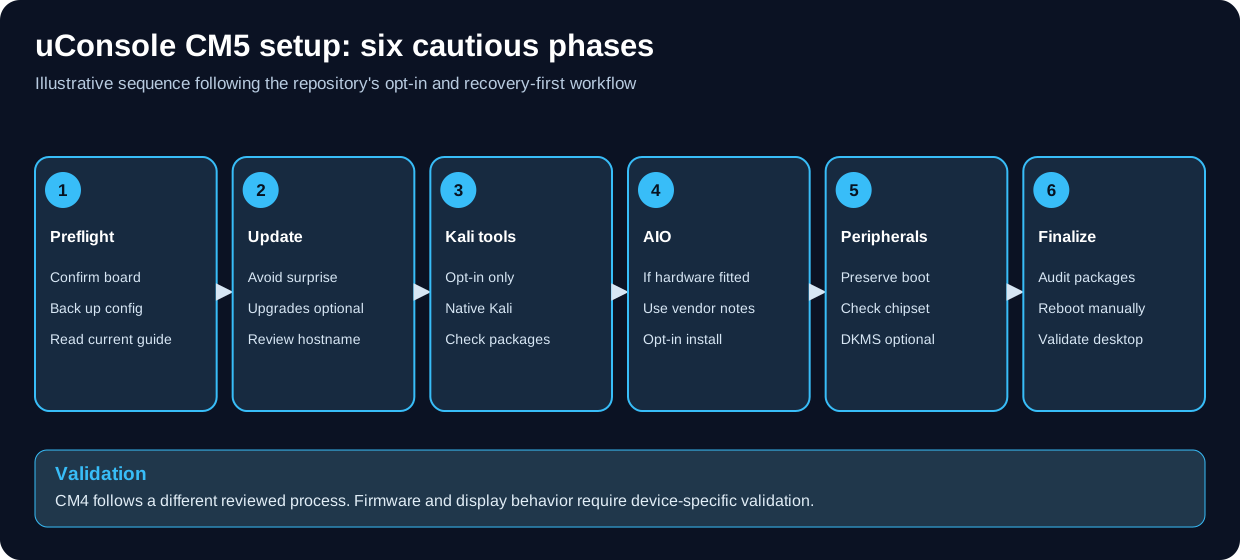
| uConsole cautious setup | uConsole | Model-aware, opt-in six-phase CM5 workflow |
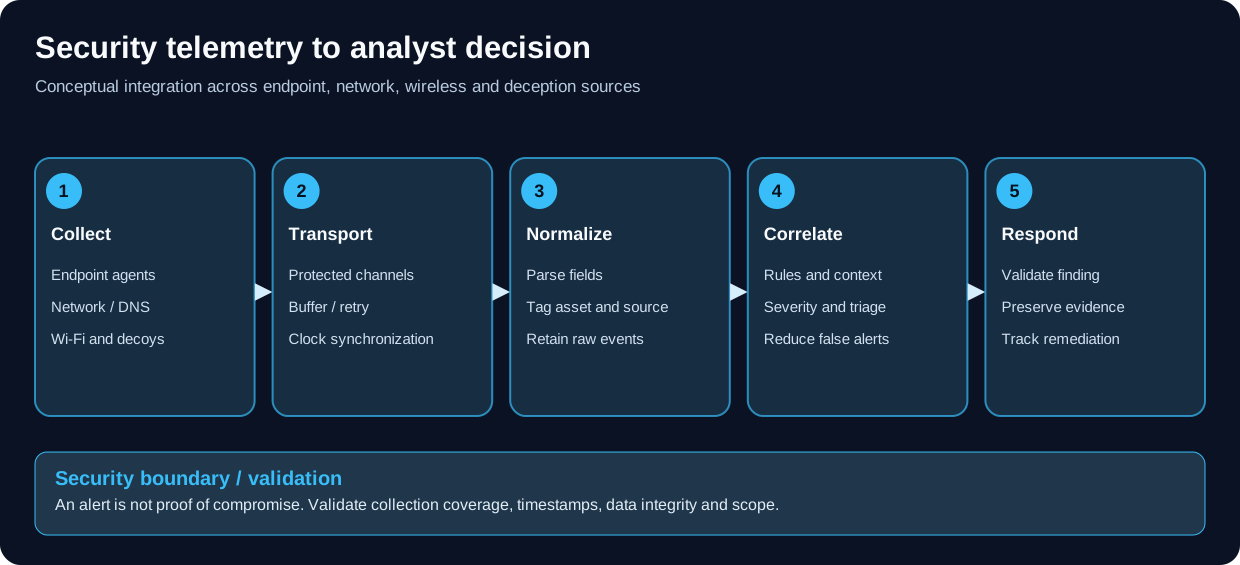
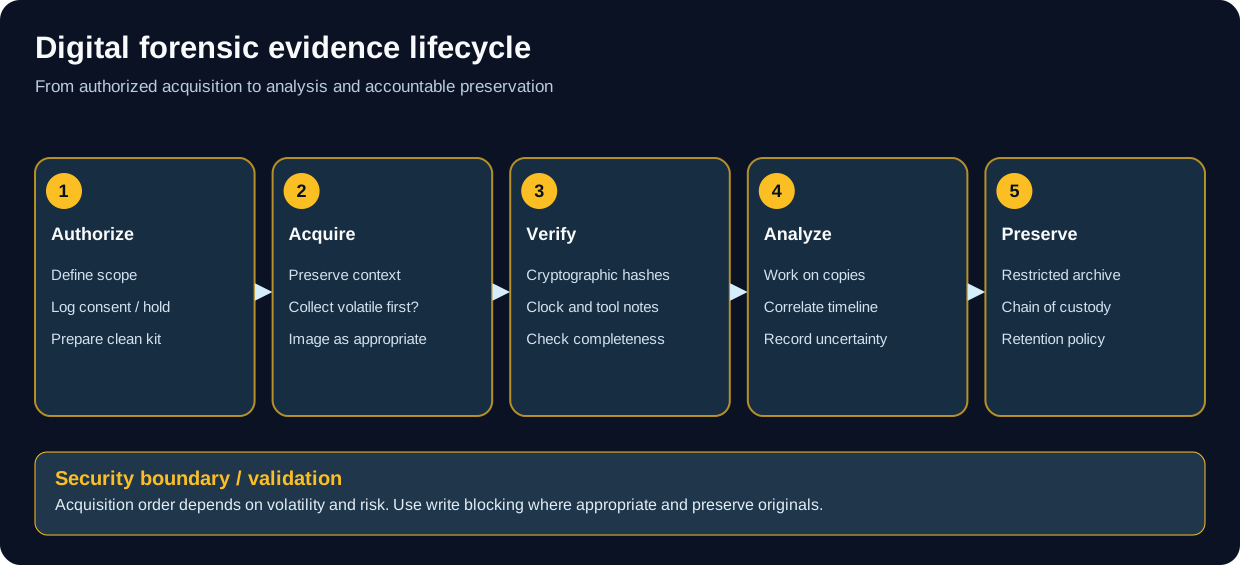
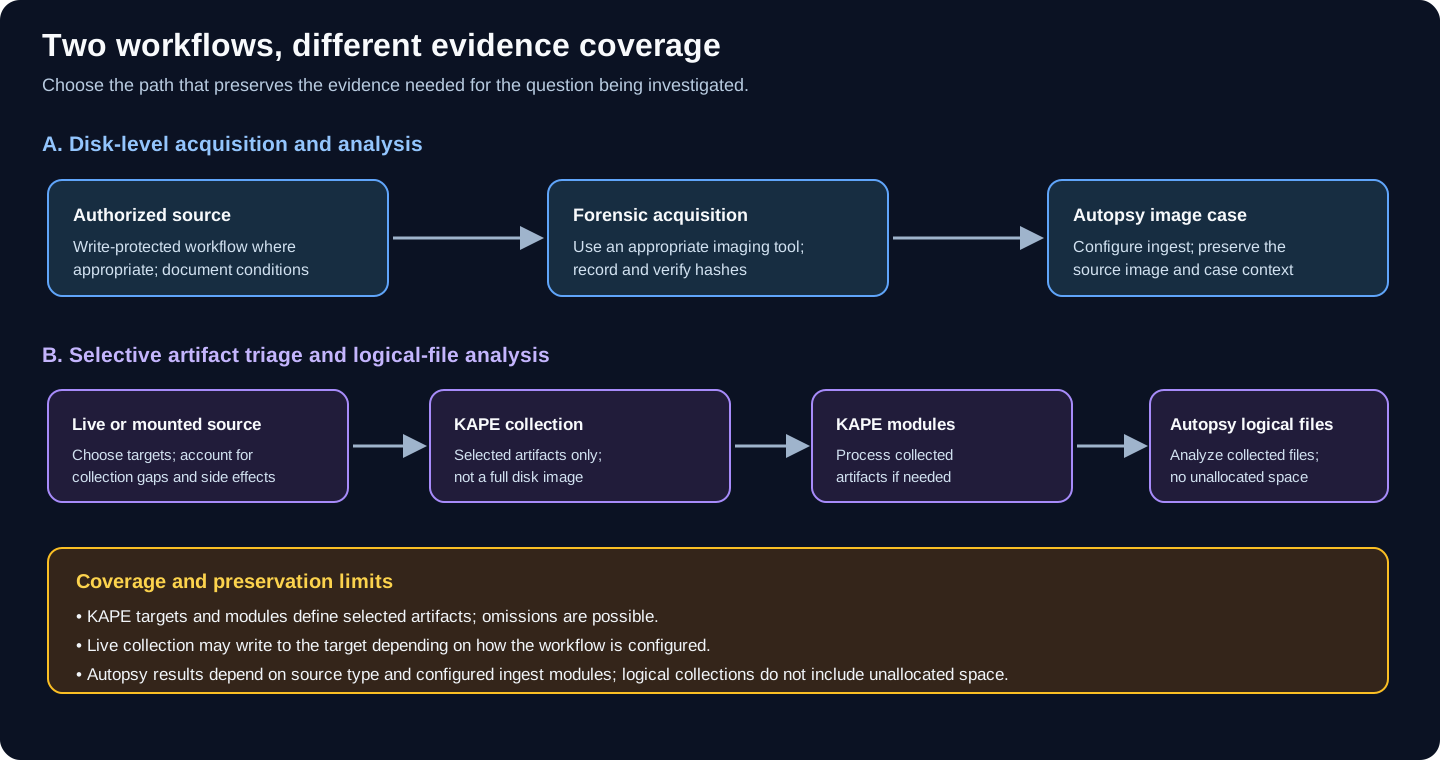
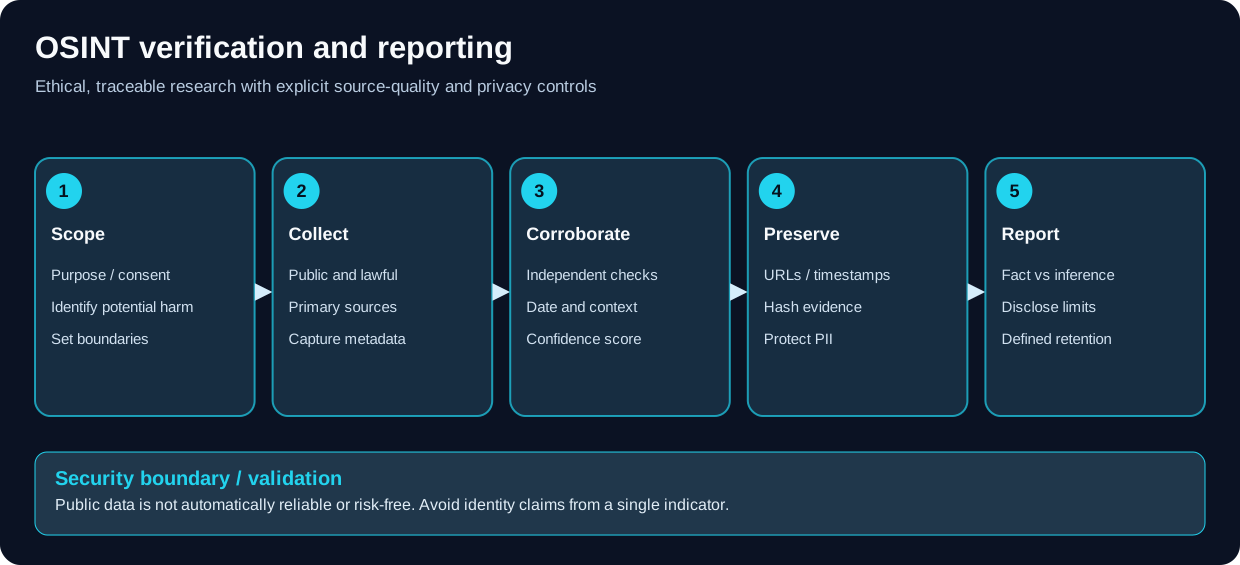
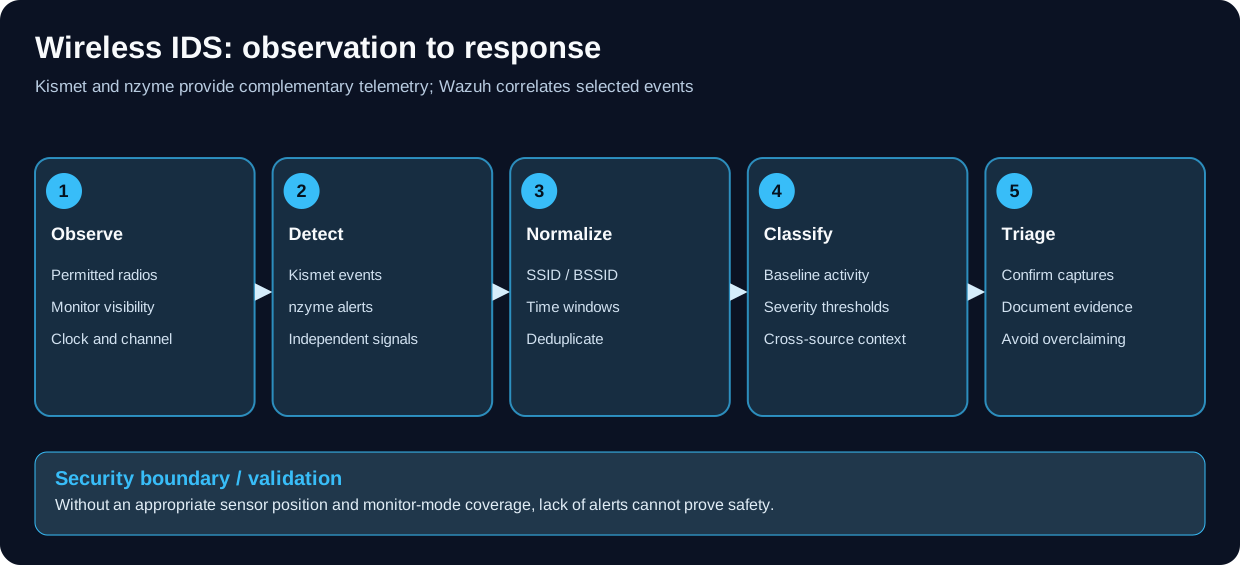
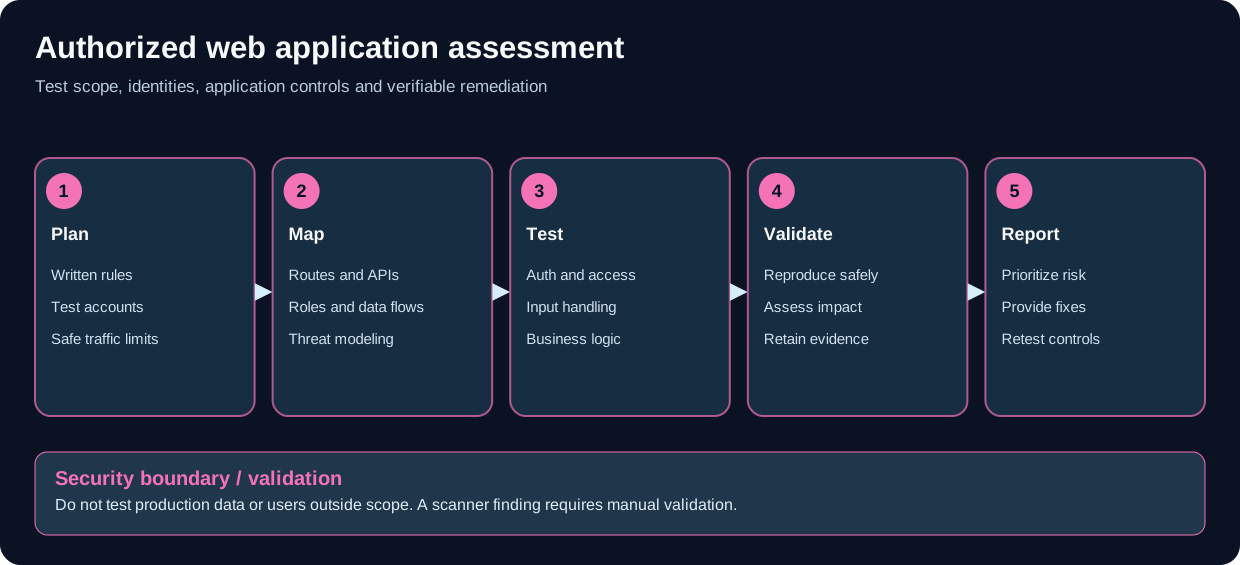
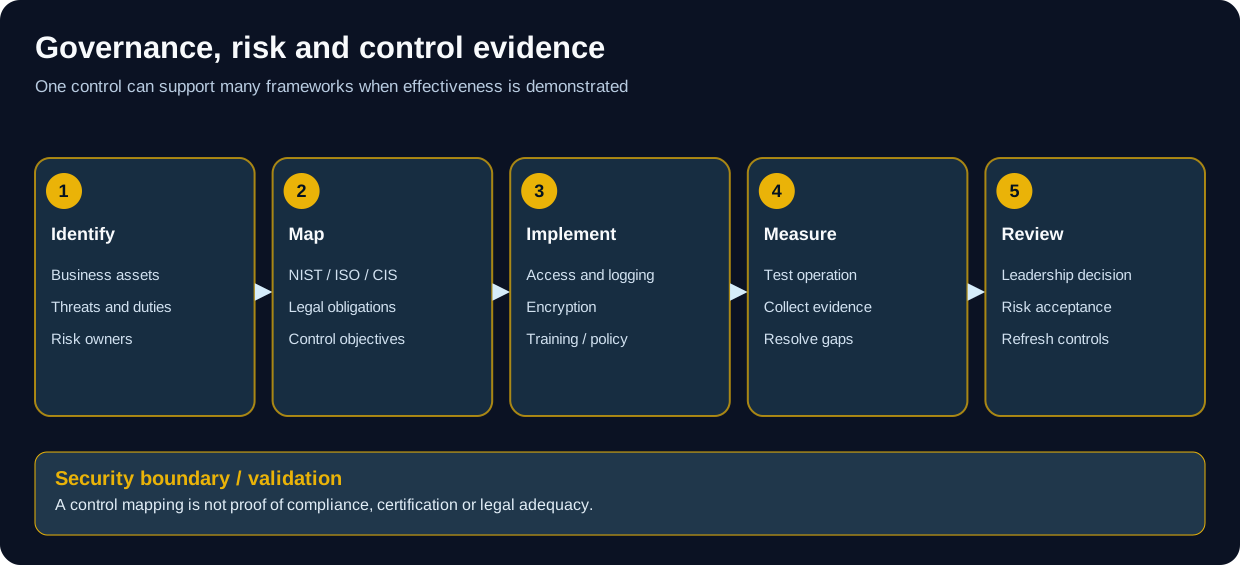
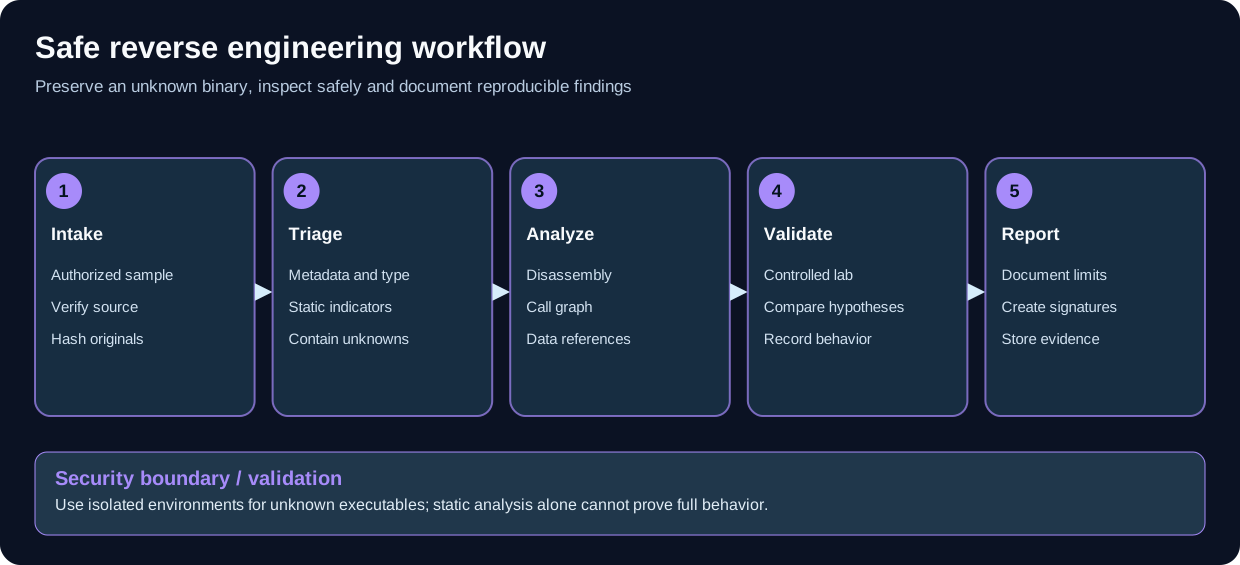
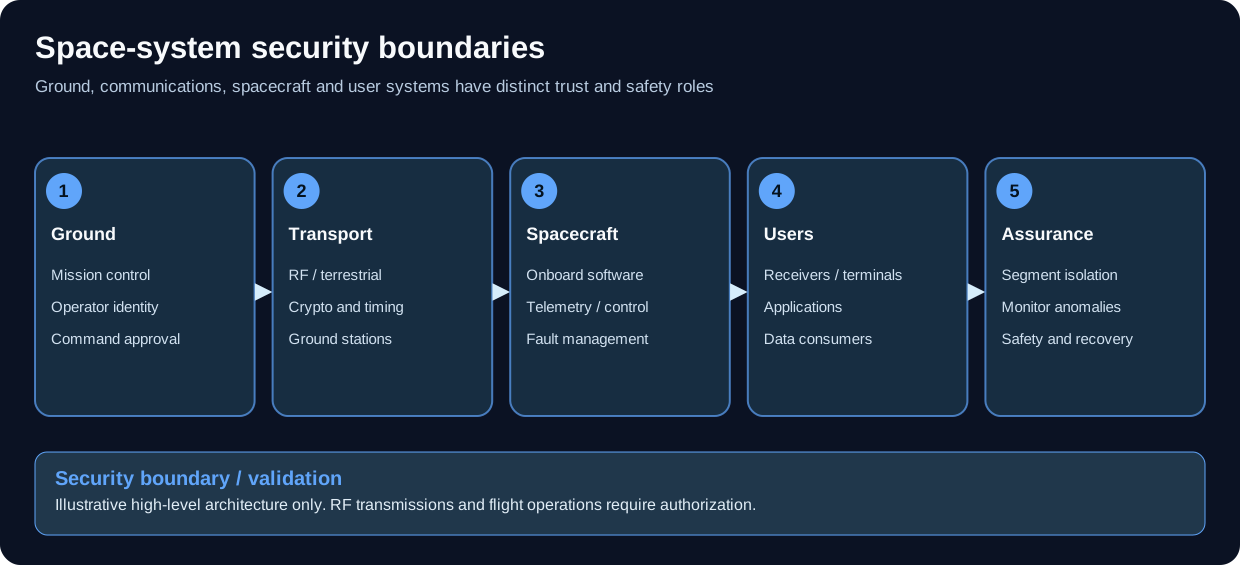
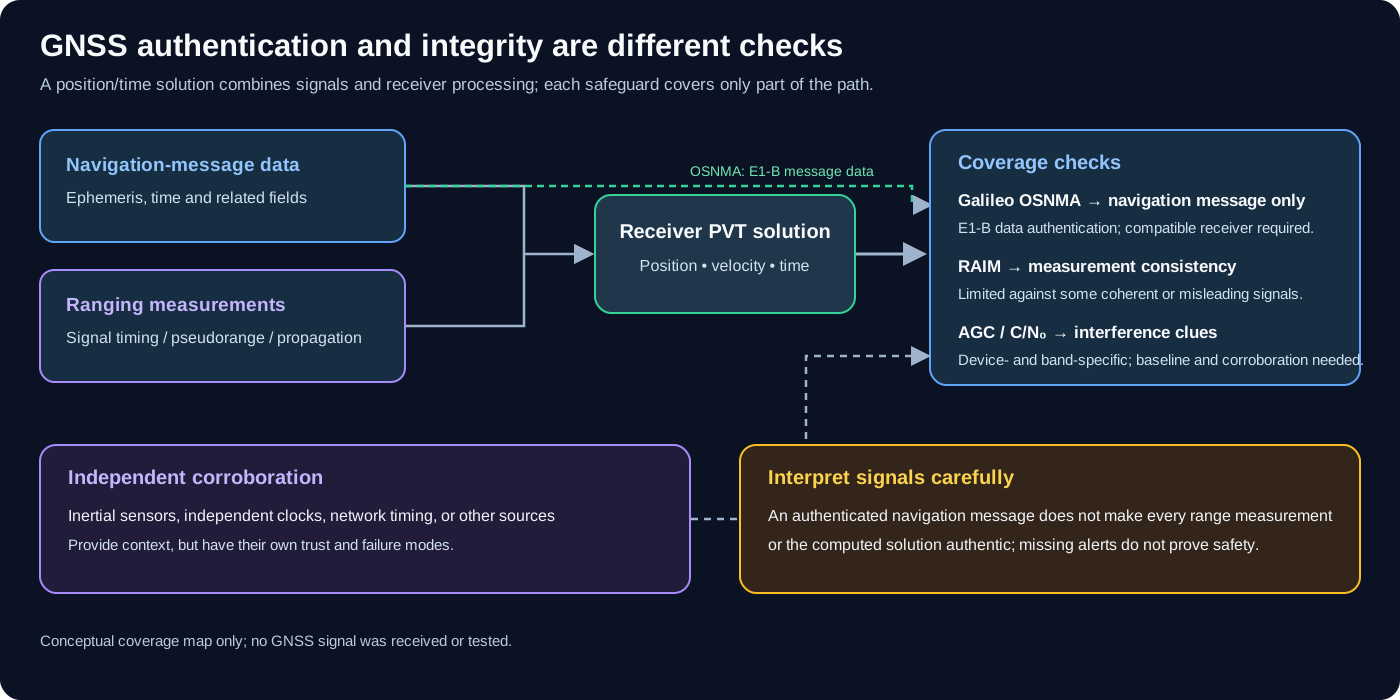
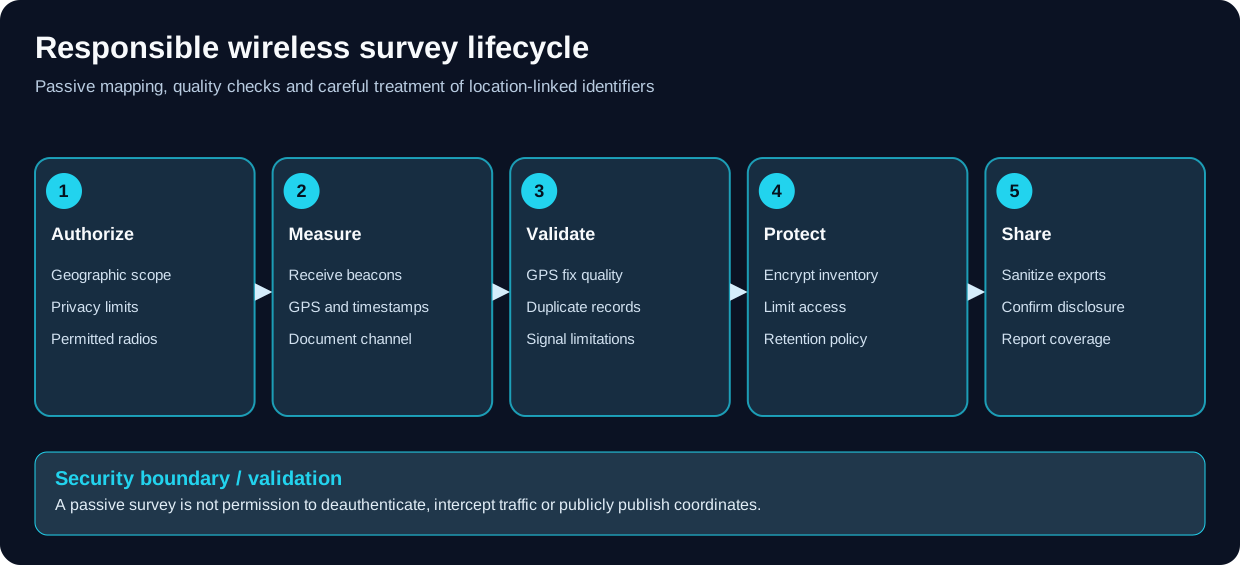
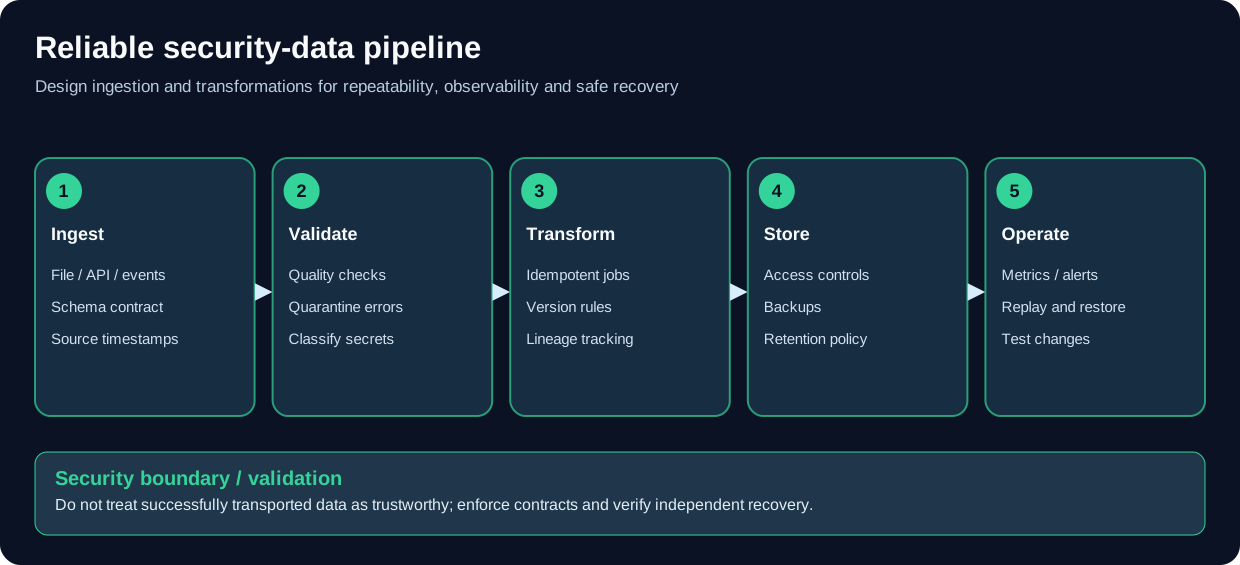
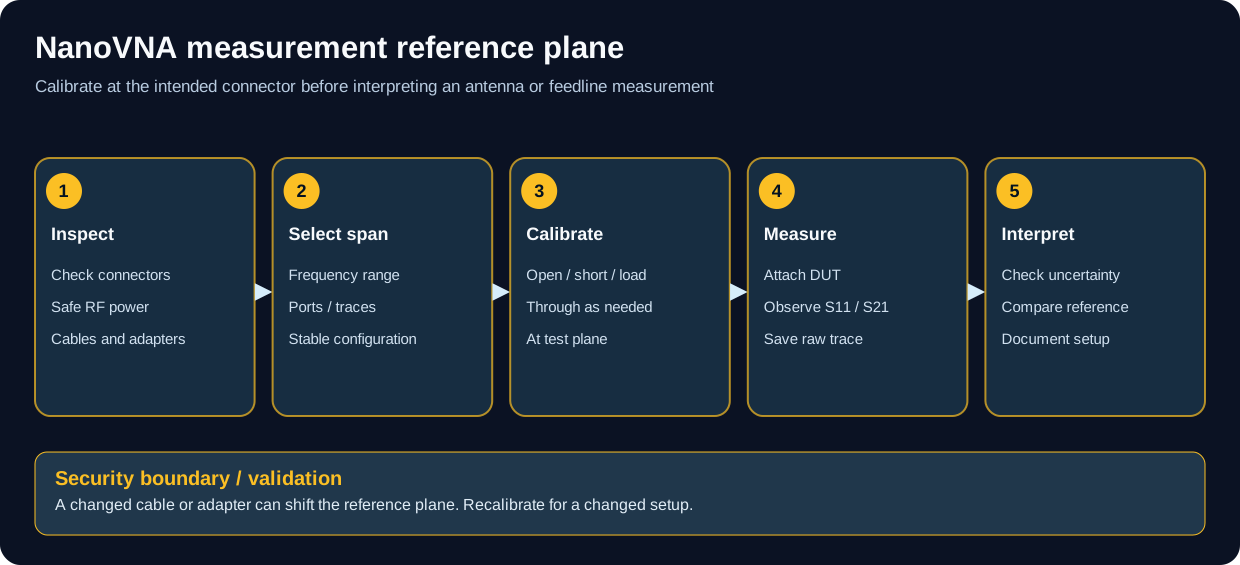
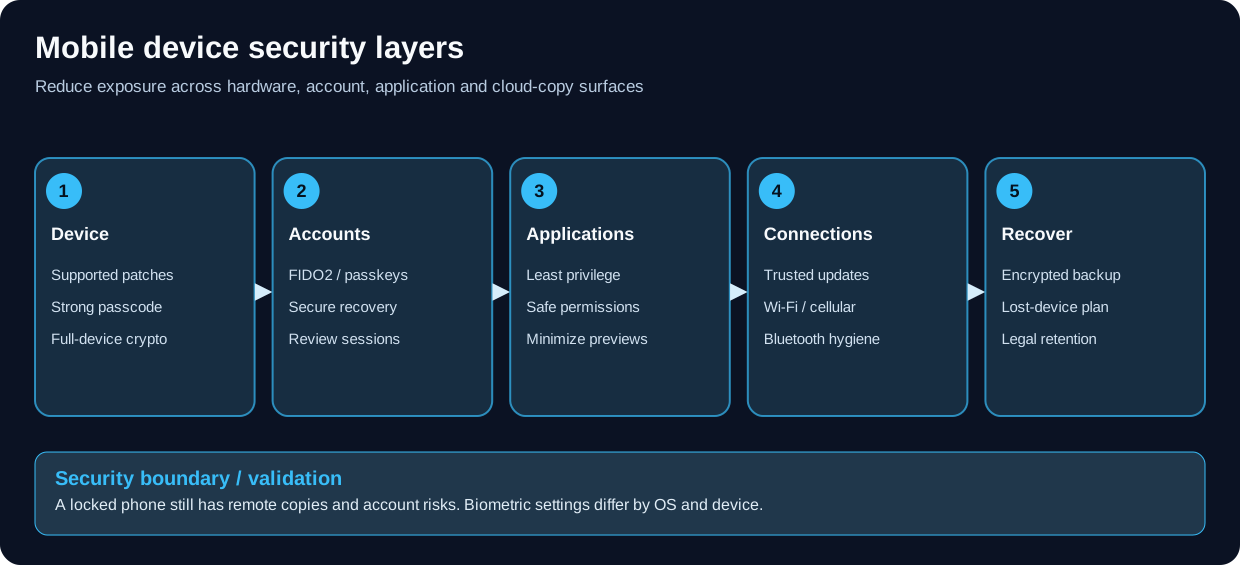
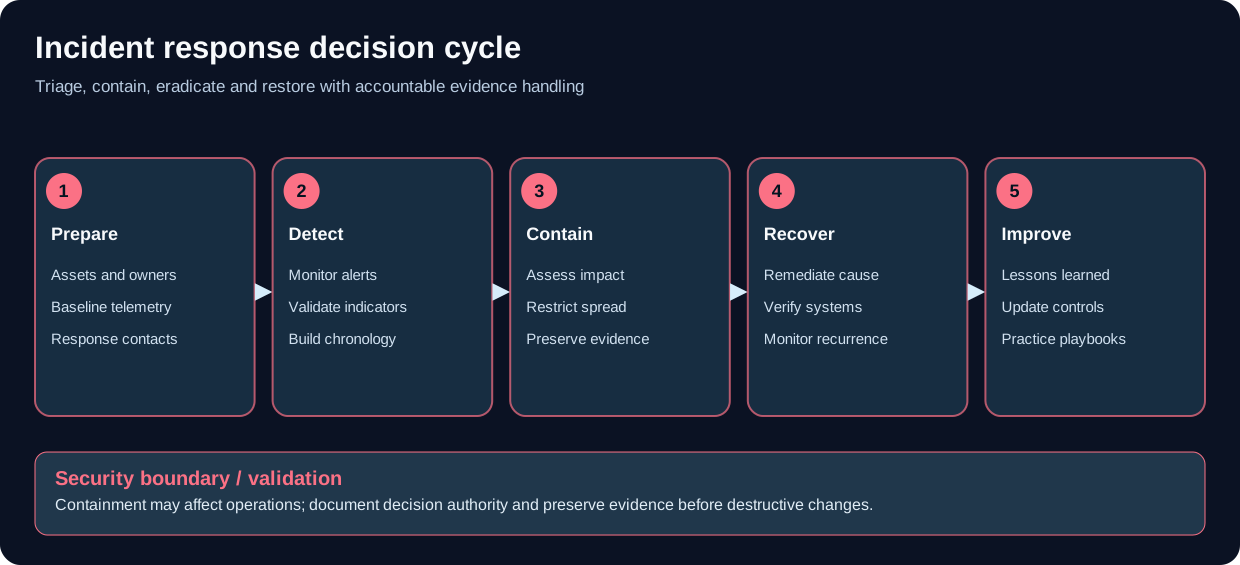
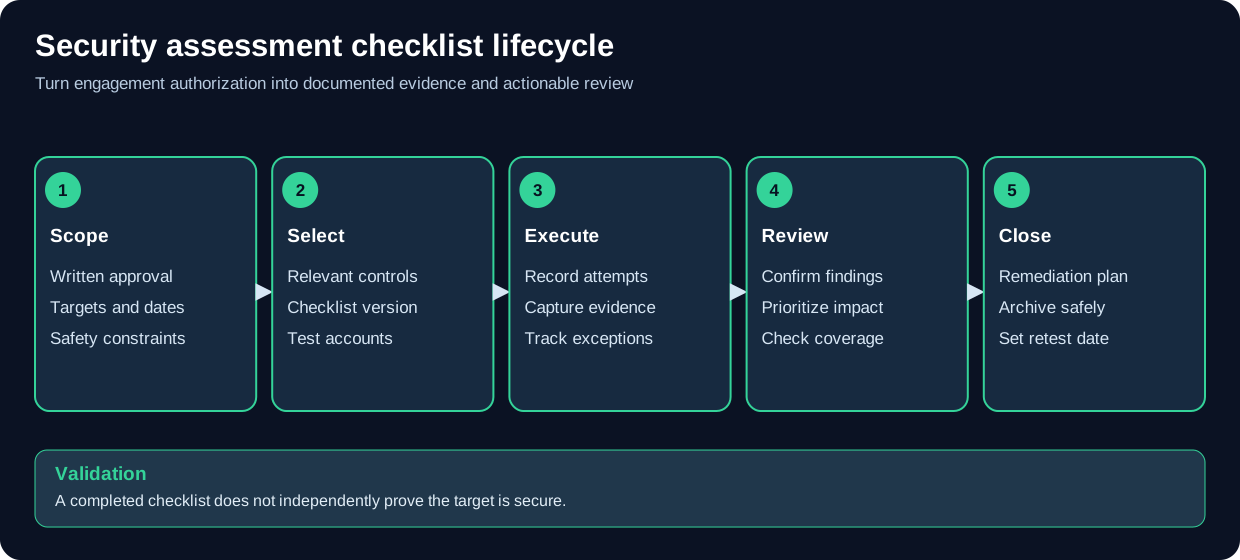
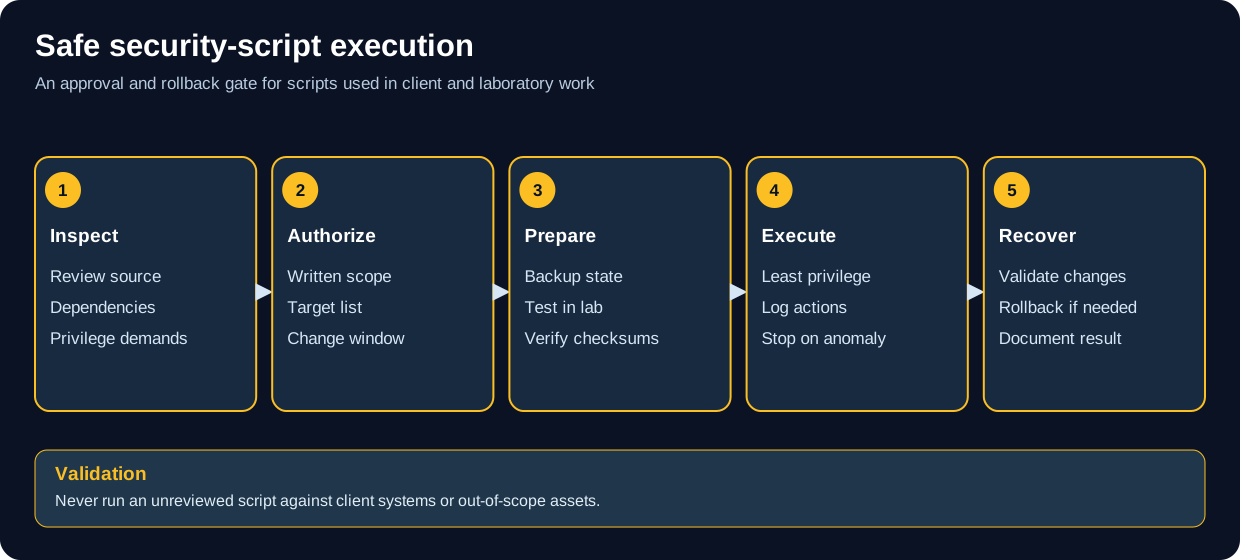
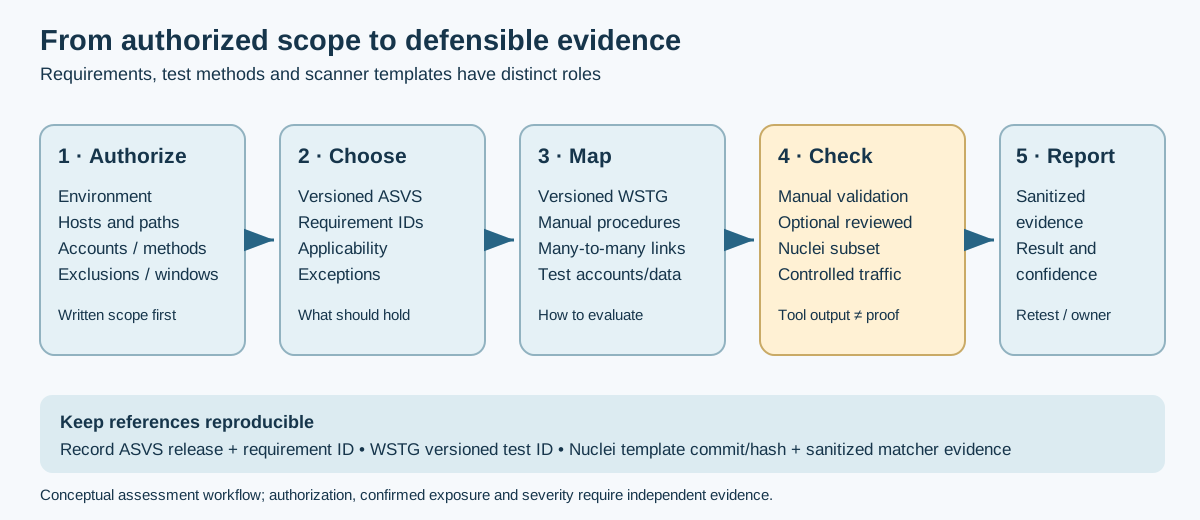
Original conceptual flow mapping authorization to versioned requirements, scoped tests, evidence and retesting.
| Diagram | Embedded guide |
|---|---|
| Web assessment requirement-to-evidence flow | OWASP standards and Nuclei review |
| Web assessment authorization and scope gates | Web testing methodology |
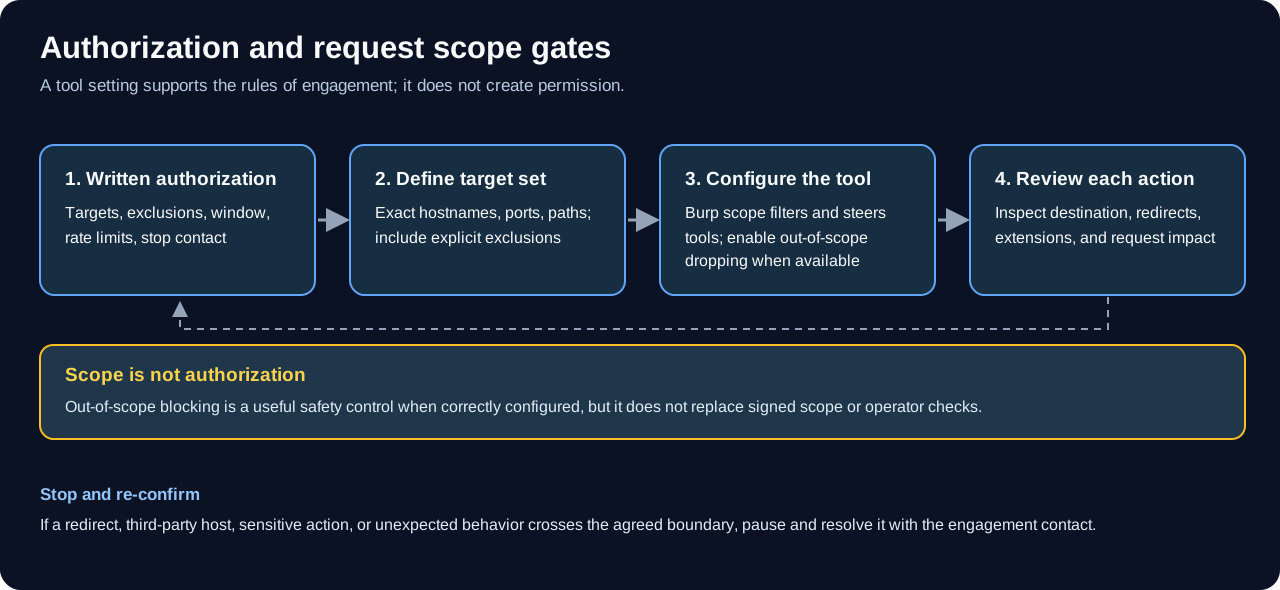
Original conceptual gates for approval, phase selection, evidence validation and closure.
| Diagram | Embedded guide |
|---|---|
| Assessment integration evidence gates | Staged security assessment integration map |
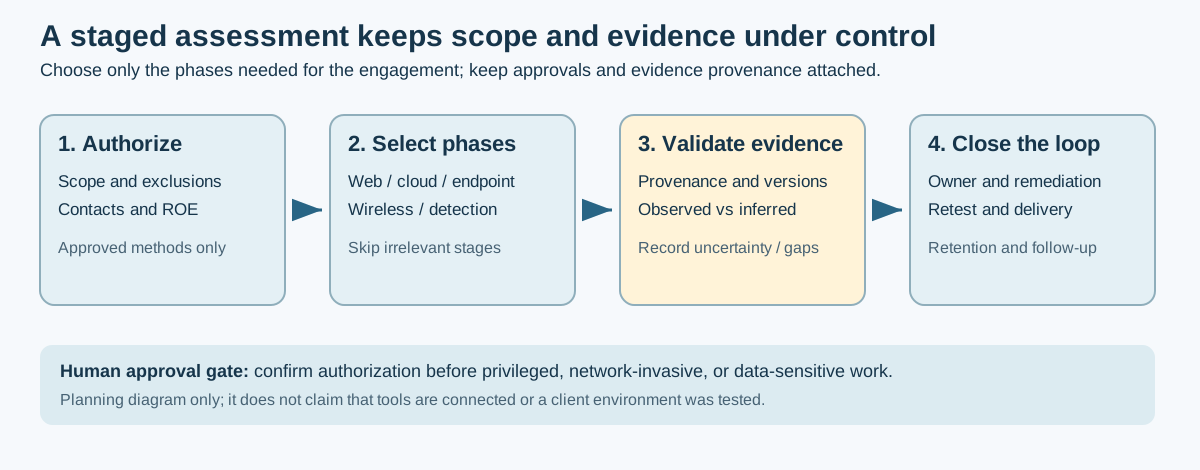
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| frameworks evidence reuse | Guide |
| privacy breach notification decision paths | Guide |
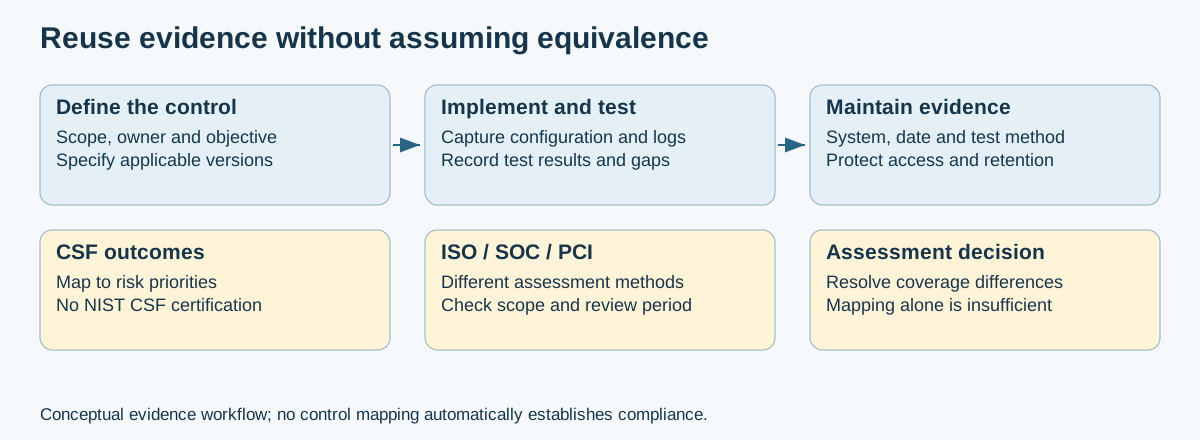
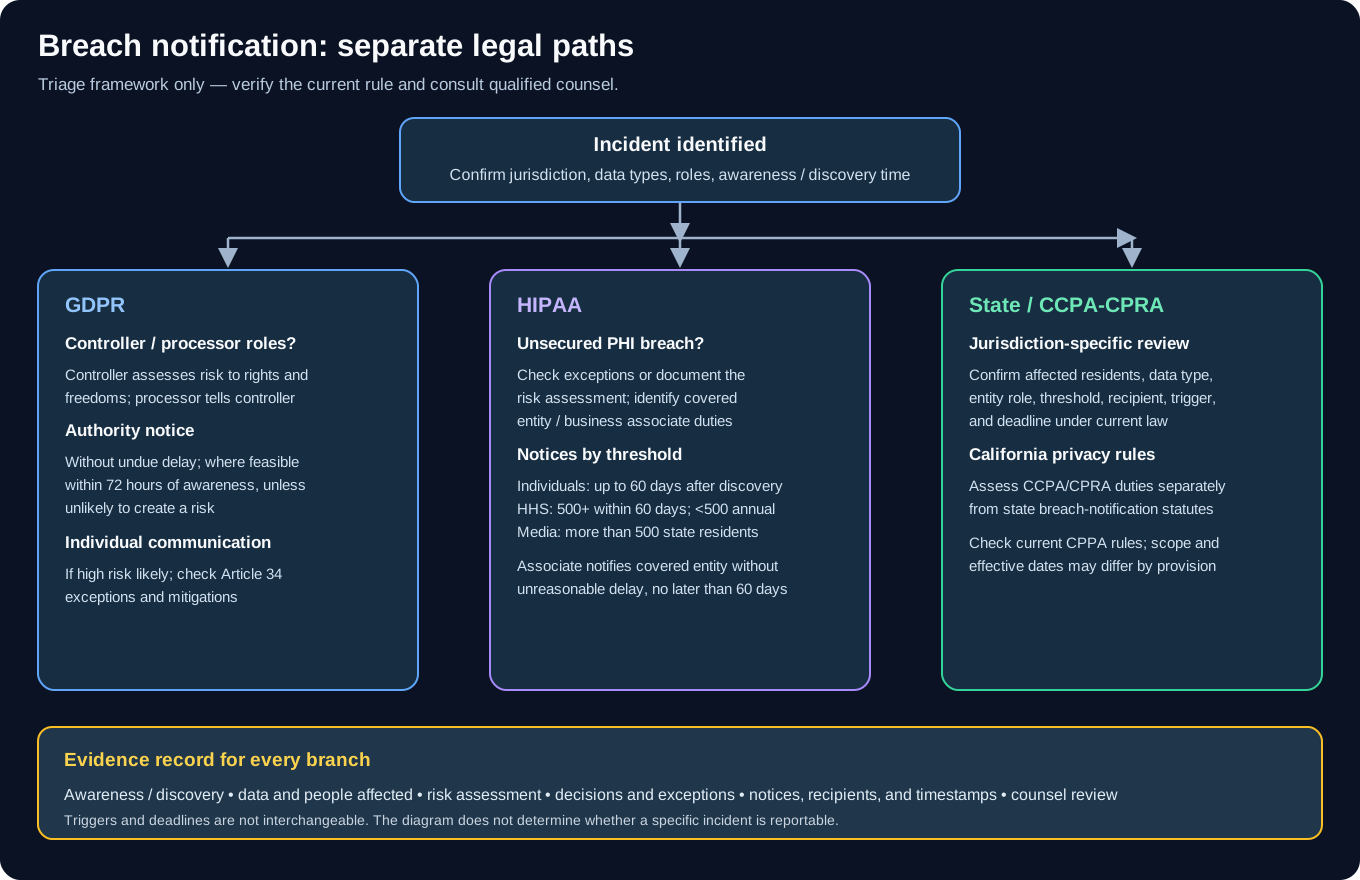
Distinct GDPR, HIPAA, and state-law triggers.
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| kubernetes security control boundaries | Guide |
| kubernetes security secret lifecycle | Guide |
| kubernetes security network policy directions | Guide |
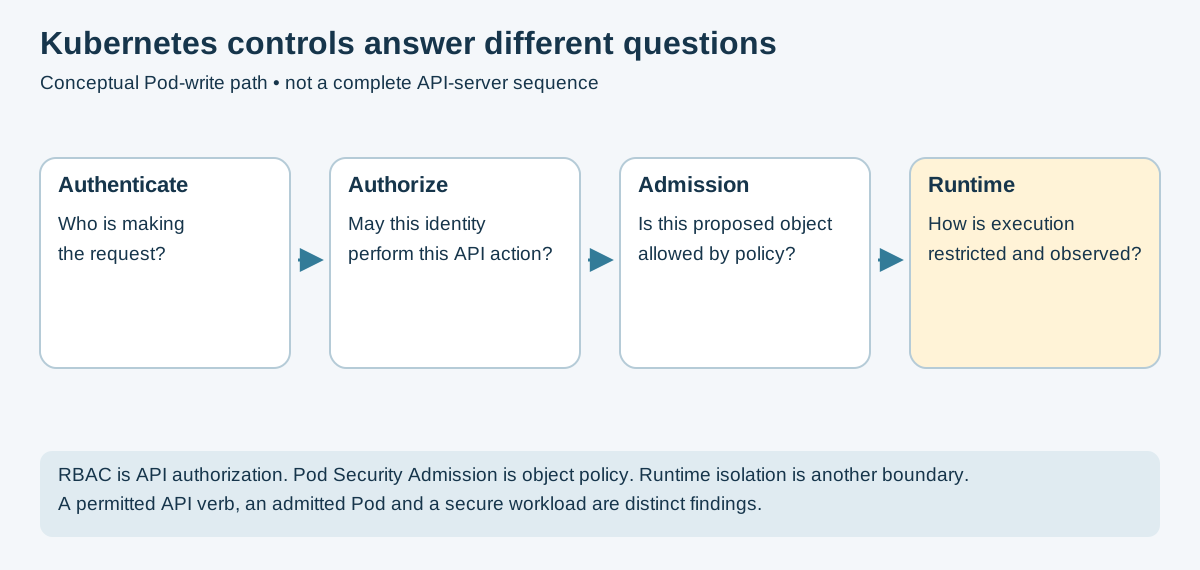
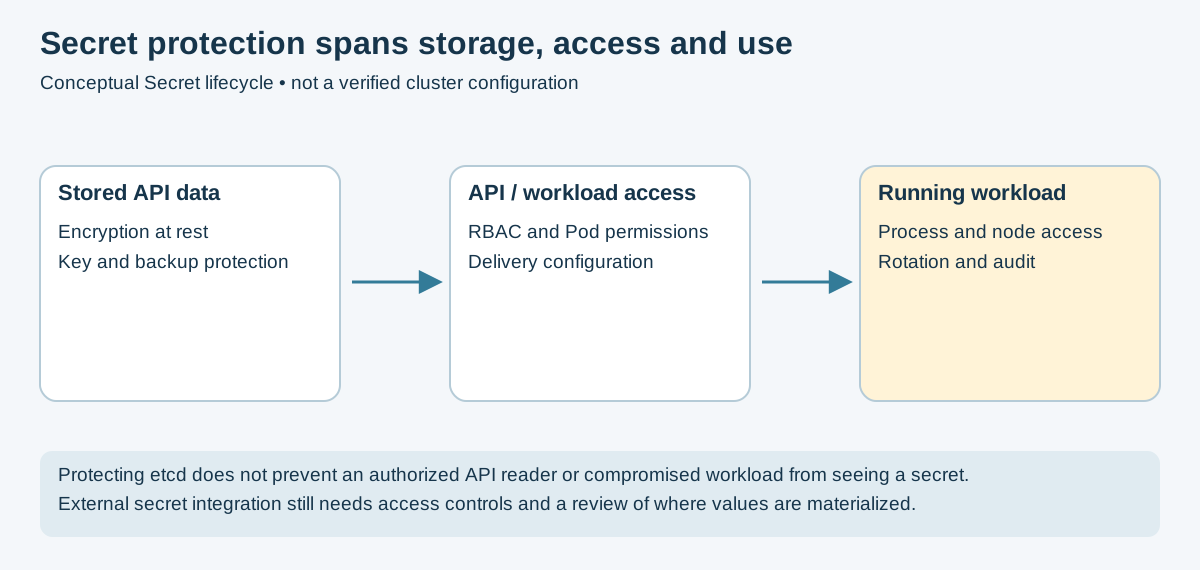
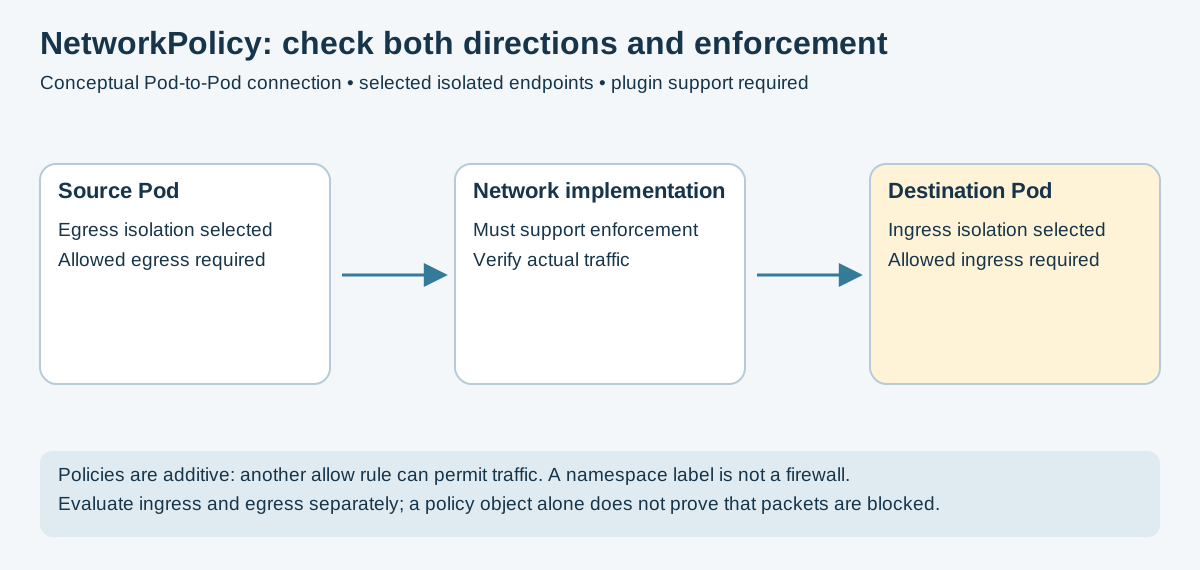
For an auditable record of the visual coverage review and remaining improvements, see Visual Audit — 2026-11-02.
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| advanced sdr lorawan security roles | Guide |
| advanced sdr dsp branching | Guide |
| advanced sdr em inference | Guide |
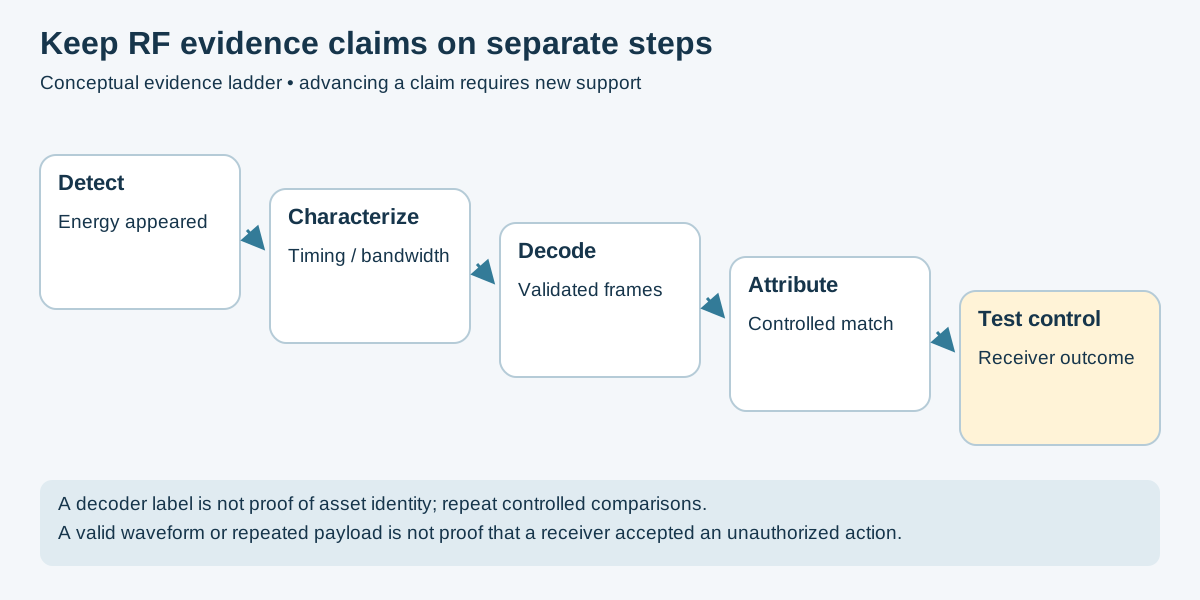
| advanced sdr evidence ladder | Guide |
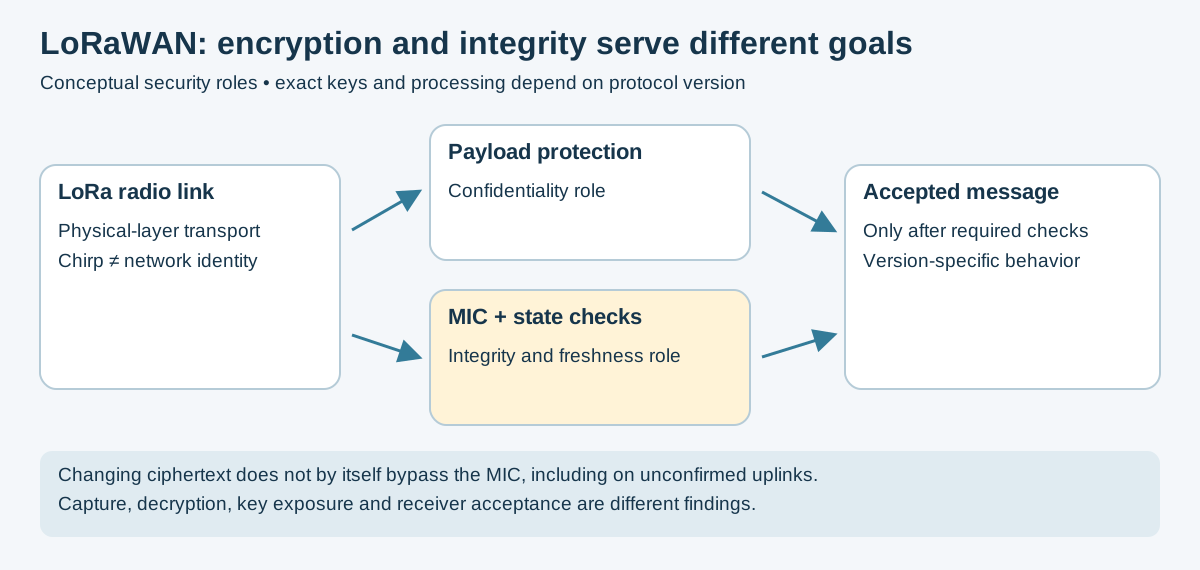
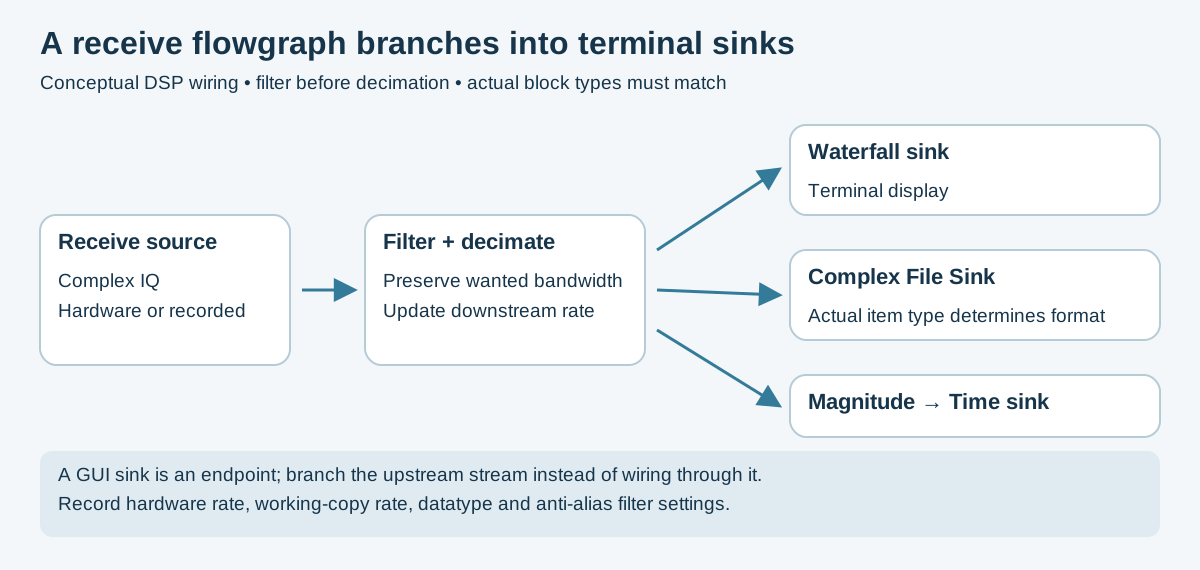
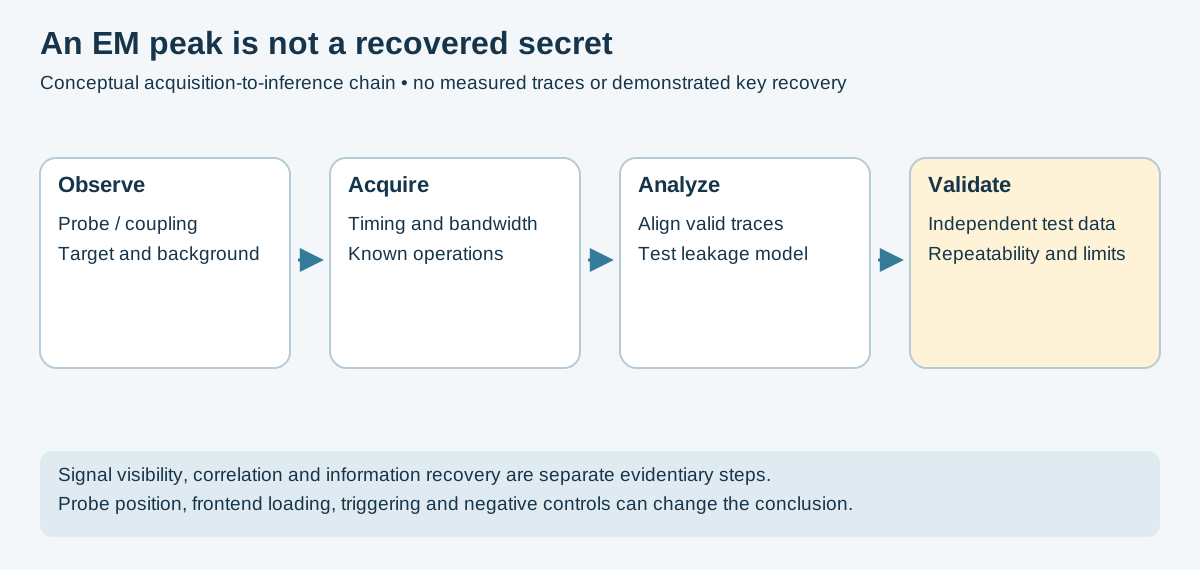
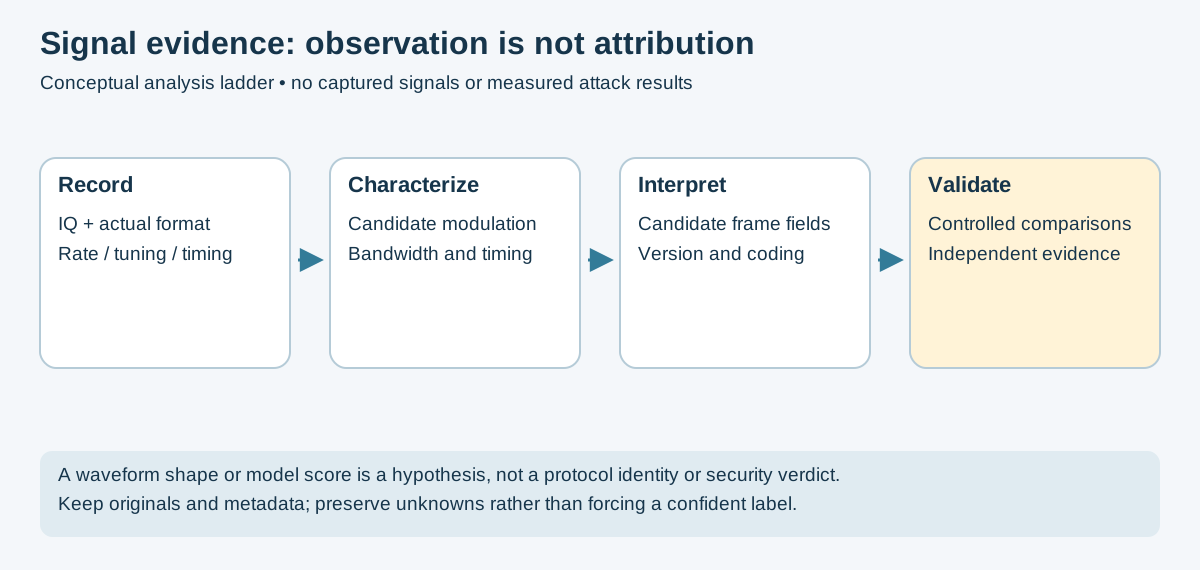
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
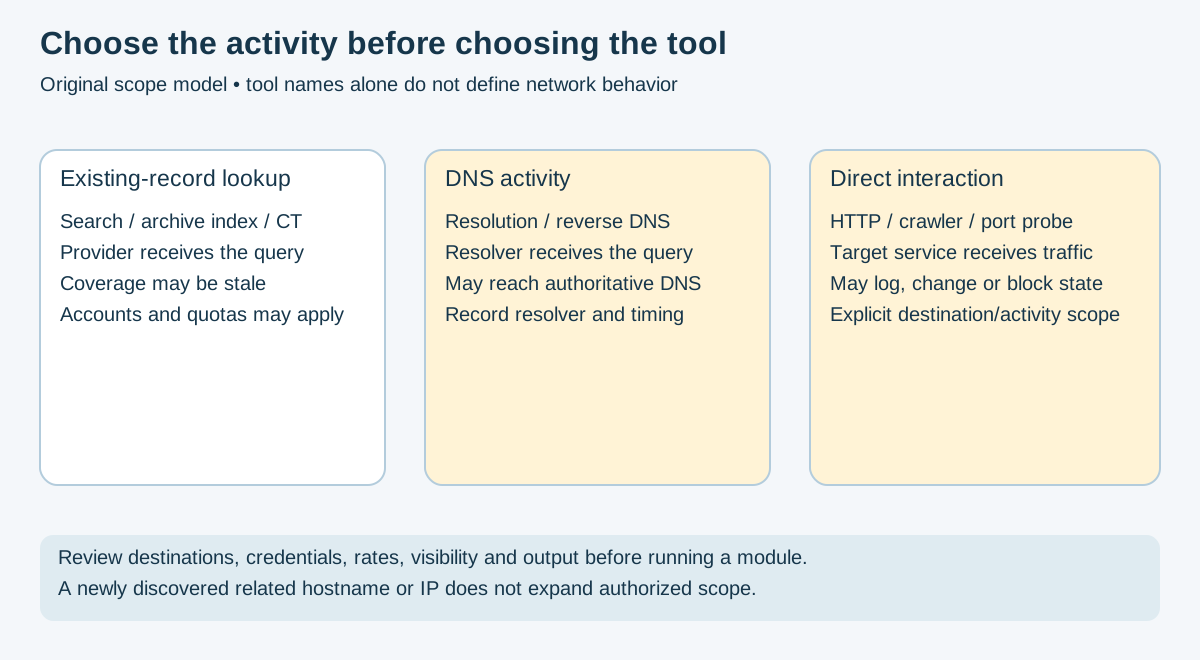
| osint investigation evidence handling | Guide |
| osint investigation cycle | Guide |
| osint investigation request scope | Guide |
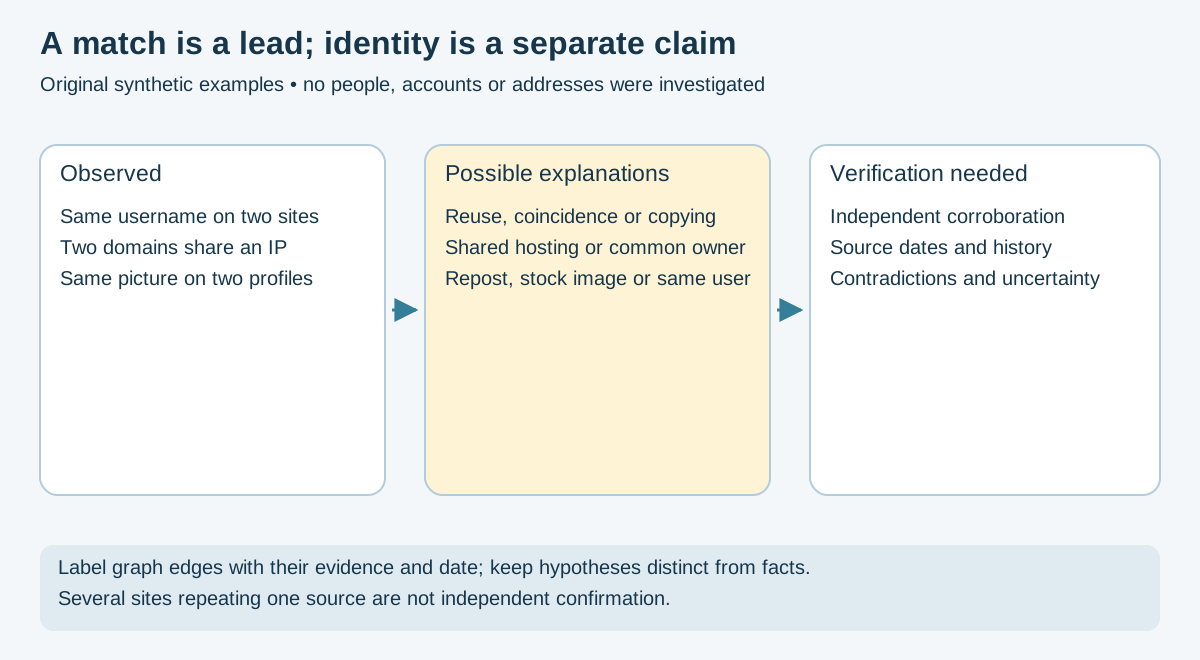
| osint investigation identity evidence | Guide |
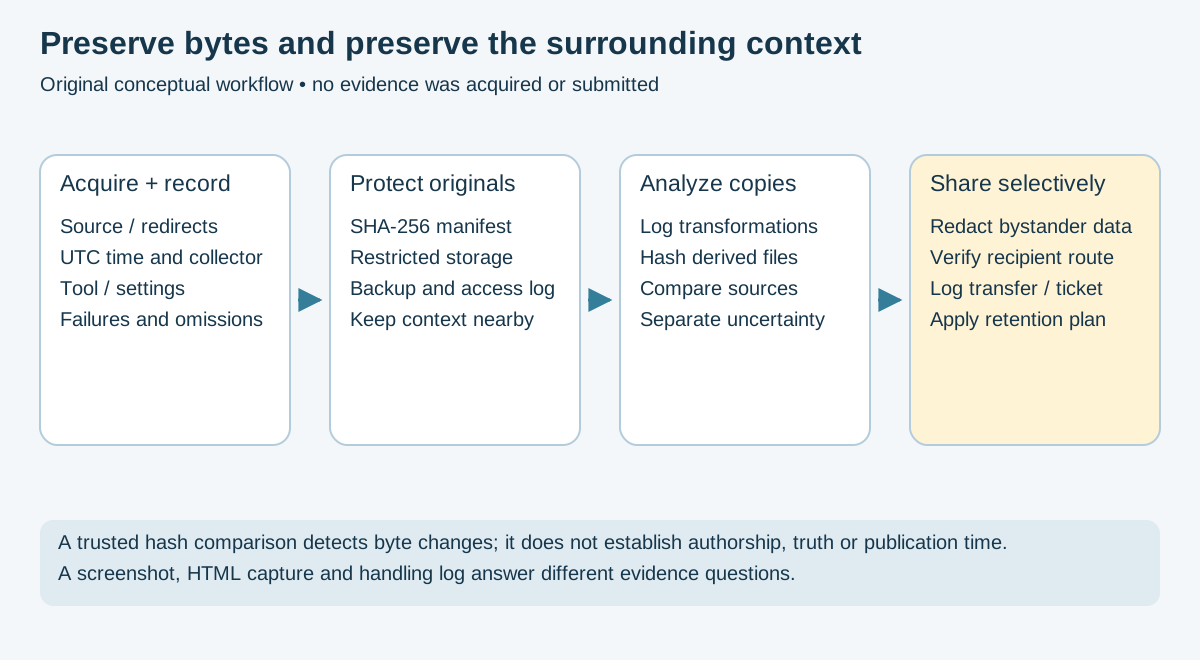
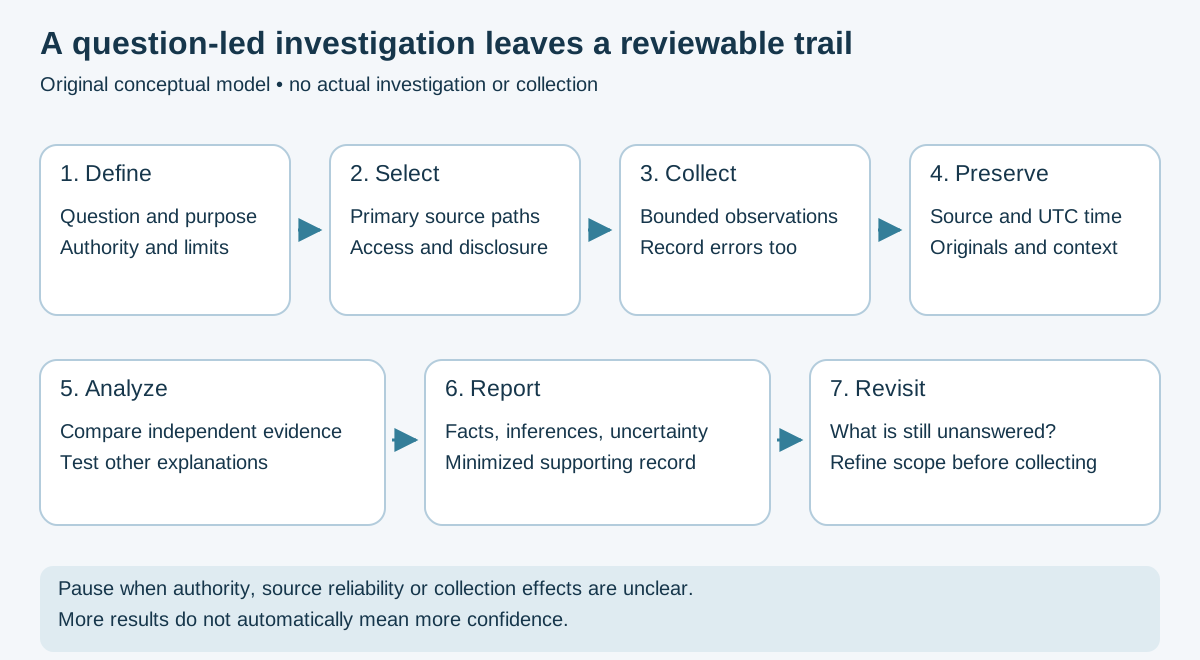
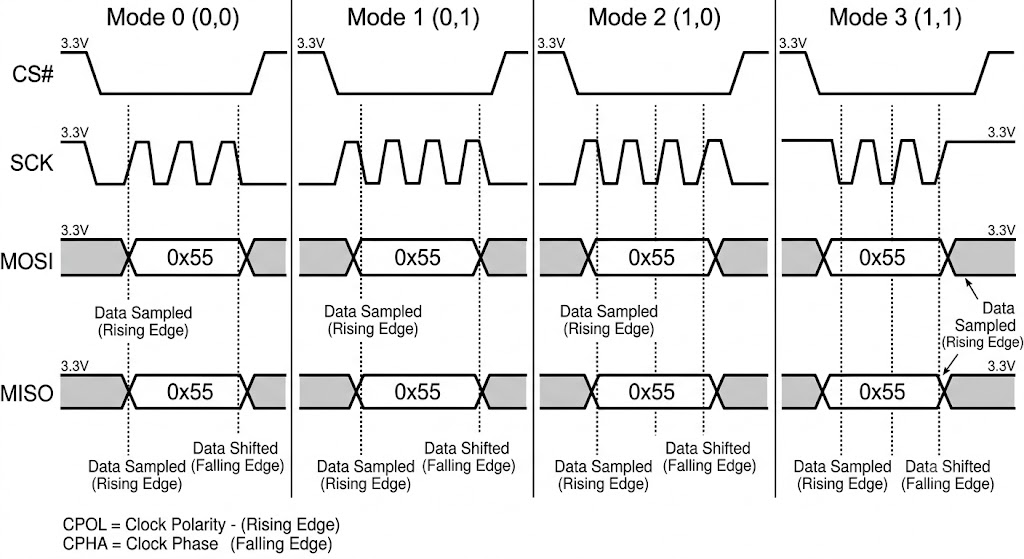
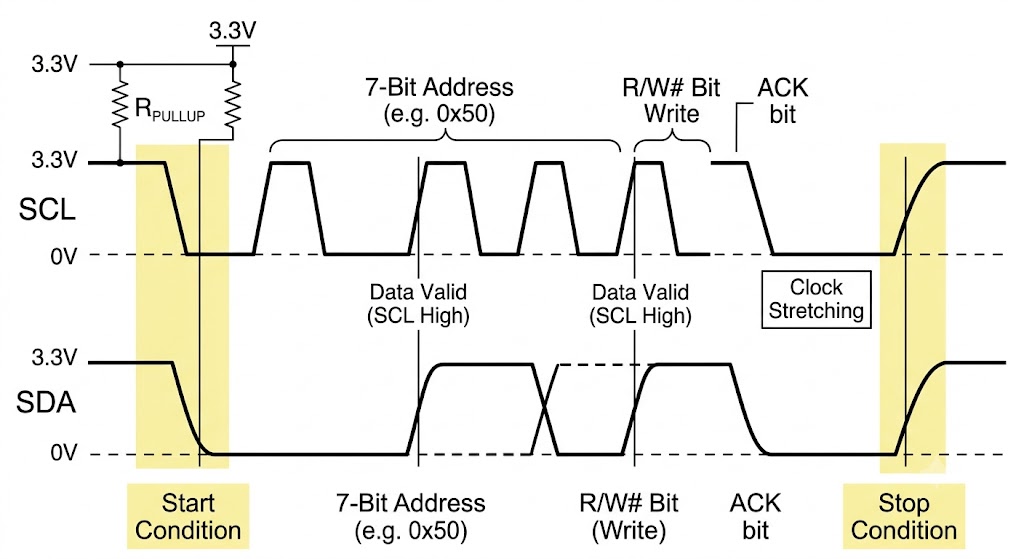
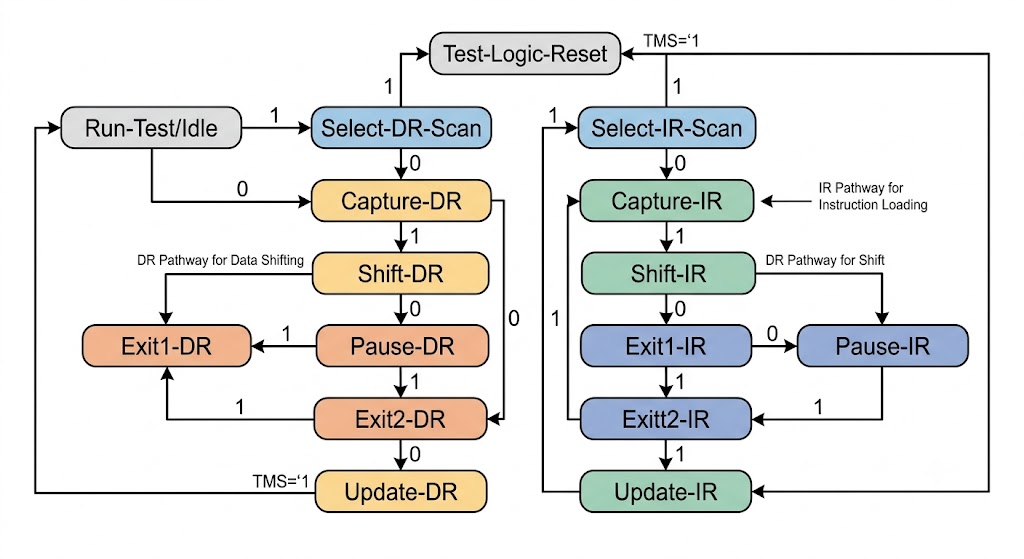
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| phishing response triage | Guide |
| phishing response control boundaries | Guide |
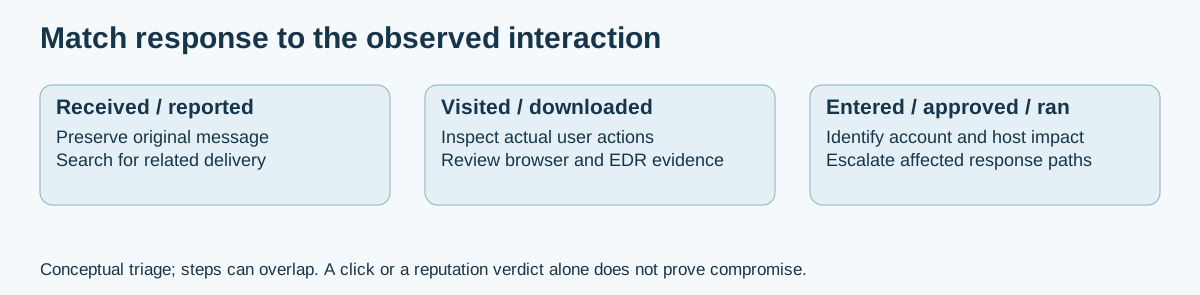
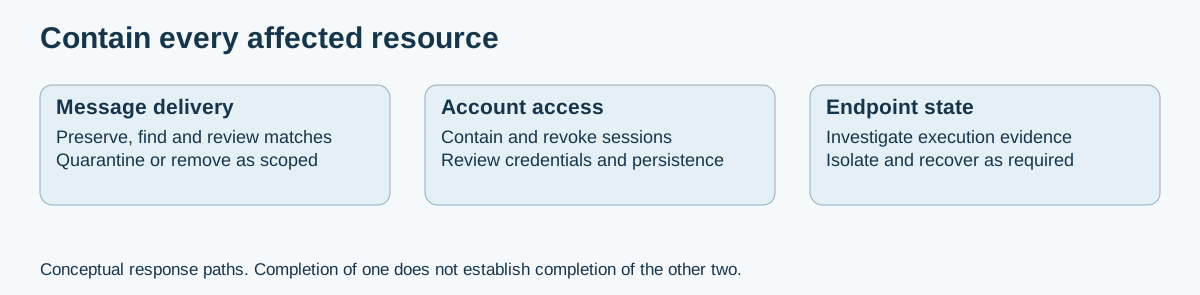
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| crypto algorithms aead contract | Guide |
| crypto algorithms primitive roles | Guide |
| crypto algorithms pqc roles | Guide |
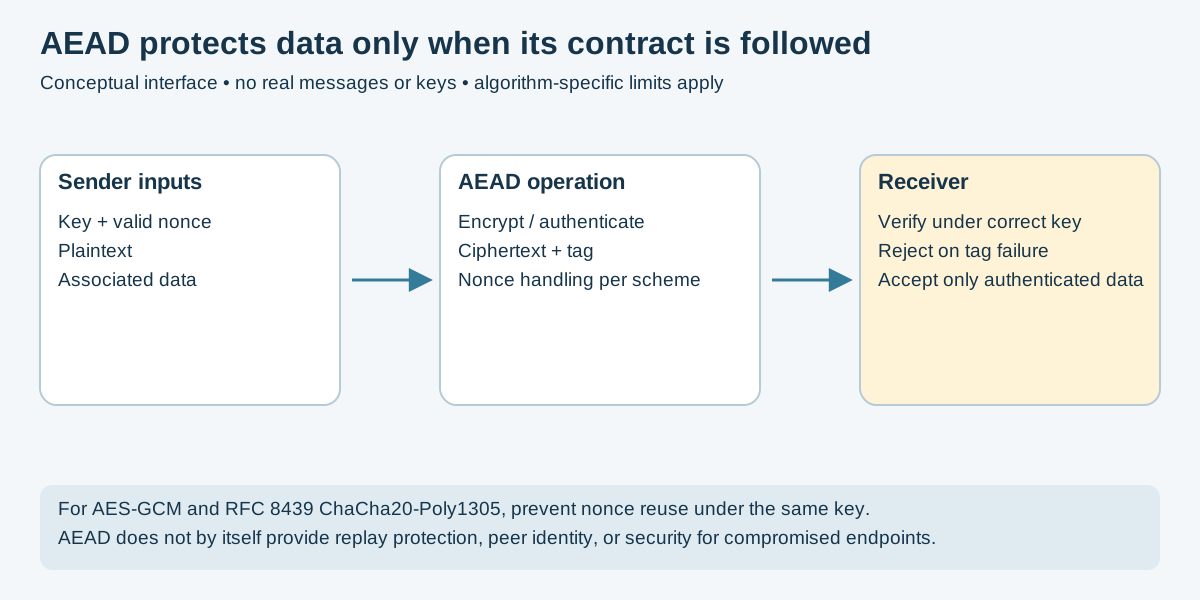
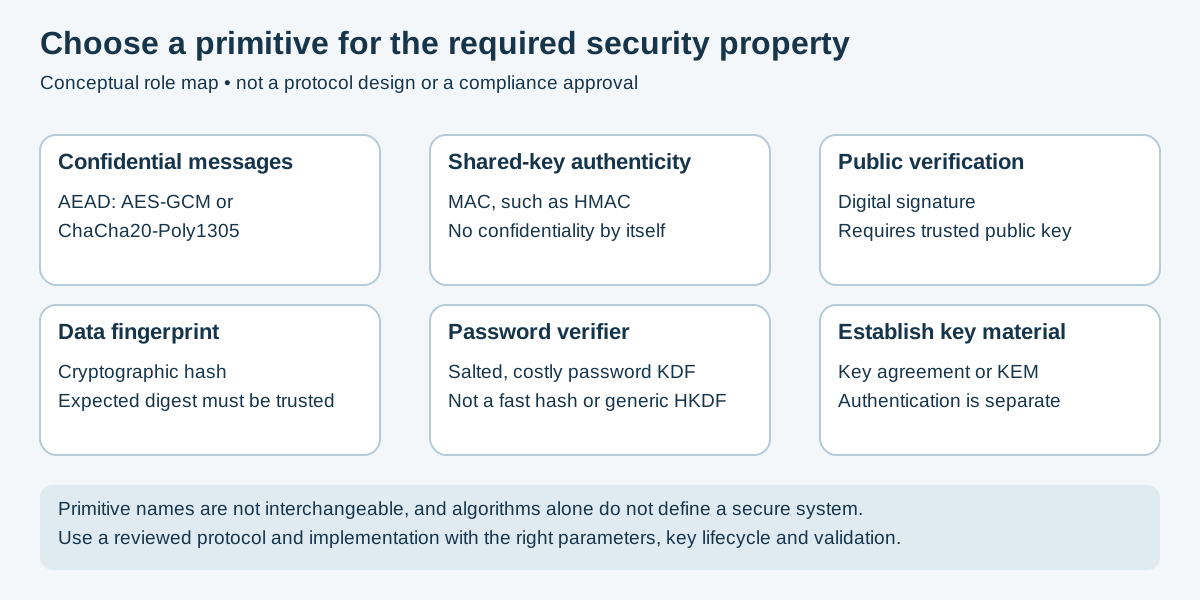
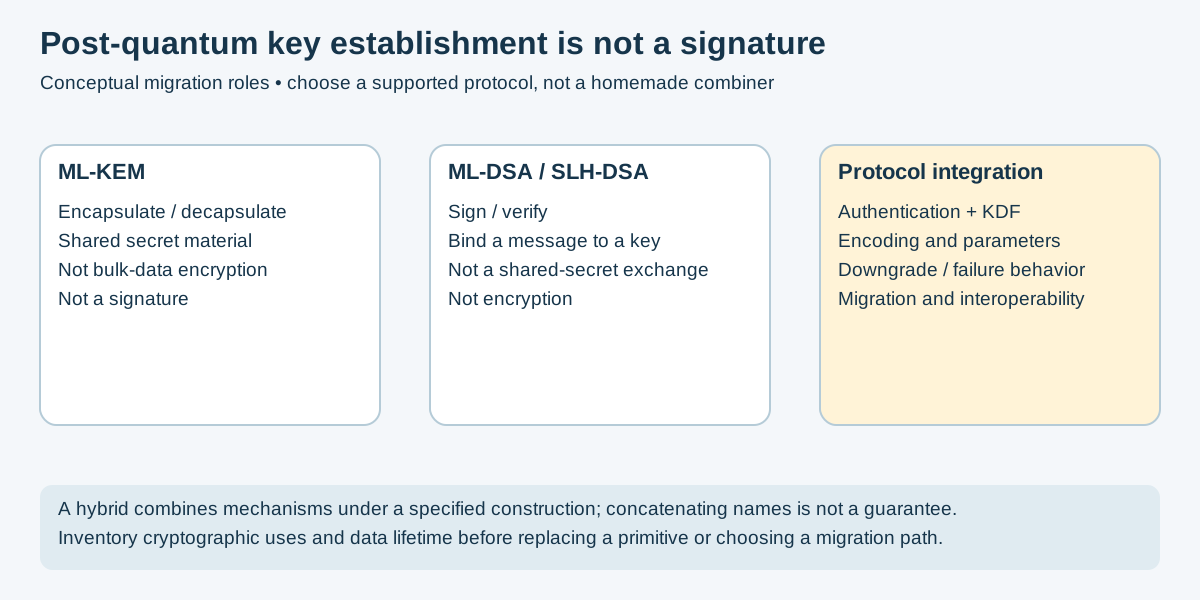
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| agent security evaluation evidence | Guide |
| agent threat-modeling evaluation loop | Guide |
| agent security trust boundaries | Guide |
| agent security action gate | Guide |
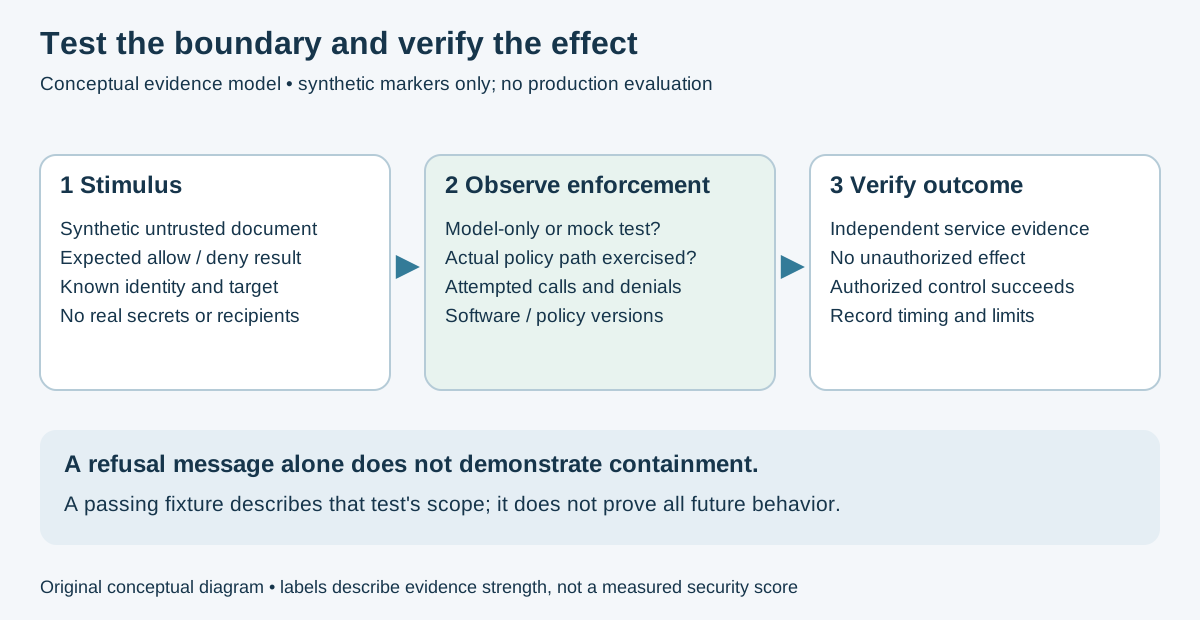
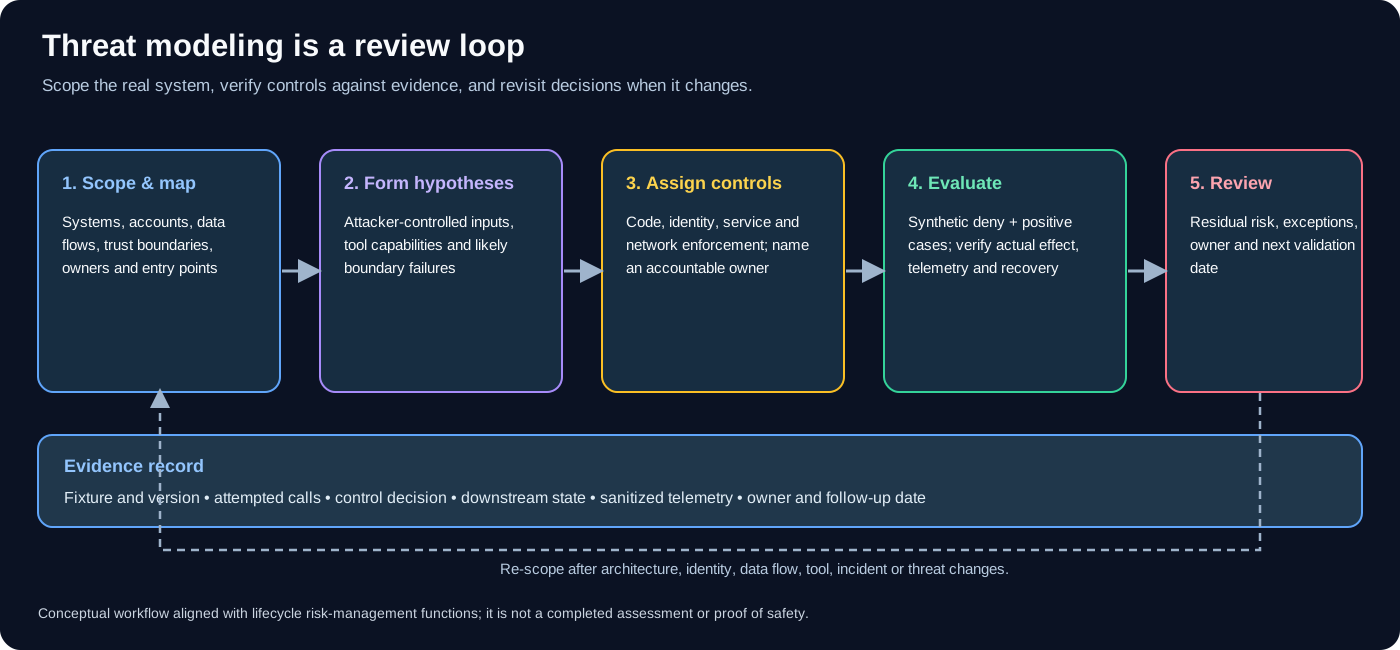
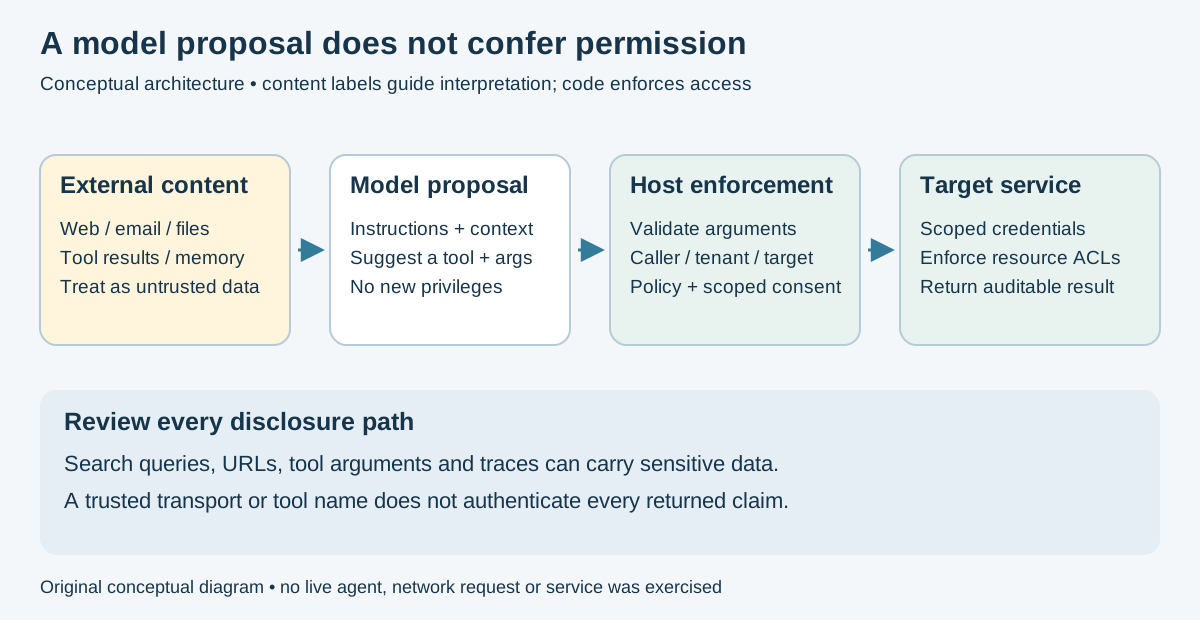
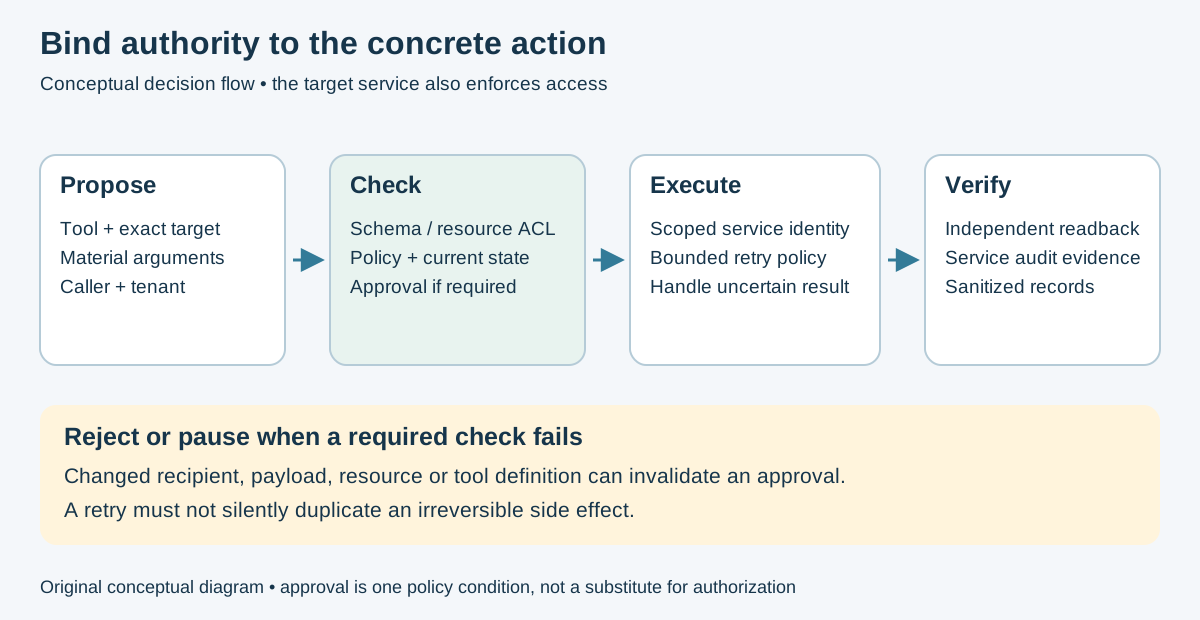
Scope, map, test, review and re-scope.
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| aws request policy evaluation | Guide |
| aws s3 independent controls | Guide |
| AWS CloudTrail event coverage | AWS Hardening & Detection |
| aws imdsv2 token boundary | Guide |
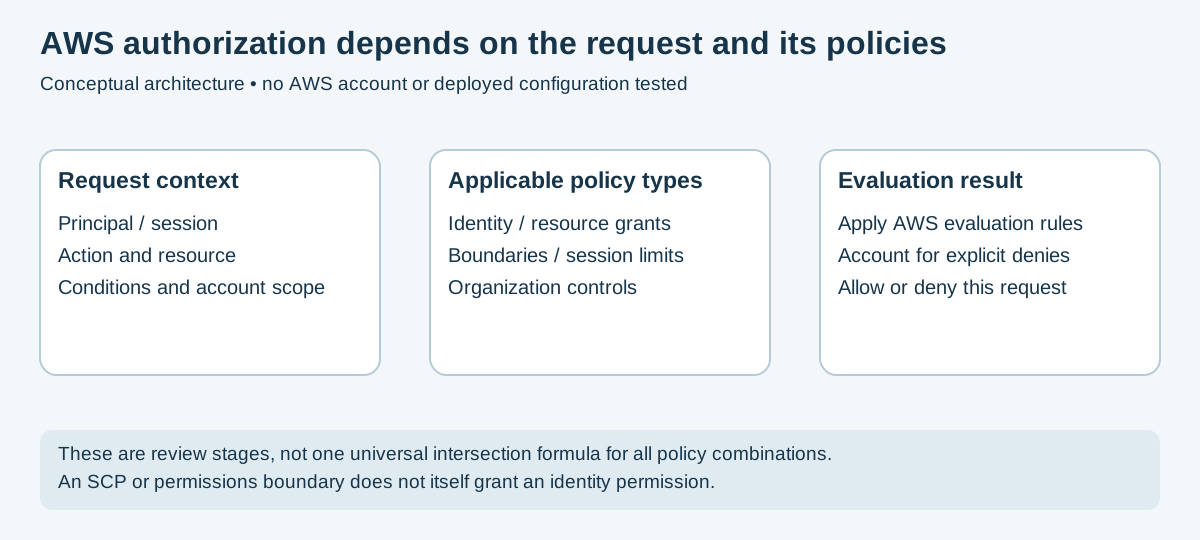
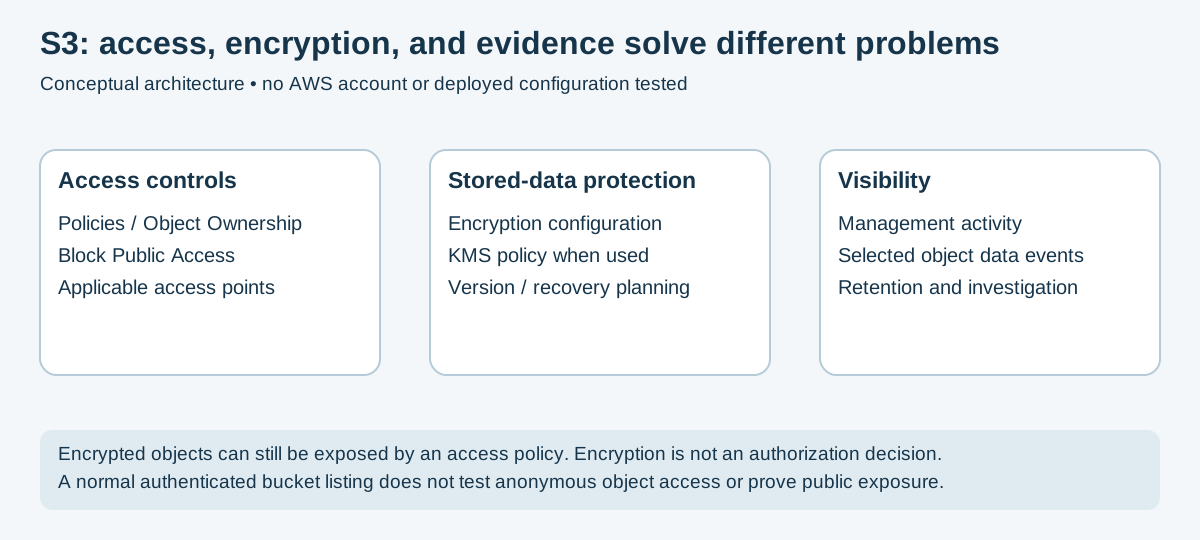
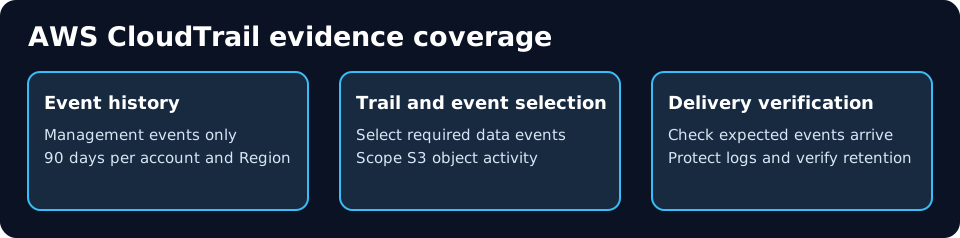
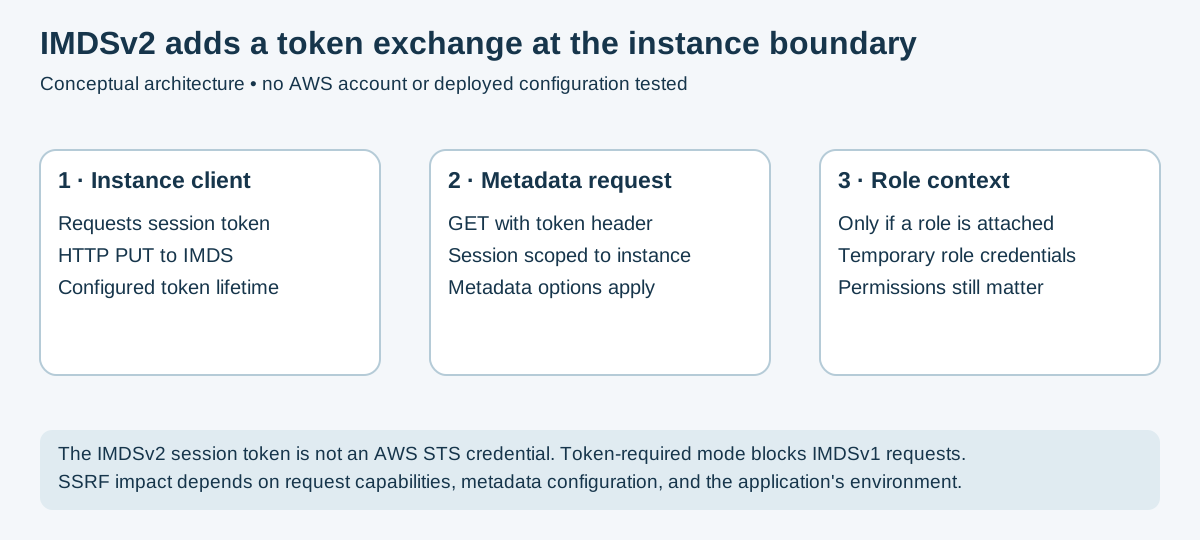
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| yara rule lifecycle | Guide |
| yara rule detection interpretation | Guide |
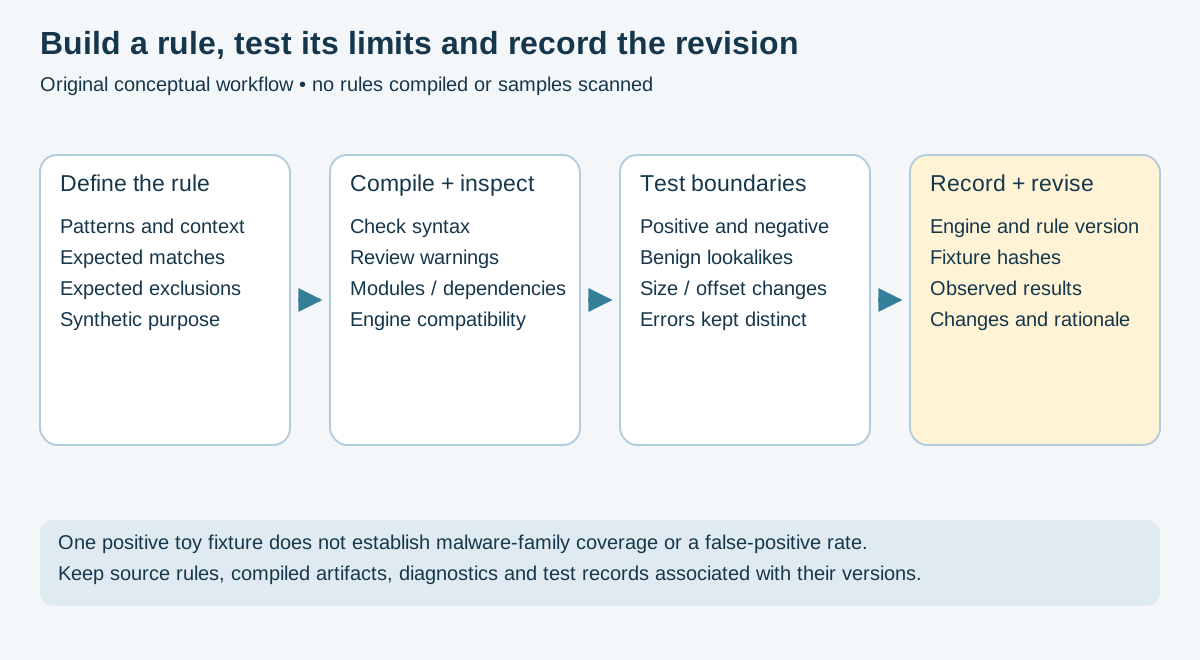
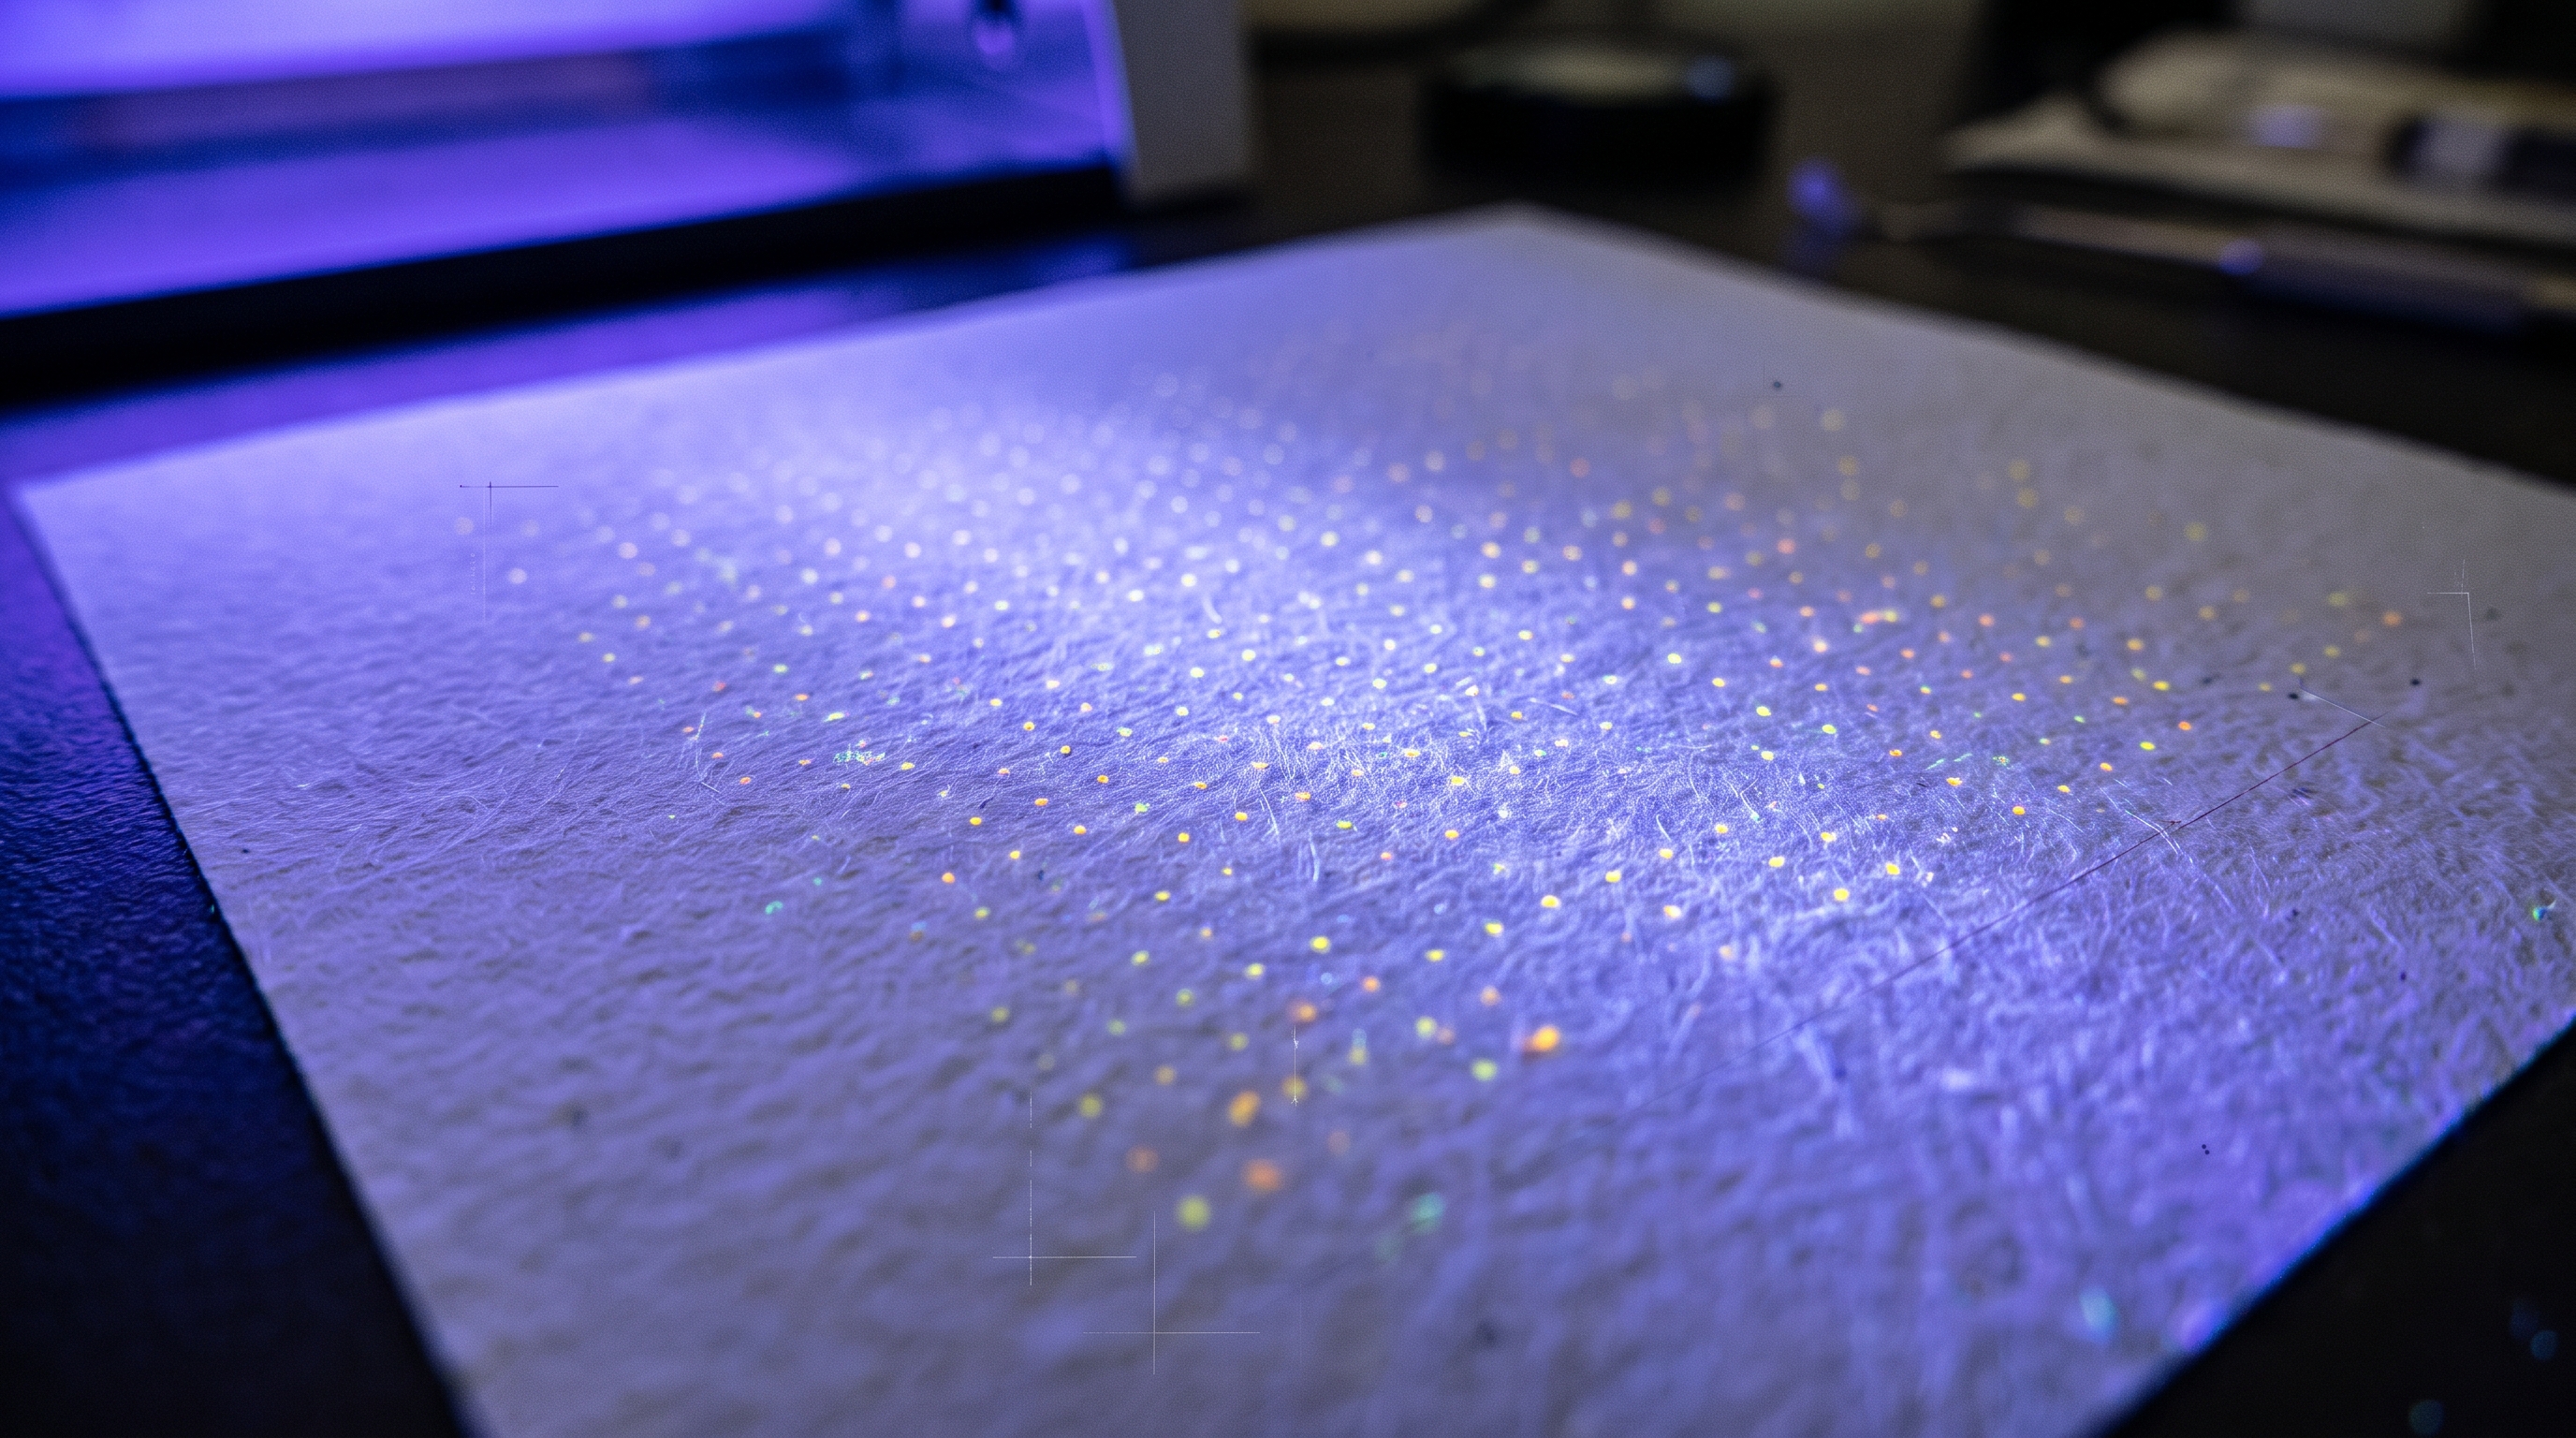
Embedded in the Xerox DocuColor case study.
| Asset | Purpose and provenance |
|---|---|
| Printer dots | Owner-supplied illustrative introduction; not authenticated as a physical capture. |
| MIC overview | Owner-supplied conceptual breakdown; caption explains layout and lighting limitations. |
| DocuColor grid | Original synthetic grid and minute-decoding example based on EFF's format. |
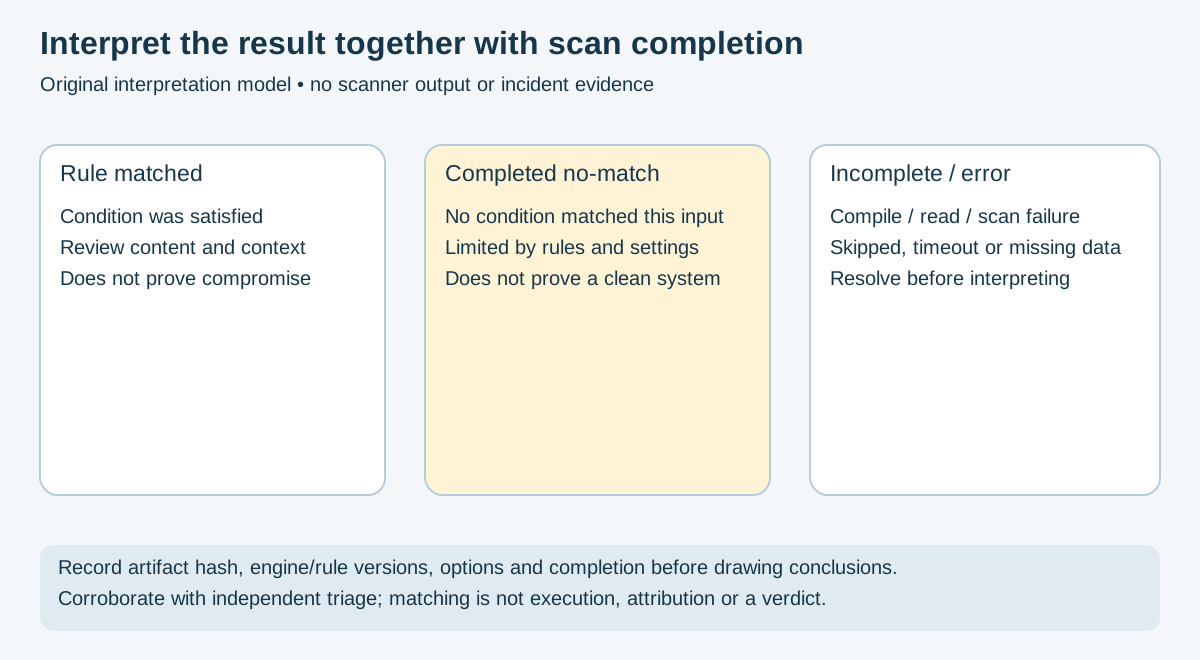
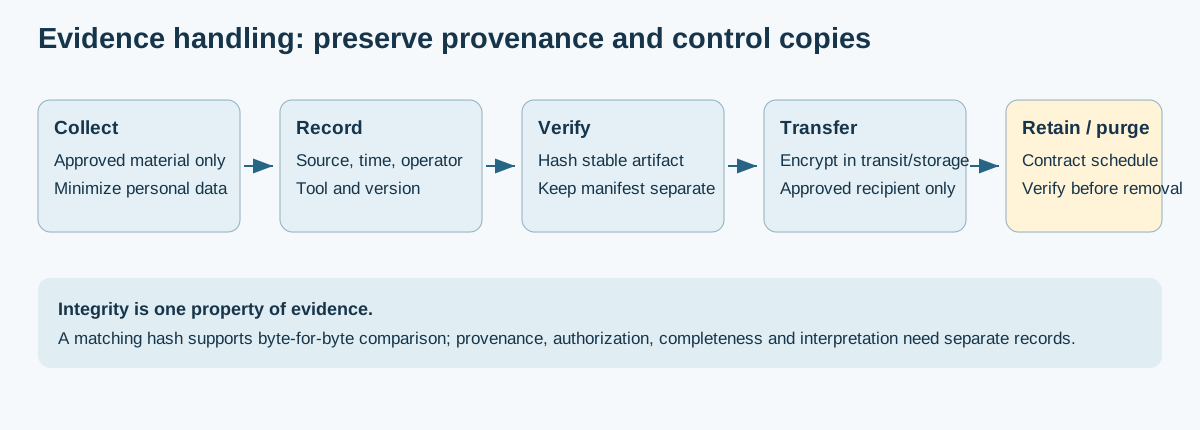
| Evidence workflow | Original conceptual preservation, observation, decoding, and corroboration workflow. |
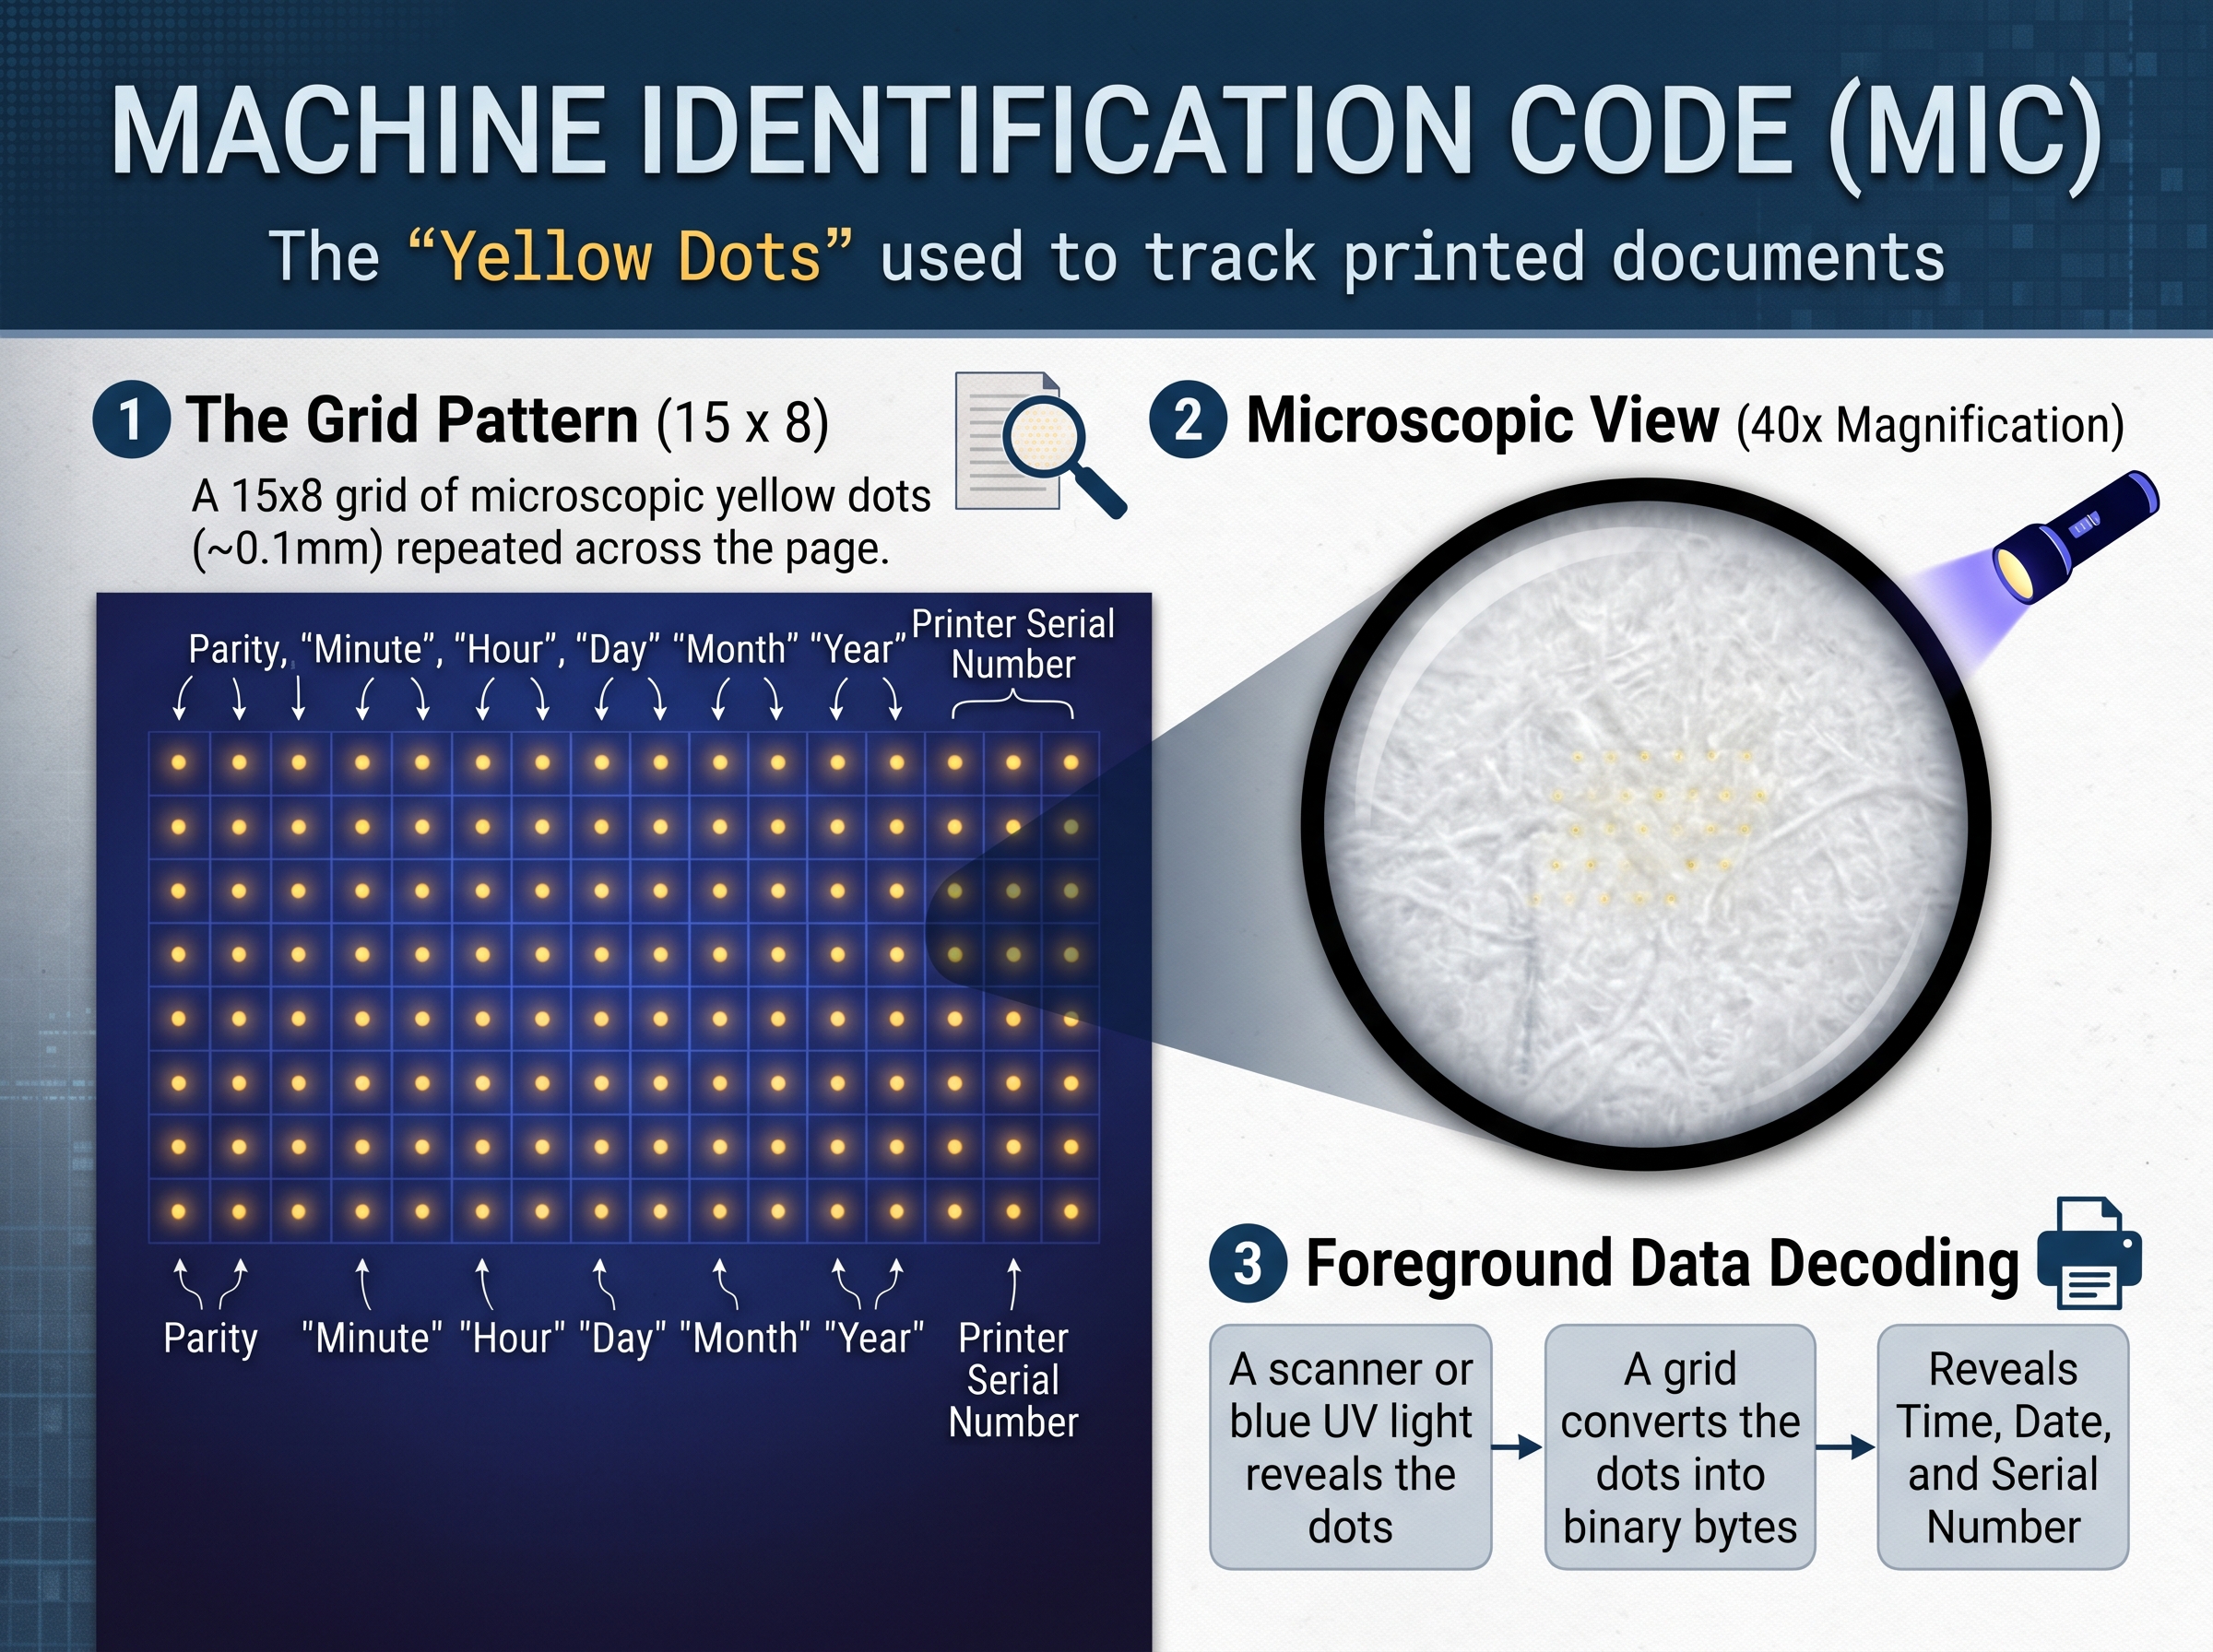
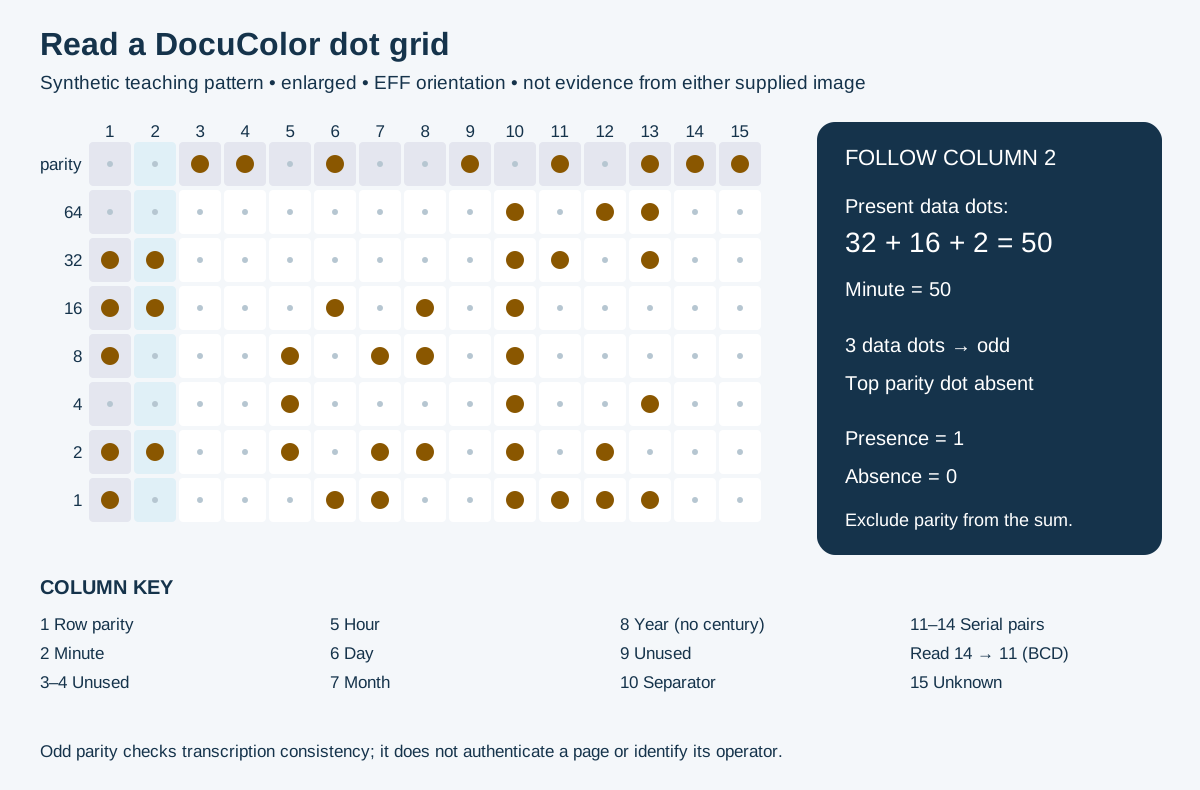
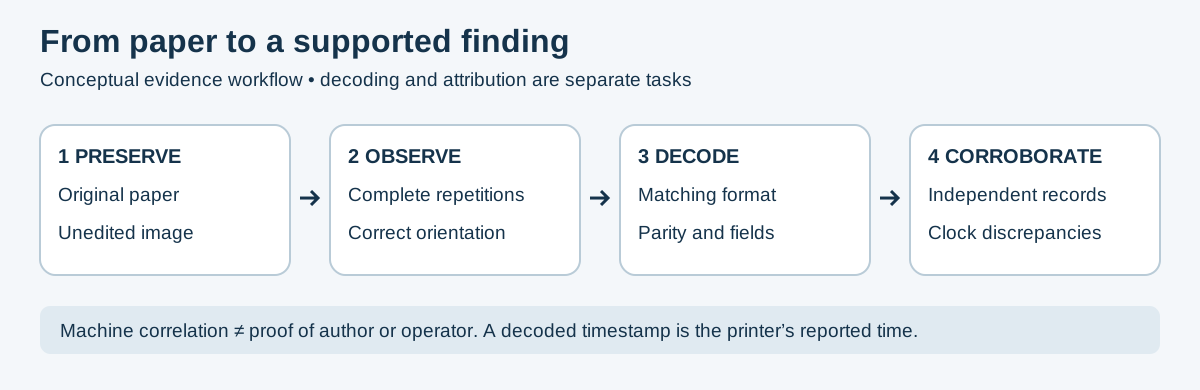
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| source verification preservation vs claim | Guide |
| source verification provenance independence | Guide |
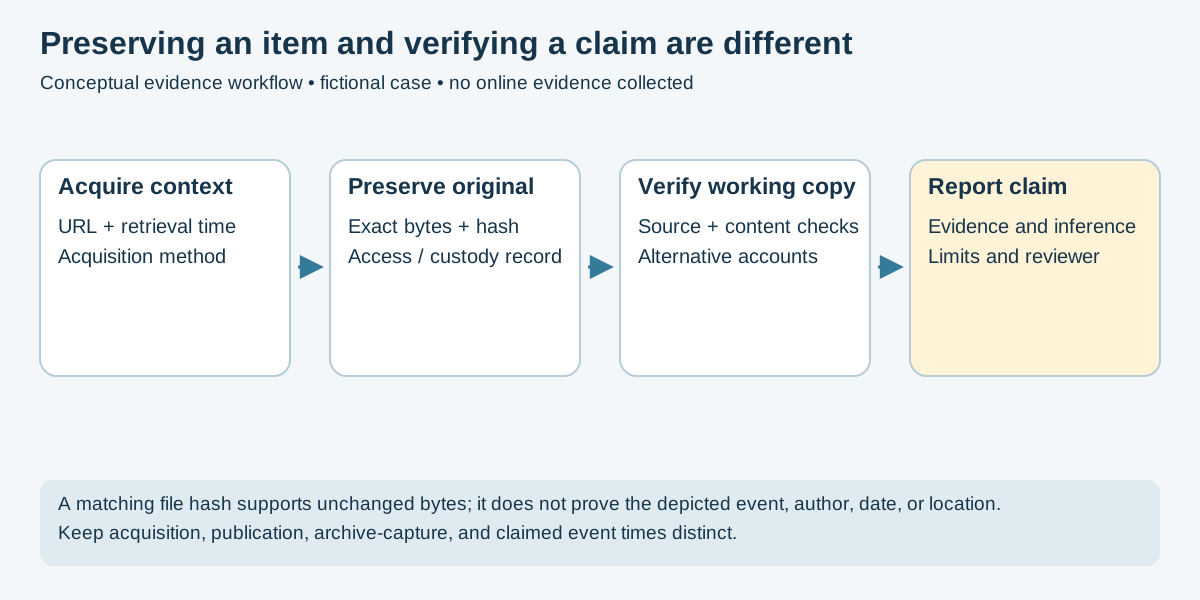
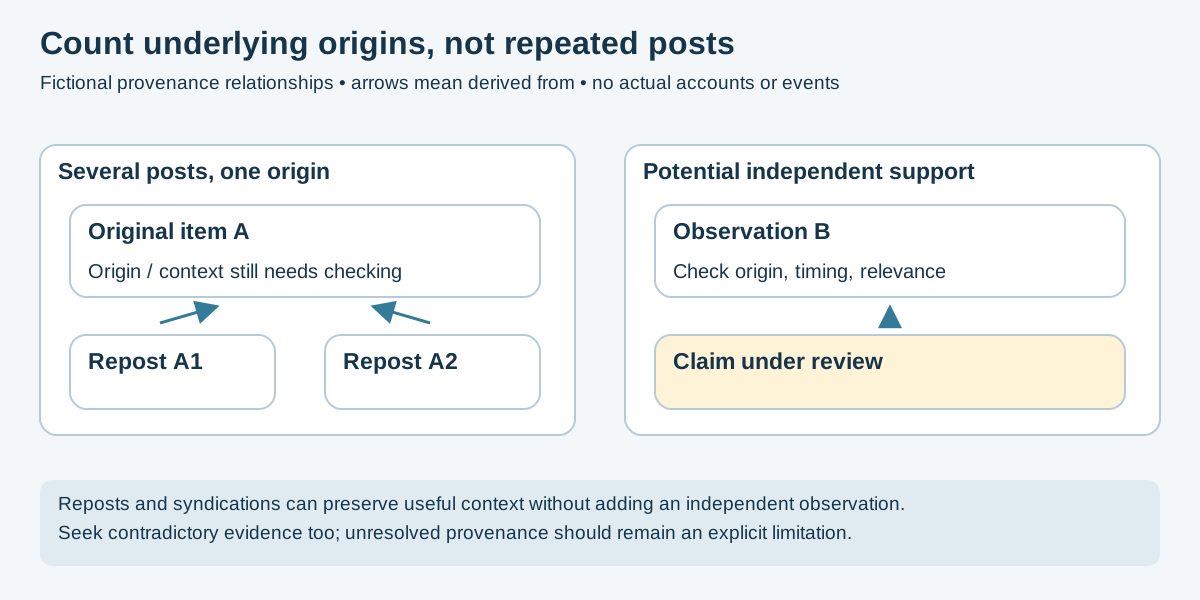
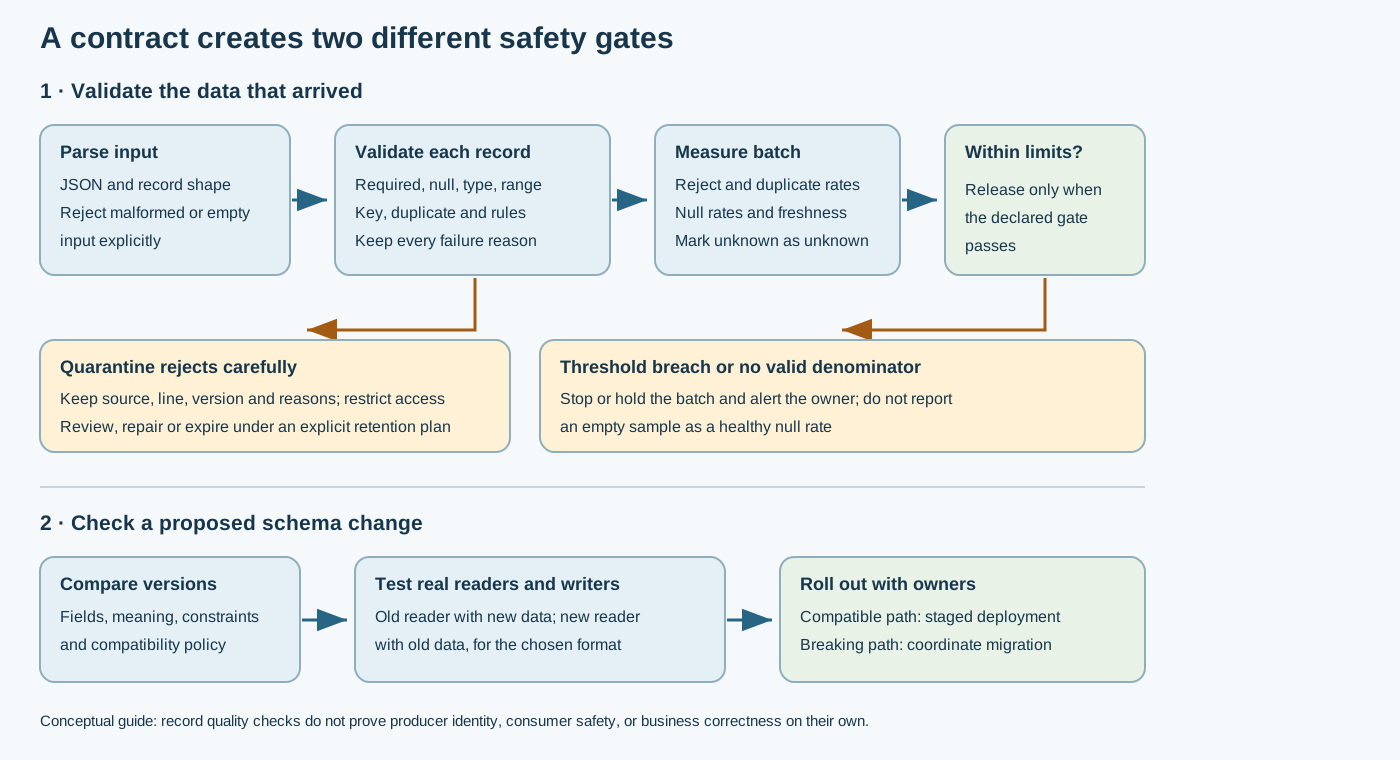
Original conceptual flow separating per-record validation, batch handling and schema evolution compatibility checks.
| Diagram | Embedded guide |
|---|---|
| Data contract validation and schema evolution | Data Quality & Schema Contracts |
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| gcp security policy inheritance | Guide |
| gcp security audit coverage | Guide |
| gcp security service account routes | Guide |
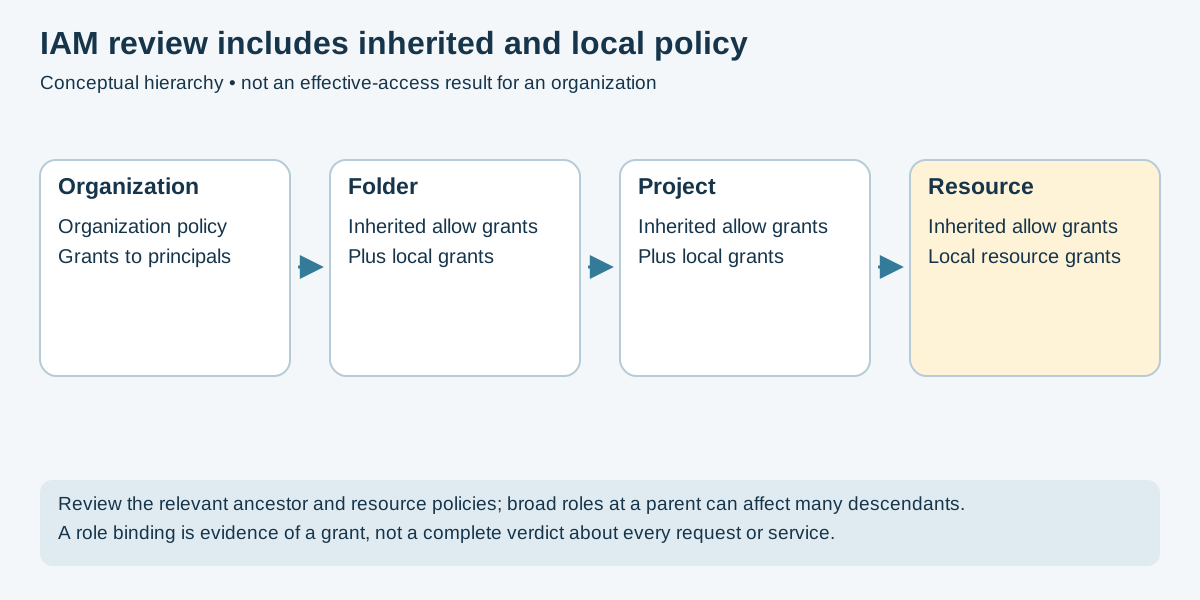
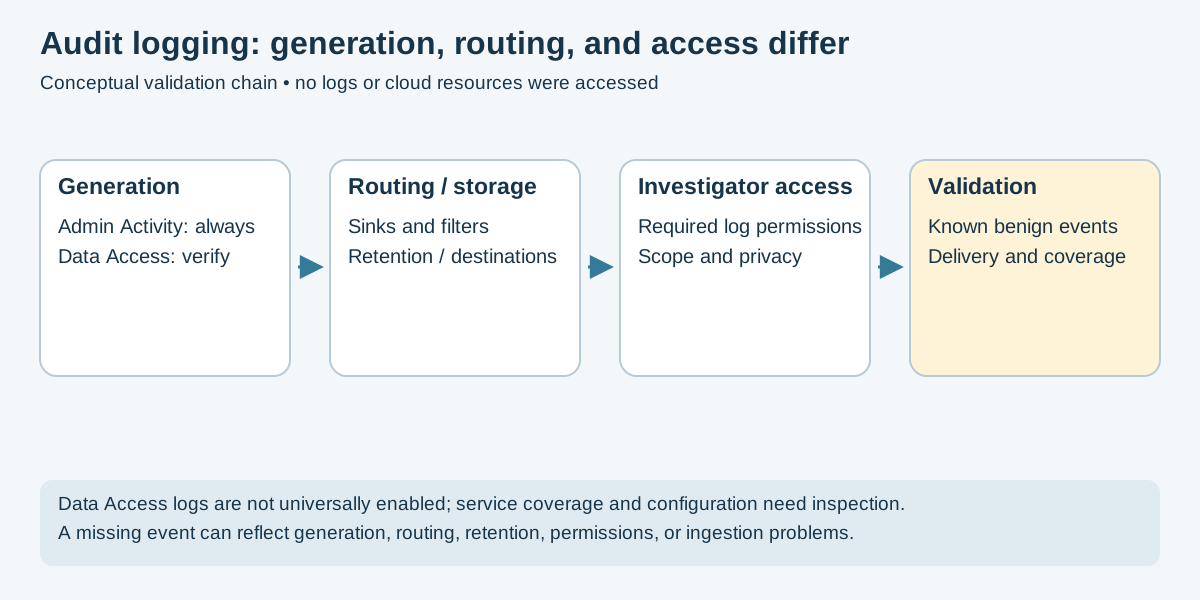
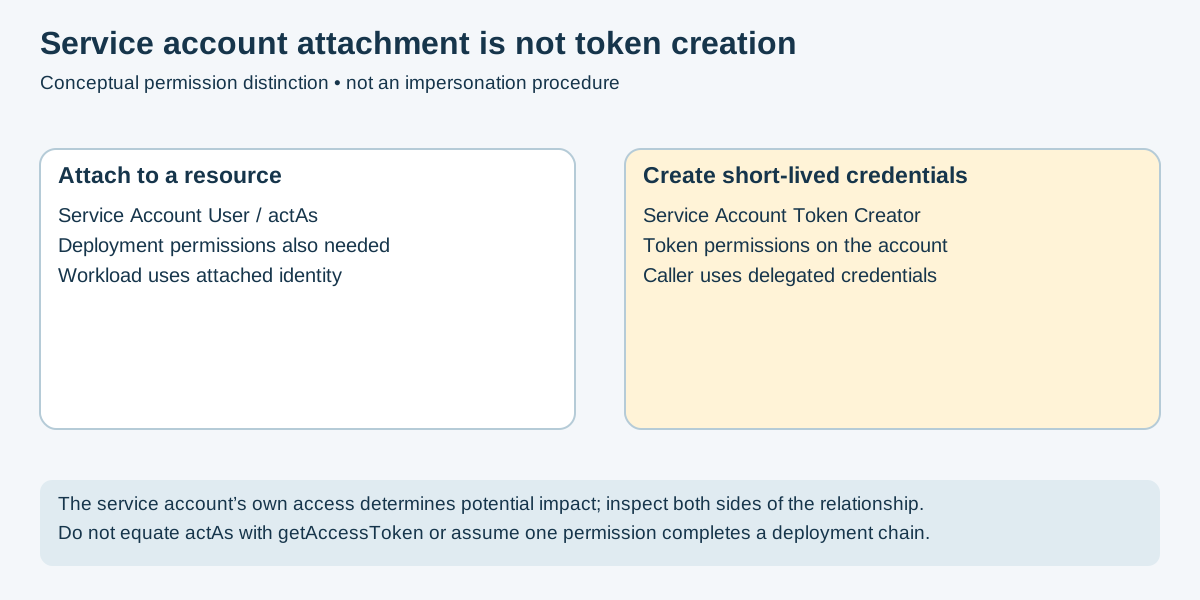
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| argus osint module scope | Guide |
| argus osint environment selection | Guide |
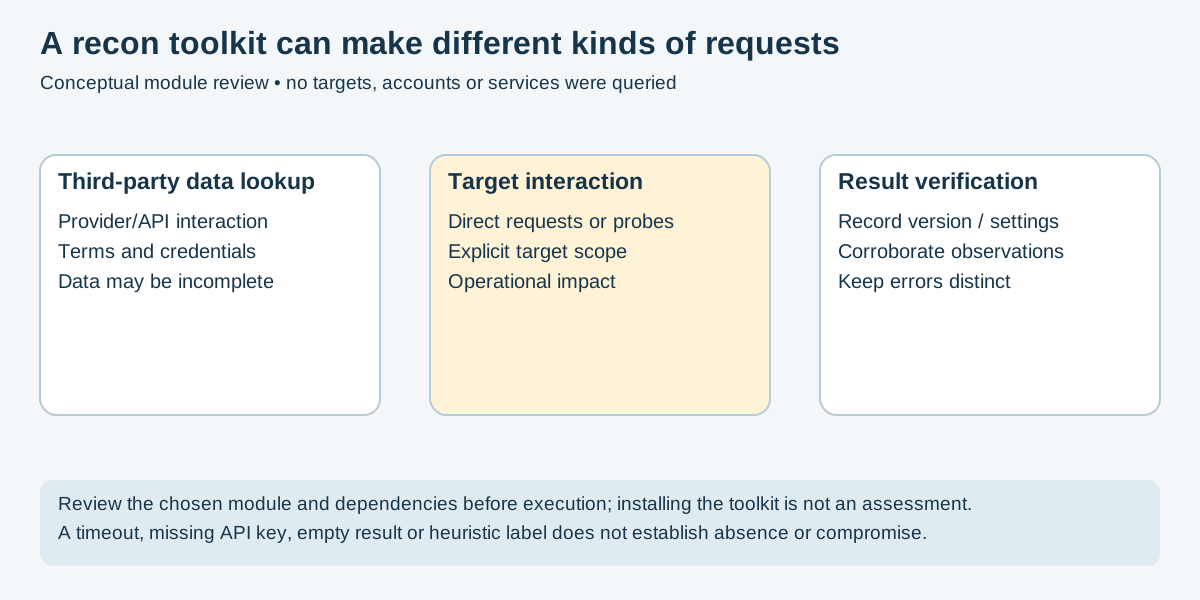
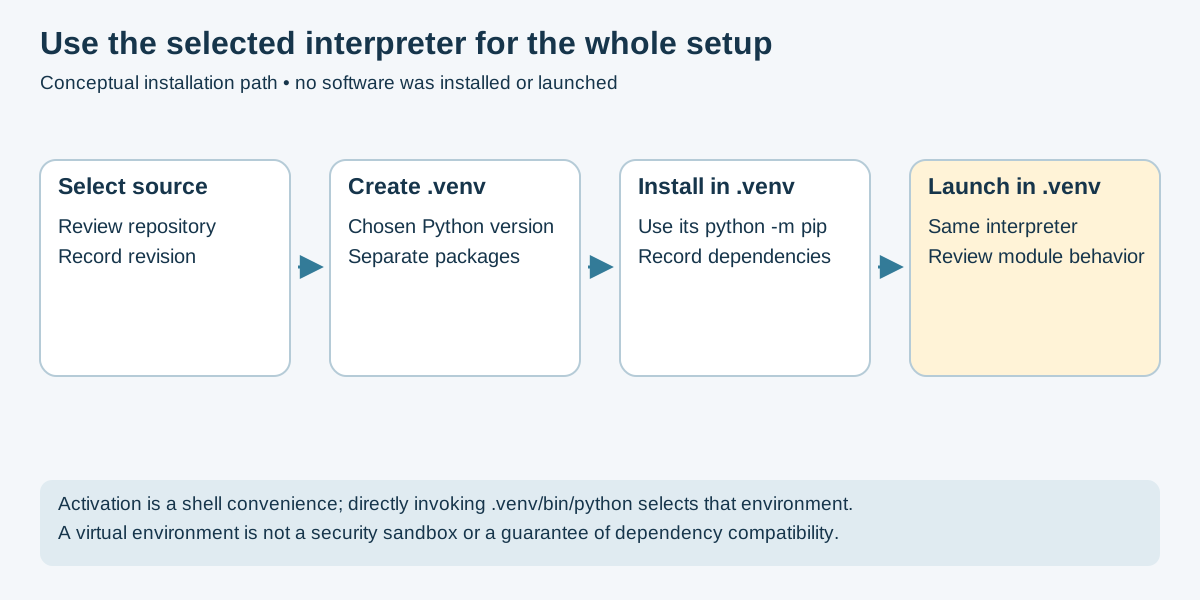
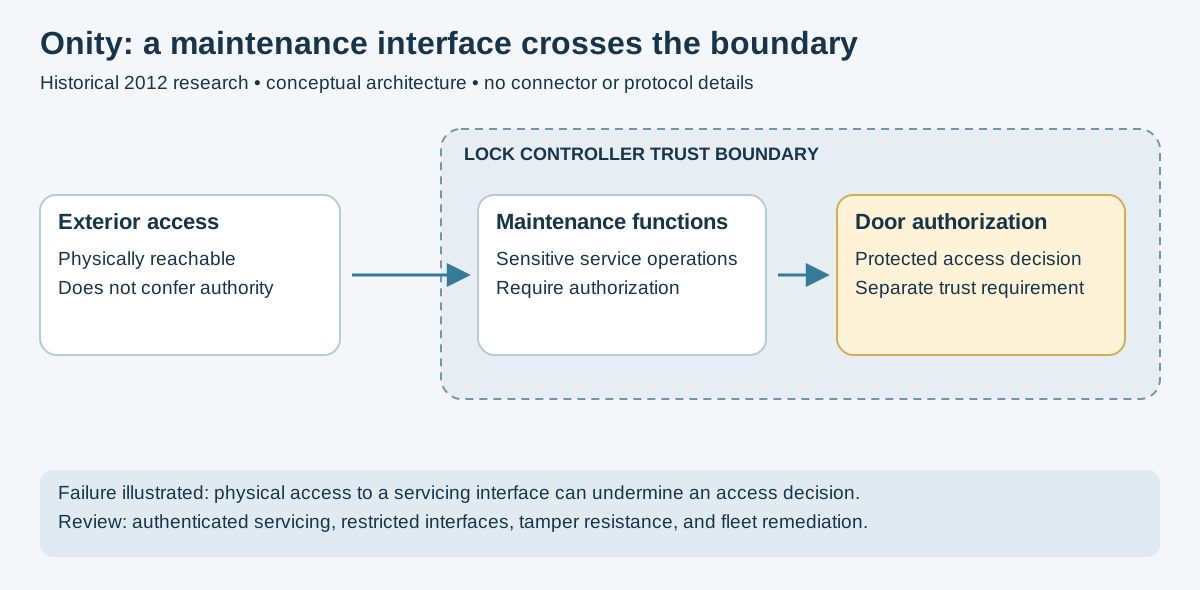
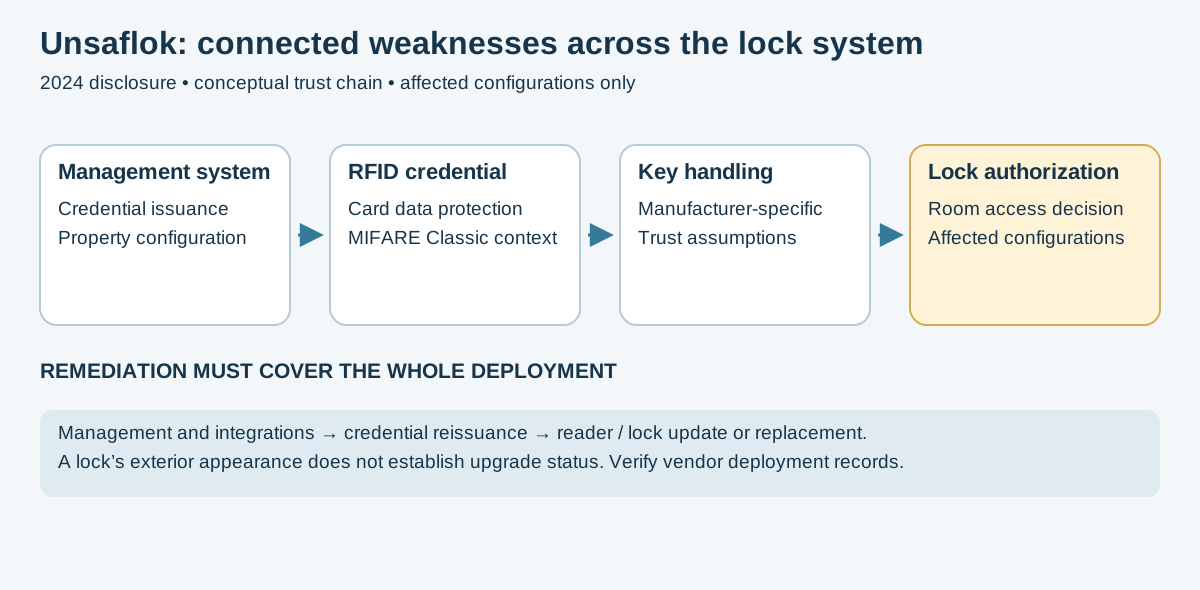
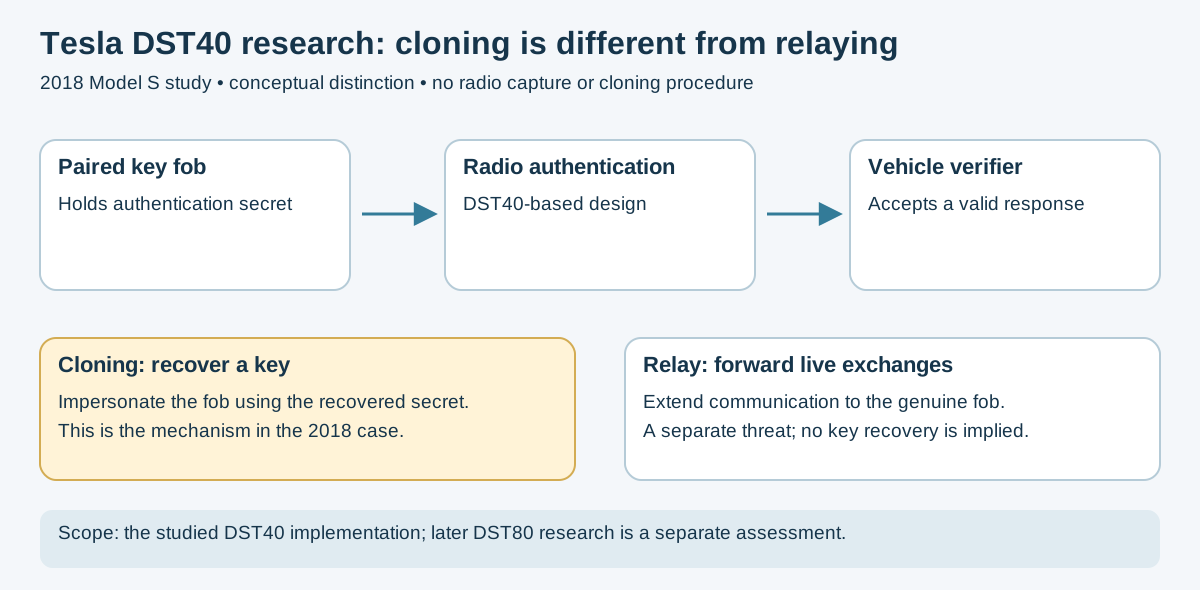
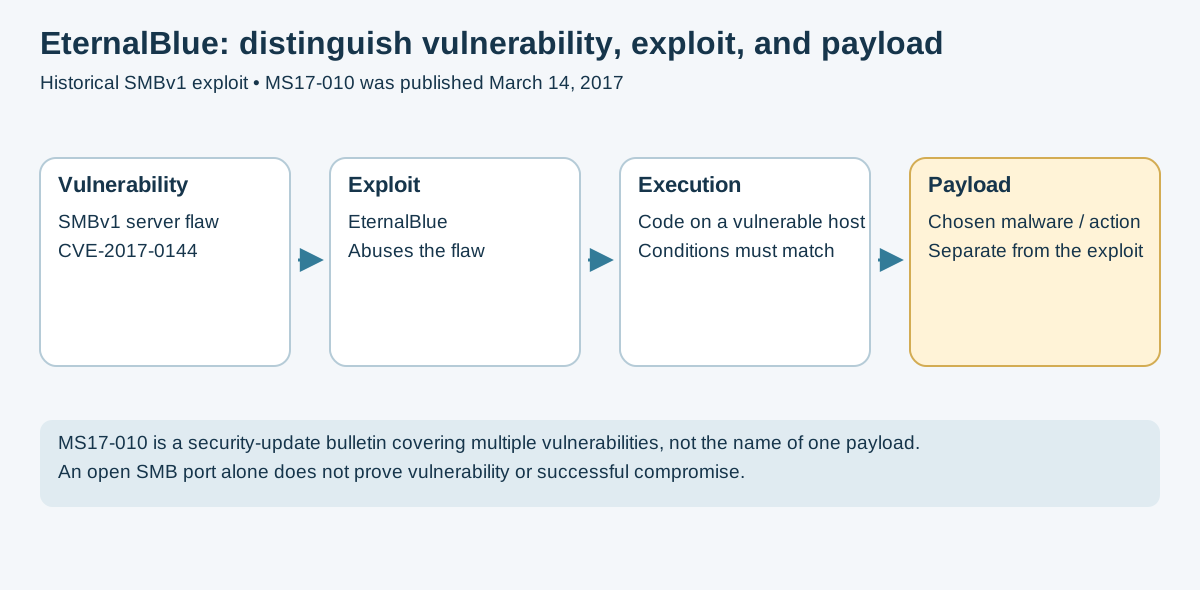
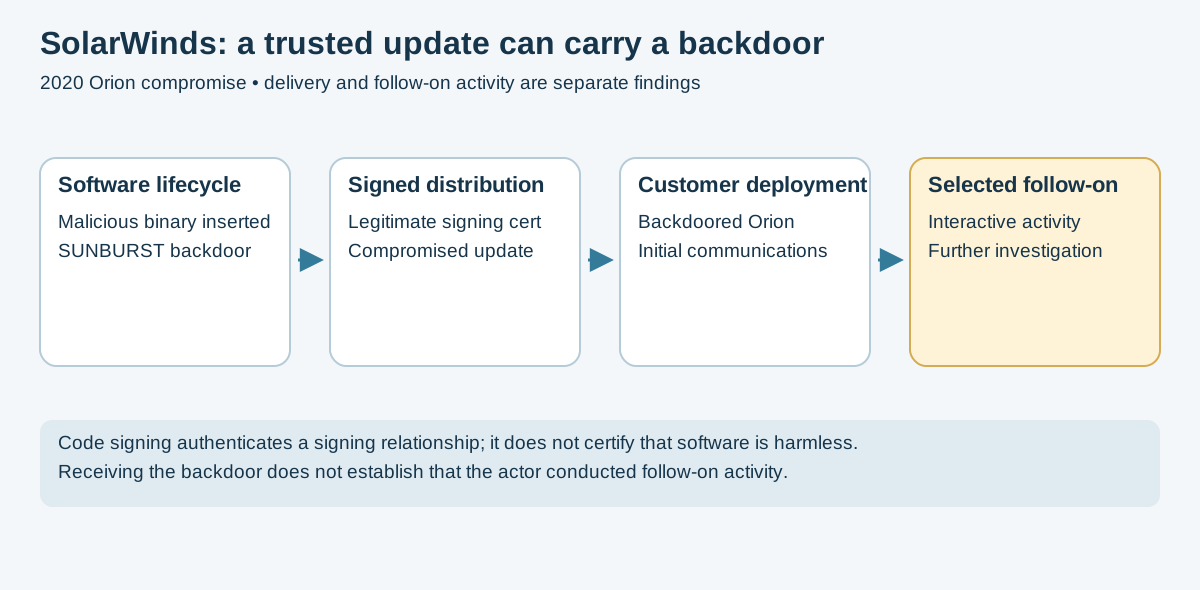
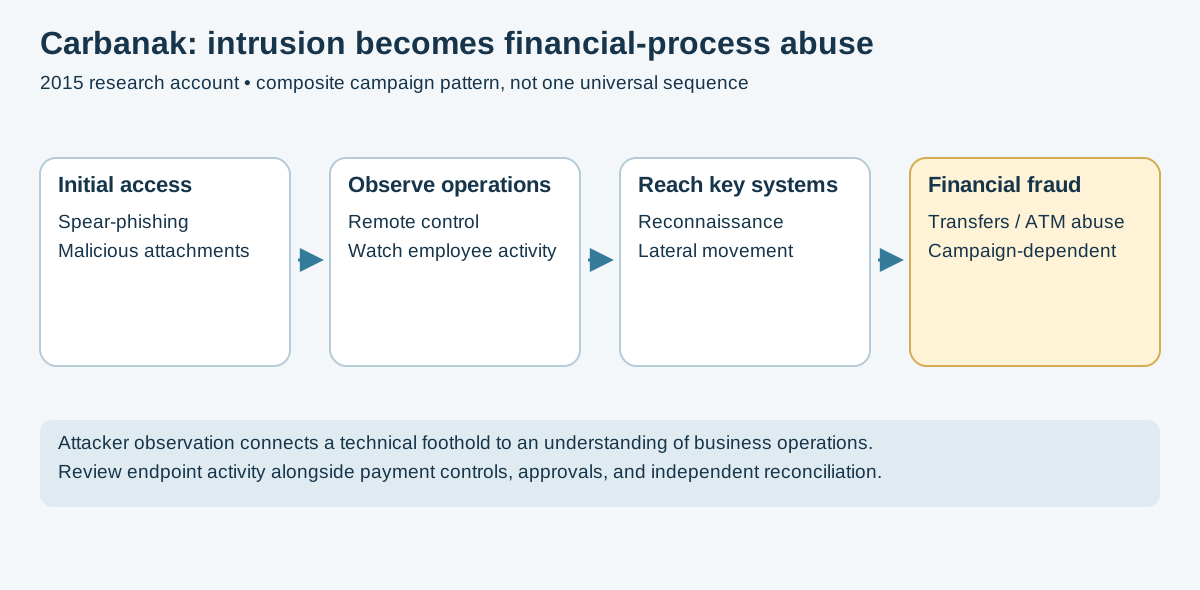
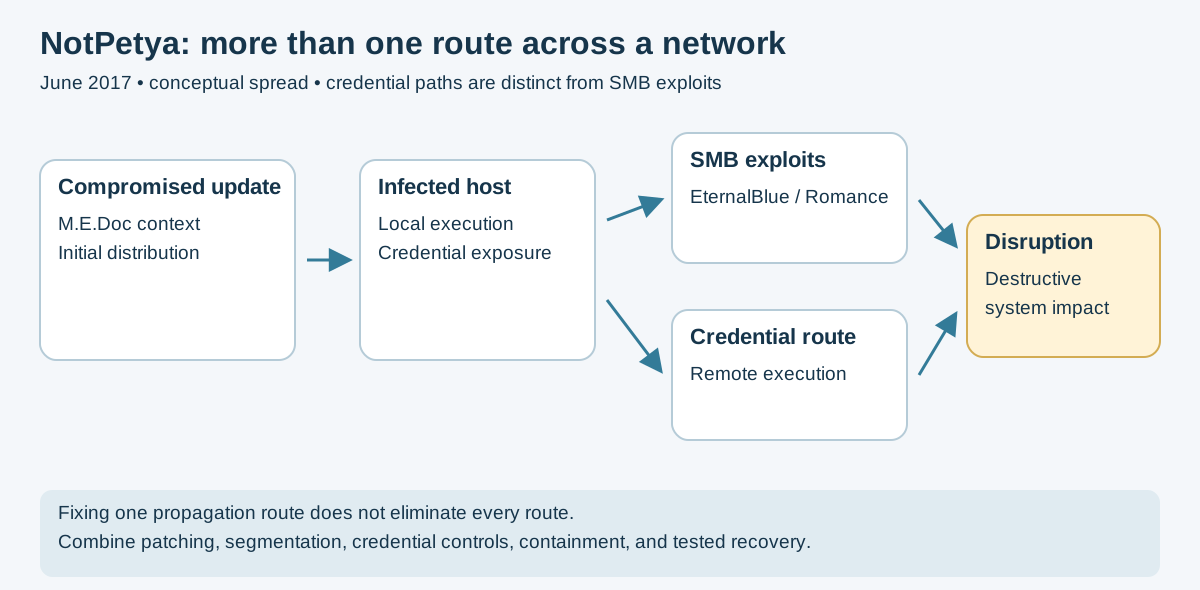
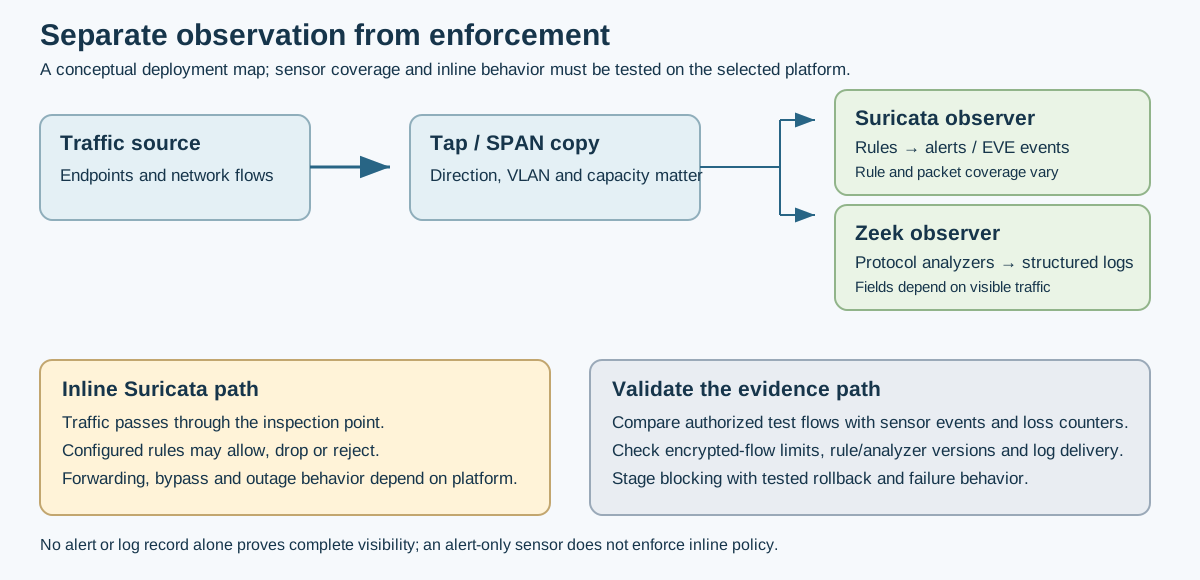
These twelve original static vector diagrams explain mechanisms and evidence limits in the other case studies. They contain no measured traces or reproduced exploit results. Each figure has an accessible title and description; source links and provenance appear in its embedding caption.
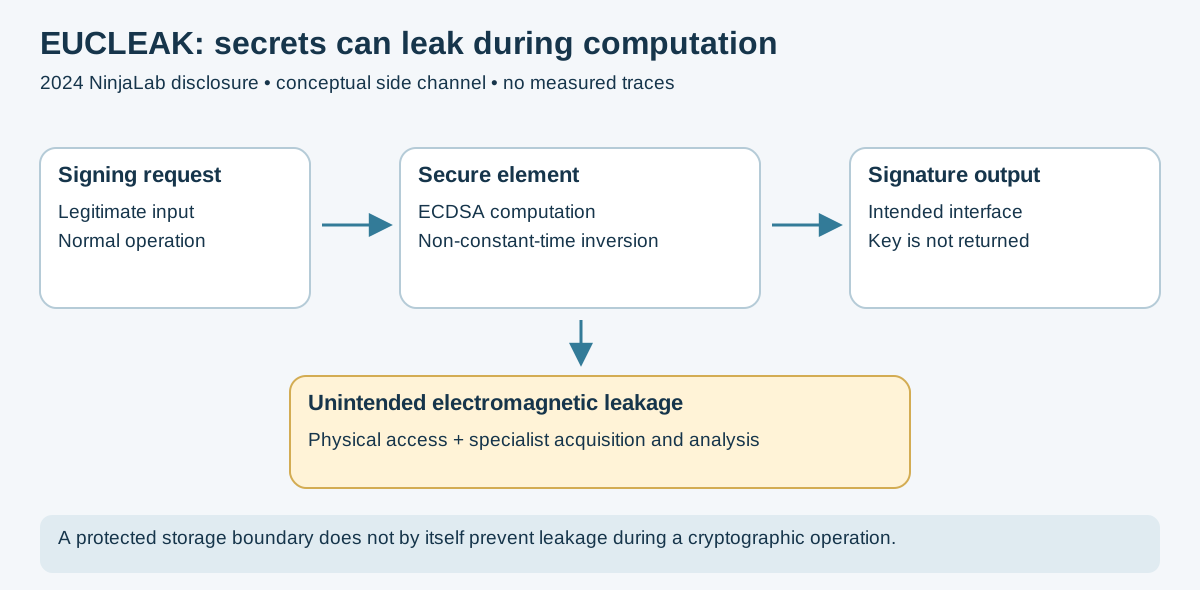
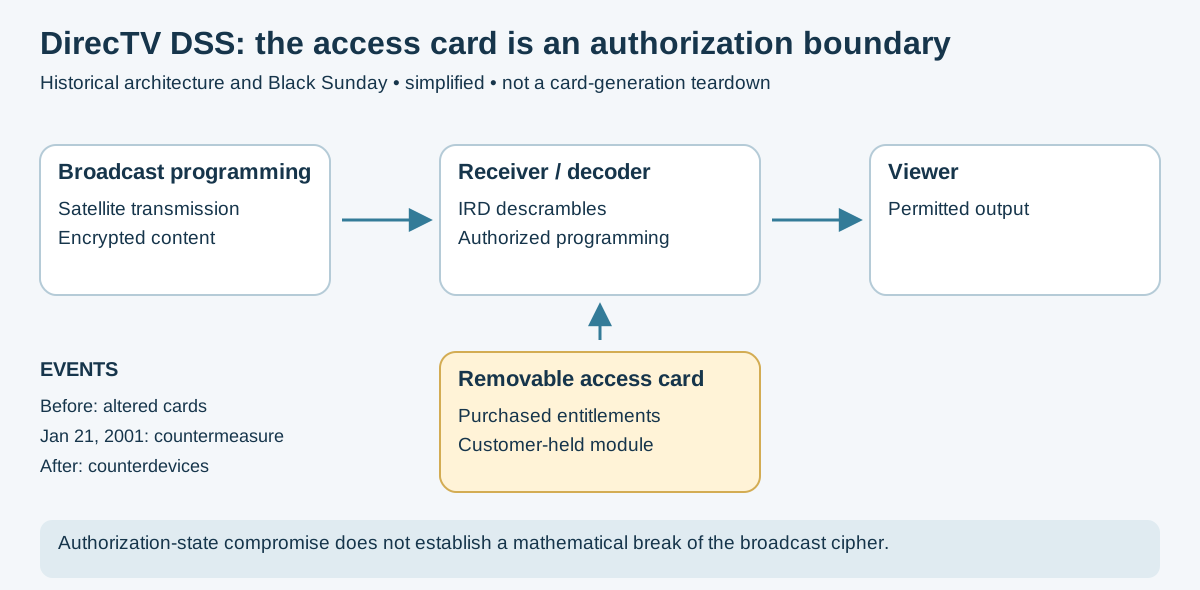
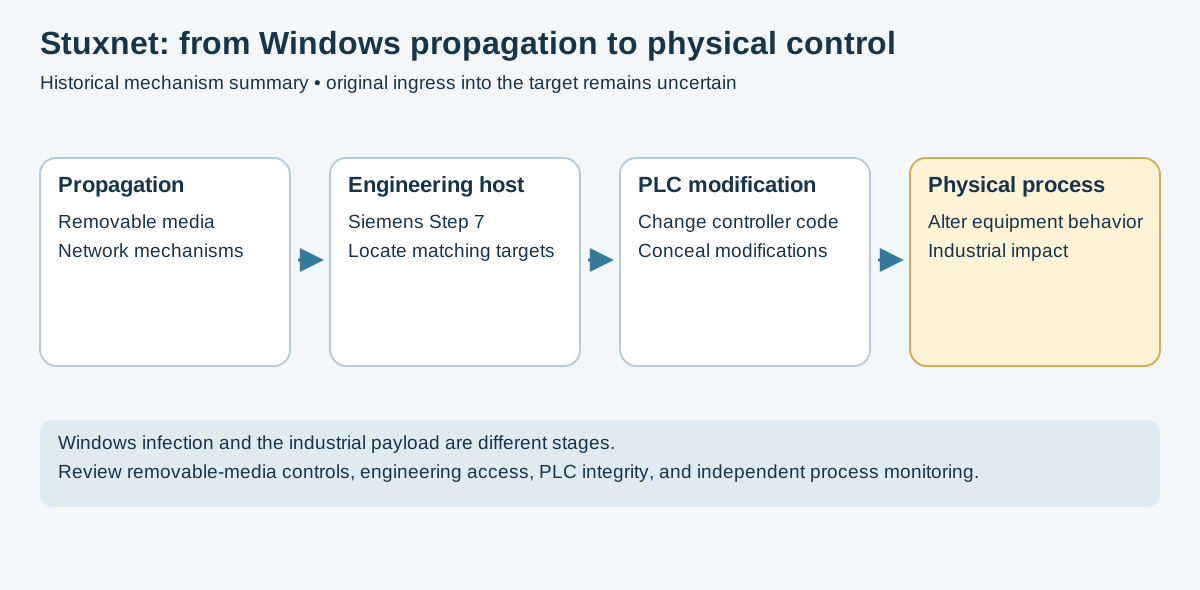
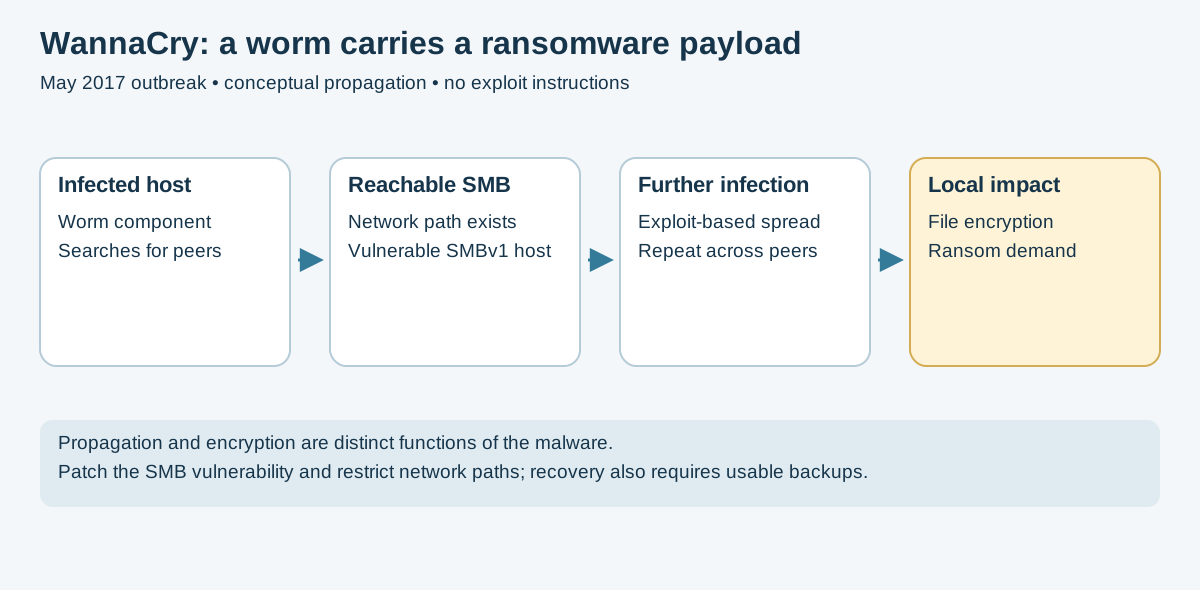
Original conceptual diagram distinguishing mirrored sensor copies, alert/protocol logs and inline enforcement.
| Diagram | Embedded guide |
|---|---|
| Suricata and Zeek visibility and blocking | Suricata & Zeek deployment guide |
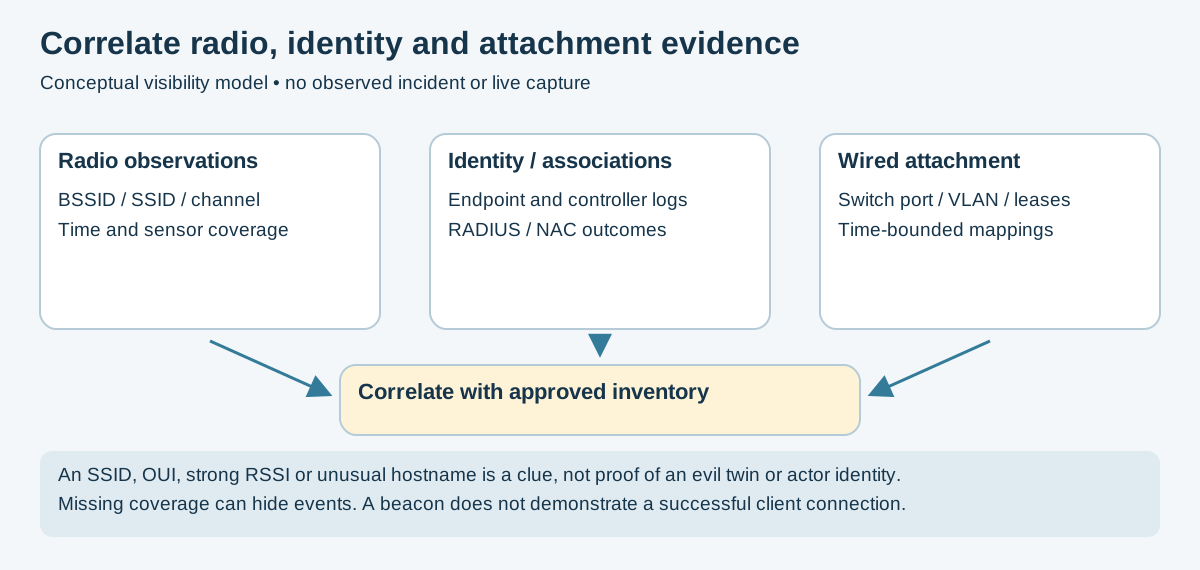
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| network intrusion evidence correlation | Guide |
| network intrusion containment recovery | Guide |
| network intrusion filter vs aggregation | Guide |
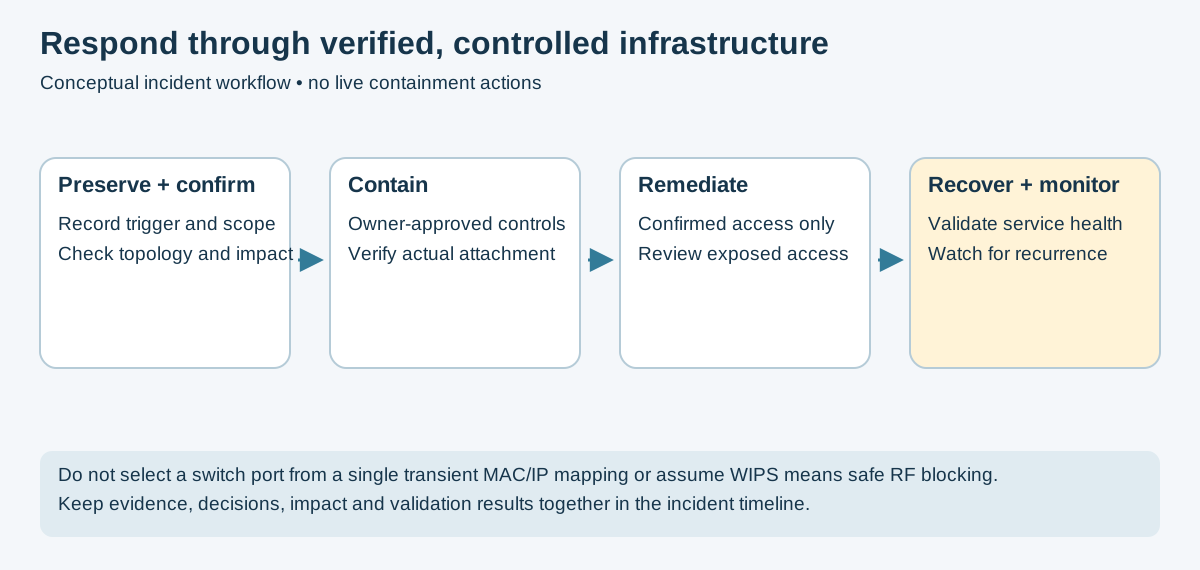
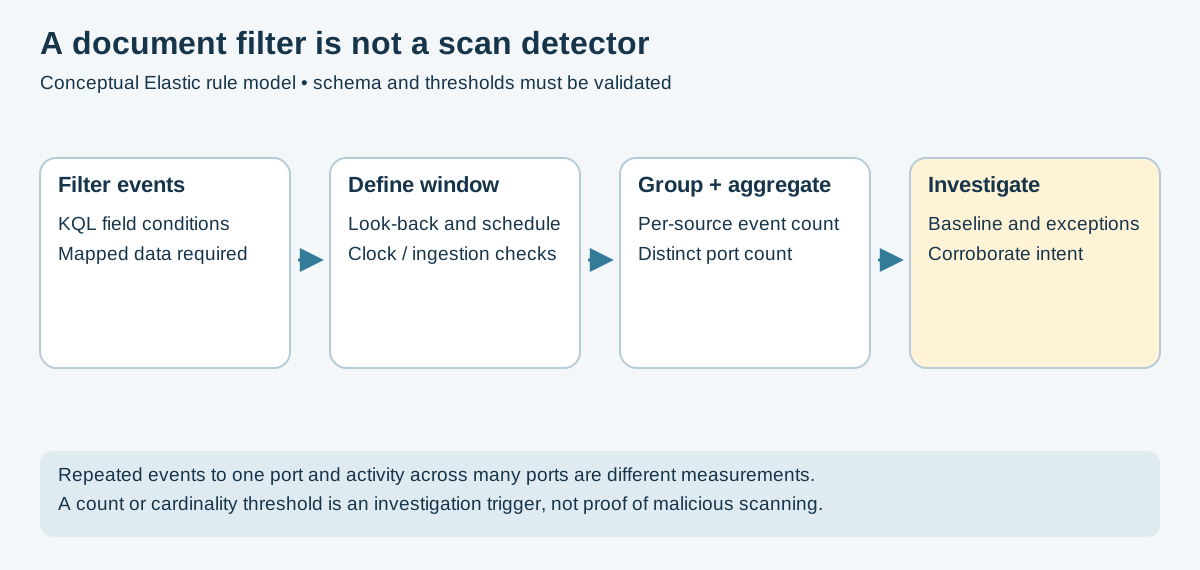
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| azure security rbac scope | Guide |
| azure security logging coverage | Guide |
| azure security role planes | Guide |
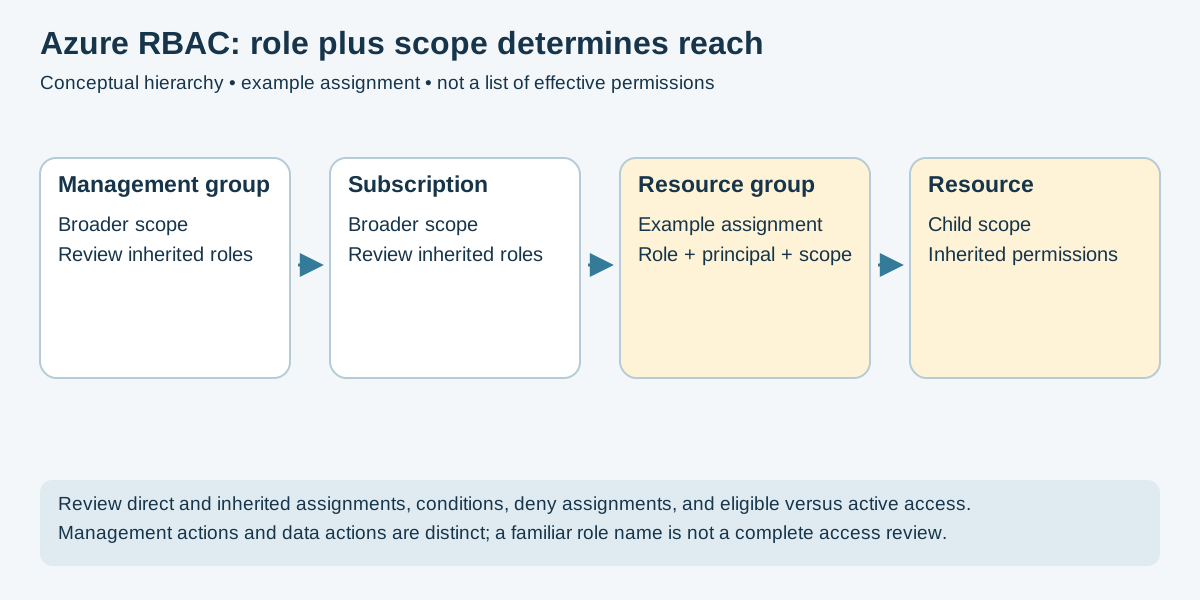
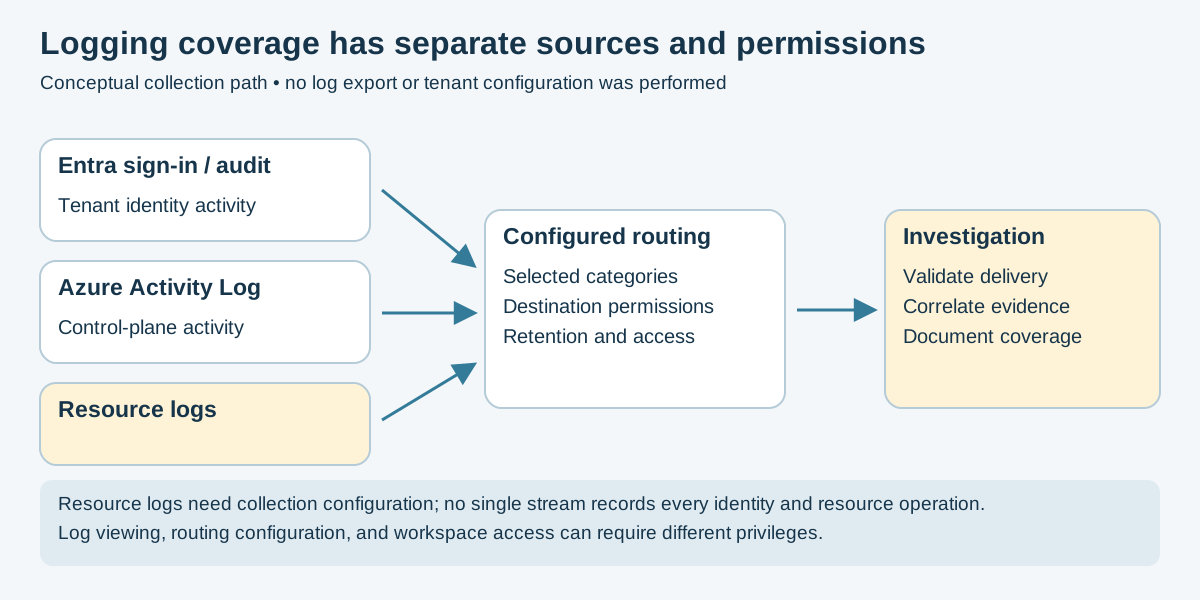
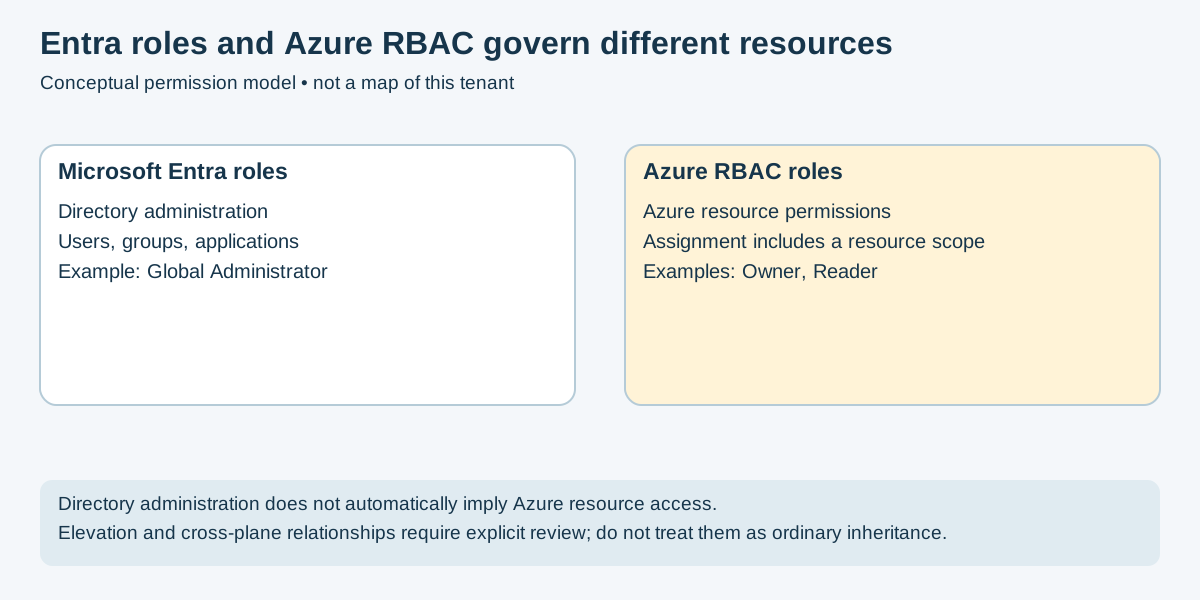
Original conceptual diagrams that summarize authorization gates and evidence handling.
| Diagram | Embedded guide |
|---|---|
| Mobile test scope gates | Mobile penetration testing SOP |
| Mobile test evidence chain | Mobile penetration testing SOP |
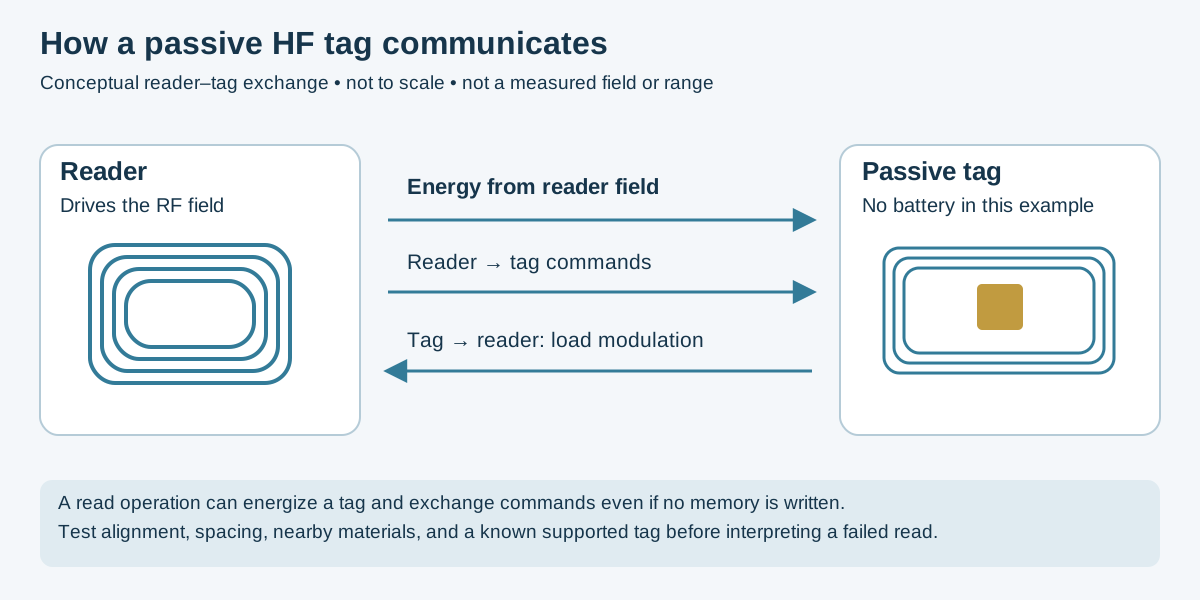
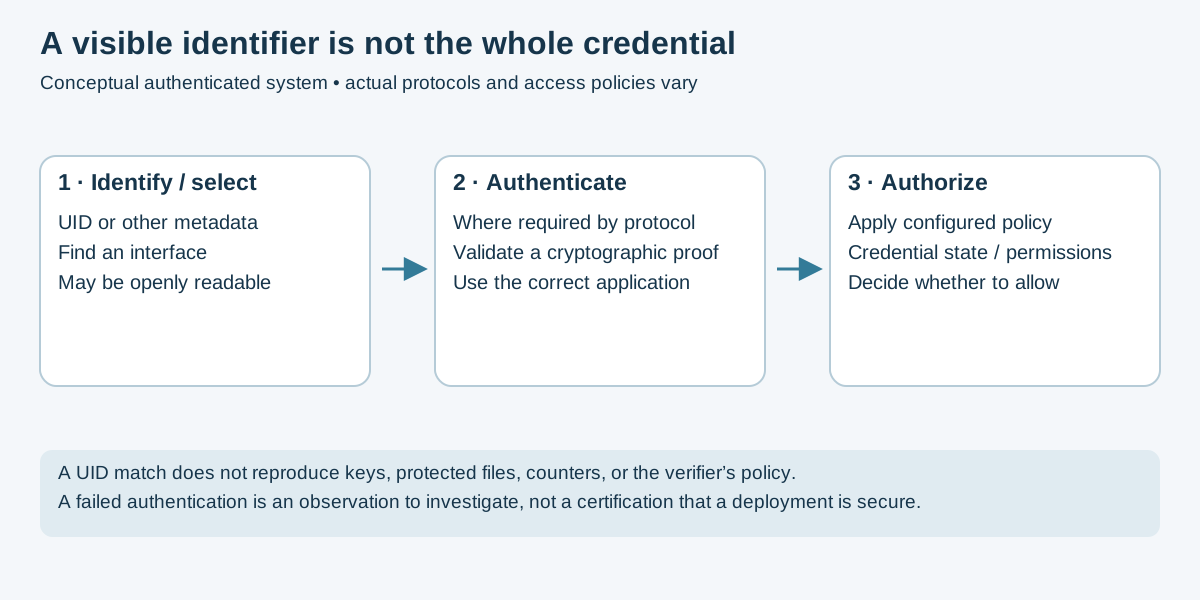
Original conceptual diagrams embedded in the RFID & NFC guide. Captions link primary technical references; no device testing or measured RF data is claimed.
| Diagram | What It Explains |
|---|---|
| Passive HF coupling | Reader energy, commands, and tag load modulation. |
| Identification, authentication, authorization | Why an identifier is only one part of a credential system. |
| Band and reader map | LF, HF/NFC, and the separate UHF reader ecosystem. |
| Read troubleshooting | Compatibility checks, controlled observations, and defensible conclusions. |
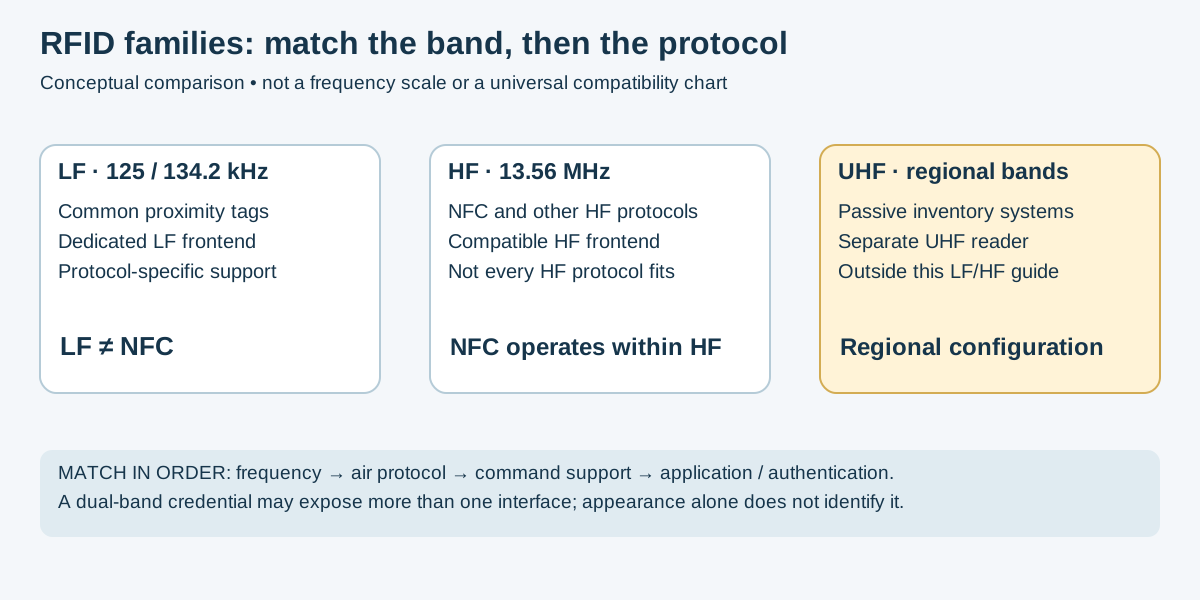
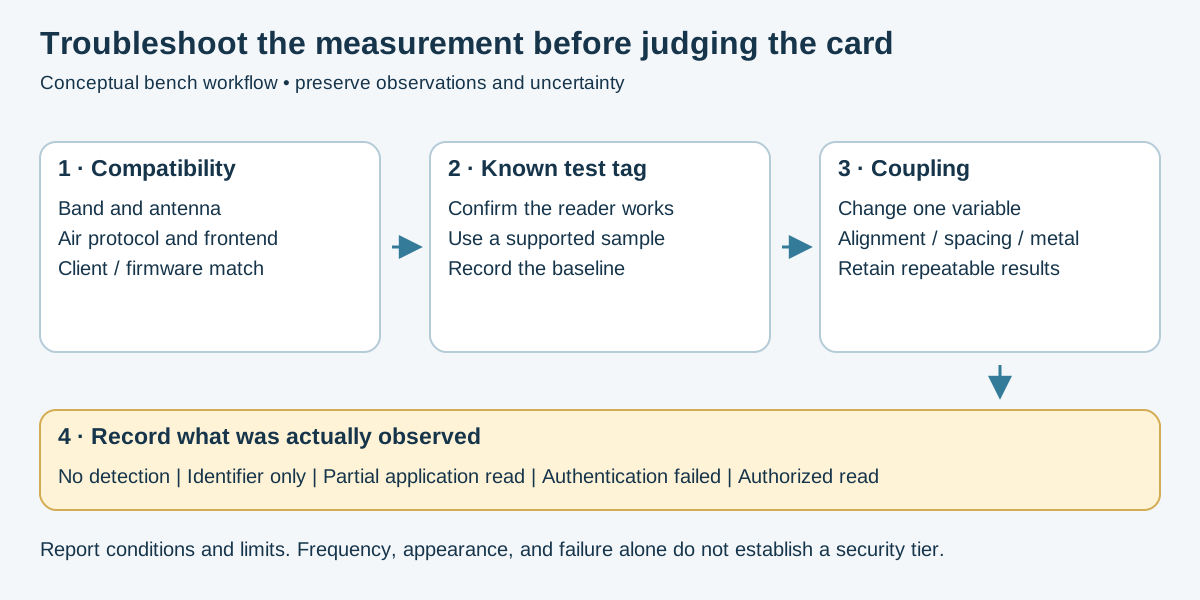
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| supply chain complementary evidence | Guide |
| supply chain subject binding | Guide |
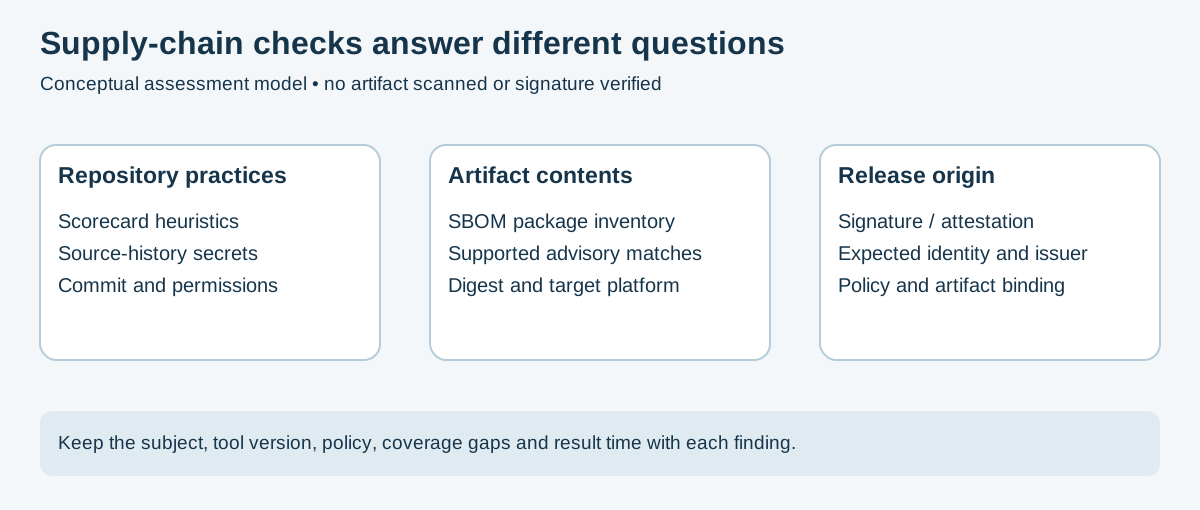
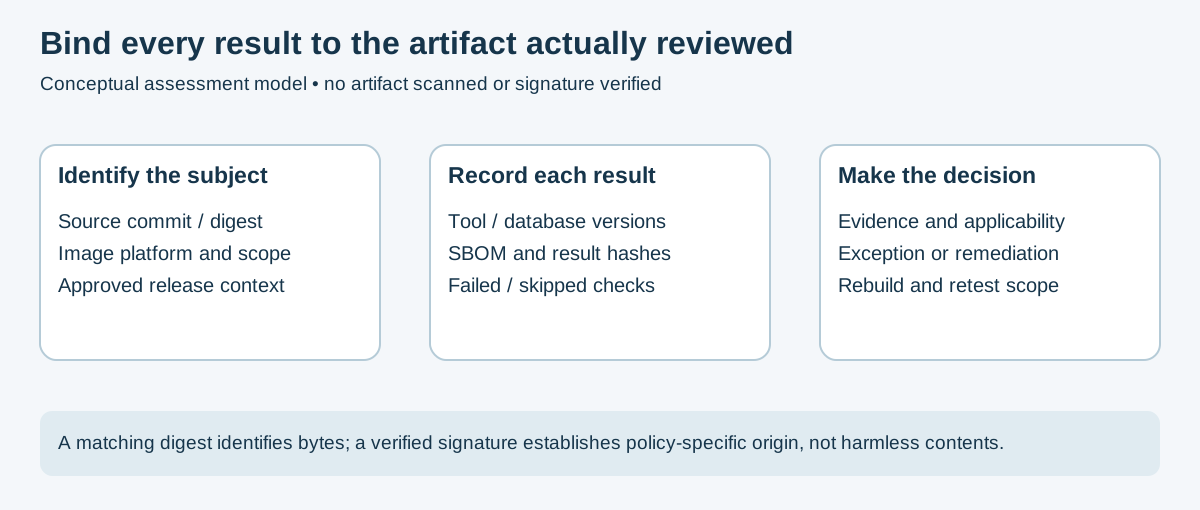
Original conceptual capture-path diagram; validate the expected test flow against packets received at the sensor.
| Diagram | Embedded guide |
|---|---|
| Proxmox sensor visibility paths | Proxmox IDS / Security Onion checklist |
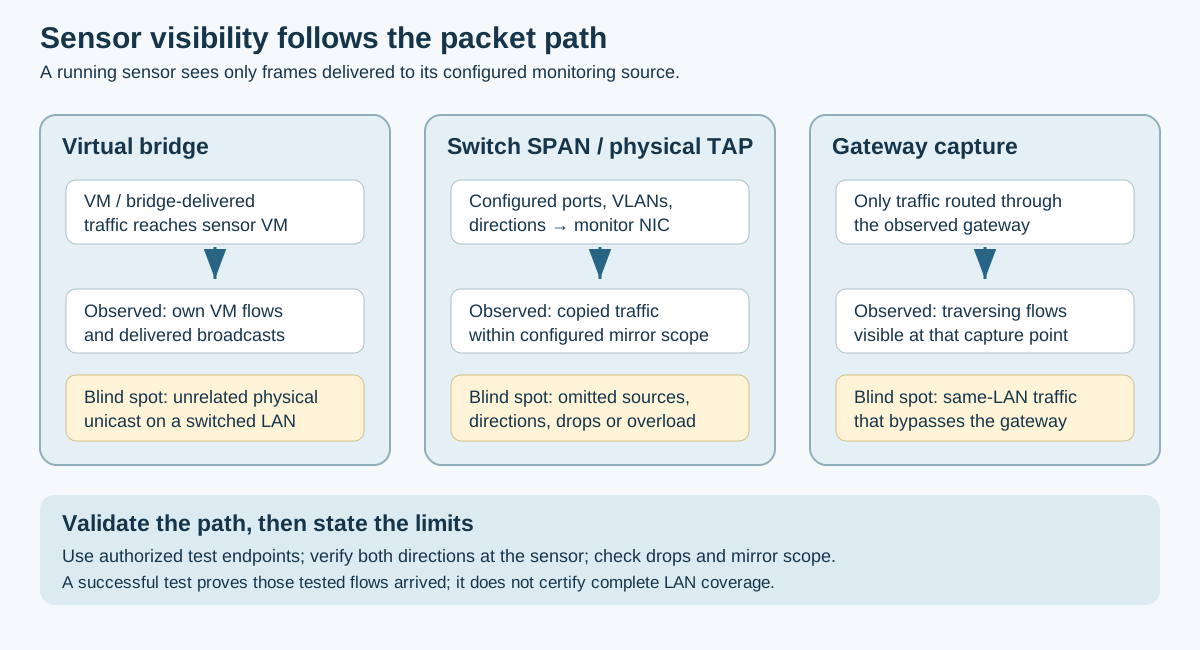
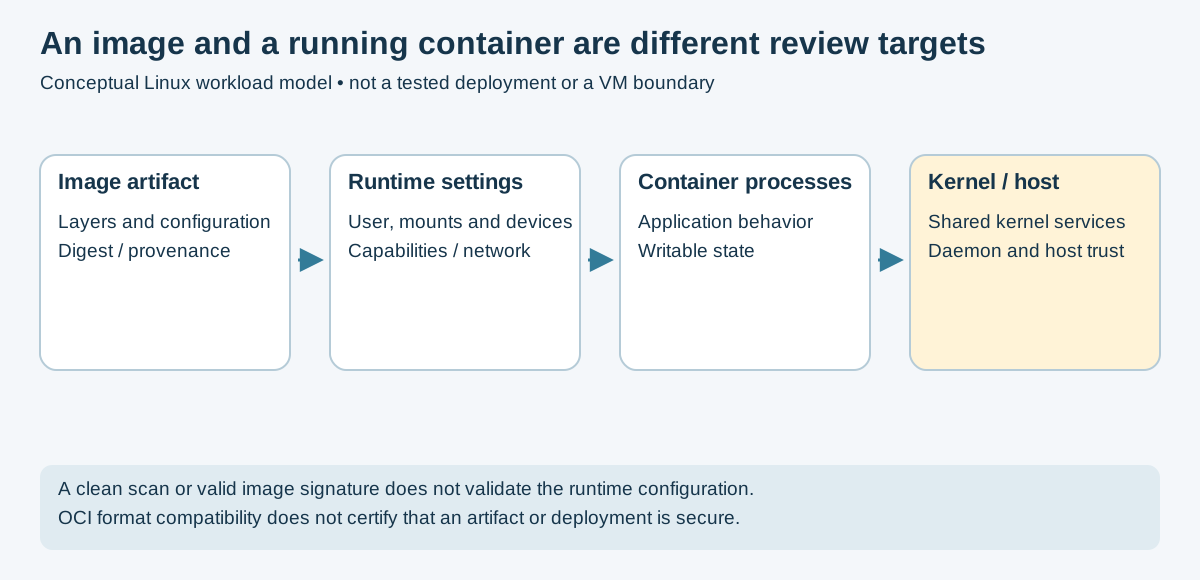
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
| container security image runtime host | Guide |
| container escape evidence paths | Guide |
| container security isolation controls | Guide |
| container security secrets lifecycle | Guide |
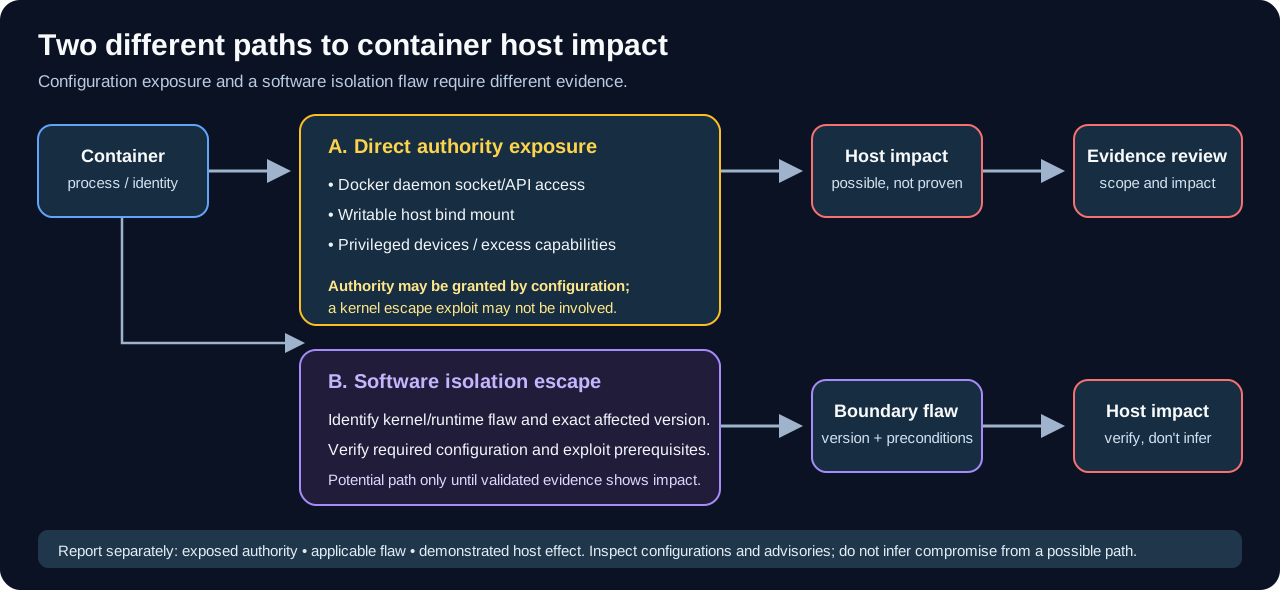
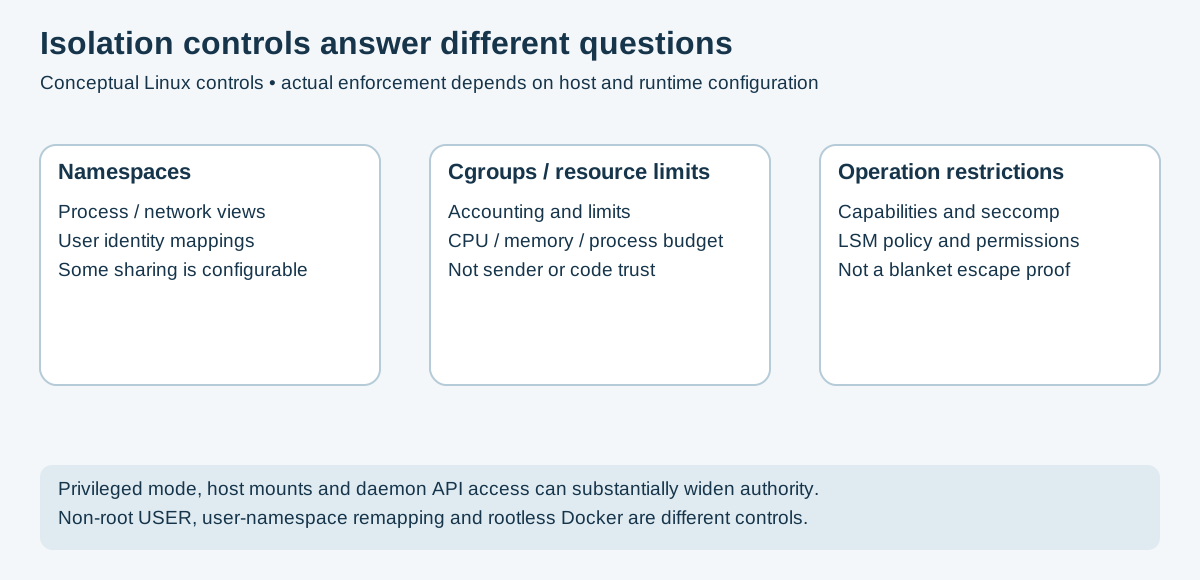
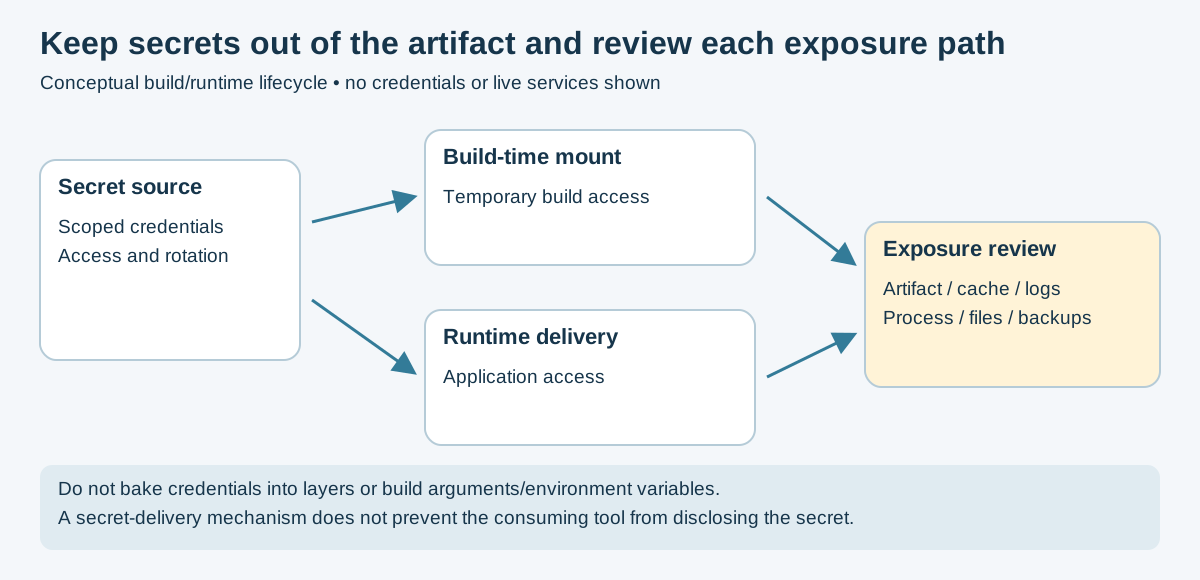
Distinguish direct authority exposure from software escape paths.
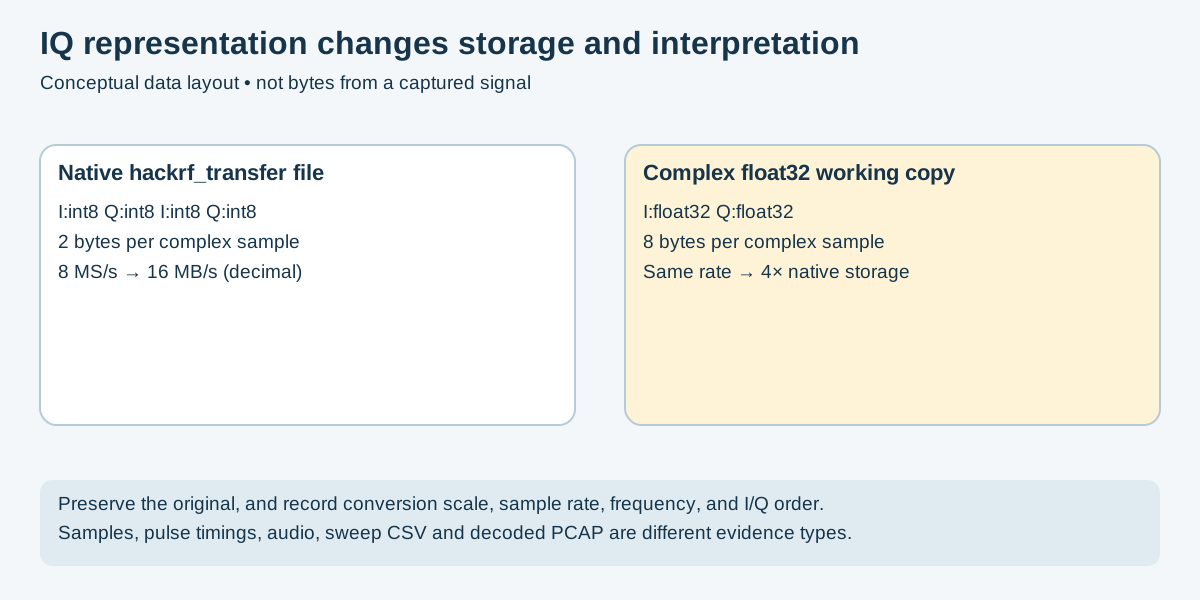
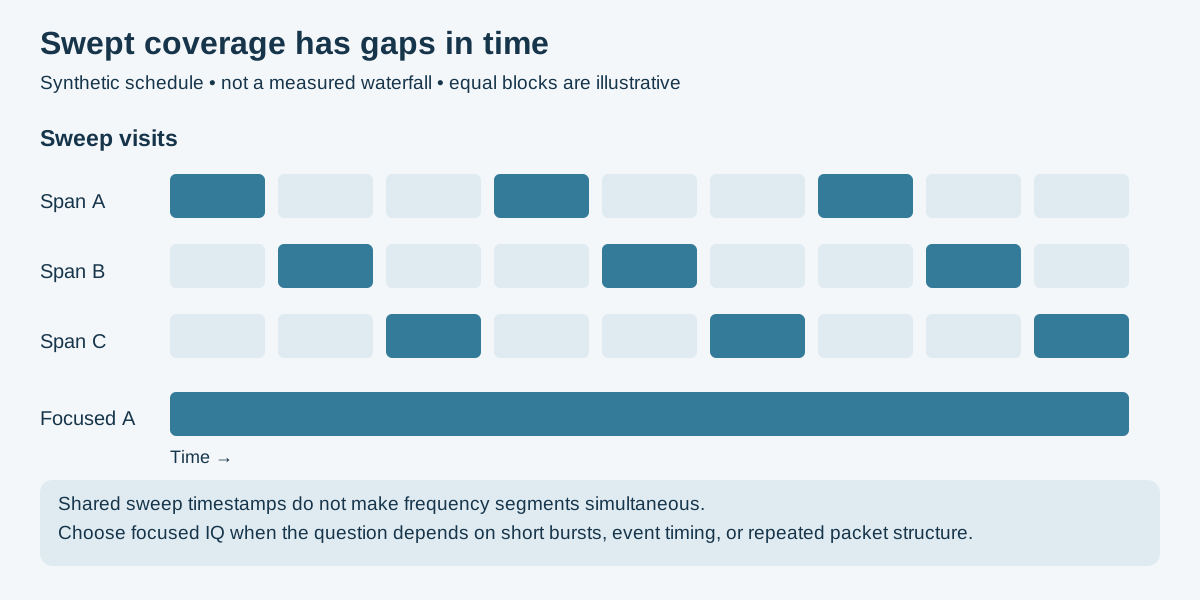
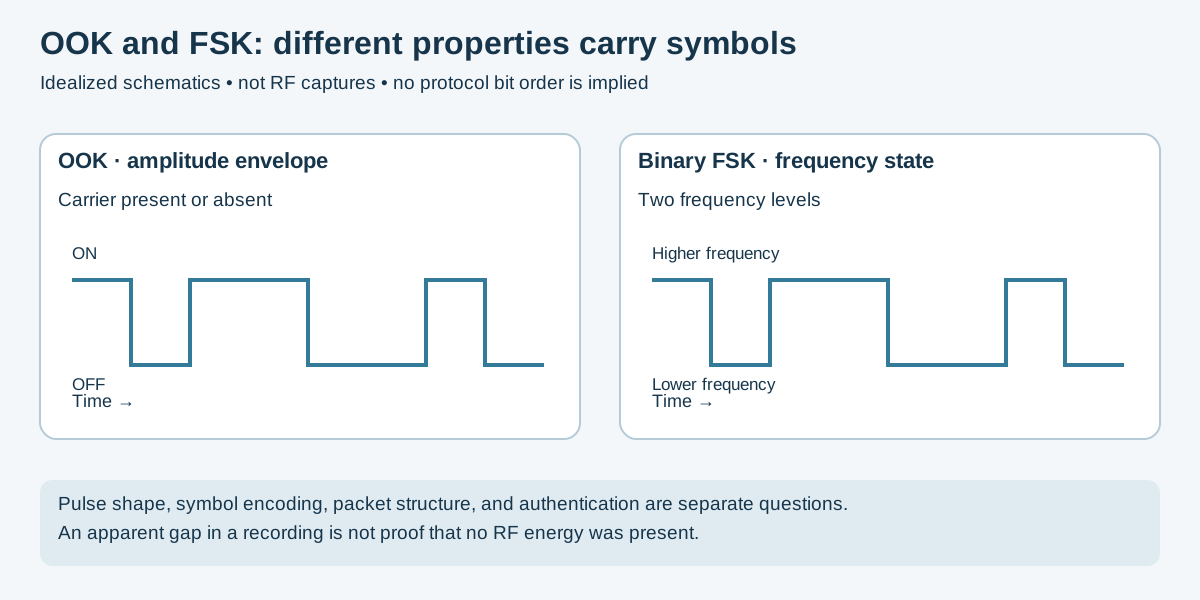
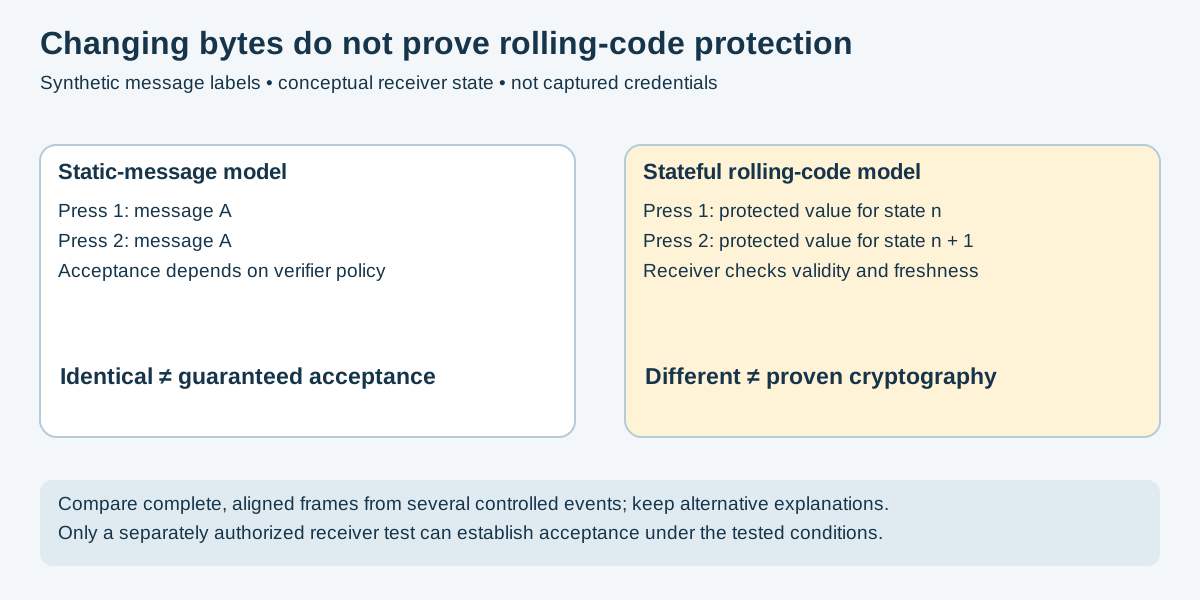
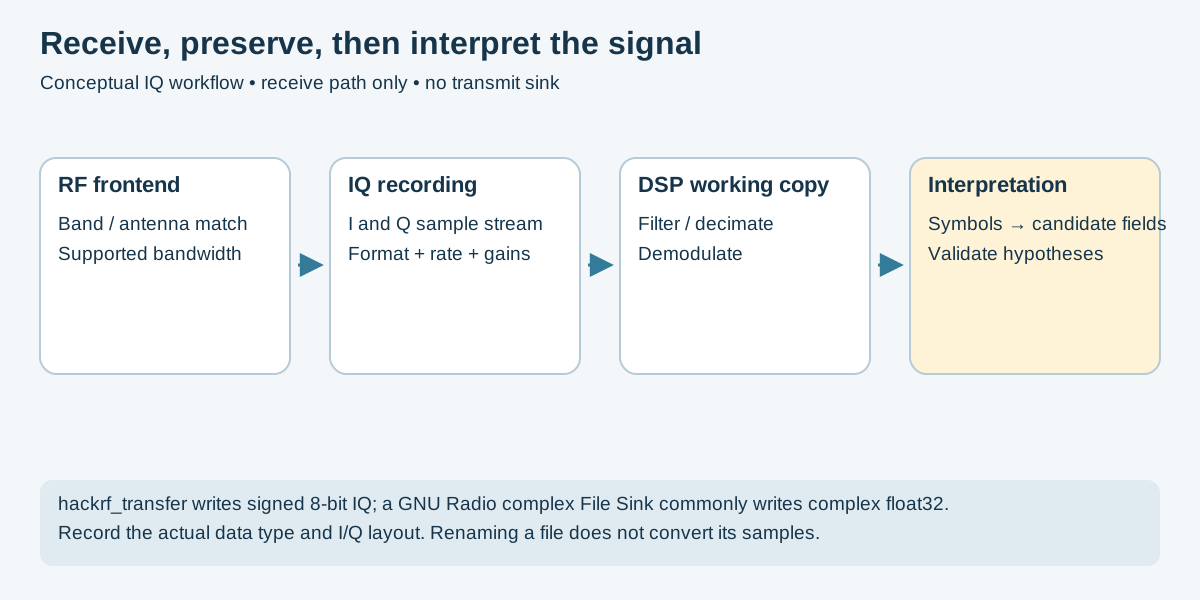
Five original conceptual diagrams embedded in the Sub-GHz RF guide. The waveform and packet examples are synthetic, not captured signals. Each caption identifies its source context and evidence limits.
| Diagram | What It Explains |
|---|---|
| OOK versus FSK | Amplitude-envelope versus frequency-state signaling. |
| Fixed versus stateful validation | Why repeated or changing messages do not alone establish replay security. |
| IQ to evidence | Capture, metadata, working-copy processing, and interpretation. |
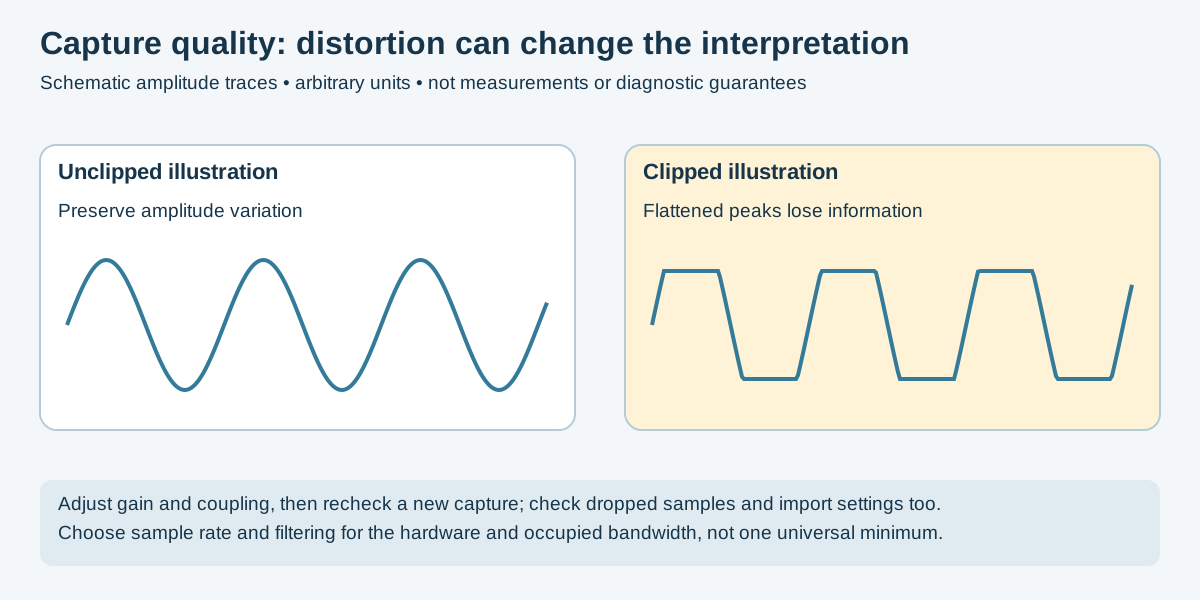
| Capture quality | Schematic clipping and the limits of visual diagnosis. |
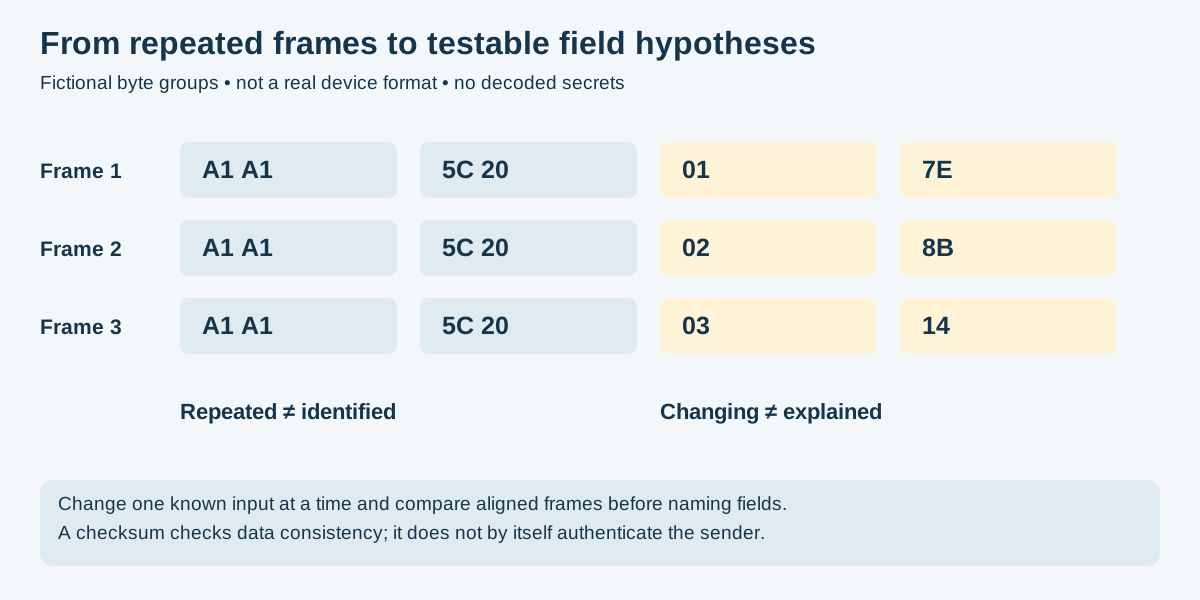
| Frame inference | Distinguishing repeated/changing regions from verified field meanings. |
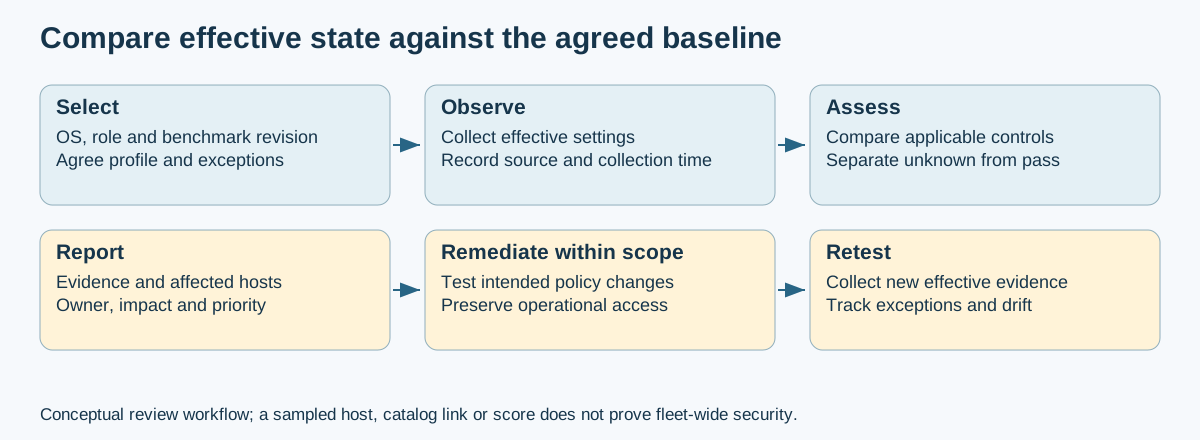
Original conceptual workflow; the checklist separates baseline selection, effective evidence and scoped follow-up.
| Diagram | Embedded guide |
|---|---|
| Windows build review evidence flow | Windows Build Review checklist |
Original conceptual figures; source links and evidence limits appear in the guide captions.
| Diagram | Embedded guide |
|---|---|
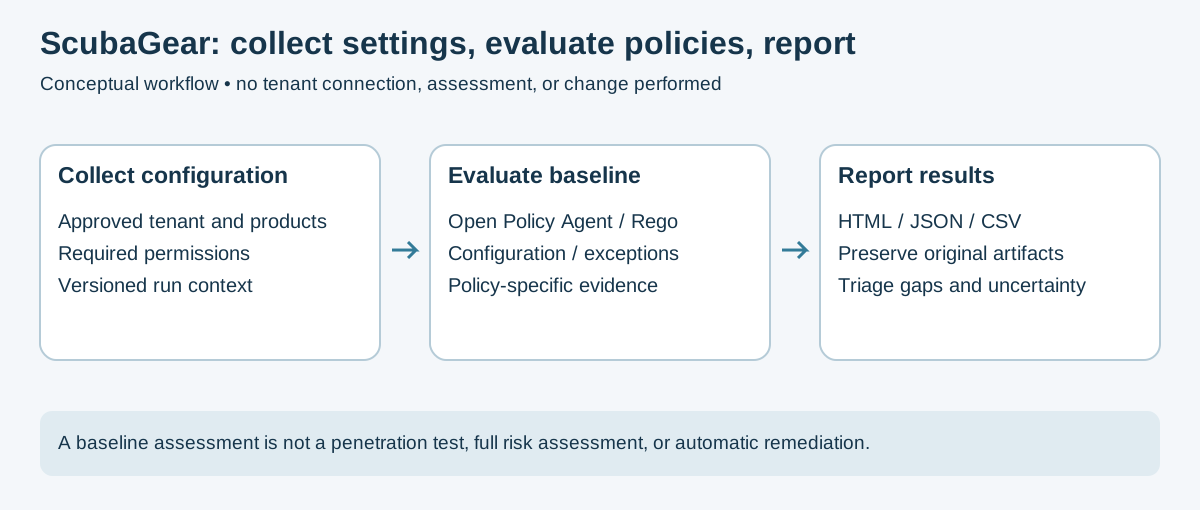
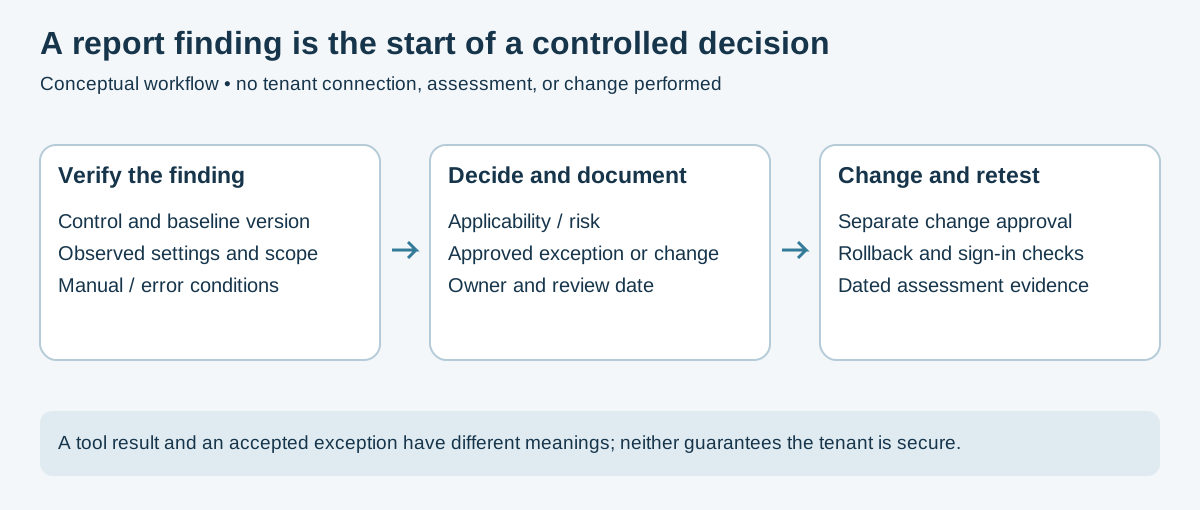
| scuba configuration assessment | Guide |
| scuba findings to controlled change | Guide |
- advnacedflows.jpg — a large image with an ambiguous filename. Not embedded automatically because its intended subject has not been visually verified; avoid mismatched or misleading placement. Review the image and rename or document its subject before assigning it.
Two original conceptual figures embedded in the receive-only telemetry lab.
| Diagram | Purpose |
|---|---|
| Decoder to collector | Separate native decoder output, normalization and collector validation. |
| Alert evidence limits | Investigate benign alternatives and corroborate anomalies. |
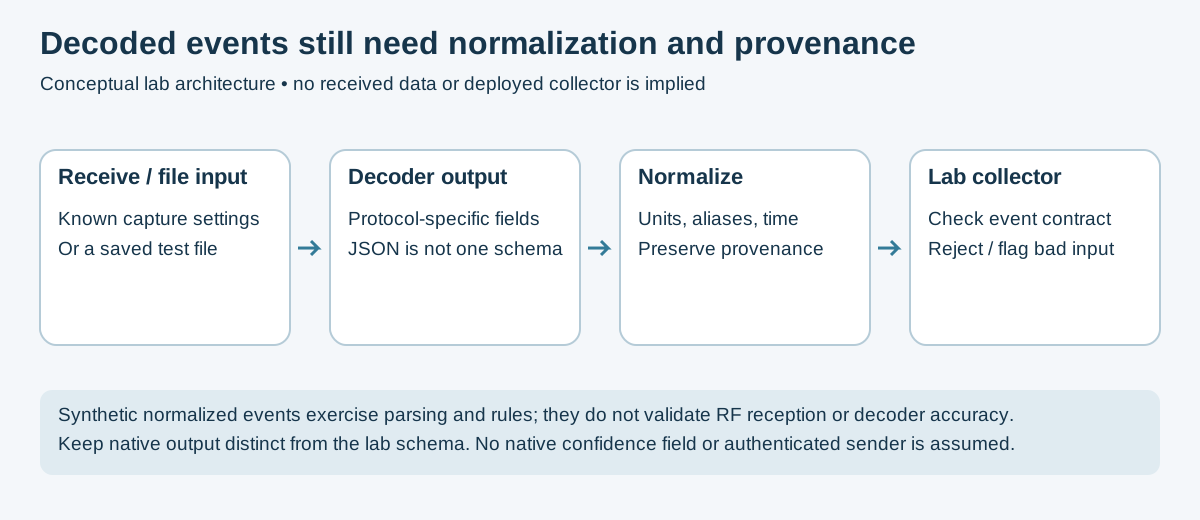
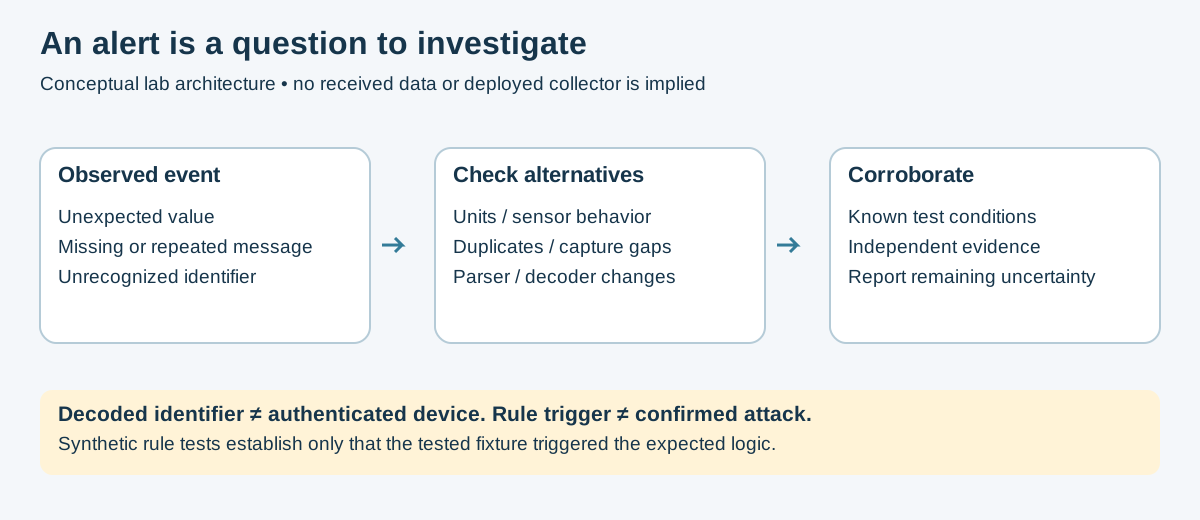
These illustrate a proposed lab; no live sensor data or deployed detection results are claimed.
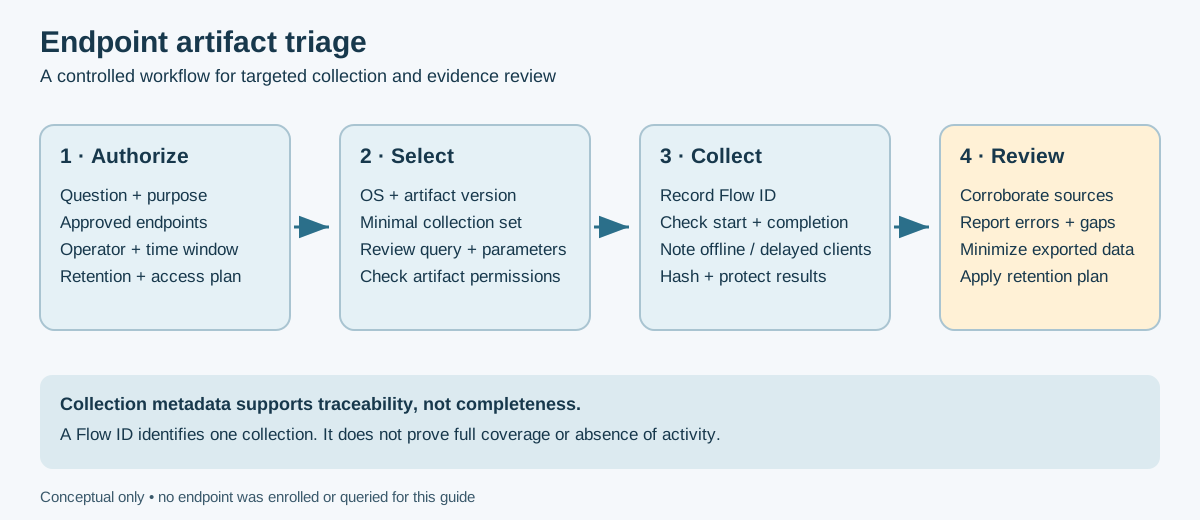
Original conceptual flow showing collection authorization, artifact selection and Flow ID/status review.
| Diagram | Embedded guide |
|---|---|
| Velociraptor endpoint triage flow | Velociraptor and ForensicArtifacts triage |
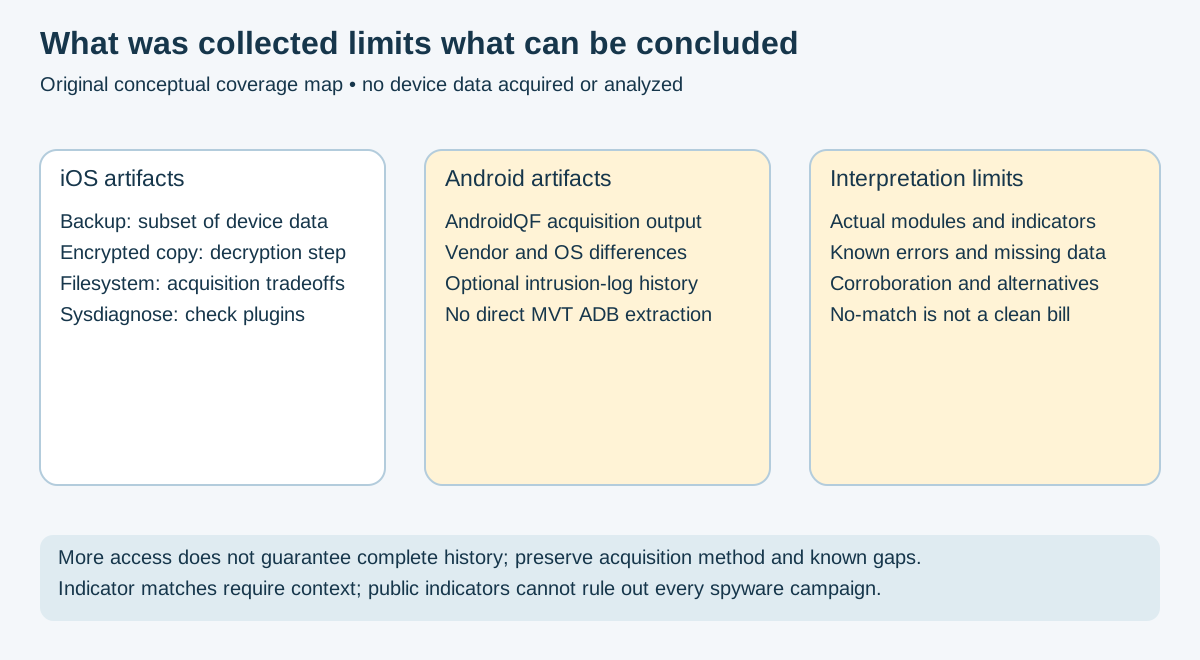
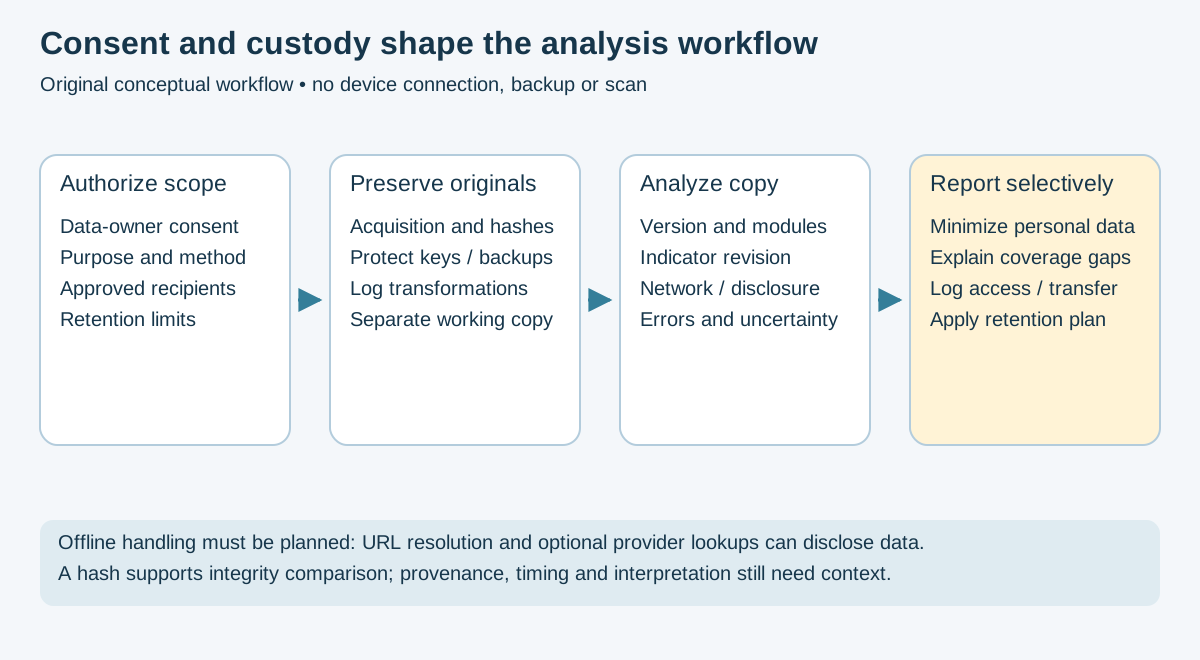
Original conceptual diagrams; MVT release behavior and evidence limits are documented in the guide.
| Diagram | Embedded guide |
|---|---|
| MVT artifact coverage | MVT forensic triage |
| MVT consent and custody | MVT forensic triage |
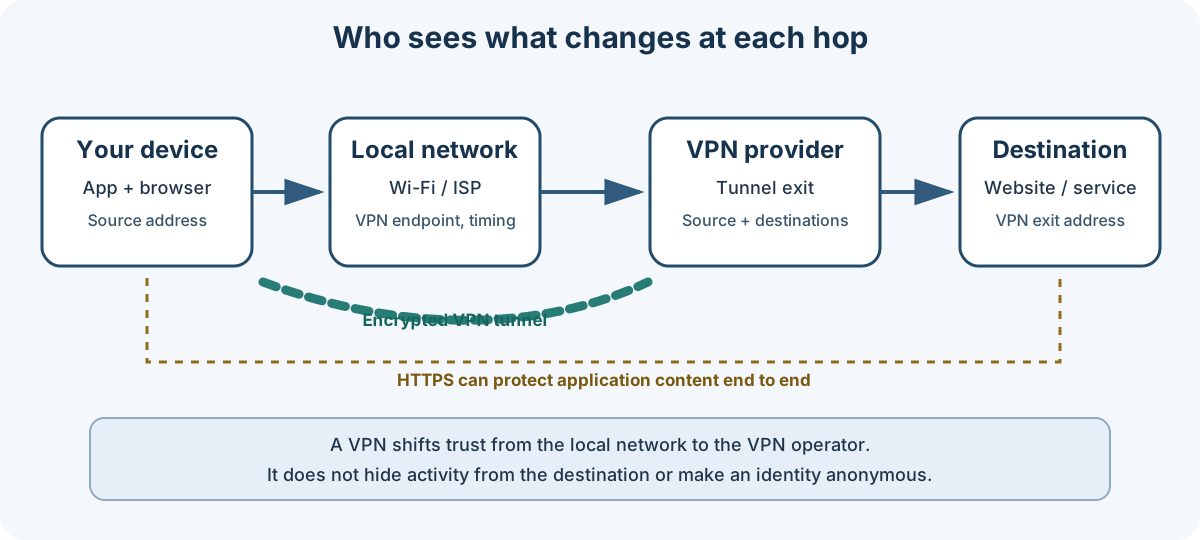
Original conceptual diagram separating what the local network, VPN operator, and destination may observe. HTTPS remains an independent end-to-end protection.
| Diagram | Embedded guide |
|---|---|
| VPN trust boundaries | VPN Security Guide |
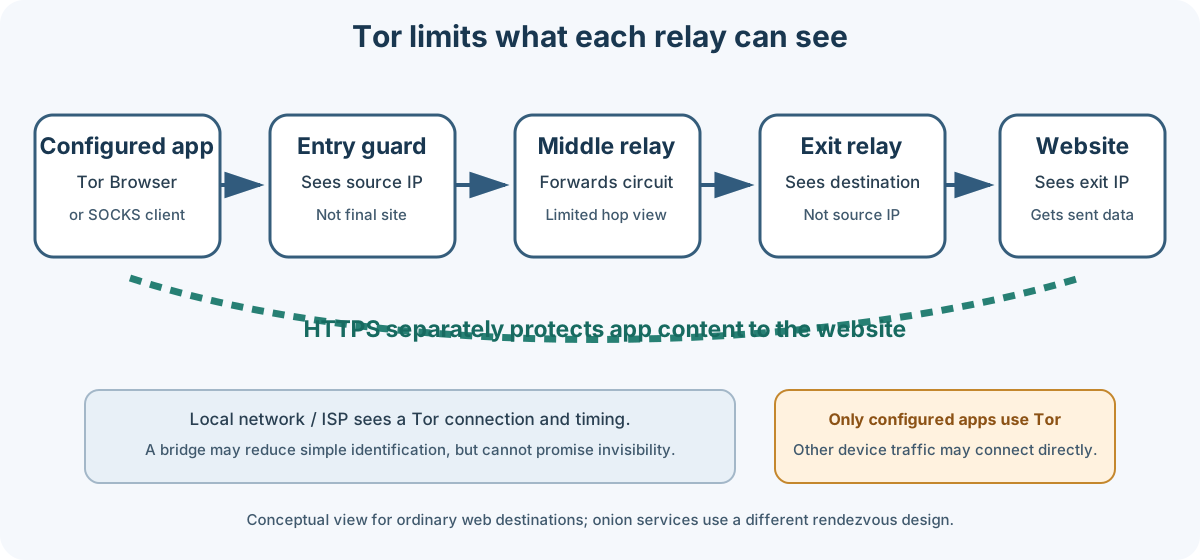
Original conceptual diagram separating Tor Browser or explicitly configured client traffic from other device traffic, with relay roles and the independent role of HTTPS.
| Diagram | Embedded guide |
|---|---|
| Tor circuit and relay visibility | Tor Browser and Tor Network Guide |
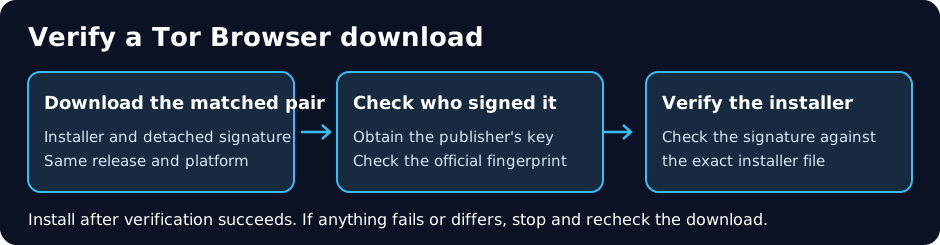
| Tor Browser download verification | Install and update Tor Browser |
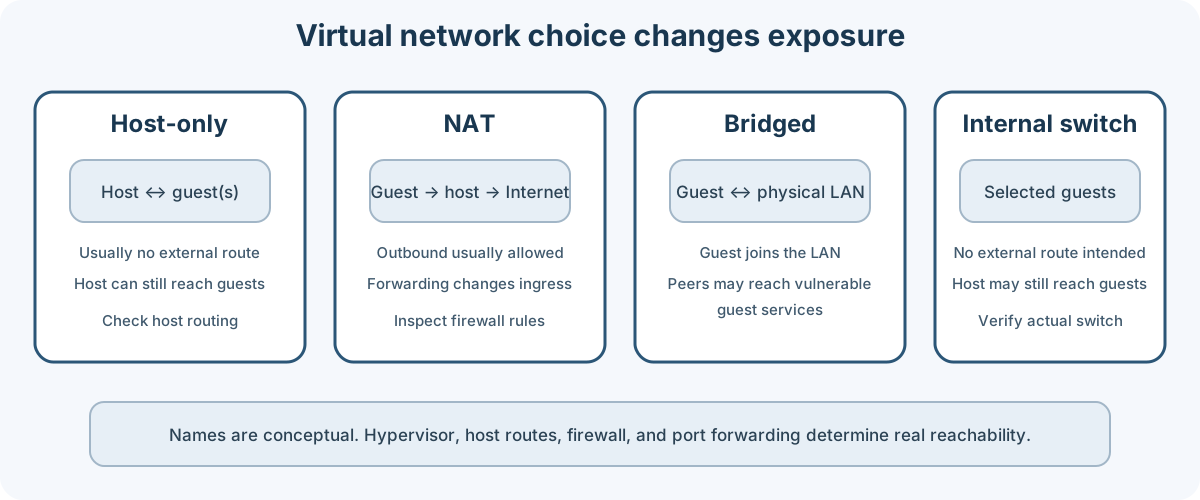
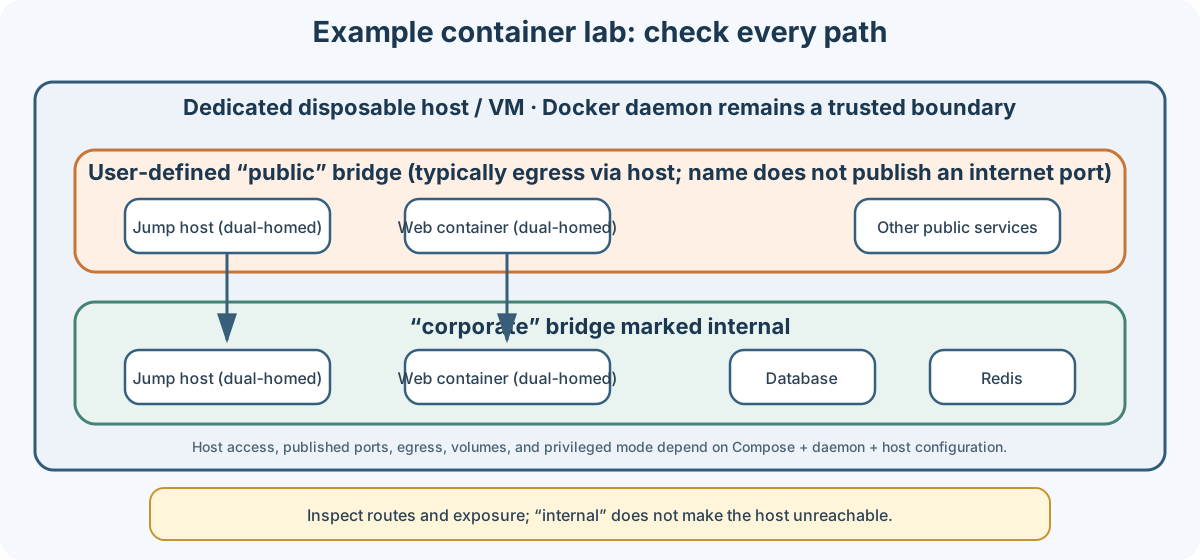
Original conceptual diagrams illustrating common VM network exposure and the Black Hat Bash container network roles. Actual reachability depends on the hypervisor, Docker Compose configuration, daemon, host routes, firewall, and published ports.
| Diagram | Embedded guide |
|---|---|
| VM network isolation modes | VM and lab environments |
| Black Hat Bash lab boundaries | VM and lab environments |
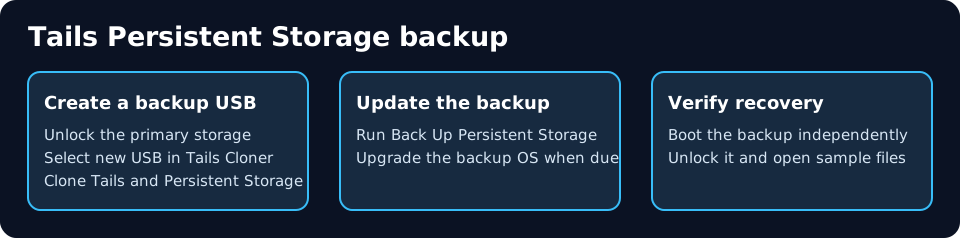
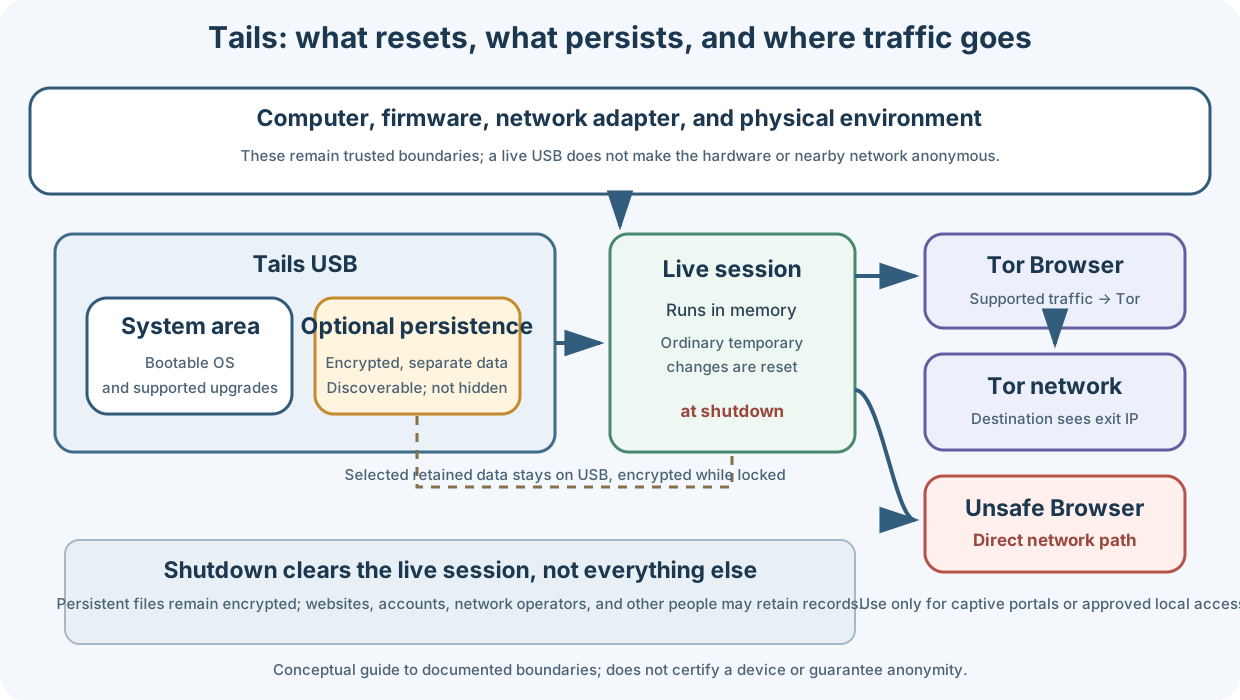
Original conceptual diagram separating the Tails system area, volatile live session, optional encrypted Persistent Storage, Tor Browser traffic, and the Unsafe Browser's direct-network exception.
| Diagram | Embedded guide |
|---|---|
| Tails Persistent Storage backup | Tails USB setup guide |
| Tails storage and network boundaries | Tails USB setup guide |
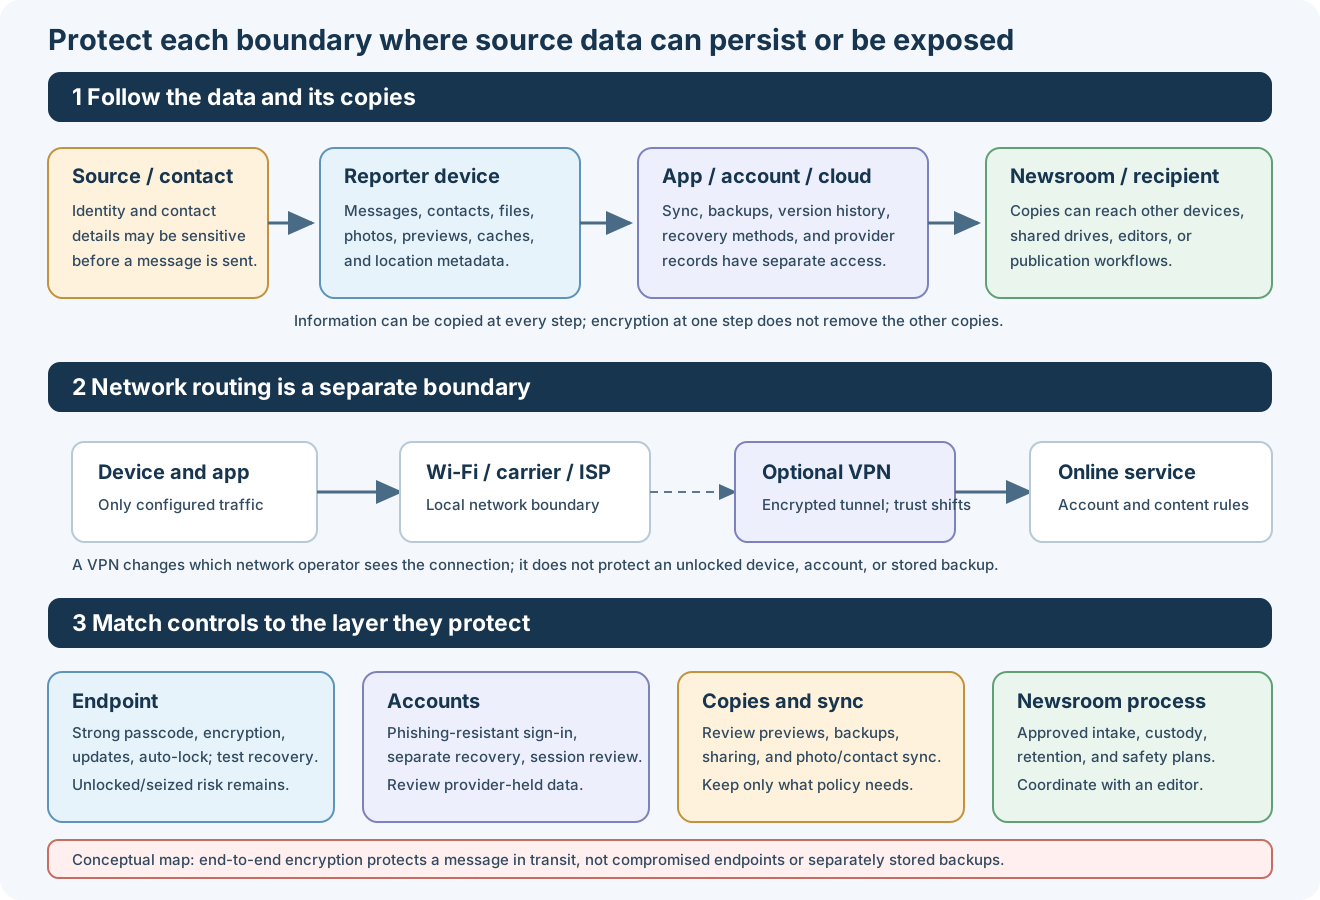
Original conceptual data-flow map emphasizing that device, account, copy/sync, and network protections address different boundaries.
| Diagram | Embedded guide |
|---|---|
| Journalist device, account, and network boundaries | Journalist device and network protection |
Original conceptual workflow for data minimization, protection, retention review, legal holds, and authorized disposal. It does not specify a legal retention period or sanitize media automatically.
| Diagram | Embedded guide |
|---|---|
| Journalist source-data lifecycle | Data retention, minimization and lawful disposal |
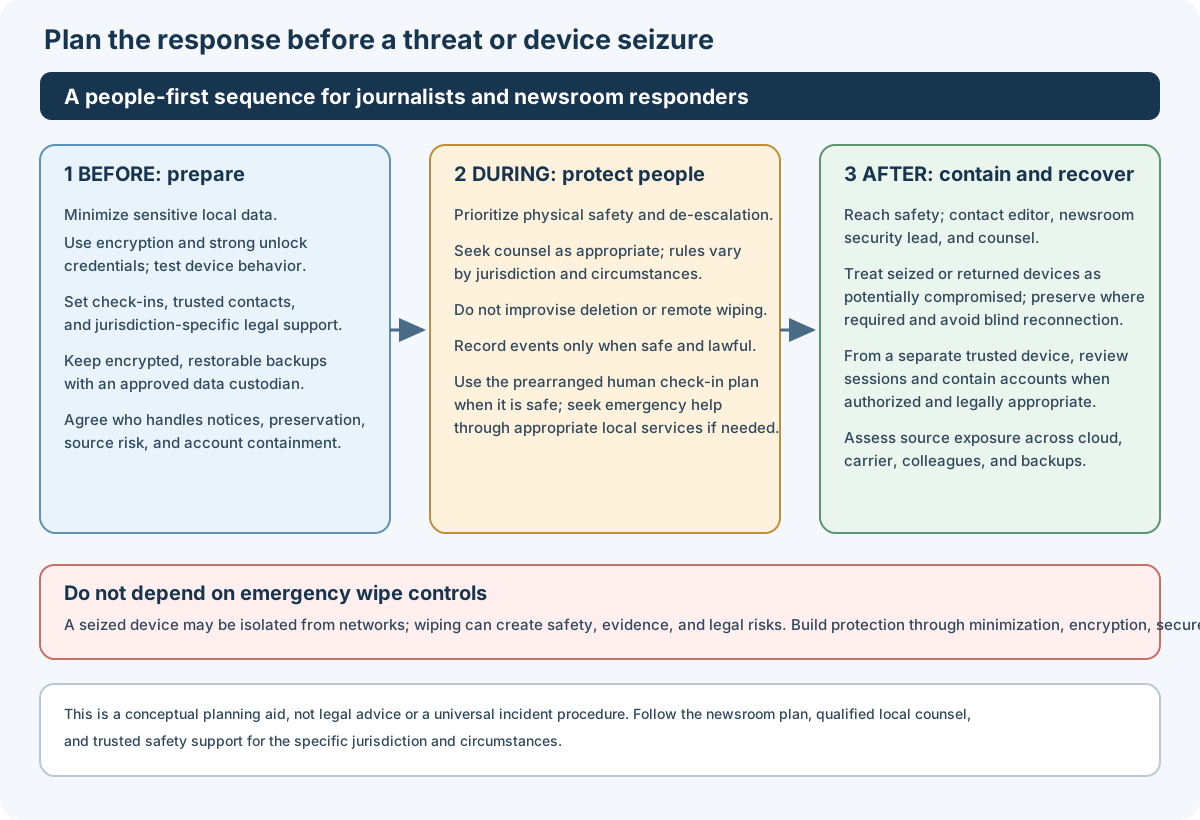
Original conceptual response sequence separating pre-incident preparation, immediate safety and counsel priorities, and post-incident preservation and account containment. It is not legal advice or a universal response procedure.
| Diagram | Embedded guide |
|---|---|
| Journalist device seizure and duress response | Duress, device seizure and emergency response |
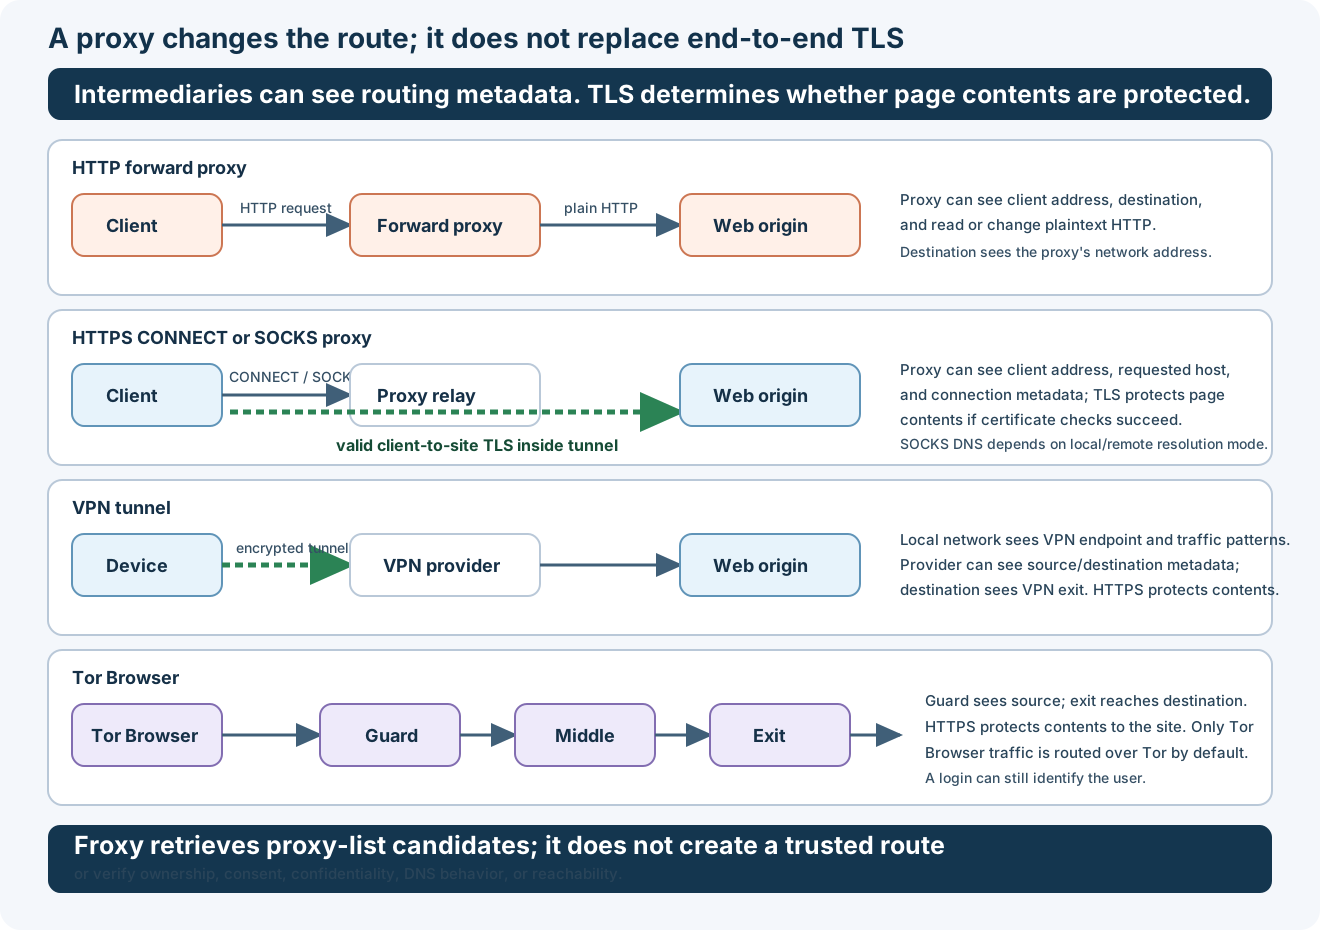
Original conceptual comparison of proxy, VPN, SSH, and Tor paths. It distinguishes routing metadata visible to intermediaries from page contents protected by valid destination TLS.
| Diagram | Embedded guide |
|---|---|
| Proxy routes and observer visibility | Proxy types, DNS leaks and Froxy |
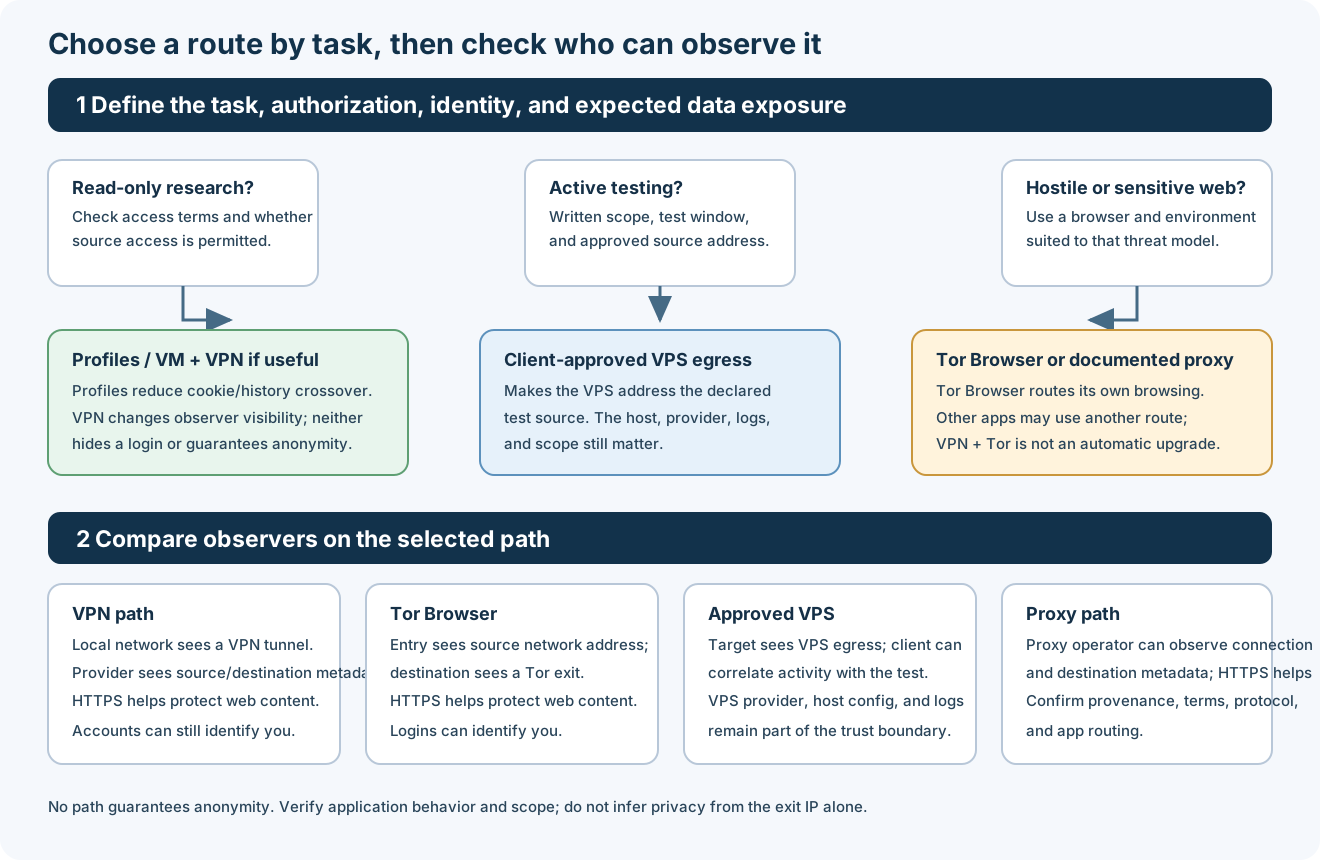
Original conceptual decision map separating task intent, network-path choices, observer tradeoffs, and the limits of proxying and browser compartments.
| Diagram | Embedded guide |
|---|---|
| Anonymity layering decision map | Anonymity layering for OSINT and authorized engagements |
| VPS tunnel health checks | Anonymity layering for OSINT and authorized engagements |
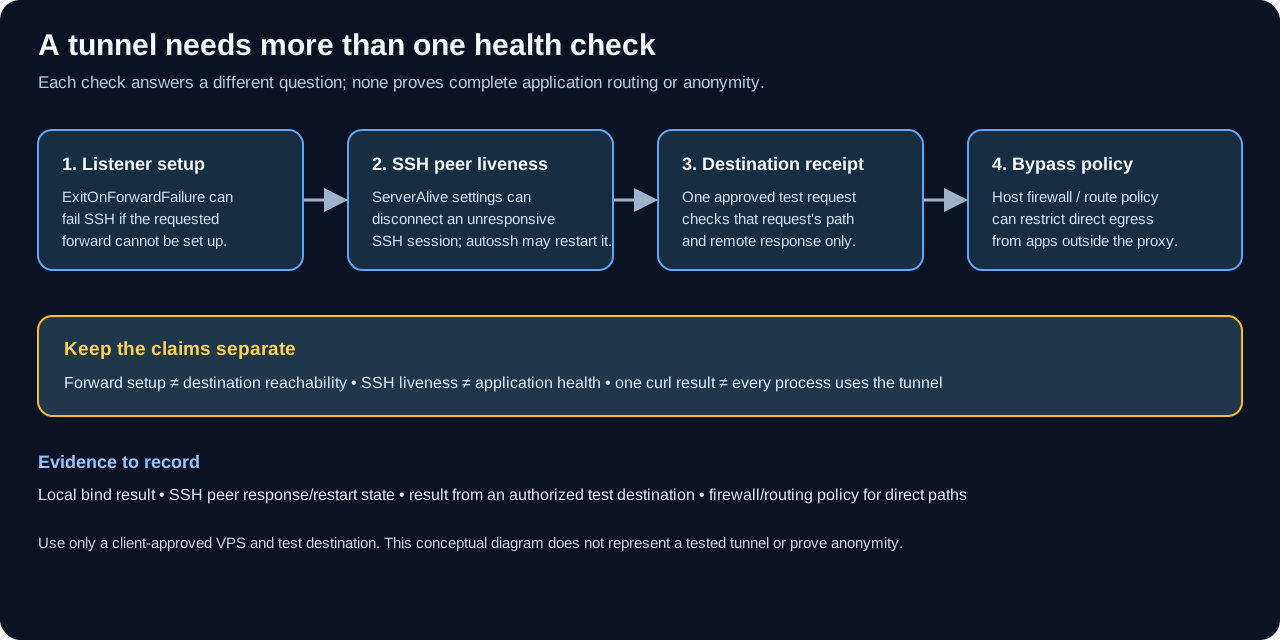
Separate listener, SSH, destination, and bypass checks.
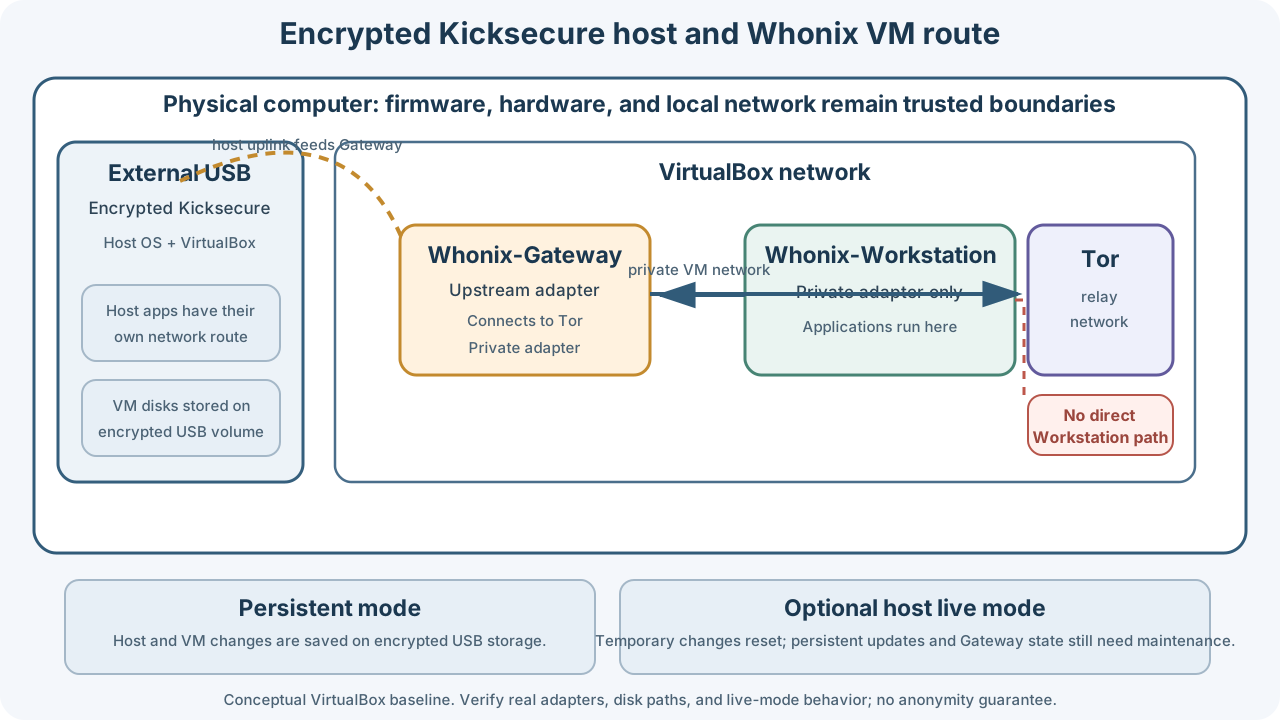
Original conceptual topology of an encrypted Kicksecure host, Whonix Gateway/Workstation routing, and persistent versus live session storage.
| Diagram | Embedded guide |
|---|---|
| Whonix and Kicksecure USB boundaries | Whonix + Kicksecure USB setup |
- Use a relative path from the embedding Markdown file; for a root-level page use
./assets/image.png, for a one-level-deep section use../assets/image.png, and for a two-level-deep section use../../assets/image.svg. - Provide meaningful Markdown alt text and a short caption, including whether the image is conceptual or based on verified deployment/test data.
- Avoid claiming an illustration proves encryption security, exploitability, network isolation, or real-world device behavior.
- Keep SVG assets static: no script, animation, external fonts or third-party image dependencies. Preserve the embedded
titleanddescfor accessibility. - When an image is superseded, update all backlinks and run repository lint/link checks. Maintain this table.
Master README | Role Navigation | Visual reference notes
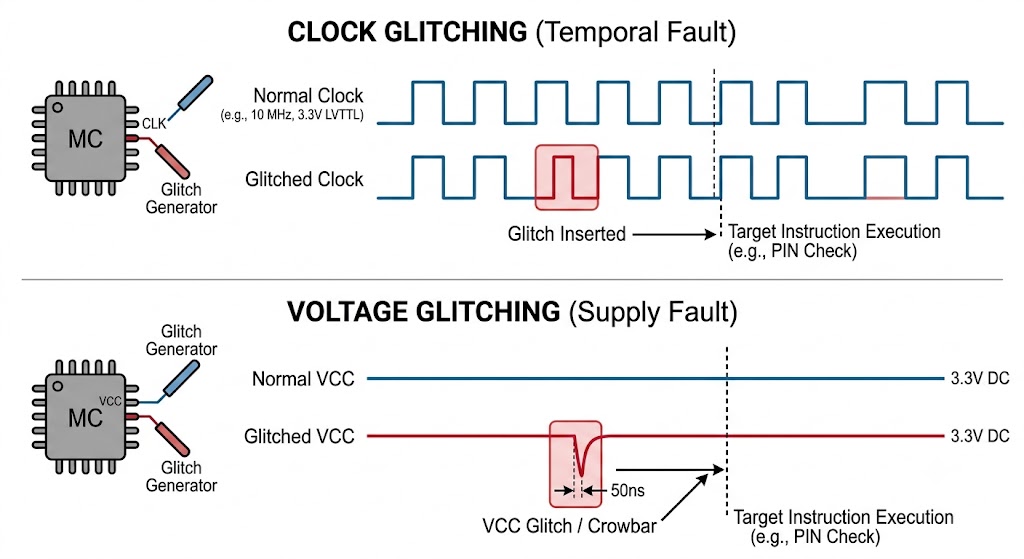
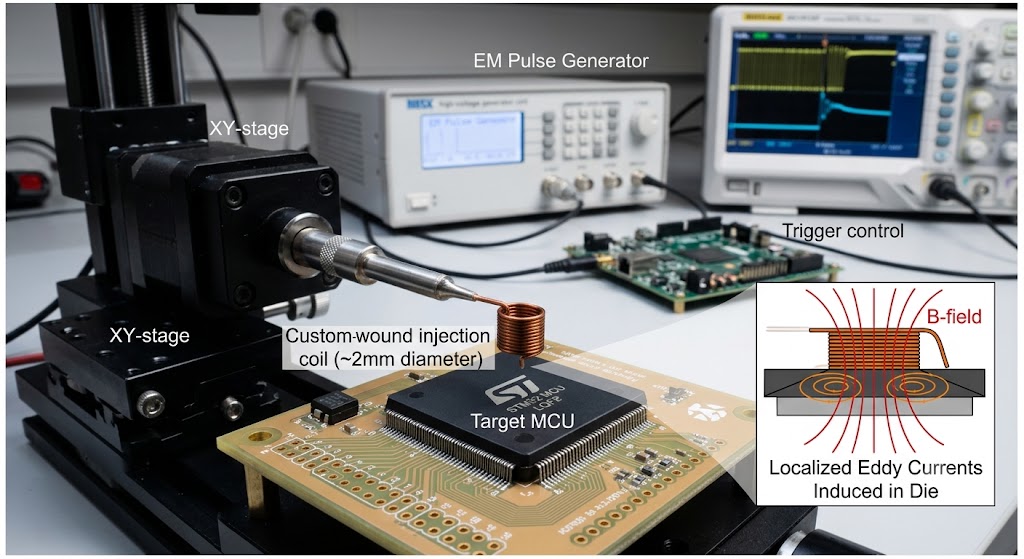
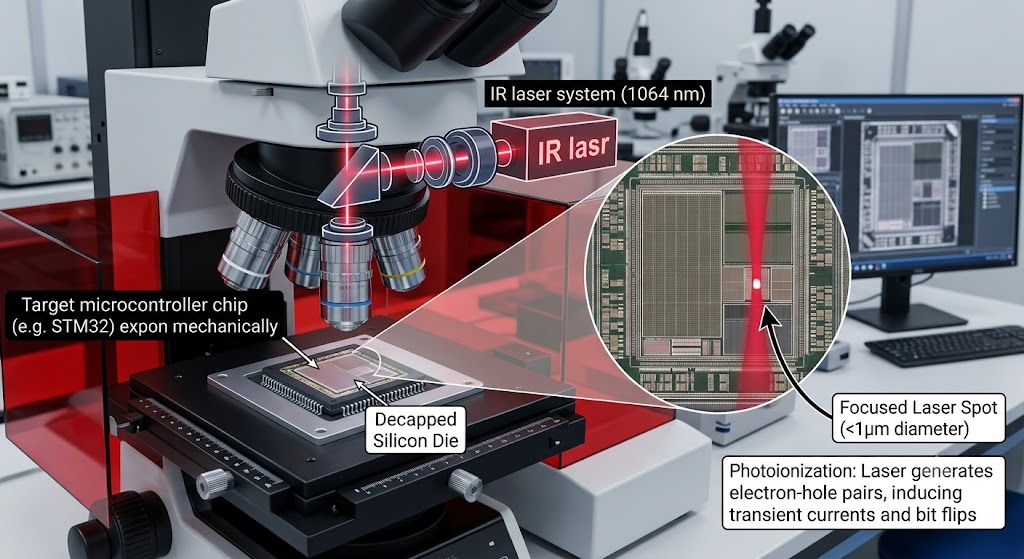
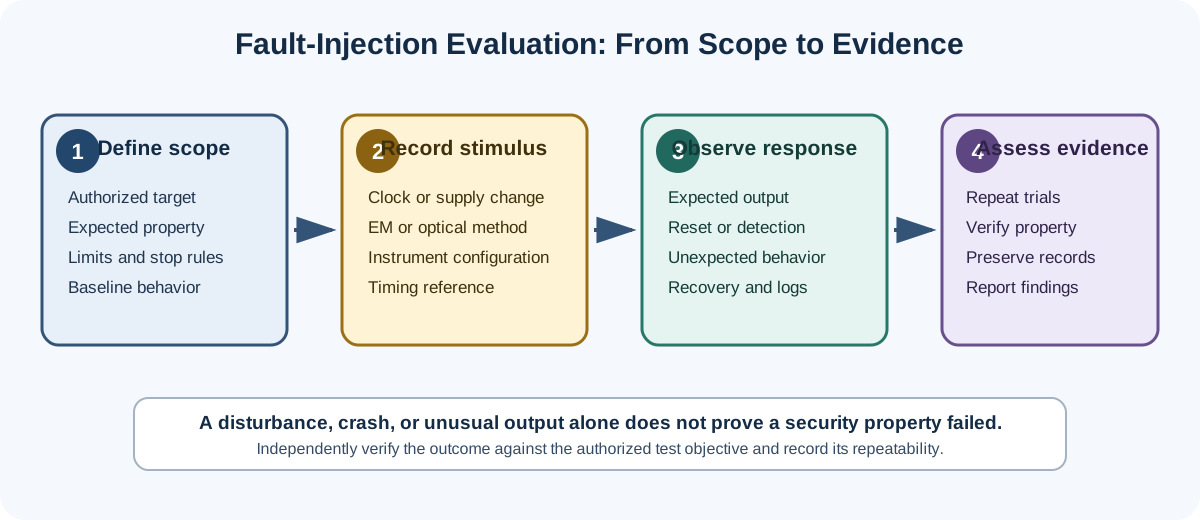
Original conceptual evidence flow for authorized, controlled assessments. It does not show circuit connections or claim a tested attack result.
| Diagram | Embedded guide |
|---|---|
| Fault-injection evaluation evidence flow | Fault Injection Attacks |
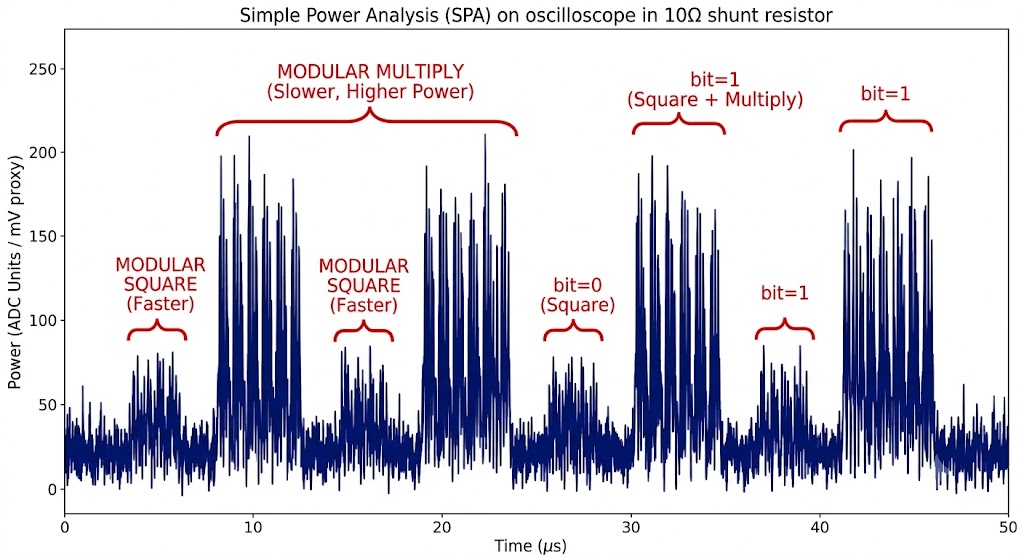
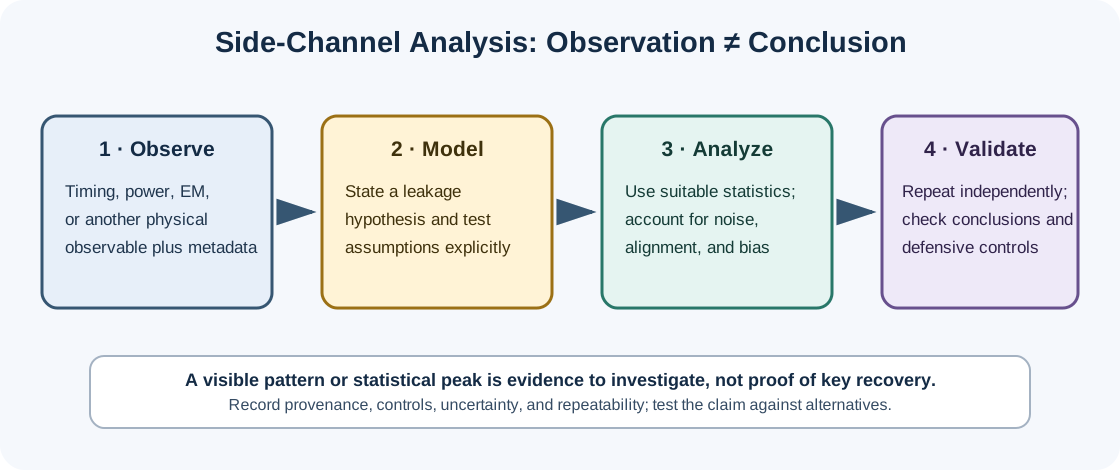
Original conceptual analysis flow separating physical observation, leakage modeling, statistical analysis, and independent validation. It does not represent a measured trace or proven key recovery.
| Diagram | Embedded guide |
|---|---|
| Side-channel evidence analysis | Timing and Power Analysis |
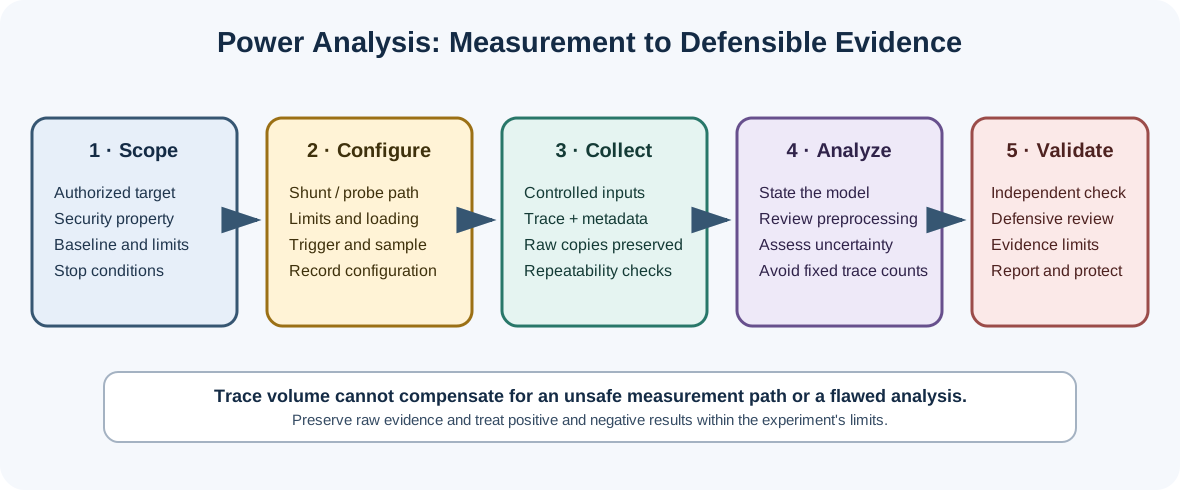
Original conceptual workflow for authorized leakage assessment. It does not represent a measured trace or tested key recovery.
| Diagram | Embedded guide |
|---|---|
| Power-analysis measurement and evidence flow | Power Analysis Practicals |
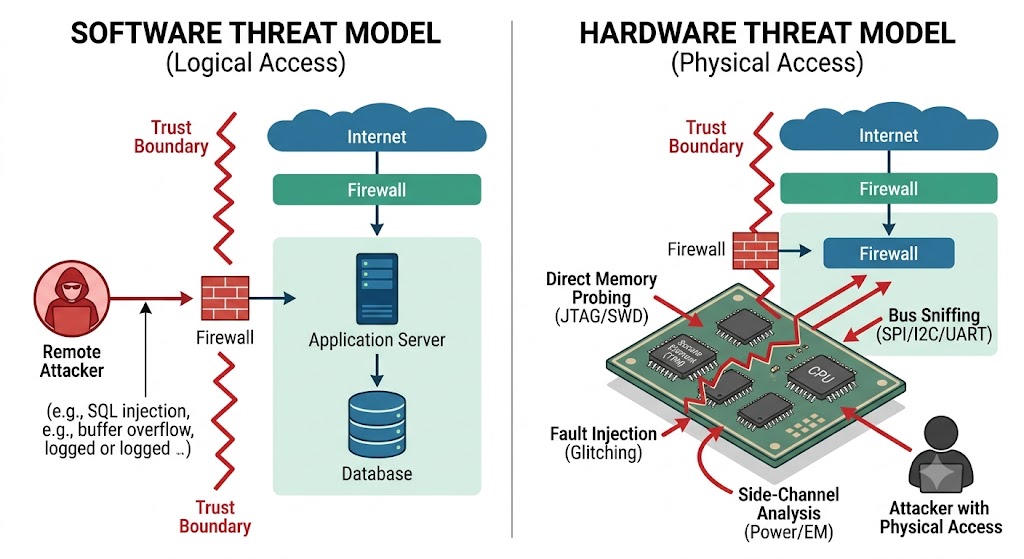
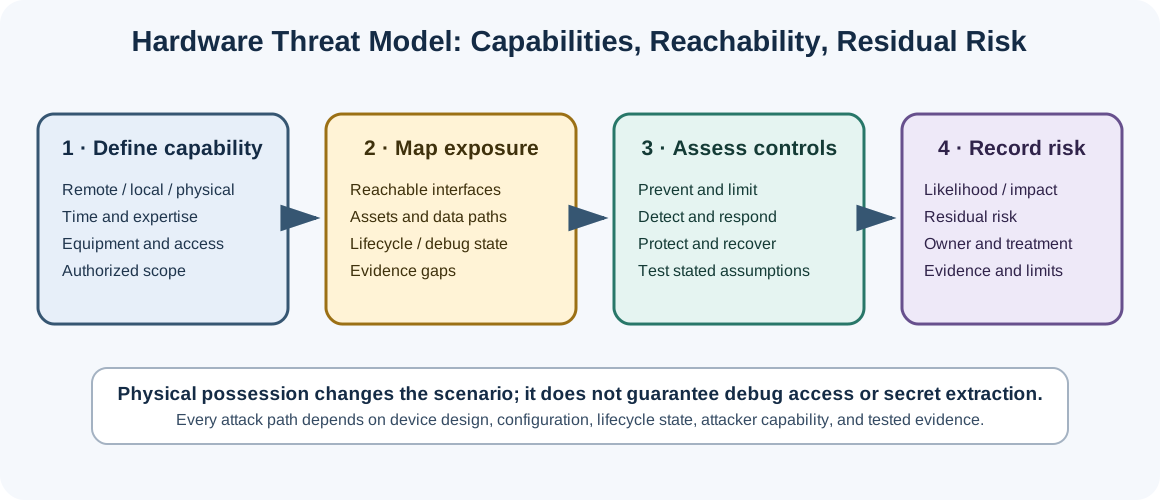
Original conceptual flow from attacker capability and reachable interfaces to assessed controls, residual risk, and evidence. Physical possession does not guarantee interface access or secret extraction.
| Diagram | Embedded guide |
|---|---|
| Hardware threat-model capability flow | Hardware Threat Modeling |
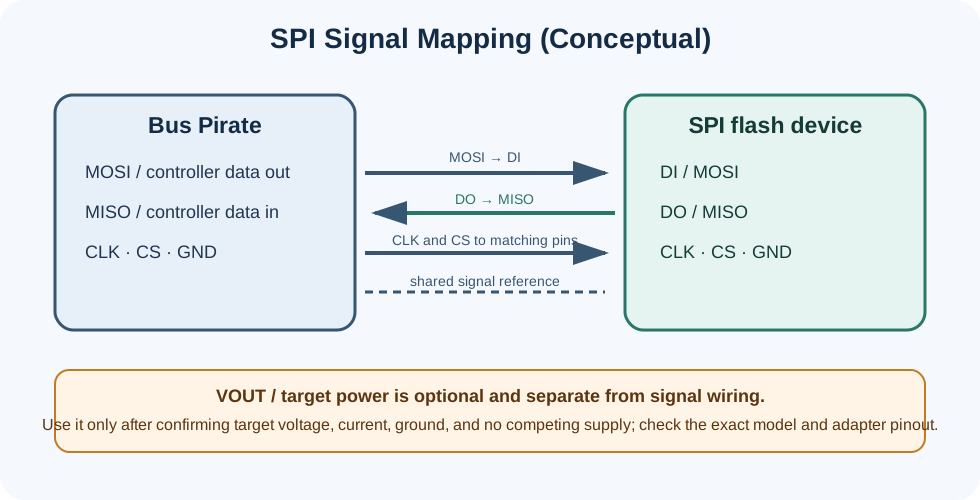
Original conceptual wiring map. Pin labels depend on hardware revision and adapters; the optional VOUT path is separate and requires checking the target rail before connection.
| Diagram | Embedded guide |
|---|---|
| Bus Pirate SPI signal mapping | Bus Pirate guide |
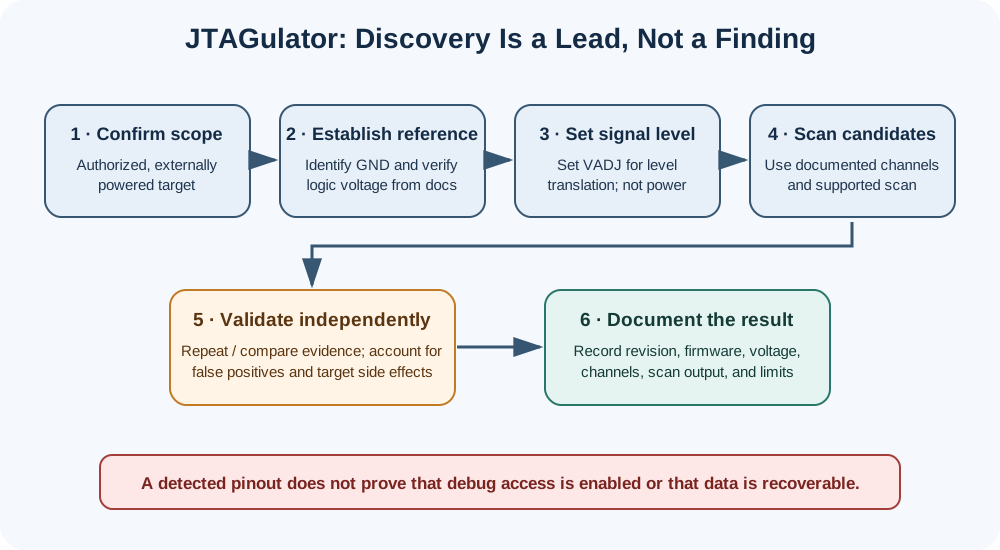
Original conceptual process map. It separates target power from VADJ level translation and treats scan output as a candidate requiring validation.
| Diagram | Embedded guide |
|---|---|
| JTAGulator discovery and validation flow | JTAGulator guide |
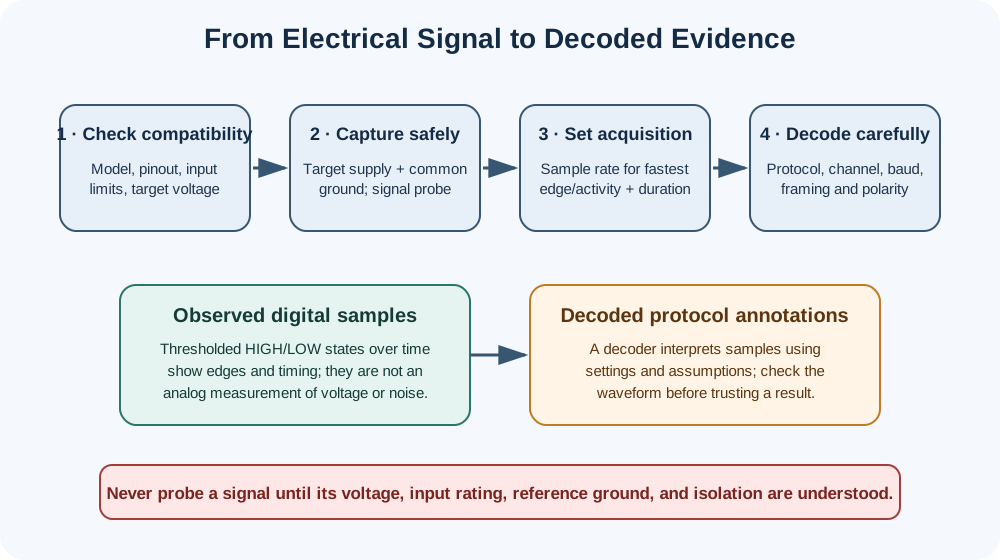
Original conceptual workflow. Device specifications, input limits, supported drivers, capture rates, and thresholds vary by hardware; decoded protocol annotations depend on configuration.
| Diagram | Embedded guide |
|---|---|
| Digital logic capture boundaries | HiLetgo logic-analyzer guide |
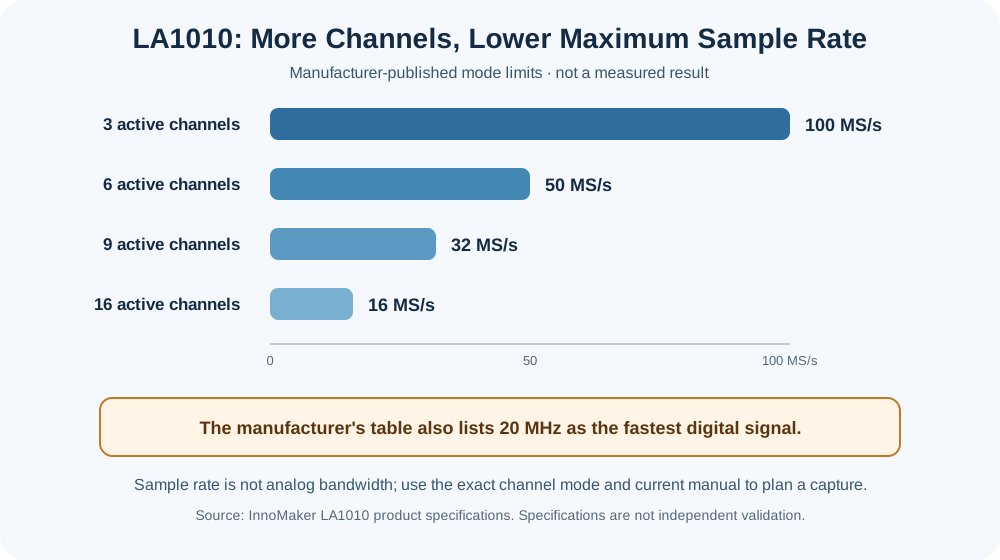
Manufacturer-published sampling limits by active-channel count. Use the detailed model specifications and current manual; the diagram is not a measured capture.
| Diagram | Embedded guide |
|---|---|
| LA1010 active-channel sample-rate tradeoff | LA1010 guide |
| Diagram | Embedded guide |
|---|---|
| PCI DSS scoping evidence trail | PCI DSS scope review worksheet |
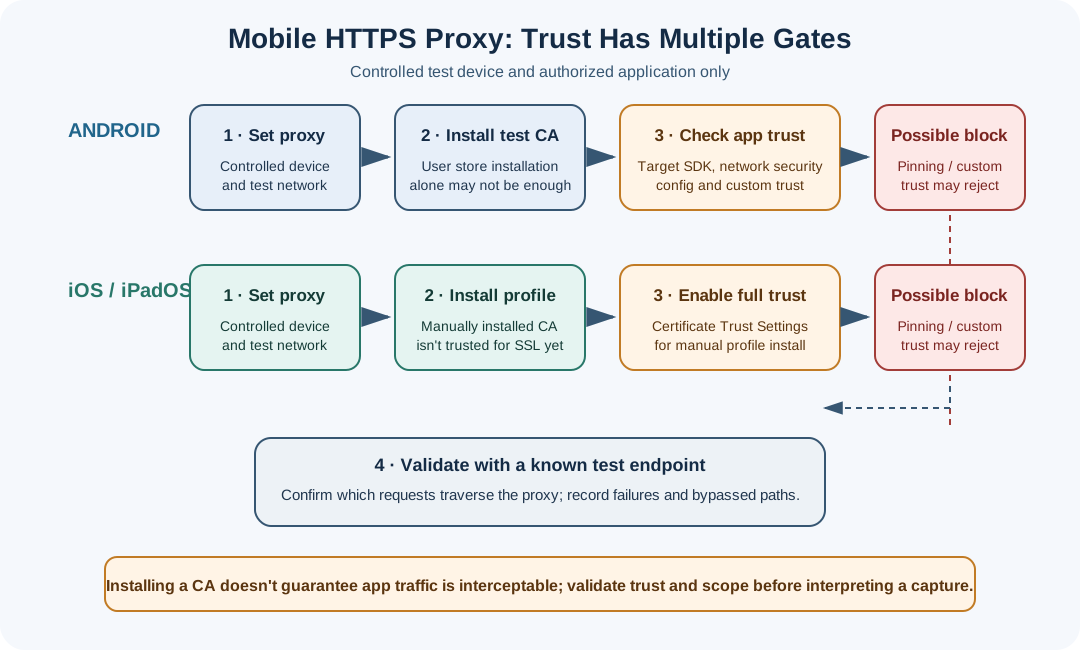
Original conceptual comparison of Android and iOS trust gates for a controlled HTTPS proxy test. CA installation, platform trust, app-specific trust, and pinning are separate checks.
| Diagram | Embedded guide |
|---|---|
| Mobile TLS proxy trust path | Mobile guide |
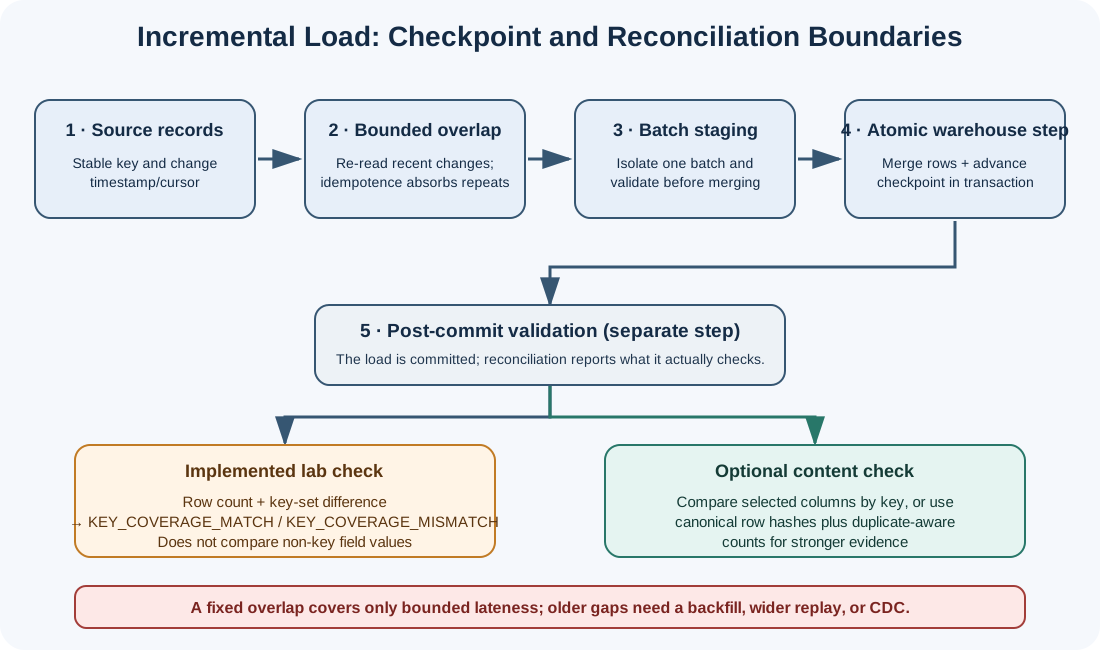
Original conceptual flow separating extraction and transactional checkpoints from post-commit validation. The diagram distinguishes key-coverage checks from optional row-content comparison and shows the bounded-lateness limitation of a fixed overlap window.
| Diagram | Embedded guide |
|---|---|
| ETL key-coverage reconciliation flow | Incremental ETL/ELT pipeline design |
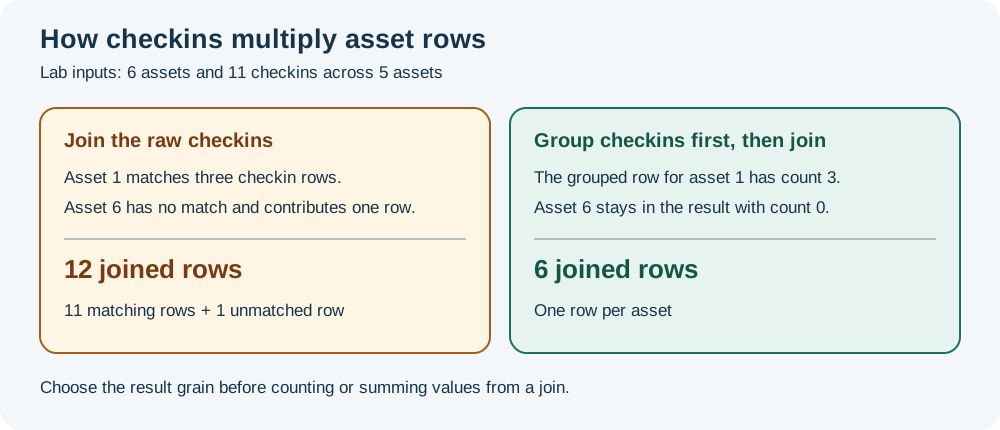
| Diagram | Embedded guide |
|---|---|
| Asset and checkin join grain | SQL joins |
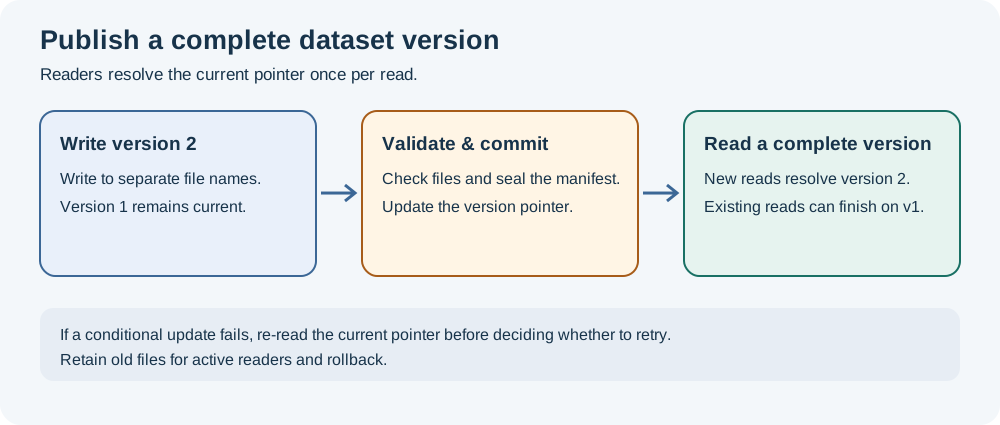
| Complete dataset version publication | Publish complete versions |
📂 Folder: assets | ✏️ Suggest an edit | 🗺️ Browse by Topic
- 🗺️ Browse by Topic
- 📂 All Repository Files
- 🧭 Learning Paths
- 📖 Master Guide
- 🔤 Glossary
- ⚖️ Legal & Disclaimer
📘 Foundations & Learning
🛡️ Defense & Investigations
- Incident Response
- Open Source Intelligence (OSINT)
- Reverse Engineering
- Operations Security (OPSEC)
- Compliance
☁️ Platforms & Infrastructure
📡 Hardware, Wireless & Field Projects
- PNWC Cyberdeck
- Hardware Testing
- Hardware Hacking
- Software-Defined Radio
- Wardriving
- uConsole
- Space Security
🧰 Assessment & Field Reference
📦 Downloads & Project Resources
🗂️ Additional Topics