Repository navigation
PCI DSS Scope Review Reusable Evidence Worksheet
Companion to the PCI DSS 4.0.1 Scoping & Segmentation Field Guide. Blank template only. Do not commit completed client copies, real payment account data, production configurations, credential material, or private third-party agreements to a public repository.
Caution
This worksheet is not a PCI SSC SAQ, ROC, AOC or certification. The entity, assessor and compliance-accepting organization determine applicability and validation. Treat every blank as unassessed, not "out of scope" or "not applicable."
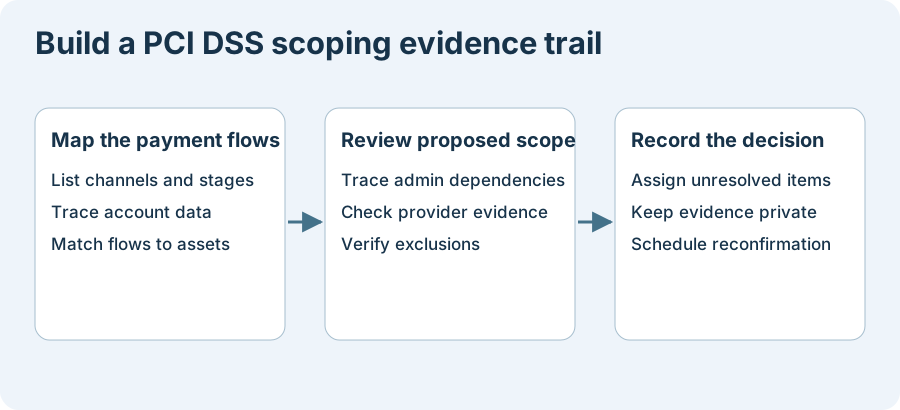
Assign stable IDs to each flow, asset and provider. Use those IDs to link proposed exclusions to their evidence and record unresolved items with an owner. Keep completed worksheets and evidence in the private review record. PCI SSC scoping and segmentation guidance.
| Field | Authorized review entry |
|---|---|
| Entity / merchant or service-provider role | Private record |
| Payment channels and brands / acceptance program | Private record |
| PCI DSS / SAQ / ROC version used | Verify current form |
| Review owner / assessor / acquirer contact | Private record |
| Review date / next review deadline | Date and cadence |
| Significant change since last review | Change IDs or none, verified |
| Written authorization and boundaries | Private evidence ID |
| Evidence repository and retention controls | Private evidence ID |
| Overall status | Draft / pending evidence / reviewed / approved |
Include authorization, capture, settlement, refunds, chargebacks and recurring billing where relevant. Record card-present, e-commerce, MOTO and virtual-terminal channels separately.
| Flow ID | Channel & stage | Entry / processing / exit | Data types present? | System & provider IDs | Evidence ID | Owner |
|---|---|---|---|---|---|---|
| FLOW-01 | To assess | Redacted architecture | PAN, SAD, token, or unknown | ASSET/TPSP IDs | Private | Role |
Reconcile all identified paths against the updated network diagram and account-data flow diagram. Include temporary logs, troubleshooting artifacts, backups and physical media when applicable.
| Asset or service ID | Role & location | Data interaction | Proposed class | Access & security dependencies | Evidence / justification | Reviewed? |
|---|---|---|---|---|---|---|
| ASSET-01 | Functional description | Store / process / transmit / none / unknown | CDE / connected-to / security-impacting / exclusion candidate | Identity, network, backup, remote support | Private evidence ID | Pending |
Document the evidence that supports each proposed exclusion. Check the component's account-data role, connectivity to the CDE, and ability to affect CDE security. Use the evidence appropriate to each question, such as current data flows, administrative access paths, and segmentation test results where segmentation is used to reduce scope. Mark unresolved exclusions as pending. PCI SSC FAQ on segmentation and assessment scope.
| Boundary ID | Source segment or identity | CDE destination / control plane | Control & rule ID | Approved test method / date | Expected / actual result | Reviewer / retest |
|---|---|---|---|---|---|---|
| SEG-01 | Representative source | Sanitized target | Private evidence ID | Written authorization required | Unverified | Pending |
Record segmentation design plus independent test results as applicable, including changes and remediation. Do not substitute a firewall screenshot or ping result for a comprehensive assessment. See PCI DSS 11.4.5 and service-provider-only 11.4.6.
| TPSP ID | Actual service | Direct/indirect CDE impact | Customer / provider / shared PCI responsibility | AOC or control evidence & expiry | Agreement & monitoring | Owner |
|---|---|---|---|---|---|---|
| TPSP-01 | Service definition | Access path | Requirement IDs / matrix ID | Private evidence | Review date | Role |
Validate that the provider evidence covers the specific service. Document nested providers, provider access and exit/revocation. Refer to 12.8/12.9 and the November 2026 PCI SSC service-provider guidance.
| Question | Review evidence |
|---|---|
| Is checkout redirected, embedded iframe/hosted fields, direct post or merchant collection? | Provider technical integration and diagram |
| Who controls the merchant page, scripts, redirects, DNS, hosting and deployment? | Change logs, inventory, responsible entity |
| Do current SAQ eligibility criteria hold (including embedded script criteria where relevant)? | SAQ version, acquirer/assessor decision |
| Have applicable payment-page script and tamper controls been evaluated? | Requirements 6.4.3 / 11.6.1 applicability record |
| Has any required SAQ A e-commerce ASV scanning been performed by a listed ASV? | Requirements 11.3.2/11.3.2.1, as applicable; private report ID |
A vendor's "PCI compliant" label does not determine the merchant's SAQ eligibility.
- All payment acceptance channels, transaction stages and account-data flows reconciled.
- Locations, storage, paper, recordings, logs, backups, cloud replicas and access paths investigated.
- Network/data-flow diagrams and in-scope inventory dated and reconciled.
- Connected-to and security-impacting identity/remote-admin/management infrastructure included.
- Proposed exclusions have documented rationale and appropriate independent boundary testing.
- All applicable third-party service access, agreements, responsibilities and supporting evidence reviewed.
- E-commerce SAQ eligibility and ASV scanning applicability checked with current PCI SSC criteria.
- Scope confirmation scheduled at least every 12 months under 12.5.2, or at least every six months for service providers under 12.5.2.1.
- Significant changes to the in-scope environment trigger a scope confirmation outside the scheduled cycle. PCI SSC significant-change FAQ.
- Findings and unknowns assigned owners; final sign-off retained privately.
| Item ID | Scope decision or unresolved question | Supporting evidence | Reviewer & date | Next action |
|---|---|---|---|---|
| DEC-01 | In scope / proposed exclusion / unresolved | Private reference | Pending | Retest / provider response / assessor review |
Final scope determination: Pending evidence and authorized review.
Do not publish completed copies. Keep this public version as a blank example; use the scope guide and PCI SSC document library for current criteria.
📄 Source: Compliance/pci-scope-review-template.md | ✏️ Suggest an edit | ⬅️ Back to Compliance